Top Fortify DAST (OpenText) alternatives [2026]
Dynamic application security testing has become essential for organizations protecting web applications and APIs. OpenText Fortify DAST is a well known enterprise tool, but many teams in 2026 are exploring alternatives that offer more flexibility, faster scanning, and smoother CI/CD integration.
With the shift toward agile and DevSecOps environments, companies now look for security tools that balance accuracy, automation, and scalability. Today’s leading DAST solutions go beyond vulnerability detection to provide remediation guidance, real time reporting, and support for compliance standards like OWASP Top 10 and PCI DSS.
This guide covers the top Fortify DAST alternatives for 2026, comparing key features, strengths, pricing, and best fit use cases to help you make an informed choice.
Top Fortify DAST alternatives: TL;DR
| Tool | Starting price | Strengths | Best for |
|---|---|---|---|
| Beagle Security | $119/month ($1,188/year) | Developer friendly, web, API, and GraphQL coverage, strong CI/CD fit | Small to mid sized SaaS teams wanting pipeline native automated pentesting at lower cost |
| Tenable (Web App Scanning) | $7,434/year for 5 FQDNs | Unified exposure and app scanning, strong enterprise reporting | Large orgs with many web apps and APIs needing a broad risk view |
| Qualys WAS | $1,995/year for 25 web apps (benchmark) | Cloud native, broad asset and app visibility, compliance support | Organizations with many apps and strong regulatory needs |
| Rapid7 InsightAppSec | $175/month per app ($2,100/year) | Continuous scanning, CI/CD integration, part of the Rapid7 ecosystem | Teams already using Rapid7 or needing deeper analytics for web and API scanning |
| Veracode DAST | $15,000/year entry level (quote based) | Enterprise grade, policy and governance focus across AppSec | Large enterprises with many applications and strong compliance demands |
| Checkmarx One DAST | Custom quote | Unified AppSec (SAST, DAST, API, IaC), strong for consolidated tooling | Enterprises wanting an all in one AppSec platform rather than standalone DAST |
| HCL AppScan DAST | From $29.99/scan, or subscription quote | Flexible pay per scan option, web and API support, on premise/cloud options | Organizations running periodic scans or needing flexible usage patterns |
| Burp Suite | Free (Community) to $475/user/year (Professional) | Widely used manual and automated toolkit, strong extensibility | Security teams with manual pentesting expertise and deep interactive needs |
| Astra Security | $2,999/year (starts at), custom pricing available | AI powered DAST plus PTaaS, expert vetted findings, strong compliance reporting (PCI, SOC 2, and more) | Businesses wanting a mix of automated DAST and manual pentesting with strict compliance needs |
| Black Duck DAST | Quote based | Runtime app scanning plus open source component risk focus | Organizations already using Black Duck SCA and extending into runtime DAST |
| Snyk API & Web (DAST) | From around $25/developer/month, Team tier (5 developer minimum) | Developer first, API and web scanning, strong CI/CD and workflow integration | Developer centric teams or startups wanting to shift security left at lower cost |
Top Fortify DAST alternatives [2026]
Beagle Security
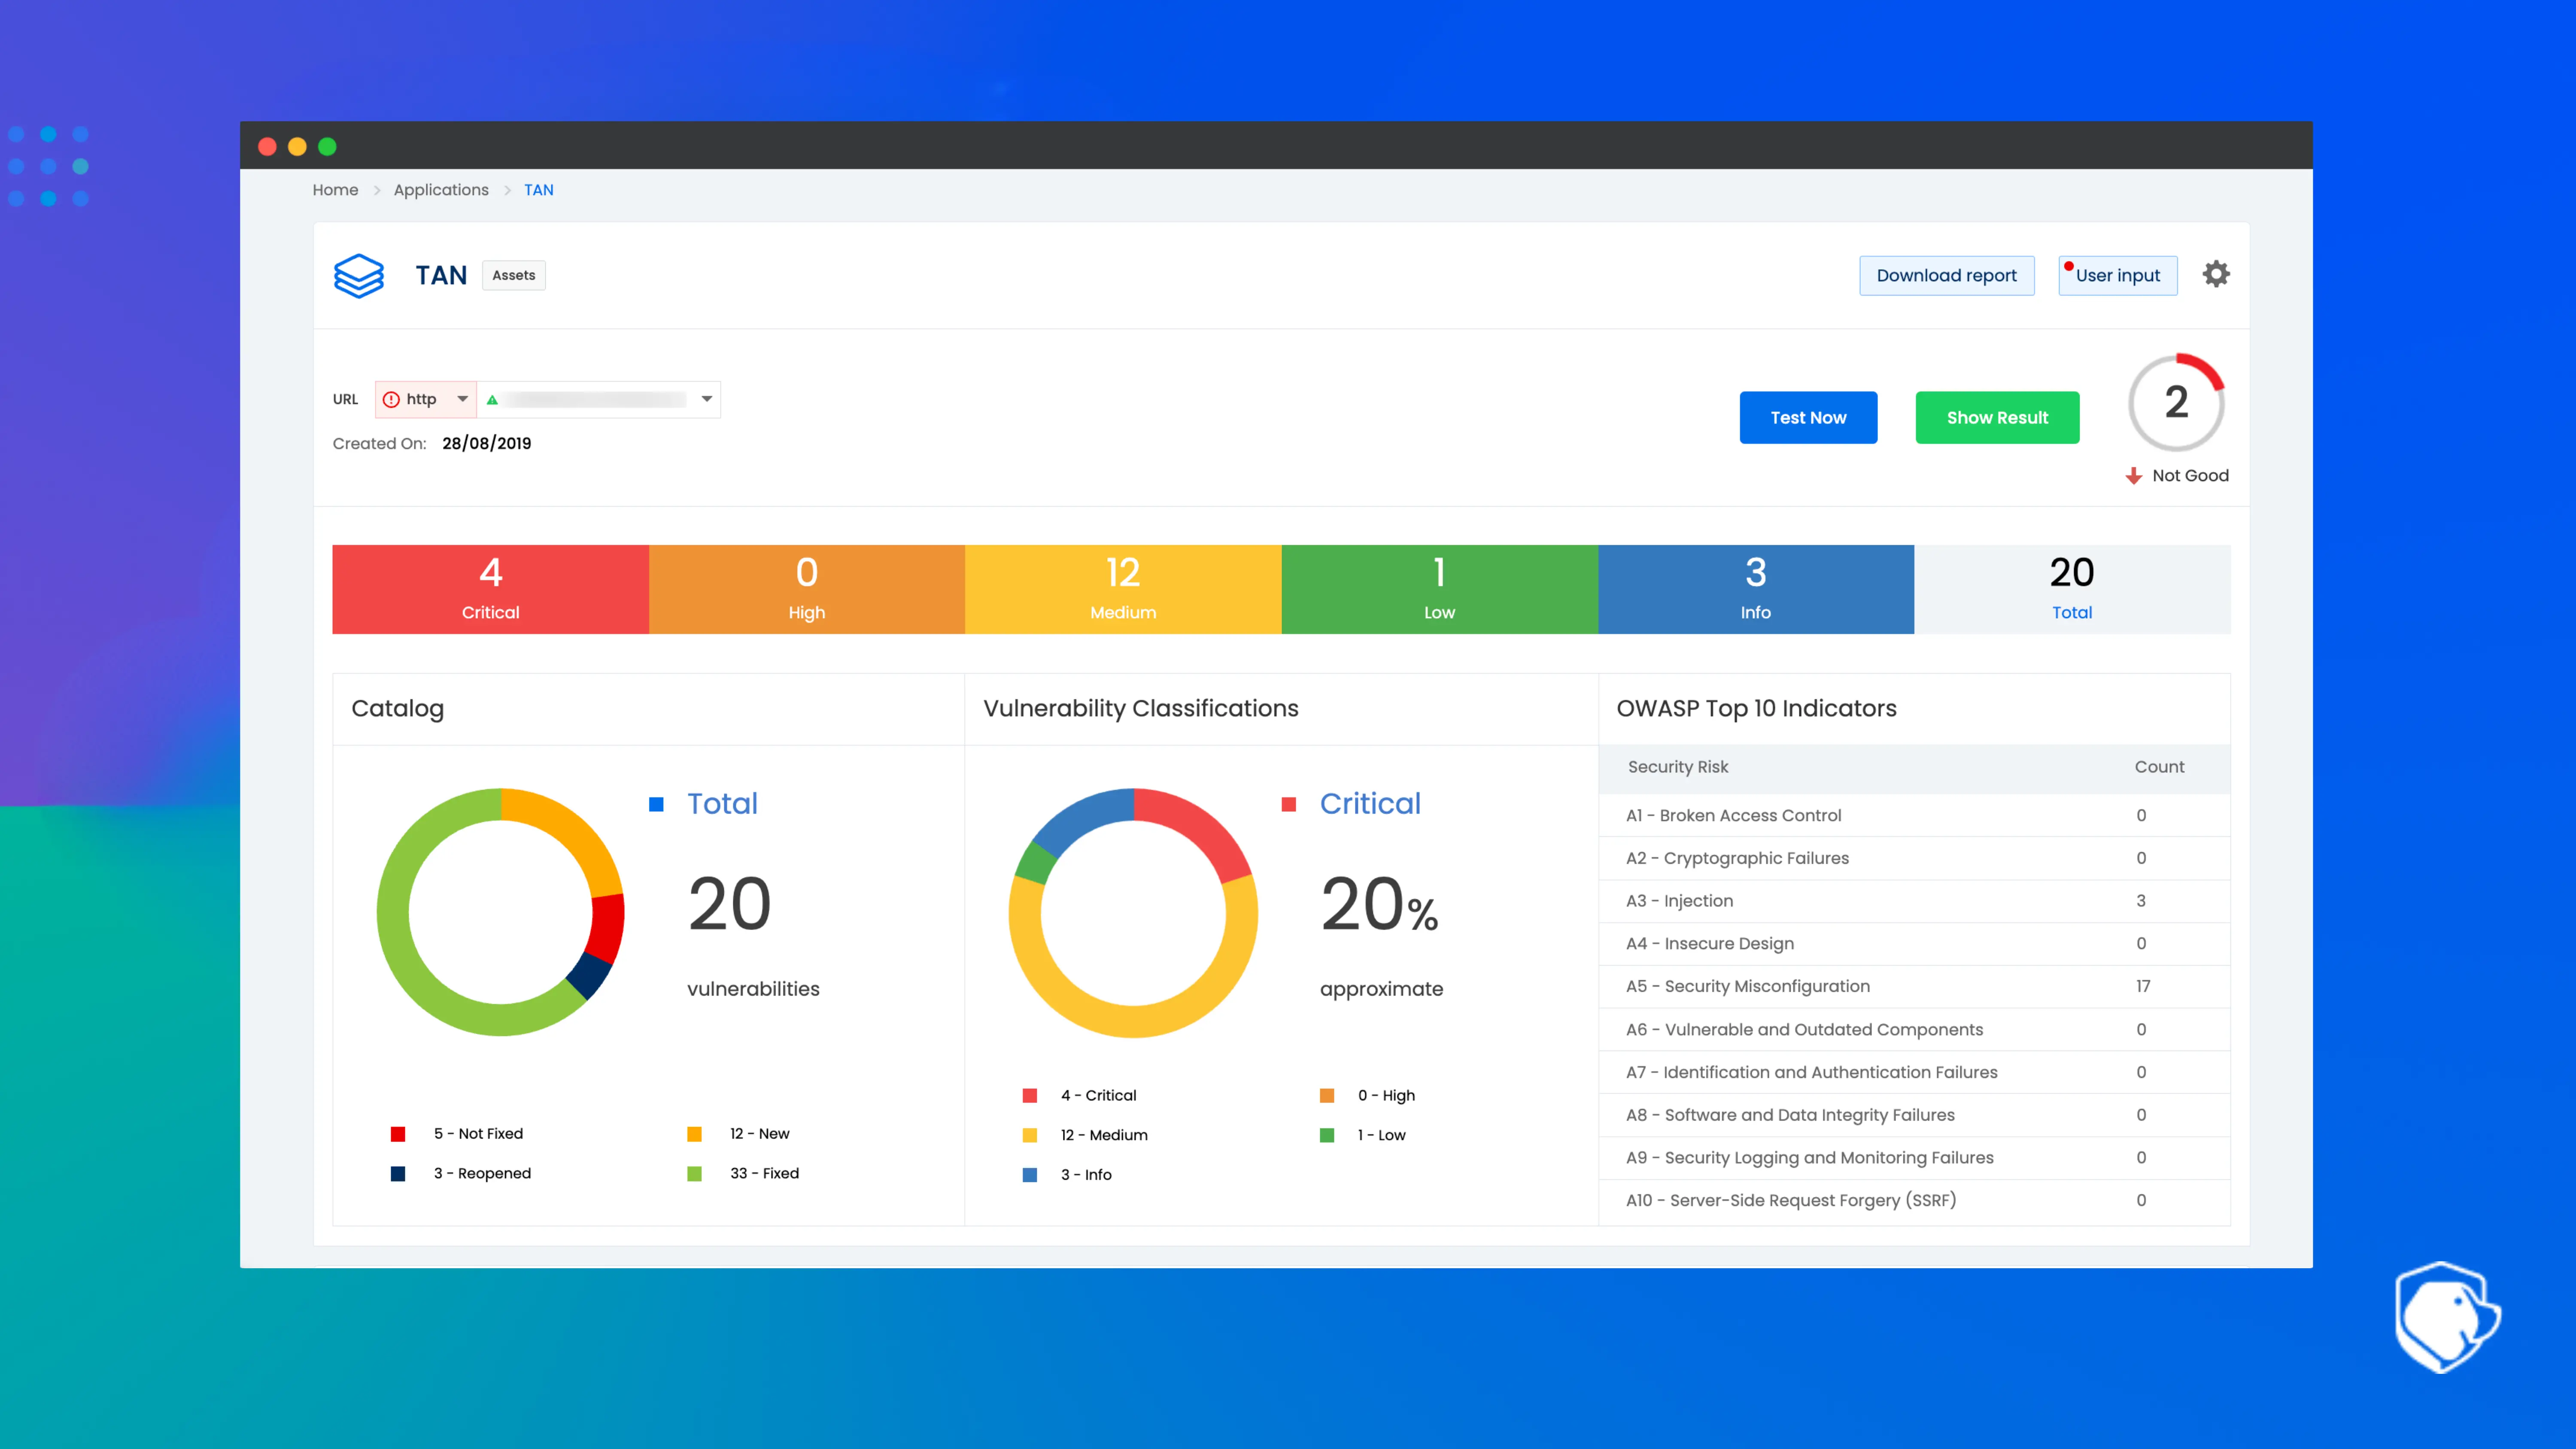
Beagle Security is a SaaS based automated application security platform built to assess web applications and APIs, helping organizations detect, prioritize, and remediate vulnerabilities. It uses agentic AI to automate business logic testing, integrates directly with CI/CD workflows, and generates remediation reports mapped to compliance standards. Teams can run multiple concurrent tests and rely on support for modern authentication flows.
Features
Agentic AI powered web application pentests
Prioritizes vulnerabilities based on business logic Integrates with CI/CD tools and workflows
Supports modern authentication flows and APIs
Provides compliance mapped remediation reports
Pricing
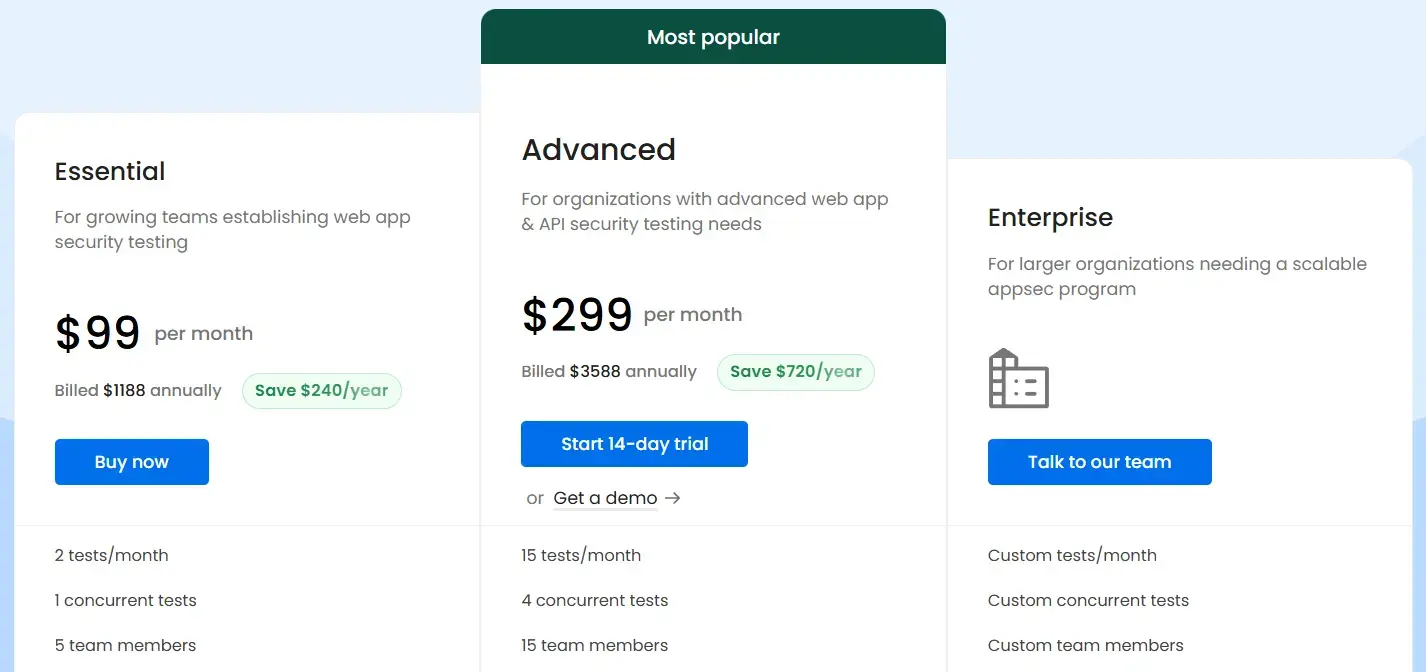
Tiered pricing starting at $1,188 per year, advanced at $3588 per year and enterprise is custom based. A 14 day advanced free trial is available.
G2 rating
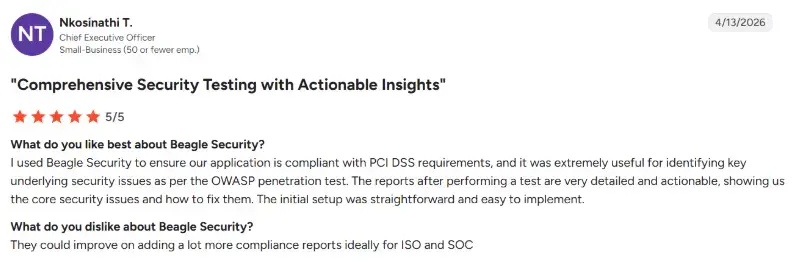
Holds a 4.7 out of 5 rating on G2. Users praise its intuitive interface, AI based test engine, and developer first reports.
Why consider it
A strong option for small to mid sized teams wanting automated, developer friendly scanning at lower cost with solid web and API coverage.
Tenable WAS
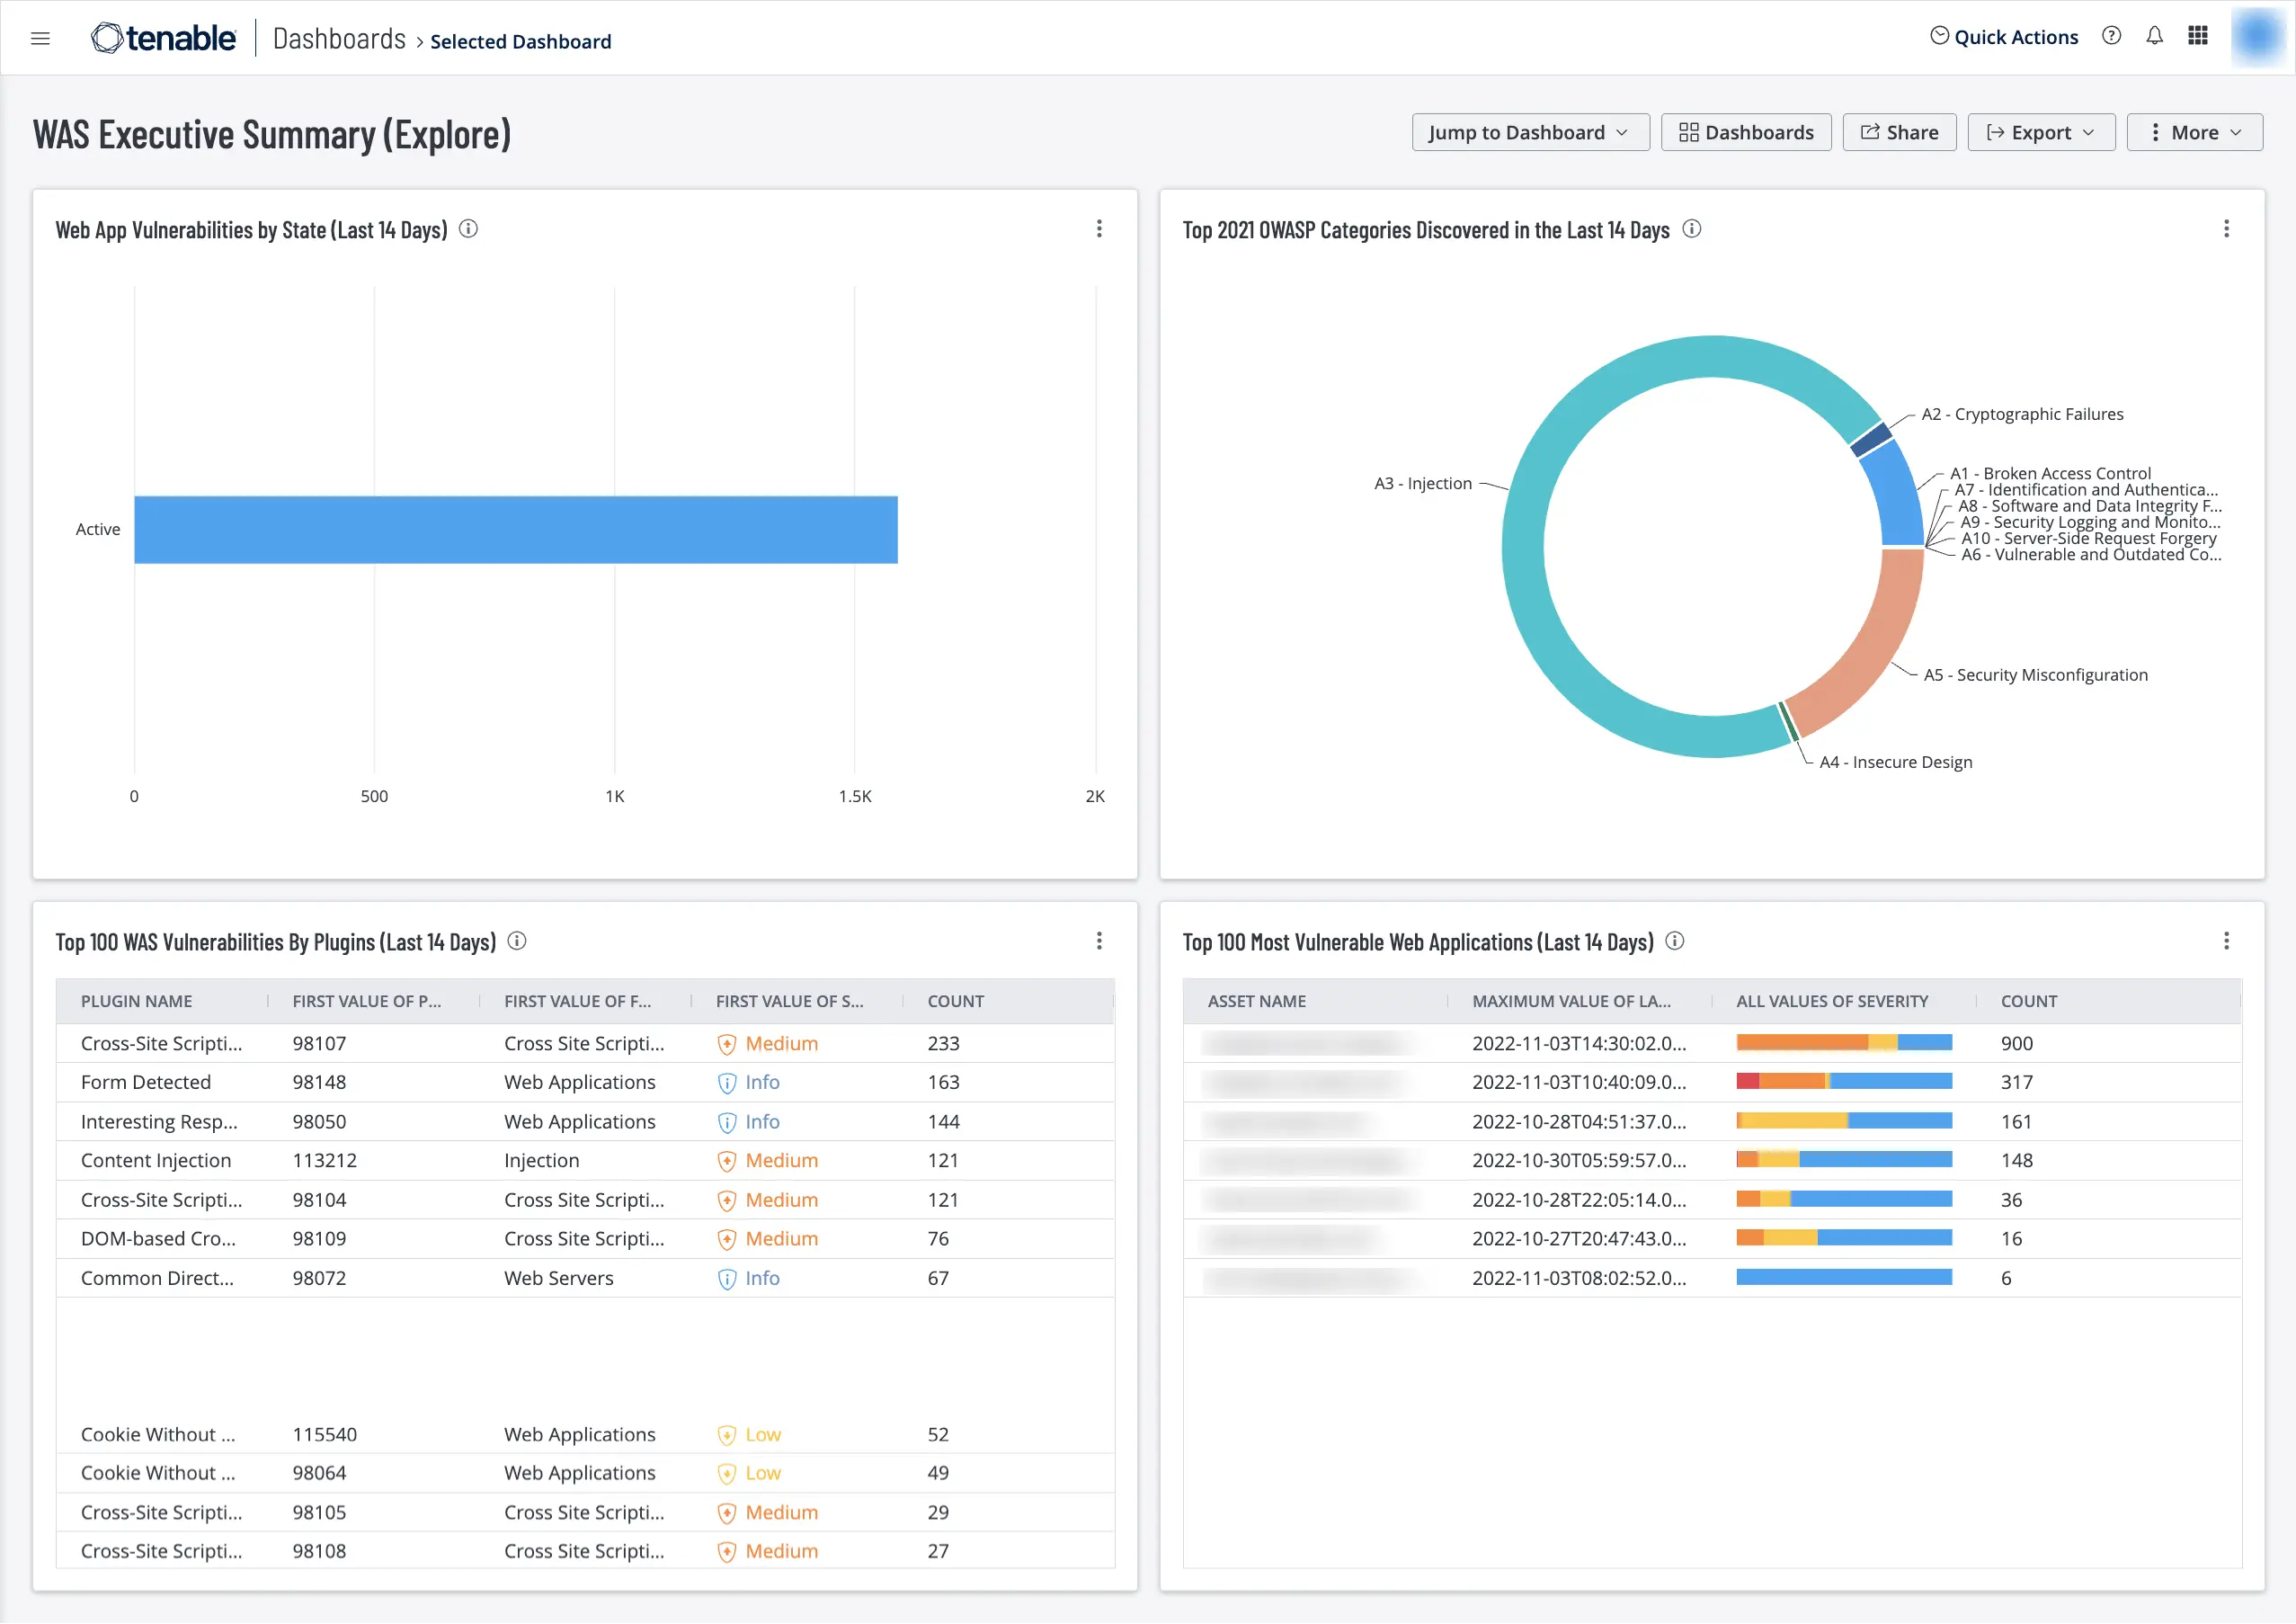
Tenable Web App Scanning is a DAST tool built to scan modern web applications for vulnerabilities such as XSS, SQL injection, improper SSL/TLS configuration, and misconfigurations. It supports both SaaS and on premises deployment, integrates into CI/CD pipelines, and is part of the broader Tenable One Exposure Management ecosystem.
Features
Scans modern web apps including SPAs
Identifies OWASP Top 10 and third party risks
Supports SaaS and on premises architecture
Integrates directly into CI/CD workflows
Safe external scanning designed to avoid disruption
Pricing
Public estimate around $7,434 per year for 5 FQDNs.
G2 rating
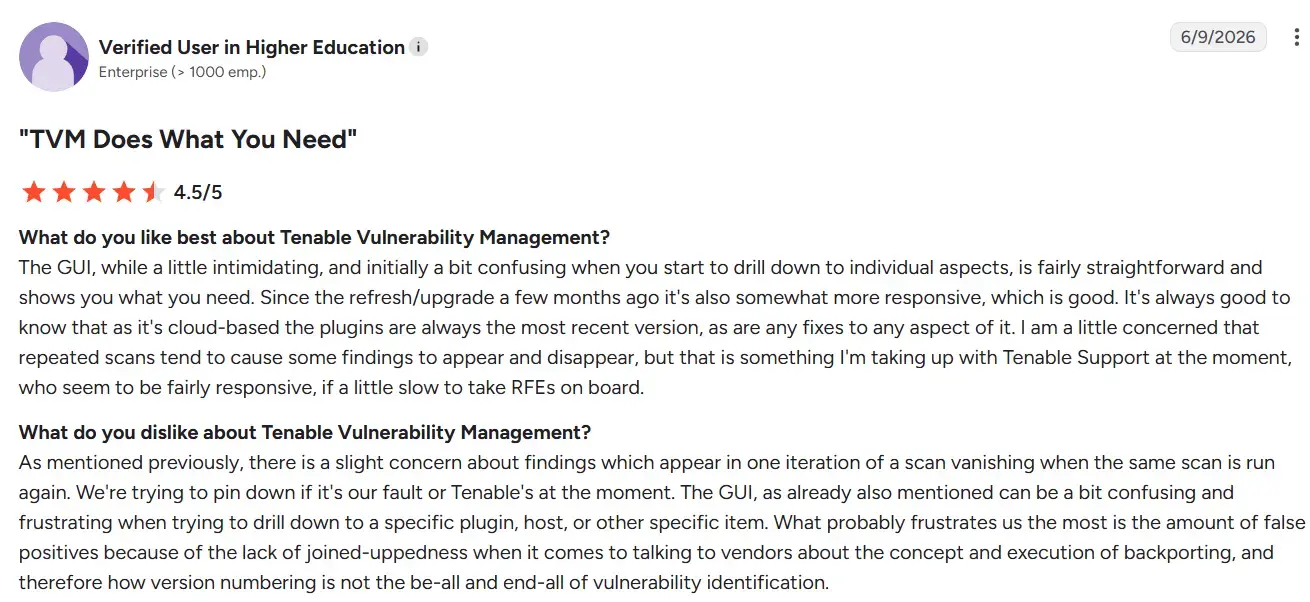
Tenable holds a rating around 4.5 out of 5 on G2, with reviewers frequently citing strong vulnerability coverage, intuitive dashboards, and integration across the broader Tenable ecosystem.
Why consider it
Ideal for enterprises already using Tenable that want unified visibility across infrastructure and applications.
Qualys WAS
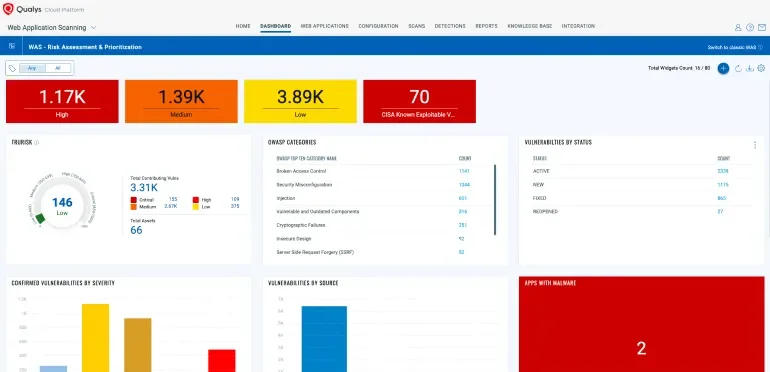
Qualys WAS is a cloud based service for automated crawling and testing of custom web applications. It supports large-scale scanning across thousands of applications, with centralized management, customizable dashboards, and integration with the broader Qualys Cloud Platform.
Features
Automated web app crawling and vulnerability testing
Scalable scanning across thousands of web apps
Centralized dashboard and customizable reporting
Integrated WAF and virtual patch capabilities
Detects web malware and misconfigurations
Pricing
Not published. Around $1,995 per year for 25 web apps(according to UnderDefense)
G2 rating
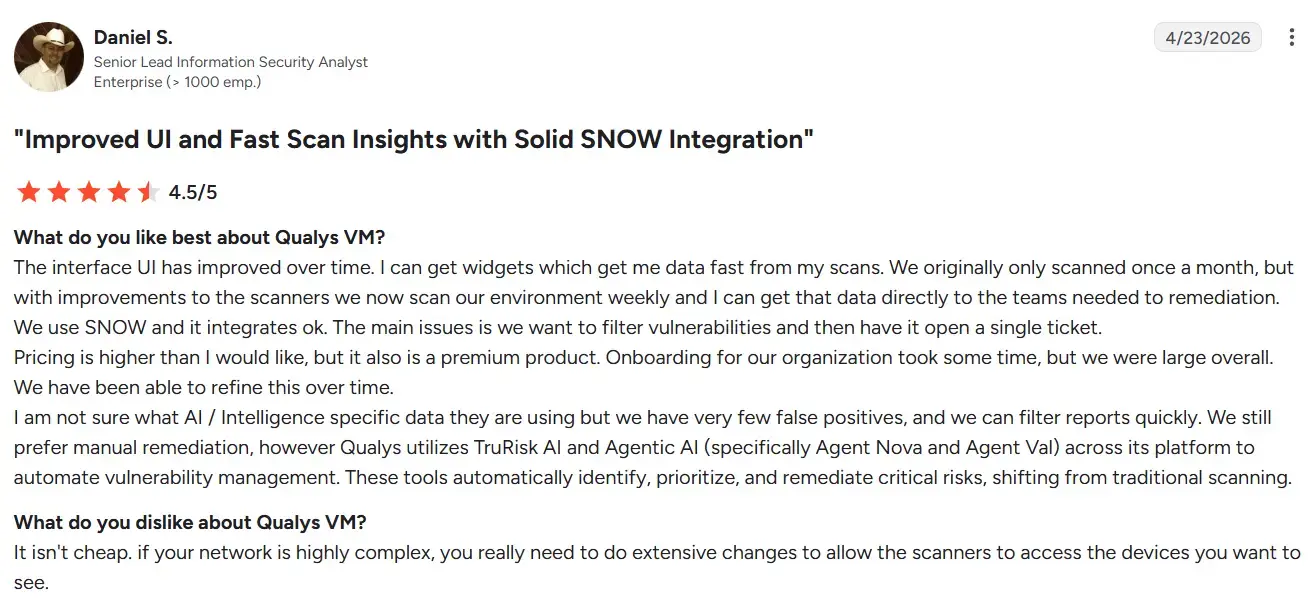
Holds a 4.3 out of 5 rating on G2, recognized for strong asset visibility and integrated vulnerability management.
Why consider it
Suited to organizations needing broad enterprise coverage across many apps with compliance readiness and minimal complexity.
Rapid7 InsightAppSec
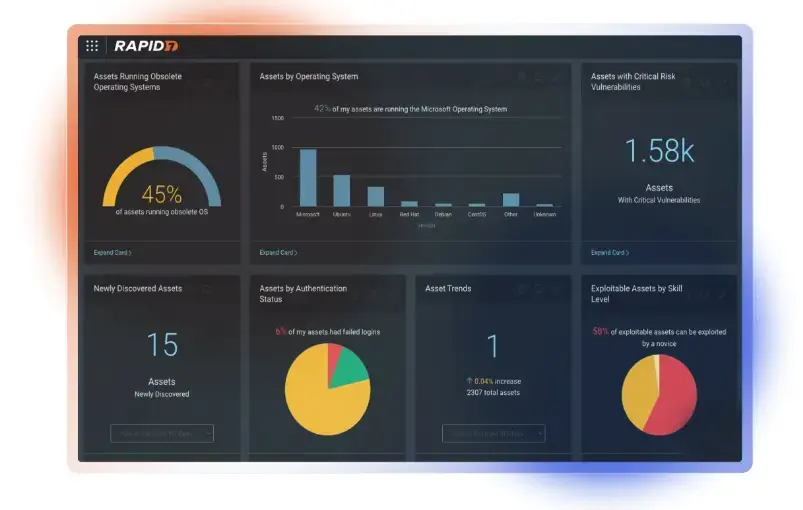
InsightAppSec is Rapid7’s DAST solution, built to automatically assess modern web applications and APIs, identify vulnerabilities, triage risk, and integrate with DevOps workflows. It supports scheduled scans, customizable scan configurations, and API based automation for larger portfolios.
Features
Automated DAST for web apps and APIs
Customizable scan configuration and scheduling
API based integration for DevOps toolchains
Incremental scanning to speed up repeat scans
Triage and prioritization of application risk findings
Pricing
Approximately $175 per month per application (around $2,100/year).
G2 rating
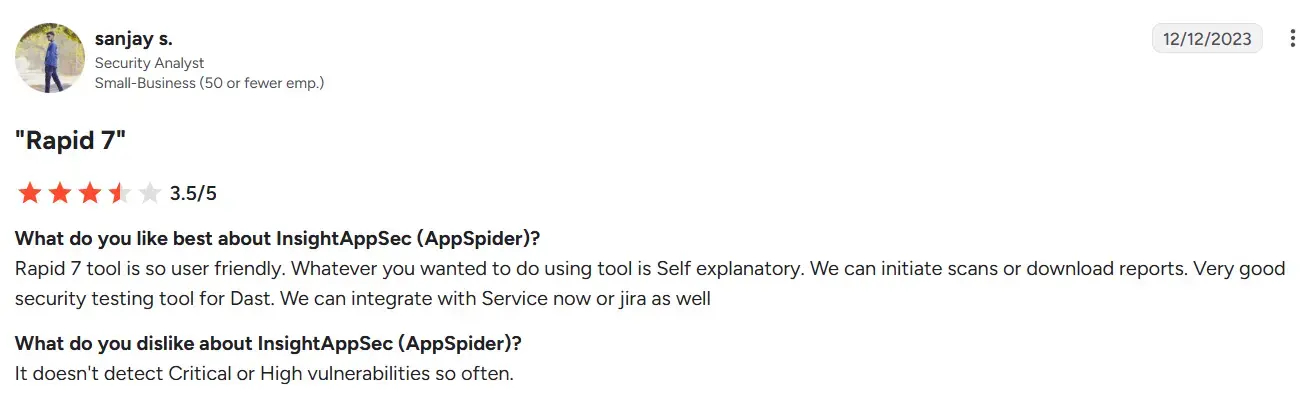
Rapid7 InsightAppSec holds a 3.9 out of 5 rating on G2, with users appreciating its integration across the Rapid7 ecosystem, though some cite a steep learning curve and scan performance issues.
Why consider it
A good fit for security teams already using other Rapid7 products, or needing deeper analytics tied into a broader DevSecOps toolchain.
Veracode DAST
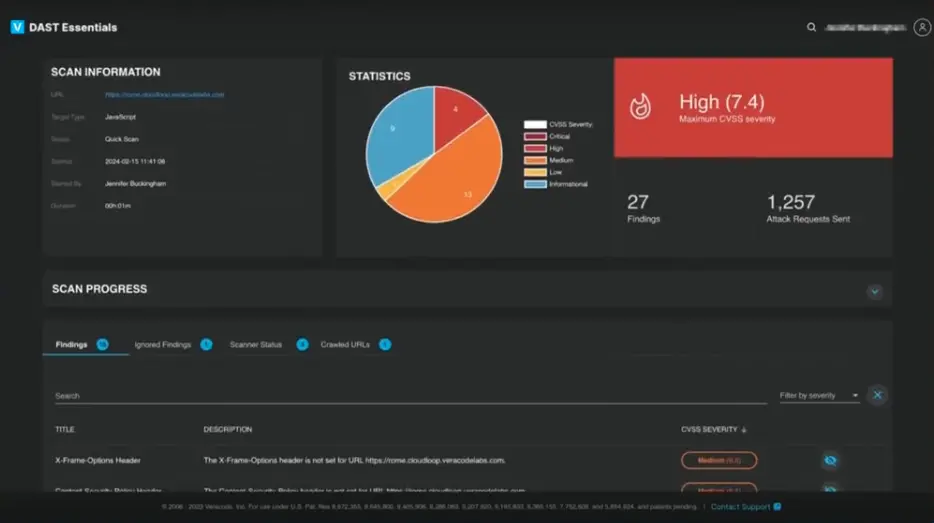
Veracode DAST scans live web applications and APIs for runtime vulnerabilities, with real time feedback and integration into DevOps pipelines. It emphasizes fast scanning, a low false positive rate, and remediation guidance for fixing critical issues quickly.
Features
Runtime scanning of web apps and APIs
Real time, actionable feedback for remediation
Low false positive rate scanning engine
Direct integration into automated
DevOps pipelines
Configurable authentication and crawl scripts for depth
Pricing
Entry estimates around $15,000 per year as per Under Defence(quote based).
G2 rating
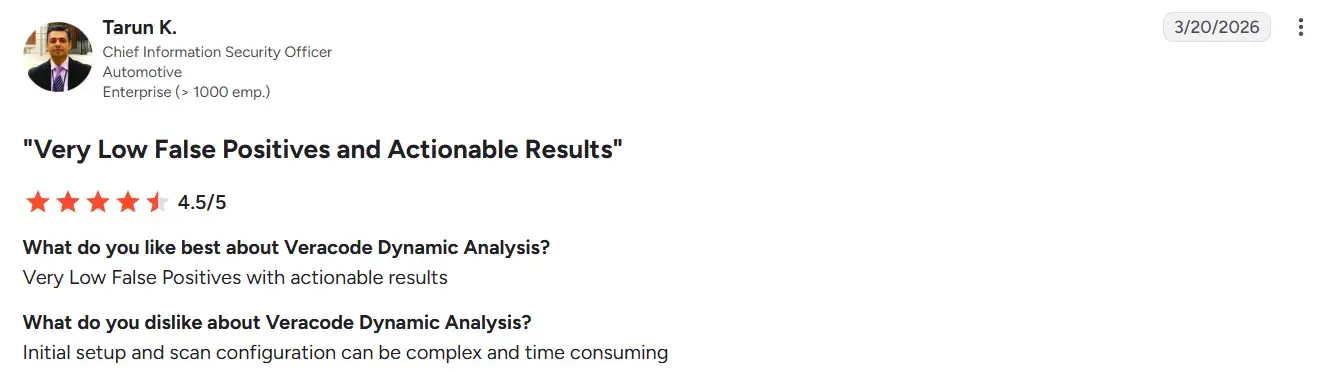
Veracode holds a 3.7 out of 5 rating on G2 for its overall AppSec platform, with reviewers praising comprehensive scanning and support while noting complex implementation and higher cost.
Why consider it
Best suited to enterprises with many applications, strong regulatory demands, and an existing Veracode investment.
Checkmarx DAST
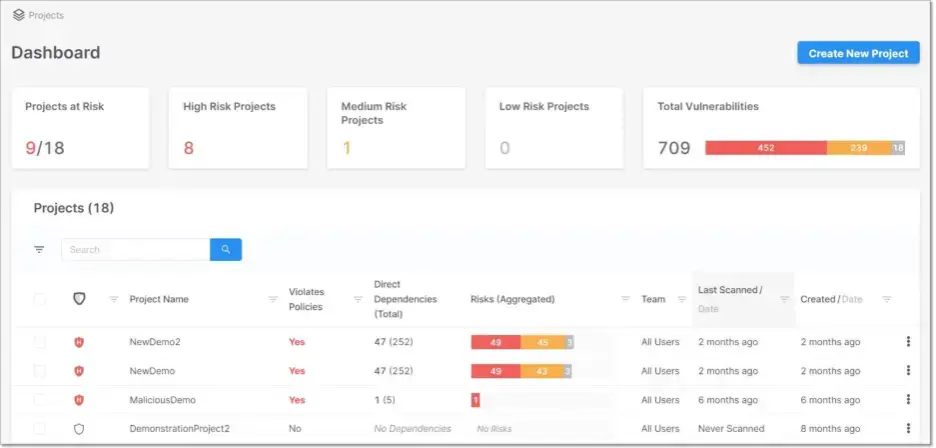
Checkmarx DAST is part of the Checkmarx One application security platform, supporting dynamic testing of live applications while correlating DAST results with SAST scans and integrating with CI/CD tools to help teams automate and prioritize remediation.
Features
Dynamic testing of live applications at runtime
Correlates DAST findings with SAST scan results
Built in integration with CI/CD and development workflows
Unified cloud native
AppSec platform covering multiple test types
Reduced false positives through contextual scan correlation
Pricing
Custom quote, with public minimums often cited around $30,000 per year.
G2 rating
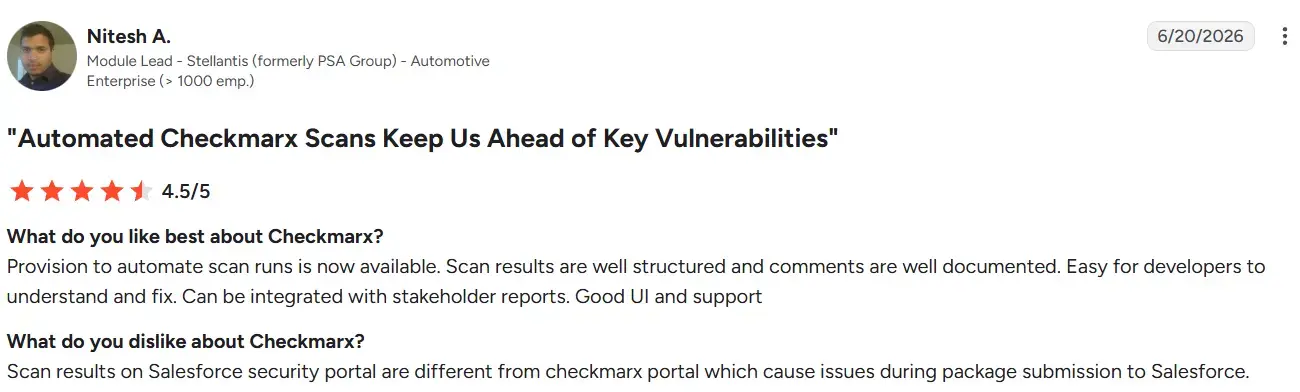
Checkmarx holds a 4.2 out of 5 rating on G2, with users praising its interface and vulnerability fix suggestions, while some reports support delays and occasional false positives.
Why consider it
A strong choice if you want a consolidated AppSec platform rather than standalone DAST, and have the budget for enterprise scale investment.
HCL AppScan
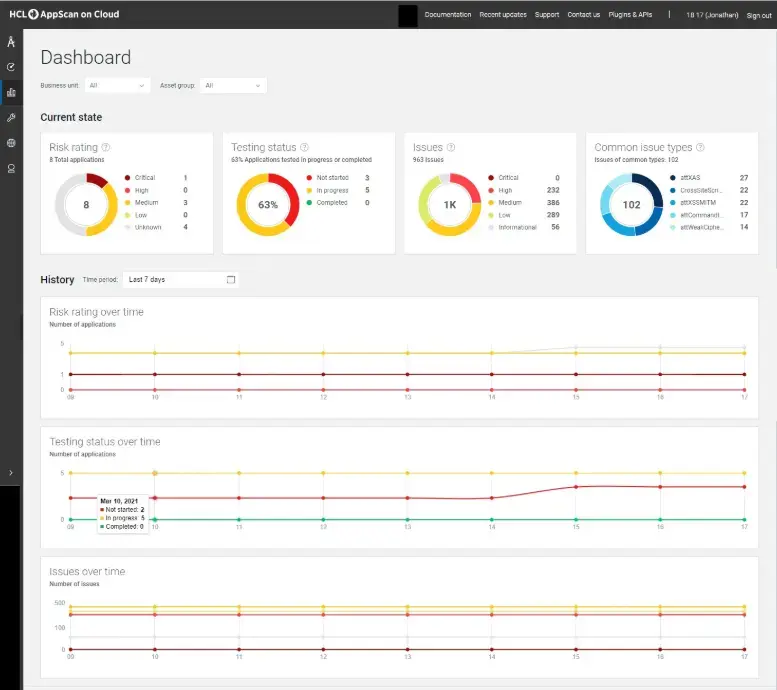
HCL AppScan is an application security testing suite offering DAST alongside other testing types for web, API, and mobile backends. It supports incremental scanning, a machine learning enhanced crawl engine, and is built for enterprise scale integration into DevSecOps workflows.
Features
Tests web apps, APIs, and mobile backends
Incremental scanning to optimize test coverage
Machine learning powered crawl and discovery engine
Enterprise scale deployment and integration
Risk management and compliance support included
Pricing
A pay per scan option is available for the cloud version, currently listed at $29.99 for a single scan (discounted from a $299 list price), with a 50 scan pack at $699. Subscription pricing is available on request.
G2 rating
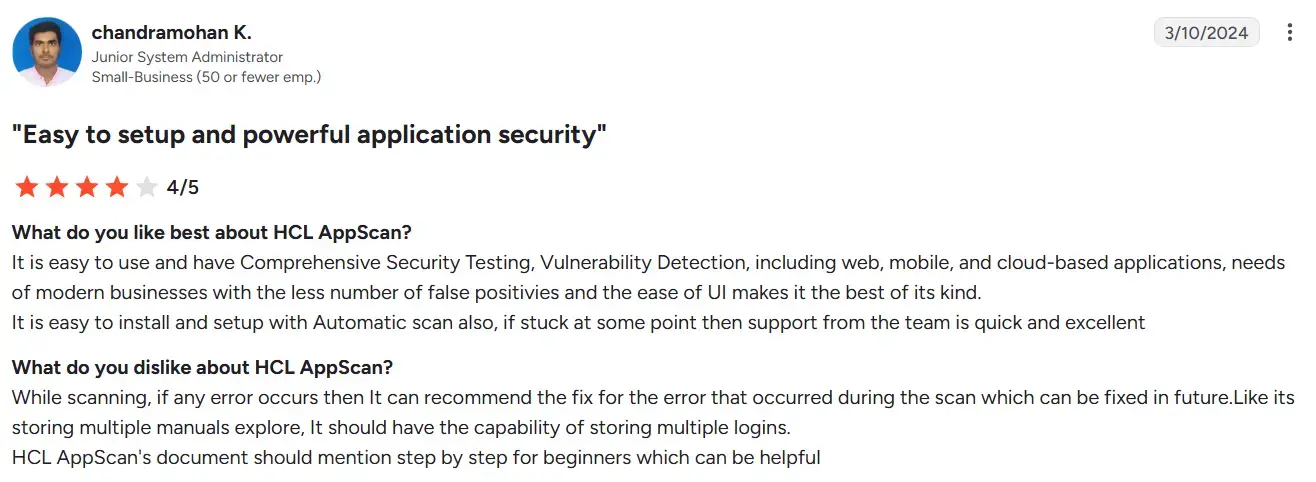
HCL AppScan holds a 4.1 out of 5 rating on G2, with reviewers appreciating accurate scan results, though some report a difficult installation process and thinner documentation than expected.
Why consider it
A flexible usage model that suits organizations running periodic scans or needing variable coverage without a large upfront cost.
Burp Suite
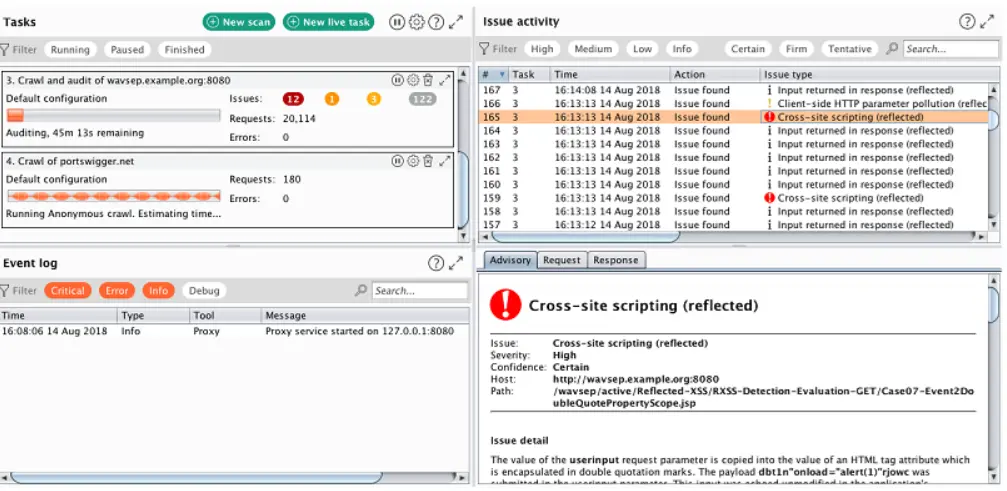
Burp Suite is a widely used web application security testing toolkit from PortSwigger, combining automated scanning with extensive manual testing capabilities, including an interception proxy, Intruder, Repeater, and extensions, for pentesters and AppSec teams working directly with vulnerabilities.
Features
Interception proxy for inspecting web traffic
Automated vulnerability scanner with manual control
Extensible through plugins and scripting via the BApp Store
Support for API and authentication testing CI/CD and enterprise automation integration (Enterprise edition)
Pricing
Free Community edition. Professional edition starts around $475 per user per year.
G2 rating
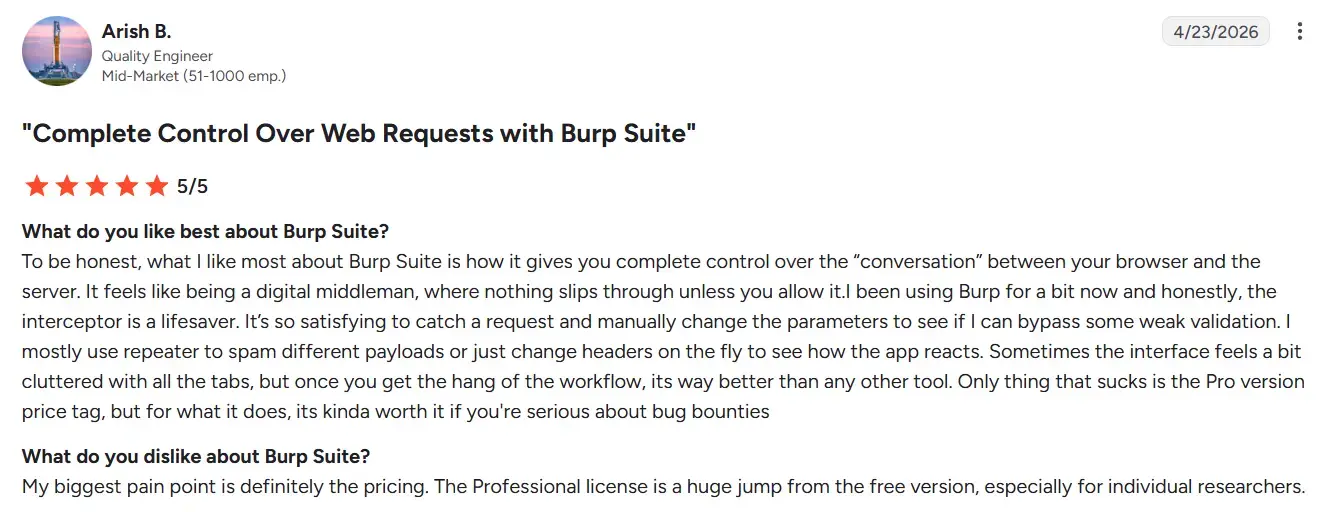
Burp Suite holds a 4.8 out of 5 rating on G2, the highest in this comparison, with users praising its depth for manual testing despite a genuinely steep learning curve.
Why consider it
Ideal for security teams with manual pentesting expertise, red teams, and organizations that value depth and control over pure automation.
Astra Security
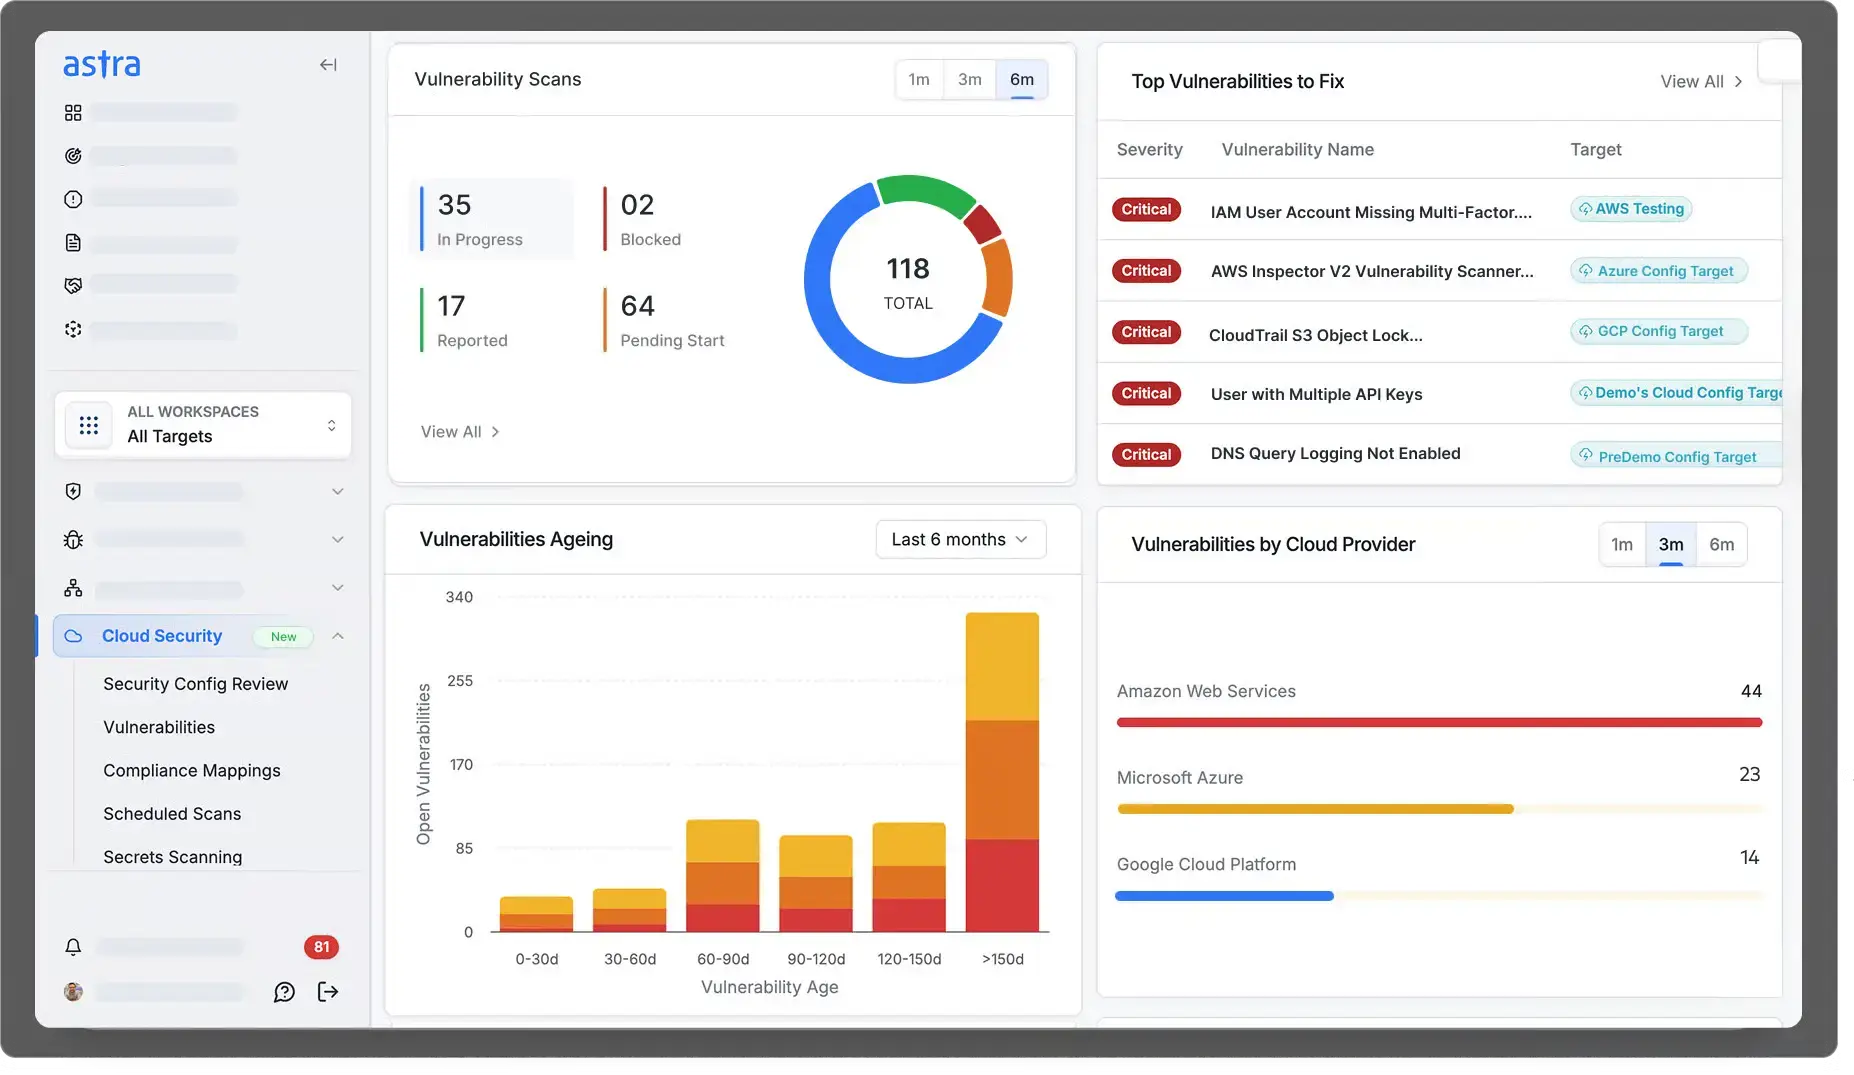
Astra Security is an online PTaaS and application security platform that emulates attacker behavior across more than 15,000 security tests, offering detailed, context aware reports. It combines automated scanning with expert reviewed findings, authenticated DAST scanning through a Chrome extension, and direct CI/CD integration. The platform also offers industry specific AI test cases, secret scanning, compliance reporting paired with manual pentests, and dedicated support through its Astranaut Bot.
Features
AI powered DAST with over 15,000 security tests and expert reviewed findings to minimize false positives
Authenticated scanning behind login pages through a Chrome extension Integrates with Slack, Jira, GitHub, GitLab, Vanta, CircleCI, Jenkins, and more
Helps identify vulnerabilities affecting compliance with PCI DSS, HIPAA, ISO 27001, and SOC 2
Continuous automated scanning with rules updated roughly every two weeks
Dedicated security expert support (OSCP and CEH certified)
Pricing
Starts at $1,999 per year, with custom pricing available through consultation.
G2 rating
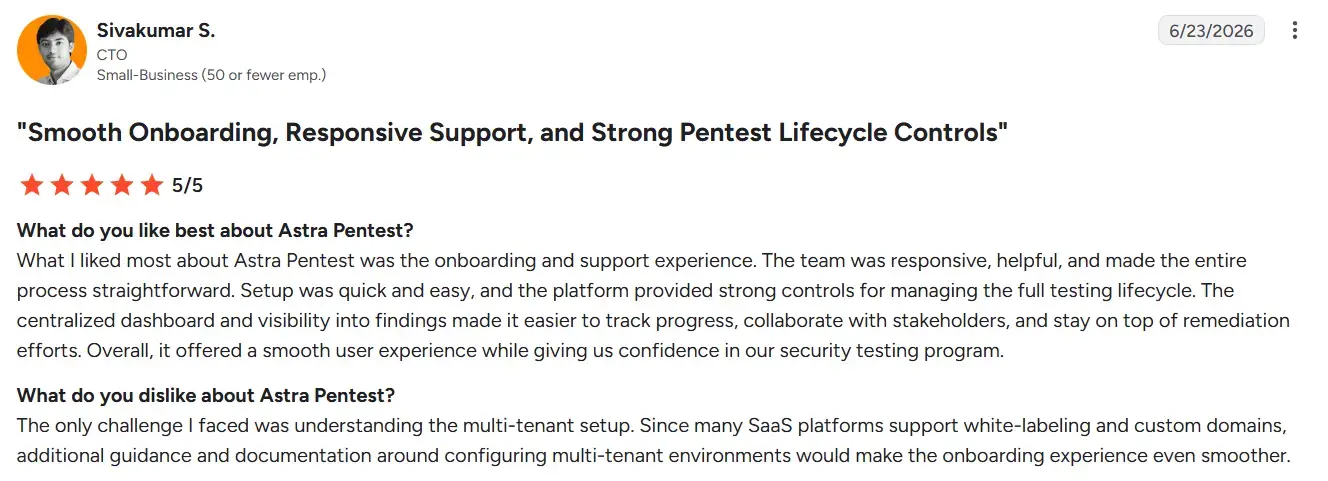
Astra Security holds a 4.75 out of 5 rating on G2, based on expert review scores, with users highlighting its compliance reporting, expert support, and low false positive rate.
Why consider it
A fit for businesses wanting expert backed vulnerability assessment and penetration testing, comprehensive compliance coverage, and automated security testing built into fast moving development workflows.
Black Duck DAST
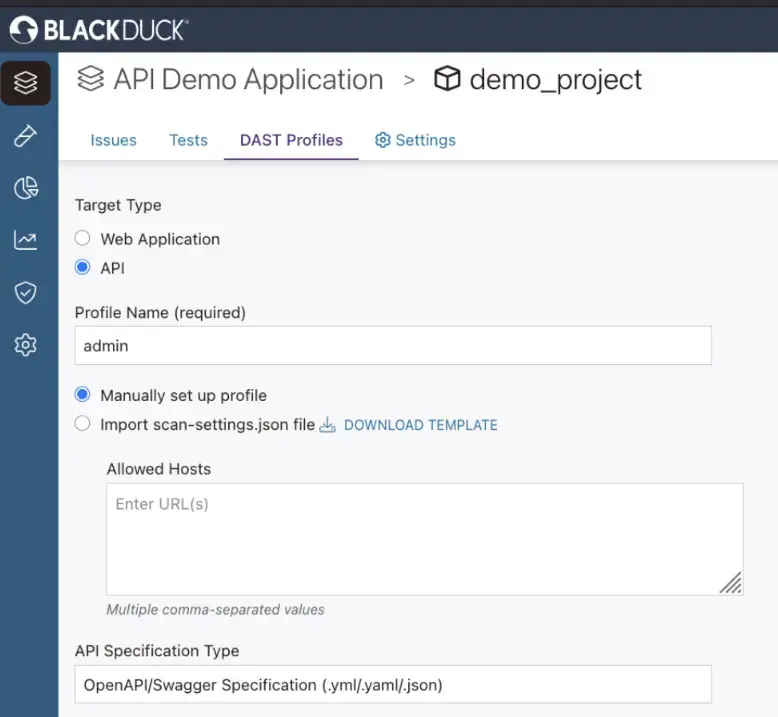
Black Duck DAST, also branded Black Duck Continuous Dynamic, is a dynamic application security testing solution offering continuous, authenticated scanning of live web applications, production safe form testing, business logic analysis, and a low false positive rate through a mix of automation and expert review.
Features
Continuous, concurrent DAST assessments in production
Authenticated scanning, including complex login flows Business logic analysis by security experts
Production safe form testing that avoids disruption
Reporting built for business risk management
Strong integration with SCA and SBOM workflows
Pricing
Quote based. Specific DAST pricing is not widely published.
G2 rating
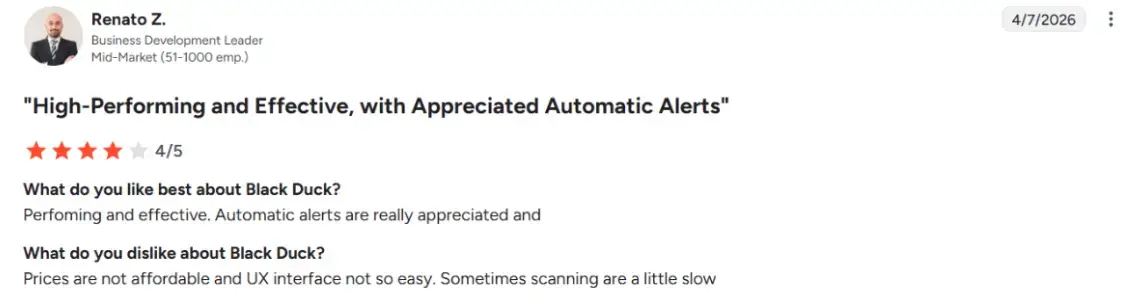
Black Duck DAST holds a 4 out of 5 rating on G2, with reviewers focused more on its integration with existing SCA workflows than on detailed feedback about the DAST module itself.
Why consider it
A good choice if you already use Black Duck SCA and want to extend into runtime DAST without adding a separate vendor.
Snyk DAST
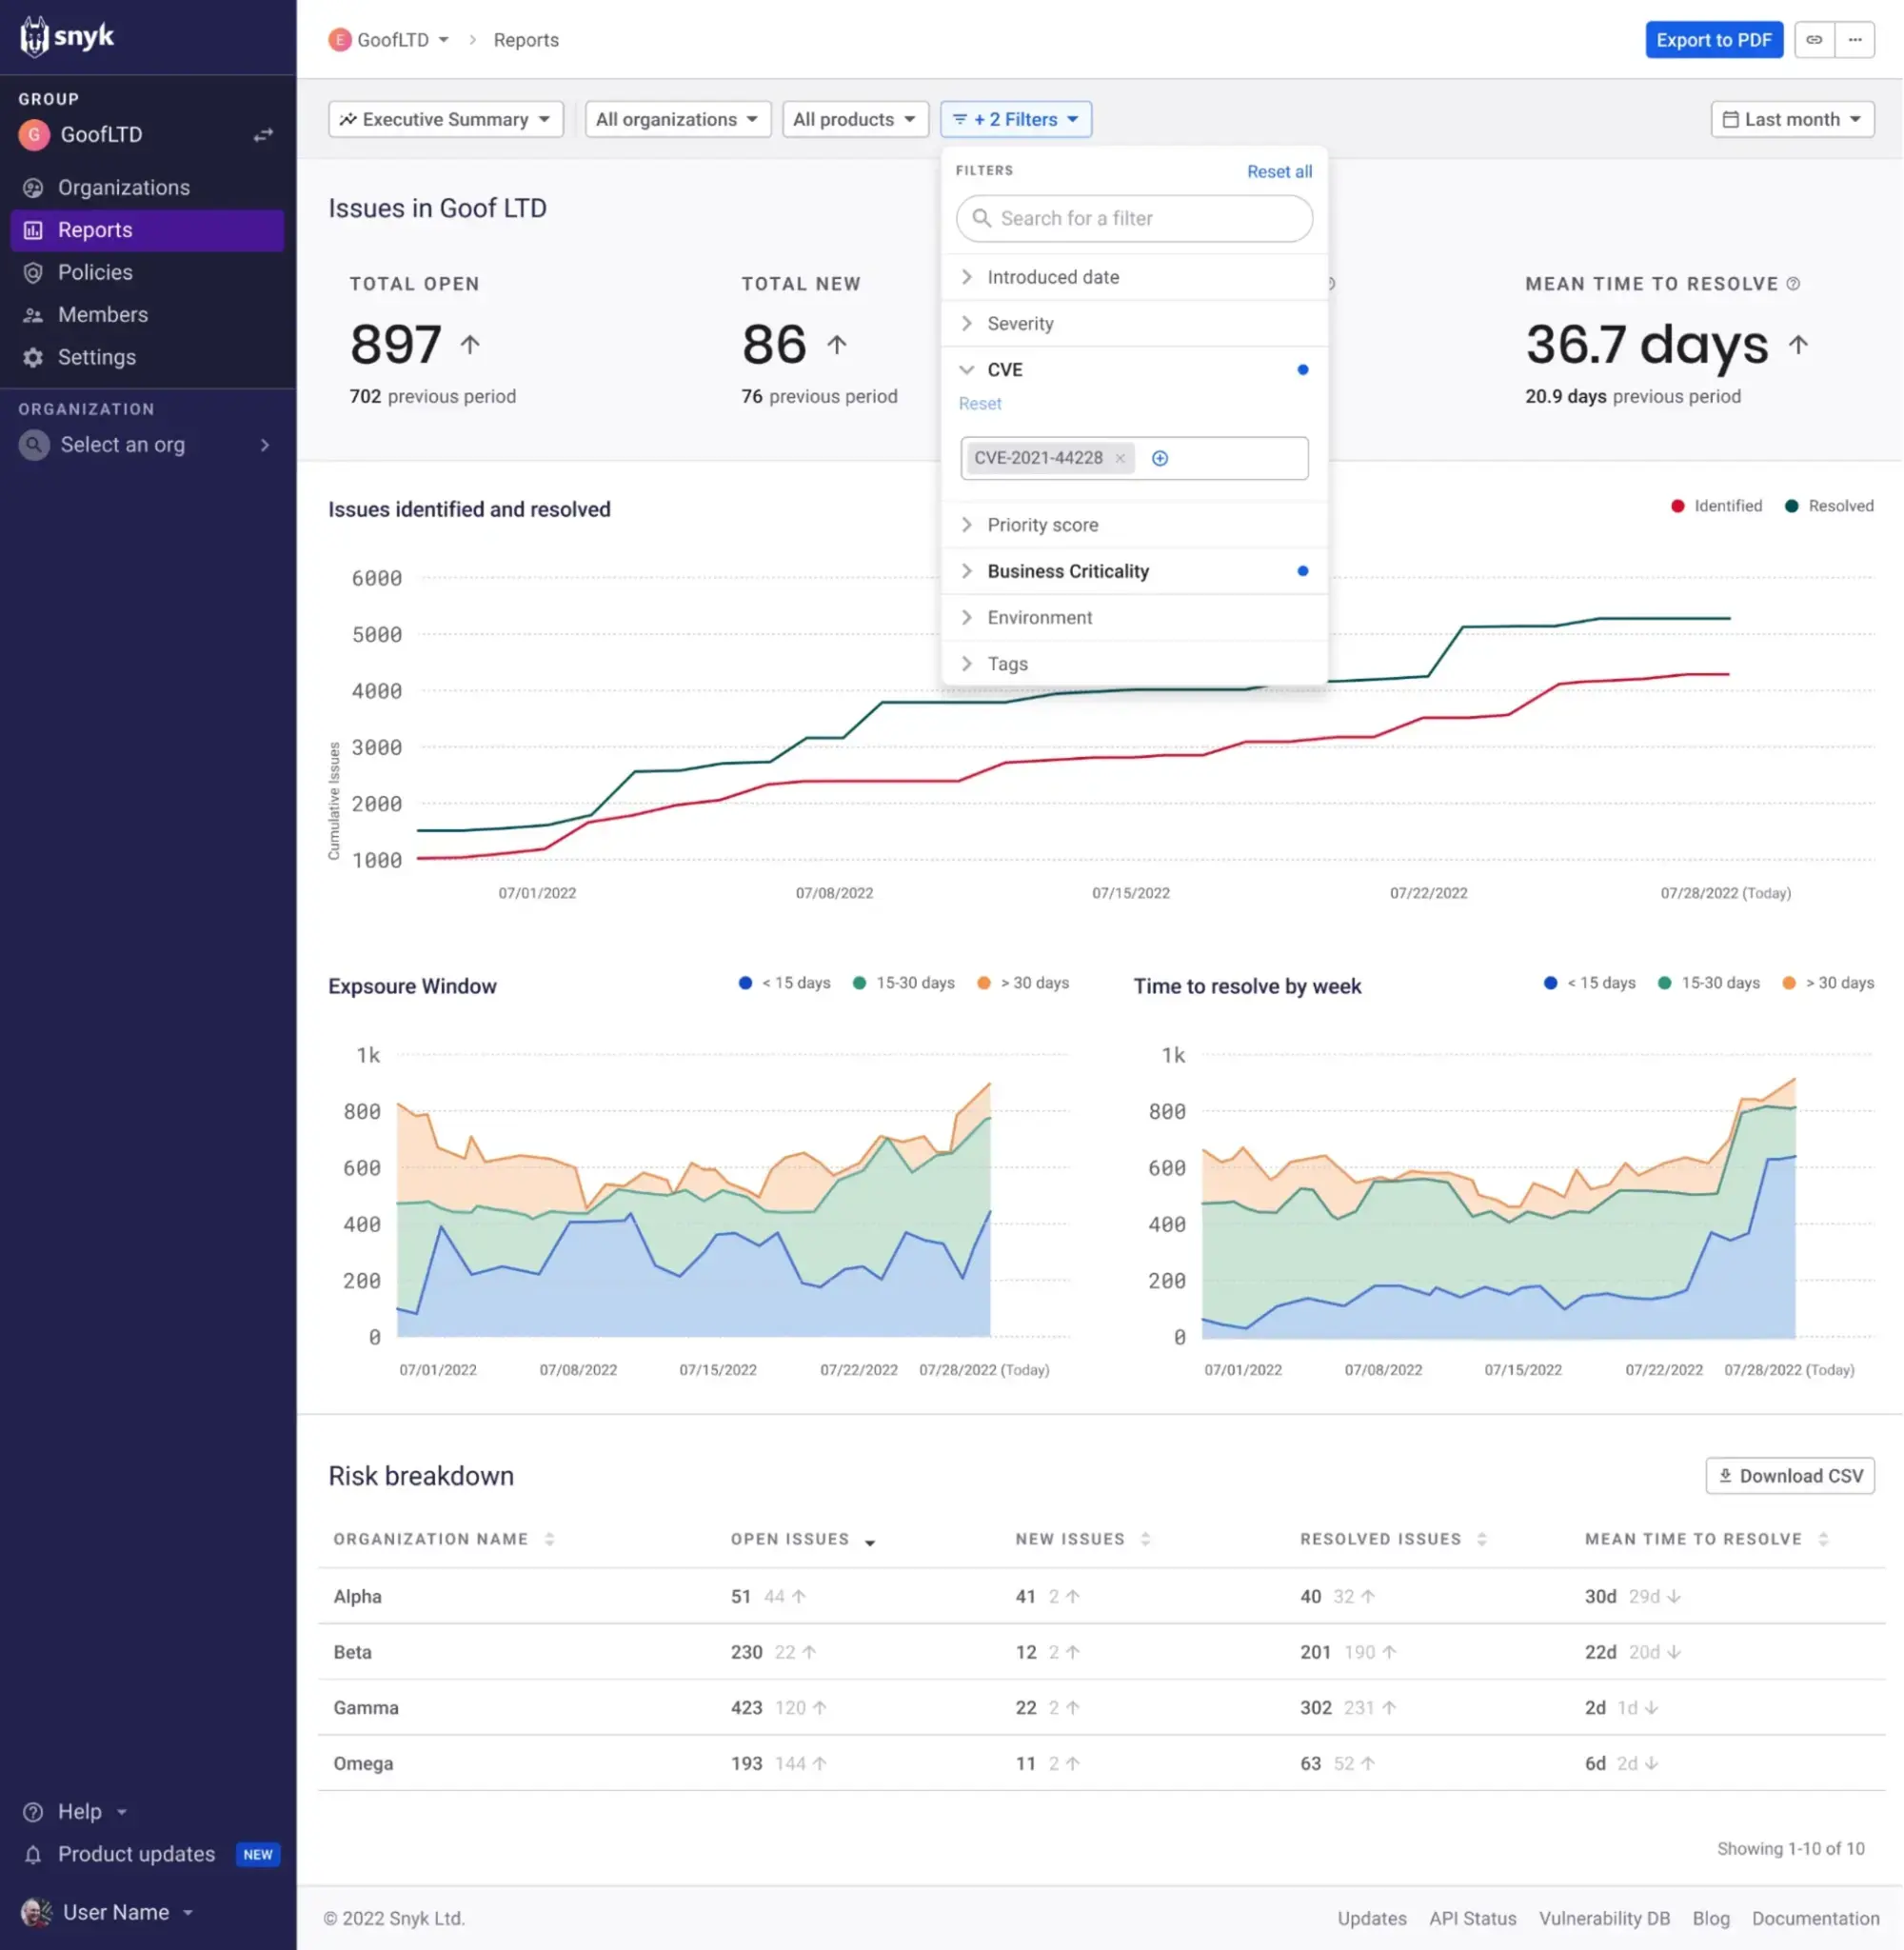
Snyk DAST, branded as Snyk API & Web, delivers dynamic testing for web apps and APIs, with AI driven API discovery, headless browser crawling for SPAs, CI/CD integration, and a low reported false positive rate. It integrates closely with developer workflows and is built around DevSecOps adoption.
Features
AI powered API and web application discovery
Headless browser crawler for JavaScript and SPAs
Direct CI/CD and developer tool integrations
Low false positive rate Compliance reporting (PCI, HIPAA, ISO, GDPR)
Pricing
The Team tier starts around $25 per developer per month, with a 5 developer minimum. DAST specific pricing may vary. [Confirm current DAST specific pricing before publishing, since it may differ from Snyk’s general Team plan figure.]
G2 rating

Snyk holds a 4.5 out of 5 rating on G2, with users praising its developer focused workflow and CI/CD integration, though most reviews reflect the broader platform rather than DAST specifically.
Why consider it
A strong fit for developer centric teams or startups that want to build web and API security into their release pipeline at a lower entry cost.
Key factors to consider when choosing a Fortify DAST alternative
Before you sign anything, these are the questions actually worth asking, either yourself or the vendor directly.
| Ask yourself | Why it matters |
|---|---|
| Does it actually test what we're building? | A tool that only covers traditional web pages will miss REST and GraphQL APIs, SPAs, microservices, and business logic flaws, exactly the surfaces most likely to ship a real vulnerability in 2026. |
| Will this fit into how the team already works? | A scanner bolted onto the side of your pipeline gets skipped under deadline pressure. Direct integration with GitHub, Jenkins, GitLab, or Azure DevOps is what decides whether testing actually happens every release or just some of them. |
| How much of what it finds is worth our time? | A tool that buries three real vulnerabilities in two hundred false positives trains your team to ignore its output entirely. Accuracy and clear remediation guidance beat sheer volume of findings every time. |
| Can it get past our login page? | Most of the interesting risk in a modern application lives behind authentication. If a tool can't handle SSO, 2FA, or OAuth, it's only ever testing the parts of your app an anonymous user can see. |
| Does this match our actual bandwidth? | Teams without dedicated AppSec staff need automation that runs itself. Teams with red team testers get more value from a tool built for manual depth. Buying the wrong one for your team's reality wastes both money and time. |
| Will these reports survive an audit? | Findings that don't map to OWASP Top 10, PCI DSS, or ISO 27001 mean someone on your team manually translating results before every compliance review, every single time. |
| What does this actually cost at our real scale? | Entry pricing rarely tells the whole story. Per app, per asset, and per user models can all scale very differently once your portfolio grows, so run the math at your actual size, not the vendor's example. |
Final thoughts
Choosing the right Fortify DAST alternative depends heavily on your organization’s maturity, tech stack, budget, and workflow style. Enterprise grade platforms like Veracode, Checkmarx, and Tenable offer broad capabilities, but come with higher cost and complexity.
If your priority is developer friendly automation, strong API and CI/CD coverage, and cost effective pricing, Beagle Security is worth evaluating for 2026. Start a 14 day advanced free trialor explore the interactive demo to see how it fits your workflow.
FAQs
What is the best alternative to Fortify DAST?
It depends on your priorities. Beagle Security fits teams wanting AI driven, developer friendly testing at lower cost, Veracode or Checkmarx fit large enterprises needing a full compliance focused AppSec suite, and ZAP or Burp Suite fit teams with security engineering capacity to manage more hands on tools.
Is there a free alternative to Fortify DAST?
Burp Suite offers a free Community edition for manual testing. Most other alternatives here, including Beagle Security, Rapid7, and HCL AppScan, offer a free trial rather than a permanent free tier.
How much does OpenText Fortify DAST cost compared to its alternatives?
Fortify’s pricing isn’t publicly listed. Among alternatives, entry pricing ranges from Beagle Security at $119 per month to enterprise platforms like Veracode and Checkmarx, which typically run into the tens of thousands per year on a custom quote.