Top Stackhawk alternatives
Modern AppSec teams pick tools by what they test (web, API, GraphQL, business-logic), how they fit into CI/CD, accuracy, and cost. As organizations adopt continuous delivery, ensuring security throughout the software development lifecycle (SDLC) is critical.
StackHawk has long been recognized as a go-to solution for DevSecOps teams looking to automate dynamic application security testing (DAST). However, as the security market expands, several tools now rival or even outperform StackHawk. Depending on your organization’s size, budget, and security maturity, a different DAST or API security solution might offer a better fit.
Below are ten prominent StackHawk alternatives in 2026 that you might want to consider.
| Tool | Starting price | Strengths | Best for: |
|---|---|---|---|
| Beagle Security | Free tier exists, paid plan starting from $119/month | Cost effective API & GraphQL coverage, CI/CD + developer friendly remediation | Small - mid SaaS teams wanting pipeline native automated pentesting at low costs |
| Escape DAST | Quote based / enterprise | Business logic testing (BOLA/IDOR), API & SPA focus, modern stack support | API/logic heavy apps, mid to large organizations needing business logic detection |
| Burp Suite | $0 (Community), $499/user/yr (Pro). Enterprise quotes available. | Deep manual & interactive testing tools, extensible plugin ecosystem | Pentesters and security that require interactive / manual testing depth |
| Invicti | Quote based; enterprise entry often high (per FQDN licensing) | Enterprise DAST + IAST, high accuracy, large scale scanning | Large organizations scanning many apps /APIs that need enterprise workflows |
| APIsec | Free tier exists, paid plans starting from $690/month | API first scanning, AI driven attack simulation, OWASP API Top 10 focus | API first products, teams needing continuous API security testing |
| Qualys WAS | $1,995/yr for 25 apps (public reference; scales up). | Cloud WAS + asset integration, compliance & low false positives at scale. | Enterprises with many web apps and strong compliance requirements. |
| Rapid7 InsightAppSec | Starting at $175/month/app | Cloud DAST integrated into the Rapid7 platform, good automation & analytics. | Teams already in Rapid7 eco or needing integrated DevSecOps analytics |
| Acunetix | Quote based, public starter examples, $7,000/year (marketplace references) | Fast scanning, good mid-market balance, solid reporting and API support. | Mid-sized companies needing reliable automated web/API scans without enterprise overhead. |
| OWASP ZAP | Free (open source) | Free, customizable, strong community & CI integrations | Budget-constrained teams, security-savvy devs wanting automation + customization. |
| Tenable (Web App Scanning) | Starts at $7,434/yr for 5 FQDNs | Unified exposure & app scanning, strong enterprise reporting & dashboards. | Large orgs wanting asset + app exposure visibility in one vendor. |
1) Beagle Security
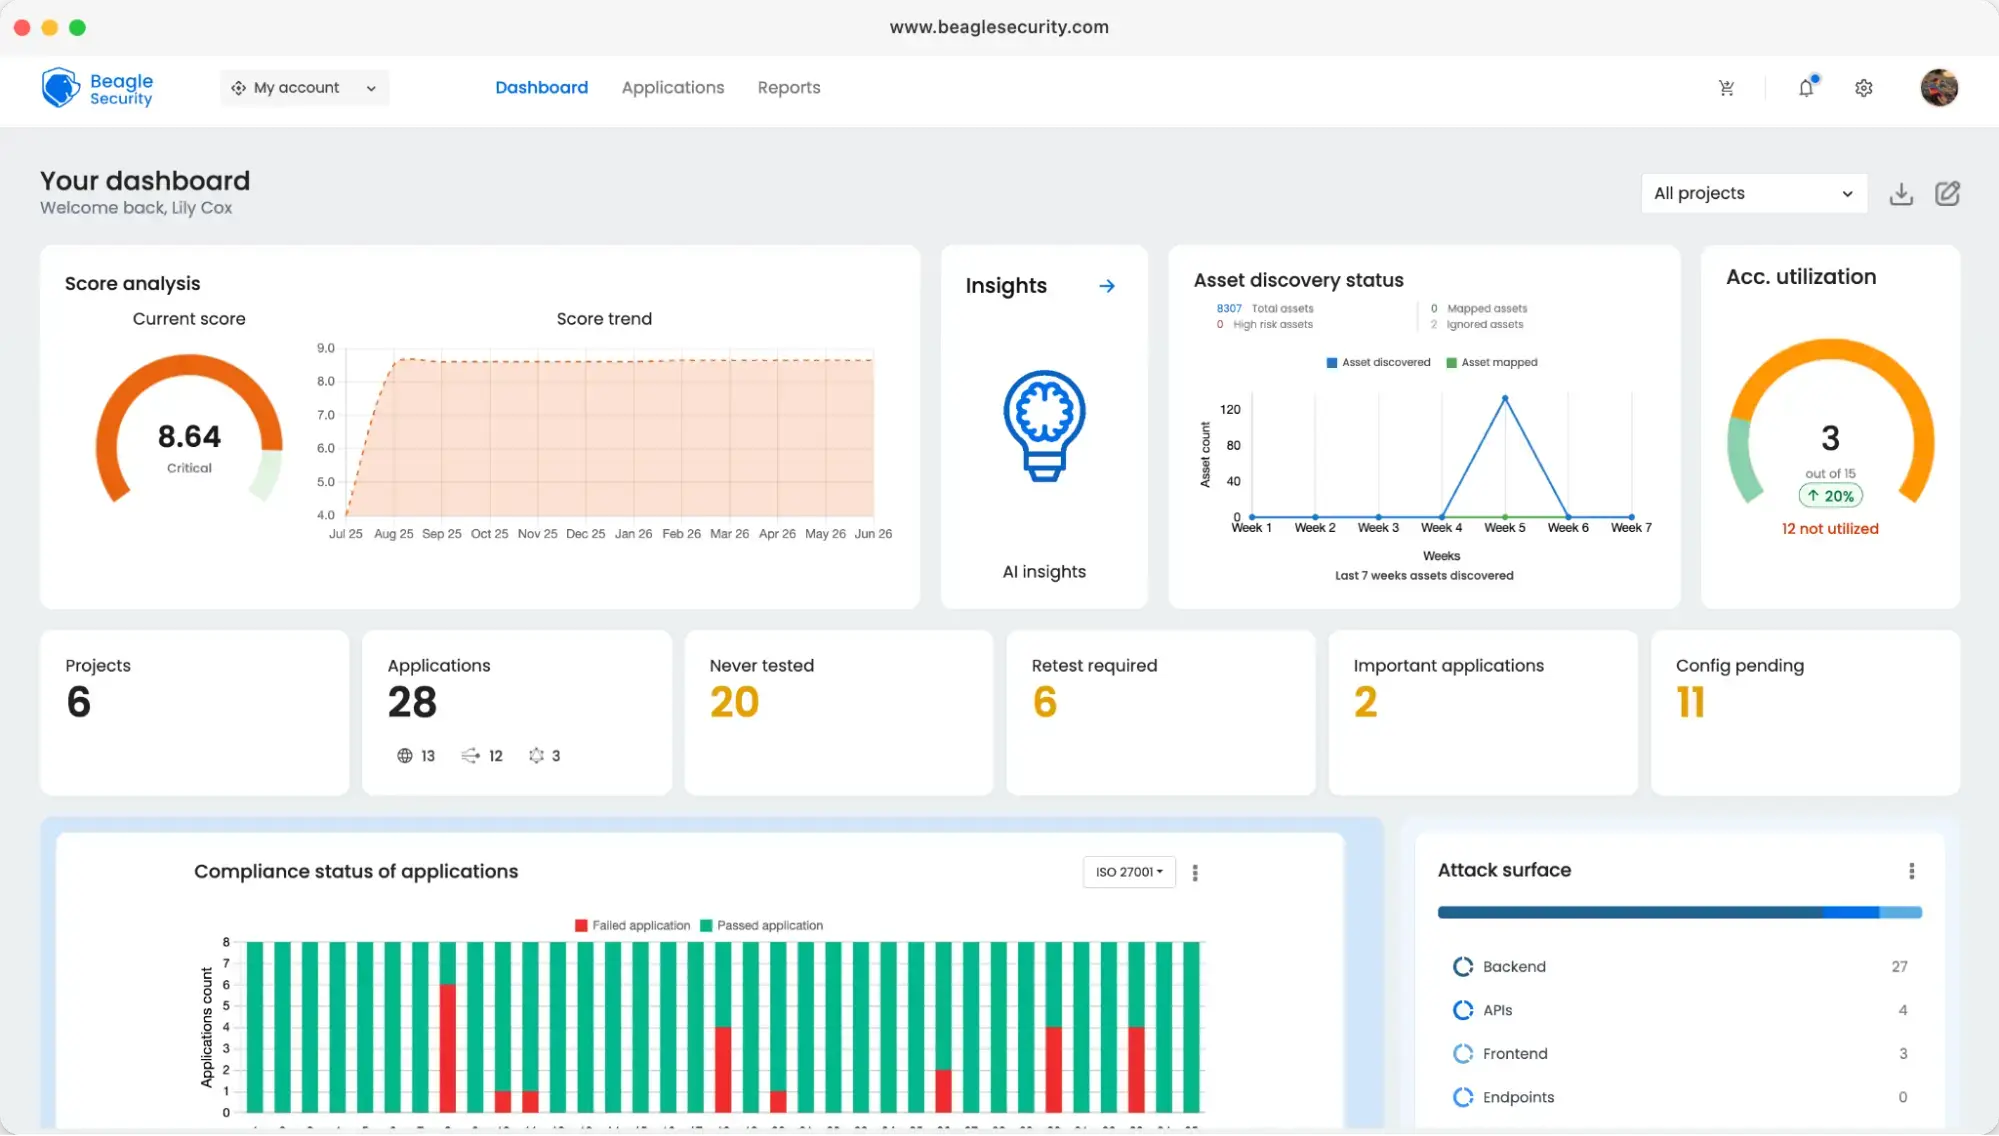
Beagle Security is a next-generation agentic AI platform built with a developer-first mindset. It leverages AI-driven attack simulations to mimic real-world hacker behavior, uncovering vulnerabilities that traditional scanners often miss.
Key features
Automated penetration-testing for web apps, APIs & GraphQL.
Covers 3,000+ test cases.
Integrations with CI/CD pipelines.
Developer-friendly remediation insights.
Compliance reports (GDPR, HIPAA, PCI DSS) for web/API security.
Pricing
Unlike tools that charge per user or scan limit, Beagle Security offers transparent usage-based pricing, starting at just $119/month, making it a cost-effective solution for both startups and enterprises.
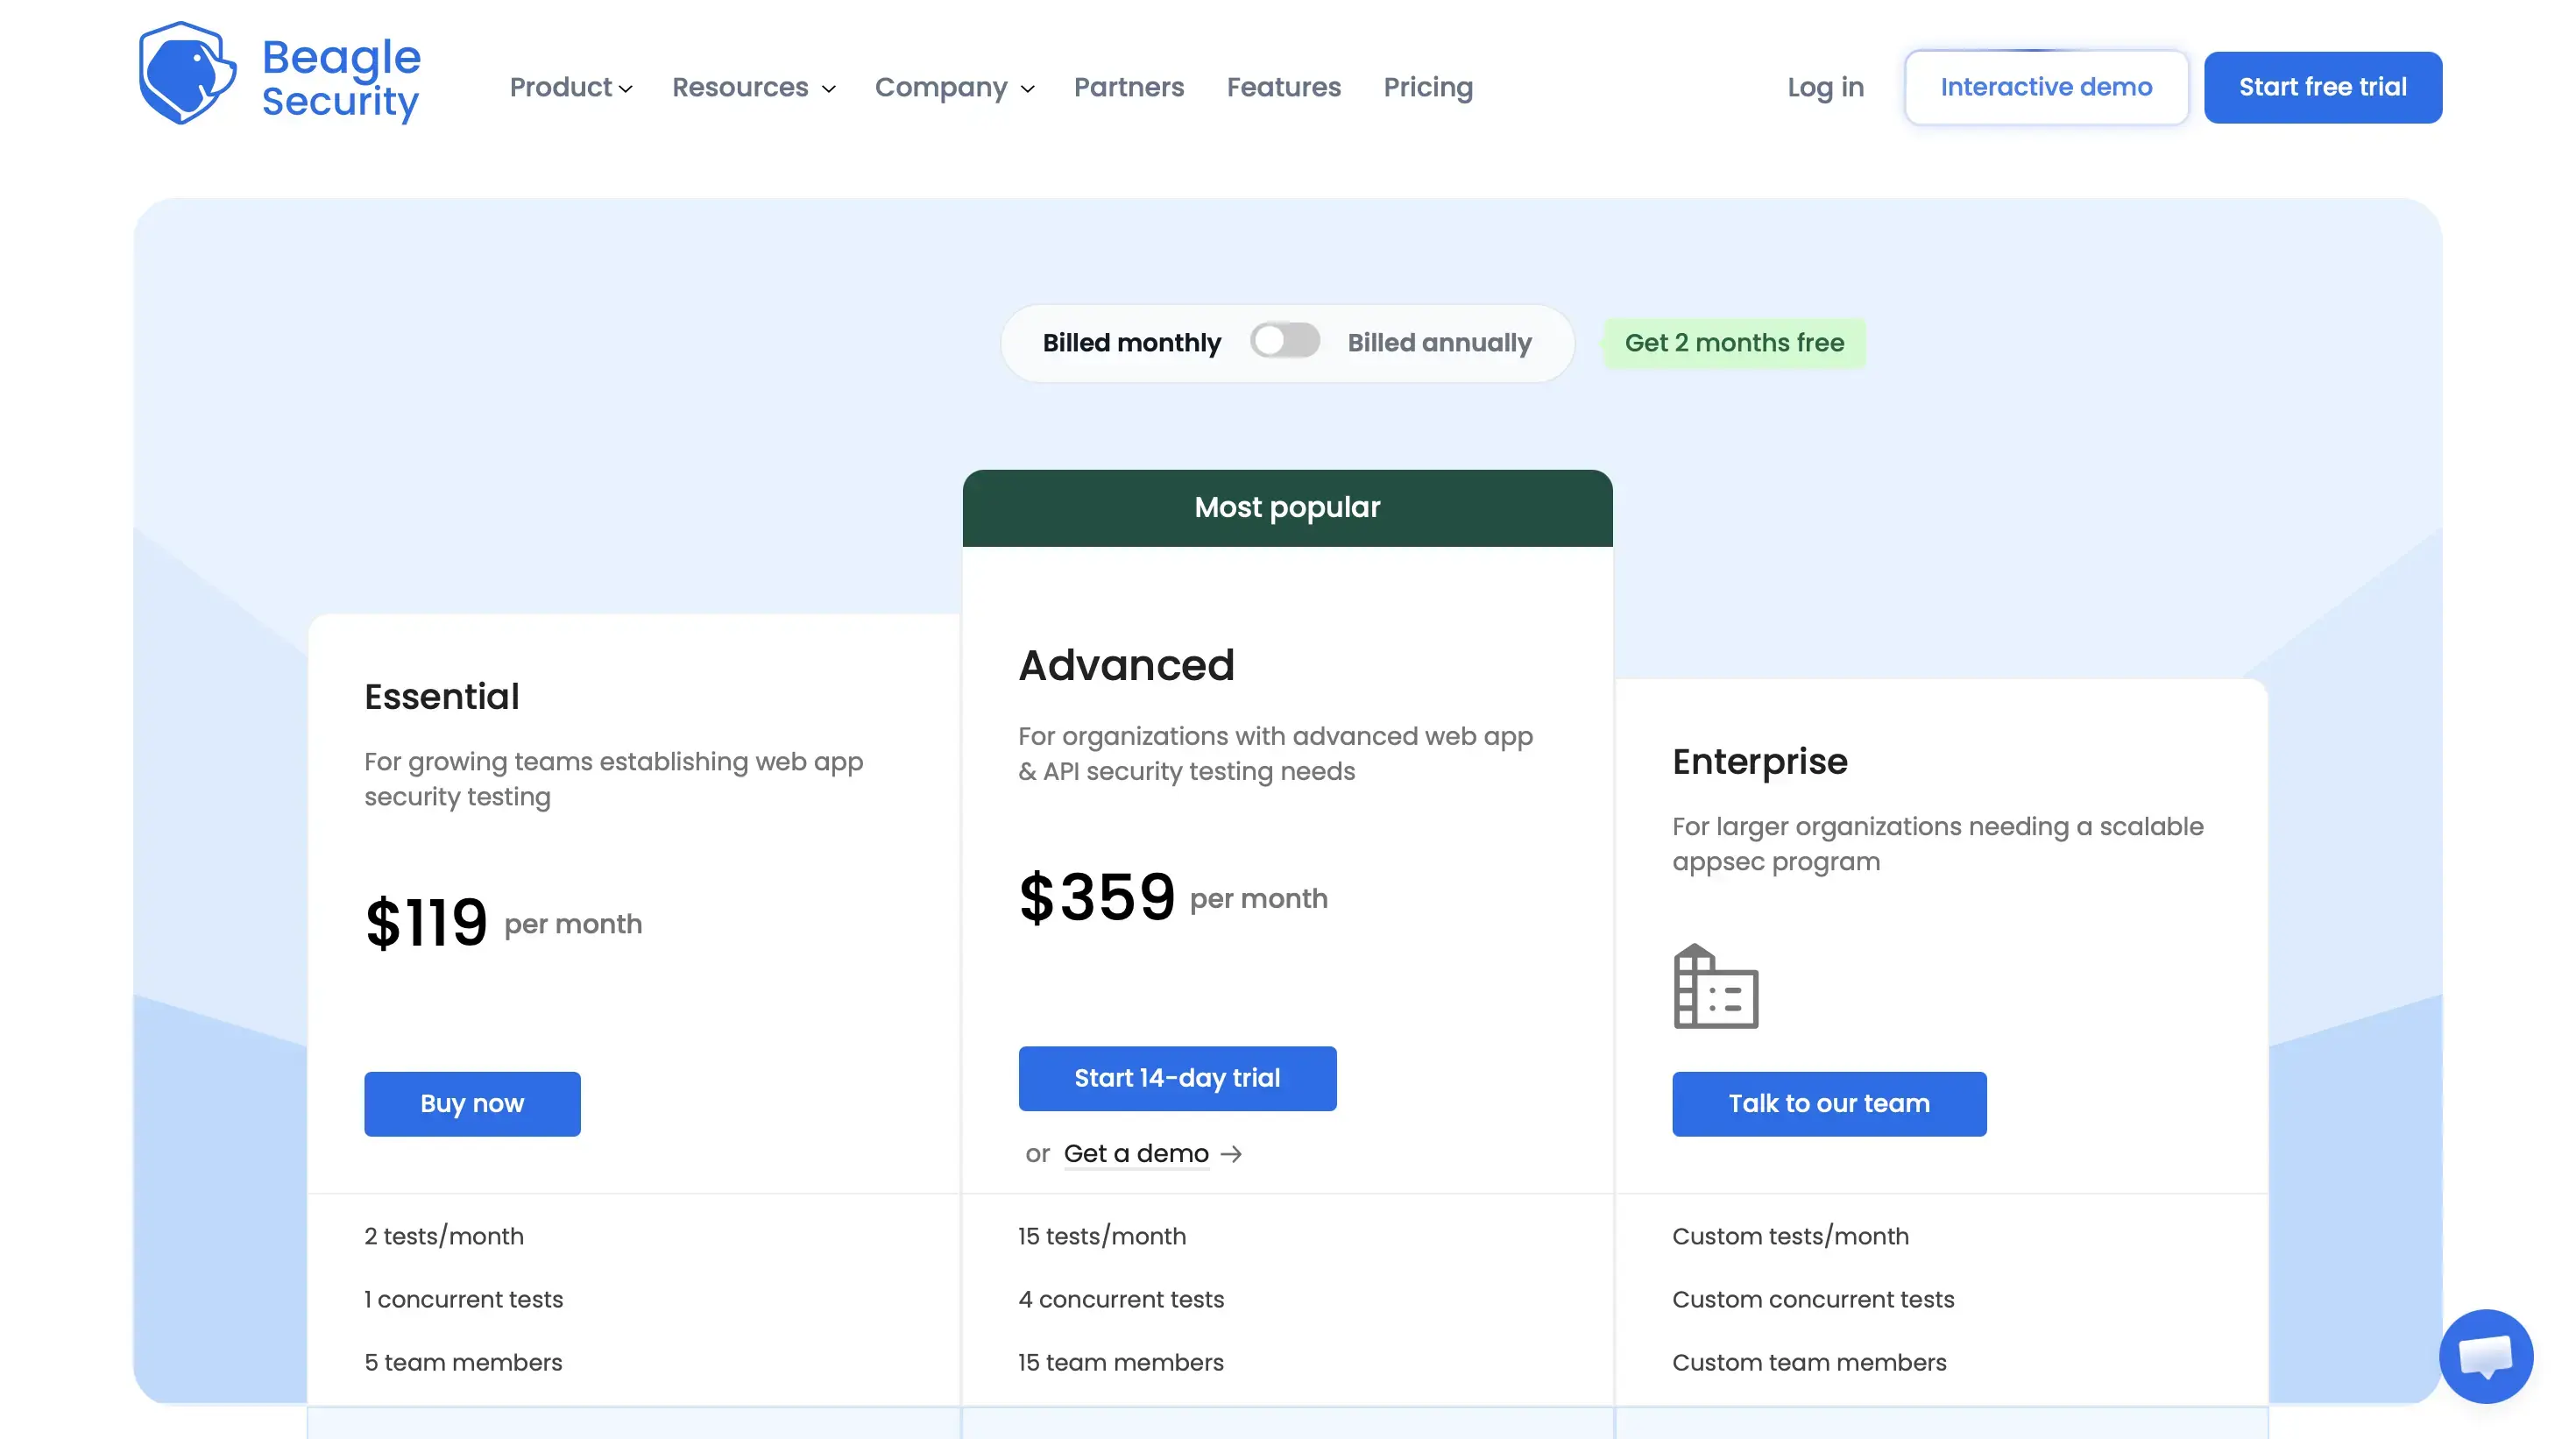
Essential : $119/month for 2 tests/month.
Advanced: $359/month for 15 tests/month.
Enterprise : Custom pricing.
Free tier available with a 14 day trial.
Reviews & ratings
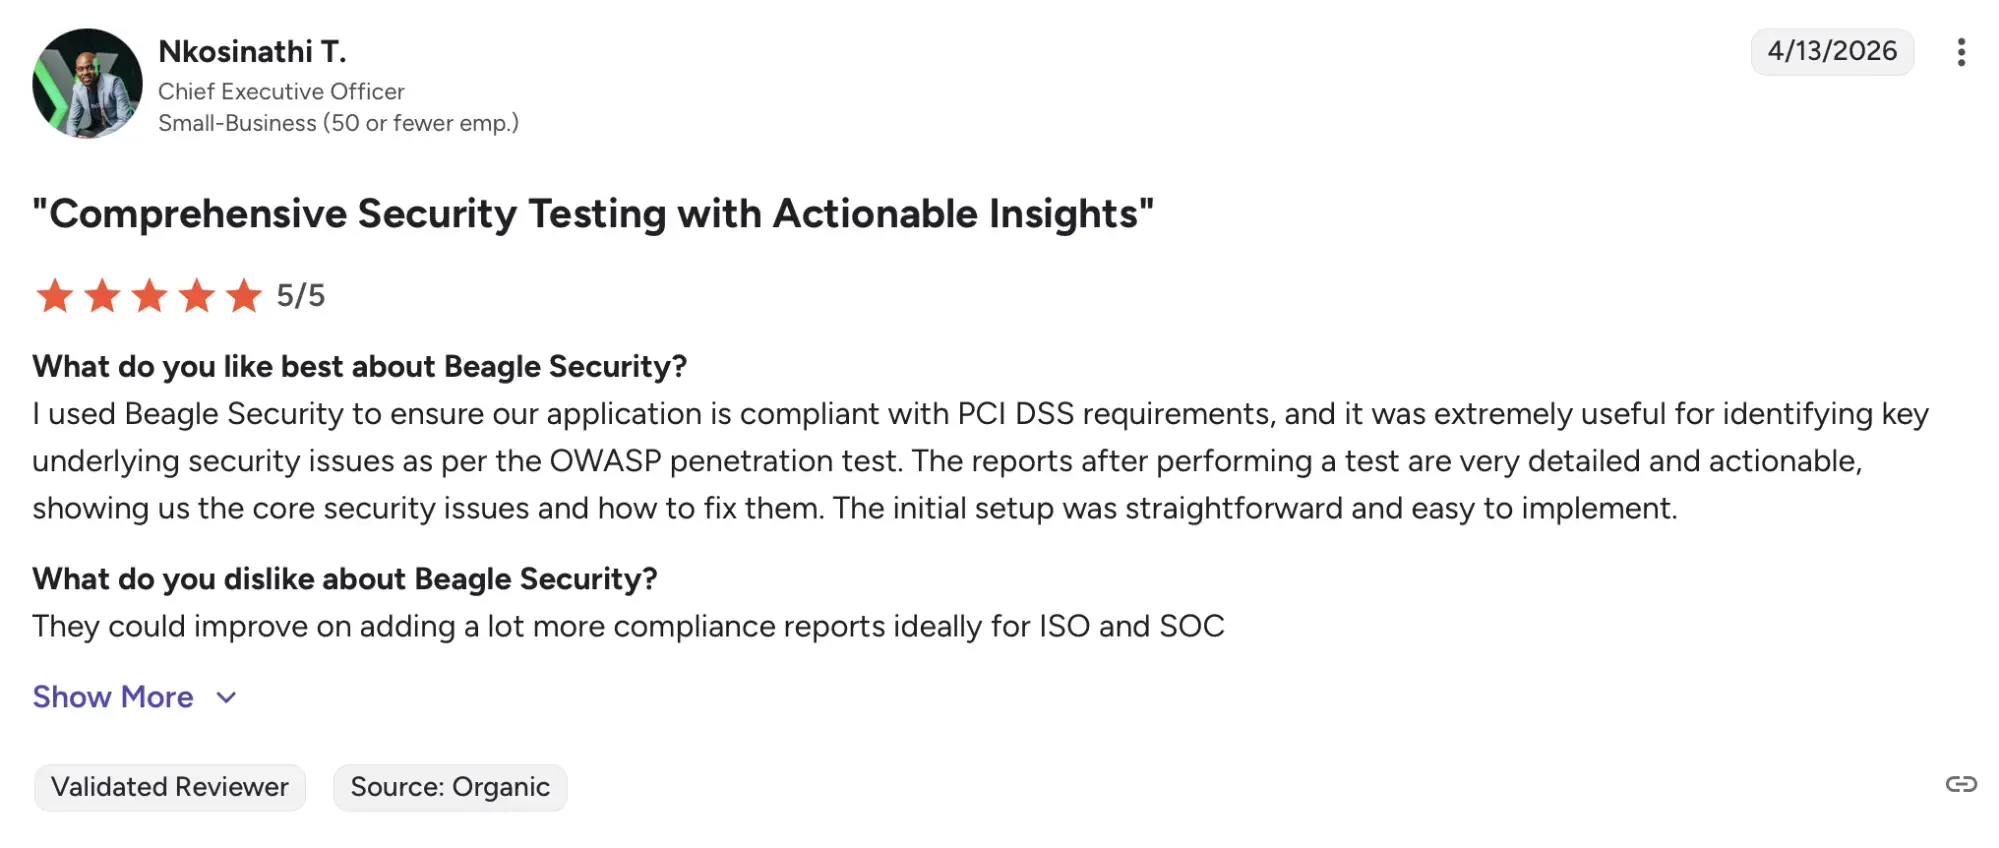
Beagle Security has a total rating of 4.7/5 based on 88 reviews.
Why consider it?
Beagle security is a great option for small-to-mid teams seeking developer-centric automation and lower cost compared to some heavy-enterprise tools.
2) Escape DAST
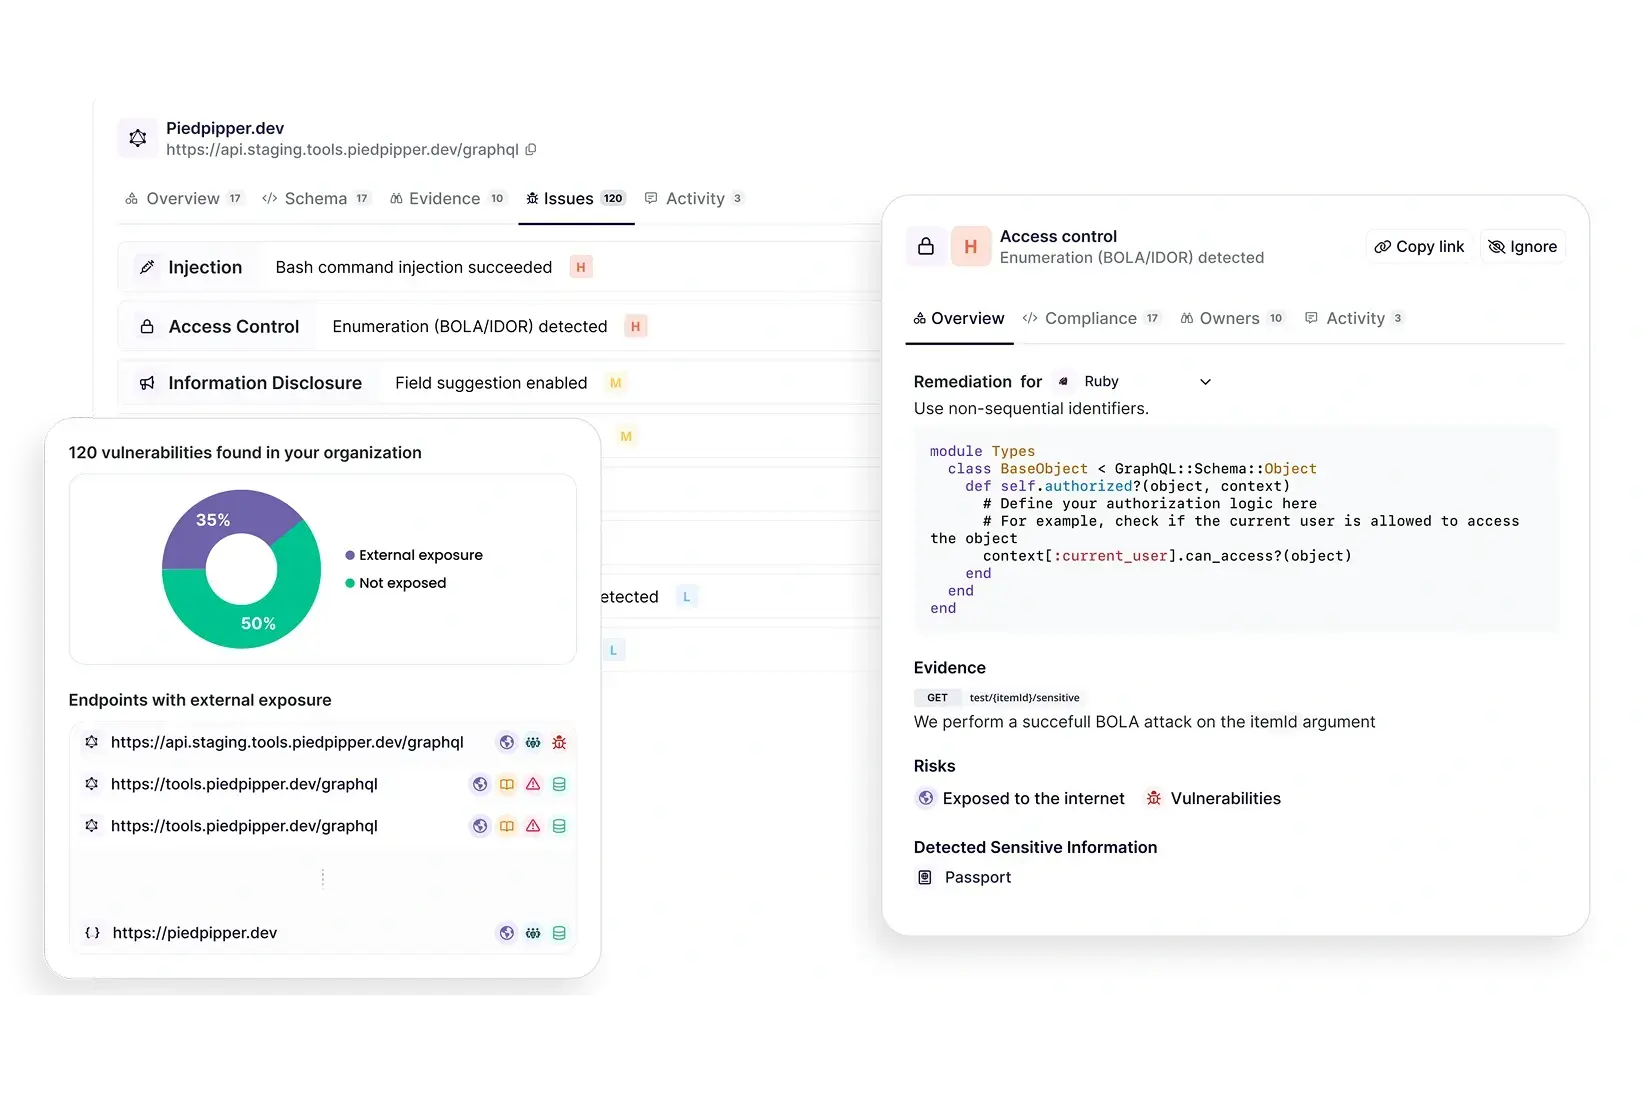
Key features
Designed for modern apps SPAs, APIs (REST, GraphQL) and microservices environments.
Business logic security testing engine.
Agentless API discovery.
Developer-centric reporting.
140+ attack scenarios including BOLAs, IDORs, and access control.
CI/CD friendly.
Pricing
Specific public pricing not widely published. Adoption is likely targeted at mid-to-large teams who value API/logic-aware testing.
Reviews & ratings
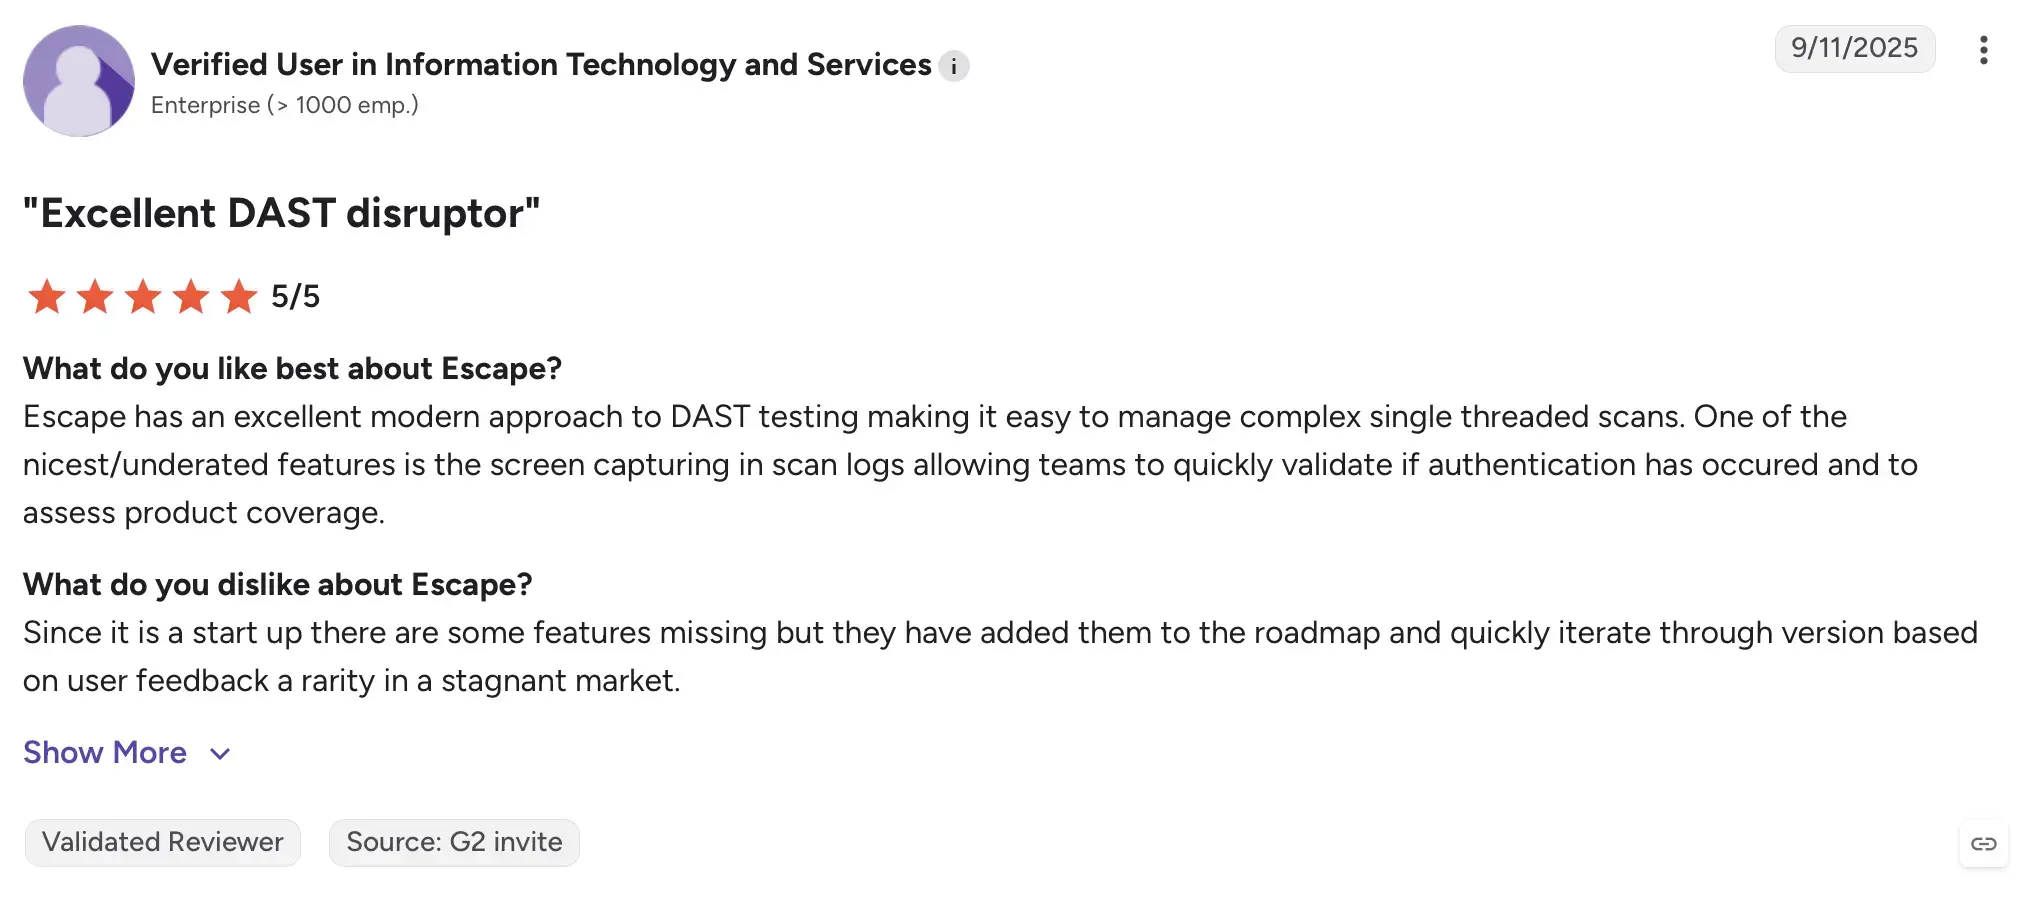
Escape has a G2 rating of 4.9/5 based on 10 reviews.
Why consider it?
If your stack is heavy on APIs and business logic, Escape offers a modern DAST alternative built for those challenges.
3) Burp Suite
Burp Suite remains one of the most trusted tools among professional penetration testers and ethical hackers. Its Professional Edition provides a comprehensive toolkit for manual and automated web application security testing.
Burp’s strength lies in its flexibility and extensibility. Testers can build custom workflows, integrate plugins from the BApp Store, and perform advanced manual testing with deep control.
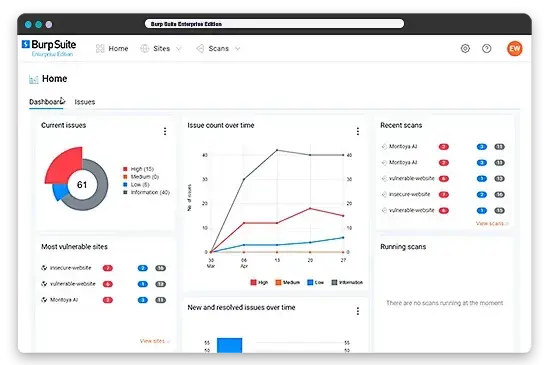
Key features
Widely used by penetration testers for both manual and automated scanning intercepting, fuzzing, brute-forcing, scanning behind login.
Strong manual tooling and plugin ecosystem.
Low false-positive scanner.
JavaScript SPA crawling.
Professional reporting.
Authentication macro support.
Pricing
Community Edition : Free (limited features).
Professional : $499/year per user.
Enterprise: Custom pricing.
Reviews & ratings

Burp Suite has a G2 rating of 4.8/5, based on 129 reviews.
Why consider it?
Burp Suite is ideal for security teams with manual pen-testing expertise or needing depth in interactive testing.
4) Invicti
Invicti is a DAST solution built for automation and large-scale vulnerability detection across complex web environments. Its scanning engine is known for reliability and integrates seamlessly with popular CI/CD tools, making it a good fit for teams with established AppSec workflows.

Key features
Automated DAST + IAST, web apps + APIs.
High accuracy with low false positives.
Enterprise workflows and integrations.
Per-FQDN licensing options.
Suitable for mid-large organisations scanning many applications.
Pricing
Pricing for 50 FQDNs starts at approximately $37,000/year, and will go higher depending on the required features and support tier.
7-day trial limited trial without advanced features
Reviews & ratings
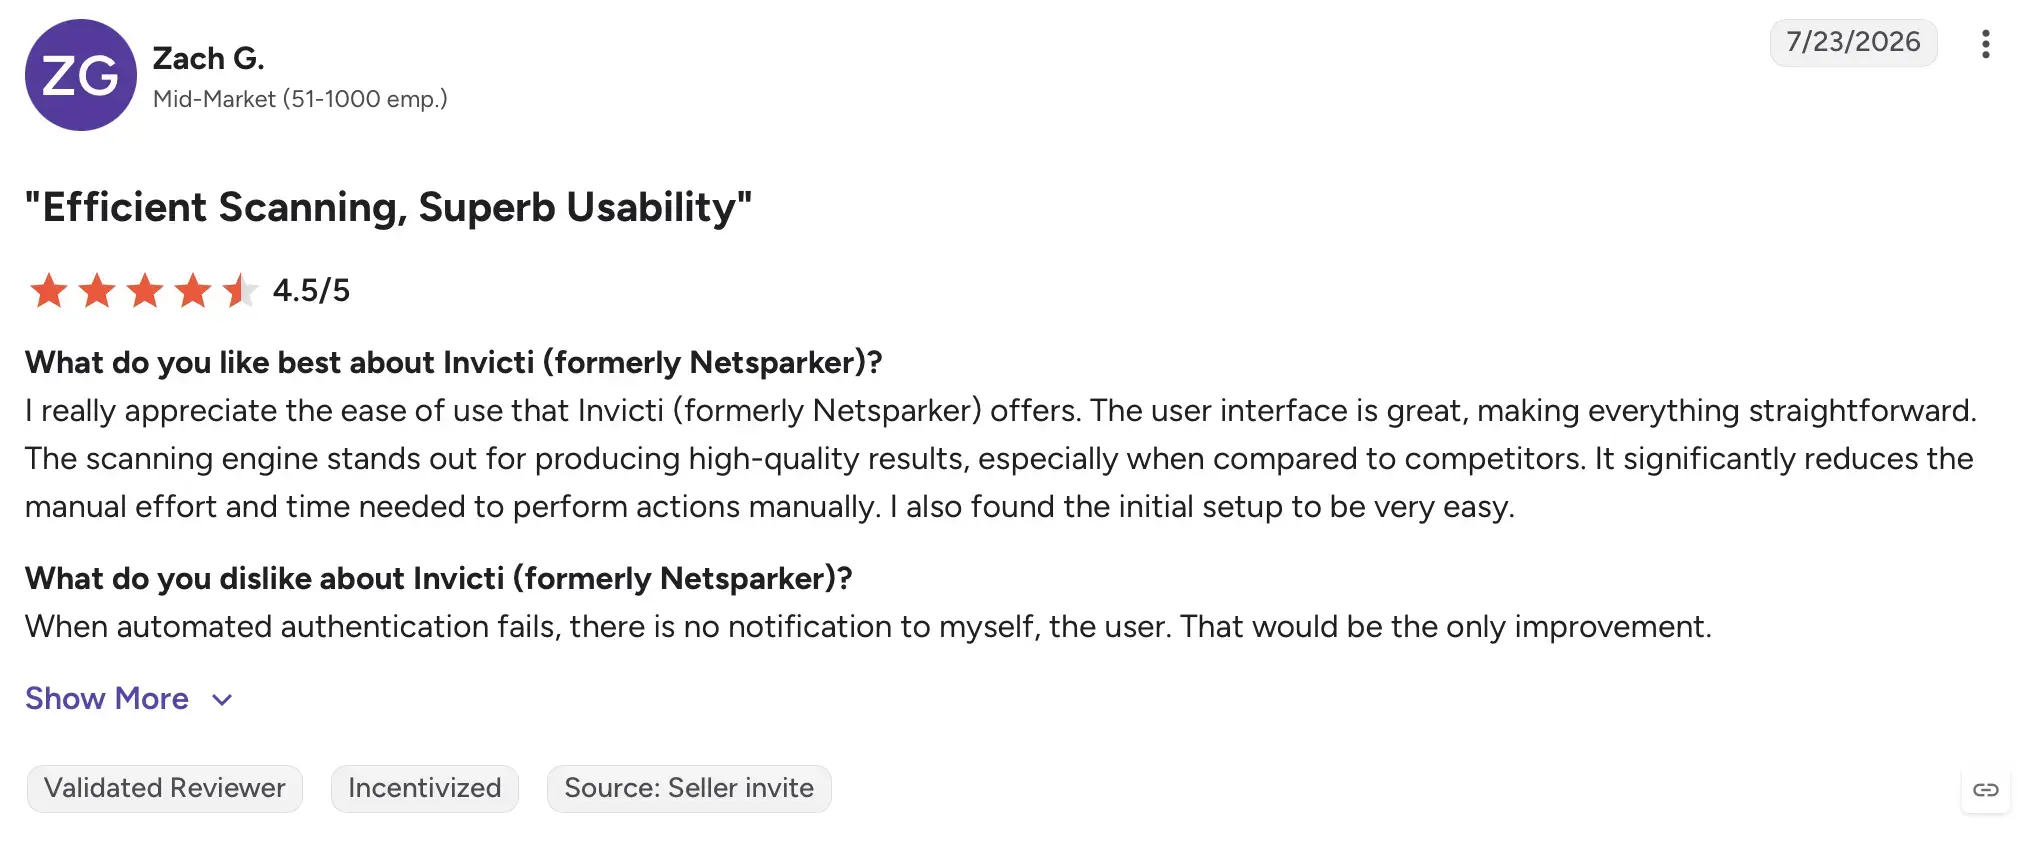
Invicti has a G2 rating of 4.5/5 based on 72 reviews.
Why consider it?
Invicti has strong enterprise grade DAST/IAST with good detection accuracy.
5) APIsec
APIsec is an AI-powered, fully automated API security testing platform built to continuously discover, validate, and remediate vulnerabilities across all API endpoints.
It generates thousands of tailored attack scenarios, integrates directly into CI/CD pipelines, and uncovers complex issues like broken access control, business-logic flaws, and OWASP API Top 10 vulnerabilities.

Key features
API-first security testing platform.
Covers OWASP API Top 10.
Covers business logic testing (BOLA, mass assignment, RBAC).
AI-driven attack simulation.
Pricing
Free tier: lifetime, covers OWASP API Top 10.
Standard : $690/month for up to 100 endpoints.
Pro: $2,750/month with full features/integrations.
Reviews & ratings
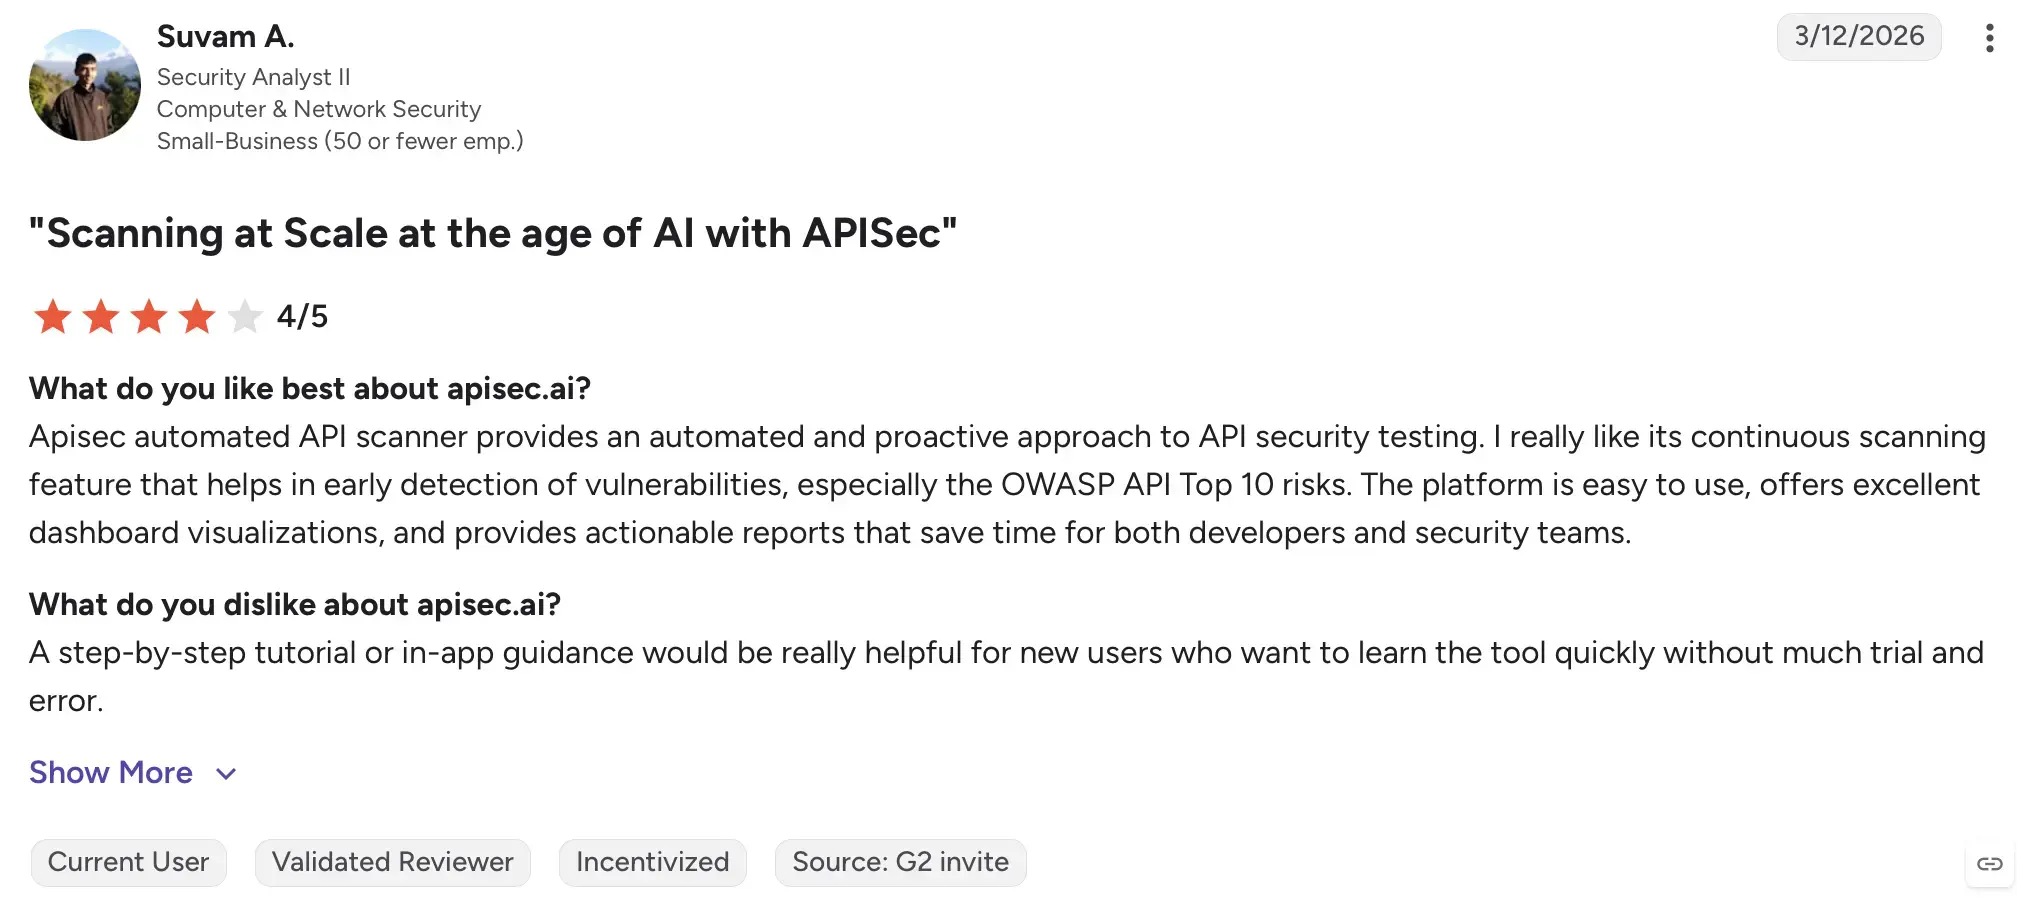
APIsec has a G2 rating of 4.7/5 based on 229 reviews.
Why consider it?
If API security is a key part of your stack (especially with many endpoints) and you want a tool tailored for that.
6) Qualys Web Application Scanning (WAS)
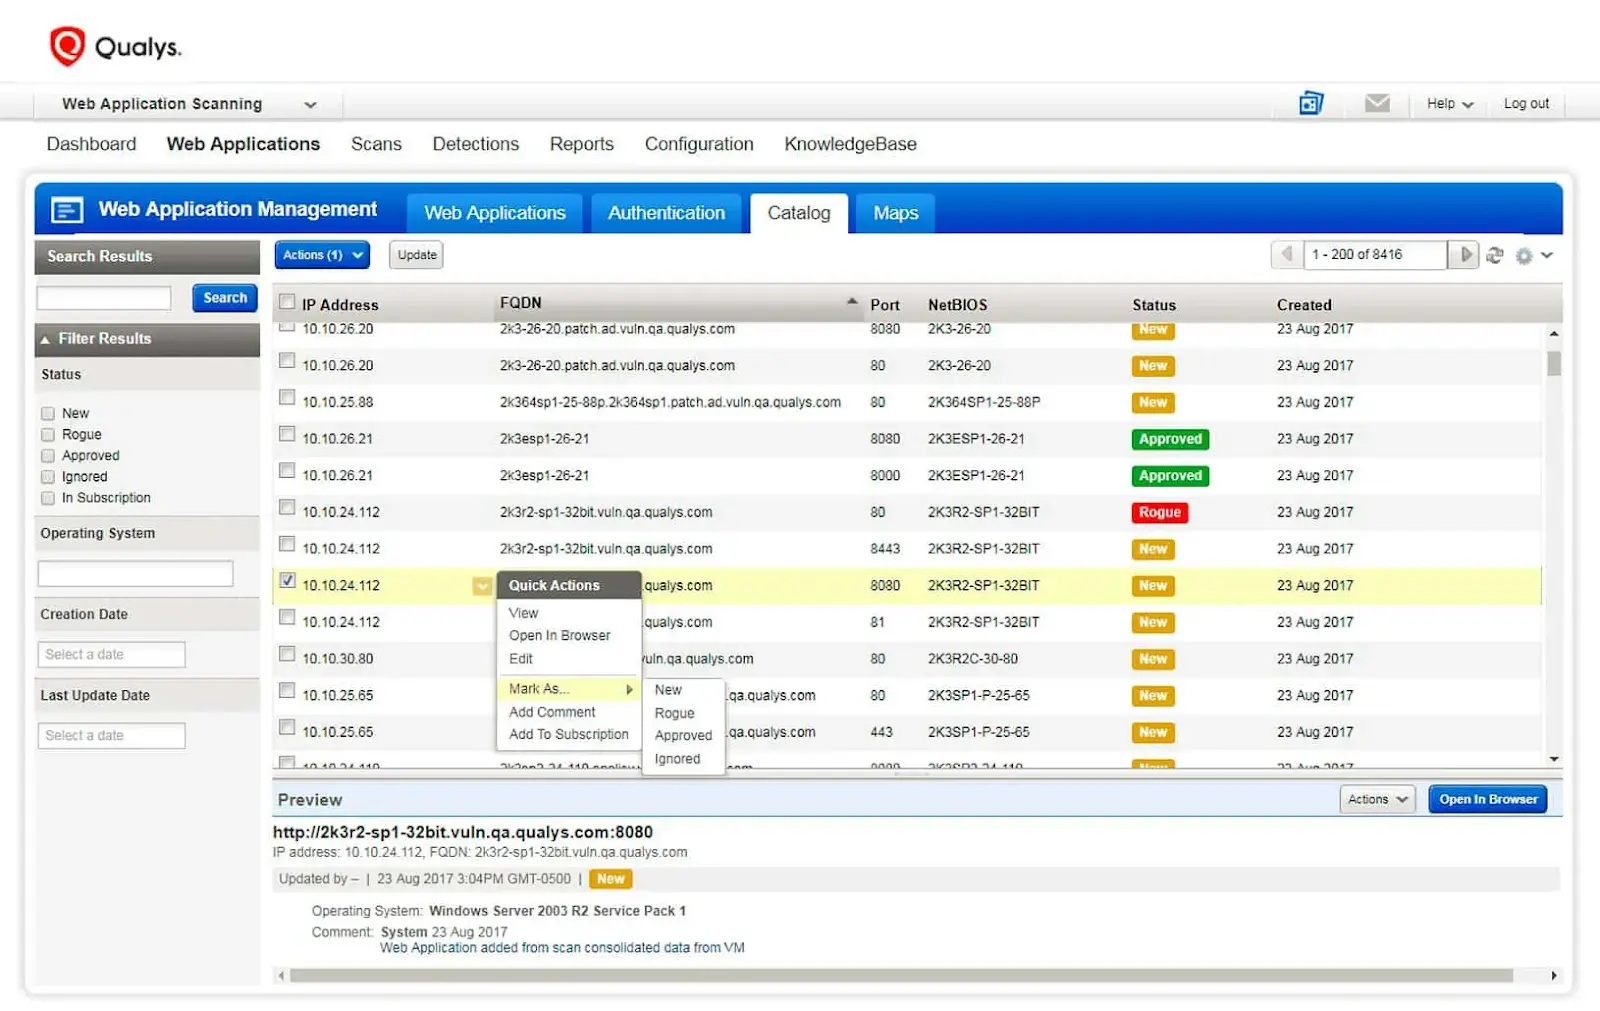
Qualys brings its well-known cloud-native vulnerability management expertise to application security through its Web Application Scanning (WAS) module.
The platform is good at asset discovery, risk prioritization, and centralized vulnerability visibility across applications, infrastructure, and cloud environments. Integration with VMDR (Vulnerability Management, Detection, and Response) offers a unified view of risk posture across the entire organization.
Key features
Cloud-based AppSec platform follows DAST, API security, AI/ML assisted scanning, OWASP Top 10 + API.
Asset discovery and tagging.
VMDR integration.
Integrations with CI/CD/DevOps.
Compliance ready workflows.
Pricing
WAS starts at $1,995 per year for 25 web applications.
VM/VMDR $199 per asset/year for vulnerability management.
Reviews & ratings
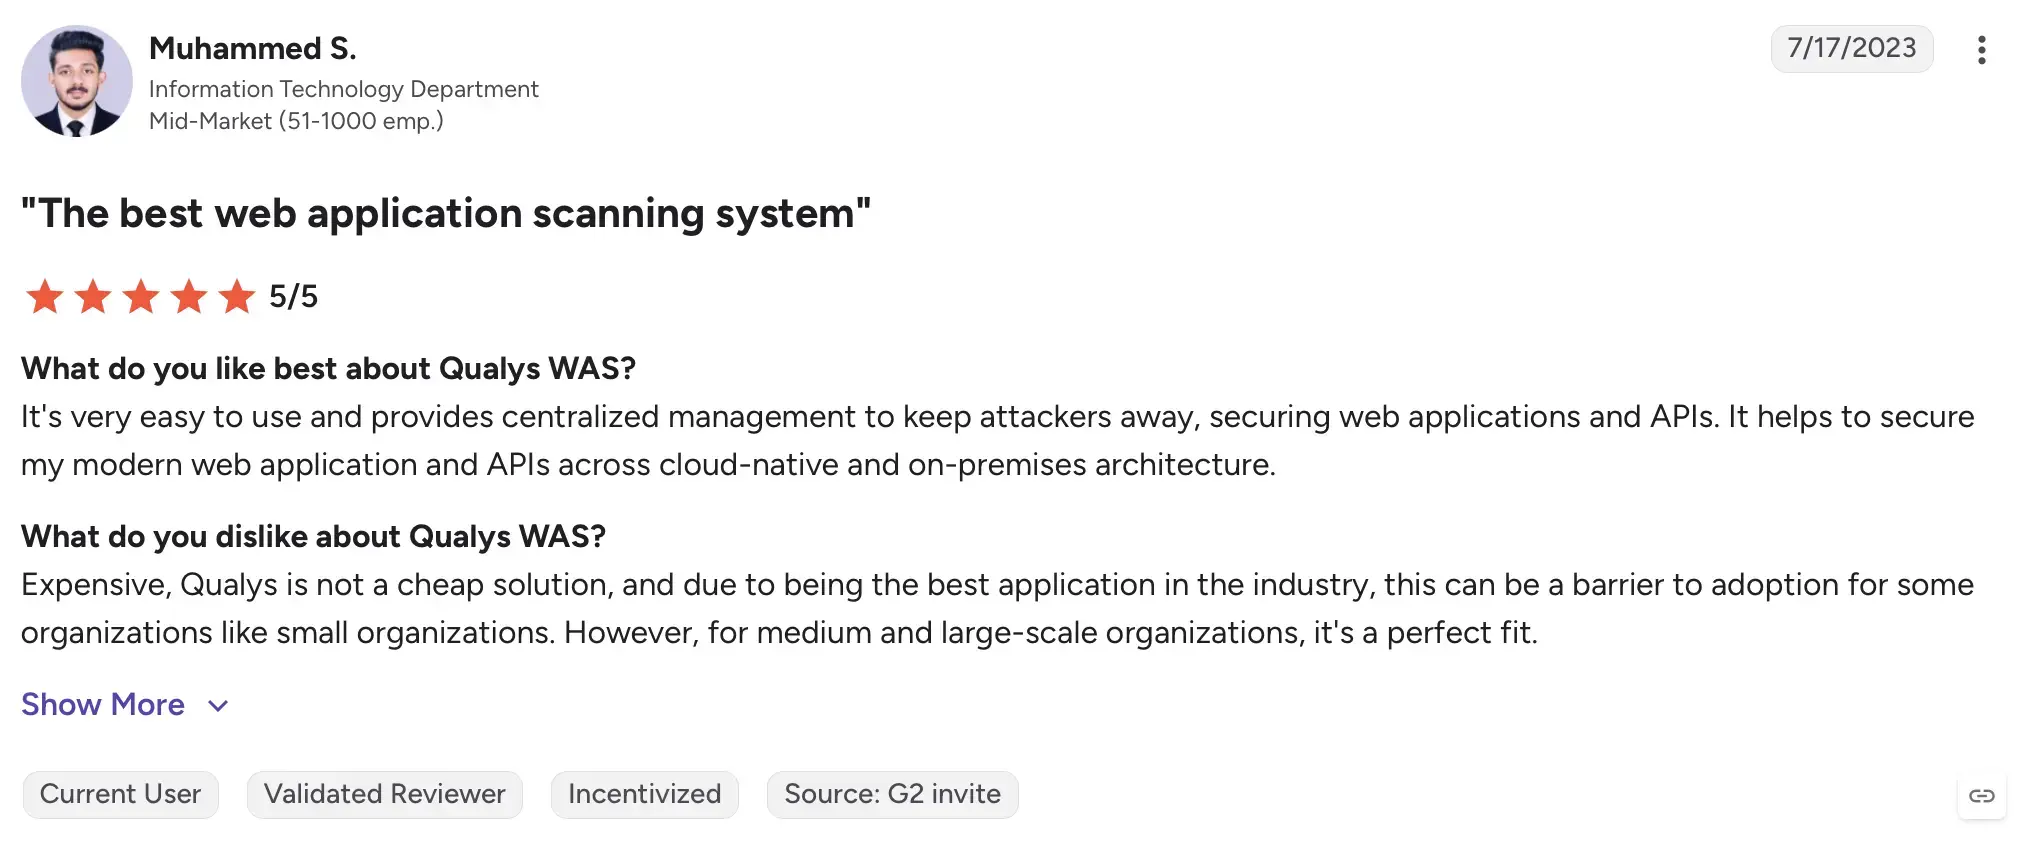
Qualys WAS has a 4.5/5 rating on G2 based on 20 reviews, with strong feedback on enterprise reporting and integration.
Why consider it
Qualys is a strong enterprise choice for organizations needing broad AppSec and vulnerability management, large number of web apps/APIs, and compliance.
7) Rapid7 InsightAppSec
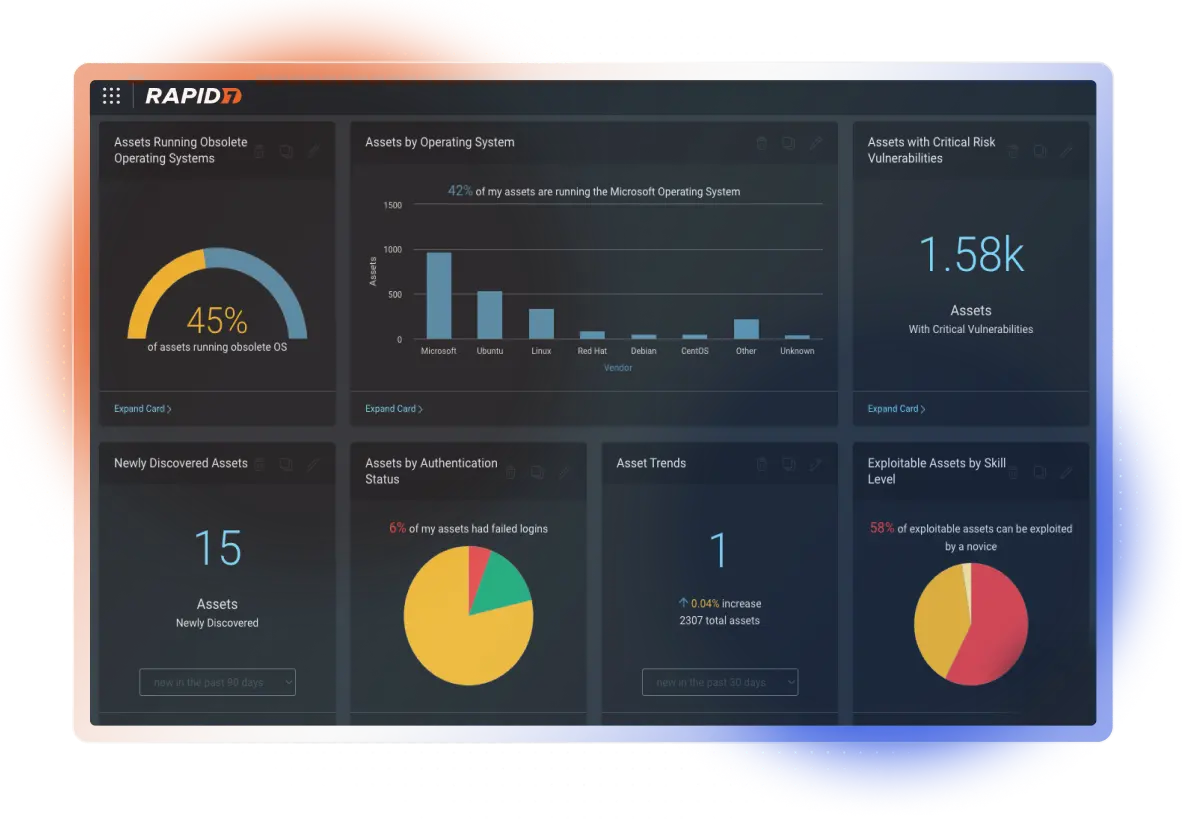
Rapid7 InsightAppSec, part of the Rapid7 Insight Platform, delivers powerful DAST capabilities combined with lightweight IAST (Interactive Application Security Testing) for deeper insights.
The platform supports automated continuous testing and integrates smoothly into CI/CD pipelines, making it ideal for DevOps and SecOps teams focused on scalability.
Key features
Cloud-based DAST/IAST style platform.
Integration into DevOps workflows.
Automated scheduling.
Incident response integration.
API security coverage.
Pricing
Starts at $175/mo per app.
Discounts are available for enterprise-level, large-scale deployments.
Reviews & ratings
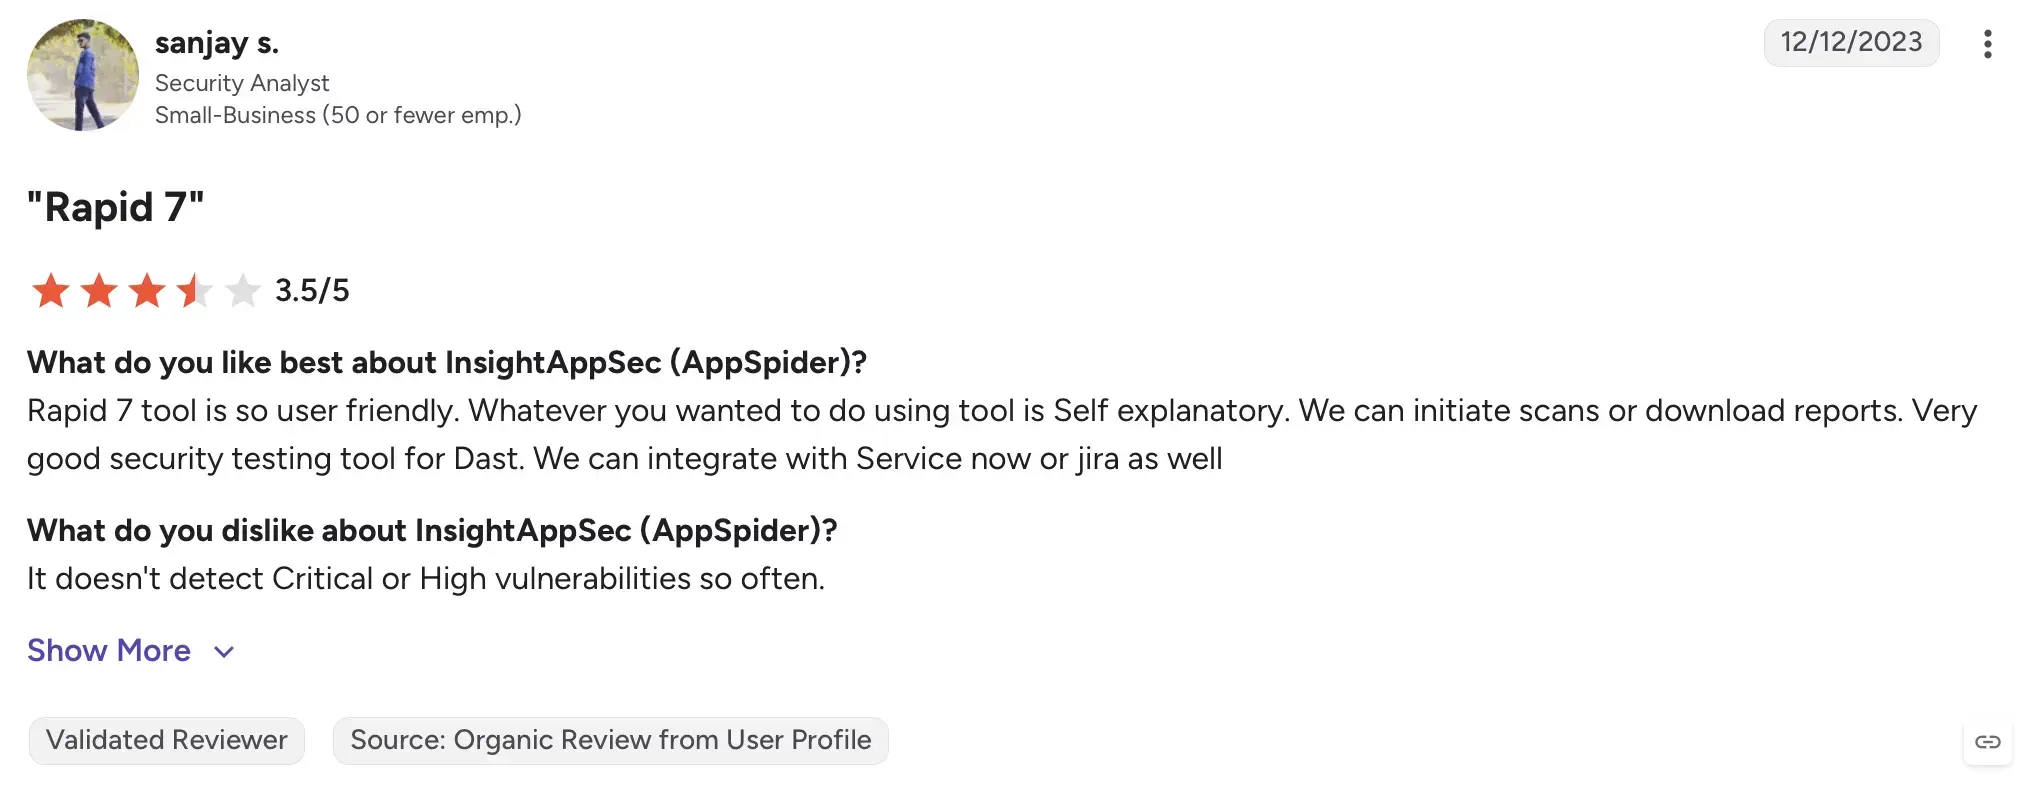
Rapid7 Insight AppSec has a G2 rating of 3.9/5 based on 10 reviews.
Why consider it?
InsightAppSec is a strong fit for security teams that already have mature infrastructure, need analytics, want dev-ops alignment and enterprise scale.
8) Acunetix
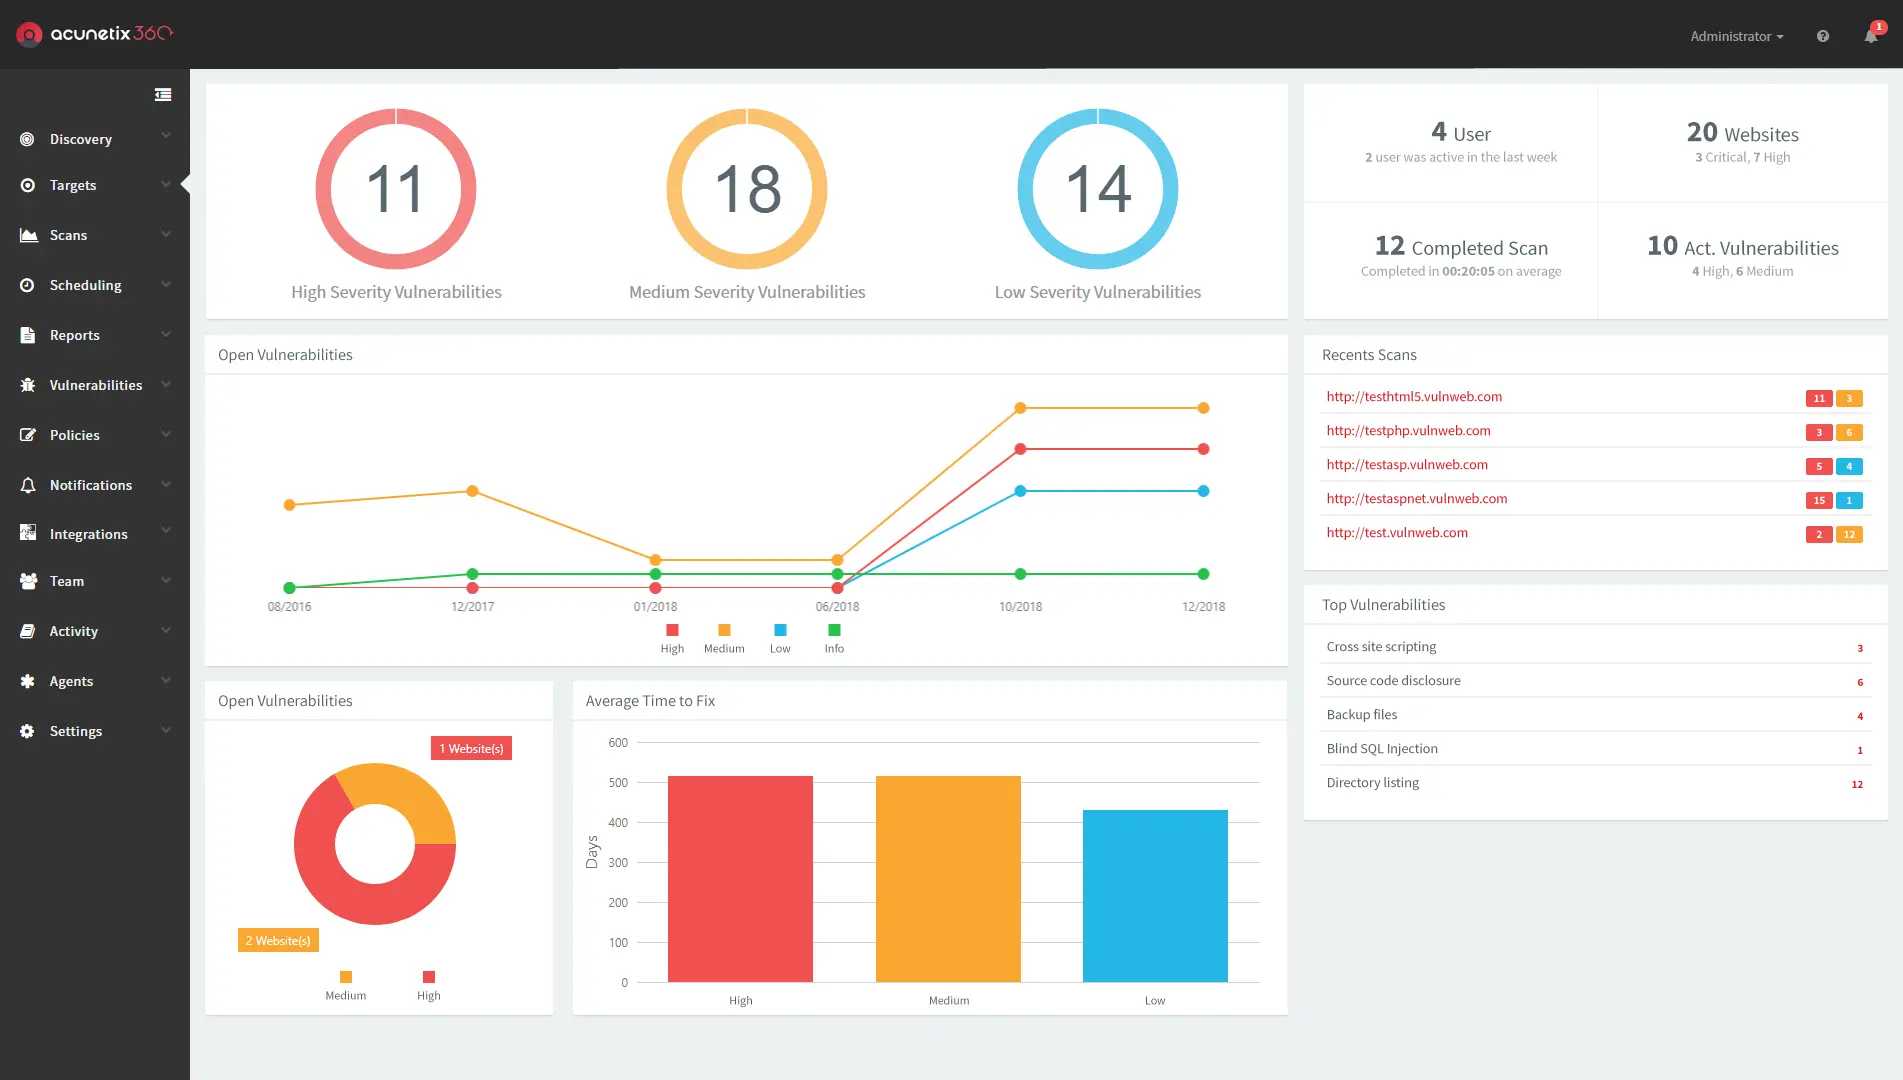
Acunetix is a long-standing web application security scanner known for its ease of use and broad vulnerability coverage, including the OWASP Top 10.
It provides automated scanning, reporting, and CI/CD integration with tools like Jenkins and Azure DevOps. However, its API testing capabilities are less advanced compared to modern DAST solutions like Beagle Security or APIsec.
Key features
Web application scanner that blends DAST & IAST.
Can detect over 6,500+ vulnerabilities.
Coverage for OWASP Top 10 vulnerabilities.
Suitable for scanning web applications and APIs with less manual overhead.
Compliance reporting for frameworks like PCI DSS and GDPR.
Pricing
Quote based but public sources indicate plans start at $7,000/year for 5 FQDNs.
Reviews & ratings
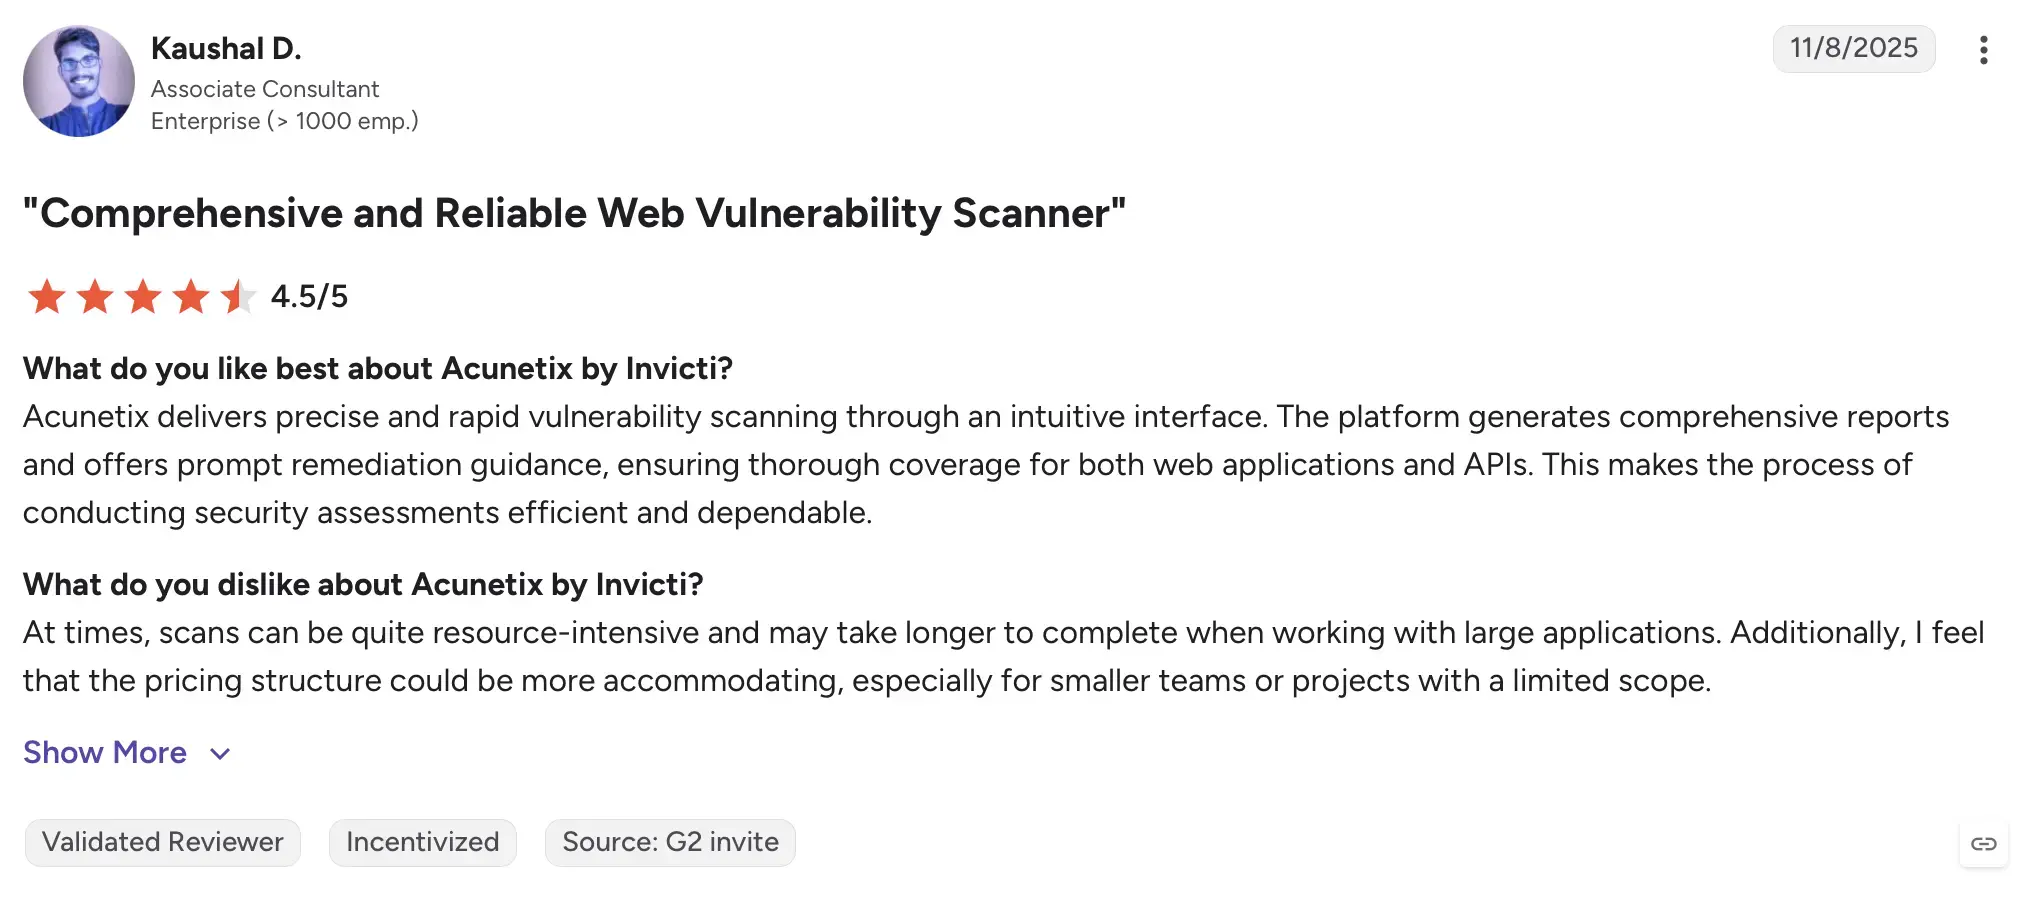
Acunetix has a G2 rating of 4.1/5 based on 105 reviews.
Why consider it?
Acutenix is good for mid-sized teams wanting a reliable web/API scanner with good coverage and moderate cost.
9) OWASP ZAP (ZAP by Checkmarx)
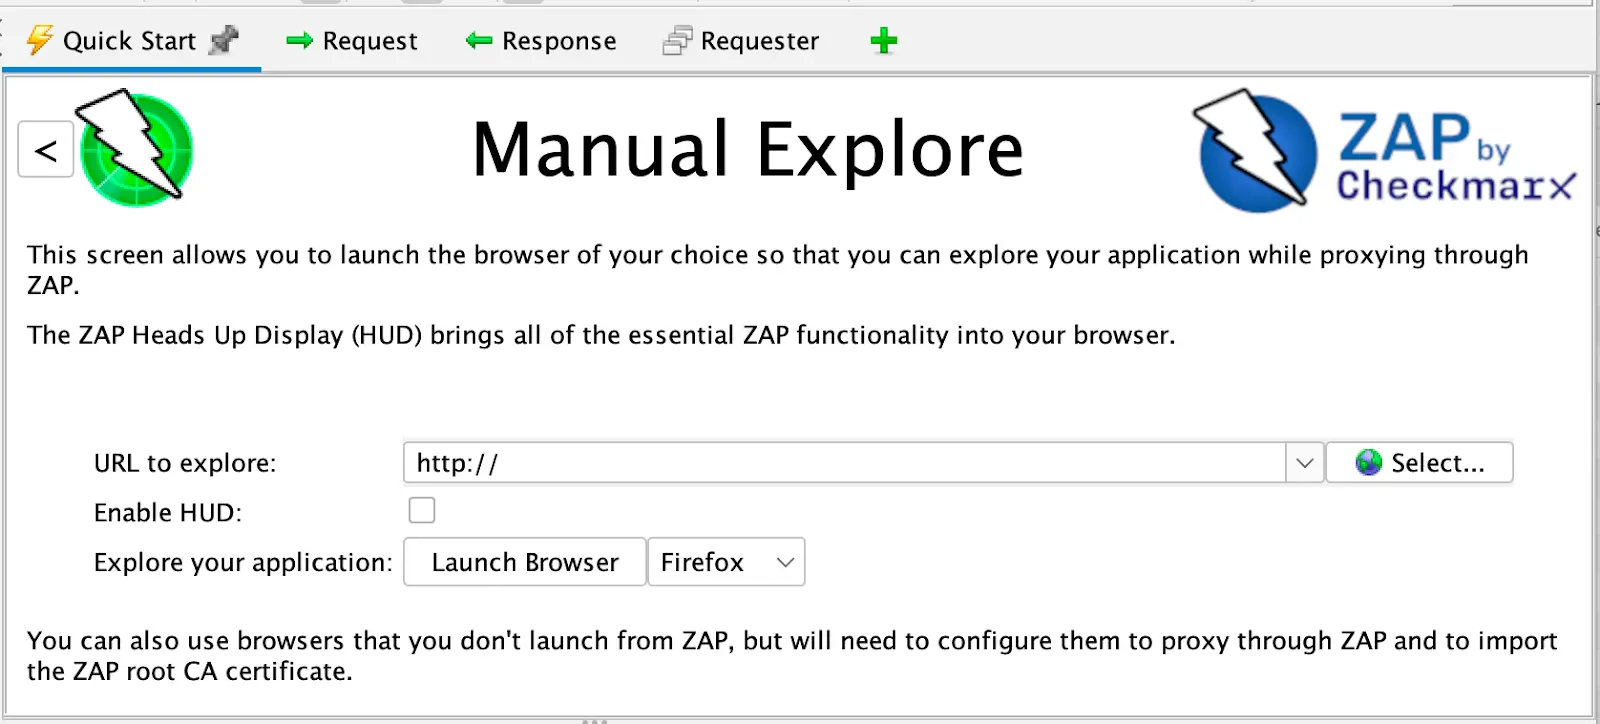
ZAP, now officially “ZAP by Checkmarx,” remains a popular open-source DAST tool globally. In 2024, Checkmarx partnered with the ZAP Core Team, strengthening its roadmap while keeping the project free and community-driven under the Apache v2 license.
ZAP offers automated scanning, intercepting proxy functionality, and scriptable testing, making it a versatile choice for developers and testers learning or customizing their workflows.
Key features
Open-source DAST tool maintained by OWASP.
Free to use.
Supports web application scanning, spidering and API fuzzing.
Has a lot of community plugins.
Good for manual or automated scanning, but requires more security expertise.
Pricing
- 100% free and open source.
Reviews & ratings
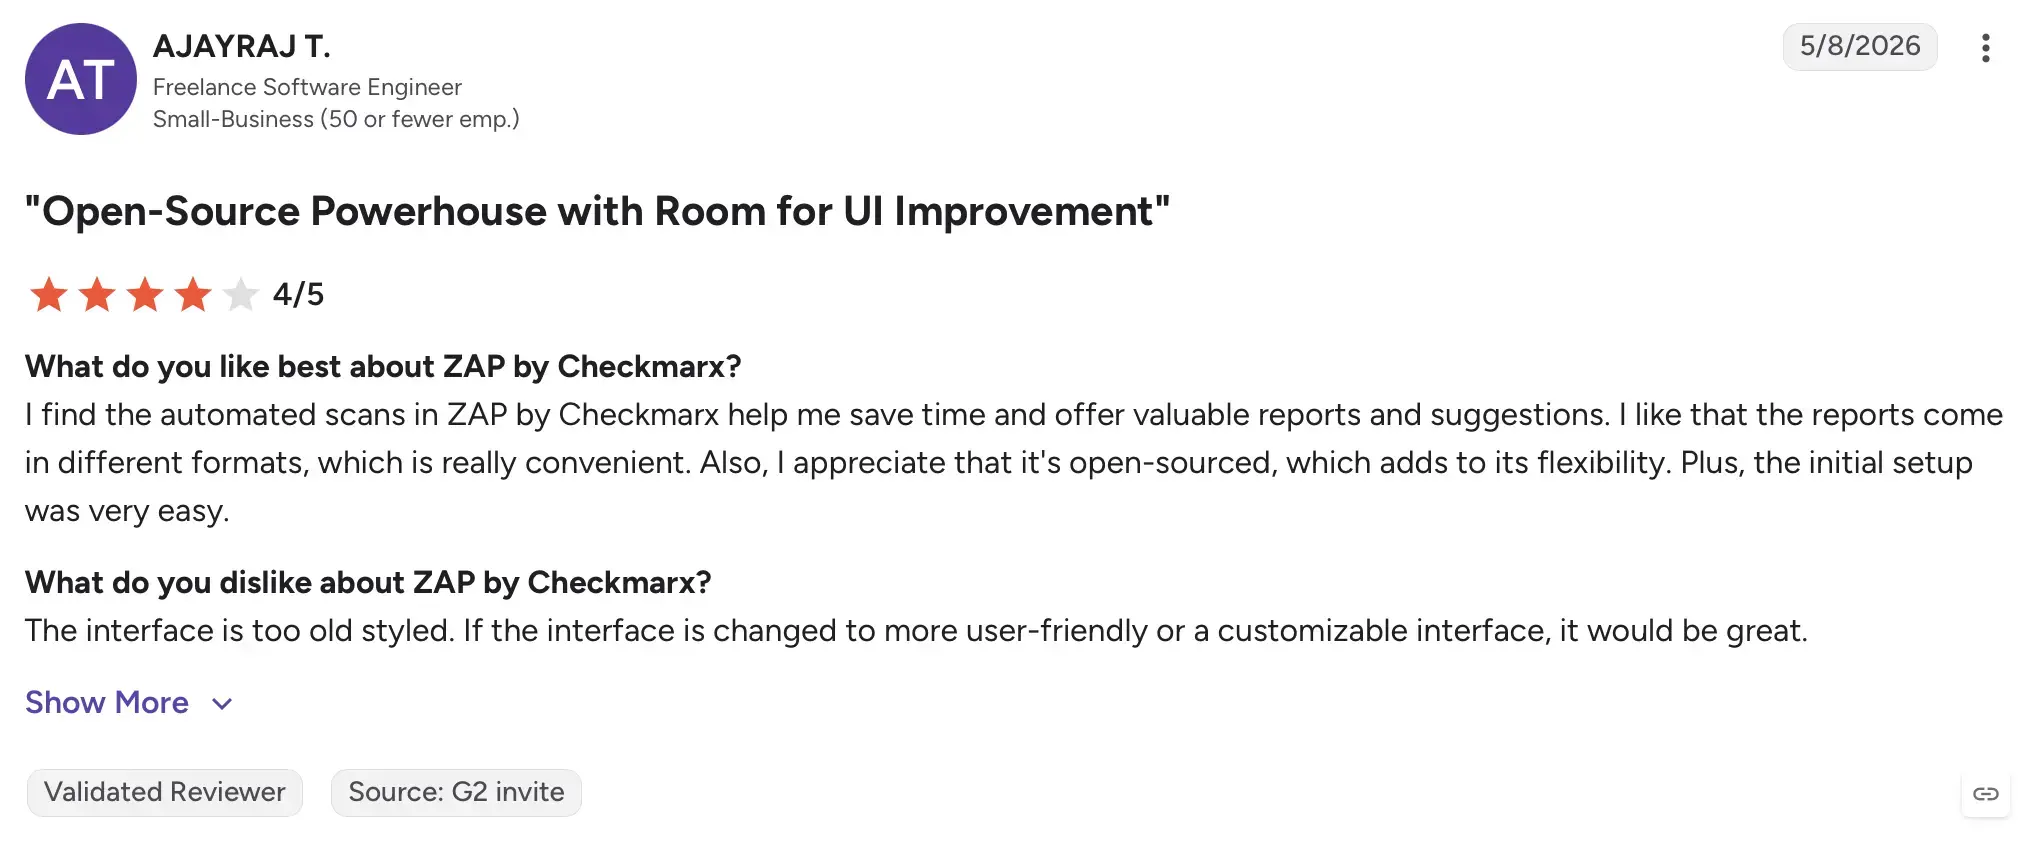
ZAP has a G2 rating of 4.7/5 based on 14 reviews.
Why consider it?
Zap is strong for teams with security expertise who want minimal licensing cost. It’s also great for smaller orgs with higher budget-constrains.
10) Tenable Web App Scanning
Tenable Web App Scanning (WAS) extends Tenable’s strong reputation in vulnerability management into application security.
It focuses on risk-based prioritization using Tenable’s Vulnerability Priority Rating (VPR) system, helping teams identify and fix issues that matter most.
Key features
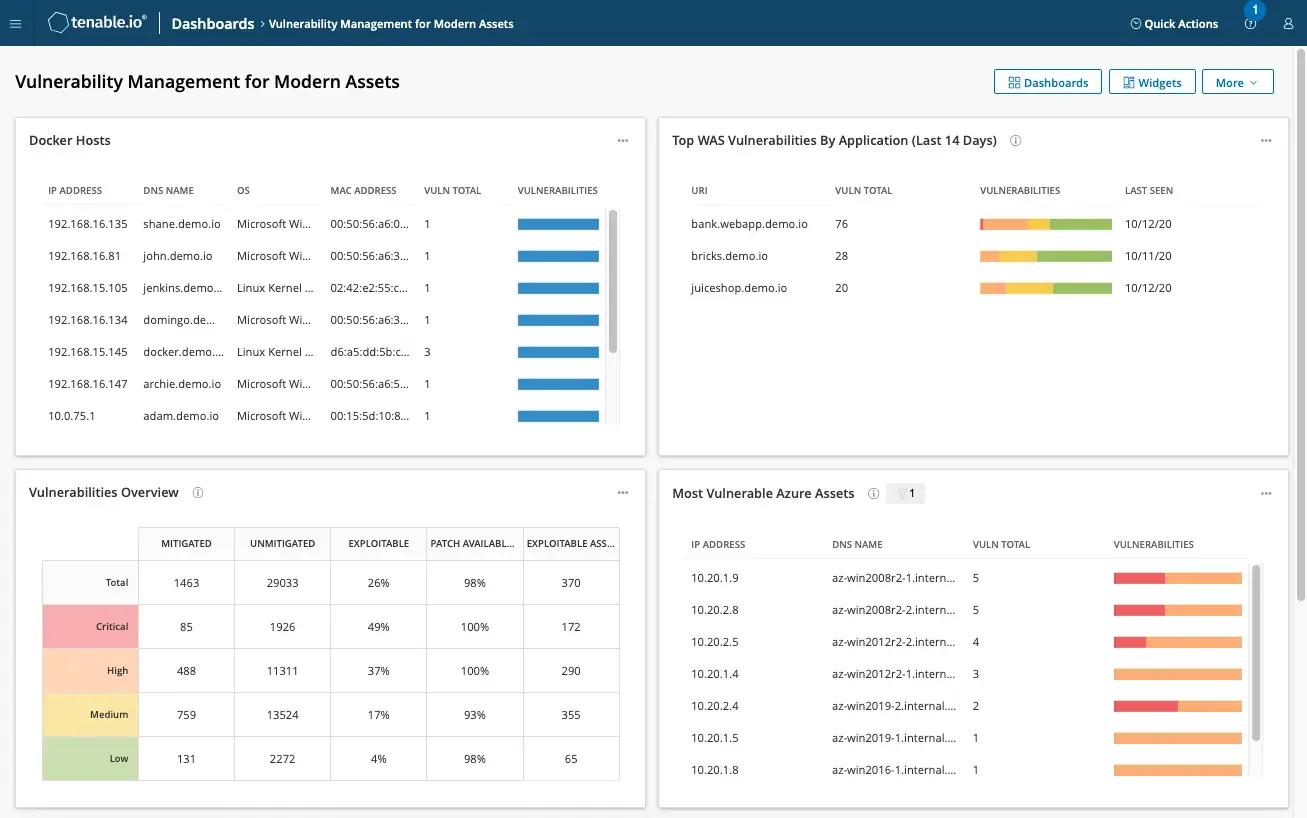
SaaS and on-prem DAST for web apps + APIs, unified with broader exposure management (via Tenable).
Built for modern web apps (SPA, API), integrates vulnerability management, exposure visibility.
Web application scanning.
Enterprise reporting and dashboards.
Pricing
Starts at $7,434 annually (5 FQDNs).
Asset-based pricing model.
30-day free trial available.
Reviews & ratings
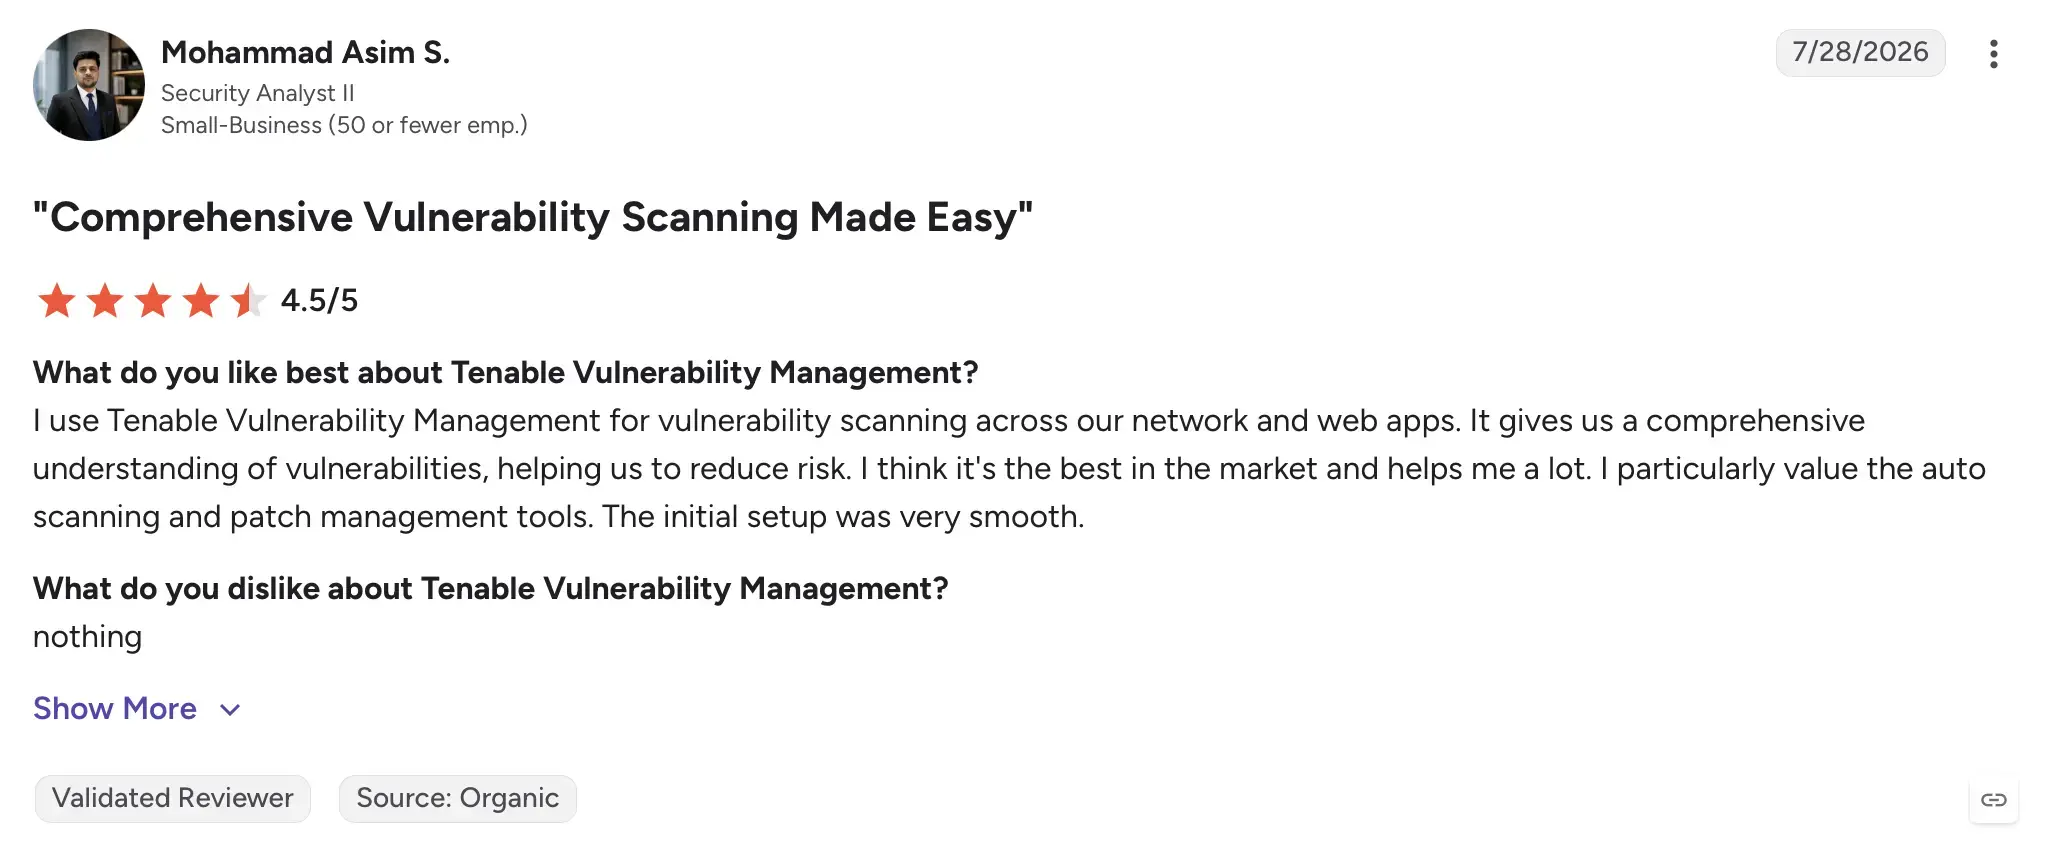
Tenable has a rating of 4.5/5 on G2, based on 125 reviews.
Why consider it?
Tenable WAS is ideal for larger orgs with many web apps, API surface, hybrid/complex environments, and who prefer one vendor for exposure/security across assets.
Key factors to consider when choosing a StackHawk alternative
When evaluating alternatives to StackHawk, it’s important to look beyond just pricing or brand reputation. Here are the most critical factors to consider.
Testing coverage & depth
Ensure the tool supports your application stack including web apps, APIs (REST/GraphQL), SPAs, and microservices. Some tools emphasize broad vulnerability scanning, while others specialize in business logic and API testing.Integration with CI/CD Pipelines
Choose a platform that fits seamlessly into your DevOps workflow, integrating with GitHub, Jenkins, GitLab, or Azure DevOps.Accuracy & false positives
Accuracy matters more than scan volume. Look for vendors that provide contextual remediation guidance or AI-assisted triage to minimize false alarms.Authentication & access support
Modern apps often use complex authentication like 2FA, SSO, or OAuth. Pick a DAST tool that can handle authenticated testing across user roles and sessions.Scalability & team management
If you’re an enterprise or growing startup, you’ll need multi-user access, role-based controls, and scalable project management features.Reporting & compliance readiness
Check whether the tool offers exportable reports aligned with frameworks such as OWASP Top 10, PCI DSS, ISO 27001, or SOC 2 to streamline compliance reviews.Pricing model & value for money
Compare cost per app, per scan, or per contributor to ensure long-term affordability. Usage-based or API-count pricing often scales better than per-user licenses.
Final thoughts
Choosing the right StackHawk alternative ultimately depends on your organization’s security maturity, tech stack, and workflow priorities. While established tools like Burp Suite, Invicti, and Rapid7 excel in enterprise-grade scanning and manual validation, they often require higher budgets or dedicated security resources to manage effectively.
For teams seeking a modern, automated, and developer-friendly DAST solution, Beagle Security stands out as a strong contender. Its AI-driven testing, accurate vulnerability detection, and CI/CD-ready integrations make it ideal for organizations aiming to embed security seamlessly into their development lifecycle. Check out our 14-day advanced trial or play around with the interactive demo to see if we’re the right fit for you.
FAQs
Why might a team consider an alternative to StackHawk?
Every organization has different security goals. Some teams may need more advanced API testing, broader authentication support, easier integrations, enhanced reporting, or a pricing structure that better suits their budget. Comparing alternatives helps ensure the chosen platform meets both current and future requirements.
What features should you compare when evaluating StackHawk alternatives?
Beyond vulnerability detection, it’s worth looking at how well a platform handles API security, CI/CD integration, authentication, compliance reporting, automation, scalability, and usability. A solution that fits naturally into your existing workflow will provide greater long-term value.
Why is Beagle Security a strong alternative to StackHawk?
Beagle Security combines automated web application and API security testing with features such as AI-assisted attack simulations, compliance reporting, and CI/CD integration. Its focus on automation and ease of use makes it a practical option for teams looking to simplify application security testing.