When it comes to vulnerability management and application security, Tenable is one of the most recognized names in cybersecurity. Its platform spans traditional vulnerability scanning, web application testing, cloud security, and exposure management across hybrid environments.
The security landscape has moved fast, though, and Tenable is often seen as the more established, traditional platform in a market now full of leaner, faster-moving alternatives. That raises a fair question: how much does Tenable actually cost in 2026, and is it worth the investment?
This guide breaks down Tenable’s pricing across its major products, what drives those costs, and a few alternatives worth comparing depending on your use case.
TL;DR: Tenable pricing 2026
| What it offers | Vulnerability management, web application scanning, cloud security, and unified exposure management (Tenable One) |
|---|---|
| Pricing | Not published publicly; third-party estimates range from roughly $3,700/year (Vulnerability Management, small scale) to $50,000+/year (Tenable One) |
| Best for | Large or mid-sized enterprises that want broad exposure management across infrastructure, cloud, and applications in one ecosystem |
| Main advantage | Breadth and enterprise maturity, with most security domains covered under one platform |
| Main limitation | Cost escalates quickly at scale, and the lack of published pricing makes upfront budgeting harder |
| Worth considering if | You need infrastructure-wide coverage rather than focused web application or API testing, and can absorb enterprise-level cost |
How much does Tenable cost?
Like most enterprise cybersecurity vendors, Tenable doesn’t publish official list pricing. Every price on Tenable’s own site leads to a quote request rather than a checkout page, and costs scale based on the number of assets, deployment model, and which modules you bundle in.
Two of Tenable’s core products have also been renamed. What used to be sold as Tenable.io is now marketed as Tenable One Vulnerability Management , and what used to be Tenable WAS is now Tenable One Web App Scanning , both positioned as part of the broader Tenable One platform. The older names still show up across the web, including in search results, so it’s worth knowing they refer to the same products.
The figures below are third-party estimates and benchmarks rather than Tenable’s own published numbers. Treat them as a starting point for budgeting, not a quote.
| Product | Estimated annual pricing | Basis |
|---|---|---|
| Tenable One Web App Scanning (formerly Tenable WAS) | $7,434/year for 5 FQDNs | Third-party benchmark |
| Tenable One Vulnerability Management (formerly Tenable.io) | Roughly $3,700 to $7,000+/year for 100–250 assets, depending on source | Third-party benchmarks (estimates vary significantly) |
| Tenable Security Center (formerly Tenable.sc) | $4,076/year, scaling with asset volume | Third-party benchmark |
| Tenable Cloud Security | Custom quote only | Not publicly estimated |
| Tenable One (bundled exposure management) | Starting around $50,000+/year | Third-party benchmark, scales with assets and modules |
Independent pricing trackers don’t agree closely with each other on Tenable Vulnerability Management specifically. Some cite entry pricing near $3,700/year for smaller asset counts, while transaction data from procurement platforms puts the median actual contract closer to $17,000 to $18,000/year. The gap comes down to asset count, negotiated discounts, and which add-ons are bundled in, so treat any single number as a rough anchor rather than what you’ll actually pay.
Tenable One Web App Scanning pricing
Tenable One Web App Scanning (formerly Tenable WAS) is built to find vulnerabilities in web applications and APIs. Third-party benchmarks put entry pricing around $7,434 per year for 5 FQDNs, with cost scaling as you add more domains.
The more FQDNs you need to cover, the higher the annual cost climbs.
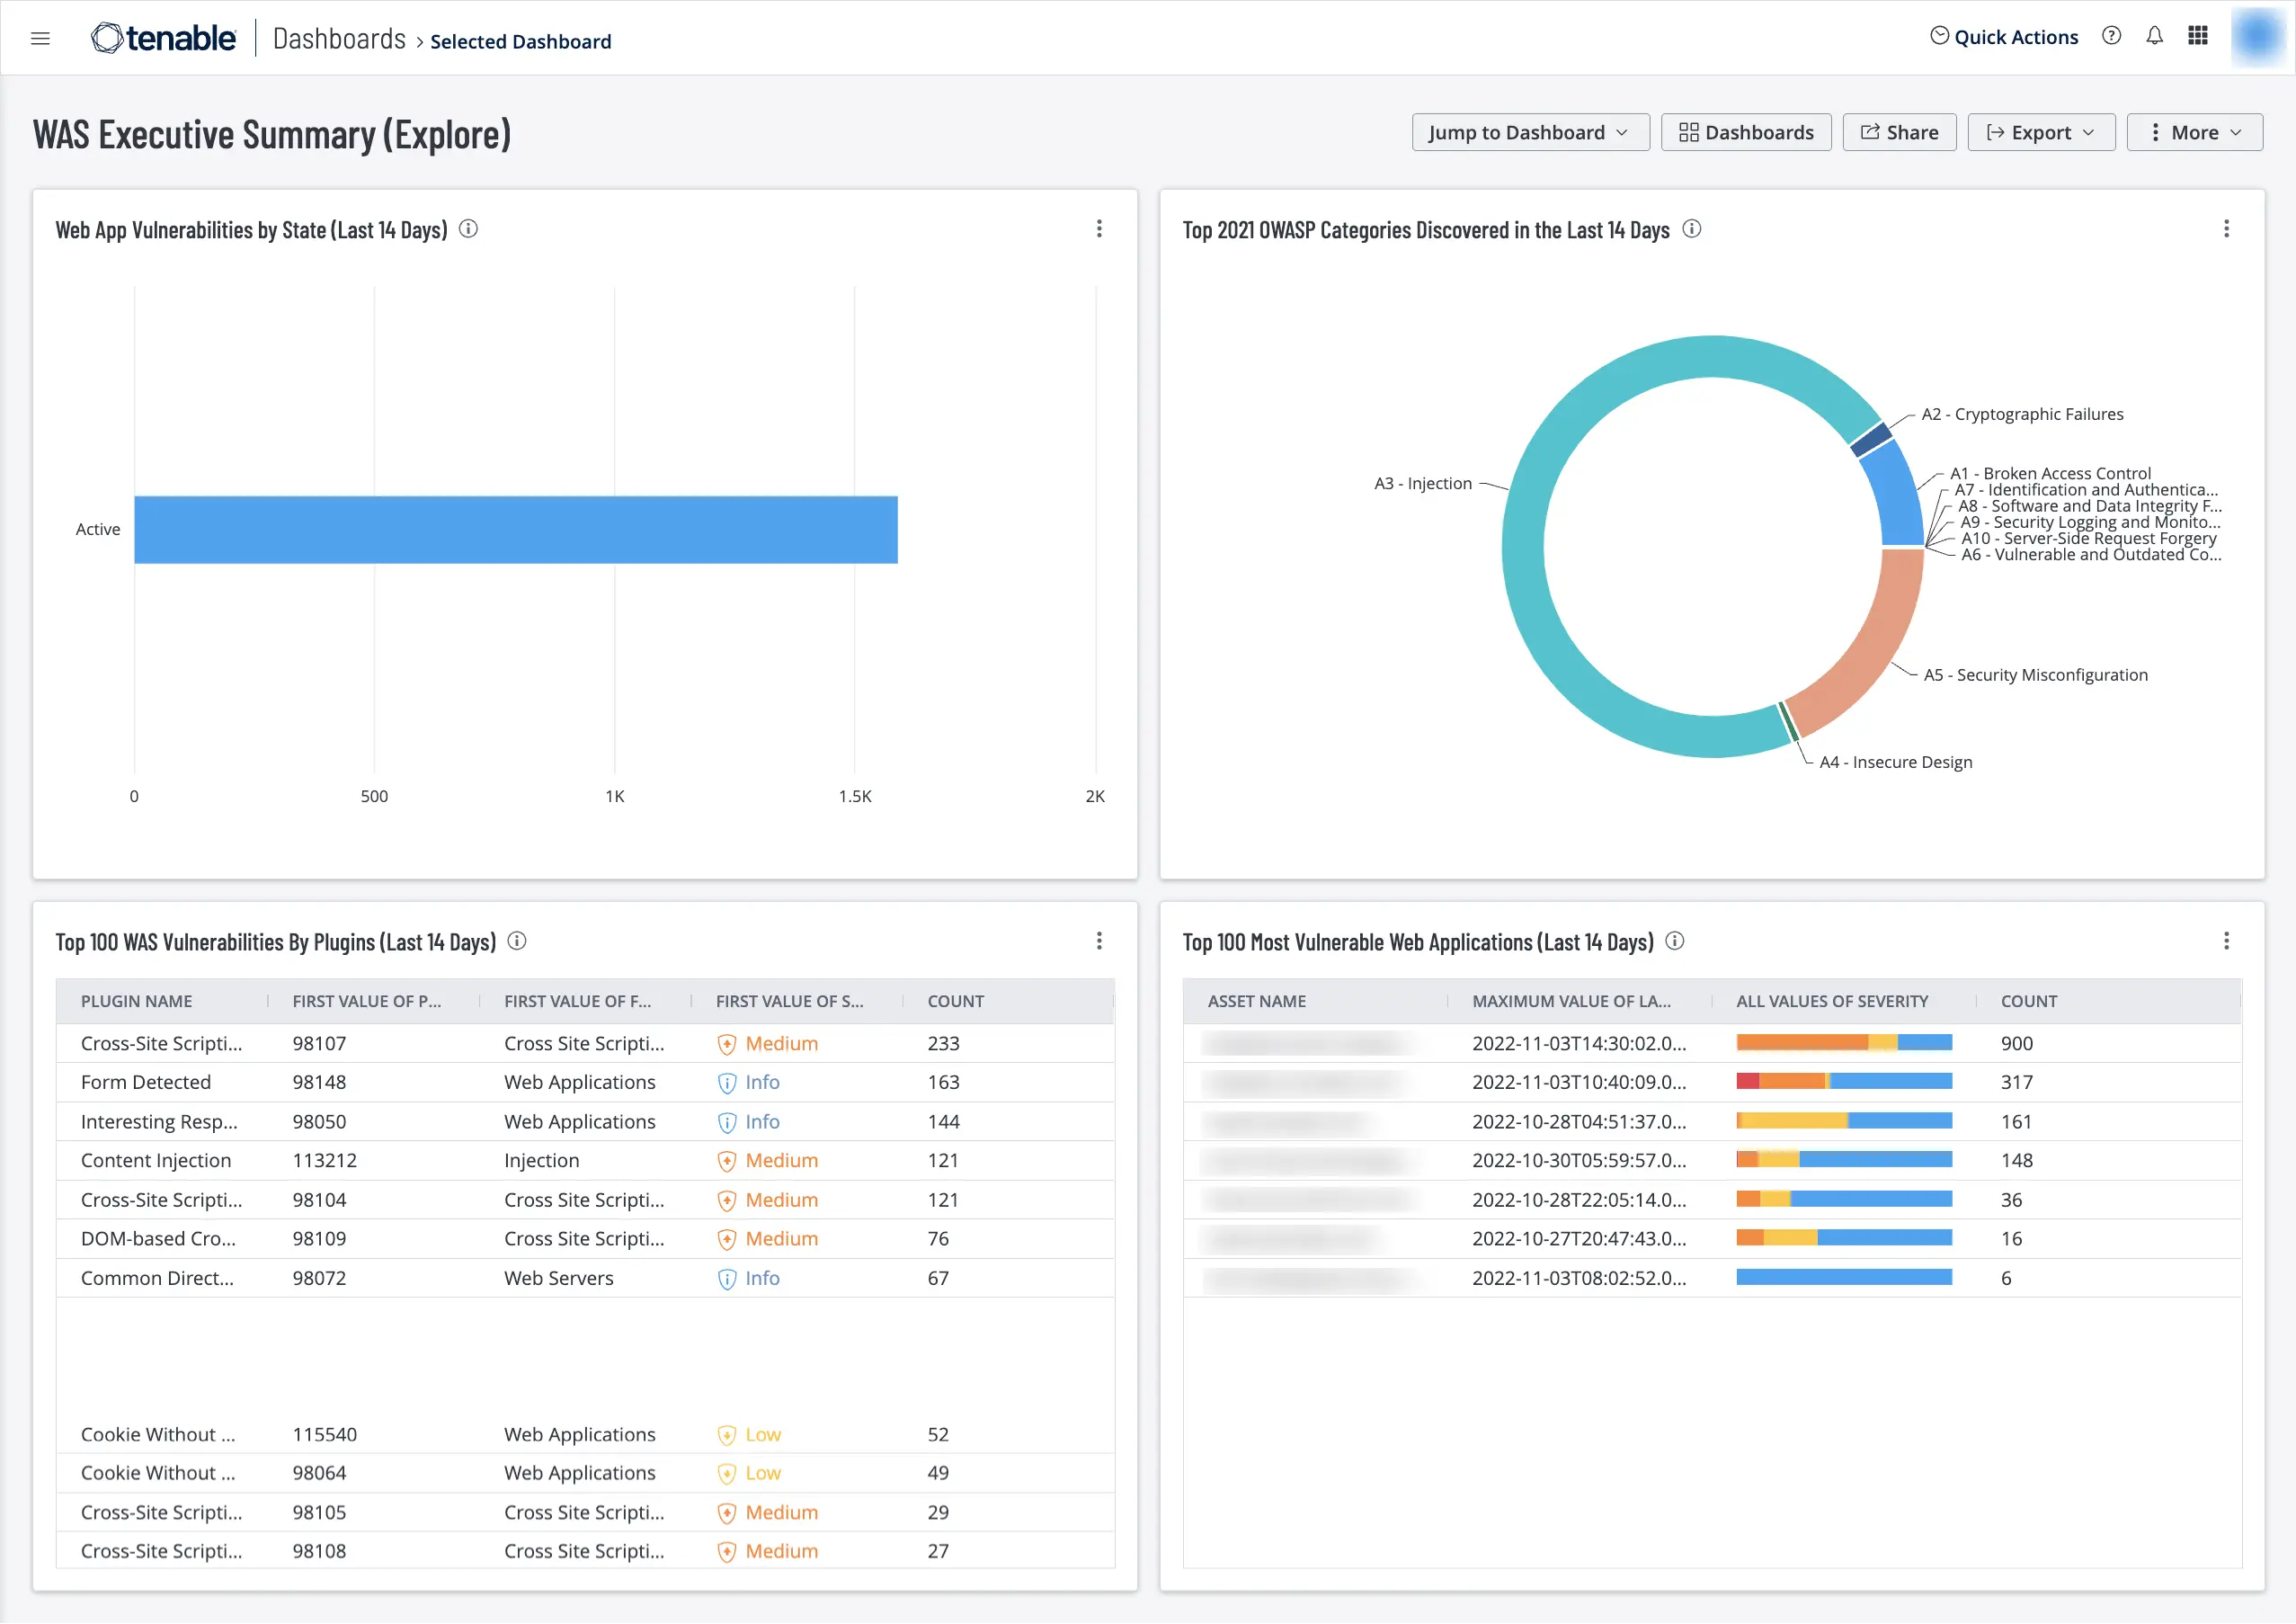
Main features:
Automated Dynamic Application Security Testing (DAST)
API scanning
DevSecOps integration
Vulnerability intelligence
Advanced reporting
Best Tenable web app scanning alternative: Beagle Security
Beagle Security is an agentic AI penetration testing platform for web application, API, and GraphQL security testing, priced starting from $1,188 per year. Unlike Tenable’s web app scanning module, it’s built to handle complex authentication flows and deliver developer-friendly remediation guidance.
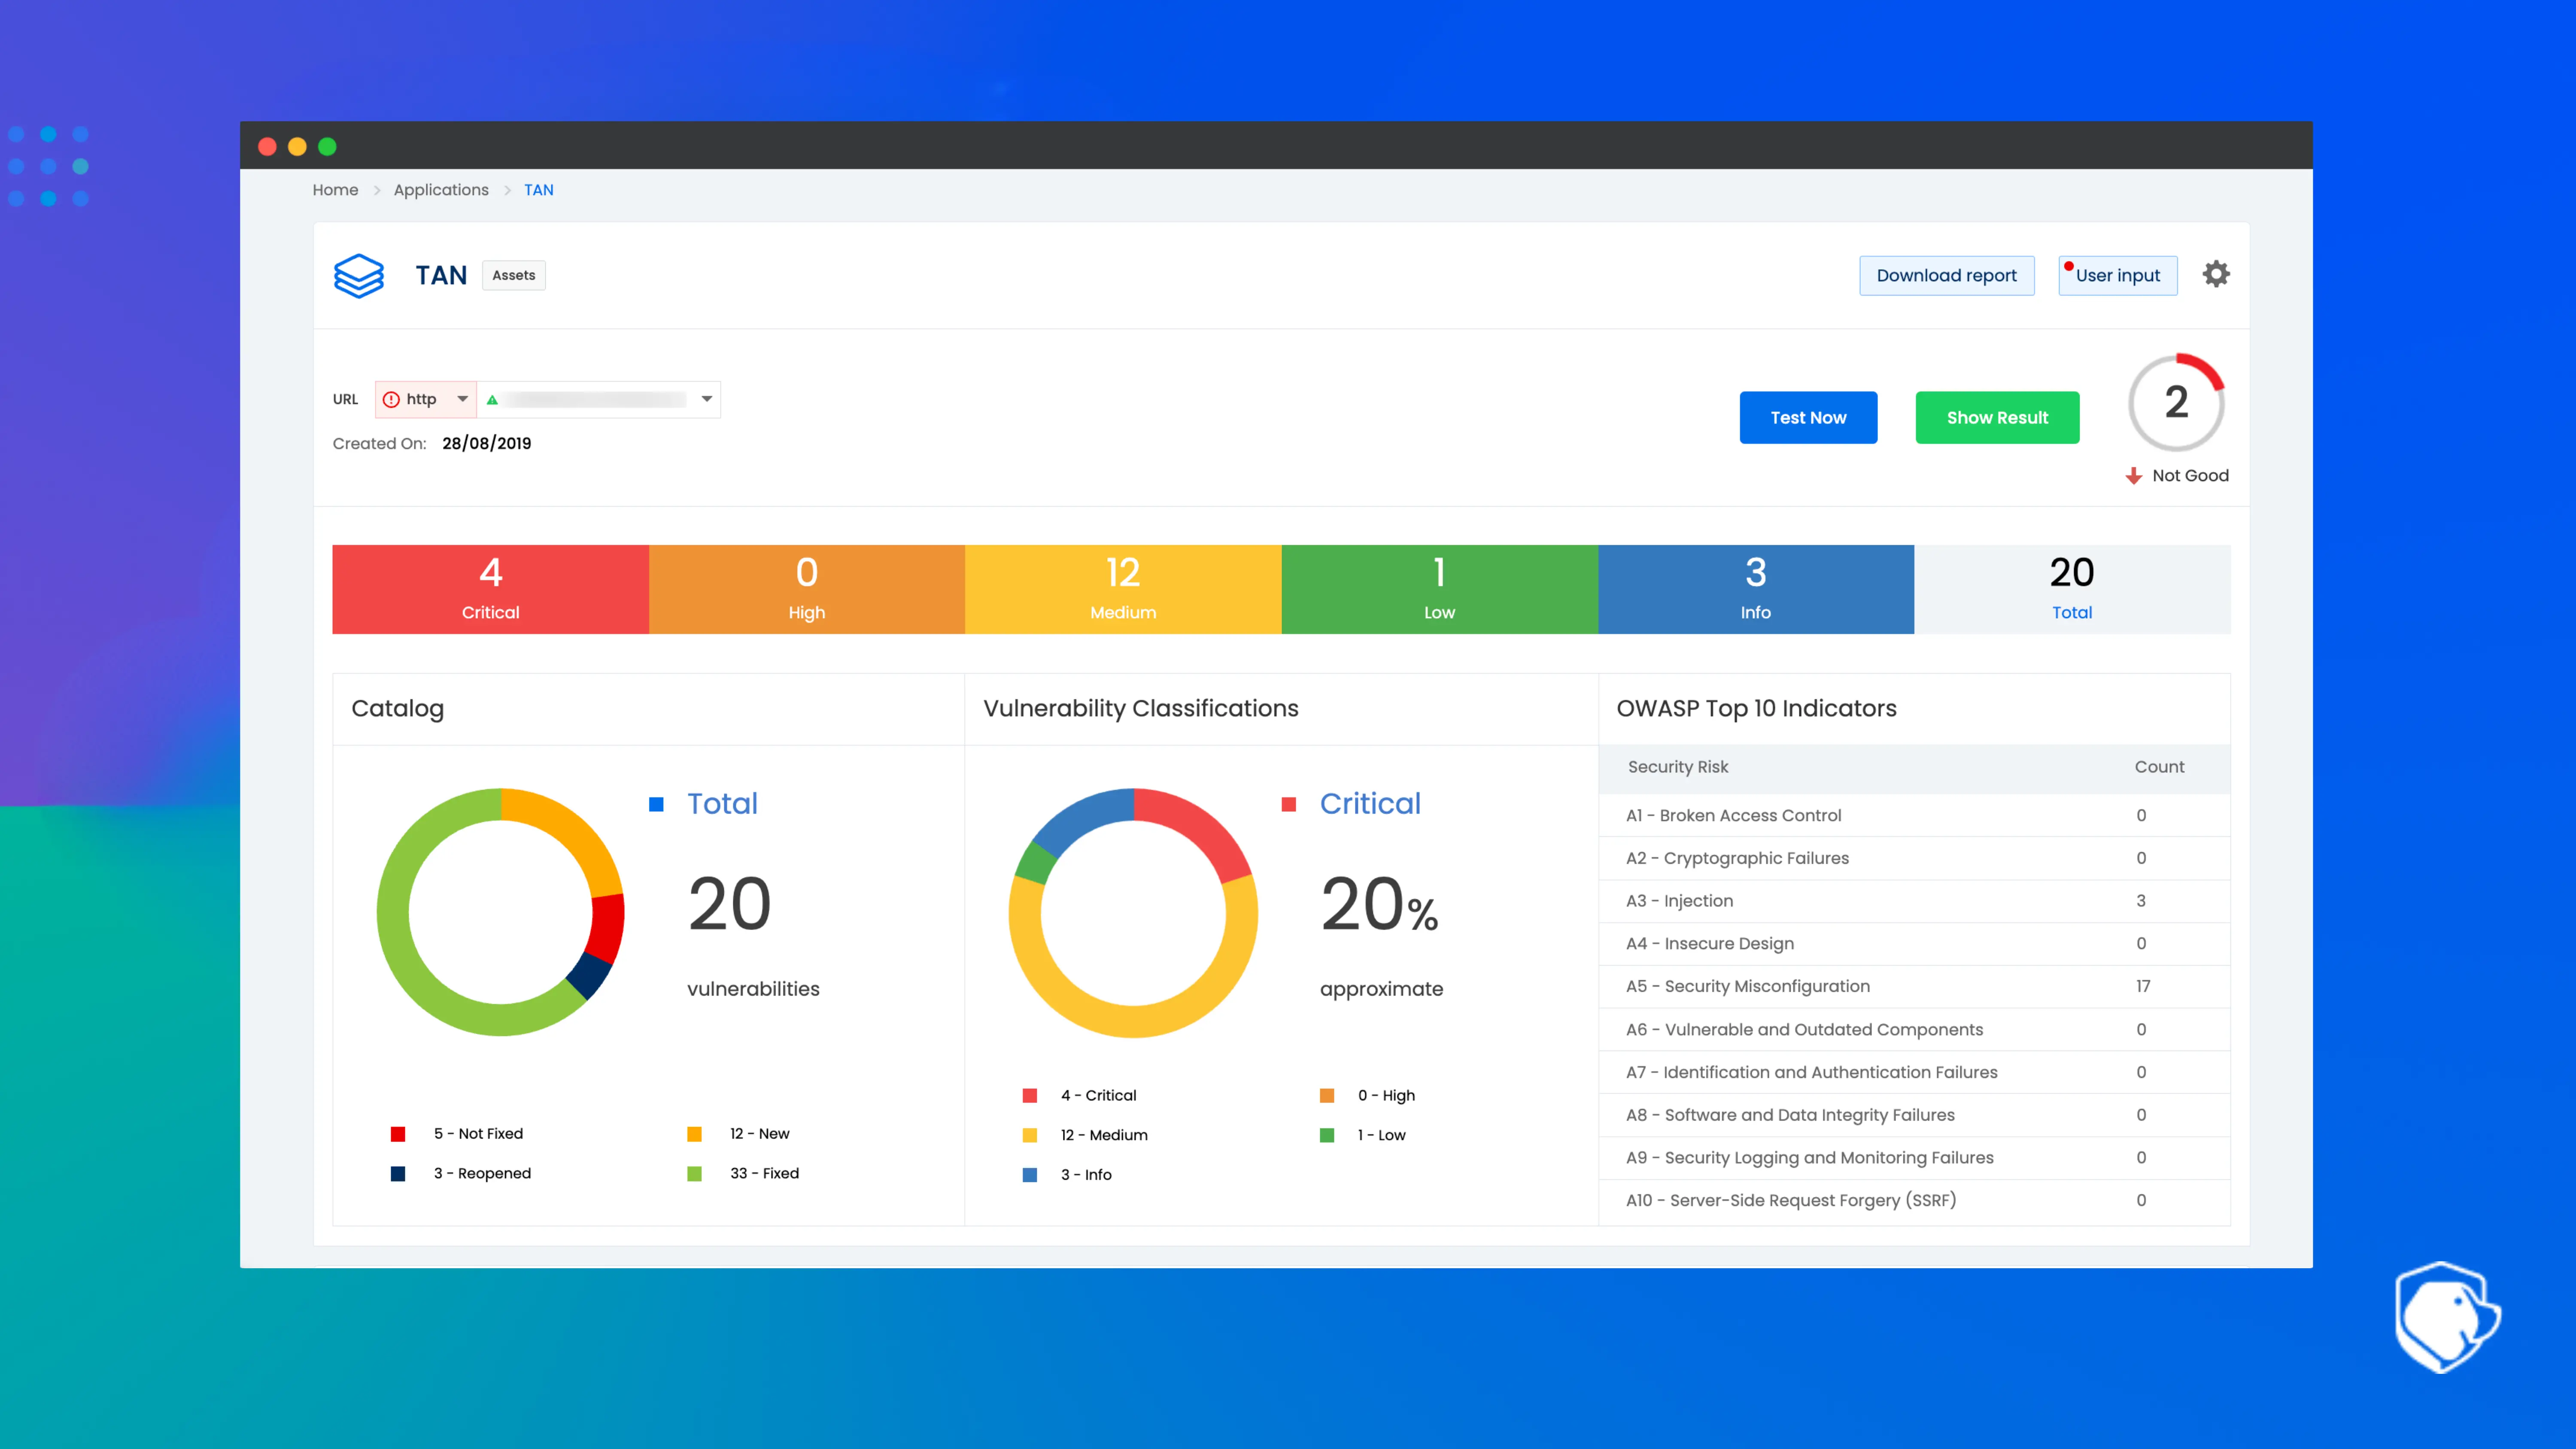
G2 rating: 4.7/5 based on 87 reviews.
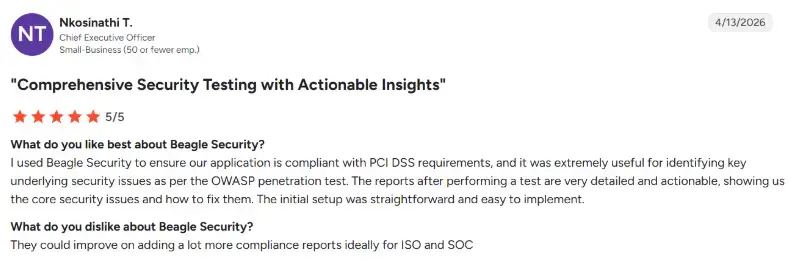
Main features of Beagle Security:
Agentic AI penetration testing
GraphQL and API security coverage
Vulnerability prioritization with a low false positive rate
Compliance-ready reports (HIPAA, PCI DSS, OWASP)
Tenable One Vulnerability Management pricing
Tenable One Vulnerability Management (formerly Tenable.io) is Tenable’s cloud-based vulnerability management product. Estimates for entry pricing vary widely by source, roughly $3,700 to $7,000+ per year for around 100 to 250 assets, with cost increasing as you scale further.
Given how much these estimates diverge, getting a direct quote is the only reliable way to know your actual cost.
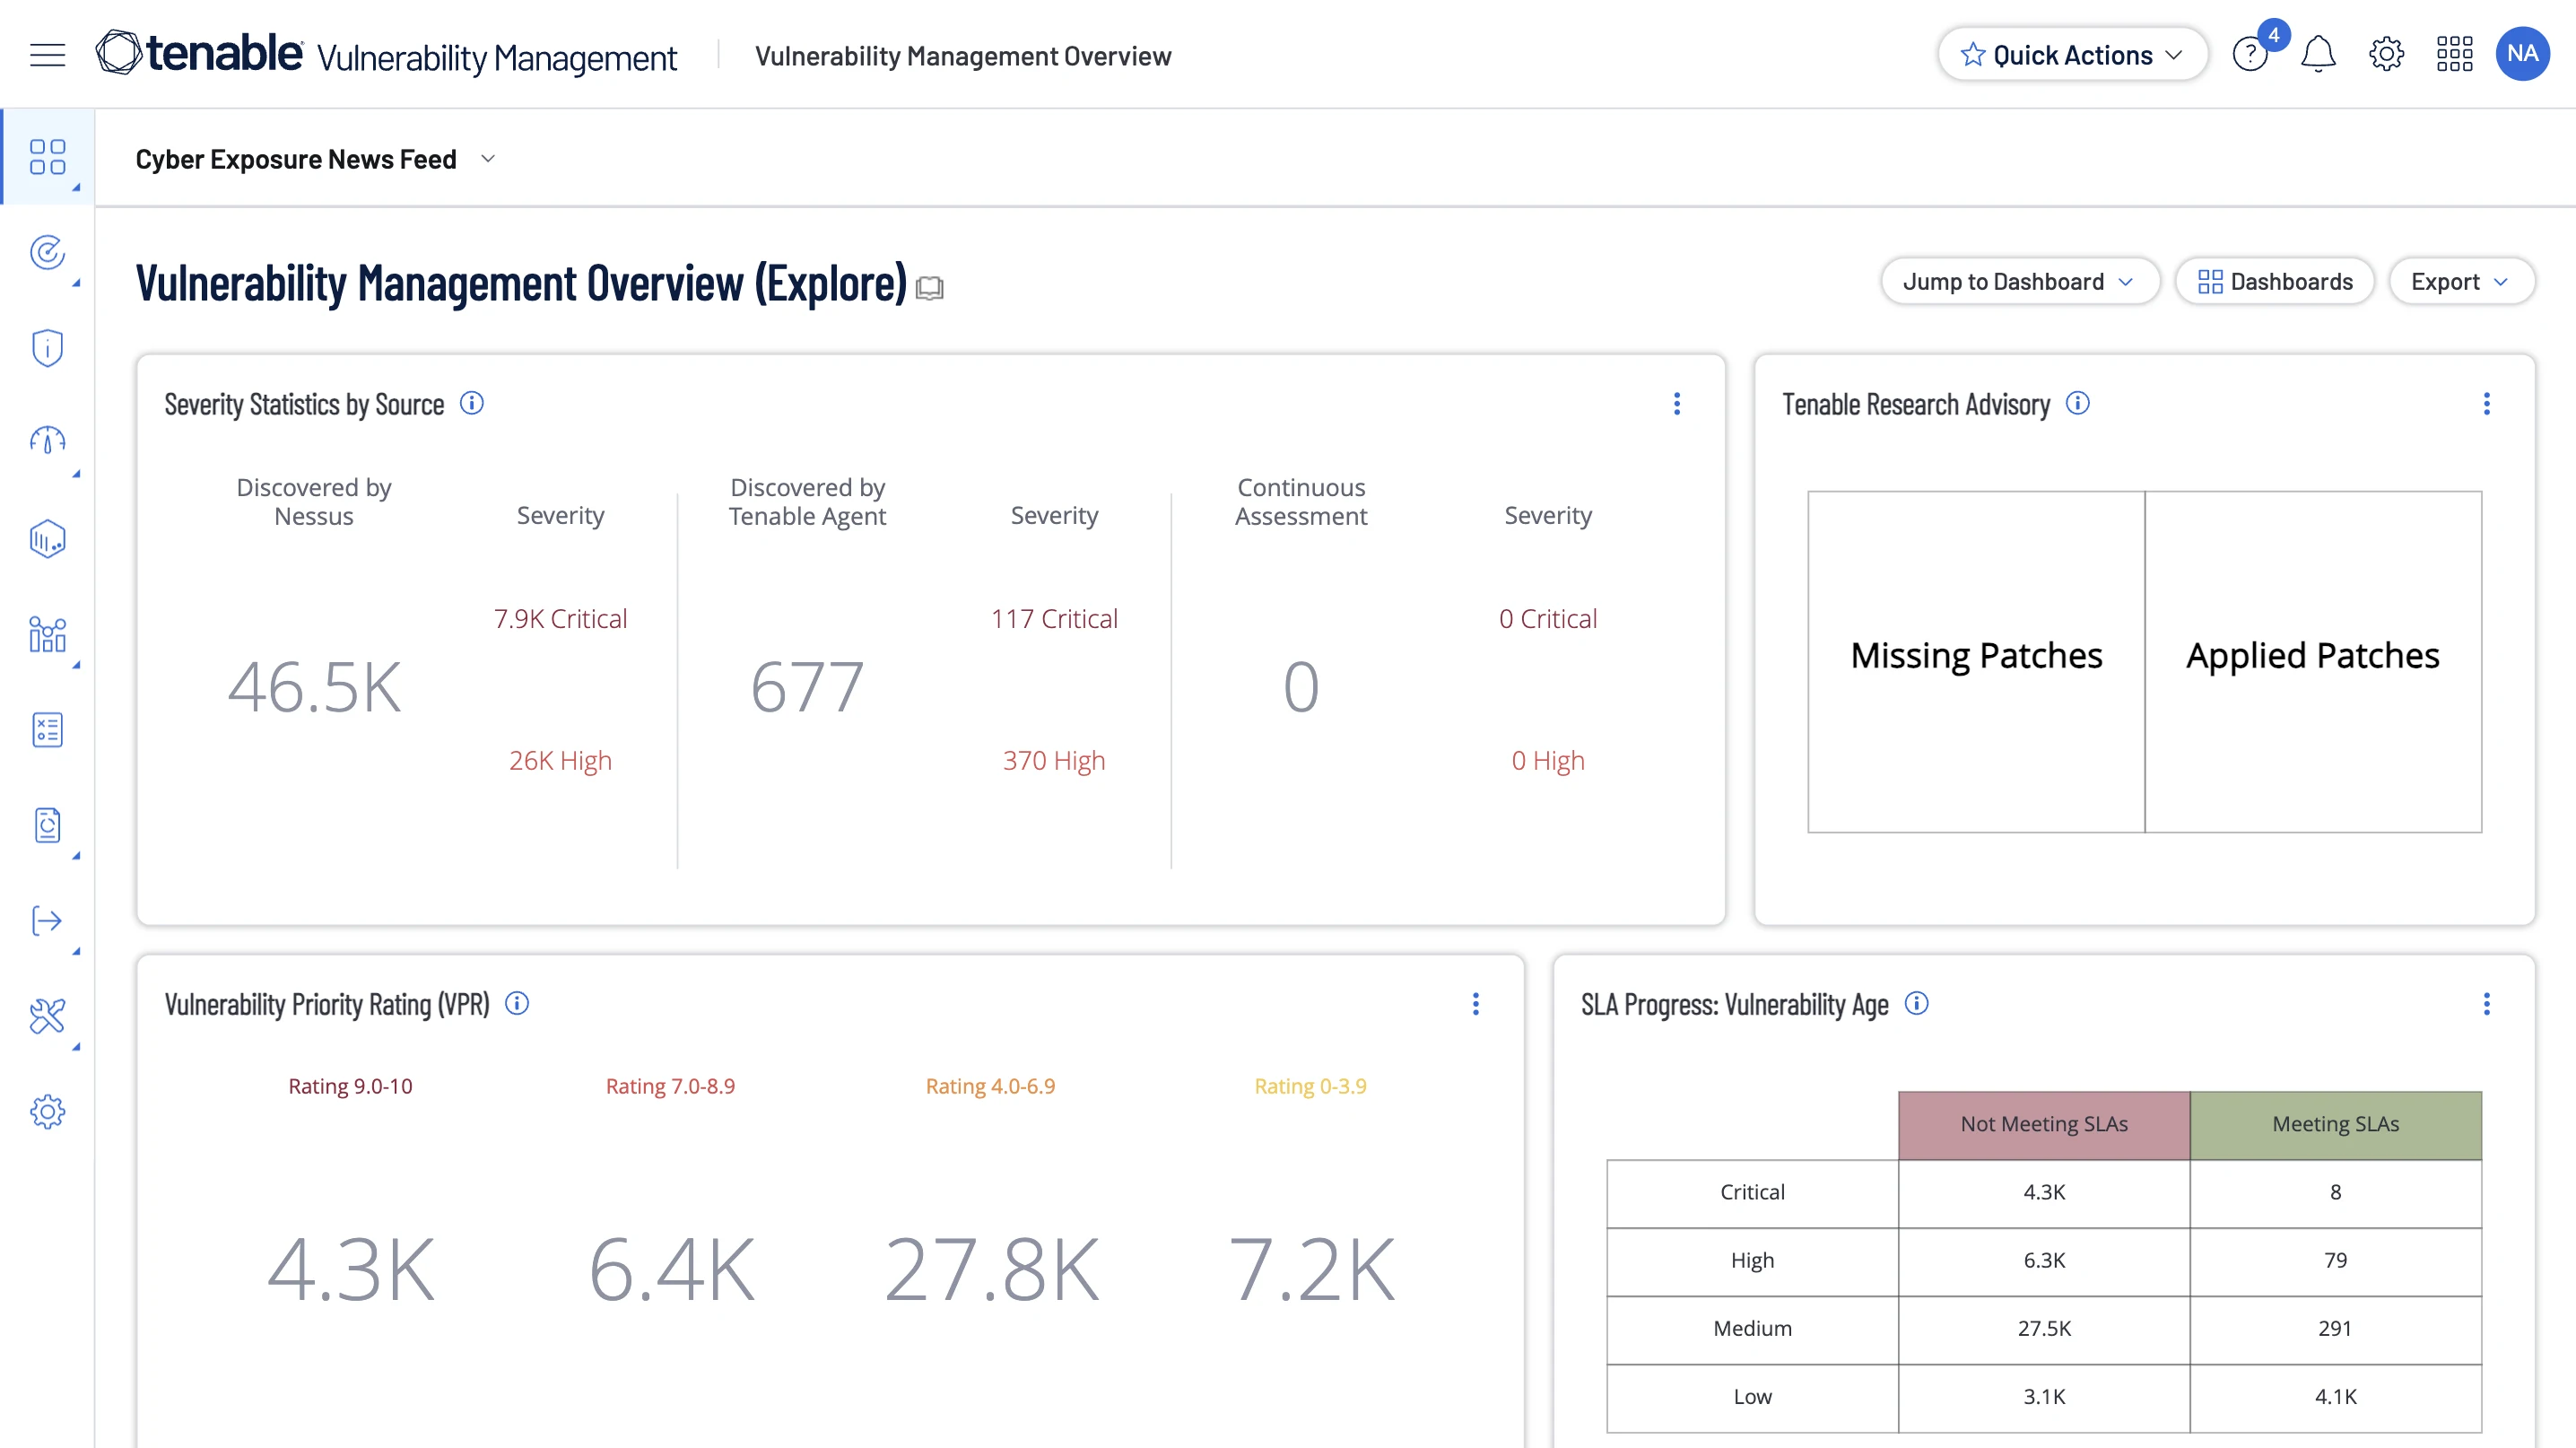
Main features:
Cloud-based vulnerability detection
Asset discovery and inventory
Integration with DevOps tools
Reporting aligned with compliance frameworks
Best Tenable Vulnerability Management alternative: SecOps Solution
SecOps Solution offers broader visibility across hybrid IT and integrates natively with incident response workflows. Compared to Tenable One Vulnerability Management, it’s positioned as offering strong ROI for teams needing continuous monitoring at scale, though pricing is not fixed and depends on asset volume and integrations.
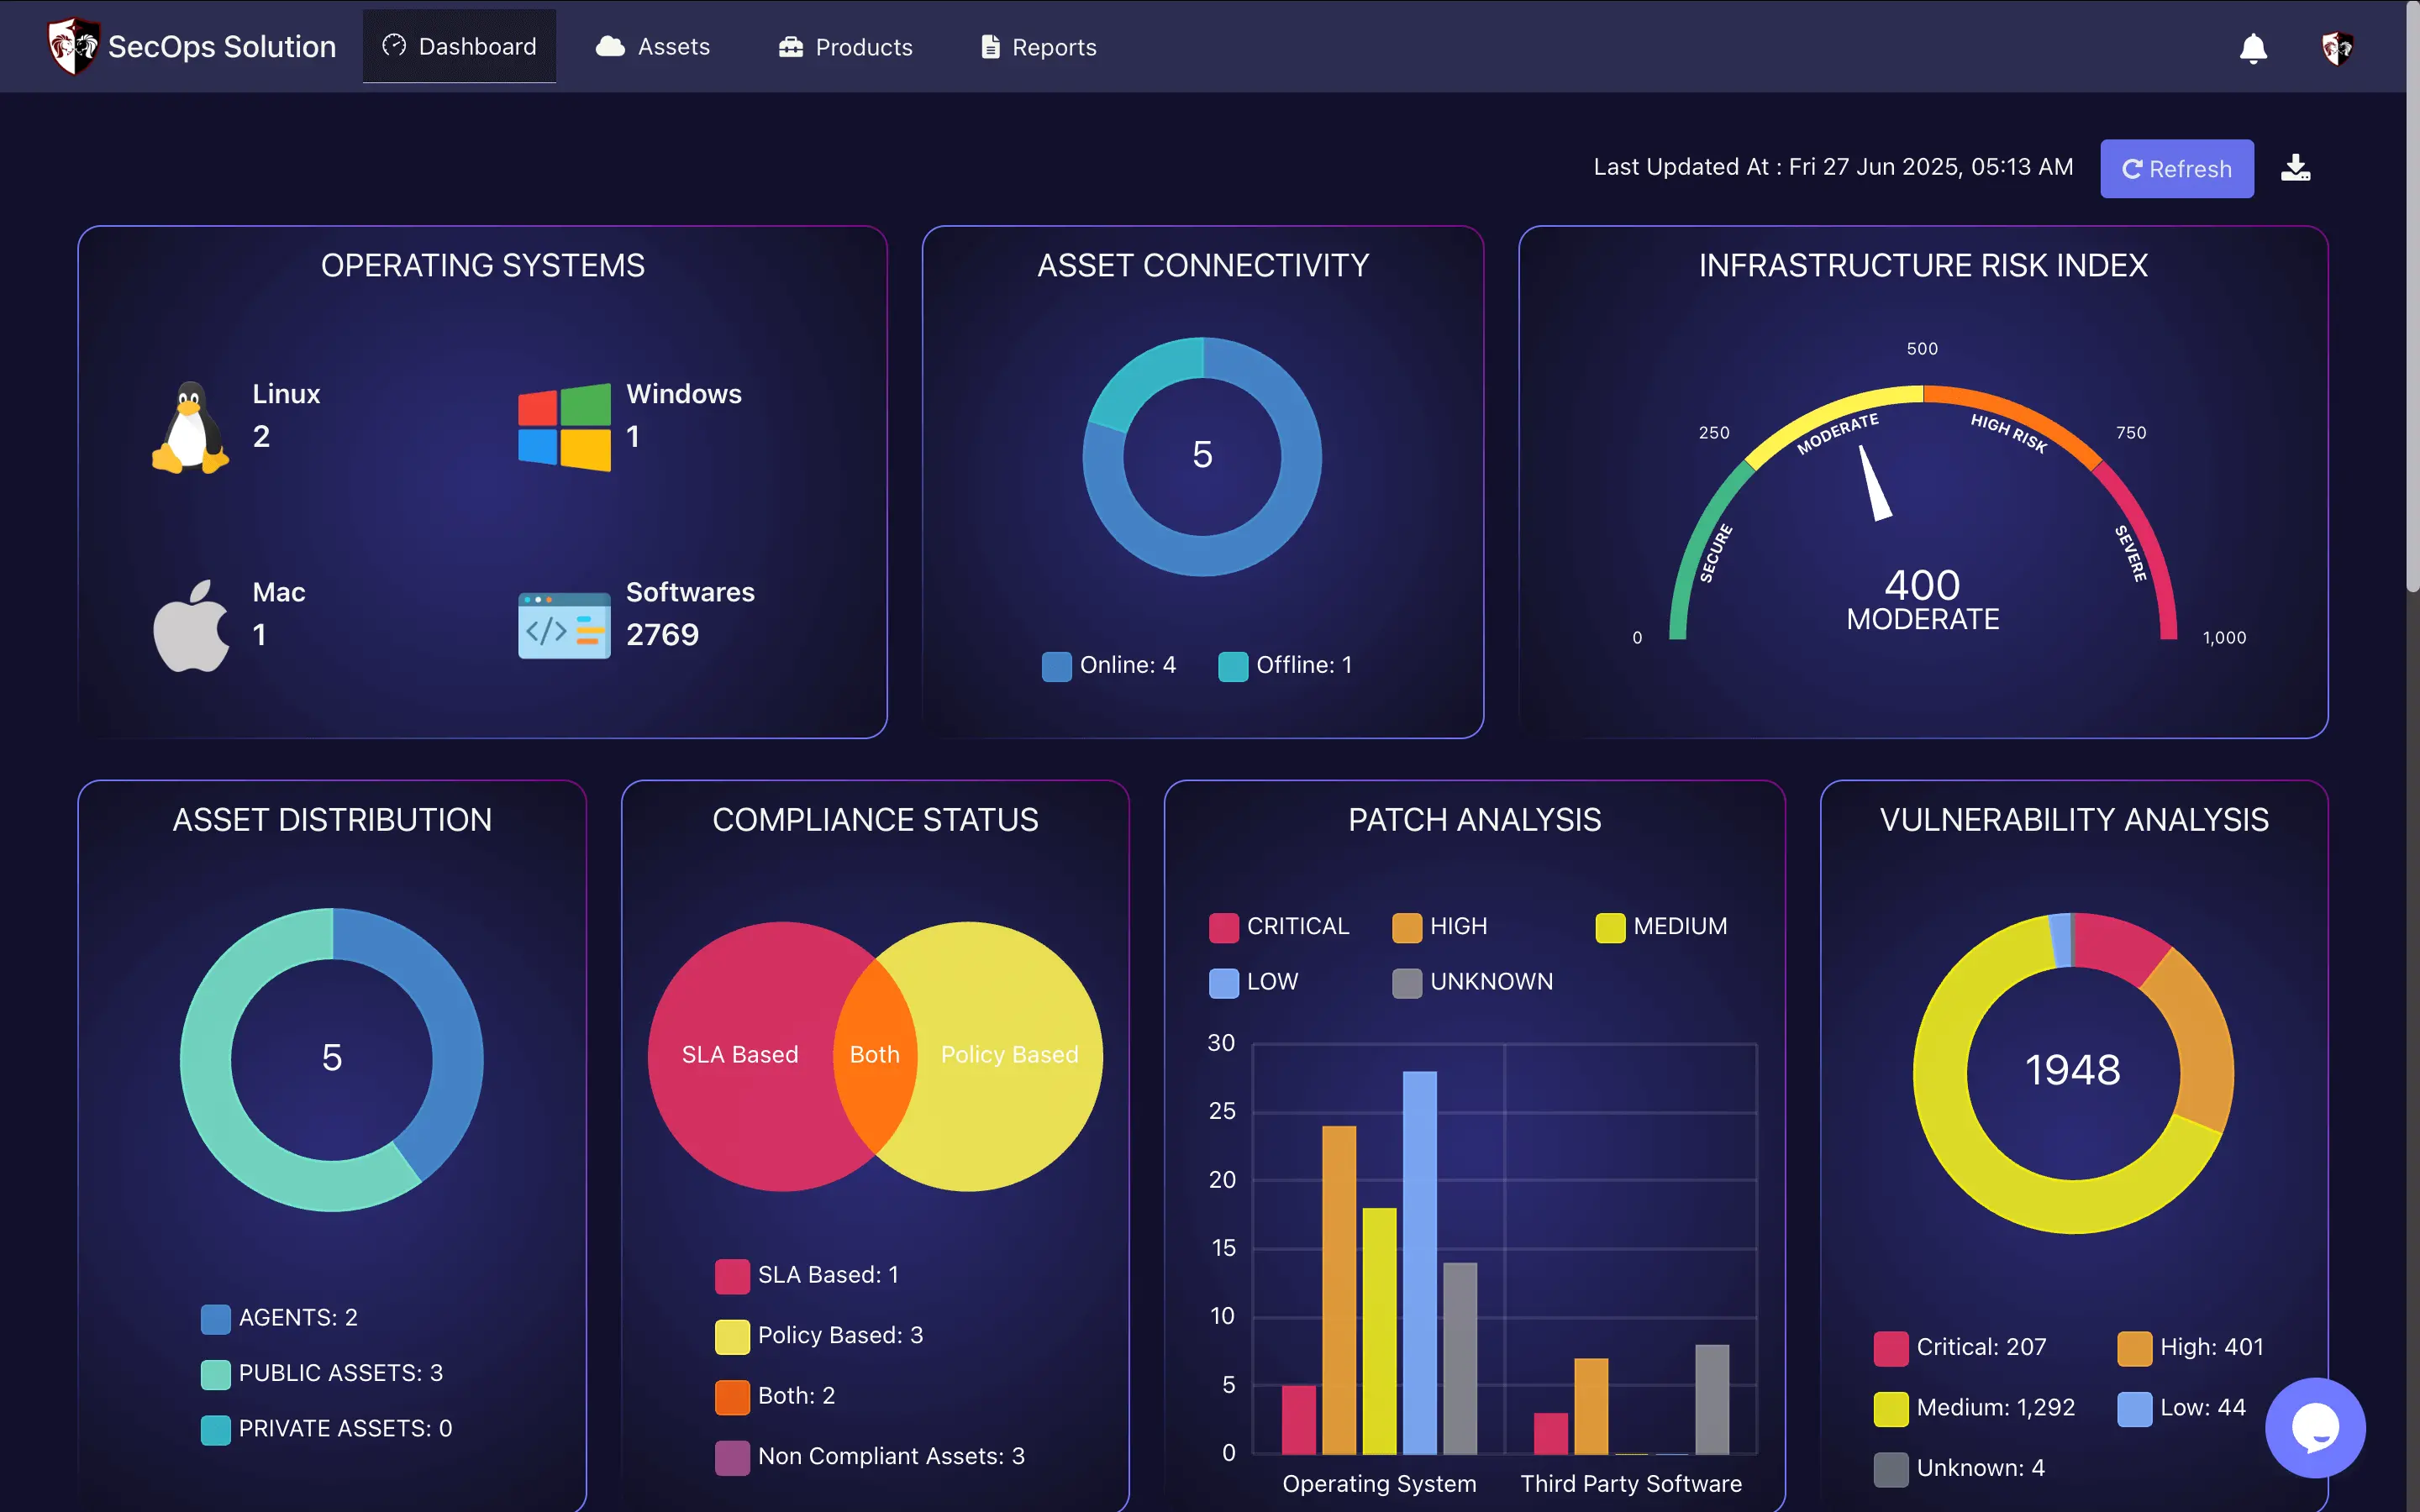
G2 review: 4.8/5 based on 37 reviews

Main features of SecOps Solution:
Continuous asset discovery and vulnerability detection
Built-in remediation tracking
Cloud and on-premise coverage
Executive dashboards and SLA tracking
Tenable Cloud Security pricing
Tenable Cloud Security is built for organizations securing cloud-native environments. Pricing is only available on request, and generally scales with the number of billable resources running in your cloud.
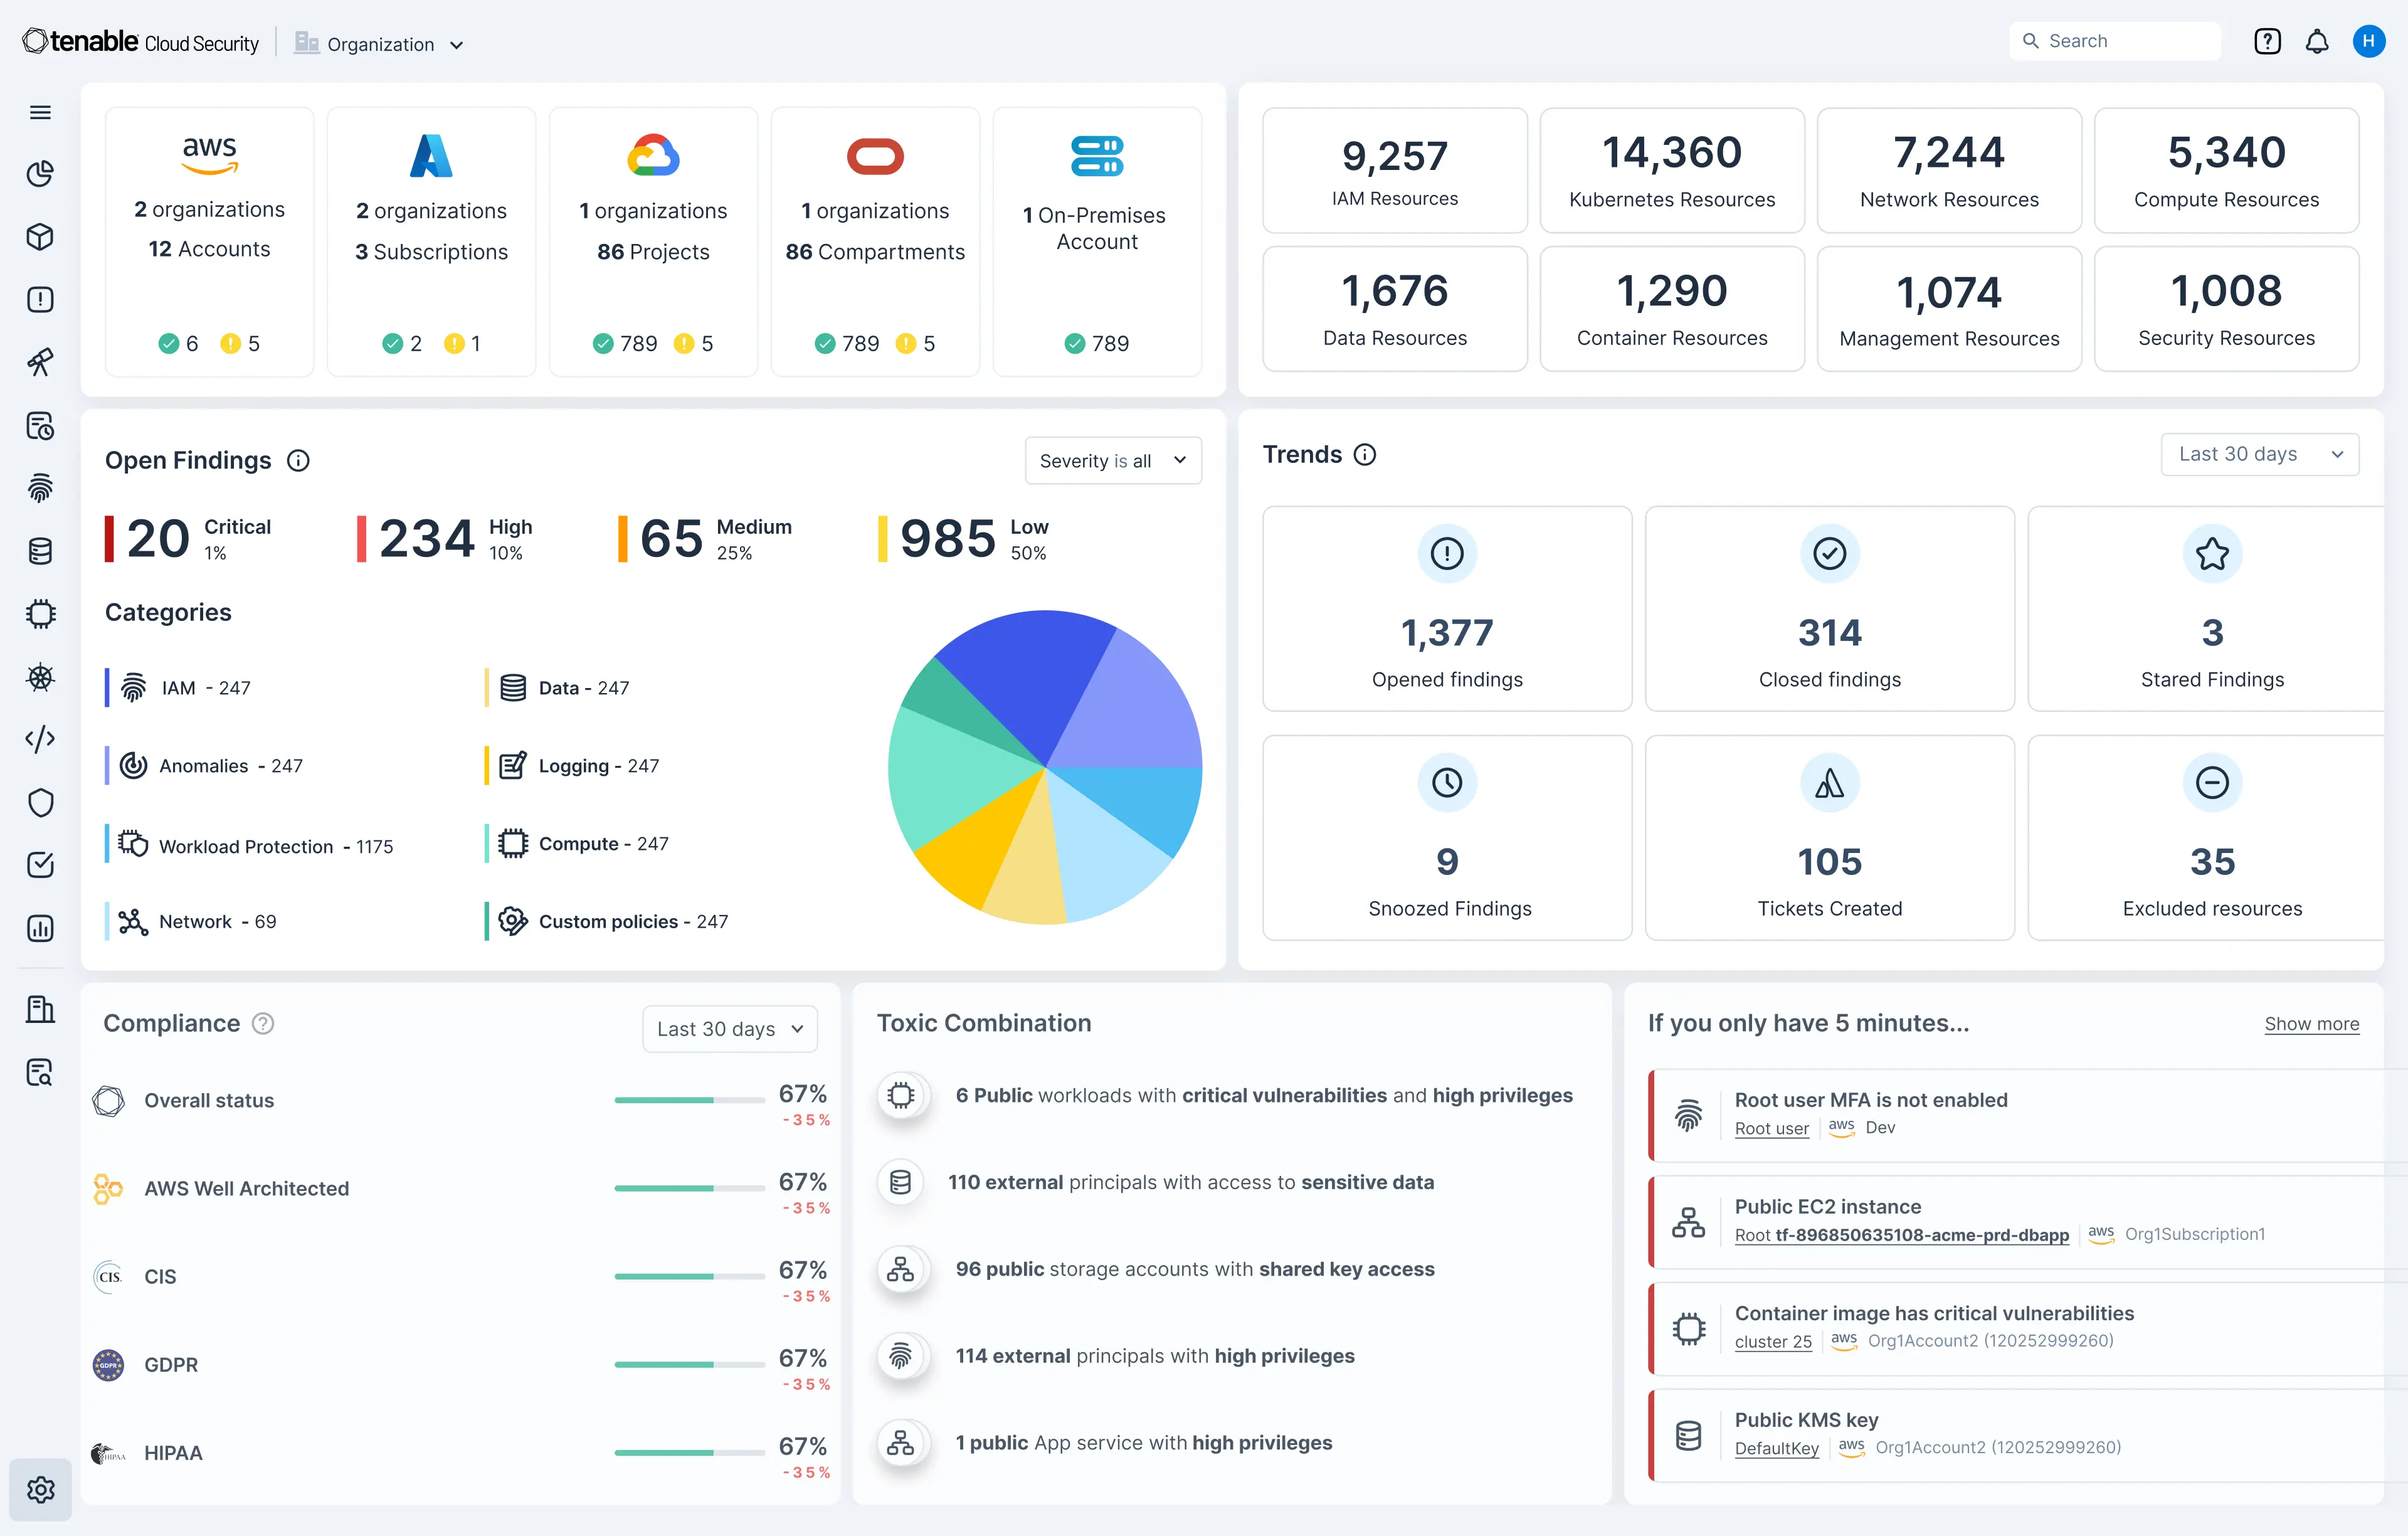
Main features of Tenable’s Cloud Security offering:
Visibility across AWS, Azure, and Google Cloud
Cloud misconfiguration detection
Compliance monitoring for cloud security standards
API-level integrations with CI/CD pipelines
Best Tenable Cloud Security alternative: Orca Security
Orca Security provides agentless cloud security, which generally means faster time to value and easier deployment compared to Tenable Cloud Security. It offers broad workload coverage with less deployment complexity.
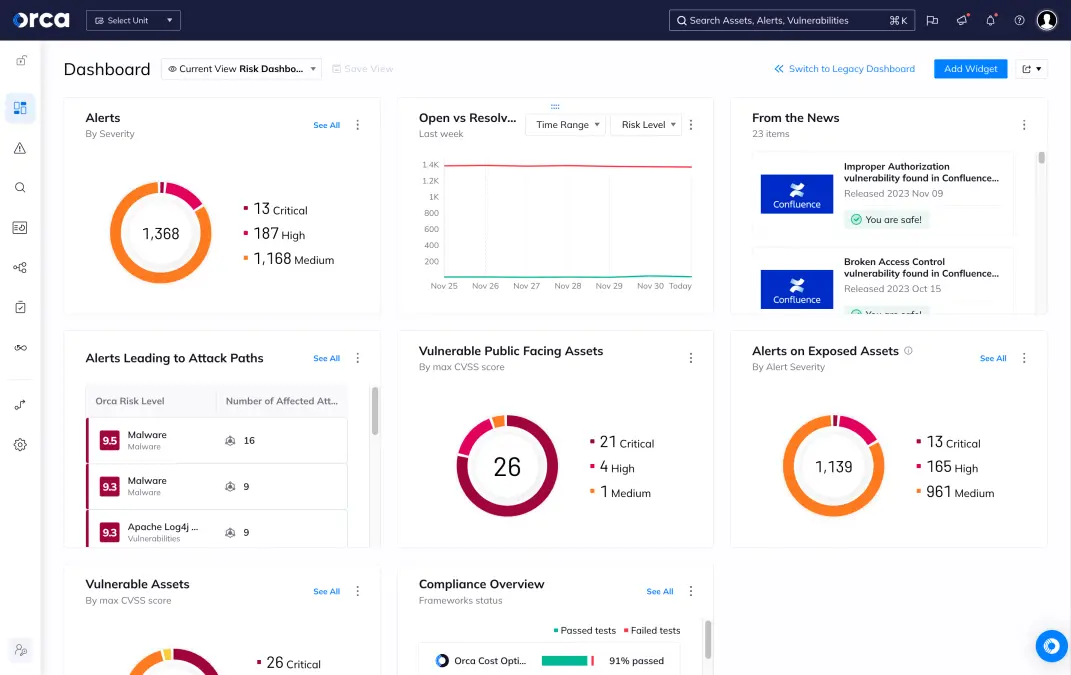
G2 rating: reported around 4.7/5 from 314 reviews.

Main features of Orca Security:
Agentless, full-stack cloud security coverage
Real-time risk prioritization
Cloud compliance reporting
Integration into DevSecOps pipelines
Tenable One pricing
Tenable One is Tenable’s unified exposure management platform, bundling most of its individual products into one license. Third-party estimates put entry pricing at roughly $50,000 or more annually, scaling with the number of assets and features licensed.
Main features of Tenable One:
Unified risk visibility across IT, cloud, and applications
Exposure analytics for executives
Asset inventory and contextual risk scoring
Integrations with SIEM, SOAR, and ITSM tools
Best Tenable One alternative: Qualys
Qualys takes a modular approach to exposure and vulnerability management, letting organizations pick features on demand rather than committing to a single bundled platform. This can offer better cost efficiency depending on what you actually need.
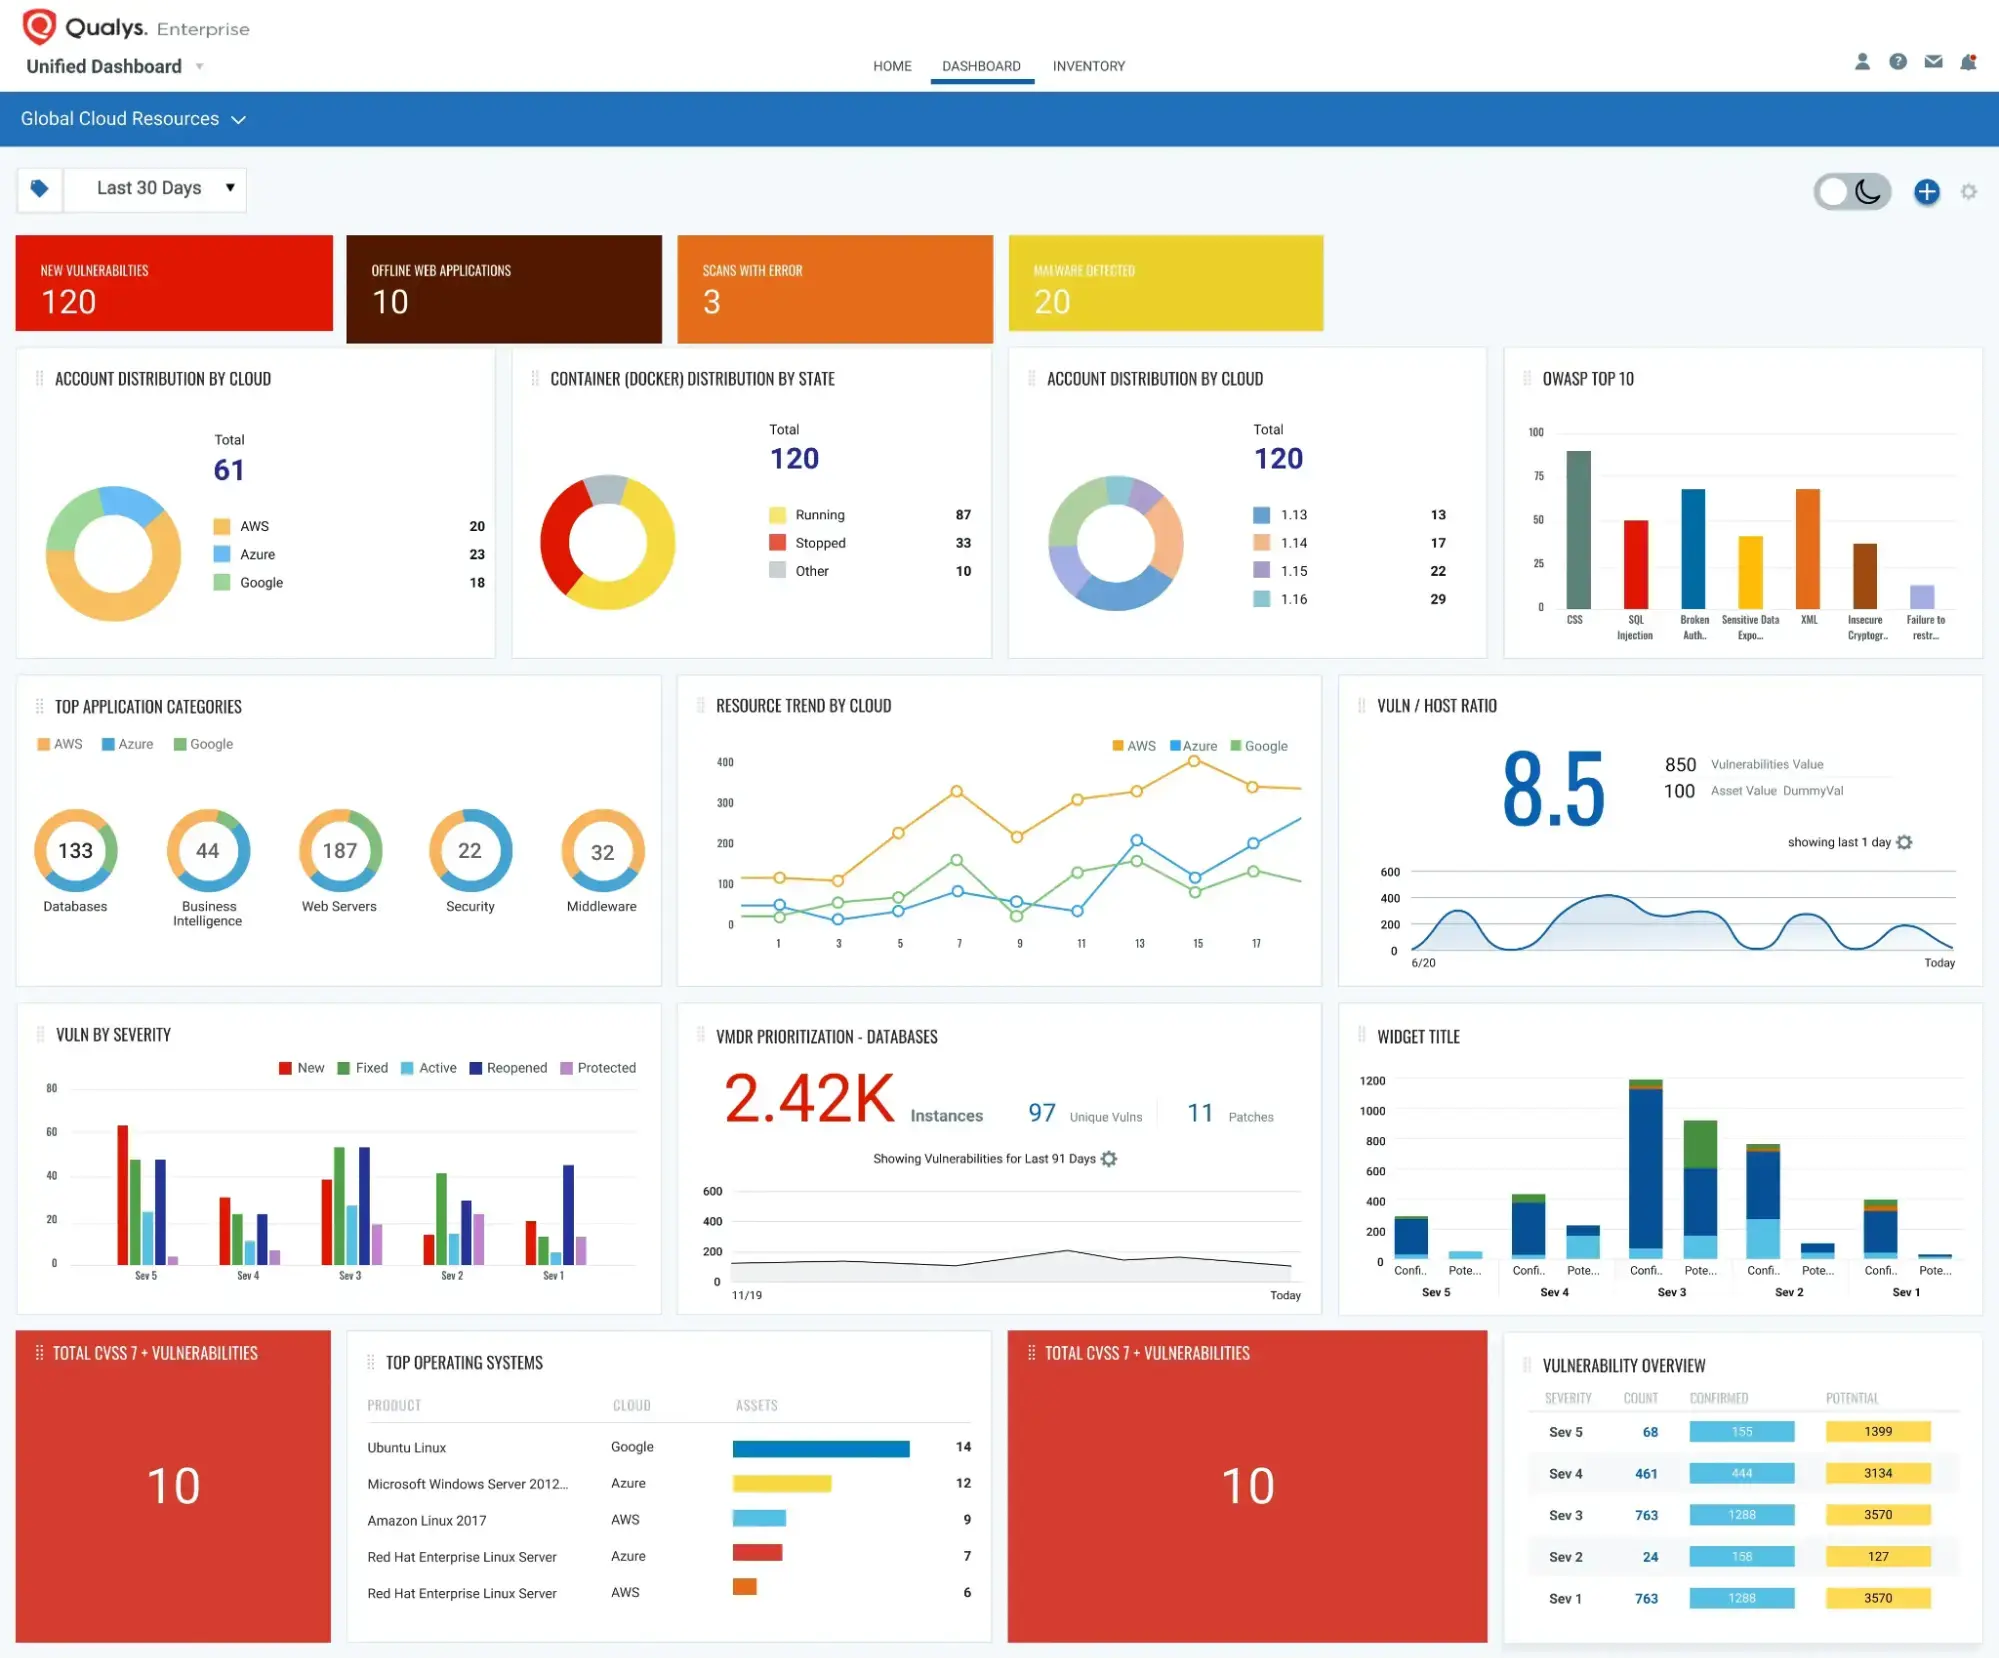
G2 rating: reported in the 4.3 to 4.5 range depending on the specific Qualys product listing.

Main features of Qualys:
Modular vulnerability and compliance offerings
Cloud-native platform
Global asset discovery and visibility
Detailed executive and compliance reporting
Factors influencing Tenable pricing
| Factor | How it affects cost |
|---|---|
| Number of assets (licensing volume) | Most Tenable products scale by asset count or applications tested |
| Product type and features | Bundled platforms like Tenable One cost significantly more than single products |
| Licensing model | Cloud (subscription-based) versus on-premise (perpetual license plus maintenance) |
| Support and training | Premium support packages add to the base cost |
| Contract duration | Multi-year agreements often lower the effective annual cost |
| Deployment type | On-premise deployments typically carry higher infrastructure and maintenance costs |
Final thoughts
Tenable remains one of the more established names in vulnerability management and application security going into 2026. Its pricing can escalate quickly as organizations scale, though, particularly for asset-heavy enterprises adopting Tenable One.
For smaller and mid-market companies, or teams focused primarily on web application and API security, alternatives like Beagle Security, SecOps Solution, Orca Security, and Qualys are worth comparing directly. They often offer more agile deployment, clearer pricing, and more developer-centric features.
The real decision comes down to whether Tenable’s breadth and enterprise track record justify the cost for your organization, or whether a more focused alternative fits your actual risk profile better.
FAQ
How much does Tenable cost in 2026?
Tenable doesn’t publish official pricing. Third-party estimates put Tenable One Web App Scanning around $7,434/year for 5 FQDNs, Vulnerability Management roughly $3,700 to $7,000+/year depending on asset count, and Tenable One starting around $50,000/year. Getting an exact quote requires contacting Tenable sales directly.
What is the pricing of Tenable Web Application Scanning?
Third-party benchmarks estimate Tenable One Web App Scanning (formerly Tenable WAS) at around $7,434 per year for 5 FQDNs, with cost increasing as you add more domains. This is an estimate, not an officially published price.
Does Tenable offer a free trial?
Tenable offers trials for several products, including Vulnerability Management and Web App Scanning, available by request through its site. Trial length and included features can vary, so it’s worth confirming current terms directly with Tenable.
What is the difference between Tenable WAS and Tenable Vulnerability Management?
Tenable One Web App Scanning (formerly Tenable WAS) focuses specifically on finding vulnerabilities in web applications and APIs. Tenable One Vulnerability Management (formerly Tenable.io) covers broader infrastructure and asset vulnerability scanning across IT, cloud, and hybrid environments.