Top GitLab DAST alternatives [2026]
As organizations increasingly embed application security into their DevSecOps pipelines, GitLab’s built-in DAST capabilities may not always meet every requirement. Whether you need deeper scanning, richer API/GraphQL support, better developer workflow integration, or enterprise-scale reporting, many teams evaluate GitLab DAST alternatives.
This article compares ten leading Gitlab DAST alternatives, alongside a comparison table showing starting pricing, strengths and use-cases. Use this guide to find the right tool to complement (or replace) GitLab’s native DAST.
Comparison table
| Tool | Starting price | Strengths | Useful for |
|---|---|---|---|
| Beagle Security | $119/month (entry) | Agentic AI pentesting, API/GraphQL focus | DevSecOps teams, modern web/API stacks |
| Acunetix | $7,000/year | Affordable web/API scanner | Smaller teams, budget constrained |
| Invicti (formerly Netsparker) | $7,000/year (5 targets), as per AWS marketplace | Proof-based scanning, low false positives | Web-app heavy orgs needing accuracy |
| Rapid7 InsightAppSec | $175/month/app | Cloud DAST, broad app support | Teams already using Rapid7 stack |
| Burp Suite | Quote (professional edition) | Manual & automated DAST + interactive testing | AppSec engineers needing deeper testing |
| ZAP (ZAP by Checkmarx) | Free/Open-source | Cost free, flexible scripting | Security-savvy teams on limited budget |
| Bright Security | Custom pricing | Developer-centric DAST, low false positive promise | Dev-first orgs, API-centric architecture |
| Tenable WAS | $7,000+/year (5 FQDNs) | Risk-based DAST, Tenable integration | Mid-/large orgs scanning multiple apps/APIs |
| Veracode DAST | $20,000 - $25,000/year(according to UnderDefense) | Enterprise AppSec platform, DAST and more | Regulated sectors, governance focus |
| HCL AppScan | $299 per scan (small) / enterprise license | Mature enterprise suite (DAST+SAST) | Large enterprises with broad AppSec needs |
Top GitLab DAST alternatives [2026]
1. Beagle Security
Beagle Security is an agentic AI-powered web application and API penetration-testing platform that brings DAST-style scanning into modern DevSecOps workflows. It supports web applications, APIs (including GraphQL), authenticated business-logic flows, and integrates into CI/CD pipelines for continuous testing. The tests yield actionable remediation guidance tailored to your technology stack and map to compliance frameworks like ISO 27001 & SOC 2.
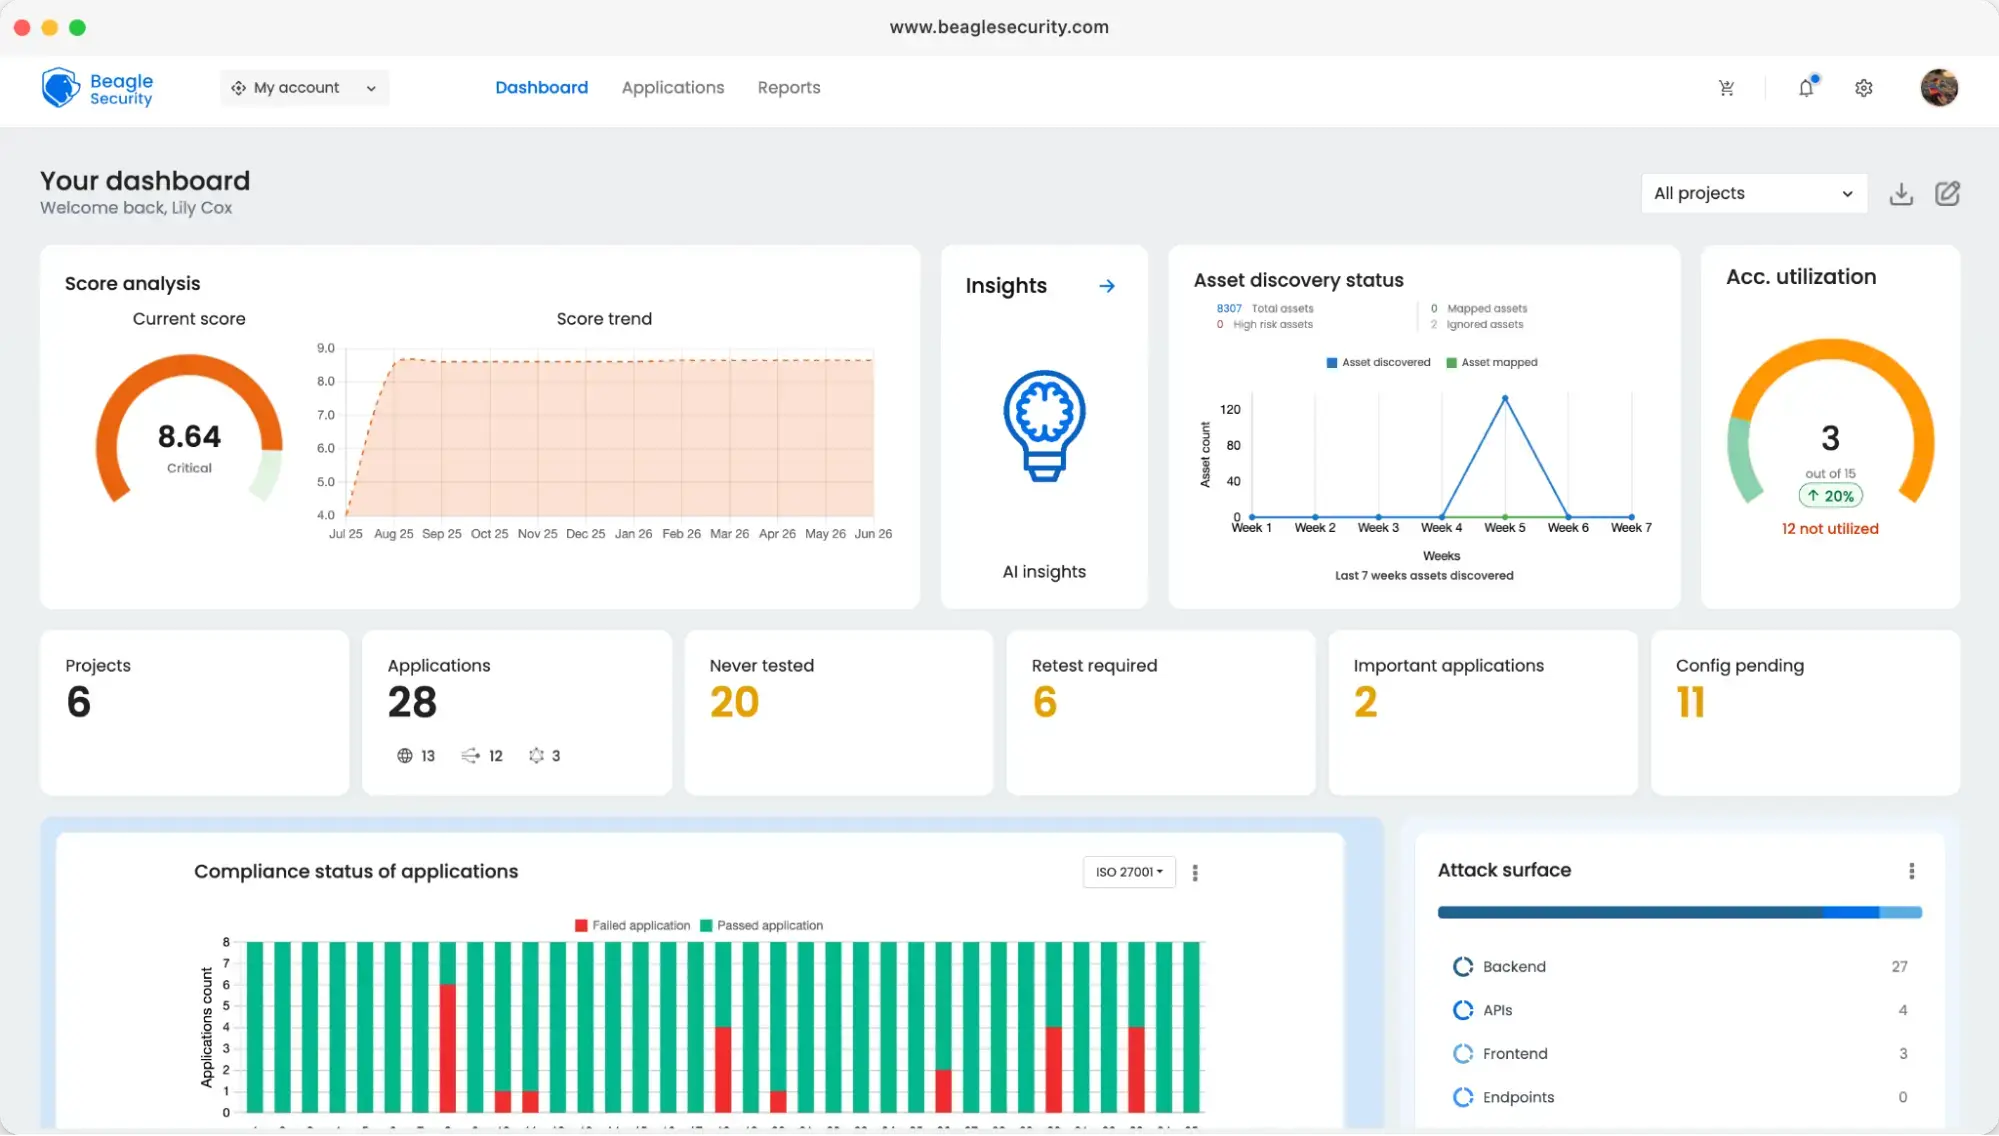
Features
Agentic AI-driven crawl and attack simulation
API & GraphQL scanning support
CI/CD pipeline integration
Authenticated business-logic flow testing
Compliance-mapped remediation reports
G2 review summary
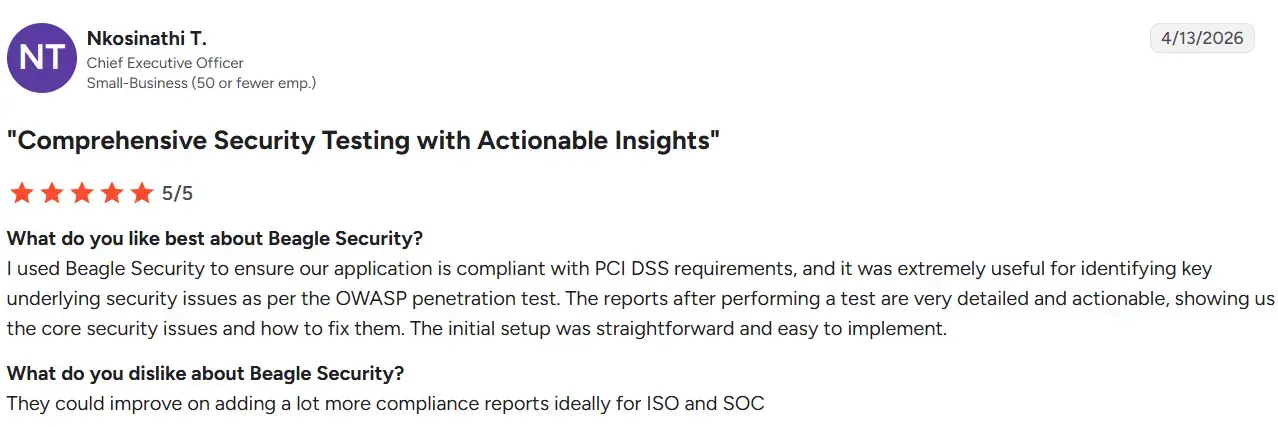
Users report the setup is rapid, the portal intuitive, and the reporting clear, making it a strong pick for teams that want developer-friendly DAST without the heavy enterprise overhead. G2 reviews show a rating of 4.7 stars with comments such as “easy to set up” and “detailed and understandable report”.
Pricing
14-day free trial (no credit card)
Entry tier $119/month
Advanced tier $359/month
Enterprise tiers quoted by vendor (custom)
2. Acunetix
Acunetix is a longstanding web application and API vulnerability scanning solution chosen by many organizations for foundational DAST coverage. It supports modern web frameworks, SPAs, JavaScript-heavy applications, and includes both cloud and on-premises editions.

Features
Web app & API vulnerability scanning
SPA & JavaScript framework support
On-premises and cloud editions
Weekly vulnerability database updates
Integration with DevOps pipelines
G2 review summary
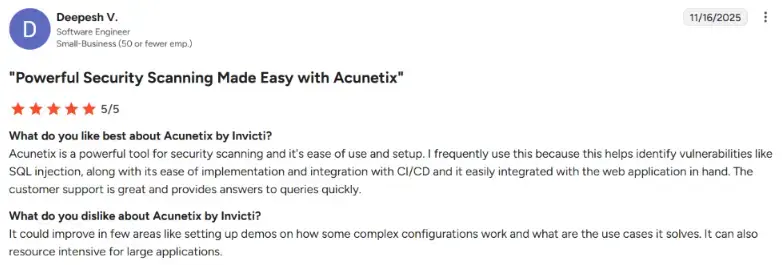
Acunetix has a review on 4.1/5 on G2. Users highlight that Acunetix offers good value and is easier to adopt for small to mid-sized teams, but some note that advanced features (authenticated flows, APIs) may require manual configuration and integration effort. They find it good for getting started with DAST but point out feature limitations compared to high-end enterprise tools.
Pricing
Starting at approximately $1,995/year for 3 targets.
Licensing tiers up to $26,600 for larger packages.
3. Invicti
Invicti (formerly Netsparker) is a mature, enterprise-grade DAST platform with emphasis on accuracy, proof-based findings and automation across web applications and APIs. It integrates with CI/CD pipelines and supports both on-premise and cloud deployment models.
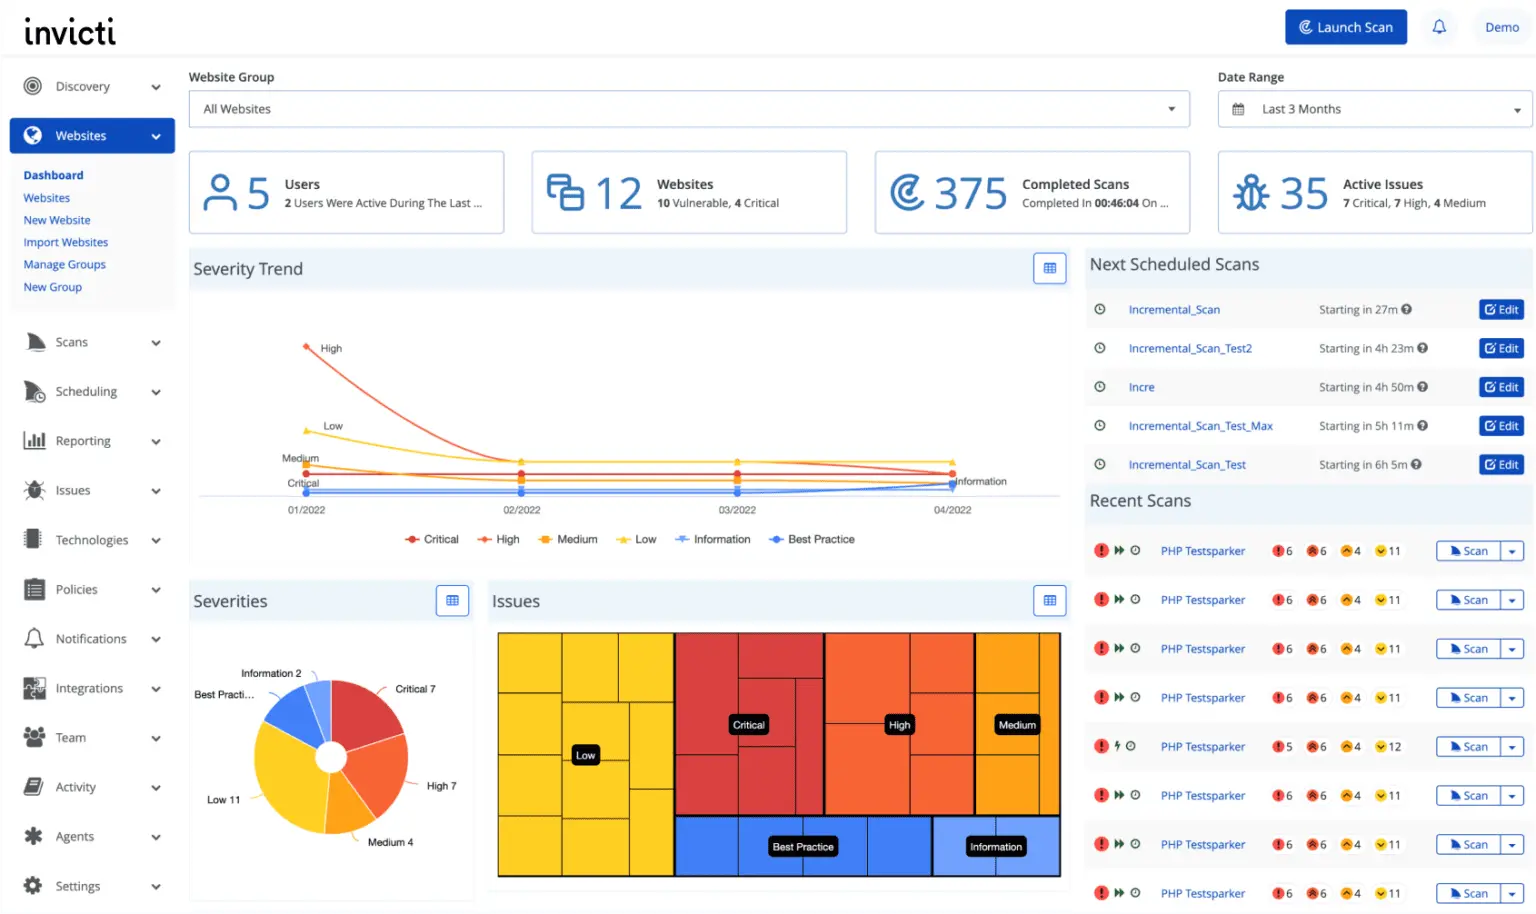
Features
Proof-based vulnerability validation
Web app & API scanning
CI/CD pipeline integration support
On-premises and cloud deployment
Low false-positive rate claims
G2 review summary
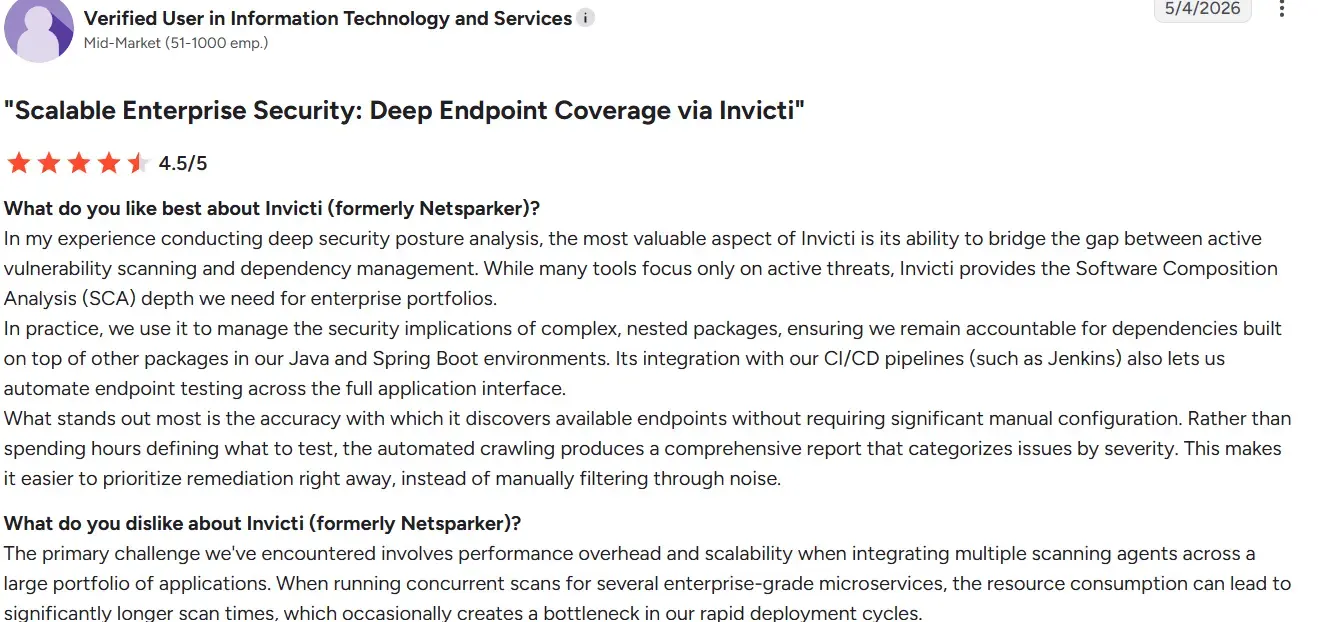
Invicti has a rating of 4.6 on G2. Verified user reviews show good satisfaction around ease-of-use, low false positives, and broad vulnerability detection. Some mention slower performance on large scans and limitations on endpoint testing/2FA flows. Users also note that some advanced API or 2FA test scenarios may require additional setup.
Pricing
Example listing: $7,000/year for 5 targets.
Larger enterprise quotes available per vendor.
4. Rapid7 InsightAppSec
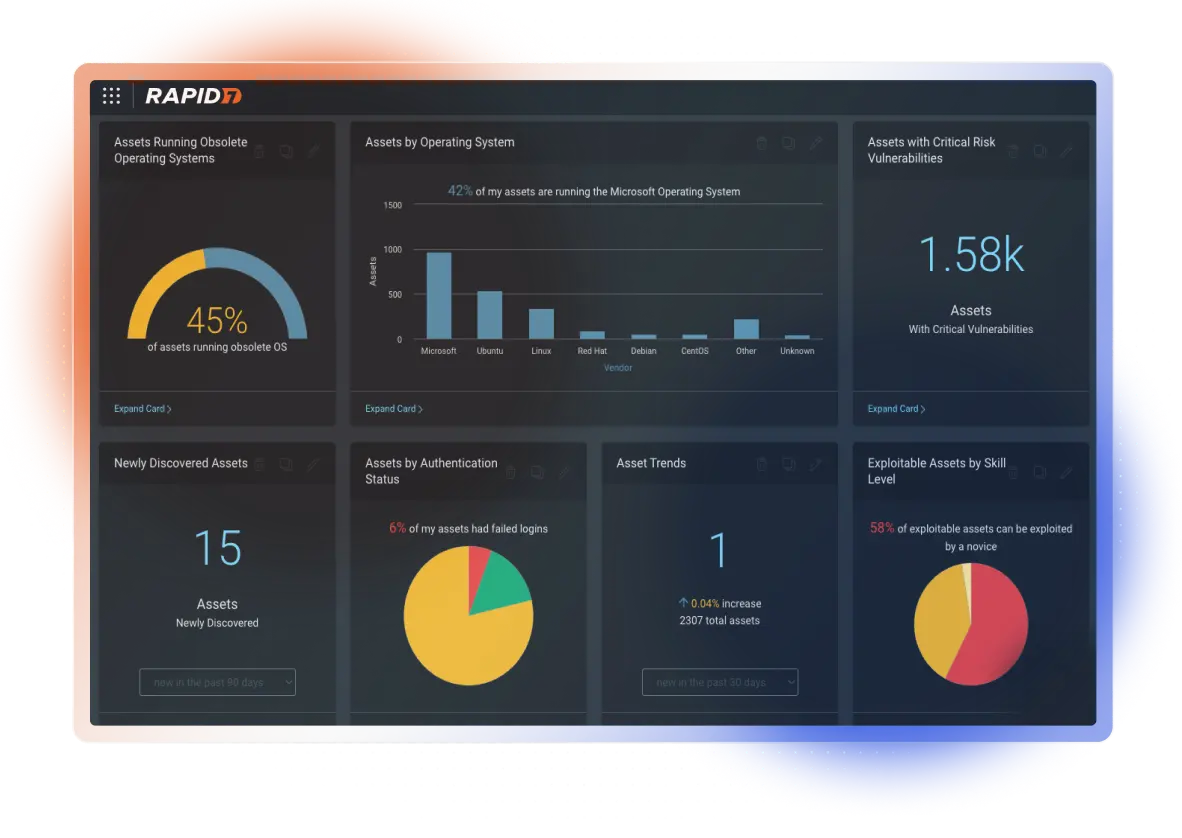
Rapid7 InsightAppSec is Rapid7’s cloud-based DAST solution designed to integrate into the broader Rapid7 “Insight” platform. It aims to provide dynamic testing of web applications and APIs, integrate with ticketing systems (Jira, ServiceNow), and fit into DevSecOps workflows.
Features
Cloud DAST for web & APIs
Risk scoring & dashboards
CI/CD integrations and automation
Supports scheduling and blackout windows
Integrates with Rapid7 Insight platform
G2 review summary
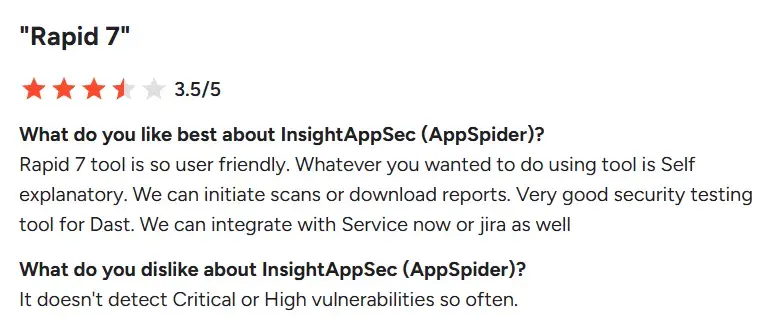
Rapid7 has a rating of 4.3/5 on G2. Users report that InsightAppSec is easy to adopt, works well for scanning multiple applications, and is especially helpful if an organization already uses Rapid7’s security tool-stack. They also highlight good integration capabilities, and effective scanning workflows. On the flip side, as the number of applications grows the cost can scale quickly.
Pricing
Entry example: $175/month per application (publicly referenced)
Full pricing by quote.
5. Burp Suite
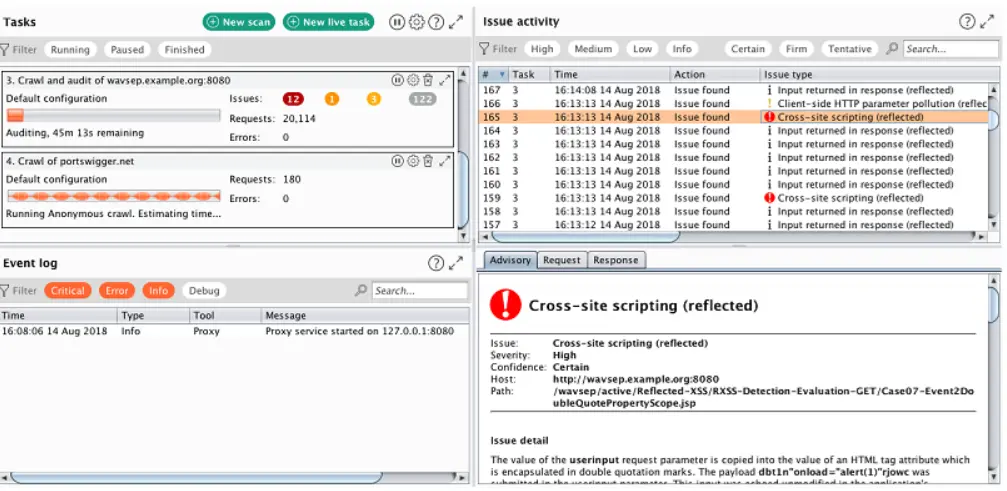
Burp Suite by PortSwigger is a widely-used tool in the AppSec community that combines manual and automated web application security testing. While not purely automated DAST in the same sense as pipeline-integrated DAST scanners, many organizations adopt its “Burp Scanner” automation module to complement CI/CD scans. It is particularly suited to skilled AppSec engineers conducting deeper interactive testing, custom exploitation and business-logic vulnerability discovery. For a team using GitLab’s native DAST, adding Burp Suite can provide manual-plus-automated depth and flexibility for complex applications.
Features
Manual + automated web app testing
Deep interactive/exploitation capabilities
Extensible via plugins and scripts
CI/CD integration optional via API
Business-logic vulnerability focus
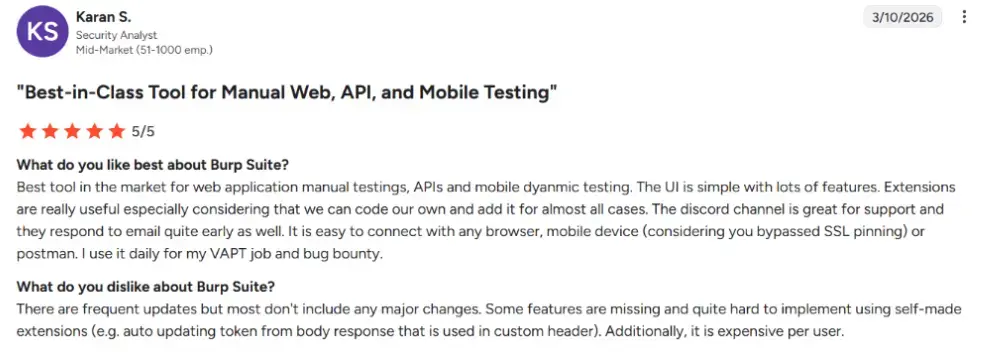
G2 review summary
Burp Suite has a rating of 4.8/5 on G2. It is highly regarded by AppSec professionals for flexibility and power but less suited for teams seeking fully automated pipeline-driven scanning only. They also note the learning curve and cost. Users appreciate the rich feature-set but report that licensing and configuration can require time.
Pricing
Professional edition and enterprise editions quoted by vendors (not widely publicly detailed).
6. ZAP by Checkmarx
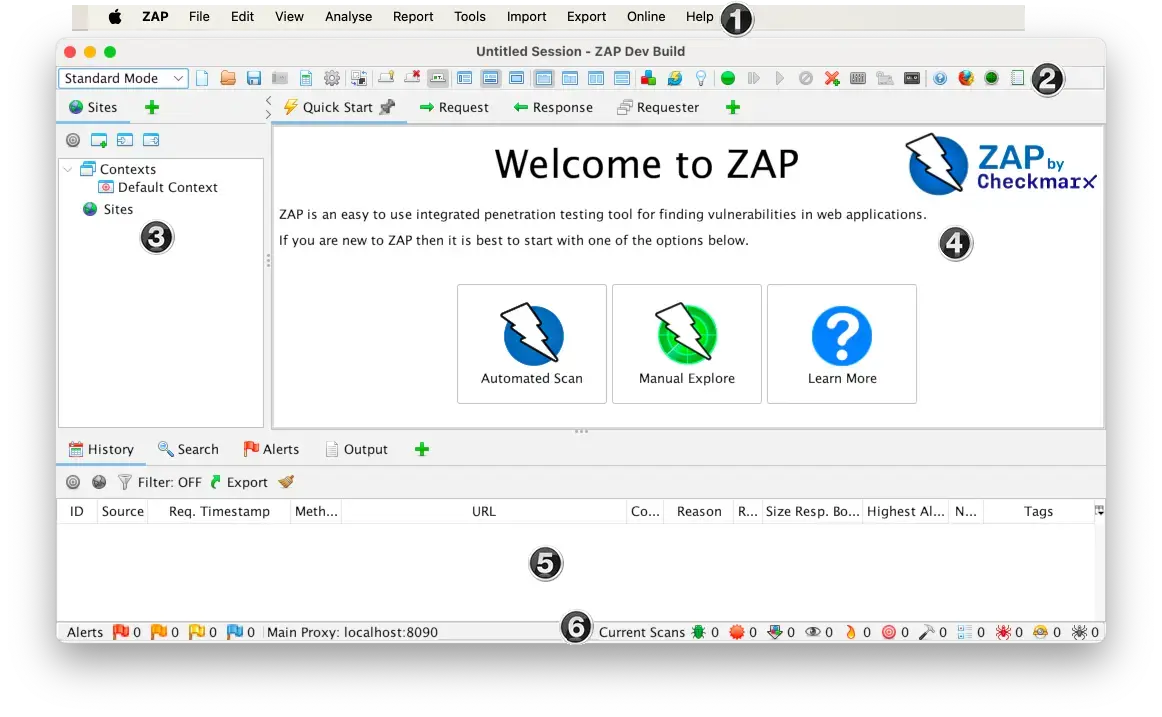
ZAP by Checkmarx (Zed Attack Proxy) is a free, open-source dynamic application security testing tool maintained by the OWASP community. It is a highly flexible scanner with support for web apps, APIs and scripting via its plugin architecture. For organizations using GitLab and looking to supplement its built-in DAST, ZAP can serve as a cost-effective alternative, especially for smaller teams or those with security engineering capability to manage configuration. While lacking some of the enterprise controls, UI polish or vendor support of commercial tools, ZAP remains a robust tool for pipeline integration, custom scans and scripting.
Features
Free/open-source DAST for web & APIs
Plugin and scripting support
CI/CD pipeline integration possible
Supports intercepting proxy & passive scanning
Community-driven vulnerability updates
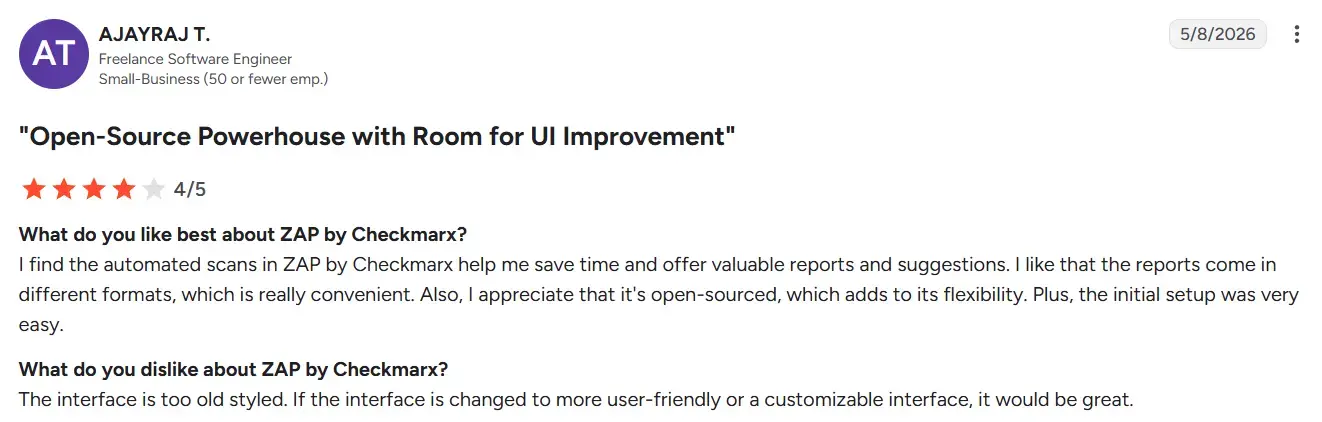
G2 review summary
ZAP by Checkmarx maintains a 4.7/5 on G2. It is praised for being cost-free and flexible but users note the manual configuration effort and sometimes higher maintenance overhead in large organizations.
Pricing
Free (open-source).
7. Bright Security
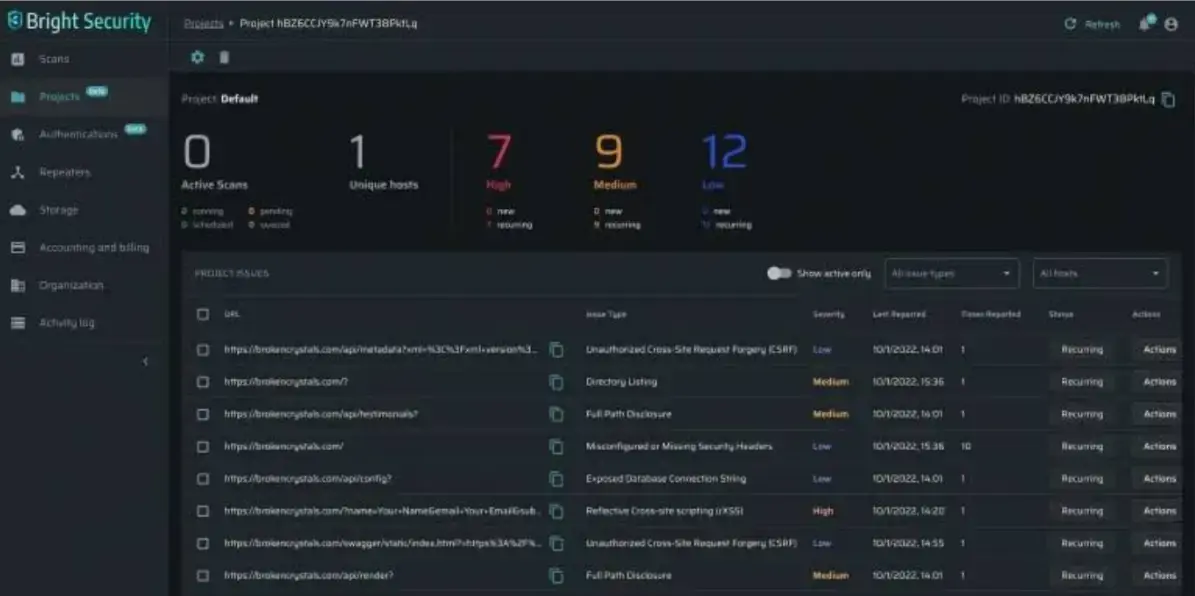
Bright Security is a developer-centric dynamic application and API security testing (DAST) platform that emphasizes automation, low false positives and seamless integration into development workflows. It supports web applications and APIs (REST, GraphQL) and can work inside CI/CD pipelines and IDEs.
Features
Developer-centric DAST for web & APIs
Low false-positive claims with AI
CI/CD and IDE integrations
REST/GraphQL API support
Automated security testing of business logic
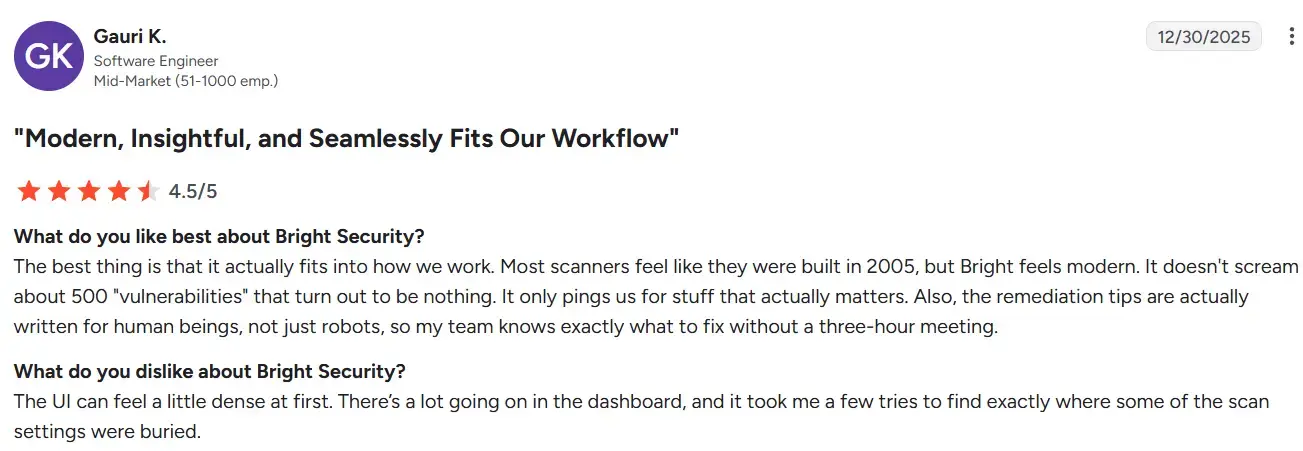
G2 review summary
On G2, reviewers highlighted near-real-time vulnerability detection and effective automation, rating it around 4.7/5. Users appreciate the developer focus, automation and scanning accuracy. Some note onboarding/configuration can be a little heavy for small teams.
Pricing
Quote based.
8. Tenable Web App Scanning (WAS)
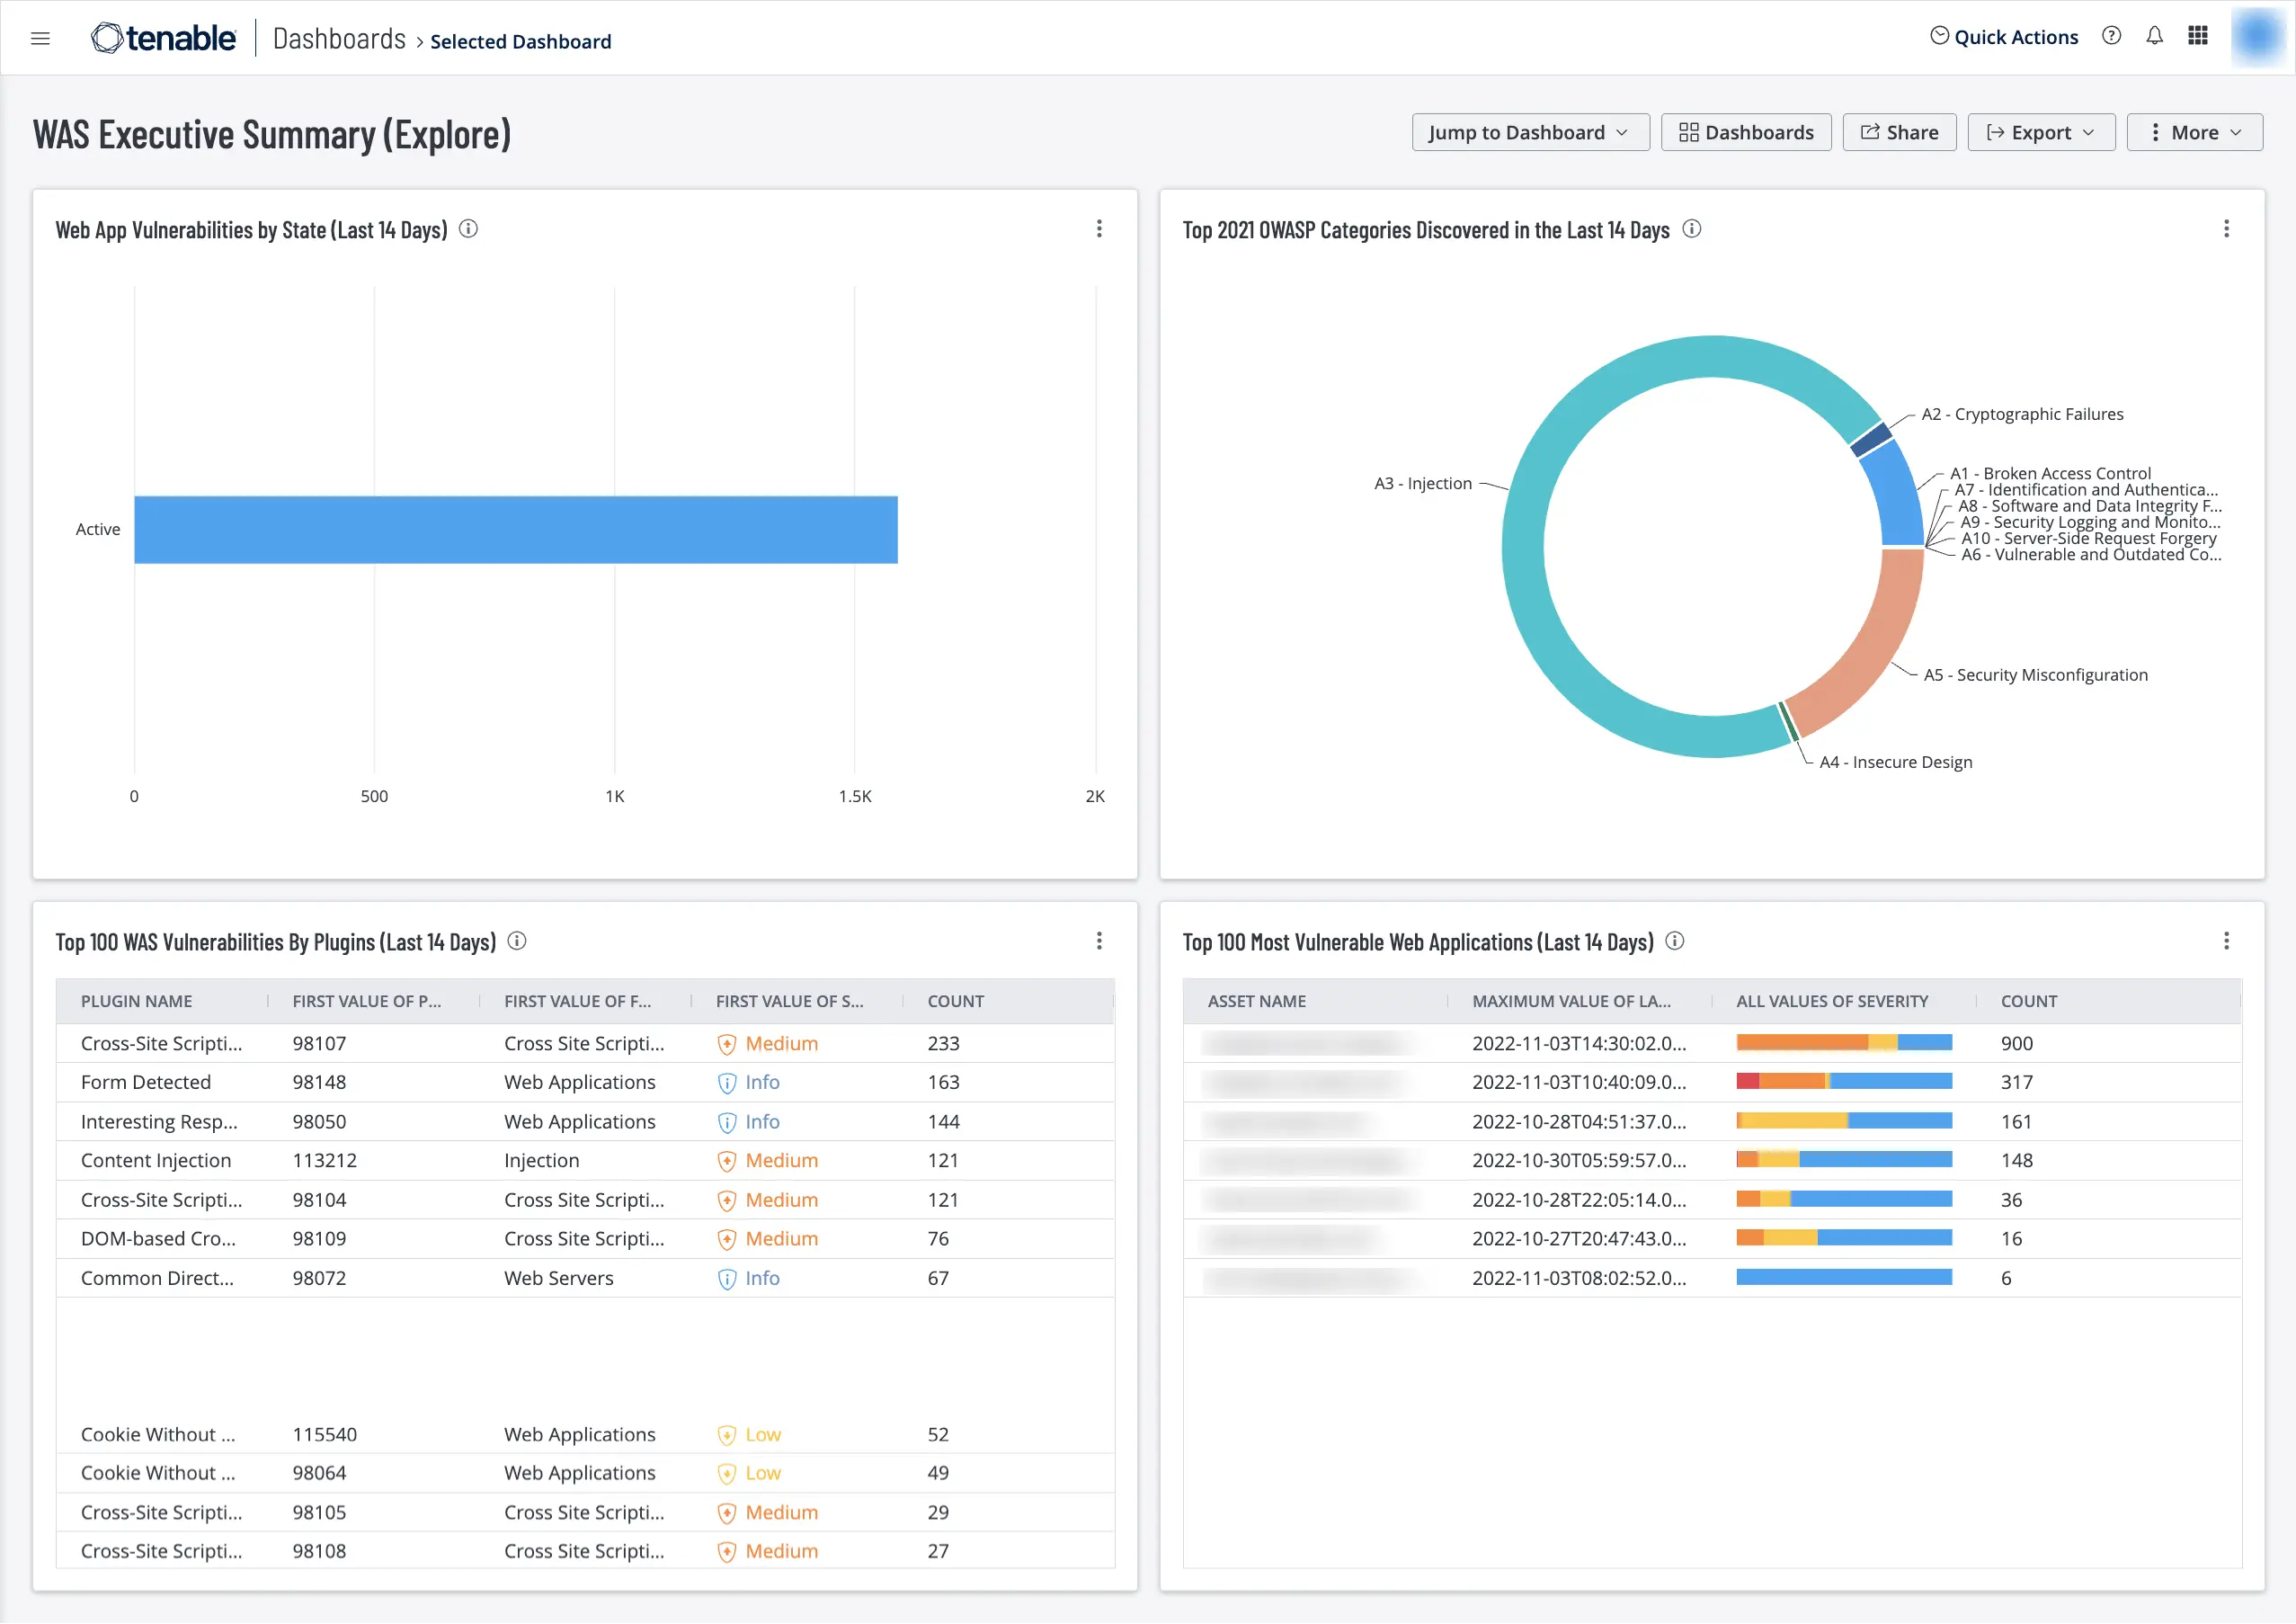
Tenable Web App Scanning (WAS) is part of the Tenable portfolio and provides dynamic application security testing for web applications and APIs, with integration into Tenable’s risk-based vulnerability management ecosystem. It is designed to support modern web and API architectures and provide visibility of application-level risk alongside network/infrastructure risk. While Tenable is better known for network vulnerability management, the WAS offering gives a strong bridge between infrastructure and application security.
Features
Web app & API DAST scanning
Integration with Tenable risk-management
Modern web framework support
SaaS + on-premise flexibility
Role-based dashboards & prioritization
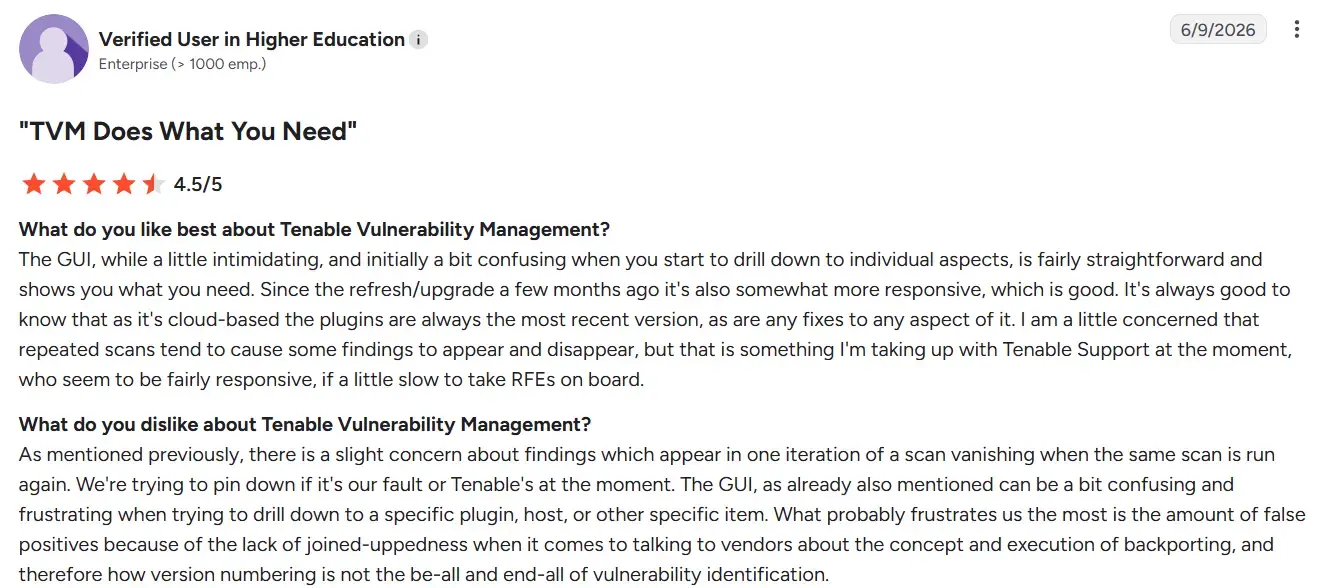
G2 review summary
Generally positive, especially for organizations already embedded in Tenable’s ecosystem. Some users find application-scanning capabilities less mature versus pure DAST specialists. One limitation noted by users is that some advanced business-logic scanning features may still lag dedicated app-security tools.
Pricing
Entry: approx $7,434/year for 5 FQDNs (public reference)
Tiered pricing beyond this via vendor quote.
9. Veracode DAST
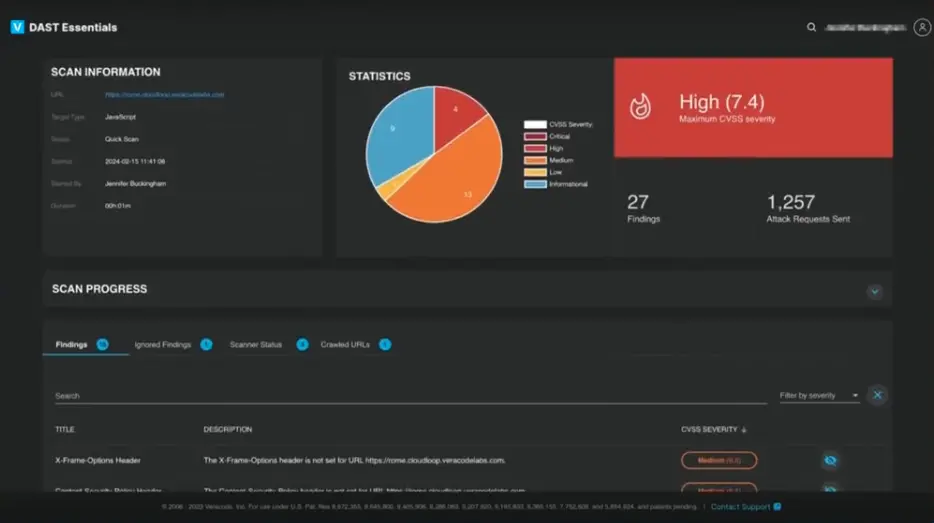
Veracode DAST is part of the Veracode Application Security Platform, offering dynamic scanning of web applications and APIs within a broader ecosystem of SAST, SCA and governance capabilities. Built for enterprise-scale organisation, Veracode DAST emphasizes compliance workflows, large application portfolios and integration with threat metrics and risk dashboards. This makes it a strong contender for organizations seeking governance, compliance and AppSec program maturity beyond GitLab’s default DAST.
Features
Enterprise dynamic scanning for web & APIs
Integrates with SAST/SCA under one platform
Policy-driven workflows & compliance support
Large application portfolio management
Reporting for governance and audit
G2 review summary
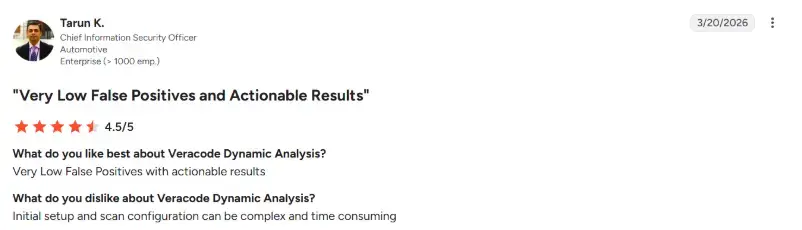
Users appreciate the enterprise strength, compliance readiness and broad coverage while some comment on slower UI and higher complexity/licensing. Users also report that while Veracode provides robust enterprise features and scale, the user experience may be less developer-friendly and costs higher than lighter DAST alternatives.
Pricing
Entry: approx $15,000/year (public benchmark)
Enterprise: Custom quote required.
10. HCL AppScan
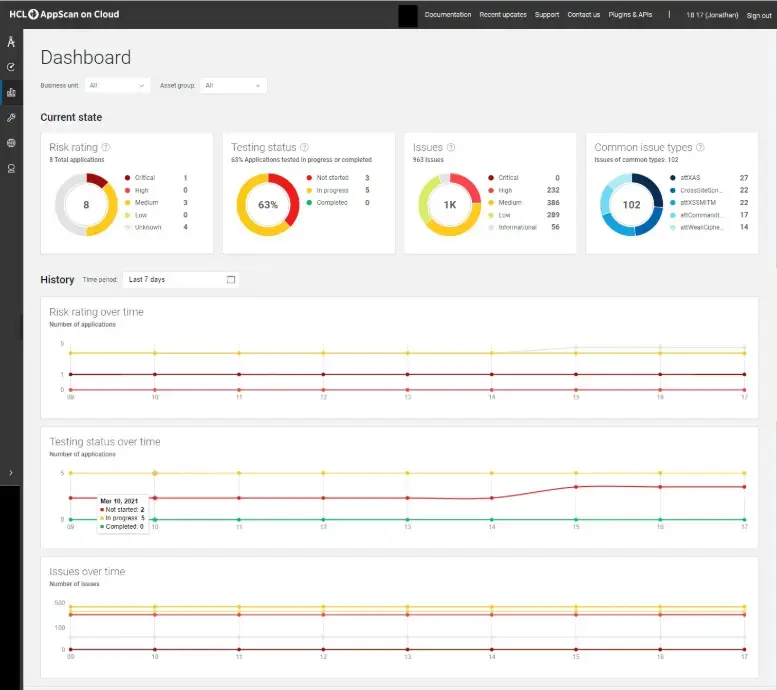
HCL AppScan (formerly IBM AppScan) is a mature, full-spectrum application security suite offering DAST, SAST, IAST and SCA. Its DAST module supports deep scanning of web applications and APIs, multi-step business-logic flows, authenticated testing and large-scale enterprise use-cases. For organisations with large portfolios, legacy infrastructure, multiple languages and regulatory demands, HCL AppScan delivers breadth and enterprise readiness.
Features
DAST + SAST + IAST + SCA suite
Cloud and on-prem deployment options
Complex web flows & authenticated scanning
Compliance-ready reporting and audit logs
Enterprise-scale portfolio management
G2 review summary
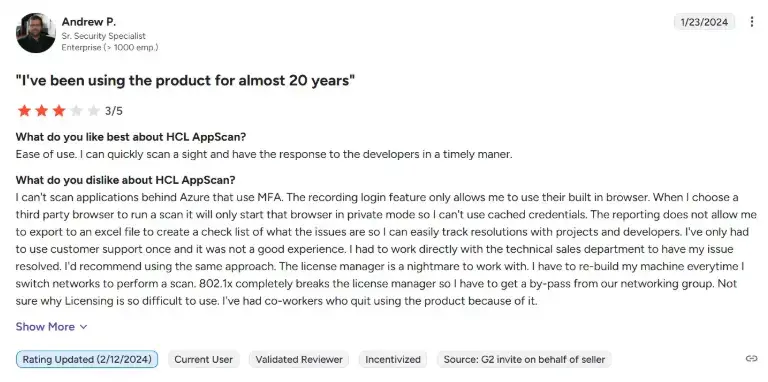
Reviewers recognize AppScan’s depth and enterprise credentials, but many users note that implementation and configuration complexity can be higher compared to more nimble DAST tools.
Pricing
Single scan: $29.99, discounted from a $299 list price, for a choice of DAST, SAST, or SCA 50 scan pack: $699, discounted from list price, for frequent users needing multiple scans
Enterprise: license costs custom quoted, often reaching tens of thousands annually
Things to consider when choosing a GitLab DAST alternative
When you’re evaluating a replacement or complement to GitLab’s built-in DAST, keep these key decision factors in mind:
| Factor | What to check |
|---|---|
| Scope and coverage | Does the tool support web apps, APIs, GraphQL, microservices, and business logic? |
| Pipeline and DevOps integration | How well does it plug into your GitLab CI/CD, build triggers, issue trackers, and developer workflows? |
| Authentication and complexity support | Can it handle multi step login flows, 2FA/MFA, dynamic business logic, GraphQL, and single page apps? |
| Accuracy and false positive rate | Does it validate findings, or does it generate false positives that waste engineering time? |
| Scalability and portfolio size | Can it handle the number of applications/domains you have, and how does cost scale as you grow? |
| Reporting & remediation guidance | Are reports actionable, understandable to developers, aligned to frameworks (OWASP, PCI, SOC2)? |
| Pricing model & transparency | Is pricing per target/app/ scan, subscription model? Are baseline costs clear and predictable? |
| Compliance & governance | Does the tool meet your audit/regulatory needs (HIPAA, PCI, ISO 27001), enterprise role-based access, dashboard? |
| Vendor ecosystem & support | Is the vendor responsive, is the tool well supported? Does the tool integrate with your existing security stack? |
| Total cost of ownership | Consider not just licensing but training, engineering ramp-up, remediation workload, integration effort. |
Final thoughts
GitLab’s built in DAST can be a good starting point, but many organizations find value in a dedicated DAST solution that better aligns with their application stack, DevSecOps practices, and security maturity. For lean DevSecOps teams and modern web and API architectures, tools like Beagle Security or Bright Security offer developer friendly coverage built around CI/CD workflows.
As you evaluate alternatives, prioritize fit over feature checklists. Consider your asset types, scanning frequency, pipeline integrations, and budget rather than choosing based on the longest features list.
If you think Beagle Security is the right fit for your team, start a 14 day advanced free trial or explore the interactive demo to see how it fits your workflow.
FAQ
Is there a free alternative to GitLab DAST?
ZAP by Checkmarx is fully open source and free. Burp Suite offers manual testing capability at no cost through its Community Edition, though its automated Scanner module requires a paid Professional or Enterprise license.
How much does a GitLab DAST alternative typically cost?
Pricing varies widely by category. Open source tools like ZAP are free. Developer focused platforms like Beagle Security start around $119 per month. Enterprise platforms like Veracode DAST and HCL AppScan often start in the thousands per year and scale with application portfolio size.
Is ZAP better than Burp?
If you want automated DAST in a pipeline at zero license cost, pick ZAP; if you have budget and want best-in-class scanning plus manual pentest tooling, pick Burp.