Top software security audit tools in 2026
Shipping software fast is exhilarating, but doing so without a strong security process is like building a race car without brakes. As development cycles accelerate and digital ecosystems expand, the attack surface grows with every new API, dependency, and integration.
Security can no longer be an afterthought, yet for many teams, understanding the alphabet soup of tools like DAST, SAST, SCA, IAST, and RASP feels overwhelming. Each serves a different purpose, operates at a different stage of the software development lifecycle, and addresses a specific type of risk.
This guide breaks down the core categories of software security audit tools, explains how they differ, and highlights the top solutions shaping the security landscape in 2026, to help you make an informed choice whether you’re on a DevSecOps team, a security engineer, or a CTO evaluating your organization’s testing capabilities.
Types of software security audit tools
Security audit tools generally fall into three main categories: Dynamic Application Security Testing (DAST), Static Application Security Testing (SAST), and Software Composition Analysis (SCA). Together, they form the foundation of a comprehensive security program.
Dynamic application security testing (DAST)
DAST tools simulate real-world attacks against running applications. They operate externally, scanning for vulnerabilities in a live environment without access to the source code. Think of DAST as a penetration tester probing your application’s defenses to find misconfigurations, injection flaws, and logic vulnerabilities.
These tools are especially useful for discovering issues that only appear at runtime, such as authentication weaknesses, API misconfigurations, or session management errors. They help organizations understand how attackers could exploit a live system, and they provide actionable insights for remediation.
DAST solutions are ideal for QA and security teams, integrating testing into pre-production environments. Their main strength lies in replicating attacker behavior across web and API surfaces, ensuring that security assessments reflect real operational risks.
DAST does have a boundary, though. It cannot identify coding errors or insecure design patterns before deployment. To close that gap, teams often complement it with static analysis tools that scan the codebase itself.
Static application security testing (SAST)
SAST tools analyze source code, bytecode, or binaries to detect security flaws before execution. They serve as an automated code review mechanism, identifying vulnerabilities such as hardcoded secrets, injection points, or insecure encryption implementations.
This “shift-left” approach lets developers fix issues early in the SDLC, reducing cost and rework. SAST integrates directly into IDEs and CI/CD pipelines, flagging issues during development or build stages.
Its main advantage is precision at the code level: it tells you exactly which line introduces the vulnerability. Static analysis can still produce false positives, though, and it lacks visibility into runtime behavior, which is why it isn’t sufficient on its own.
That’s where software composition analysis tools come in, to help ensure the components you build upon are secure.
Software composition analysis (SCA)
SCA tools focus on open-source and third-party components. They identify dependencies, monitor vulnerabilities in public databases like NVD, and flag outdated or insecure libraries.
In modern development, where over 80 percent of codebases rely on open-source components, SCA is essential. These tools help organizations manage supply chain risks, track license compliance, and ensure timely patching.
Their strength lies in continuous monitoring and integration with build pipelines. Yet, SCA cannot detect logic flaws or vulnerabilities in custom code; It must be paired with SAST and DAST for complete coverage.
Together, these three categories, DAST, SAST, and SCA, form the backbone of a layered software security testing strategy.
Top software security audit tools at a glance
Tools | Type | Key features | Limitations / considerations |
Beagle Security | DAST | AI-powered vulnerability detection, business logic testing, CI/CD integration | Primarily web and API-focused |
ZAP (Checkmarx ZAP) | DAST | Open-source scanner, active and passive scans, plugin architecture | Requires manual configuration and expertise |
Burp Suite | DAST | Manual + automated testing, BApp extensions, SPA crawling | Limited automation and scalability |
Invicti | DAST | Proof-based scanning, CI/CD integrations, enterprise reporting | High cost for small teams |
Semgrep | SAST | Lightweight static analysis, custom rule creation, CI/CD ready | Coverage depends on community rules |
Checkmarx SAST | SAST | Enterprise-grade code scanning, deep IDE integration | Expensive and resource-intensive |
Veracode SAST | SAST | Cloud-native analysis, compliance reporting, multi-language support | Slower analysis time for large codebases |
Coverity | SAST | Deep static analysis, precise defect detection, strong governance | Complex setup for smaller teams |
Mend.io | SCA | Continuous dependency monitoring, license compliance, real-time alerts | Focused mainly on open-source components |
Snyk | SCA | Developer-friendly interface, automated fixes, container and IaC support | Limited manual control in free tier |
Ratings are based on G2 reviews as of Sep 2026. Pricing varies by organization size and requirements.
Top software security audit tools
1. Beagle Security (DAST)
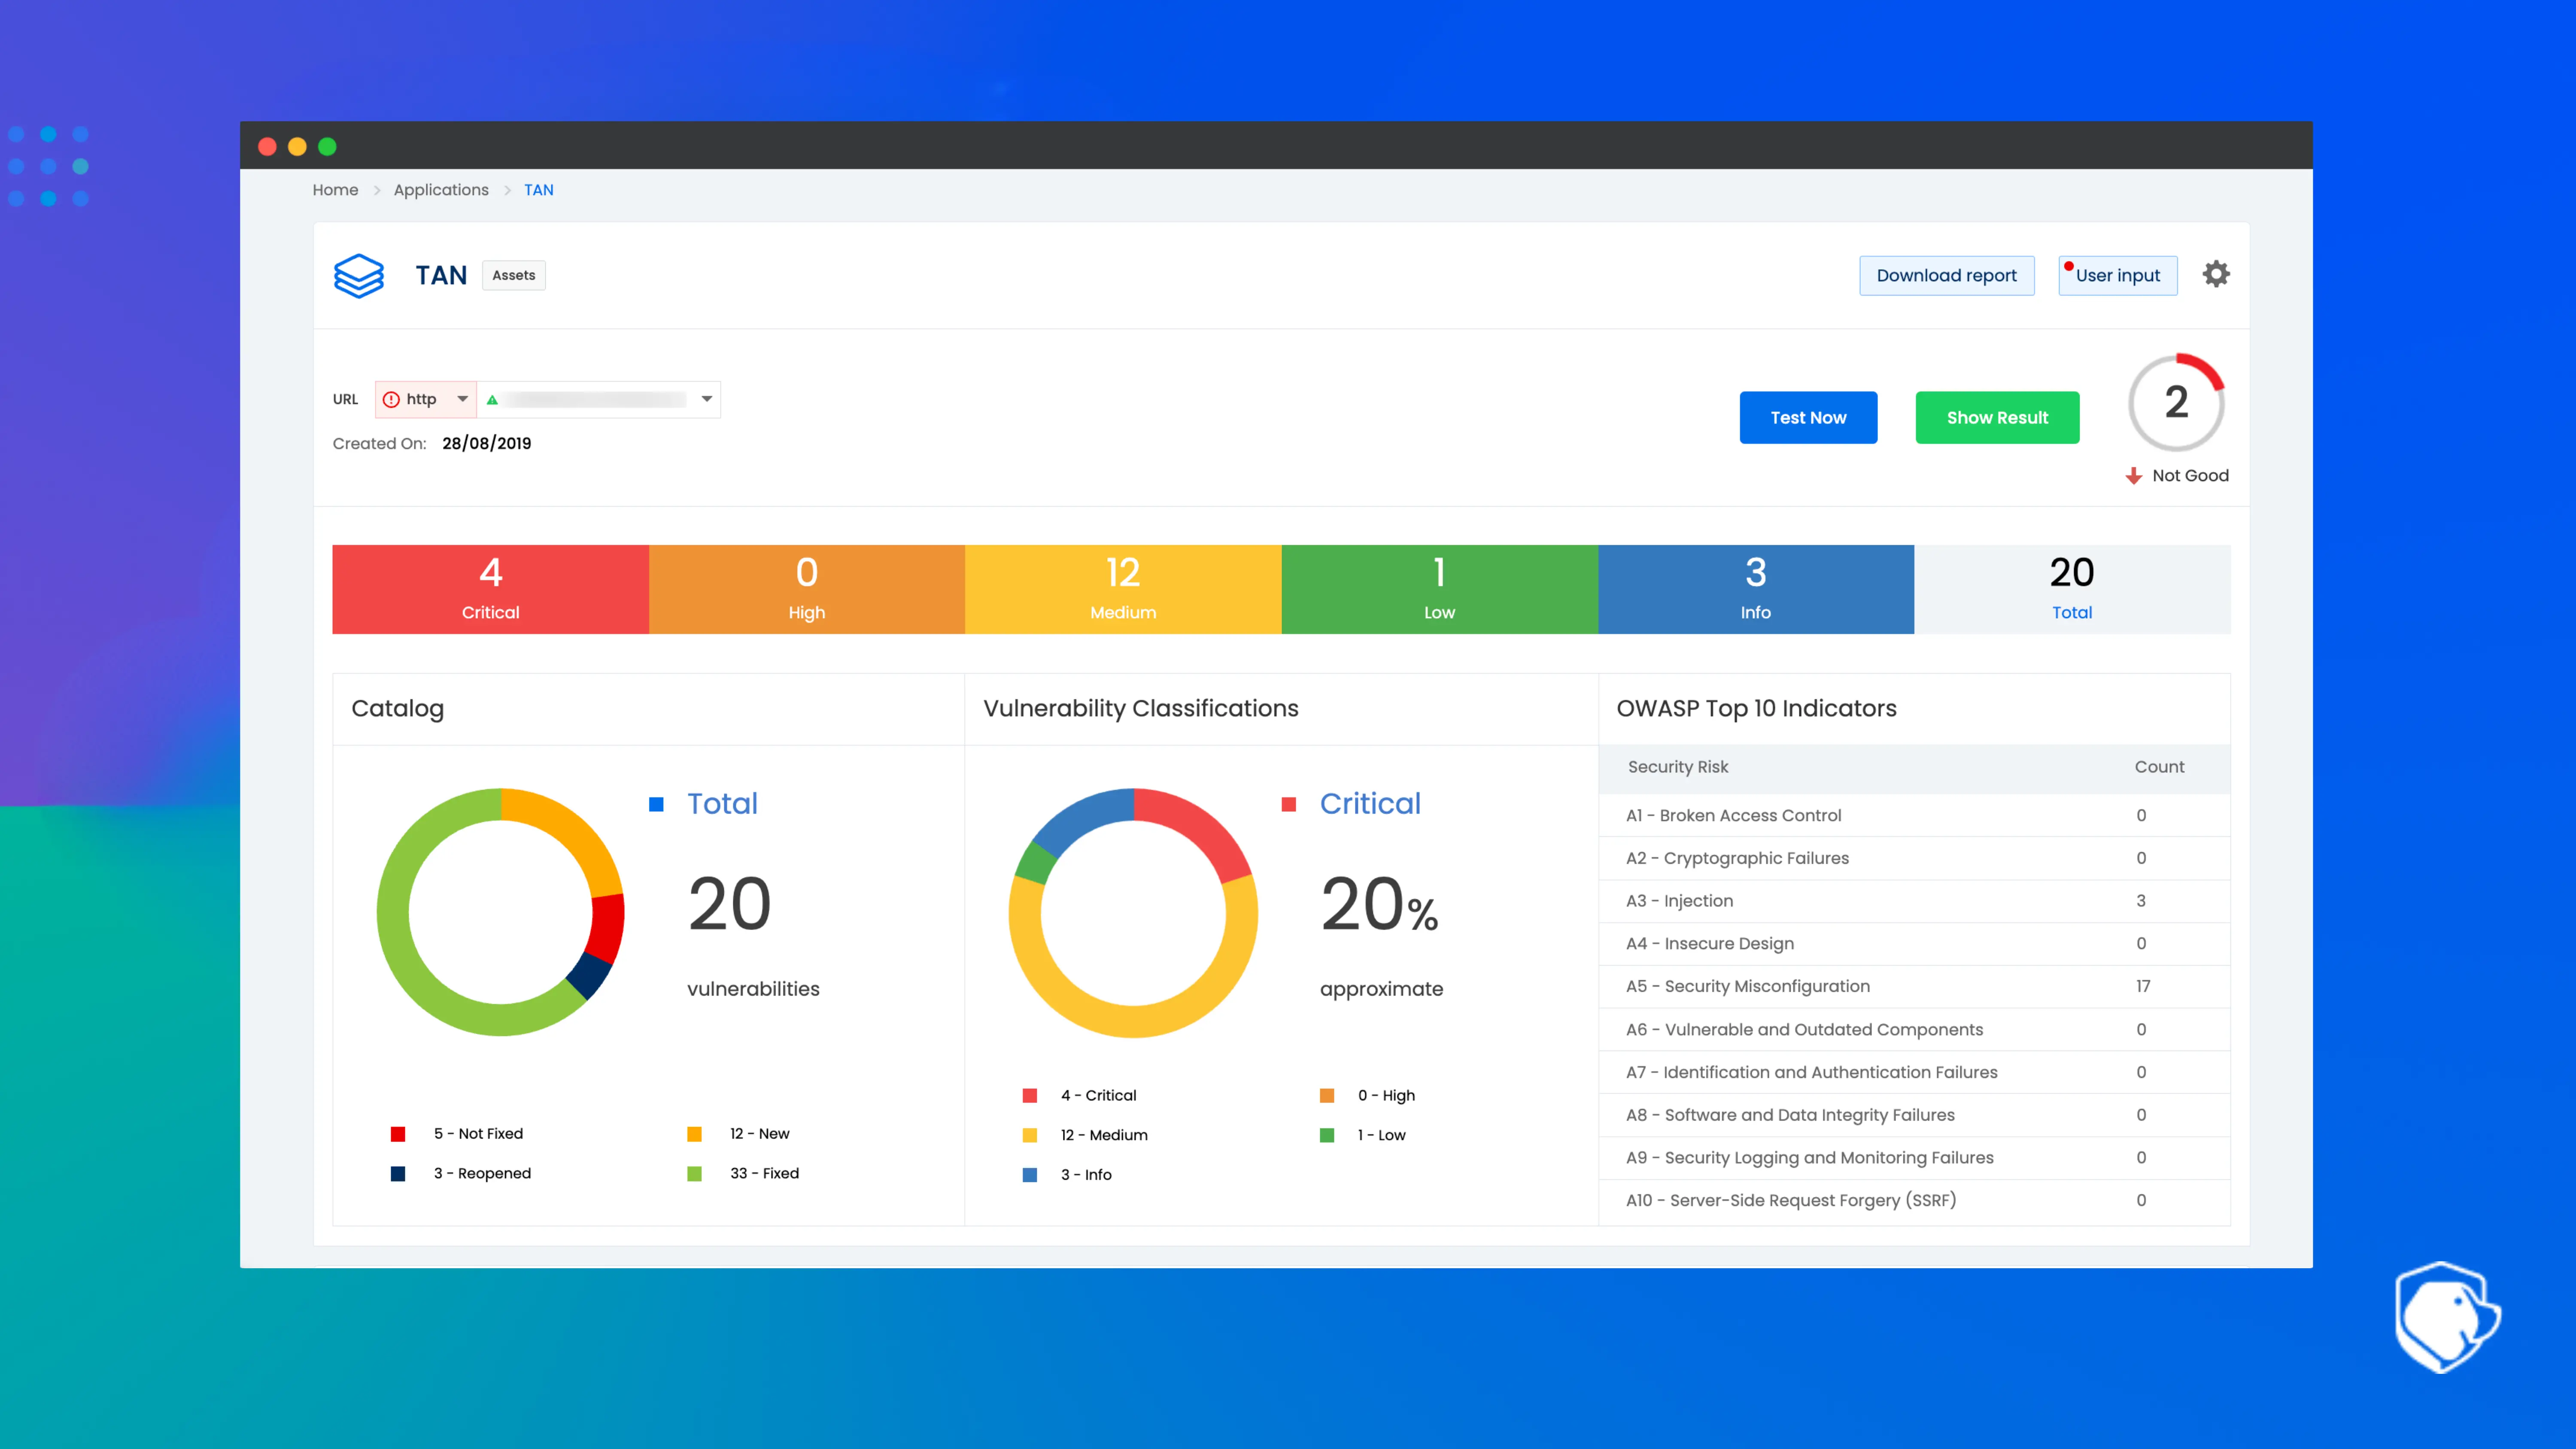
Beagle Security is an agentic AI penetration testing platform designed for modern development teams. It specializes in automated web and API security testing, helping organizations identify business logic flaws and runtime vulnerabilities before attackers do. The platform integrates directly into CI/CD pipelines, running continuous testing without disrupting workflows.
Its standout capability is intelligent attack simulation. Rather than only checking for known issues, it replicates real-world attacker behavior using machine learning models that adapt to application context.
Key features
Agentic AI-powered vulnerability validation with zero false positives
Native support for REST, GraphQL, and SOAP APIs
Business logic and access control testing
Pre-built integrations for GitHub Actions, GitLab, Jenkins, and Azure DevOps
Developer-friendly reports with remediation guidance
Pricing
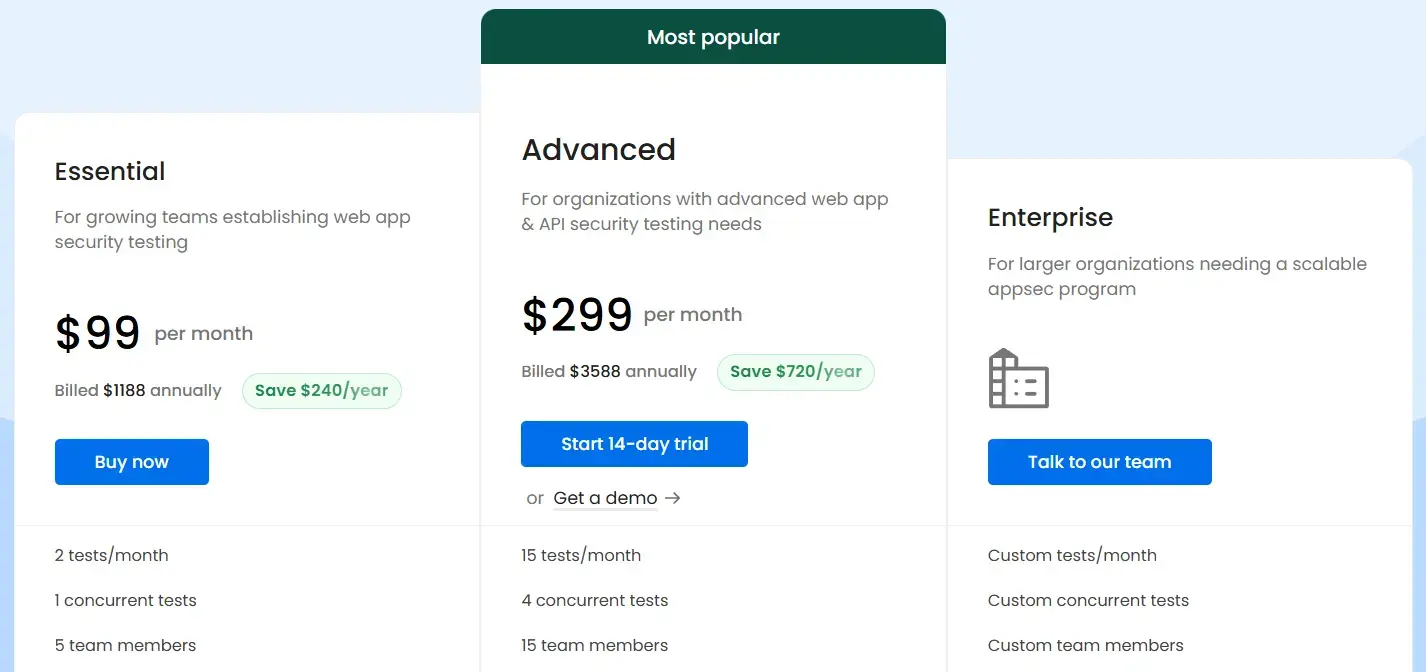
Starting at $99 per month (billed $,1188/year)
Enterprise plans with usage-based scaling
Ratings & review
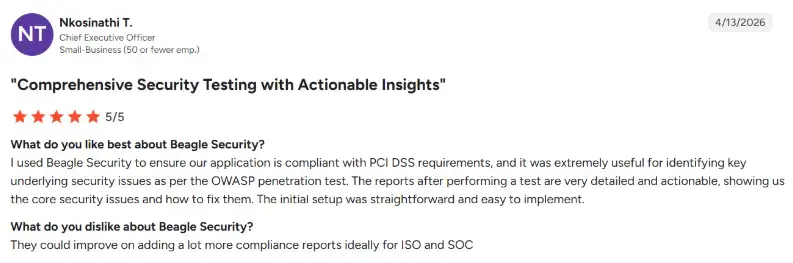
Beagle Security maintains a strong G2 rating of 4.7 out of 5, with users consistently praising its ease of use, API coverage, and agentic AI-powered vulnerability detection. Many reviewers highlight its near-zero false positives and smooth CI/CD integrations, which make it a favorite among DevSecOps teams. Feedback often emphasizes its excellent support and balanced value for both startups and enterprises.
2. Checkmarx ZAP (DAST)
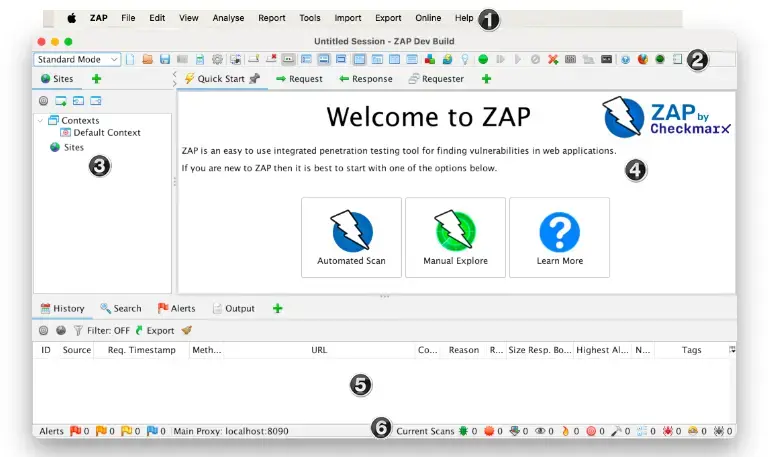
Originally known as OWASP ZAP, this open-source tool is now maintained by Checkmarx and continues to be one of the most popular dynamic testing frameworks worldwide. ZAP provides both automated scanning and manual testing modes, making it suitable for teams that want flexibility and community-backed extensibility. It’s often used by developers and penetration testers who prefer open-source control with plugin-based customization. While it’s not the easiest to set up, its power lies in flexibility and community-driven innovation.
Key features
Active and passive scanning modes
Powerful plugin ecosystem for automation
Proxy-based interception for manual testing
Cross-platform support with frequent updates
Scripting interface for custom scan policies
Pricing:
Free open-source version
Enterprise support available through Checkmarx
Ratings and reviews:
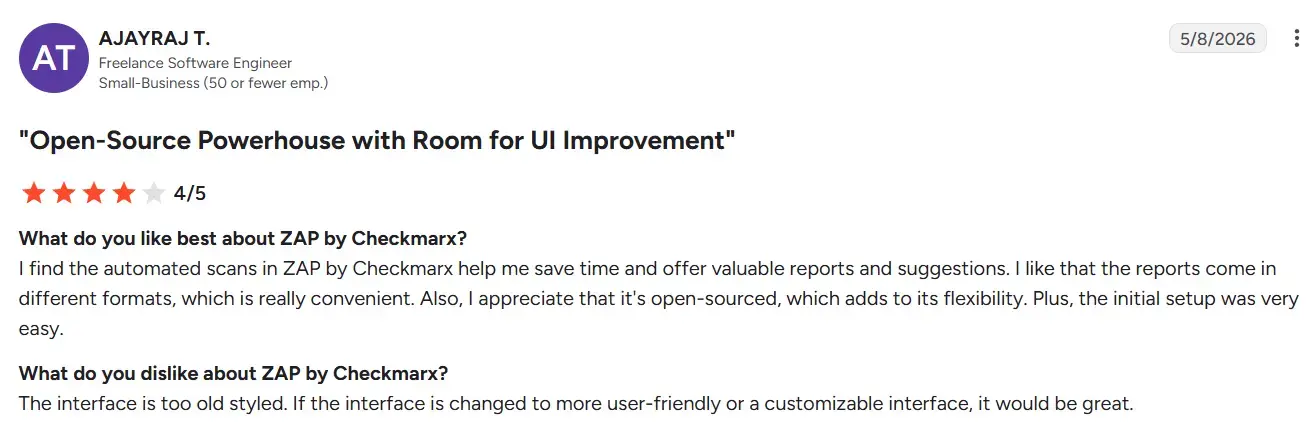
Checkmrx ZAP holds a commendable G2 rating of 4.2 out of 5, reflecting its popularity as a robust open-source DAST solution. Users appreciate its flexibility, community-driven enhancements, and strong automation support in CI/CD pipelines. Reviews frequently mention its impressive capabilities for a free tool, though some note that large-scale management features may require additional setup.
3. Burp Suite (DAST)
Developed by PortSwigger, Burp Suite remains the gold standard for manual web application testing. It’s a favorite among penetration testers and security researchers due to its deep inspection capabilities and modular tools such as Intruder, Repeater, and Proxy.
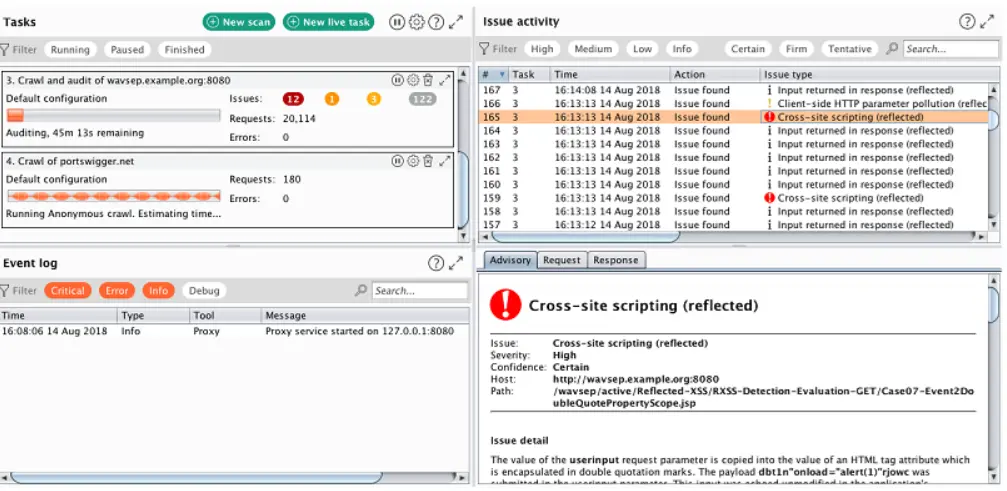
Burp Suite balances manual and automated testing well, offering professional extensions through its BApp Store to enhance functionality and coverage.
Key features:
Manual testing toolkit (Proxy, Repeater, Intruder, Scanner)
JavaScript and SPA crawling support
BApp Store with hundreds of community extensions
Reporting and vulnerability tracking features
Integrations with CI/CD through Burp Suite Enterprise
Pricing:
Community Edition: Free
Professional Edition: $499 per year
Enterprise Edition: Custom pricing
Ratings and reviews:
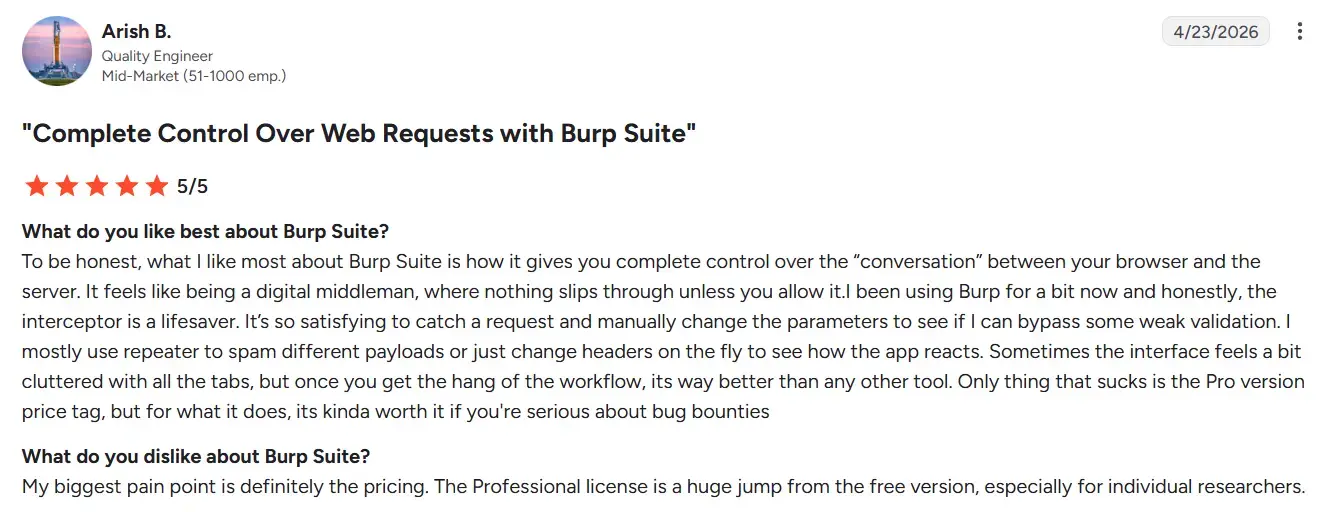
Burp Suite enjoys one of the highest ratings in this category, with a G2 score of 4.8 out of 5. Professionals value its deep manual testing capabilities, advanced interception proxy, and extensive library of community extensions. Many reviewers praise its precision and control, calling it an indispensable tool for both professional pentesters and application security researchers.
4. Invicti (DAST)
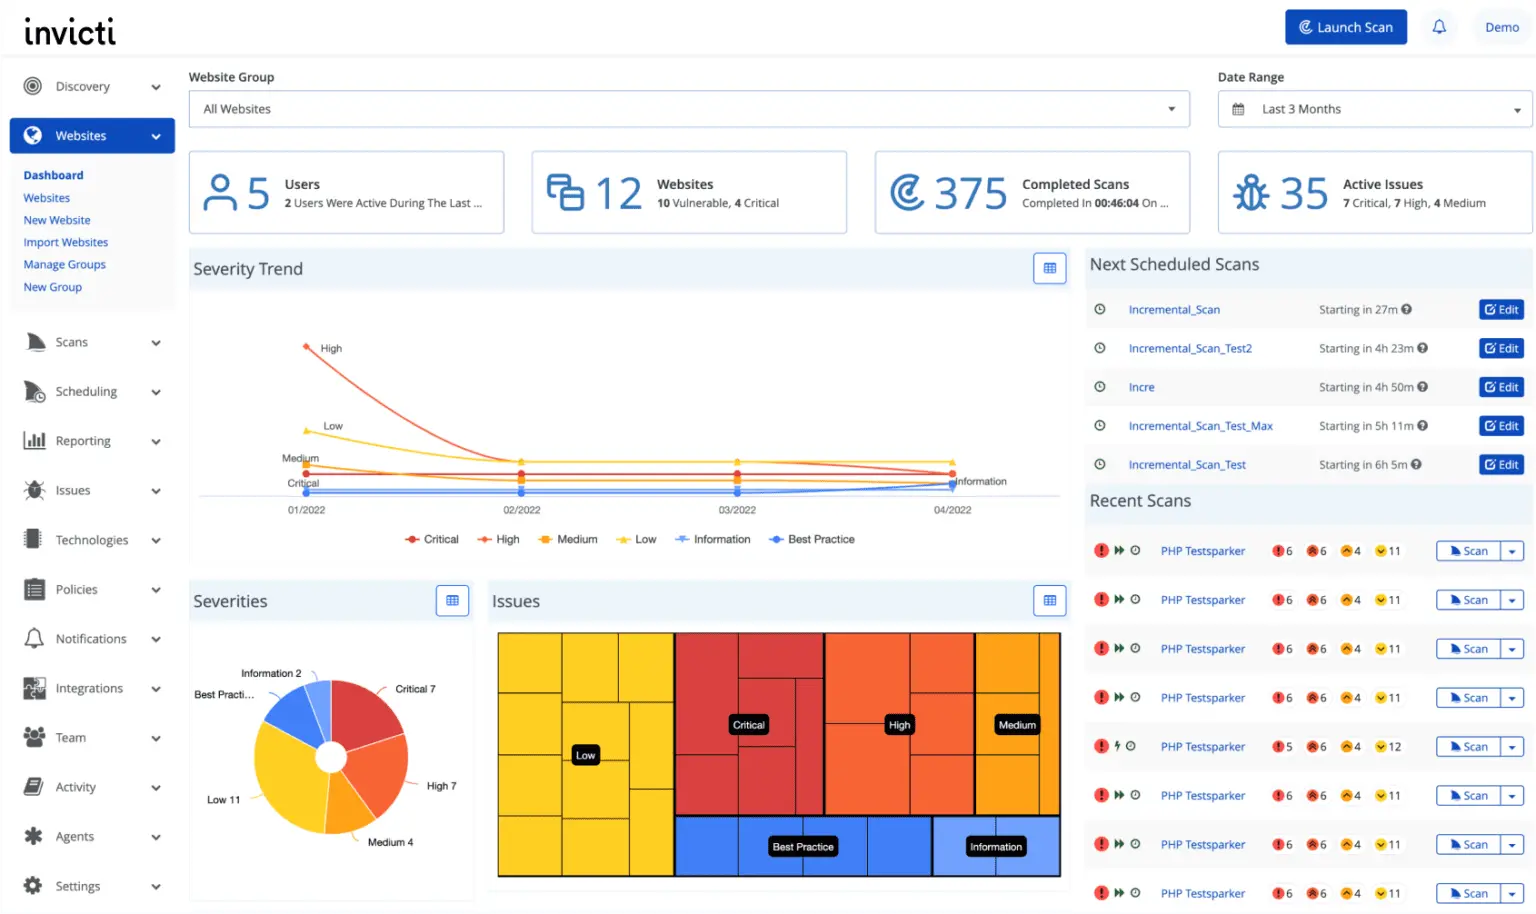
Invicti, formerly Netsparker, is an enterprise-grade DAST solution known for its proof-based scanning technology. It automatically confirms vulnerabilities by safely exploiting them in a controlled environment, reducing false positives dramatically.
It’s particularly suited for large organizations needing governance, compliance, and reporting at scale. Invicti integrates with issue trackers, CI/CD pipelines, and ticketing systems for seamless workflow alignment.
Key features
Proof-based scanning for validated results
Role-based access and audit management
Integration with Jira, Jenkins, GitHub, and Azure DevOps
Detailed technical and executive reporting
Centralized dashboard for large-scale monitoring
Pricing
- Custom enterprise pricing based on scope
Ratings and reviews
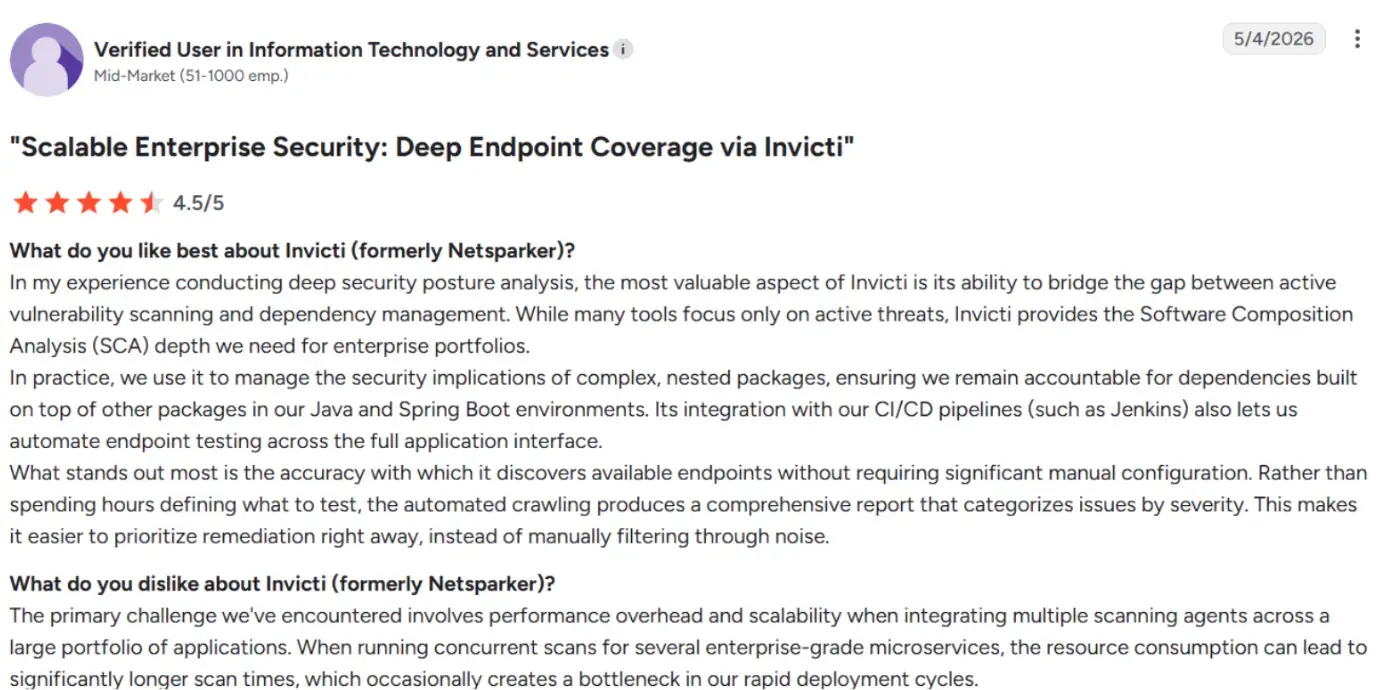
Invicti carries an excellent G2 rating of 4.6 out of 5, with users appreciating its proof-based scanning that eliminates false positives. Reviewers highlight its automation, accuracy, and seamless integration into CI/CD pipelines. Teams frequently mention that Invicti helps them validate vulnerabilities quickly and streamline their remediation workflow.
5. Semgrep (SAST)
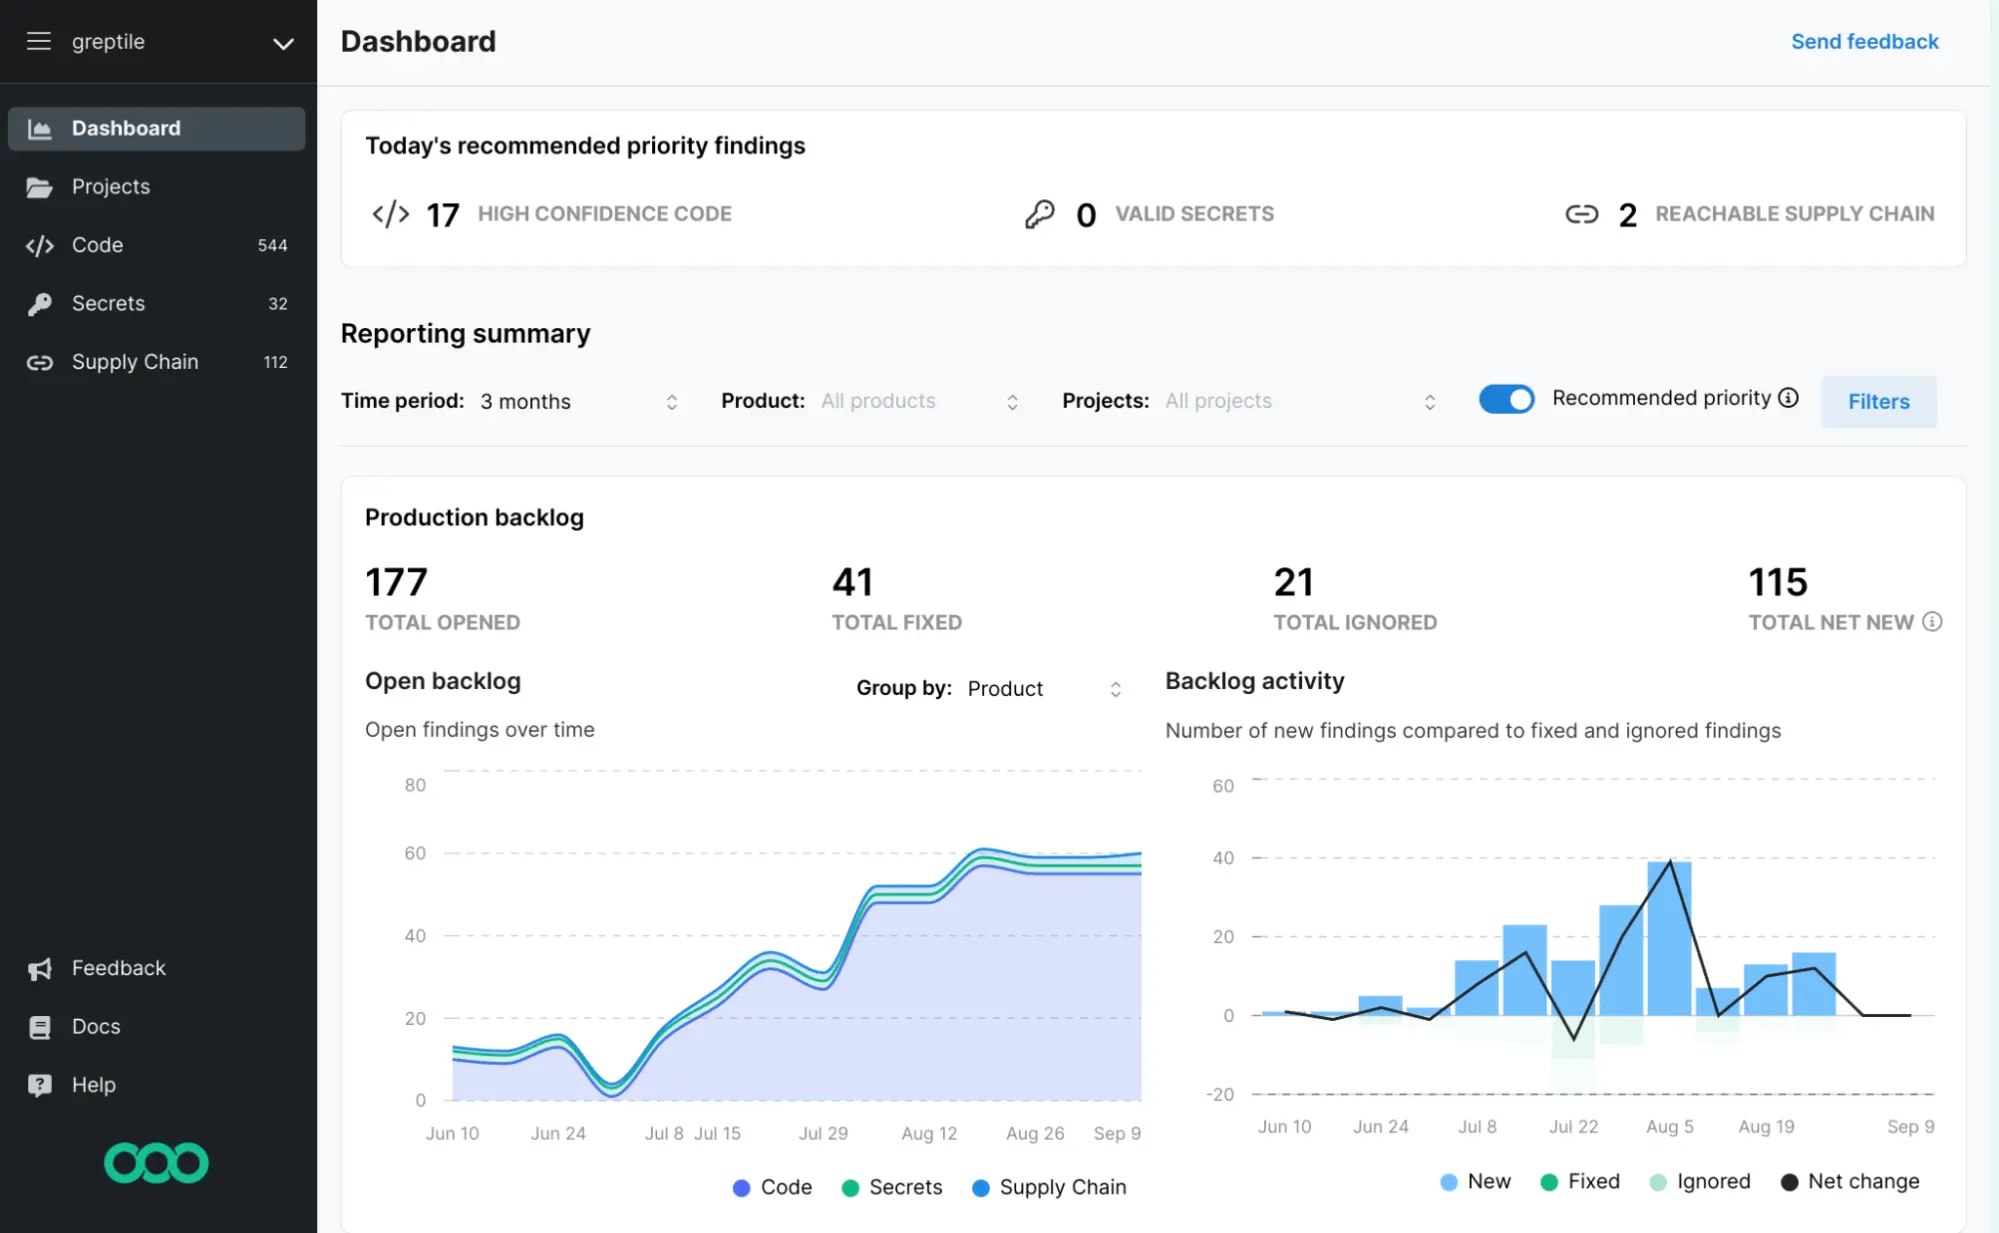
Semgrep brings a developer-first approach to static analysis. It allows teams to write and customize rules in simple YAML syntax, offering unmatched flexibility in scanning source code for security issues, code smells, and policy violations.
It’s fast, lightweight, and integrates easily into developer workflows, making it a preferred choice for engineering-driven security teams.
Key features
2,000+ prebuilt community rules
Custom rule engine for organization-specific checks
CI/CD and IDE integrations
Support for 30+ programming languages
Policy-as-code support for consistent enforcement
Pricing
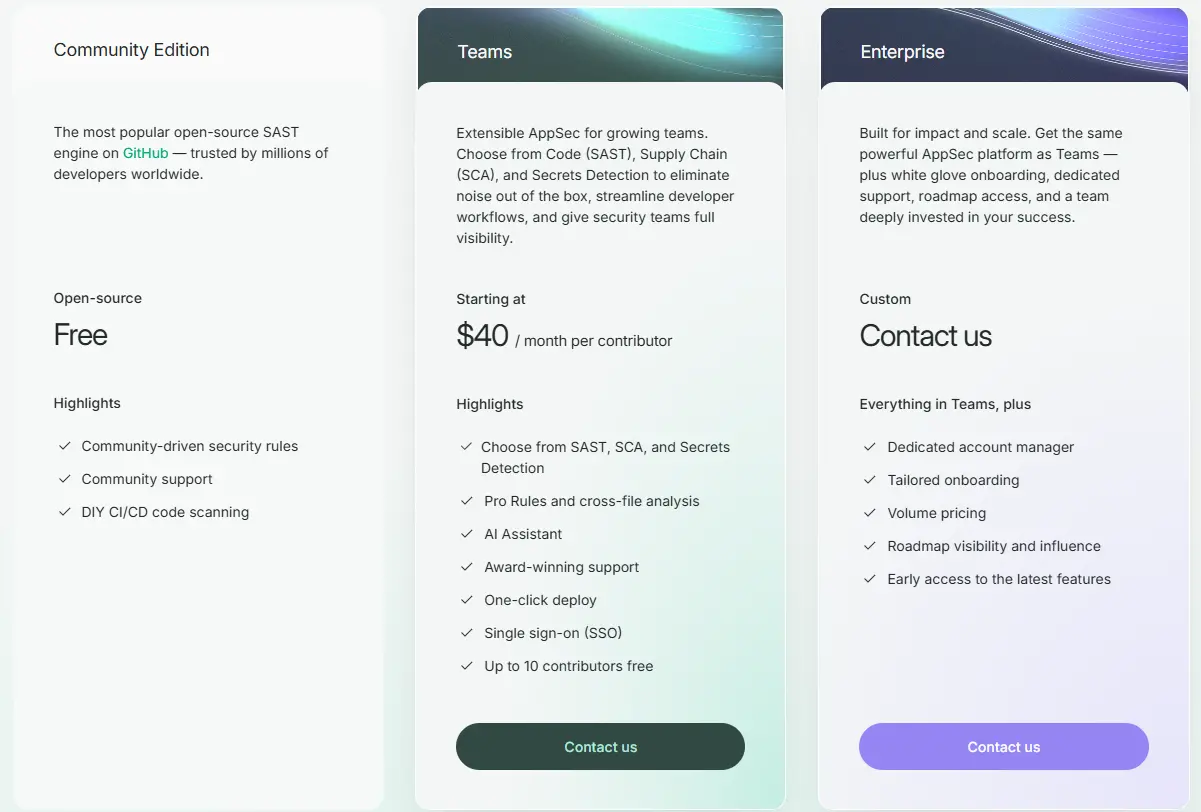
Community Edition: Free
Team Plan: From $40 per developer per month
Enterprise: Custom pricing
Ratings and reviews:
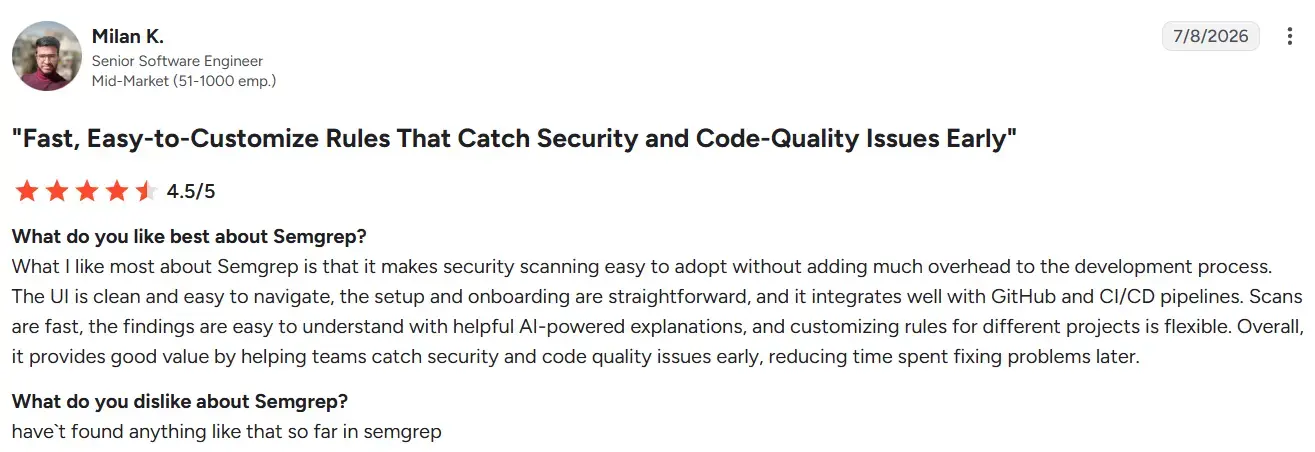
Semgrep holds a solid G2 score of 4.6/5, with developers commending its fast and customizable static analysis. Users particularly value its simple rule syntax and extensive library of prebuilt checks that support multiple programming languages. Reviews often describe it as lightweight, developer-friendly, and ideal for integrating security earlier in the SDLC.
6. Checkmarx SAST
Checkmarx SAST is an enterprise-grade static analysis solution built for deep code inspection. It scans source code and binaries across multiple languages and frameworks, providing detailed insights into security weaknesses.
With strong CI/CD integrations and compliance support, it’s favored by large organizations prioritizing governance and centralized management.
Key features
Comprehensive multi-language support
Deep IDE integration for shift-left testing
Centralized policy and compliance management
Advanced reporting and risk visualization
Integration with SCMs and build tools
Pricing
- Custom enterprise pricing
Ratings and reviews
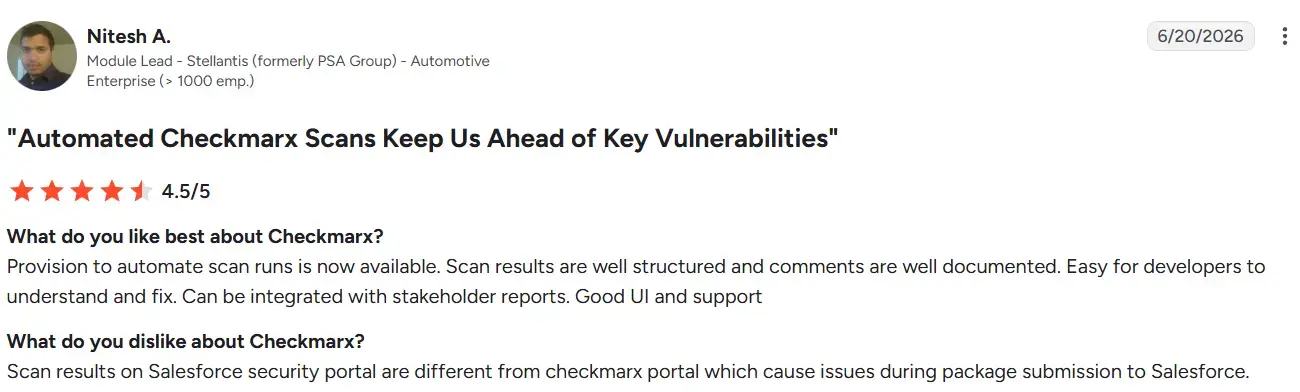
Checkmarx SAST maintains a G2 rating of 4.3 out of 5, receiving consistent praise for its comprehensive code scanning and policy management. Users appreciate its ability to identify complex security flaws and compliance issues at scale. Some mention that scan speed can be slower on very large projects, but most agree it is a mature and feature-rich enterprise solution.
7. Veracode SAST

Veracode offers a cloud-based SAST platform tailored for enterprises requiring scalable, policy-driven security assessments. It provides code analysis, compliance reporting, and integrations across development environments.
Its managed service model appeals to organizations seeking operational simplicity without maintaining on-premise infrastructure.
Key features
Cloud-native SAST scanning
Integrated compliance reporting (SOC 2, ISO 27001)
Multi-language and framework support
IDE plugins for real-time feedback
Centralized policy enforcement
Pricing
- Custom enterprise pricing
Ratings and reviews
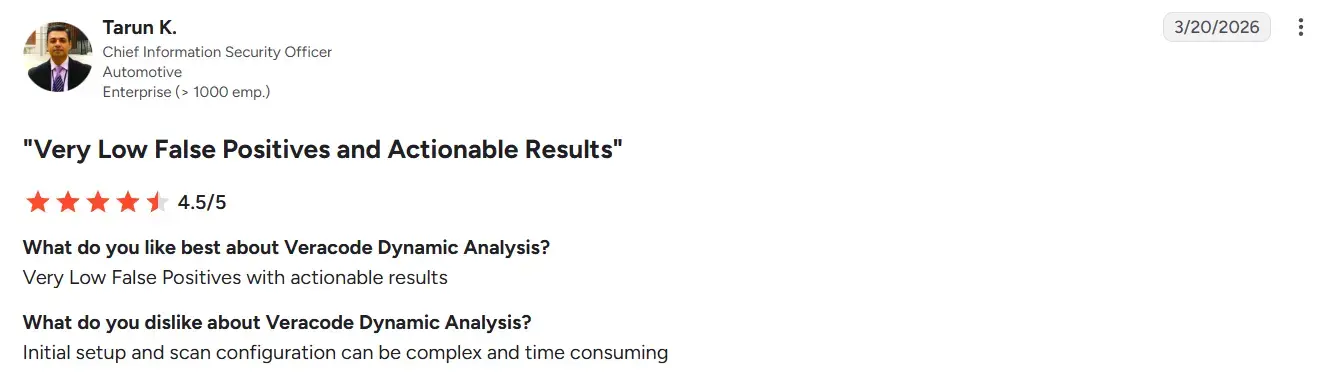
Veracode SAST scores a respectable G2 rating of 4.2 out of 5, with users valuing its cloud-based scanning and detailed vulnerability remediation guidance. Reviewers note that it integrates well into enterprise workflows, offering strong governance and reporting features. Some mention that results interpretation requires training, but most appreciate its accuracy and breadth of language support.
8. Coverity (SAST)
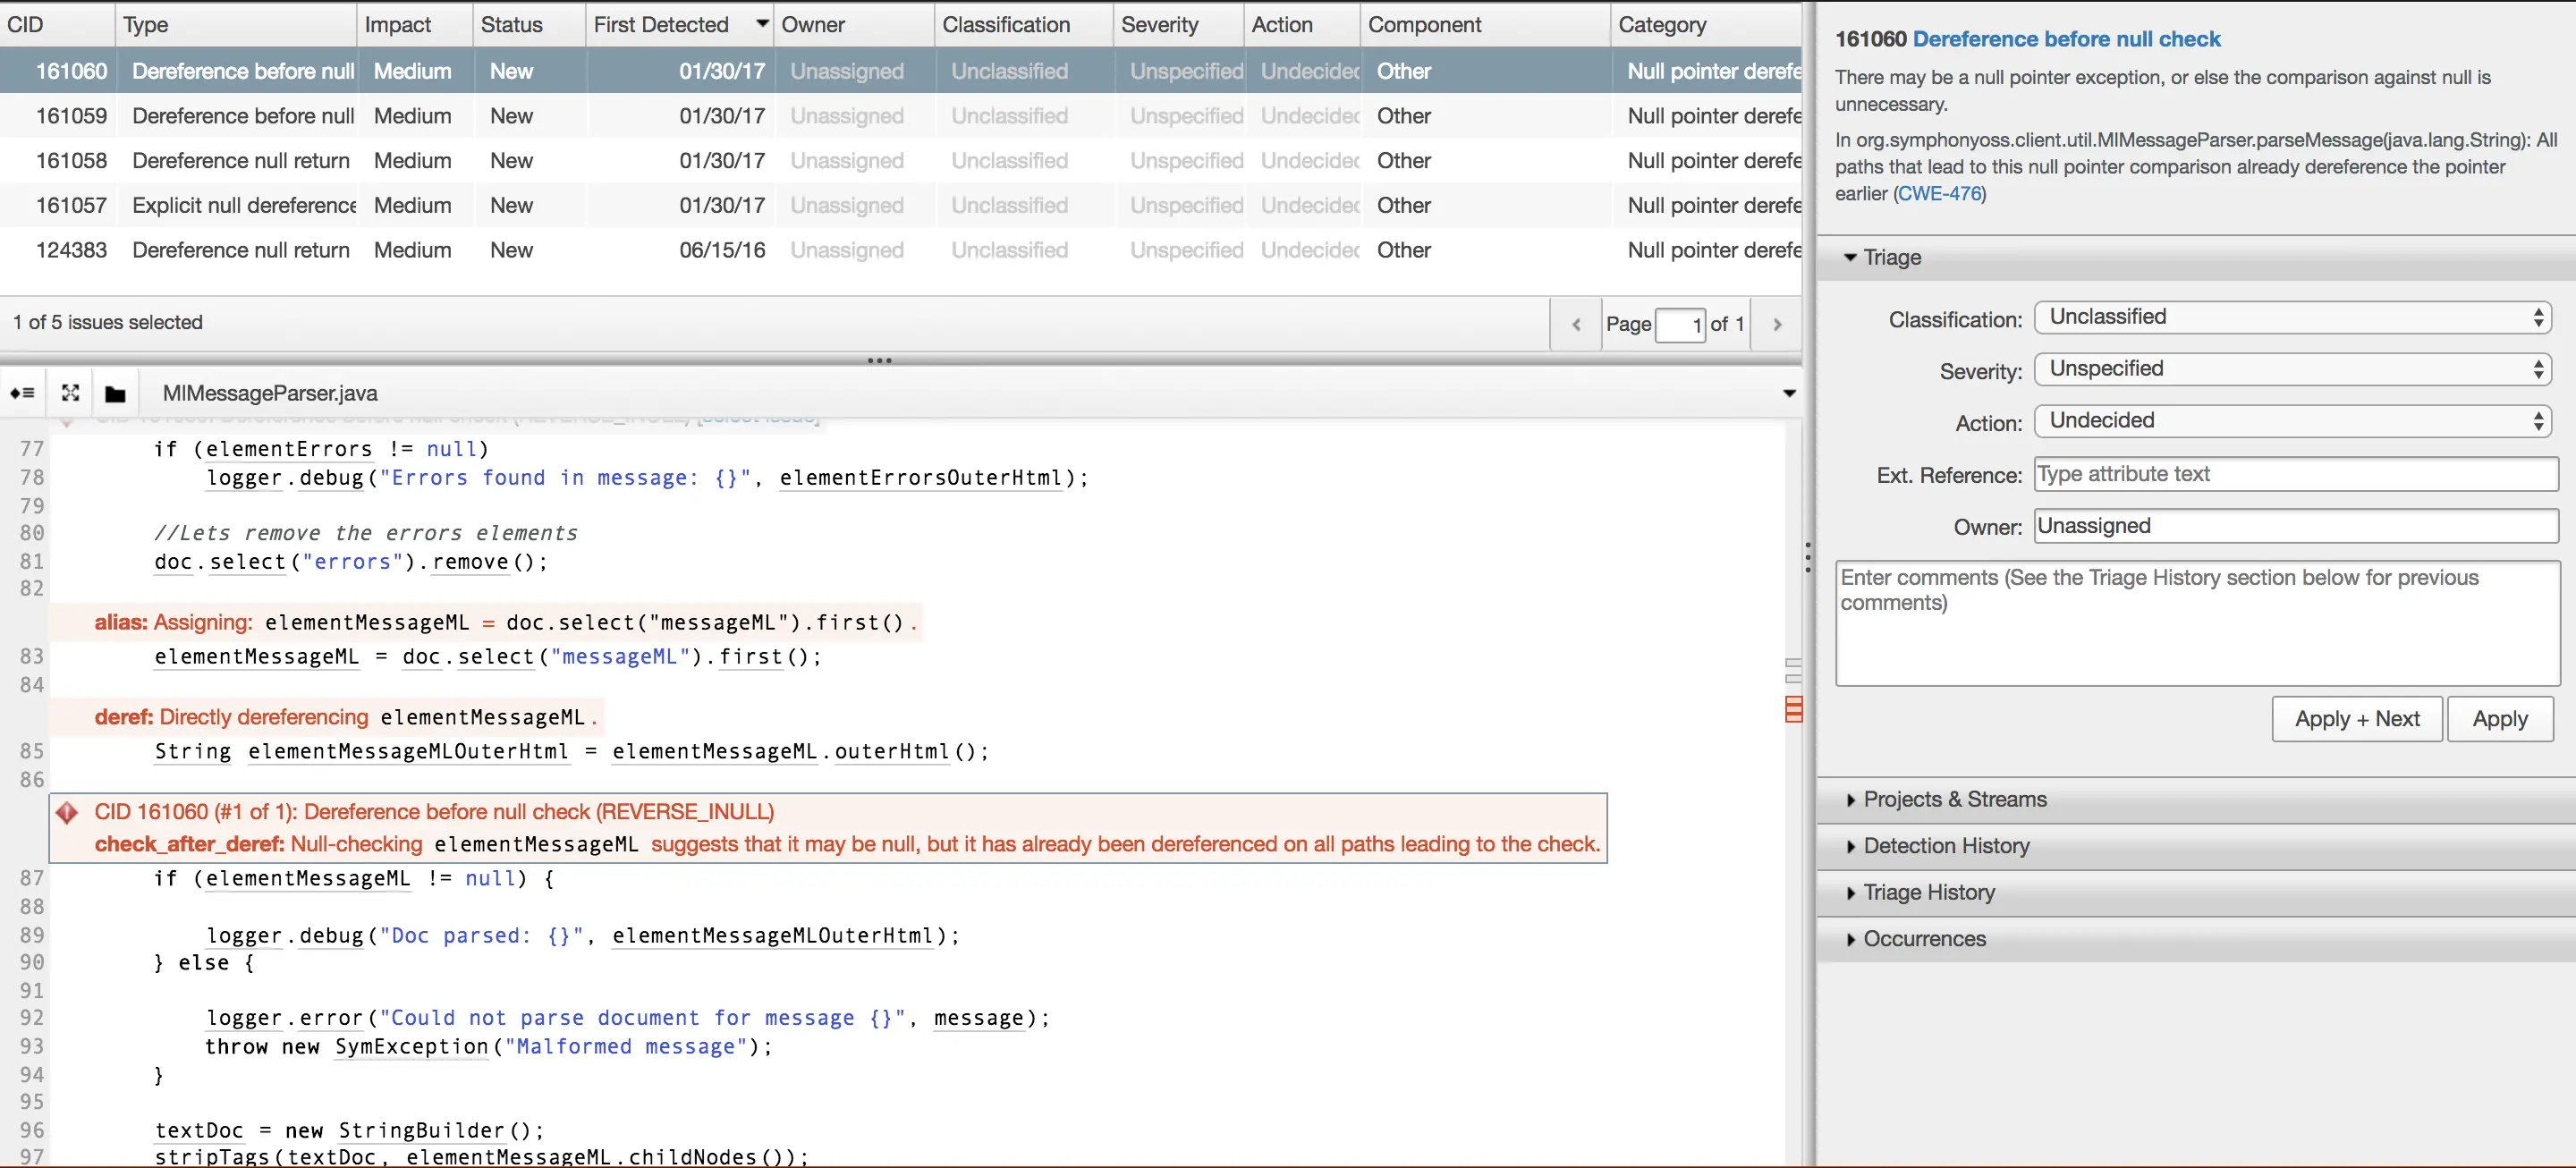
Coverity, now part of Black Duck Software, is a mature static analysis tool trusted for its precision in identifying complex software defects and security vulnerabilities. It supports large-scale enterprise environments and is widely used in safety-critical industries.
Its strength lies in advanced dataflow analysis that minimizes false positives while still providing detailed remediation guidance.
Key features
Deep static analysis with contextual insights
Enterprise governance and audit trail support
Integrations with major build systems and IDEs
High scalability for large codebases
Accurate defect classification and remediation guidance
Pricing
- Custom enterprise pricing
Ratings and reviews
Coverity from Black Duck holds a 4.4 out of 5 rating on Gartner Peer Insights from 156 reviews. Reviewers consistently highlight low false positives, straightforward CI/CD integration, and strong compliance support for standards like MISRA and HIPAA.
9. Mend.io (SCA)
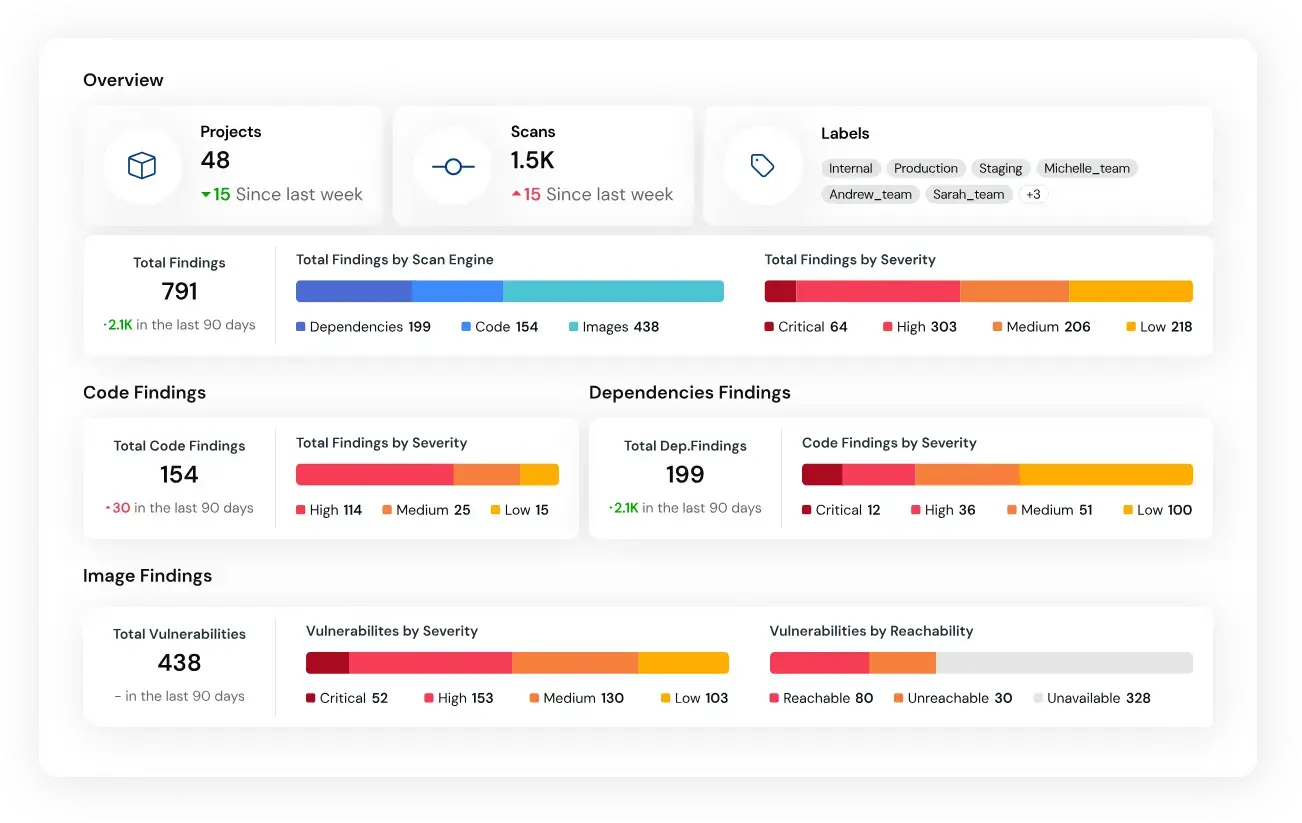
Mend.io, formerly WhiteSource, focuses on managing open-source risk. It automates dependency scanning, license compliance, and vulnerability alerts across complex codebases.
The platform’s continuous monitoring ensures that teams are notified as soon as a new vulnerability affects any dependency, supporting proactive remediation.
Key features
Continuous dependency and license scanning
Real-time alerts for new CVEs
Integration with GitHub, Bitbucket, and CI/CD tools
Policy management for license compliance
Automated remediation suggestions
Pricing
- Custom enterprise pricing
Ratings and reviews
Mend.io, formerly known as WhiteSource, holds a G2 score of 4.3 out of 5, with users praising its effective open-source vulnerability management and license compliance tracking. Many reviewers highlight its automation and continuous monitoring features that help teams maintain visibility across software dependencies. Some users mention that the interface can be dense, but overall satisfaction remains high.
10. Snyk (SCA)
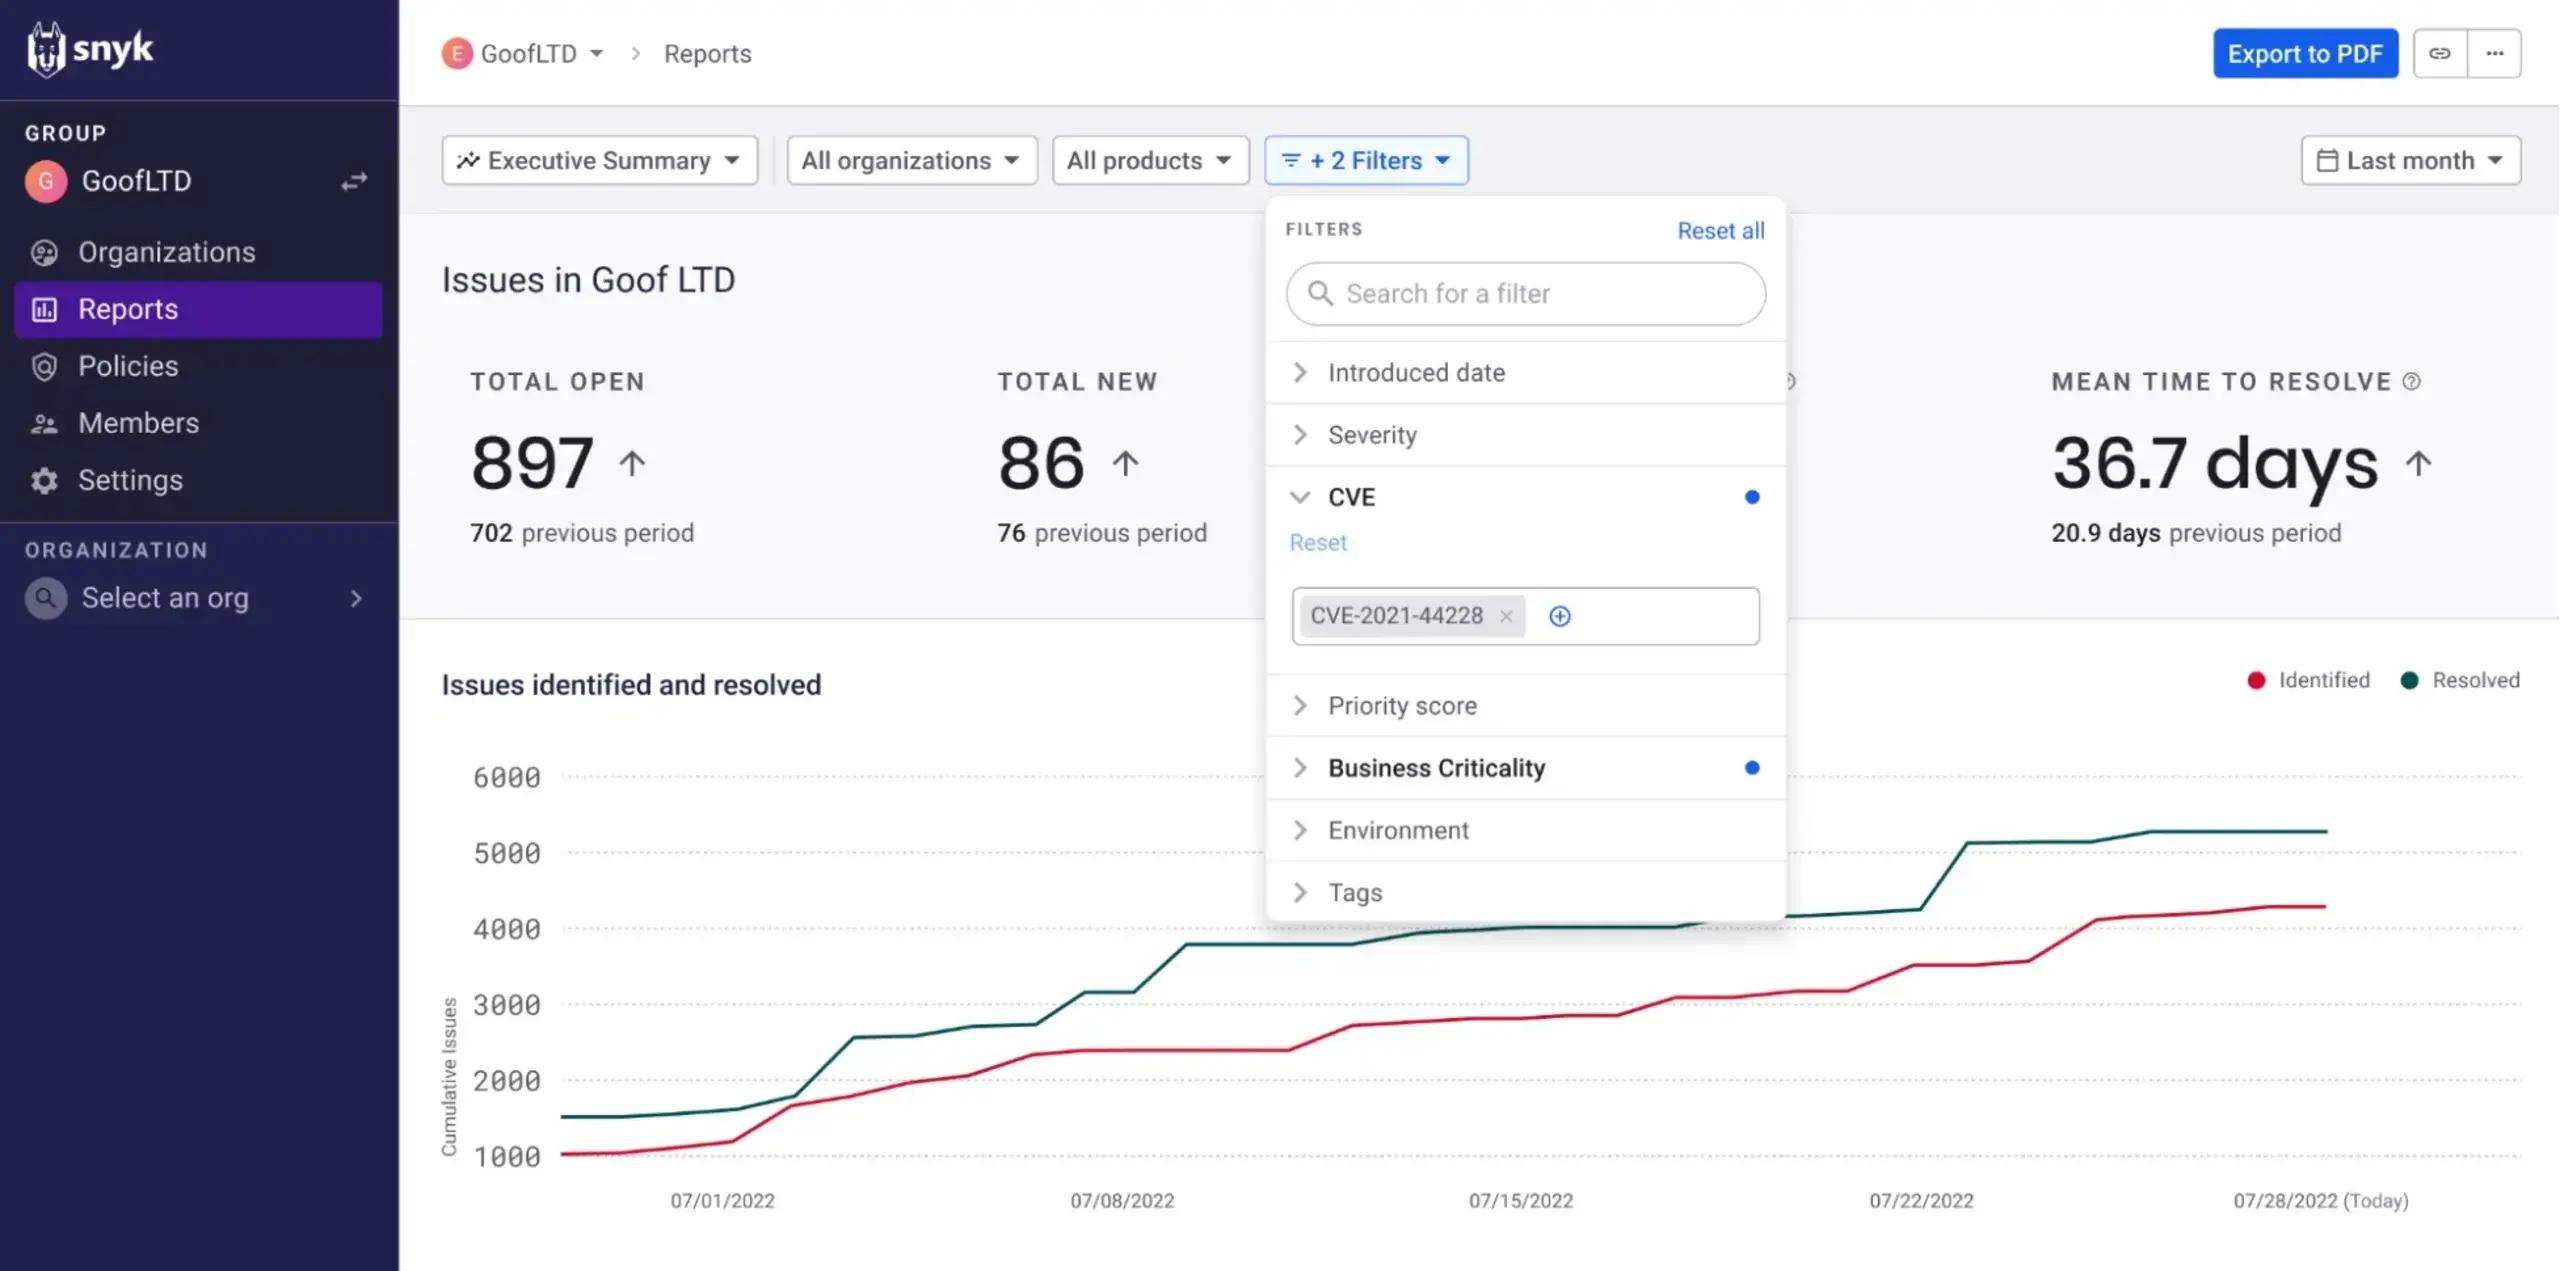
Snyk is a developer-friendly SCA platform that extends into container, IaC, and open-source scanning. It’s widely adopted by DevOps teams for its automation and intuitive user experience.
Its strength lies in actionable remediation. Snyk not only detects vulnerabilities but also suggests and applies fixes automatically through pull requests.
Key features
Automated fix suggestions and pull requests
Container, IaC, and open-source scanning
Integration with GitHub, GitLab, and Bitbucket
Developer-first CLI and IDE support
Real-time vulnerability database updates
Pricing
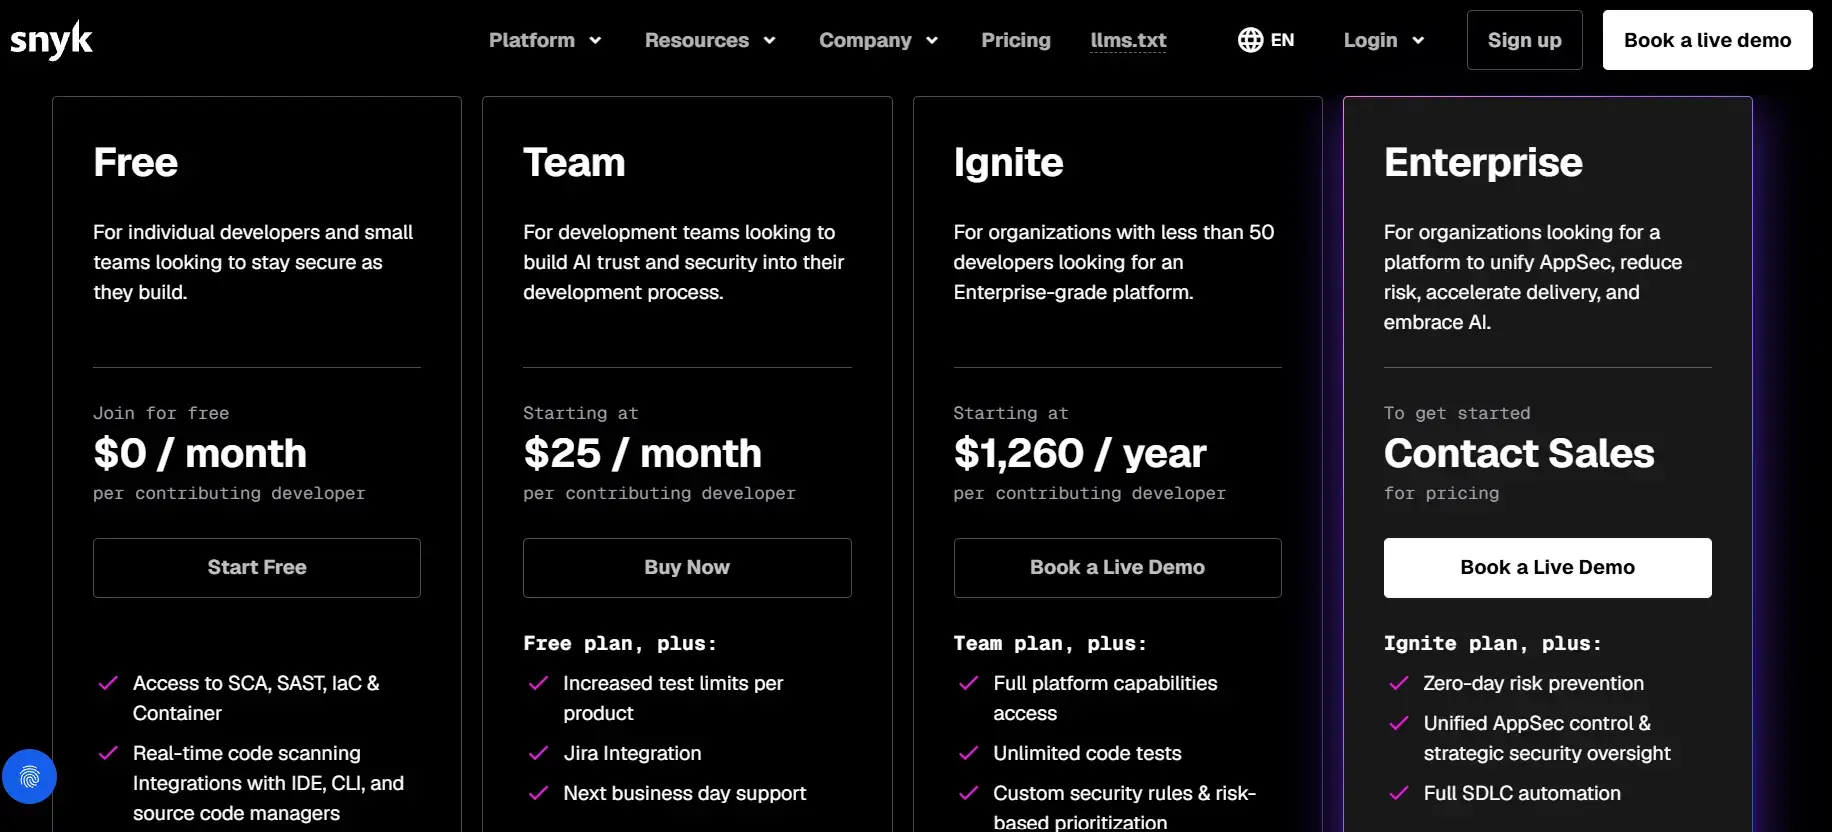
Free tier available
Team Plan: From $25 per developer per month
Enterprise: Custom pricing
Ratings and reviews
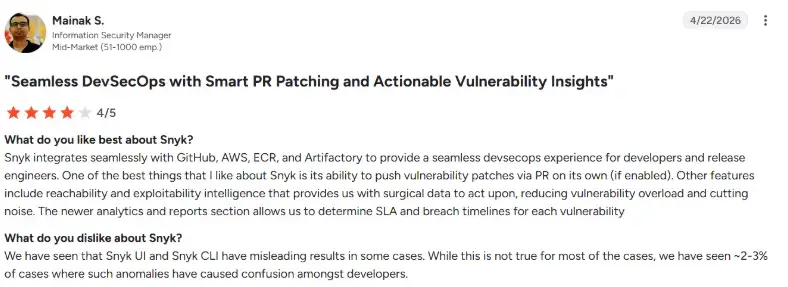
Snyk maintains a strong G2 rating of 4.5 out of 5, widely recognized for its developer-first approach to security scanning and open-source dependency management. Reviewers frequently highlight its seamless IDE integration, fast feedback loops, and actionable fix suggestions. While some users mention pricing increases for larger teams, most agree it delivers exceptional value for securing modern development workflows.
What makes a good software security audit tool
As you evaluate security audit tools, weigh the following factors to make sure the solution fits your workflow and organizational needs.
| Factor | What to look for |
|---|---|
| Platform support | Support for diverse environments, from on-premise to cloud-native and containerized systems, with compatibility across multiple OS and deployment models so your options stay open as your architecture evolves |
| Integration with CI/CD tools | Direct integration with tools like Jenkins, GitHub Actions, or GitLab CI, so you can run automated scans and fail builds when vulnerabilities exceed a defined threshold |
| False positive ratio | AI-driven validation or proof-based scanning that keeps results reliable and actionable, since high false positive rates waste developer time and erode trust in the tool |
| Coverage | Comprehensive vulnerability coverage, including OWASP Top 10, CWE, and zero-day patterns, plus custom rule support for further adaptability |
| Licensing model | Transparent, predictable pricing, whether the tool charges per application, per developer, or by scan frequency |
| Reporting | Reports that bridge the gap between developers and executives, with both technical remediation detail and compliance-ready summaries |
| Ease of use | Intuitive interfaces, strong documentation, and quick onboarding, all of which meaningfully improve adoption |
Final thoughts
Software security audit tools are essential in 2026 for protecting an expanding digital ecosystem, and each category brings its own strengths. DAST tools like Beagle Security, ZAP, Burp Suite, and Invicti focus on runtime vulnerabilities and real-world attack simulations. SAST tools, including Semgrep, Checkmarx, Veracode, and Coverity, catch security issues directly in the code. SCA tools such as Mend.io and Snyk protect open-source dependencies and supply chain integrity.
Enterprises seeking broad integrations tend to find Invicti and Checkmarx solid picks, while developer-centric workflows lean toward Semgrep and Snyk. Beagle Security stands out for teams that want automation, agentic AI attack simulation, and developer-friendly integration without enterprise pricing.
Building a strong security program isn’t about choosing one tool. It’s about combining the right categories to match your development lifecycle and security goals. Start a 14-day advanced free trial or explore the interactive demo to see how agentic AI penetration testing fits into that mix.
FAQs
What is the difference between DAST, SAST, and SCA?
SAST scans your source code before the application runs, catching issues like hardcoded secrets or injection points early in development. DAST tests a running application from the outside, the way an attacker would, catching runtime issues SAST can’t see. SCA scans your open-source and third-party dependencies for known vulnerabilities and license risk. Most mature security programs use all three together.
What should I look for in a security audit tool besides price?
Platform support, CI/CD integration, false positive ratio, vulnerability coverage, licensing model, reporting quality, and ease of use all affect whether a tool actually gets used consistently by your team, not just whether it’s technically capable.
Do I need more than one type of security audit tool?
Yes, in most cases. Each category has a blind spot the others cover: SAST can’t see runtime behavior, DAST can’t see inside your code, and SCA doesn’t catch logic flaws in code you wrote yourself. A layered approach combining SAST, DAST, and SCA gives more complete coverage than any single tool.