Burp Suite vs ZAP: Which is the best choice for you? [2026]

The DAST tool you choose has a real effect on how well you meet your security goals, not just which vulnerabilities you catch but how much friction testing adds to your team’s workflow. Burp Suite and ZAP (Zed Attack Proxy) are two of the most widely recognized options for dynamic application security testing, and both come up constantly in comparison discussions. Each takes a different approach to finding vulnerabilities, and each suits a different kind of team.
The real question is whether either tool actually fits your specific workflow and organizational requirements. Burp Suite and ZAP sit at opposite ends of the spectrum, commercial depth versus open source flexibility, and that gap can leave some modern DevSecOps needs unmet.
This comparison covers Burp Suite versus ZAP, including their core features, strengths, and limitations. It also introduces Beagle Security as a modern alternative built to close gaps found in traditional DAST tools.
Burp Suite vs ZAP at a glance
| Feature | Burp Suite | ZAP (by Checkmarx) |
|---|---|---|
| Target market | Security professionals, Pen-testers | Developers, security professionals of all skill levels |
| Scanning technology | DAST, Manual testing tools | DAST (automated and manual) |
| Ease of use | Steep learning curve | User-friendly interface, but setup has a learning curve |
| AI features | Limited/none | Limited/none |
| Free trial | No | Free (Open-source) |
| Pricing starts at | Custom quote | Free |
| G2 rating | 4.8/5 from 129 reviews | 4.7/5 from 14 reviews |
| Capterra rating | 4.8/5 | 5/5 |
An alternative web & API penetration testing platform: Beagle Security
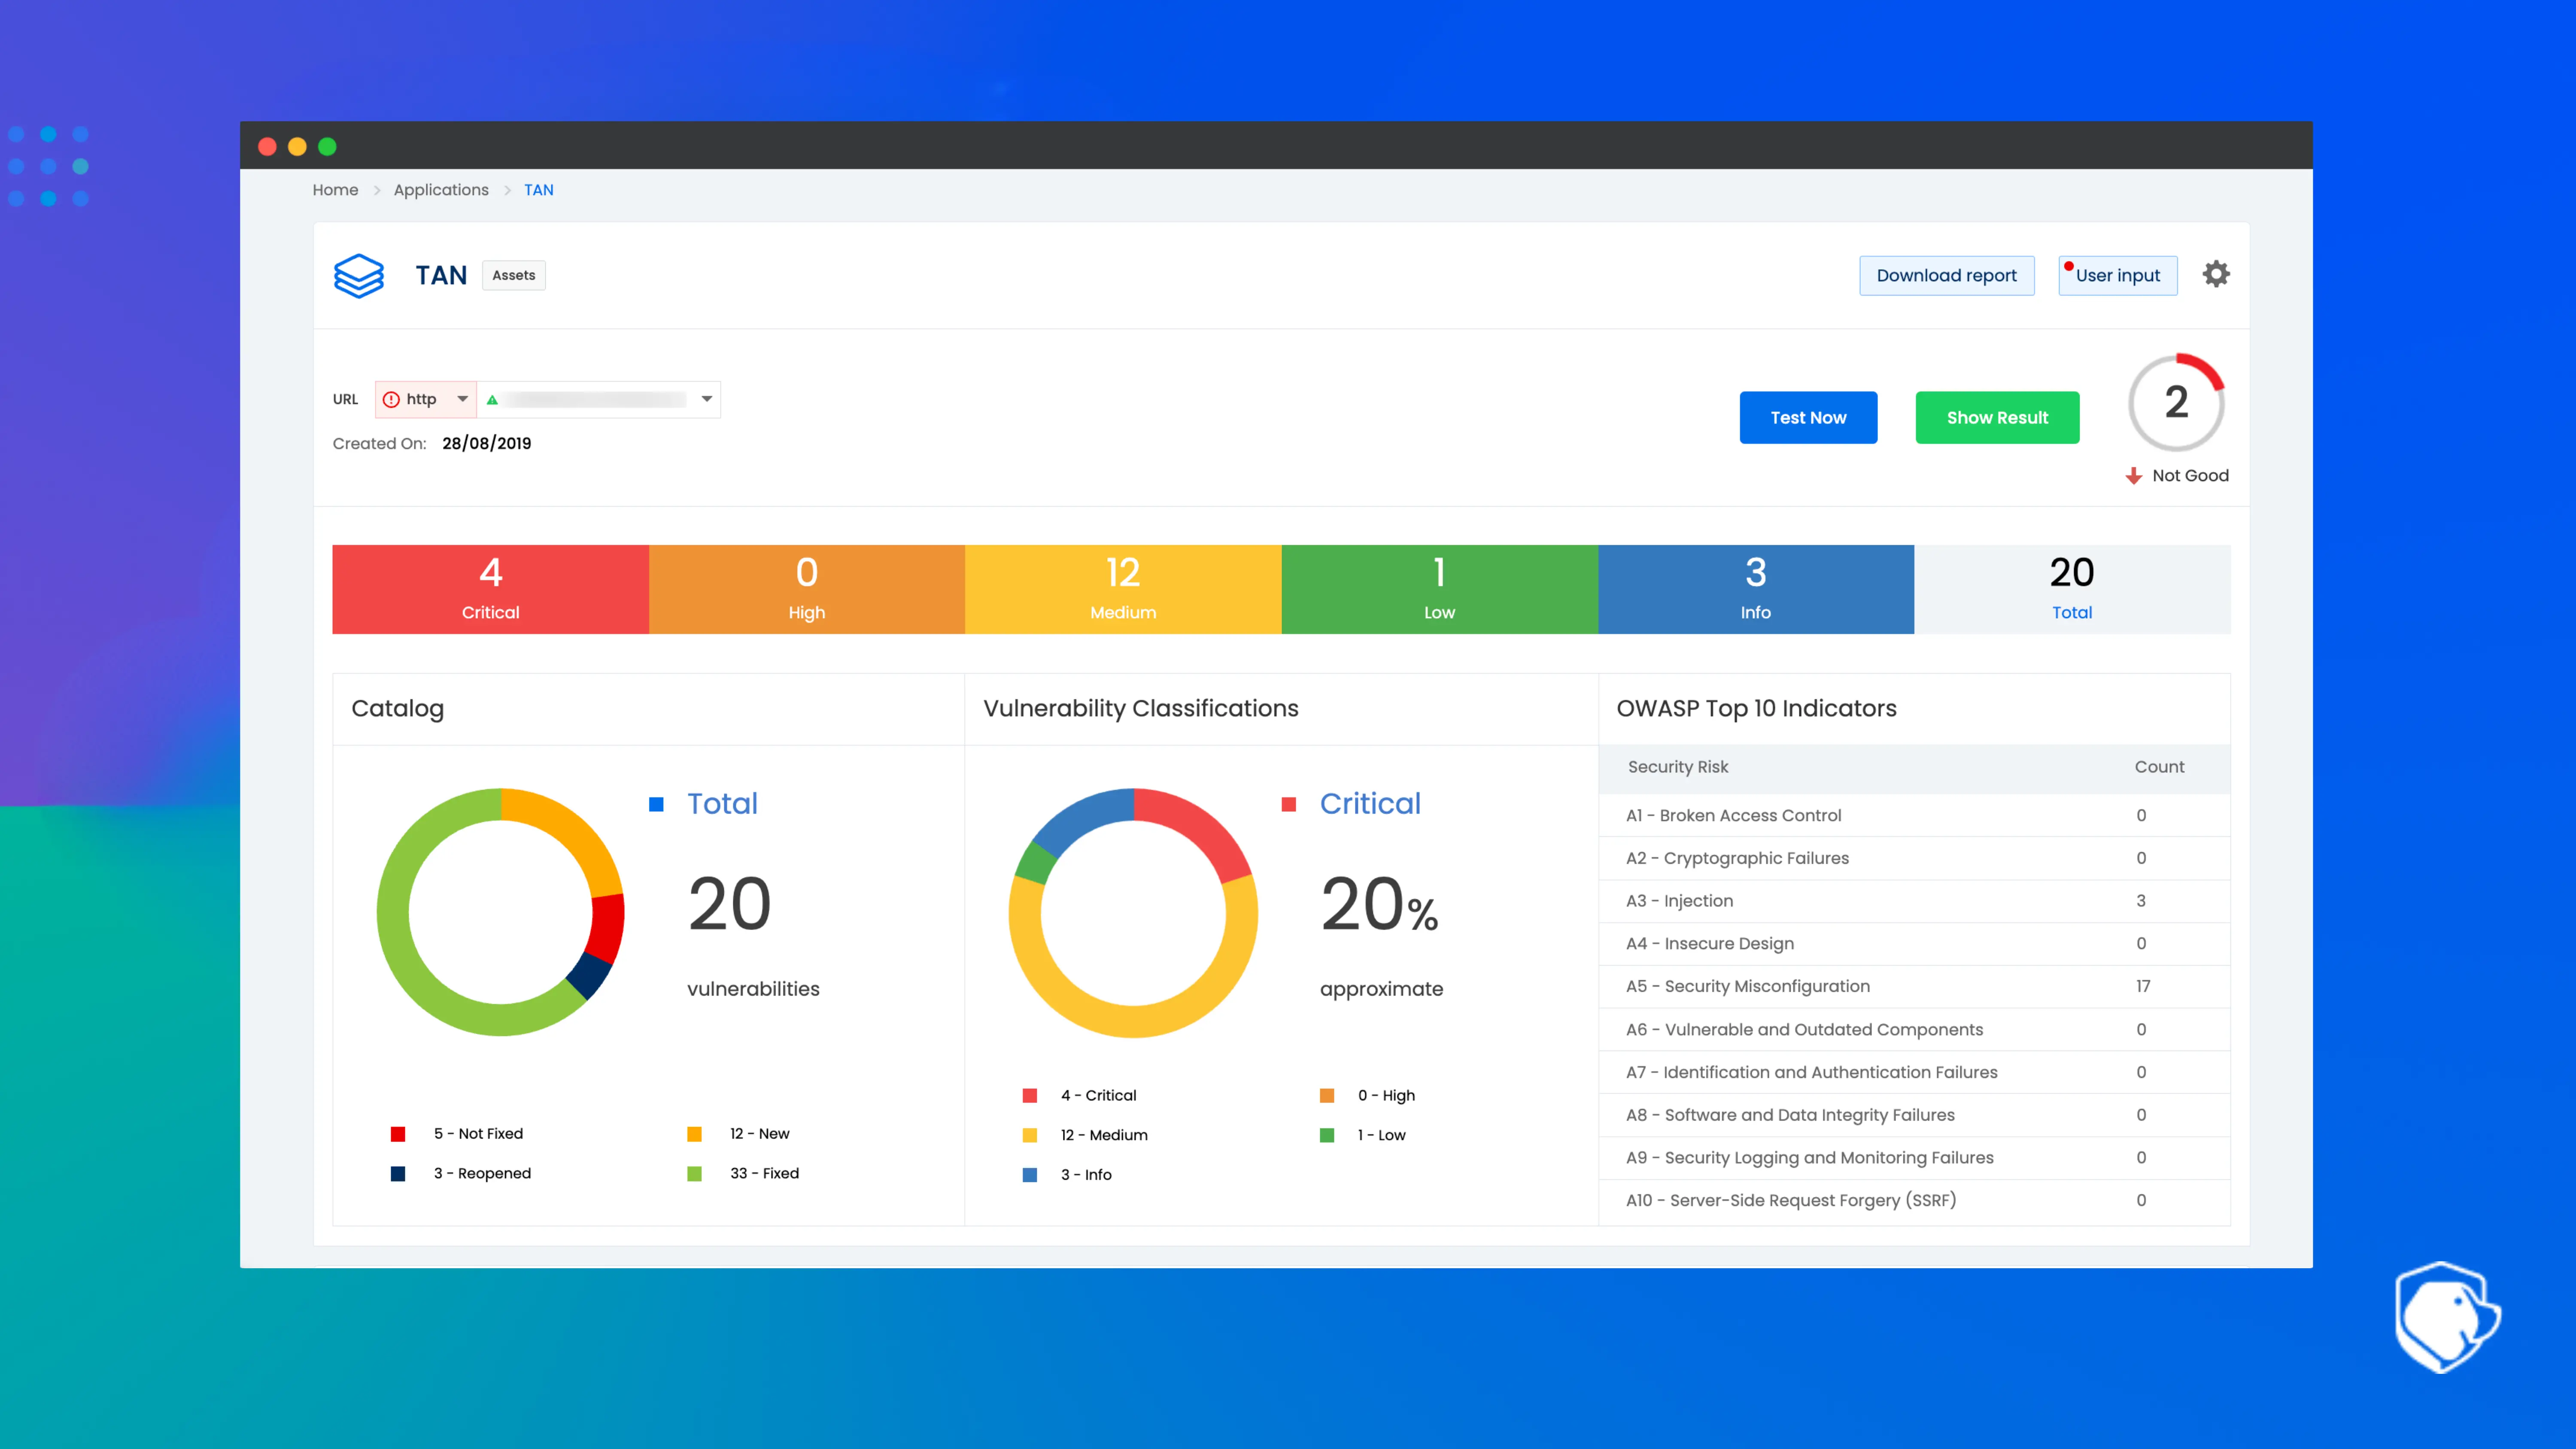
Beagle Security is a next-generation DAST platform built from the ground up to solve a problem many organizations face: balancing depth of testing, ease of use, and affordability without compromising on enterprise-grade capabilities.
While Burp Suite and ZAP come from different ends of the spectrum (commercial vs. open-source), Beagle Security takes a more developer-first and DevSecOps-friendly approach that appeals equally to security and engineering teams.
Beagle Security’s strength lies in its AI-powered automation, its ability to adapt to modern web technologies (including SPAs and GraphQL APIs), and the flexibility it offers without the complexity often associated with legacy tools.
Why consider Beagle Security in the Burp Suite vs ZAP conversation?
Advantages:
Fast to start: Minimal learning curve, teams of any skill level can get going quickly
Contextual vulnerability reports: Findings prioritized and mapped to your app logic, with remediation guidance tailored to your tech stack instead of generic suggestions
No lock in on targets: Concurrent test based enterprise pricing instead of per FQDN limits, which gives more flexibility for growing teams and multi app environments
Enterprise-grade features without the price tag
| Capability | What it does |
|---|---|
| AI based login flow navigation | Automatically navigates authenticated flows during testing |
| Business logic understanding | Tests how your application actually behaves, not just known attack patterns |
| Intelligent test case selection | Adapts test cases to your specific application architecture |
| False positive filtering | Cuts down on noise so findings are more likely to be real |
| Real world attack simulation | Built on penetration testing principles rather than static, predefined scans |
Burp Suite vs ZAP vs Beagle Security: Feature comparison
| Feature | Burp Suite | ZAP (by Checkmarx) | Beagle Security |
|---|---|---|---|
| API security | Yes | Yes (REST, GraphQL) | Full support (REST, GraphQL) |
| AI-based login authentication | No | No | Yes |
| CI/CD integration | Yes | Yes | Seamless |
| Developer experience | Complex | Moderate (setup) | Built for developers |
| Reporting & exports | PCI DSS & OWASP Top 10 reports | OWASP Top 10, customizable | Contextual & dev-friendly |
| OWASP mapped reports | Yes | Yes | Yes |
| False positive filtering | Manual | Manual effort | Agentic AI-assisted |
| PCI DSS compliance reports | Yes | No | Yes |
| HIPAA compliance reports | No | No | Yes |
| Scheduled testing | Yes | Yes | Yes |
| Scan SPAs | Yes | Yes | Yes |
| SSO Supported Testing | Yes | Yes | Yes |
Burp Suite features
Key Burp Suite features:
Scheduled testing
CI/CD integrations
Scan SPAs
PCI DSS & OWASP Top 10 reports
SSO supported testing
Burp Suite is primarily known for its depth as a manual penetration testing toolkit. It offers some automated scanning, but its real strength is letting security professionals analyze and manipulate web traffic directly, which makes it a common choice for in depth vulnerability discovery. That power comes with a steep learning curve, and it can be resource intensive for large scale scanning.
ZAP (by Checkmarx) features
Key ZAP features:
Open-source DAST tool for identifying web application vulnerabilities.
Offers automated and manual security testing, accessible to all skill levels.
Automated scanner tests for common vulnerabilities like XSS and SQL injection.
User-friendly interface and integrates with development workflows.
ZAP (Zed Attack Proxy) by Checkmarx is a popular open-source DAST tool designed to help identify security vulnerabilities in web applications. It provides both automated and manual testing capabilities, making it accessible for a wide range of users, from developers to experienced security testers.
Its automated scanner uses predefined attack scripts to detect common vulnerabilities such as cross site scripting, SQL injection, and broken authentication. ZAP’s interface is generally described as approachable, which helps it fit into development workflows for early detection and remediation. The known tradeoff is that initial setup is complex and presents a real learning curve for new users.
Beagle Security features
Key Beagle Security features:
Agentic AI pentesting and business logic testing
Contextual remediation guidance based on tech stack
Full API security support (REST, GraphQL)
Real-world penetration testing simulations
Intelligent test case selection and false positive filtering
Seamless CI/CD integration and DevSecOps alignment
Concurrent test-based pricing for enterprise flexibility
Easy onboarding and intuitive UX
Beagle Security is designed for modern development practices. Its AI engine goes beyond predetermined scripts, analyzing the application’s tech stack and generating contextual test cases.
The automated penetration testing capability understands how an attacker might exploit your specific application architecture, catching business logic flaws traditional scanners miss. API security testing is a strong point, designed for API-first organizations and supporting API discovery.
Beagle Security’s continuous security testing adapts to your development cycle, and its dynamic test case selection means the platform evolves its testing approach based on what it learns about your applications.
Burp Suite vs ZAP vs Beagle Security: Pricing comparison
| Platform | Starting price | Free trial |
|---|---|---|
| Burp Suite | Custom quote | No |
| ZAP (by Checkmarx) | Free (open-source) | Free |
| Beagle Security | Self-serve plans start at $1188/year. | 14-day free trial |
Burp Suite pricing
Burp Suite pricing is typically custom and depends on the specific edition (e.g., Community, Professional, Enterprise) and the features required.
- Burp Suite Professional: $499 per user per year
For larger organizations and enterprise-grade scanning, it can be a significant investment, often requiring dedicated security personnel to maximize its capabilities.
ZAP (by Checkmarx) pricing
ZAP (Zed Attack Proxy) by Checkmarx is an open-source, non-profit tool. As such, it is entirely free to use, making it a highly attractive option for individual developers, small teams, and those with budget constraints. Its open-source nature means the community contributes to its development and support.
Beagle Security pricing
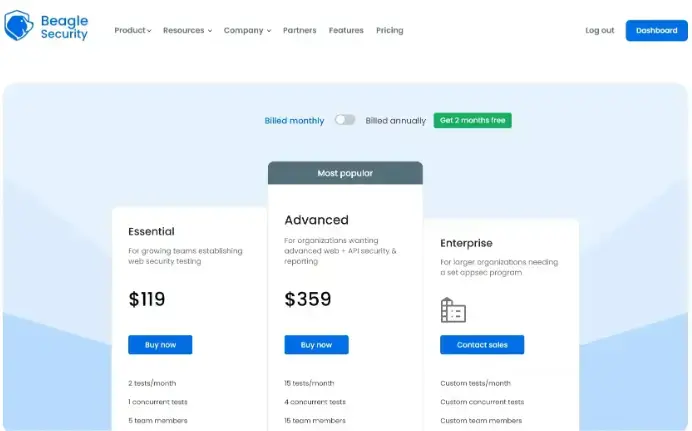
Beagle Security offers transparent and scalable pricing. Pricing is based on features and usage, not arbitrary target limits. It offers annual and monthly plans with MSSP-friendly models. Most importantly, you can try it for free before deciding. Even at lower tiers, core features like AI automation, business logic testing, and CI/CD integration are accessible, making it one of the most cost-effective platforms for proactive security testing.
Burp Suite vs ZAP vs Beagle Security: Customer reviews comparison
| Platform | G2 rating |
|---|---|
| Burp Suite | 4.8/5 based on 129 reviews |
| ZAP by Checkmarx | 4.7/5 based on 14 reviews |
| Beagle Security | 4.7/5 based on 87 reviews |
*As of latest G2 comparison in July 2026 *As of latest Capterra comparison in July 2026
Burp Suite reviews
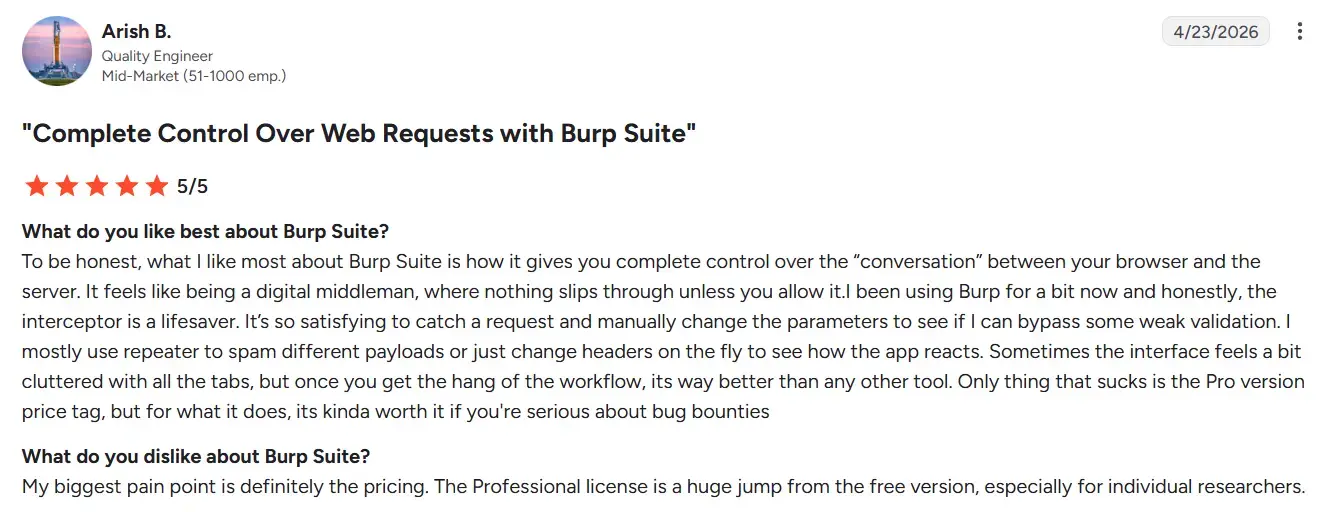
Users appreciate Burp Suite’s powerful features for detailed manual testing and its flexibility for advanced security professionals. However, customers commonly complain about the steep learning curve required to master the platform and that it can be resource-intensive, particularly for large-scale or continuous scanning.
ZAP (by Checkmarx) reviews
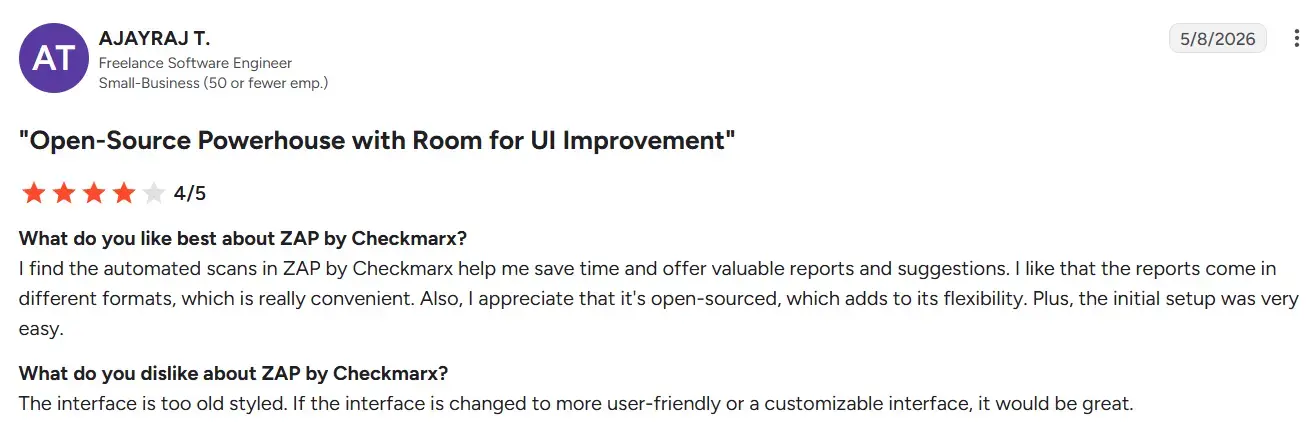
ZAP generally receives positive feedback, particularly for its accessibility as a free, open-source tool and its effectiveness in identifying common web vulnerabilities.
Users praise its strong community support and the ability to customize and extend its functionalities. However, some users note the initial learning curve associated with setting up and configuring the tool, which might require some technical proficiency.
Beagle Security reviews
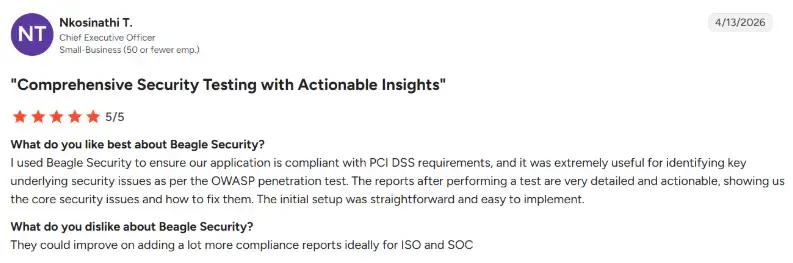
Beagle Security is praised for its intuitive UI, developer-first reporting, realistic testing, and affordable pricing. Many customers appreciate its AI capabilities and fast, responsive support. Users consistently highlight the ease of onboarding, configuration, and launching tests. Reports are structured for technical clarity and business context, reducing dependency on security experts for interpretation.
Burp Suite vs ZAP vs Beagle Security: Which is best for you?
The right pick usually comes down to whether you need deep manual control, free and flexible open source tooling, or modern coverage without per target pricing.
| Tools | Choose if: |
|---|---|
Burp Suite: |
|
ZAP (by Checkmarx): |
|
Beagle Security: |
|
Elevate your application security with Beagle Security
The choice between Burp Suite and ZAP often comes down to a trade-off: commercial depth versus open-source flexibility. While both are valuable tools, they may not fully address the demands of modern DevSecOps, especially when it comes to balancing advanced automation, ease of use, and scalability.
Beagle Security offers a compelling alternative, designed to provide comprehensive, agentic AI penetration testing that integrates seamlessly into today’s fast-paced development environments.
Discover how Beagle Security can provide the advanced capabilities you need, without the traditional complexities or budget constraints.
You can start a 14-day free trial or schedule a demo to get started with the Beagle Security platform.
FAQs
Is Burp Suite better than ZAP?
It depends on what you need. Burp Suite offers deeper manual testing control for security professionals, while ZAP gives you a free, open source option that’s more accessible across skill levels. Neither is universally better, they’re built for different workflows.
What is the difference between Burp Suite and ZAP?
Burp Suite is a commercial tool built around deep, manual penetration testing with a steep learning curve. ZAP is free and open source, offering both automated and manual testing that’s more approachable for developers and teams without dedicated security specialists.
Is ZAP by Checkmarx really free?
Yes. ZAP is entirely free and open source, maintained through community contributions, with no paid tier required to use its core scanning and testing features.