Top Indusface WAS alternatives in 2026
Indusface WAS has built its reputation as a managed web application security testing service that blends AI powered scanning with manual validation from certified security experts. It sits between automated DAST and full scale penetration testing, with pricing starting around $59 per app per month for continuous scanning and manual verification of findings.
As development cycles become more agile and DevSecOps adoption grows, teams increasingly need faster, more scalable, and more autonomous testing. Many now prefer self service platforms that combine automation, CI/CD integration, and a low false positive rate without relying on manual validation for every finding.
The DAST market in 2026 includes several strong alternatives, from agentic AI pentesting platforms like Beagle Security to developer focused tools like StackHawk and hybrid platforms like Bright Security. This guide compares the top 10 Indusface WAS alternatives, covering their features, pricing, and best use cases to help you choose the right fit.
Indusface WAS alternatives quick comparison table [2026]
| Platform | Starting price | Key strength | Best for |
|---|---|---|---|
| Beagle Security | $119/month | Zero false positives with agentic AI powered module | Teams prioritizing pentest depth & accuracy |
| Invicti | Custom pricing | Proof-based scanning | Enterprises needing certainty |
| Burp Suite | Free for community edition, professional, $499/user/year | Deep testing control | Security professionals |
| Rapid7 InsightAppSec | $175/month/app | Platform integration | Rapid7 ecosystem customers |
| Acunetix | Custom pricing | Comprehensive scanning | Enterprise environments |
| StackHawk | Starts from $10/month | Developer-first approach | Modern engineering teams |
| Snyk DAST | Starts from $25/month | Snyk ecosystem integration | Teams already using Snyk |
| Tenable WAS | Custom pricing | Risk-based prioritization | Organizations in Tenable ecosystem |
| Bright Security | Custom pricing | Developer-centric DAST | Agile teams |
| Qualys WAS | Custom pricing | Integration with Qualys products | Qualys ecosystem users |
Best Indusface WAS alternatives [2026]
1. Beagle Security
Beagle Security stands as a modern evolution from traditional DAST platforms. It empowers teams to run instant, agentic AI-driven pentests with accuracy and zero false positives. It is designed for speed, depth, coverage and integration into DevSecOps pipelines.
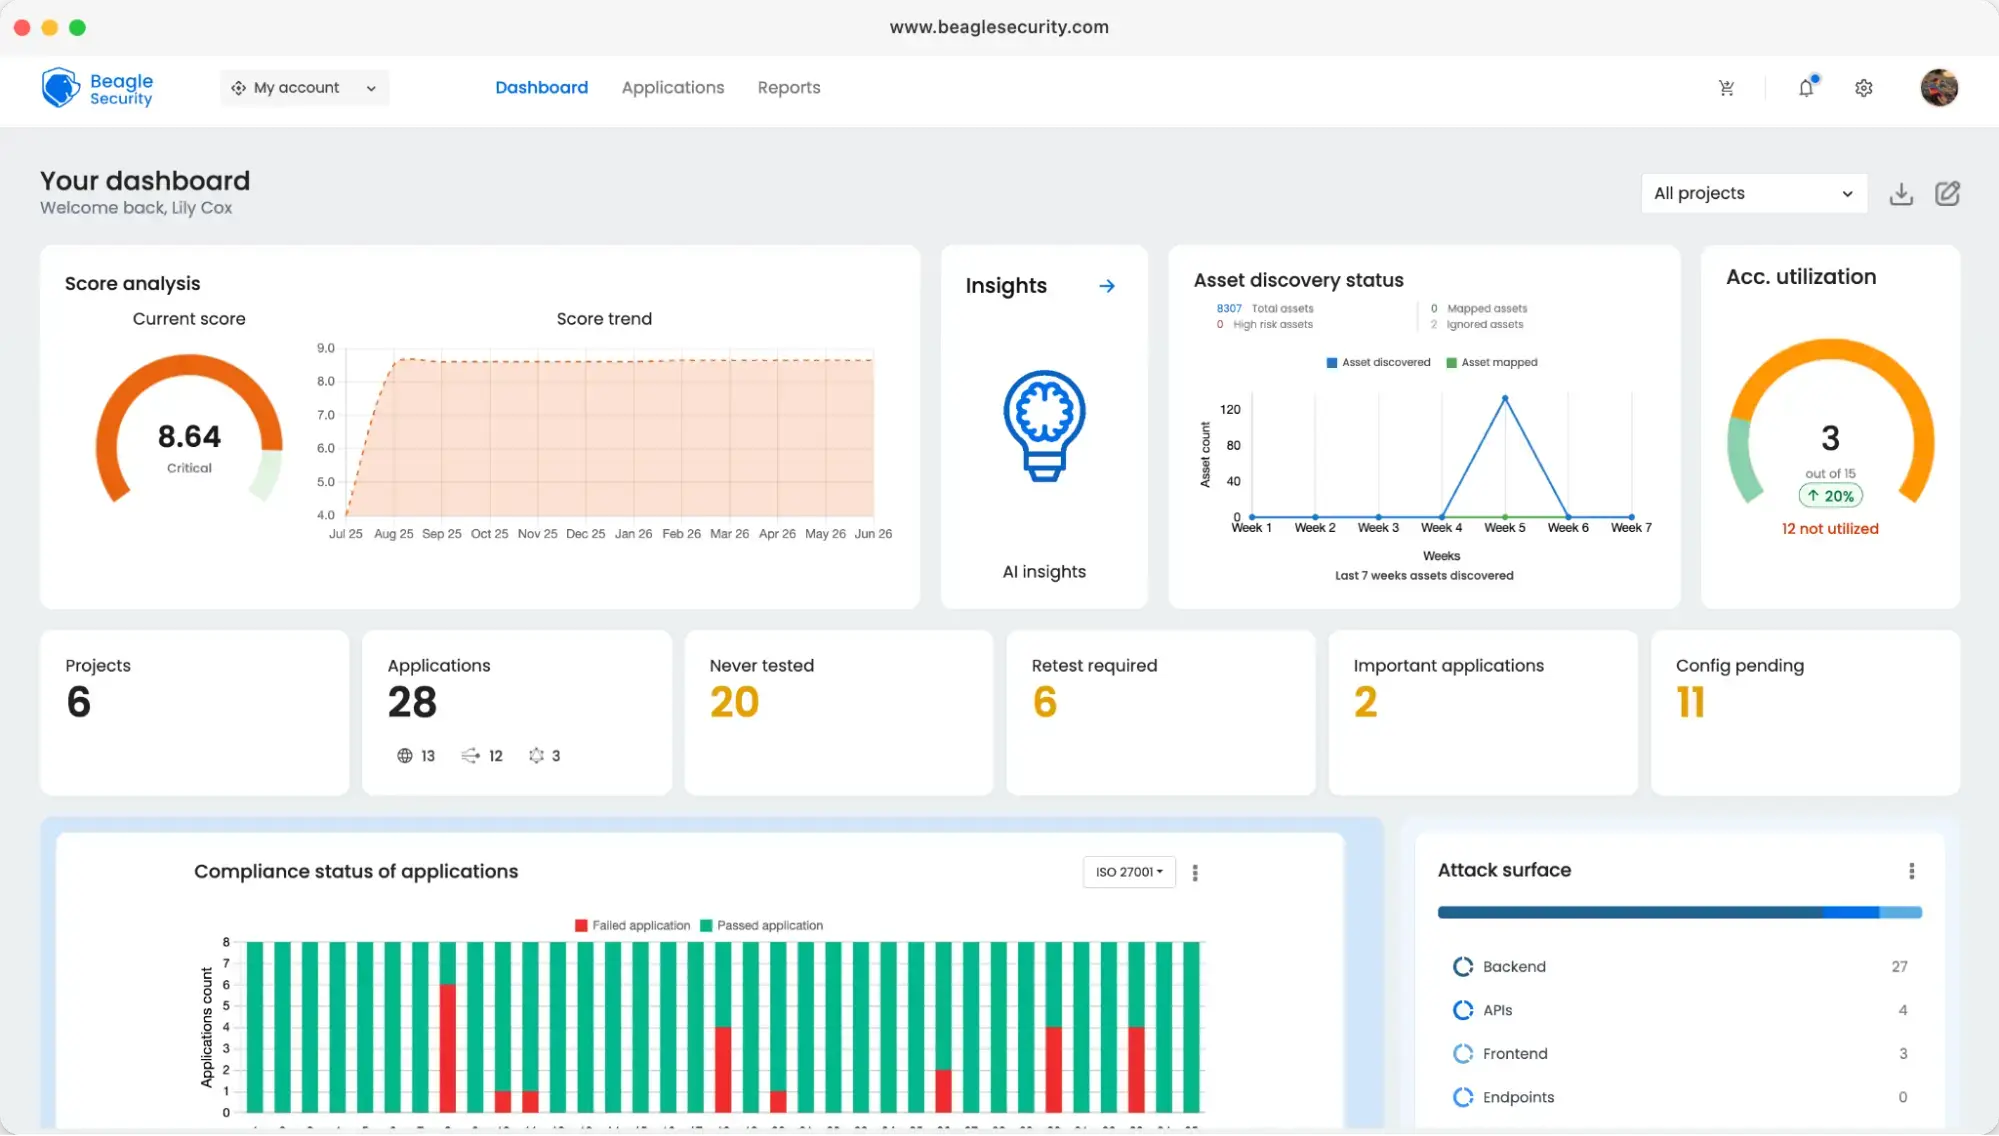
Its self-service model allows you to get started on your own while maintaining enterprise-grade accuracy. Teams can run tests instantly, receive actionable insights, and integrate them directly into CI/CD workflows for true continuous security.
Key features:
Agentic AI-powered zero false positives
Business logic and authentication testing
Full CI/CD integration for DevSecOps pipelines
Supports SPAs, GraphQL, and microservices
Developer-friendly vulnerability reports
Pricing:
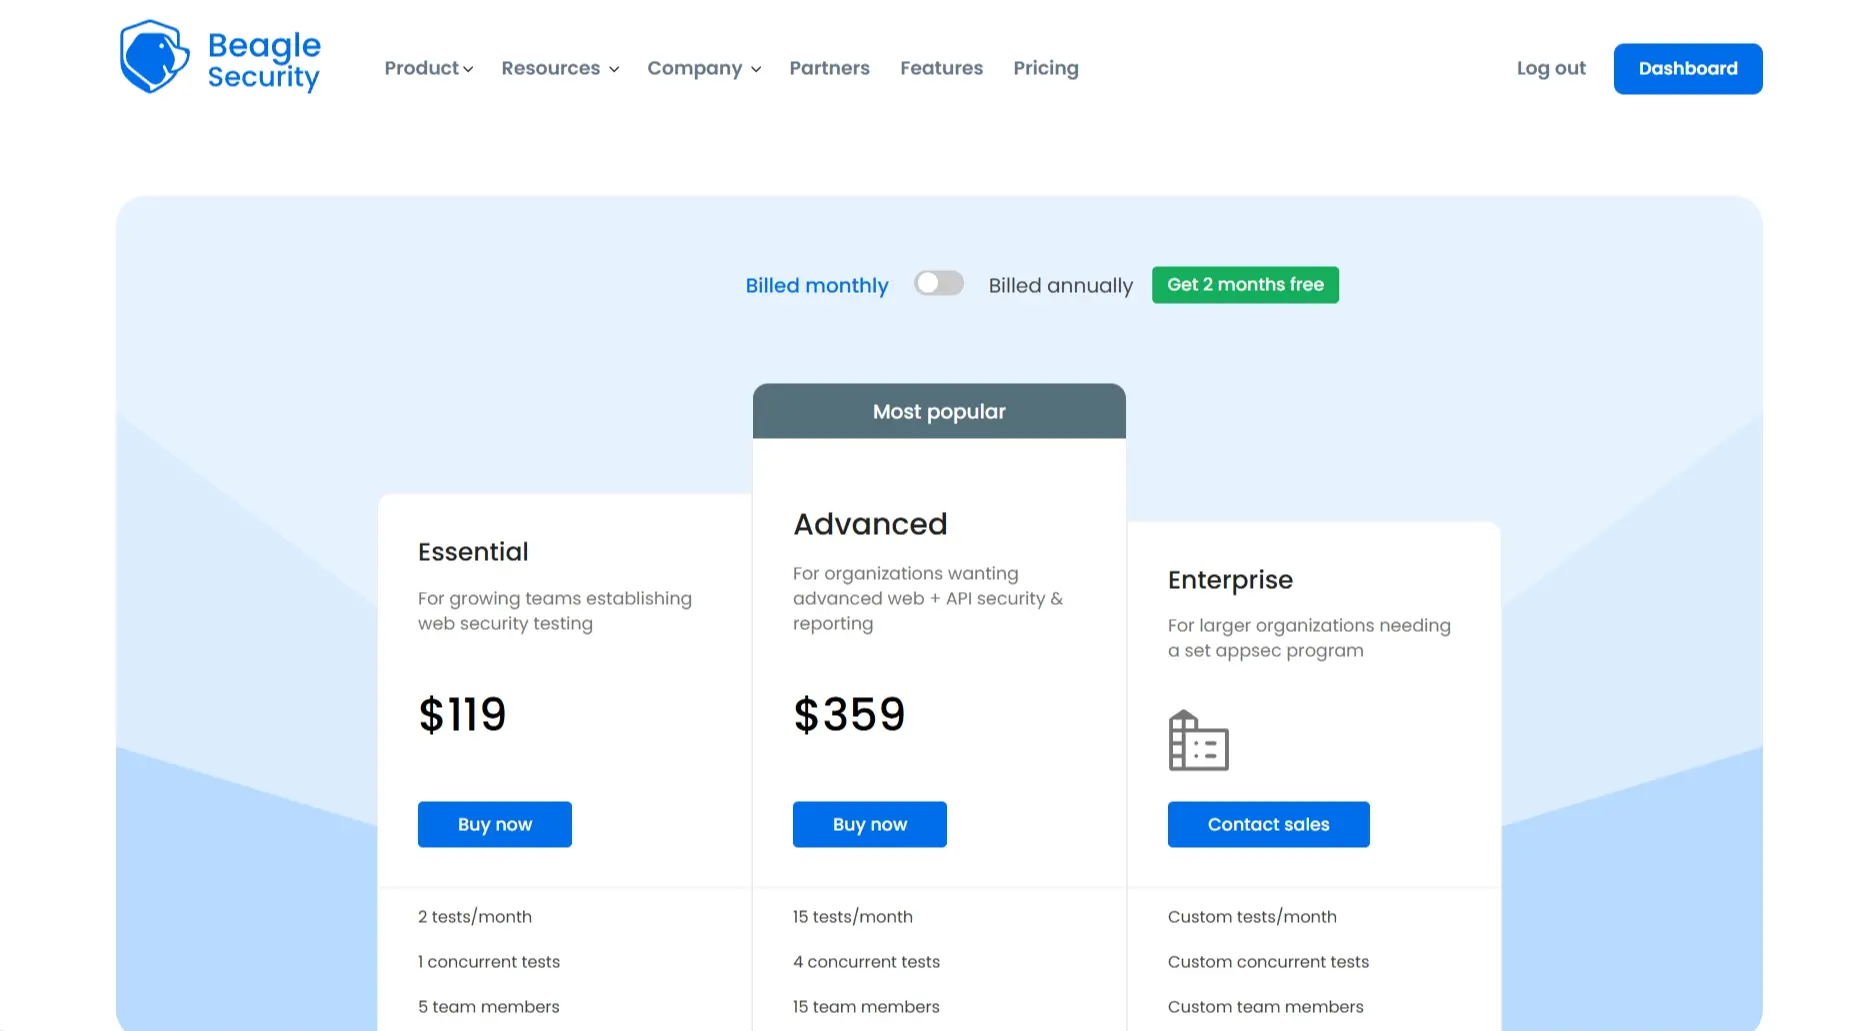
Starts at $119/month
Transparent usage-based scaling
14-day free trial with full features
Ratings and reviews:
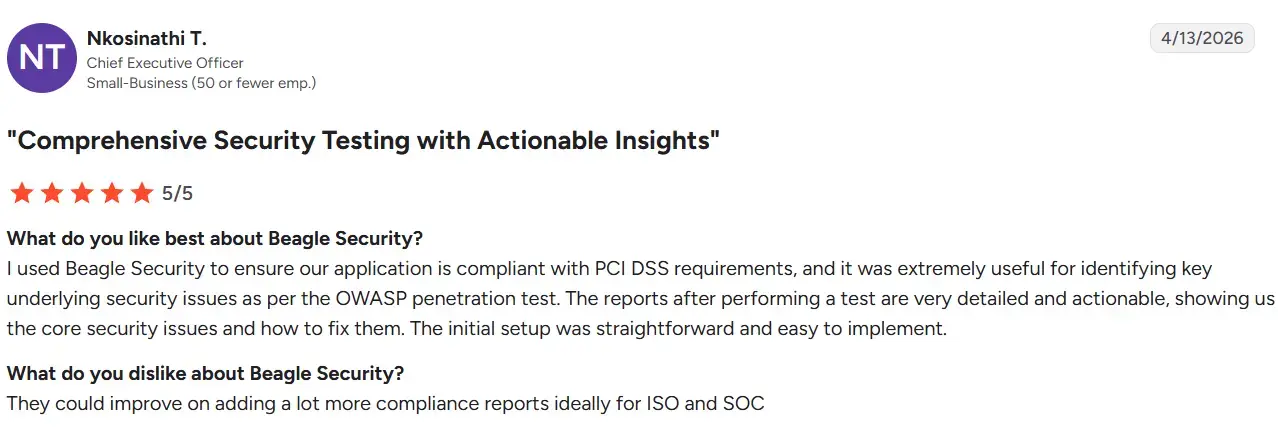
Beagle Security holds a 4.7/5 rating on G2, with users praising its automation, usability, and zero false positive performance. Reviewers often highlight how Beagle Security replaces slow manual reviews with fast, repeatable, and accurate pentests. Many users describe it as “a DAST tool developers actually use,” commending its clean reports and integration-ready workflows.
2. Invicti (formerly Netsparker)
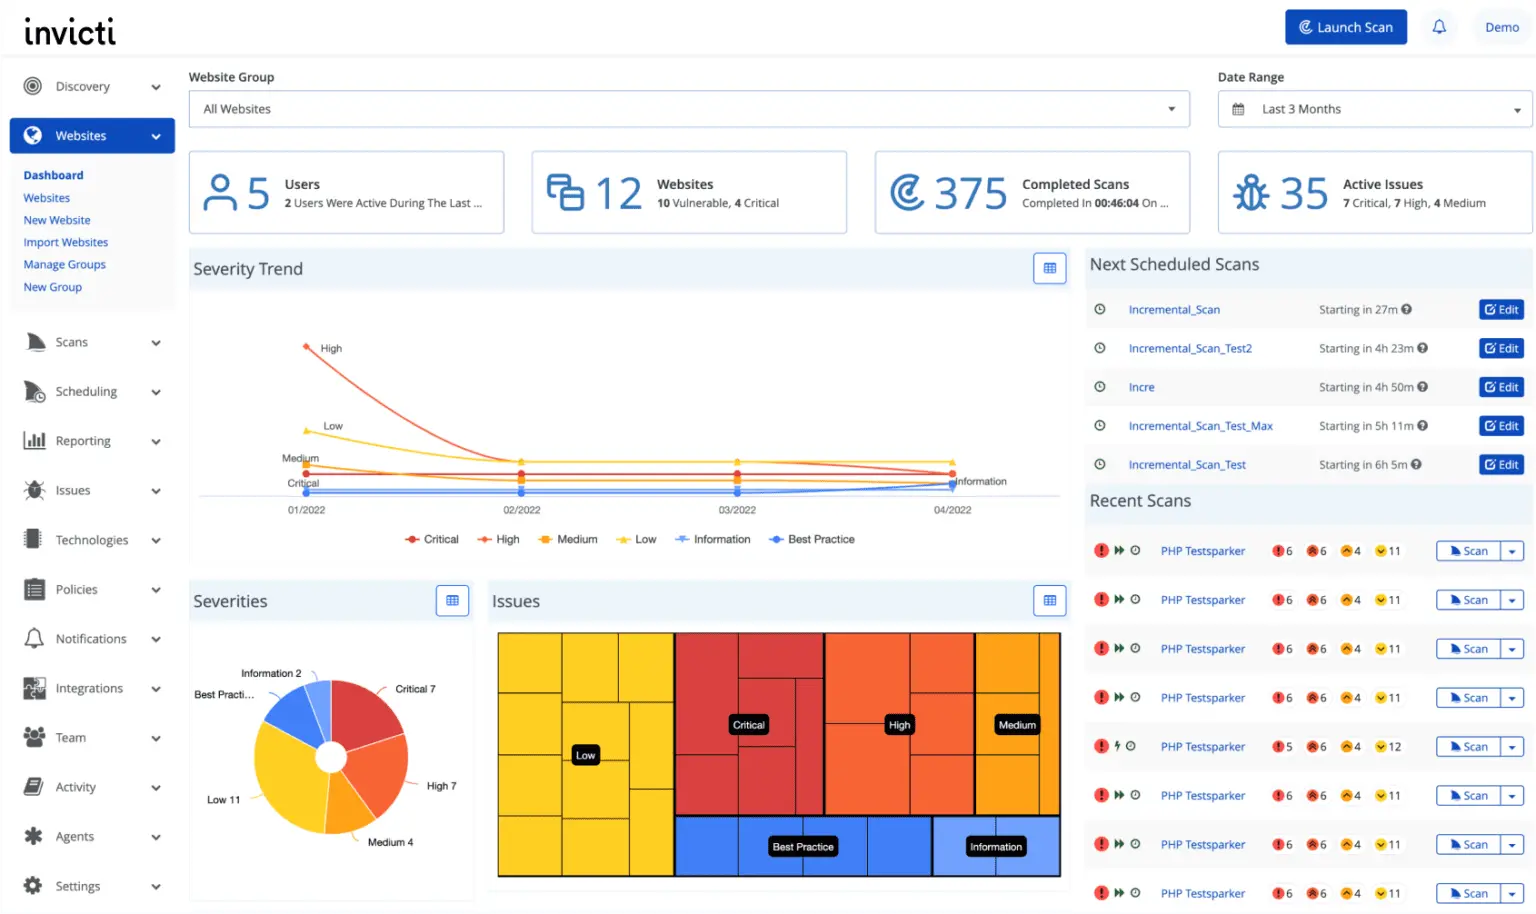
Invicti delivers enterprise-grade automated DAST with its proprietary proof-based scanning technology. Unlike Indusface’s managed model, Invicti is fully self-service, offering reliable validation through its unique approach that confirms vulnerabilities automatically without human intervention.
Its scalability, accuracy, and integrations make it a go-to for enterprises that require autonomy and control. However, its cost and setup complexity place it beyond the reach of smaller organizations.
Key features:
Proof-based vulnerability validation
CI/CD pipeline integration
Multi-user management and reporting
Comprehensive API and web app coverage
Pricing:
Custom enterprise pricing
Tailored per application or domain
Ratings and reviews:
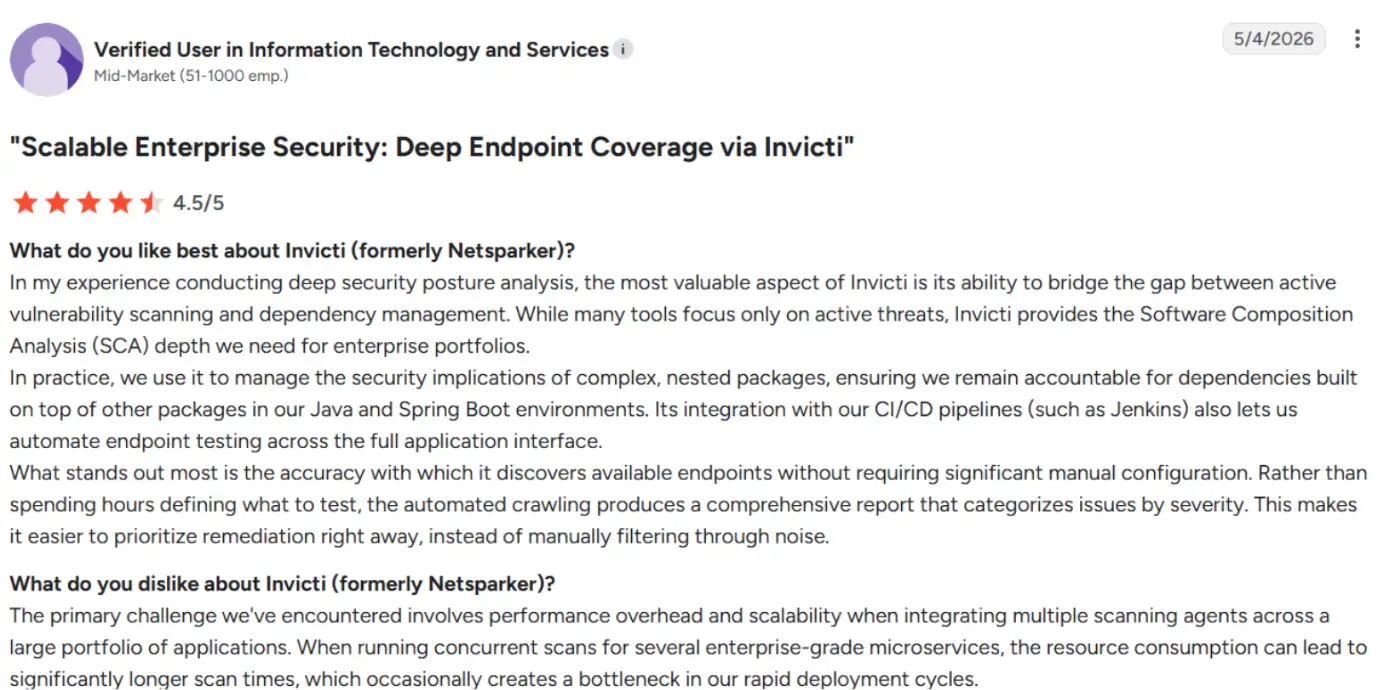
Invicti maintains a 4.6/5 rating on G2, with users praising its accuracy and proof-based confirmation system that virtually eliminates false positives. However, some note that setup and maintenance can be challenging for smaller teams.
3. Burp Suite
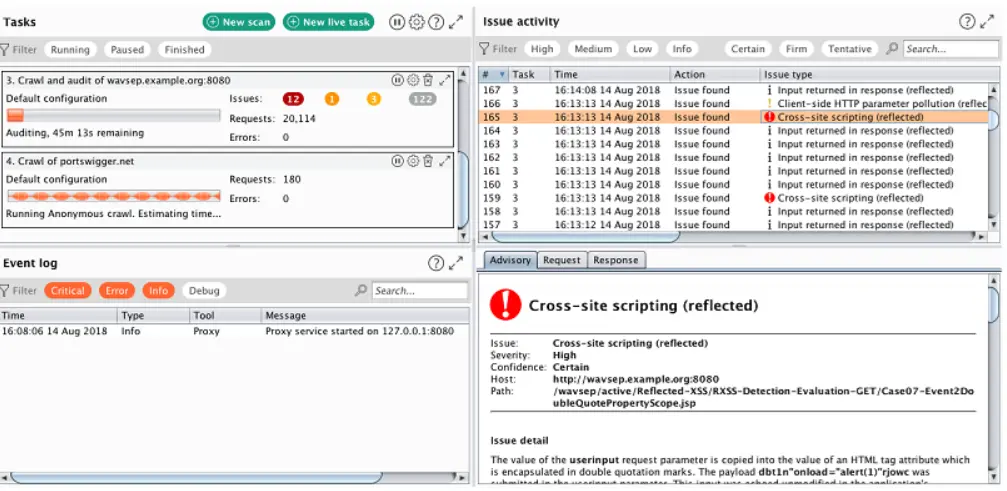
Burp Suite remains a cornerstone in manual penetration testing. Its professional edition enables in-depth manual testing while its enterprise version automates scans at scale. While Indusface WAS offers managed testing through experts, Burp gives testers complete control over the process.
Professionals prefer Burp for its precision, extension ecosystem, and the level of control it provides. However, it demands considerable expertise to operate effectively and does not fit DevSecOps pipelines as naturally as newer tools.
Key features:
Manual and automated scanning modes
BApp Store for extensions
Advanced penetration testing toolkit
Customizable scanning logic
Pricing:
$475 per user per year (Professional Edition)
Custom pricing for Enterprise Edition
Ratings and reviews:
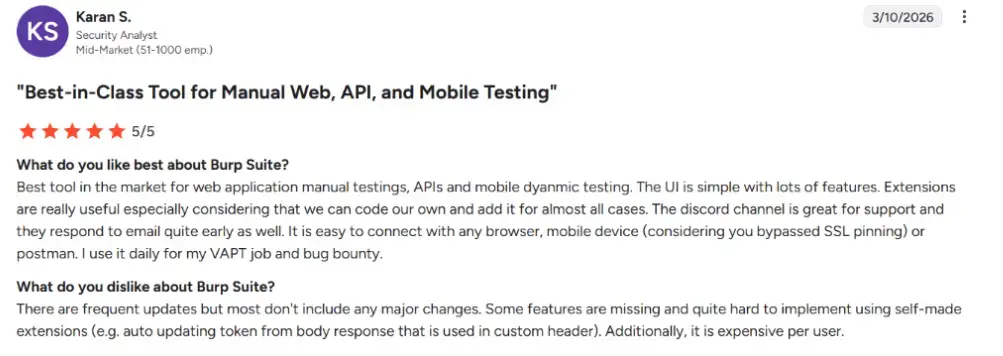
Burp Suite enjoys a 4.8/5 rating on G2, frequently praised for its unmatched manual control. Reviewers note that it remains the go-to for professionals but is less suited for teams seeking speed and automation.
4. Rapid7 InsightAppSec
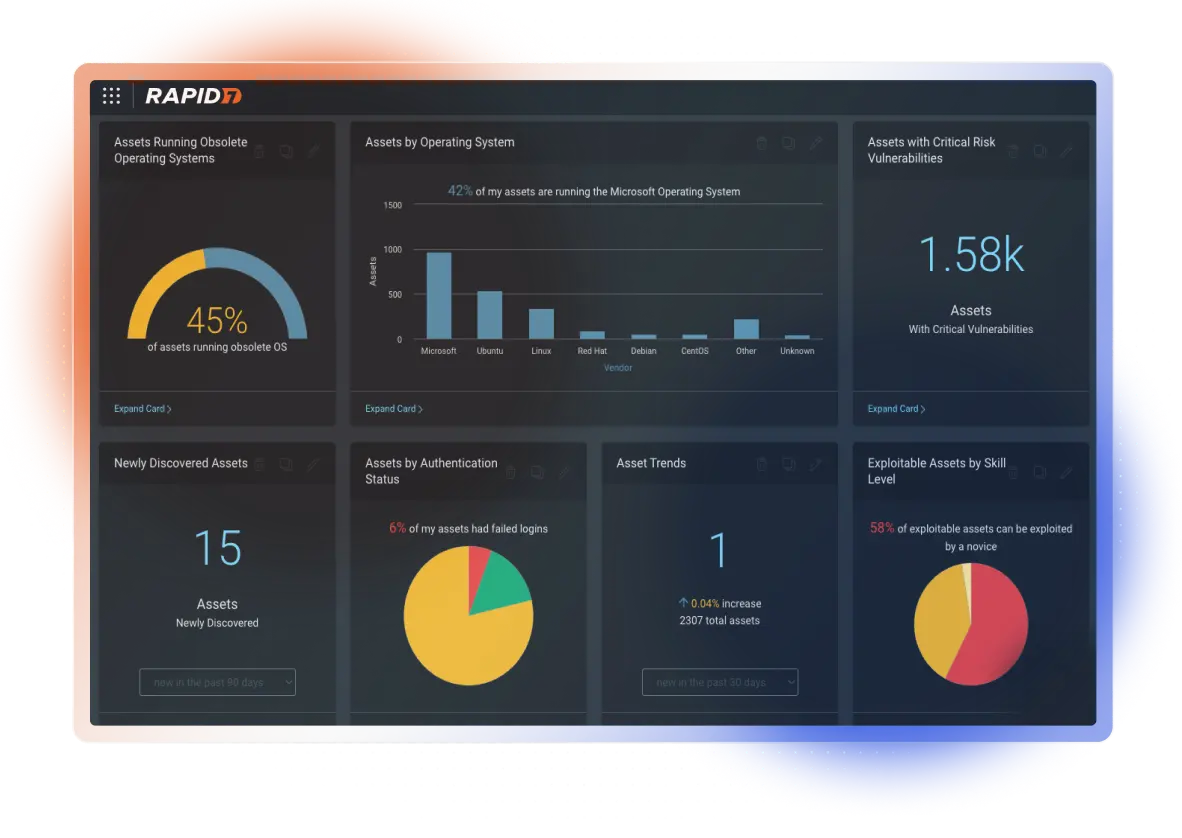
Rapid7 InsightAppSec integrates seamlessly within the Rapid7 Insight cloud platform, enabling vulnerability scanning alongside threat intelligence and asset management. It suits organizations already using Rapid7 solutions.
The platform’s strength lies in its ecosystem integration, providing risk prioritization and correlation with broader security analytics. However, for teams seeking a pure-play DAST tool, it can feel heavy and costlier.
Key features:
Dynamic application testing
Integration with Rapid7 InsightVM and SIEM
Risk scoring and prioritization
Multi-app management
Pricing:
- Starts around $175 per month per application
Ratings and reviews:
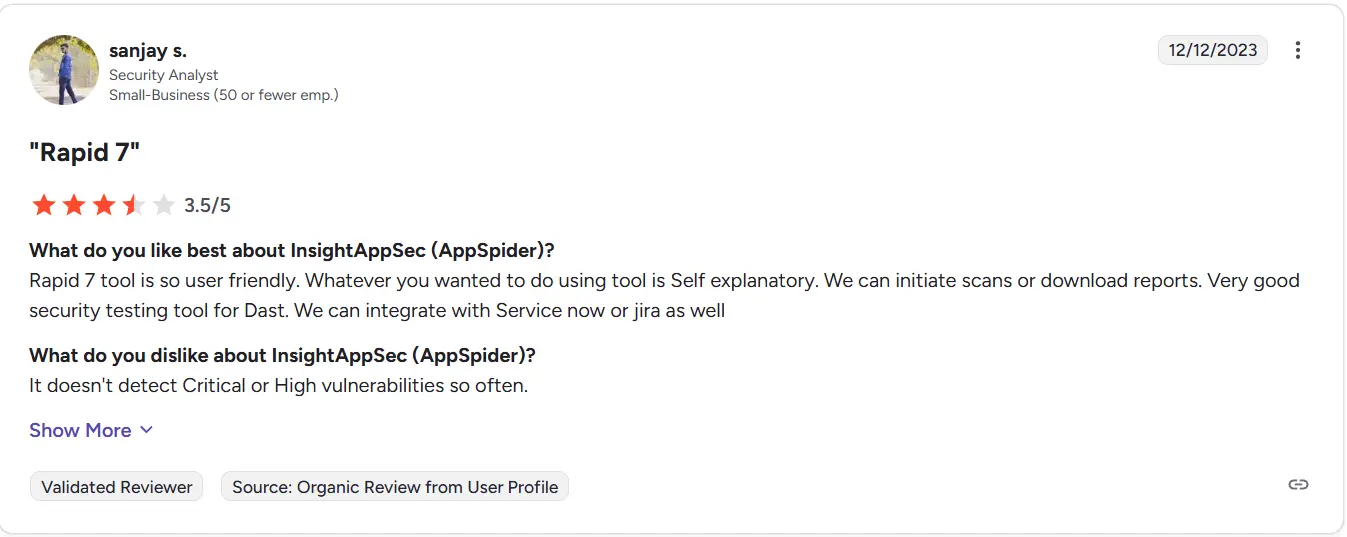
Rated 3.9/5 on G2, users appreciate its integration with the Rapid7 suite. Common feedback highlights its comprehensive analytics but also notes slower scan times compared to standalone DAST tools.
5. Acunetix

Acunetix, now part of Invicti, is known for its automated web application and API security testing. It provides broad coverage for OWASP Top 10 vulnerabilities and beyond, with strong reporting and remediation guidance.
Unlike Indusface, Acunetix is self-service, emphasizing automation and integration over manual intervention. It remains a top choice for enterprise DevSecOps teams that require comprehensive yet manageable testing.
Key features:
Automated scanning of web apps, APIs, and complex websites
Vulnerability verification and remediation guidance
CI/CD pipeline integration
Multi-role management
Pricing:
Custom enterprise pricing
Available as on-premise or cloud
Ratings and reviews:
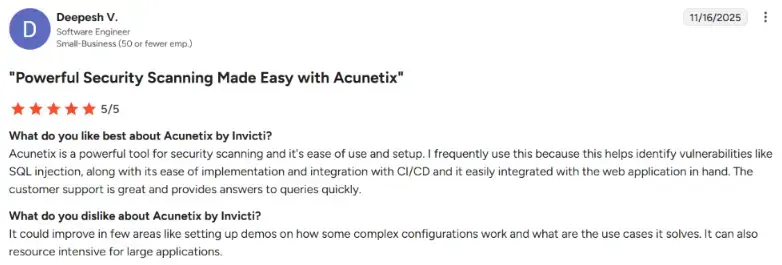
Acunetix maintains a 4.1/5 G2 rating, with reviewers valuing its accuracy and ease of use. Some note that its scans can be resource-intensive for large-scale deployments.
6. StackHawk
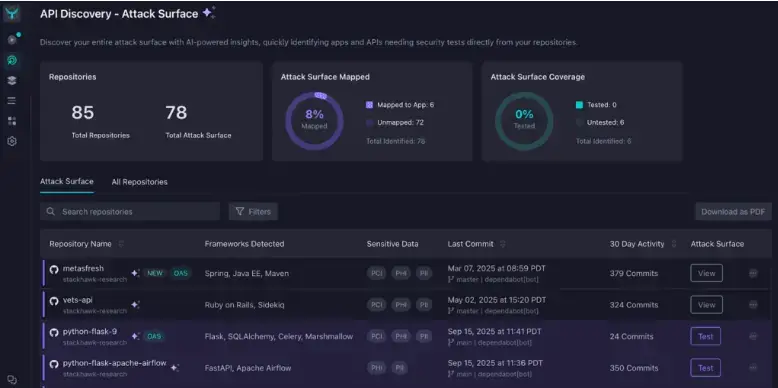
StackHawk is built for developers, making application security part of the CI/CD process rather than a post-release task. Its self-service DAST model focuses on empowering development teams with security ownership.
Compared to Indusface’s managed testing, StackHawk offers speed and autonomy, making it ideal for agile teams that want instant visibility into security issues during builds.
Key features:
CI/CD and container-native integration
API and GraphQL testing
Developer-first UX and automation
Pricing:
AI Coding Agent Security: $10/user/month
Pro: $49 per code contributor per month
Enterprise: $59 per code contributor per month
Custom: Custom pricing
Ratings and reviews:
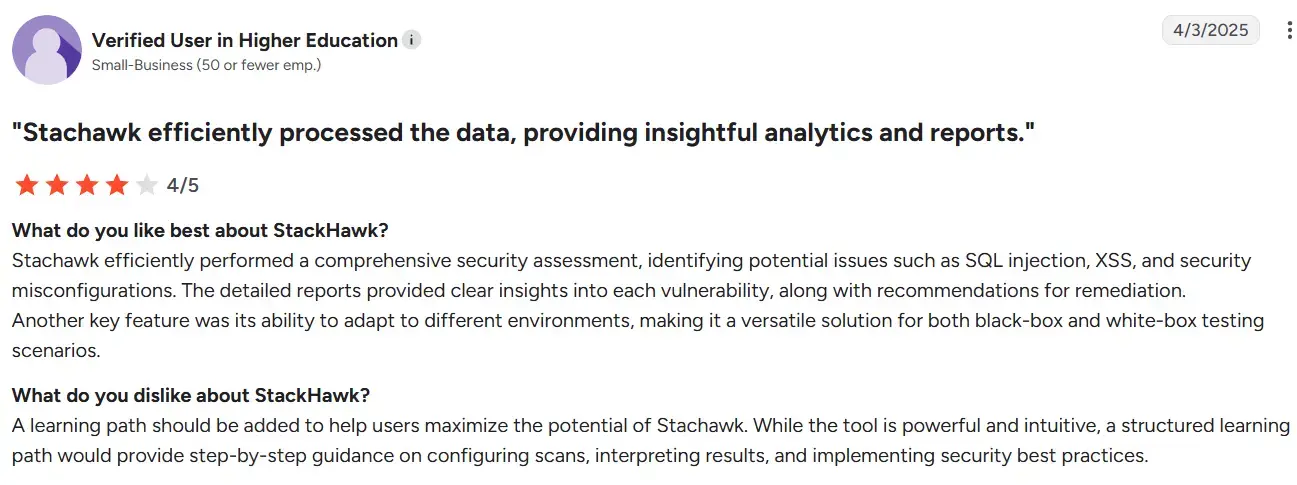
With a 4.6/5 G2 rating, users appreciate StackHawk’s developer-oriented interface and fast feedback loop. Some note it lacks advanced enterprise governance features.
7. Snyk DAST
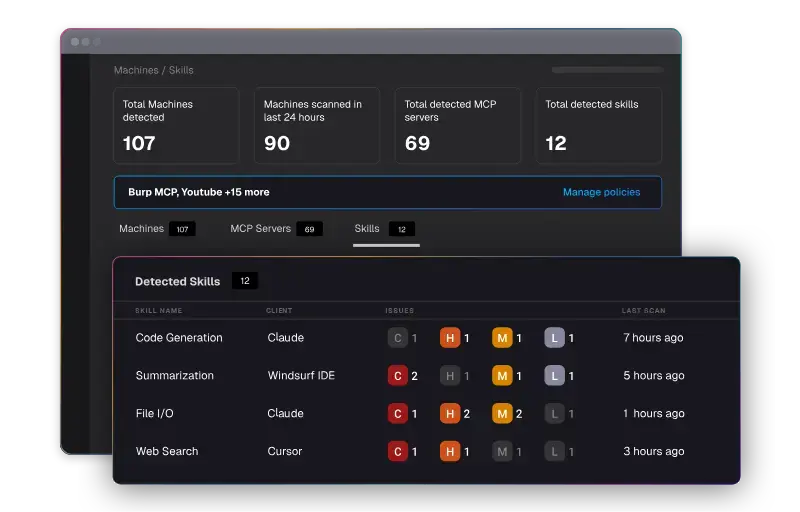
With its recent acquisition of Probely, Snyk DAST extends Snyk’s developer security platform, integrating dynamic testing into existing workflows alongside SAST and SCA capabilities.
It is designed for teams already using Snyk, providing a unified view of vulnerabilities across the SDLC. While not as deep as standalone DAST platforms, its ecosystem benefits are significant.
Key features:
Integrated SAST, SCA, and DAST in one suite
CI/CD pipeline integration
Developer-friendly vulnerability insights
Pricing:
Free Tier available
Team Plan: $25/month per contributing developer
Enterprise: Custom quote
Ratings and reviews:
Rated 4.5/5 on G2, users praise Snyk’s unified platform and ease of integration but note its DAST component is less mature than dedicated solutions.
8. Tenable WAS
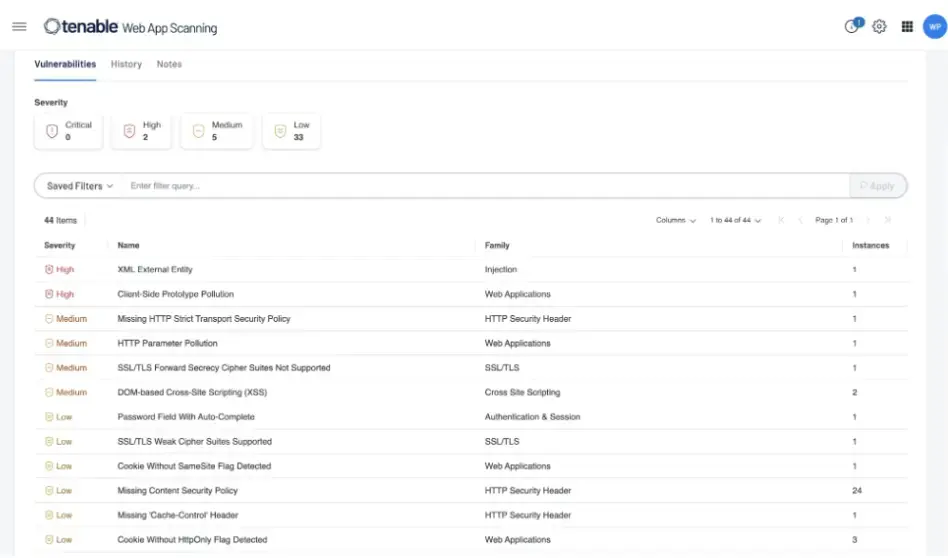
Tenable WAS brings Tenable’s vulnerability management expertise into web application testing. It focuses on risk-based prioritization and is ideal for organizations already invested in Tenable’s ecosystem.
Its key difference from Indusface lies in its automation and analytics, which eliminate the need for managed service coordination.
Key features:
Risk-based vulnerability prioritization
Integration with Tenable One
Automated scanning for compliance
Pricing:
- Custom quote
Ratings and reviews:
Tenable WAS holds a 4.5/5 rating, with users appreciating its enterprise reporting and integration. Some note that configuration and tuning can be complex.
9. Bright Security (formerly NeuraLegion)
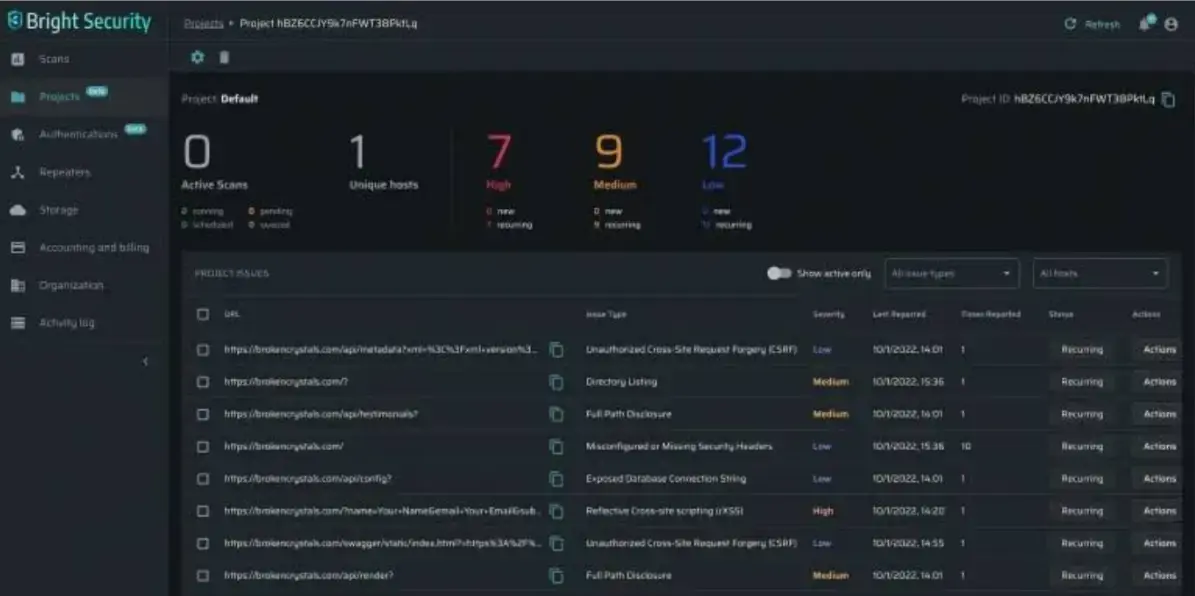
Bright Security combines developer-first automation with optional managed support, offering a hybrid model for teams that want flexibility. It allows organizations to switch between full automation and expert validation when needed.
This hybrid model positions Bright Security as a middle ground between Indusface’s managed service and modern self-service tools.
Key features:
API and web app testing
Optional expert-assisted validation
CI/CD pipeline integration
Developer-first dashboard
Pricing:
- Custom pricing based on testing volume
Ratings and reviews:
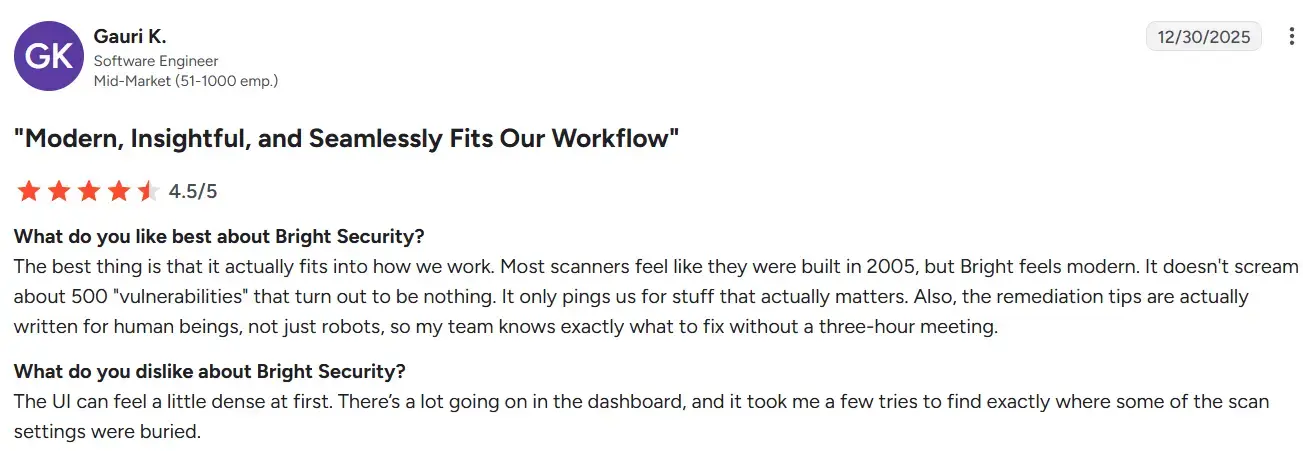
With a 4.7/5 rating, users appreciate its flexible hybrid approach and strong developer experience. Feedback highlights its versatility and rapid deployment.
10. Qualys WAS
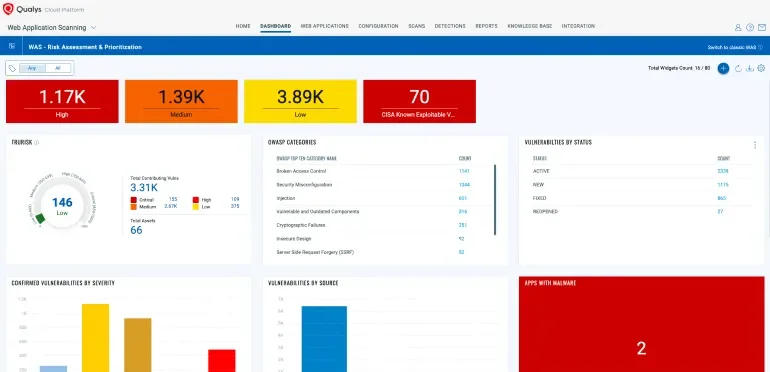
Qualys WAS provides enterprise-grade web app scanning as part of its larger VMDR (Vulnerability Management, Detection, and Response) suite. It is highly suitable for organizations already using the Qualys cloud platform.
While Indusface provides managed validation, Qualys offers scalable automation and unified risk visibility across assets.
Key features:
Automated web app discovery and scanning
Integration with Qualys VMDR
Detailed compliance reporting
Pricing:
- Custom enterprise pricing
Ratings and reviews:
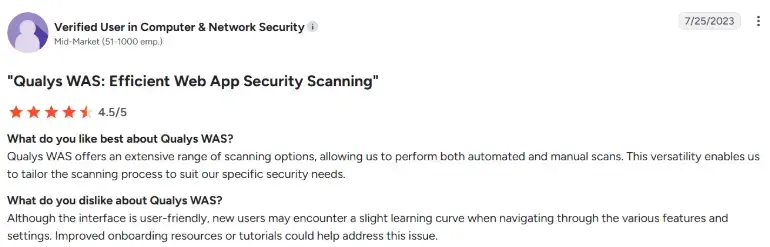
Qualys WAS maintains a 4.5/5 rating. Users praise its ecosystem and scalability but note that its UI can feel dated compared to modern tools.
Managed service vs self-service DAST: Which is right for you?
| Choose managed service (like Indusface) when | Choose self service DAST when |
|---|---|
| You have limited in house security expertise | You have DevSecOps maturity or plan to build it |
| You prefer expert validation and manual review | You need continuous, on demand testing |
| Continuous testing is not a priority | You want speed and developer autonomy |
| You want end to end service management | You prefer predictable, scalable pricing |
| You have the budget for managed services | You value fast remediation cycles |
Recommendations by organization type:
Startups/SMBs : Beagle Security (best value), Bright Security
Mid-Market : Beagle Security, StackHawk, Rapid7
Enterprise : Invicti, Acunetix, Qualys WAS, Tenable WAS
Security Professionals : Burp Suite
DevSecOps Teams : Beagle Security, StackHawk, Snyk DAST
Final thoughts
Indusface WAS continues to be a strong choice for organizations that value managed services with human validation. Its combination of AI and expert review provides reliable results, especially for teams that lack in house security skills.
The landscape in 2026 increasingly favors self service, automation driven security testing. AI advancements have significantly reduced false positive rates industry wide, and tools like Beagle Security now deliver highly accurate results without requiring manual validation for every finding.
Choosing the right alternative depends on your organization’s capability, speed, and scalability goals. For modern teams, Beagle Security combines agentic AI driven precision, easy integration, and a developer friendly experience at a self service price point.
FAQ
What makes Indusface WAS different from other DAST tools?
Indusface WAS is a managed service that pairs automated scans with human validation from certified experts. This approach ensures zero false positives but adds coordination overhead. Modern self-service tools like Beagle Security achieve similar accuracy through advanced AI validation without human intervention.
Is a managed DAST service better than self-service platforms?
It depends on your needs. Managed services like Indusface are ideal for teams without dedicated security staff. Self-service tools are faster, more scalable, and better suited for DevSecOps environments where autonomy and speed are priorities.
What is the best alternative to Indusface WAS?
It depends on what you need. Teams that want agentic AI driven pentest depth often look at Beagle Security, teams already in the Rapid7 or Qualys ecosystem tend to stay within that platform, and security professionals doing manual testing often reach for Burp Suite.
Do Indusface WAS alternatives support API and GraphQL testing?
Most modern alternatives do. Beagle Security, StackHawk, Snyk DAST, and Bright Security all include API testing, with Beagle Security and StackHawk specifically supporting GraphQL.