Top 10 Invicti Web + API (formerly Acunetix) alternatives in 2026: Comprehensive analysis
Invicti Web + API has long been one of the most recognized names in dynamic application security testing (DAST). The tool is valued for its ability to uncover thousands of vulnerabilities across web applications, APIs, and complex authentication flows. It provides wide coverage of the OWASP Top 10 and misconfiguration issues, alongside proof-of-concept exploits that help confirm whether vulnerabilities are real.
Despite these strengths, organizations in 2026 are increasingly considering alternatives to Invicti Web + API. Some find Invicti Web + API’s pricing restrictive as they scale, while others look for more modern, developer-friendly platforms that fit naturally into CI/CD pipelines. Many also seek stronger API security, advanced business logic testing, or simply better cost-to-value ratios. With the rapid evolution of DevSecOps, the landscape of Invicti Web + API alternatives has never been richer or more diverse.
Best Invicti Web + API (formerly Acunetix) alternatives TL;DR
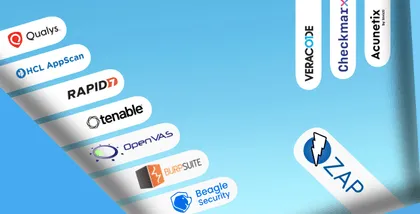
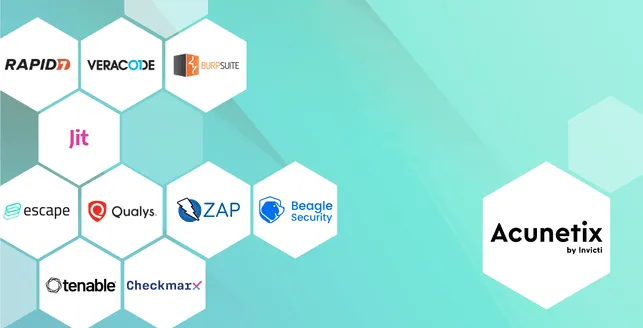
The table below provides a quick comparison of the top 10 Invicti Web + API alternatives in 2026, covering pricing, strengths, and best use cases.
| Software | Starting price | Strengths | Best for |
|---|---|---|---|
| Beagle Security | $119/month | Agentic AI powered, developer-friendly | Modern web app testing |
| ZAP | Free | Open-source, extensible | Budget-conscious teams and automation |
| Burp Suite | $499/user/year | Comprehensive, industry-standard | Professional penetration testing |
| Checkmarx | Custom quote | Enterprise-grade, customizable | Large-scale secure SDLC |
| Veracode | Custom quote | Cloud-native, compliance-focused | Enterprise compliance needs |
| Jit | $50/dev/month | AI agents, automation | Developer-first security orchestration |
| Qualys WAS | Custom quote | Integrated with VMDR | Enterprises already using Qualys |
| Tenable WAS | $7,434/year | Unified with Tenable.io | Organizations on Tenable platform |
| Rapid7 InsightAppSec | $175/app/month | Part of InsightPlatform | Rapid7 users with app portfolios |
| Escape DAST | Custom quote | API-first, BLST engine | API-centric organizations |
Beagle Security
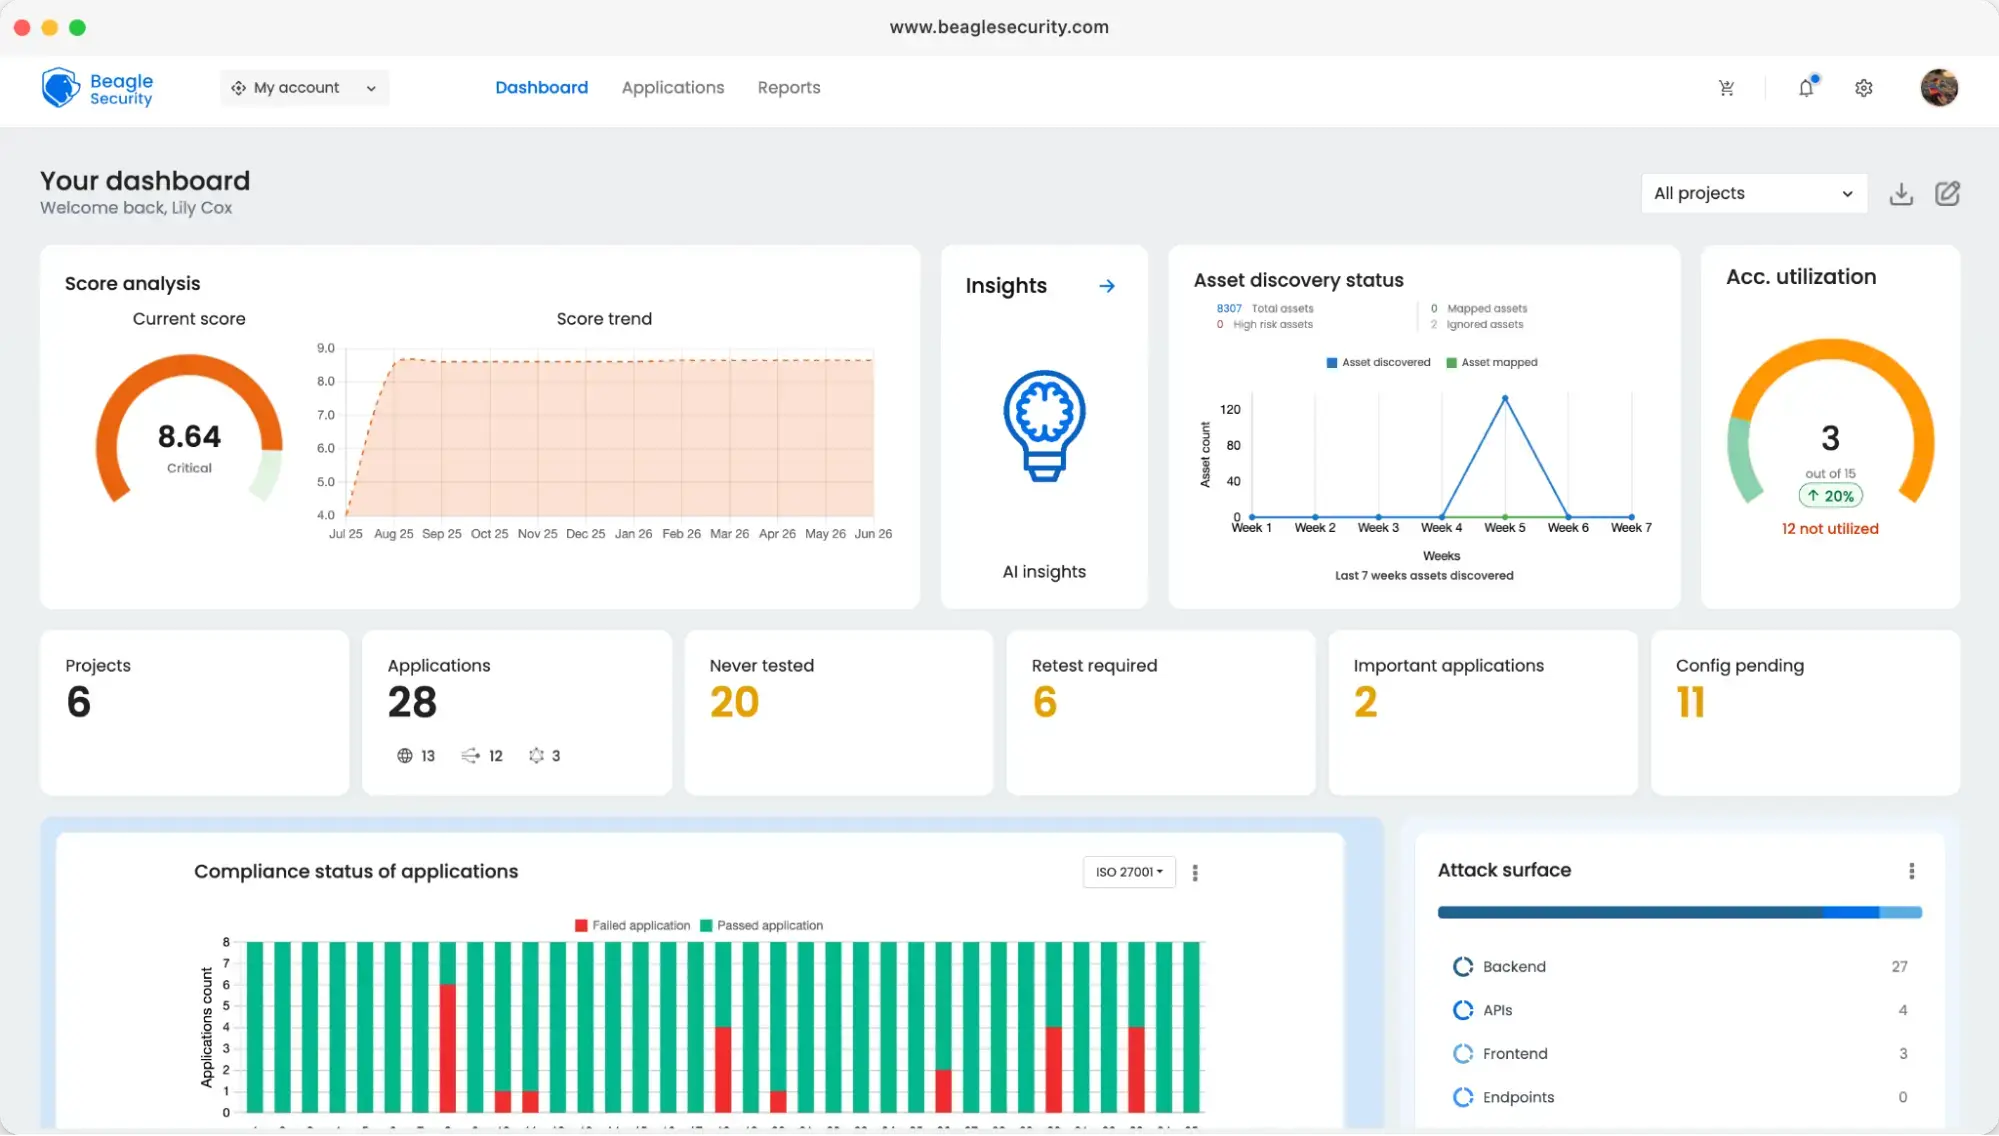
Beagle Security has quickly become a strong alternative to Invicti Web + API by focusing on agentic AI powered attack simulations and business logic testing. The platform is designed to be developer-friendly, with clear remediation guidance and seamless CI/CD integration, making it a popular choice for modern DevSecOps teams.
Unlike traditional DAST tools that primarily rely on signature-based detection, Beagle Security uses AI-driven methodologies to adapt tests to application behavior. This approach reduces false positives while improving accuracy, giving teams more reliable insights with less manual tuning.
Key features
Agentic AI penetration testing simulates real-world attacks, giving more accurate results than signature-based scans.
Detects business logic flaws that traditional scanners often miss.
Advanced crawling supports single-page applications (SPAs) and GraphQL APIs.
Handles 2FA and dynamic authentication without requiring heavy manual setup.
Integrates smoothly with CI/CD tools to embed testing in development workflows.
Provides developer-friendly remediation guidance with actionable code snippets.
Pricing
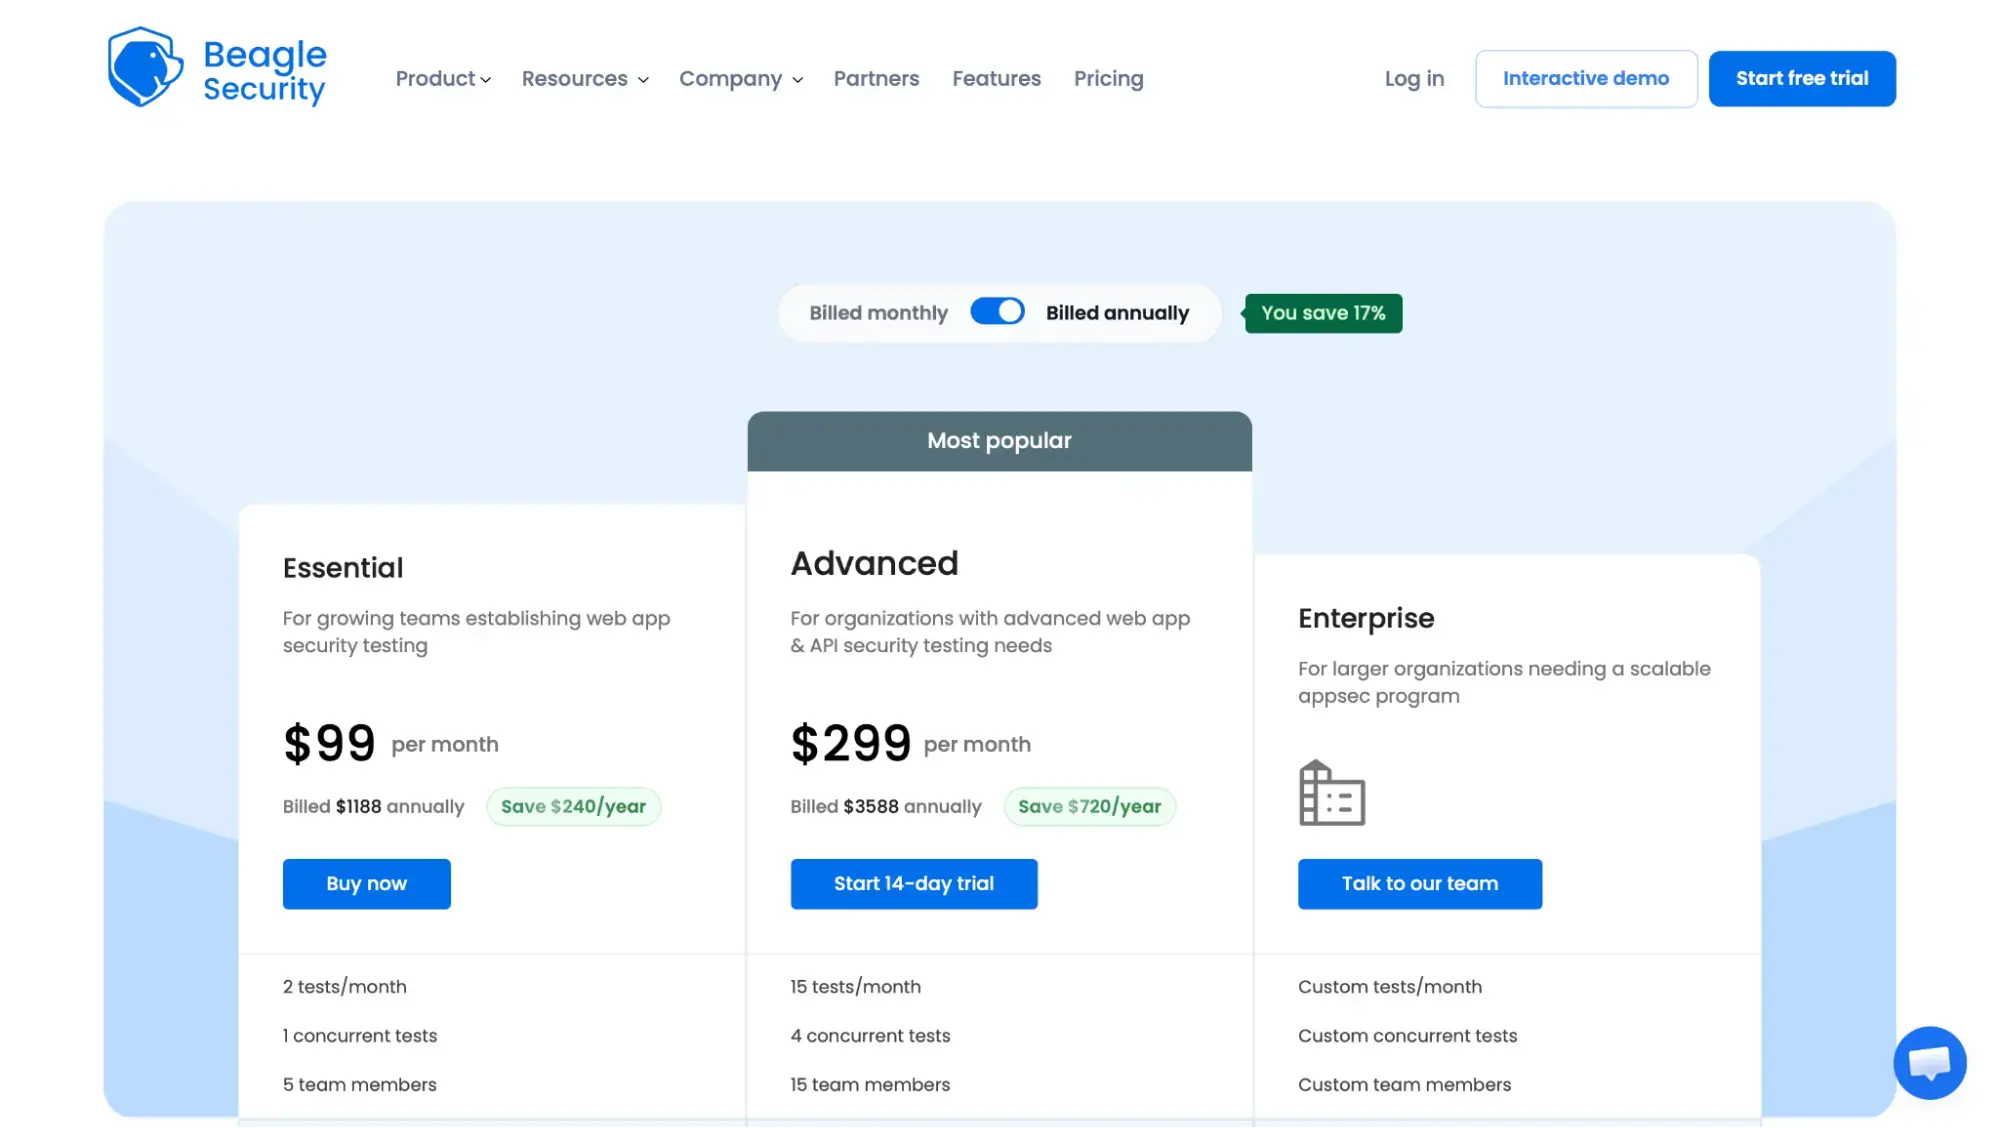
Beagle Security follows a usage-based pricing model with custom quotes. Self-serve annual plans typically start at around $1,188, with enterprise pricing scaling according to testing volume. It avoids the per-domain restrictions common in legacy tools.
Ratings & reviews
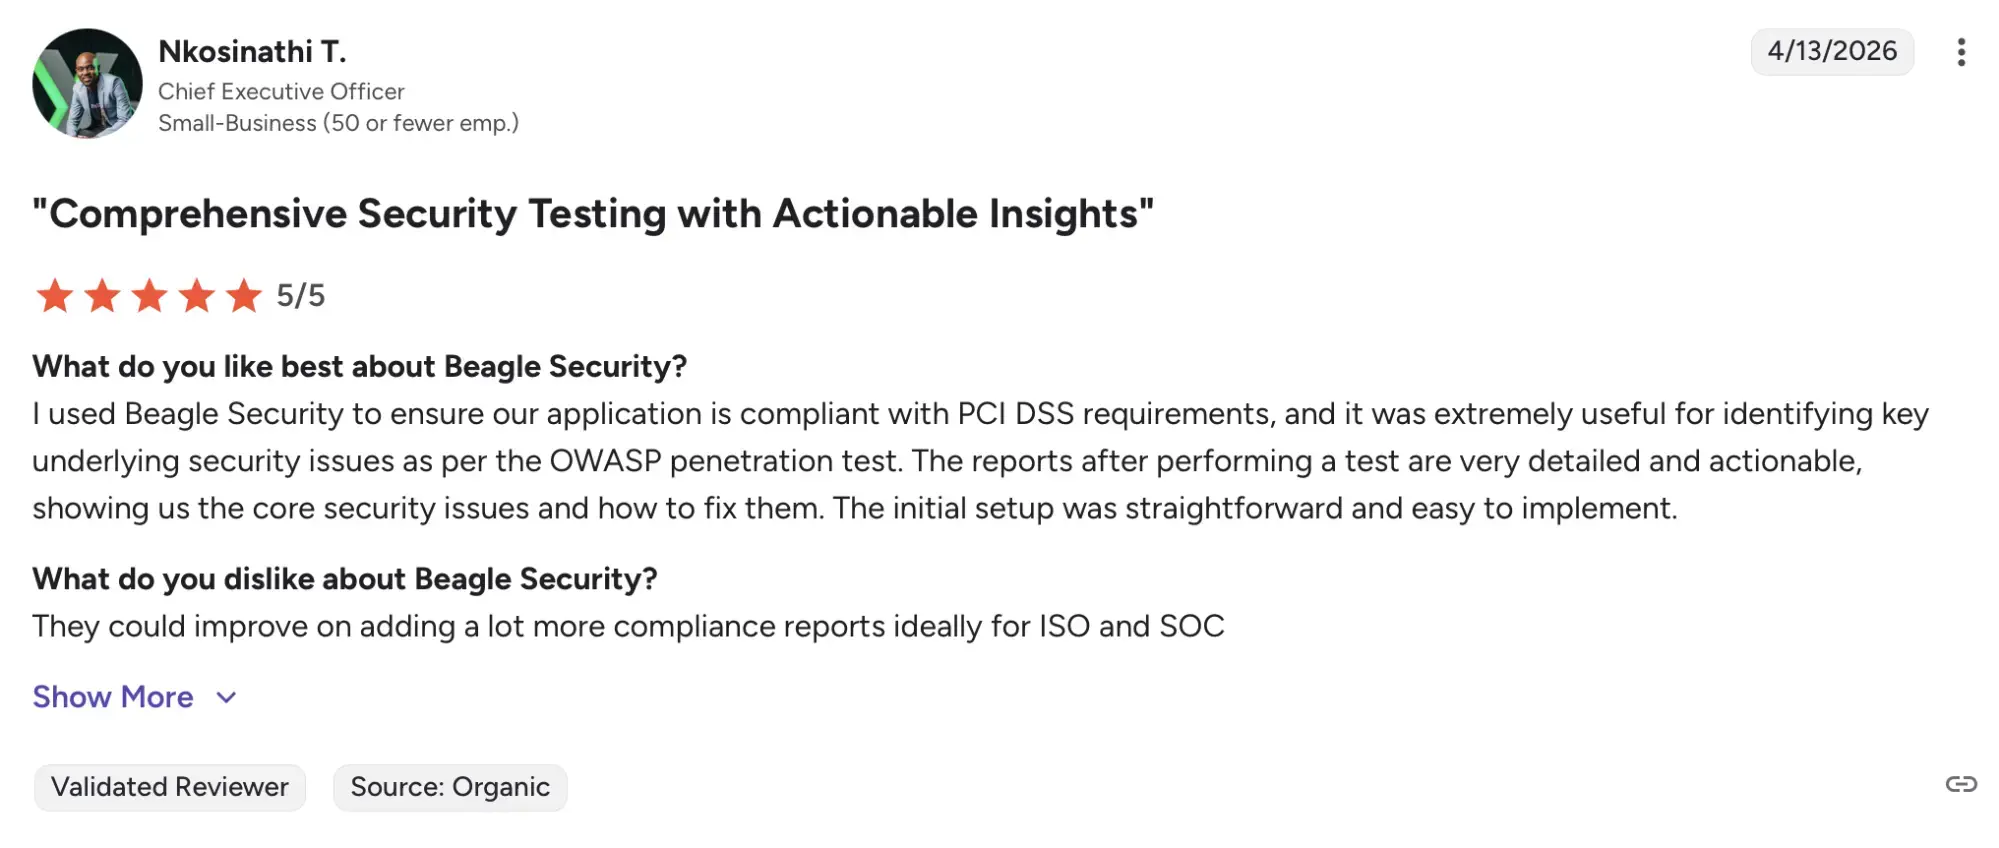
On G2, Beagle Security is rated 4.7/5 from 88 reviews. Users highlight its ease of setup and intuitive UI, noting a smooth onboarding experience compared to older scanners. The AI-driven testing earns praise for producing accurate results with almost no false positives. Developers particularly appreciate the clear, code-level remediation guidance.
ZAP (Zed Attack Proxy by Checkmarx)
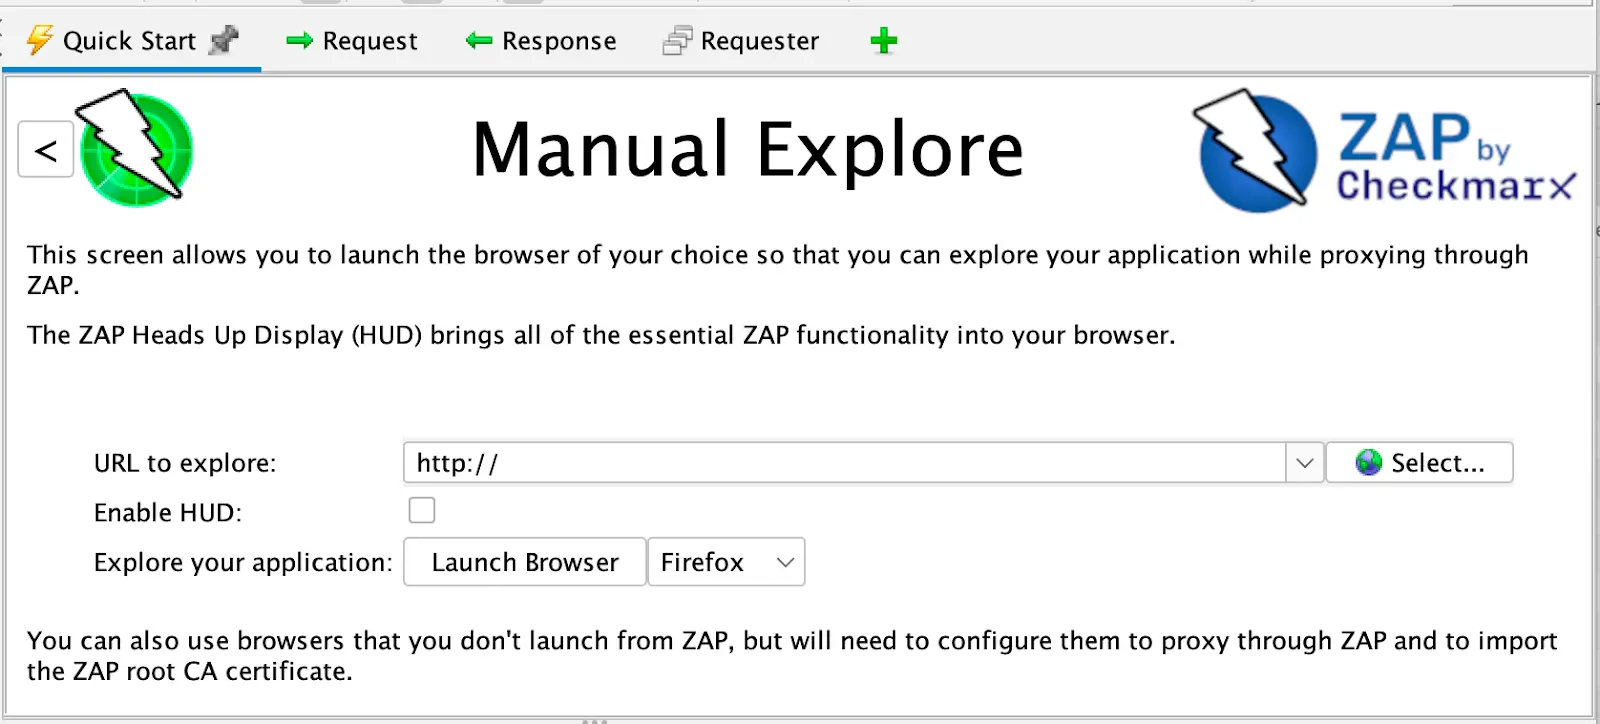
ZAP is one of the most popular open-source dynamic application security testing (DAST) tools and is now maintained under Checkmarx. It has grown from a community-driven OWASP project into a globally recognized security scanner, widely used by developers, QA teams, and security professionals. The tool provides strong automation capabilities and flexibility, making it a go-to option for teams looking for cost-effective and customizable security testing.
Key features
Automated scanner and spider crawl applications to detect vulnerabilities quickly.
Passive scanning monitors traffic in real time without affecting performance.
Extensible through plugins, add-ons, and scripting for tailored use cases.
AJAX spider and JavaScript execution help test modern web applications.
Supports API testing with OpenAPI and Swagger definitions.
Built-in proxy allows manual interception and modification of requests.
Pricing
ZAP is completely free under the Apache 2 license. Organizations can run unlimited scans and deploy multiple instances at no cost, making it an attractive choice for budget-conscious teams.
Ratings & reviews
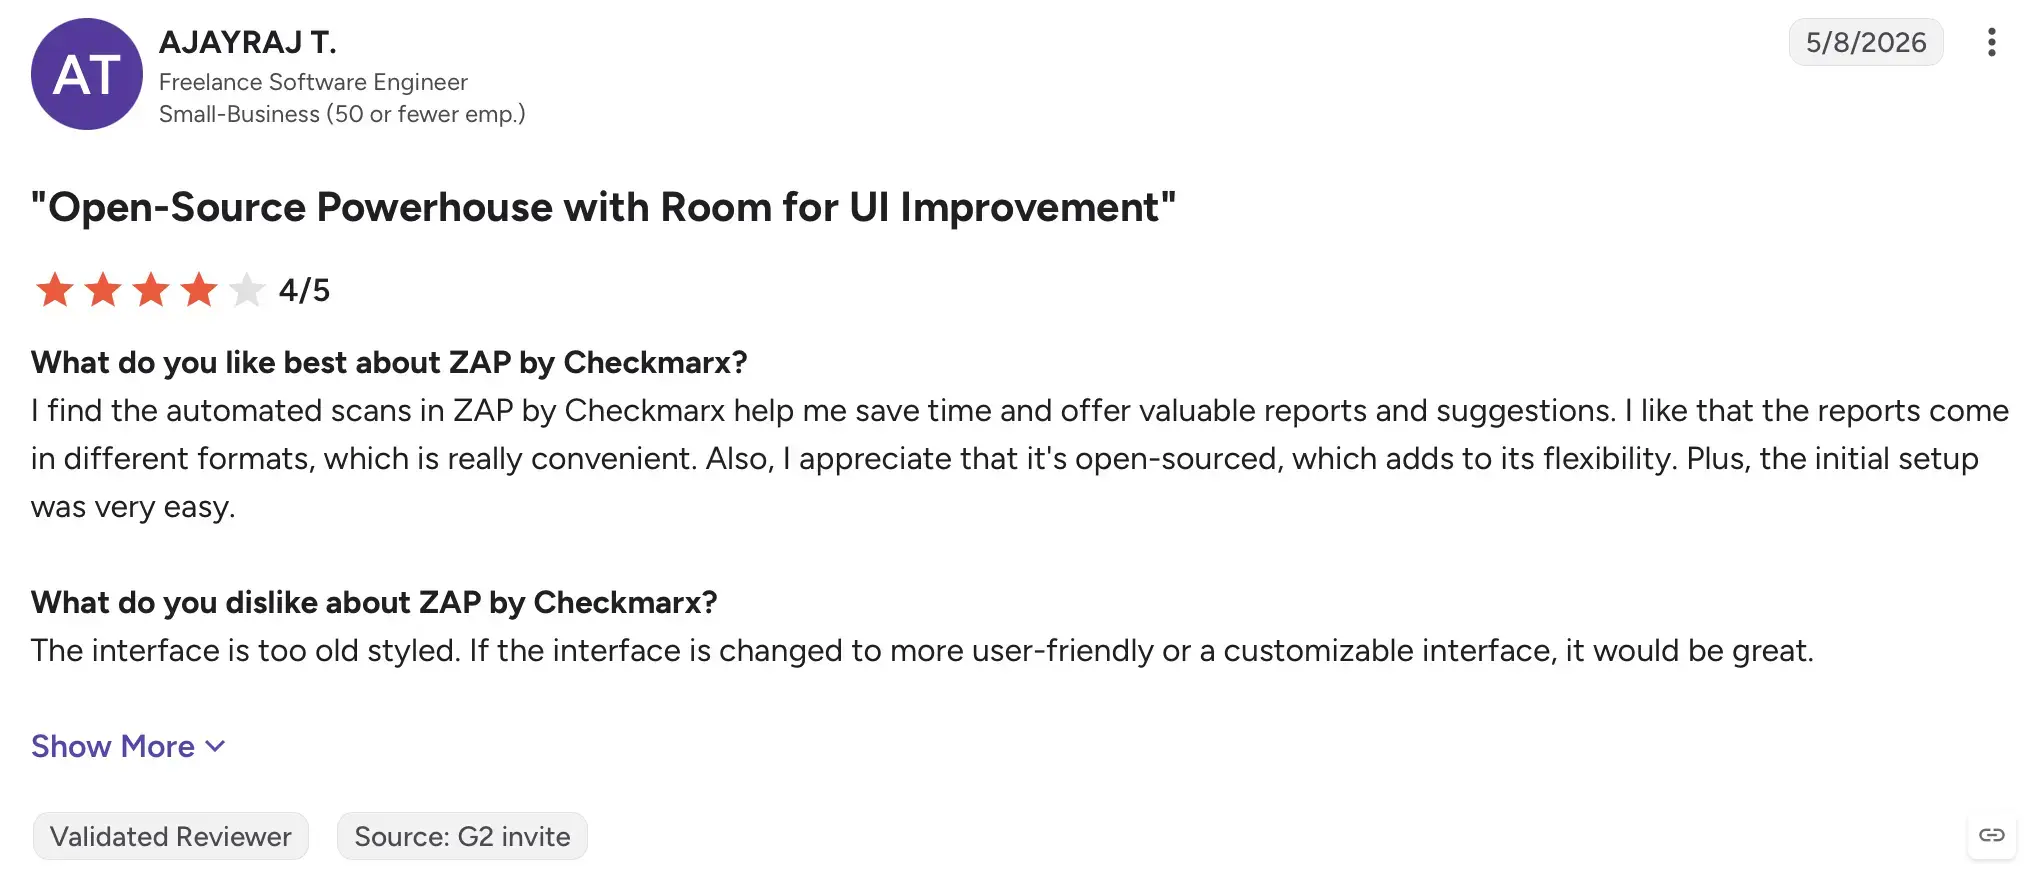
ZAP is rated 4.7/5 on G2 from 14 reviews. Users often describe it as “feature-rich for a free tool” and praise its flexibility. While some note that it requires technical expertise for optimal tuning, others highlight its value as both a learning tool and a professional-grade DAST platform. Community support is considered one of its strongest assets.
Burp Suite
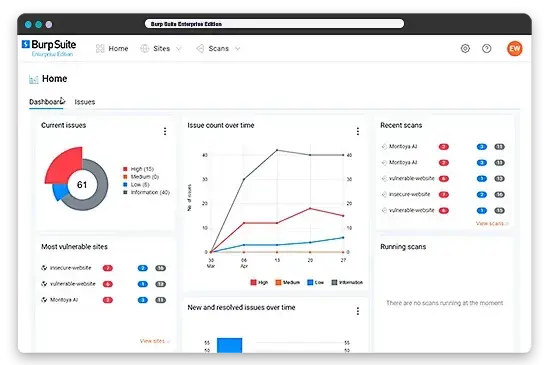
Burp Suite is considered the industry-standard toolkit for application security testing, relied on by penetration testers worldwide. It combines powerful automated scanning with advanced manual testing modules, giving professionals deep control over their assessments.
Key features
Offers a complete toolkit for both automated scanning and manual testing.
Built-in proxy enables request interception and modification in real time.
Manual testing tools like Intruder and Repeater provide granular control.
The automated scanner is known for high accuracy and low false positives.
Supports session handling and authentication for complex apps.
Extensible with BApp Store plugins to add specialized features.
Pricing
Burp Suite offers several tiers: The Community Edition (free), Professional Edition at $499 per user annually, and Enterprise Edition with custom pricing. The Professional Edition is the most widely used for penetration testing.
Ratings & reviews
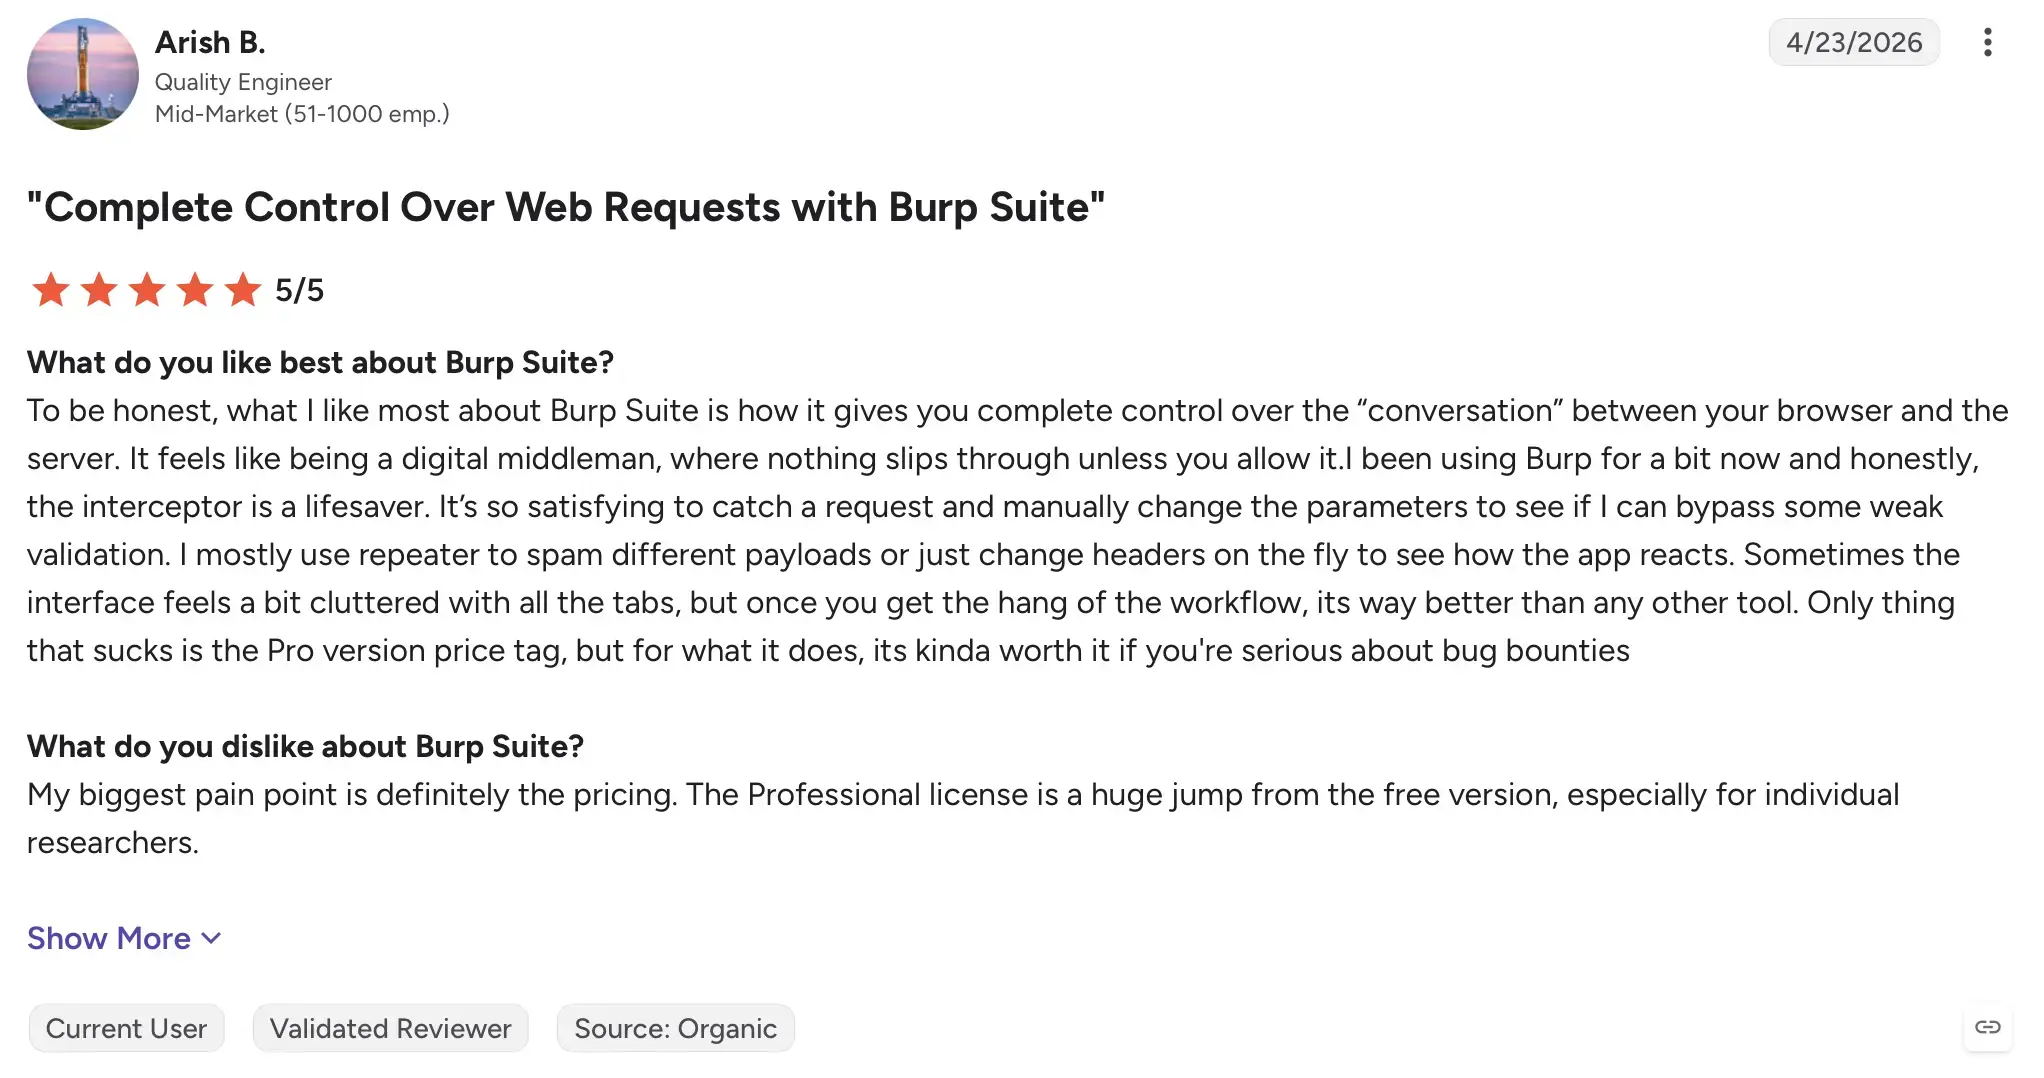
Burp Suite holds a 4.8/5 rating on G2 from 129 reviews. Users praise its accuracy, especially when testing complex authentication and session handling. Security professionals highlight the tool’s reliability in detecting critical vulnerabilities while keeping false positives low. However, some mention that the learning curve can be steep for beginners.
Checkmarx
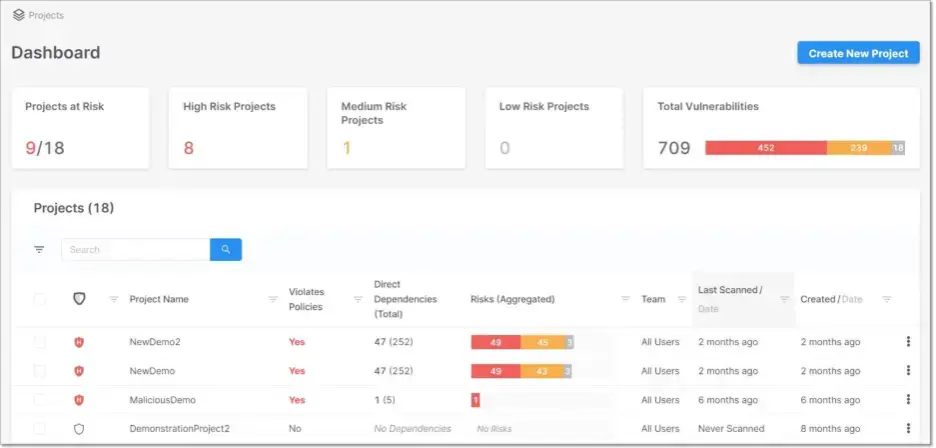
Checkmarx positions itself as an enterprise-grade platform that extends far beyond basic DAST. Its strength lies in unifying SAST, DAST, SCA, and application security posture management (ASPM), giving organizations end-to-end coverage across the software development lifecycle.
For enterprises with complex environments, Checkmarx provides a high degree of customization and policy control. It is especially suited for organizations that require centralized dashboards, deep integrations, and governance features to meet compliance needs.
Key features
Unified application security platform combining SAST, DAST, SCA, and ASPM.
Customizable query sets allow teams to tailor static code analysis.
The DAST engine supports authentication and testing of modern applications.
Software composition analysis manages risks in open-source dependencies.
Infrastructure-as-Code scanning improves cloud-native security.
Provides risk-based prioritization through ASPM integration.
Pricing
Checkmarx uses enterprise custom pricing. Costs depend on the number of applications, modules, and enterprise support needs. Organizations typically receive tailored quotes.
Ratings & reviews
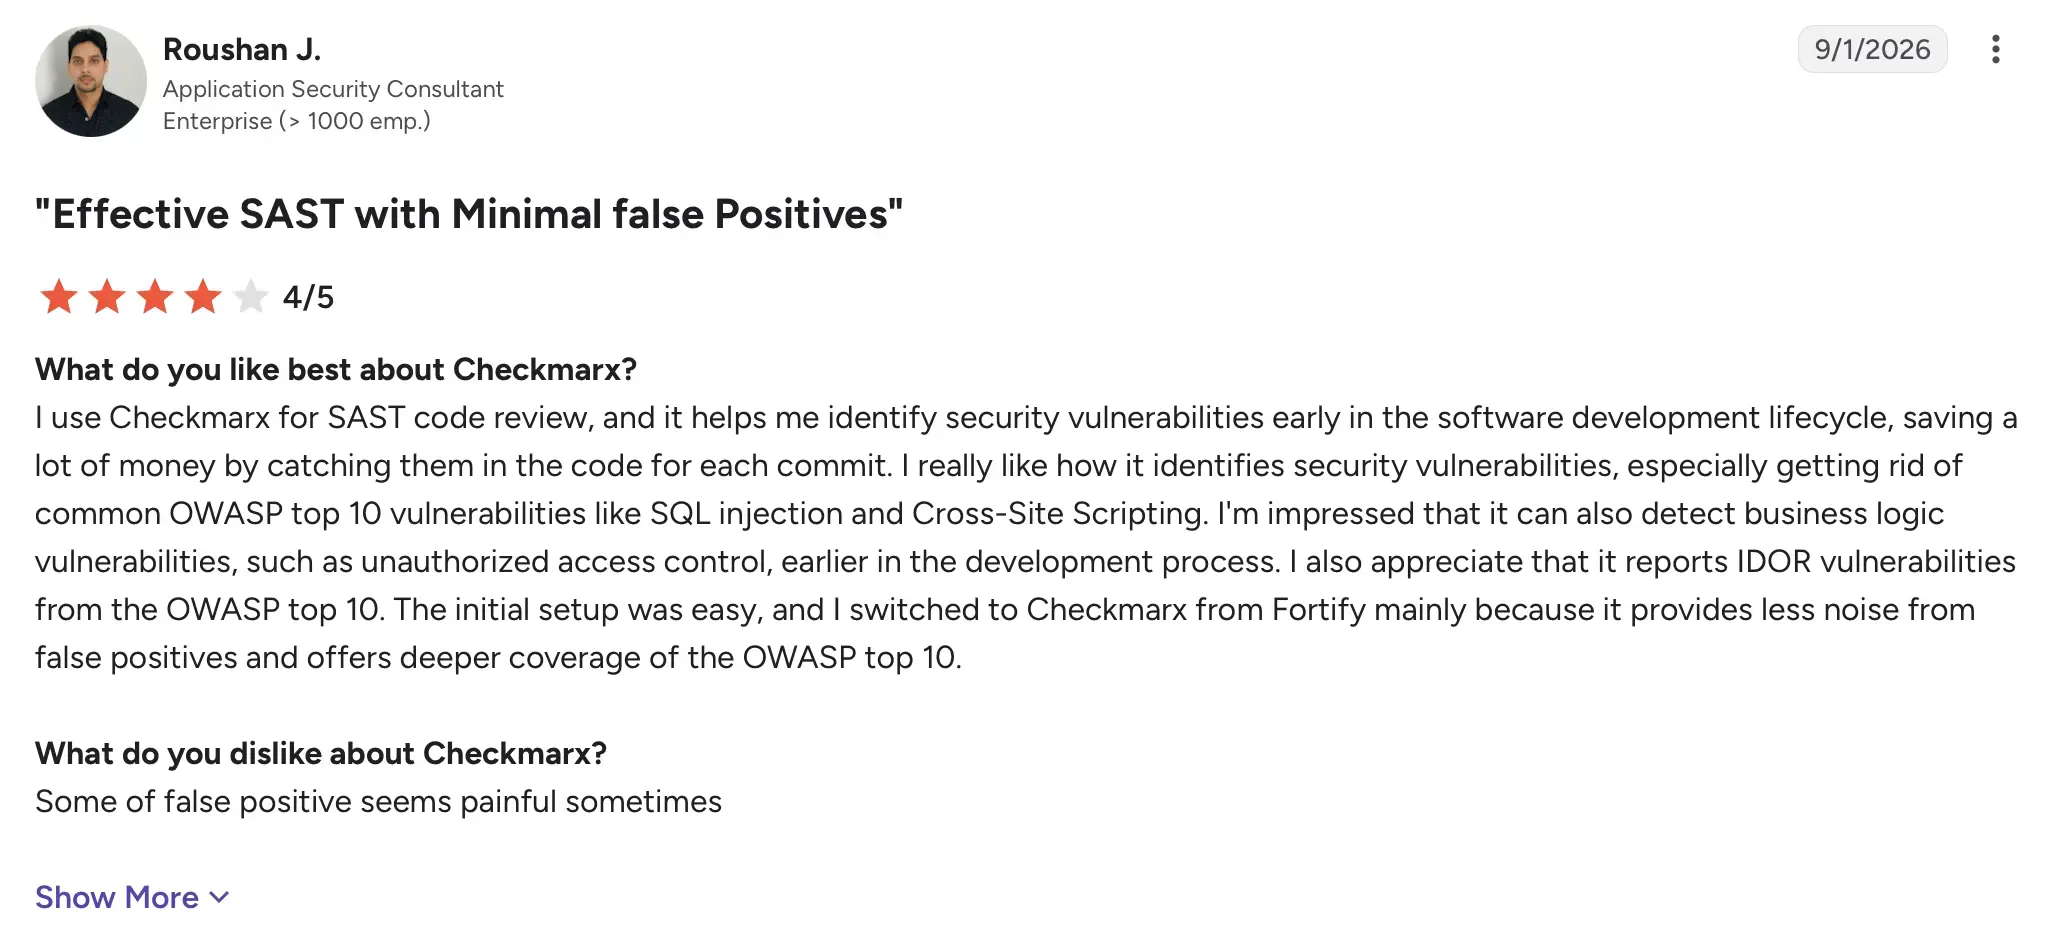
On G2, Checkmarx is rated ** 4.2/5 from 49 reviews.** Users praise its customization flexibility and ability to integrate into large DevSecOps pipelines. Some note that dashboards could be more intuitive and that triaging false positives can take time. Support is consistently rated as strong.
Veracode
Veracode is another enterprise-focused platform that offers a cloud-native approach to application security. It provides coverage across SAST, DAST, SCA, and manual penetration testing, with strong compliance features that make it a trusted choice for large organizations.
The platform emphasizes automation and scalability, allowing enterprises to embed security testing directly into development workflows. Its reputation for compliance support and global reach makes it especially valuable to organizations working in regulated industries.
Key features
Cloud-native security platform that scales with enterprise needs.
Performs static analysis including advanced binary code scanning.
Dynamic analysis covers runtime vulnerabilities across applications.
Software composition analysis secures open-source and third-party components.
Offers interactive application security testing (IAST) for runtime insights.
Provides manual penetration testing services for high-risk applications.
Pricing
Custom quote
Ratings & reviews
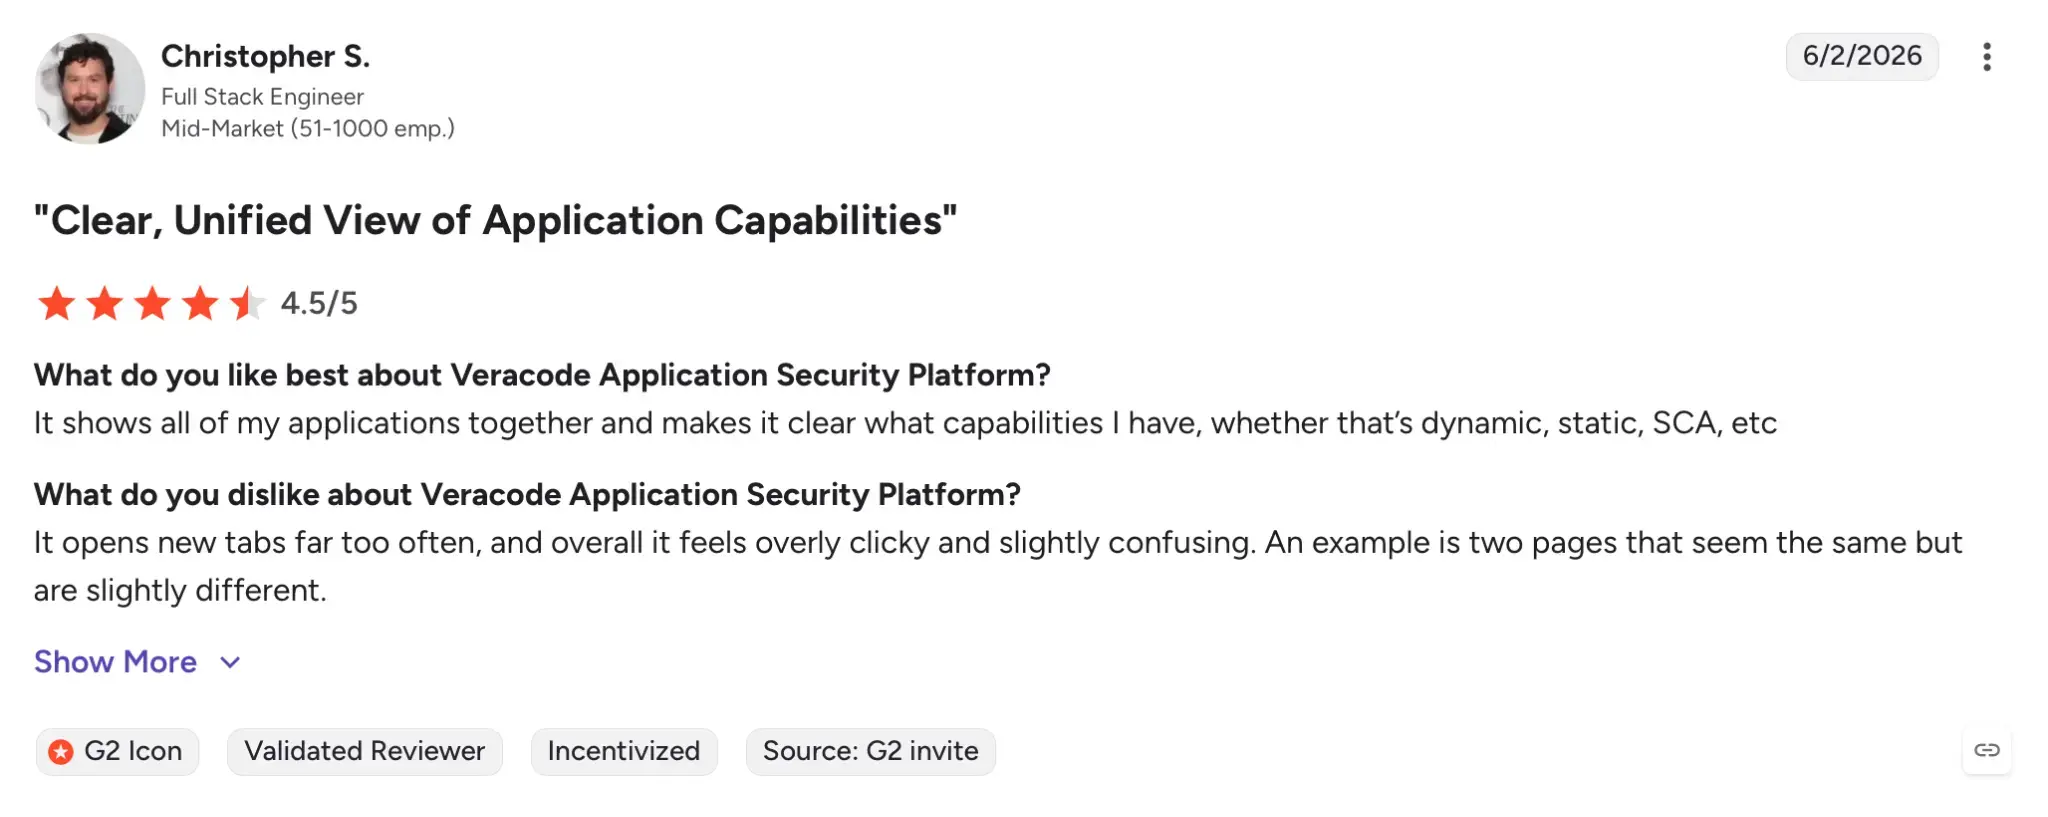
Veracode is rated 4.0/5 on G2 from 44 reviews. Users appreciate its breadth of coverage and strong compliance capabilities, especially for regulated industries. However, many point out that the interface can be challenging to use and the learning curve steep. Still, its scalability and global infrastructure are seen as major advantages.
Jit
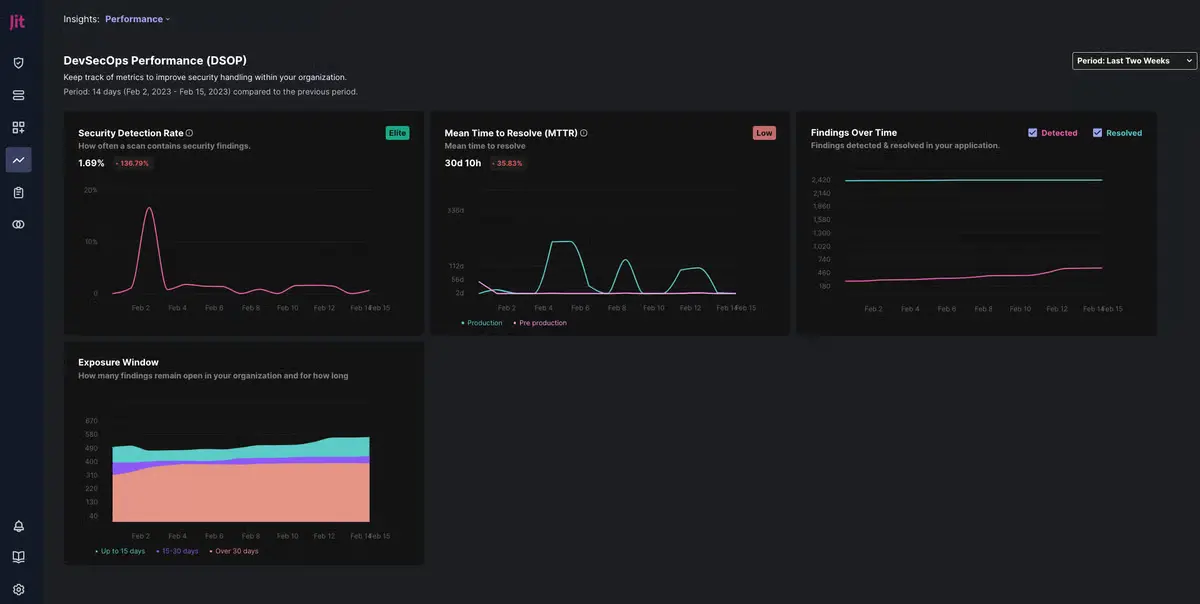
Jit represents a new generation of application security tools built around AI-powered automation. Instead of requiring manual triage and prioritization, Jit uses intelligent agents to reduce alert fatigue and streamline remediation.
Its per-developer pricing model makes it accessible to teams of all sizes, while still providing advanced scanning capabilities. By focusing on simplicity and automation, Jit appeals to teams looking to embed security without adding unnecessary complexity.
Key features
AI-powered agents automate vulnerability scanning, triage, and remediation.
Provides full-stack scanning across SAST, SCA, DAST, and IaC security.
Automates prioritization of issues based on business impact.
Delivers developer-focused remediation with code examples and fixes.
Includes preconfigured “security plans” to speed up DevSecOps adoption.
Offers organization-wide visibility with dashboards and leaderboards.
Pricing
Jit offers a Growth plan at $50 per developer per month, billed annually, with a minimum of 4 developers. Enterprise plans are available with custom pricing.
Ratings & reviews
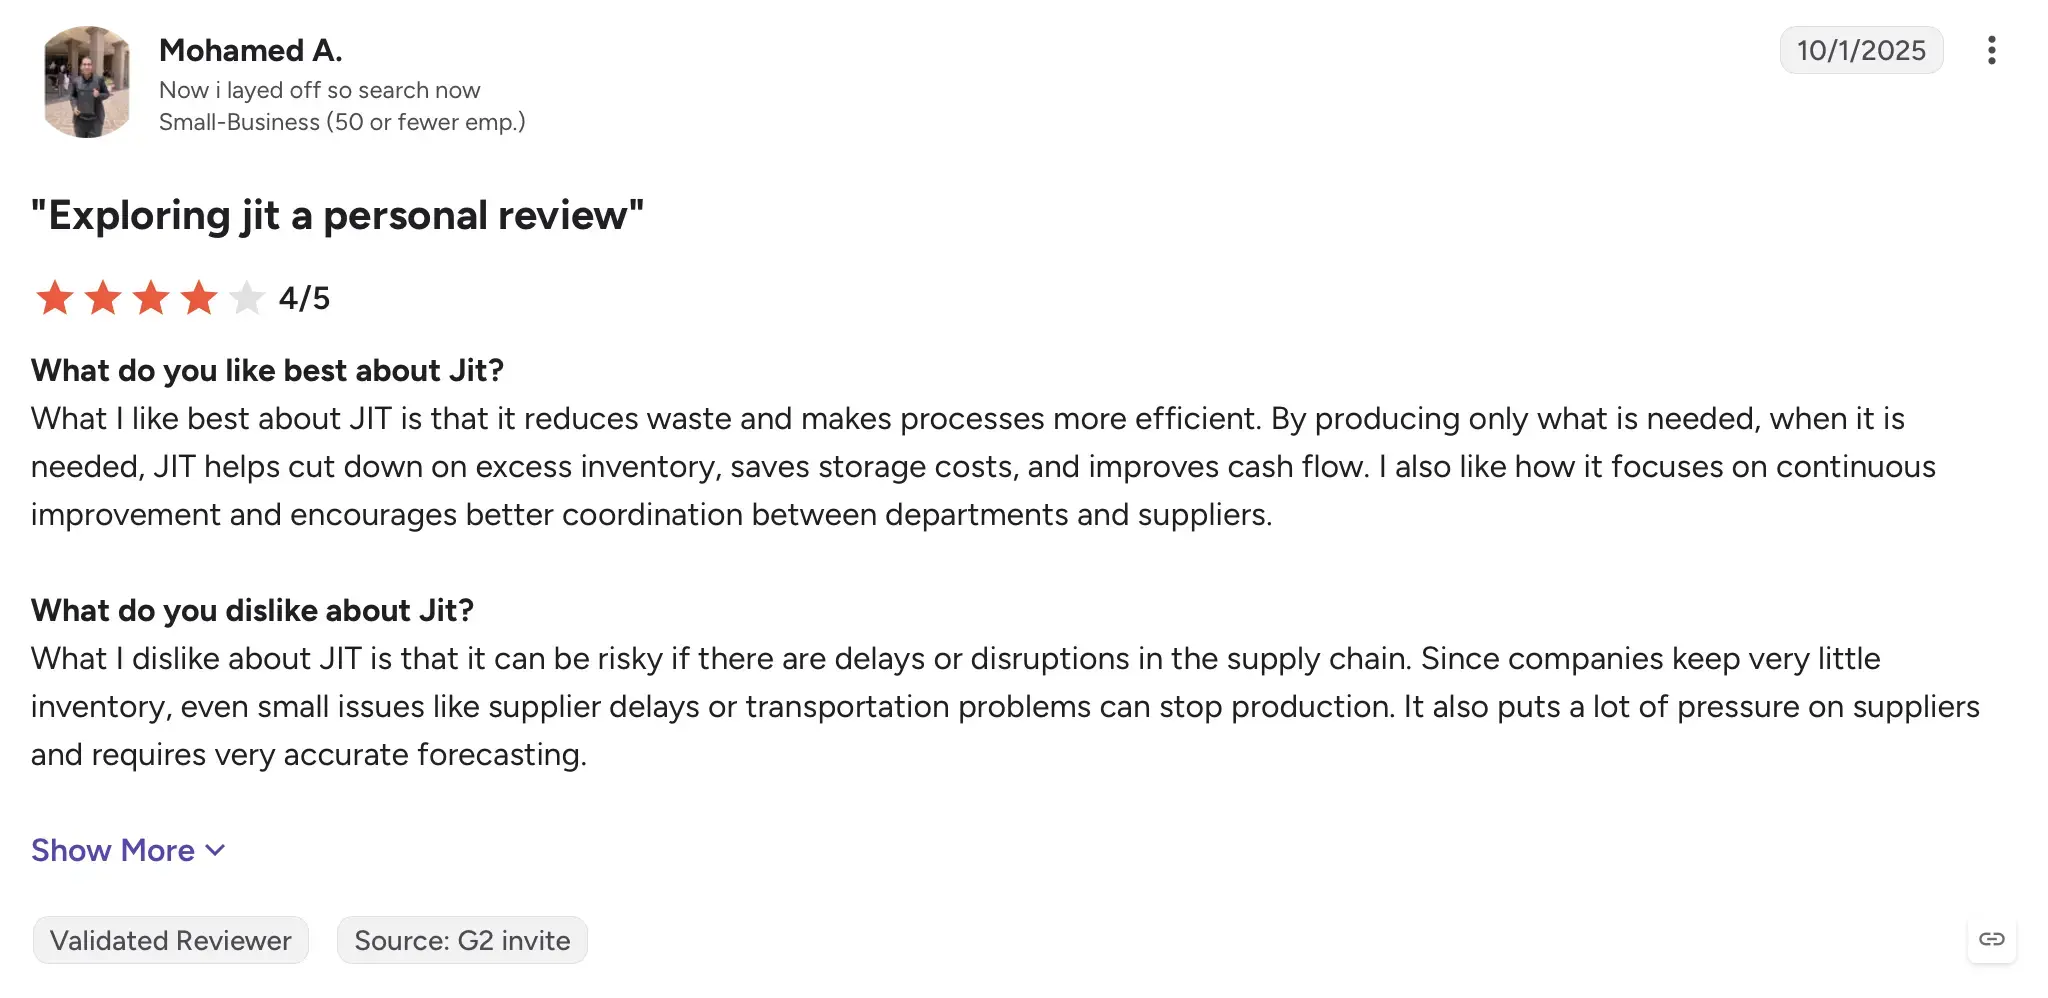
Jit has a 4.5/5 rating on G2 from about 43 reviews. Users highlight its seamless onboarding and simple pricing model. Teams report that the automation significantly reduces time spent on manual triage. Some note that its feature set is still growing compared to older platforms, but its developer-first focus is highly praised.
Qualys WAS
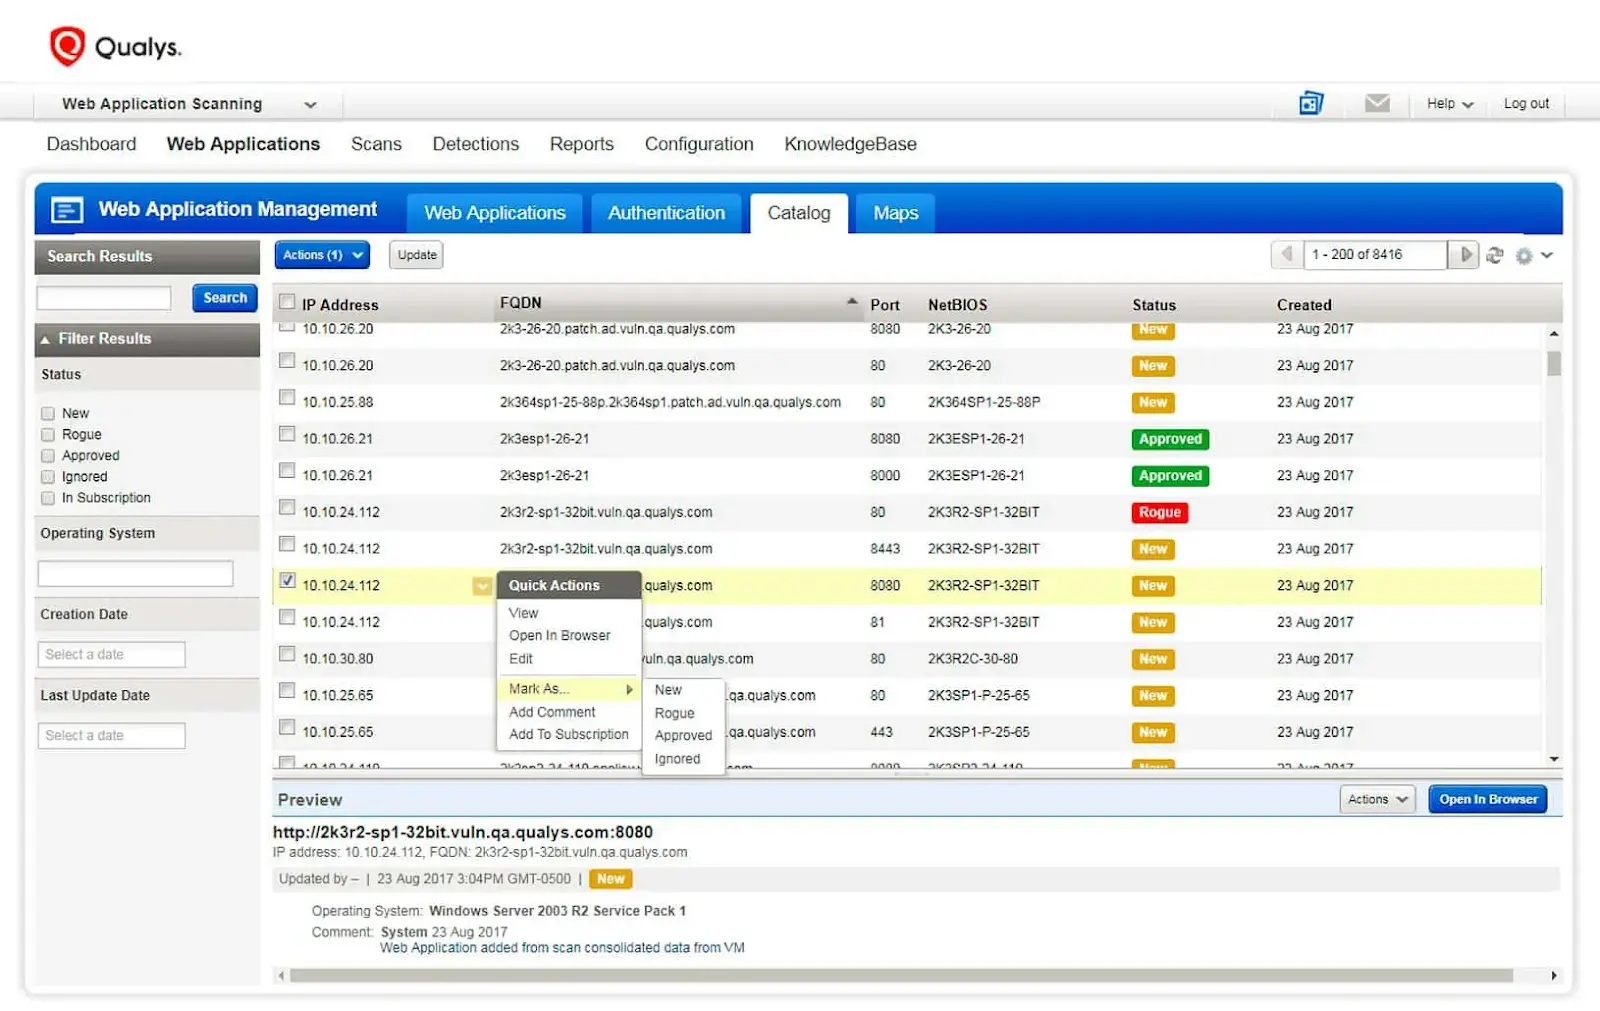
Qualys WAS is an enterprise-grade solution that benefits from integration with the broader Qualys ecosystem. It is designed for organizations that already rely on Qualys VMDR or other modules, providing a seamless way to extend coverage to web applications.
The platform emphasizes compliance and audit-ready reporting, which makes it particularly valuable for regulated industries. Although its interface feels dated compared to newer competitors, its reliability and integration capabilities remain strong selling points.
Key features
Scans web apps for vulnerabilities with a reliable enterprise-grade engine.
Provides dedicated API security testing for REST and SOAP services.
Tests authentication flows and session handling in complex apps.
Generates audit-ready reports aligned with compliance standards.
Integrates with Qualys VMDR for centralized vulnerability management.
Supports scheduled scans and automated alerts for continuous monitoring.
Pricing
Qualys WAS pricing scales with the number of applications tested, and volume discounts are available. It is available upon request for a custom quote.
Ratings & reviews
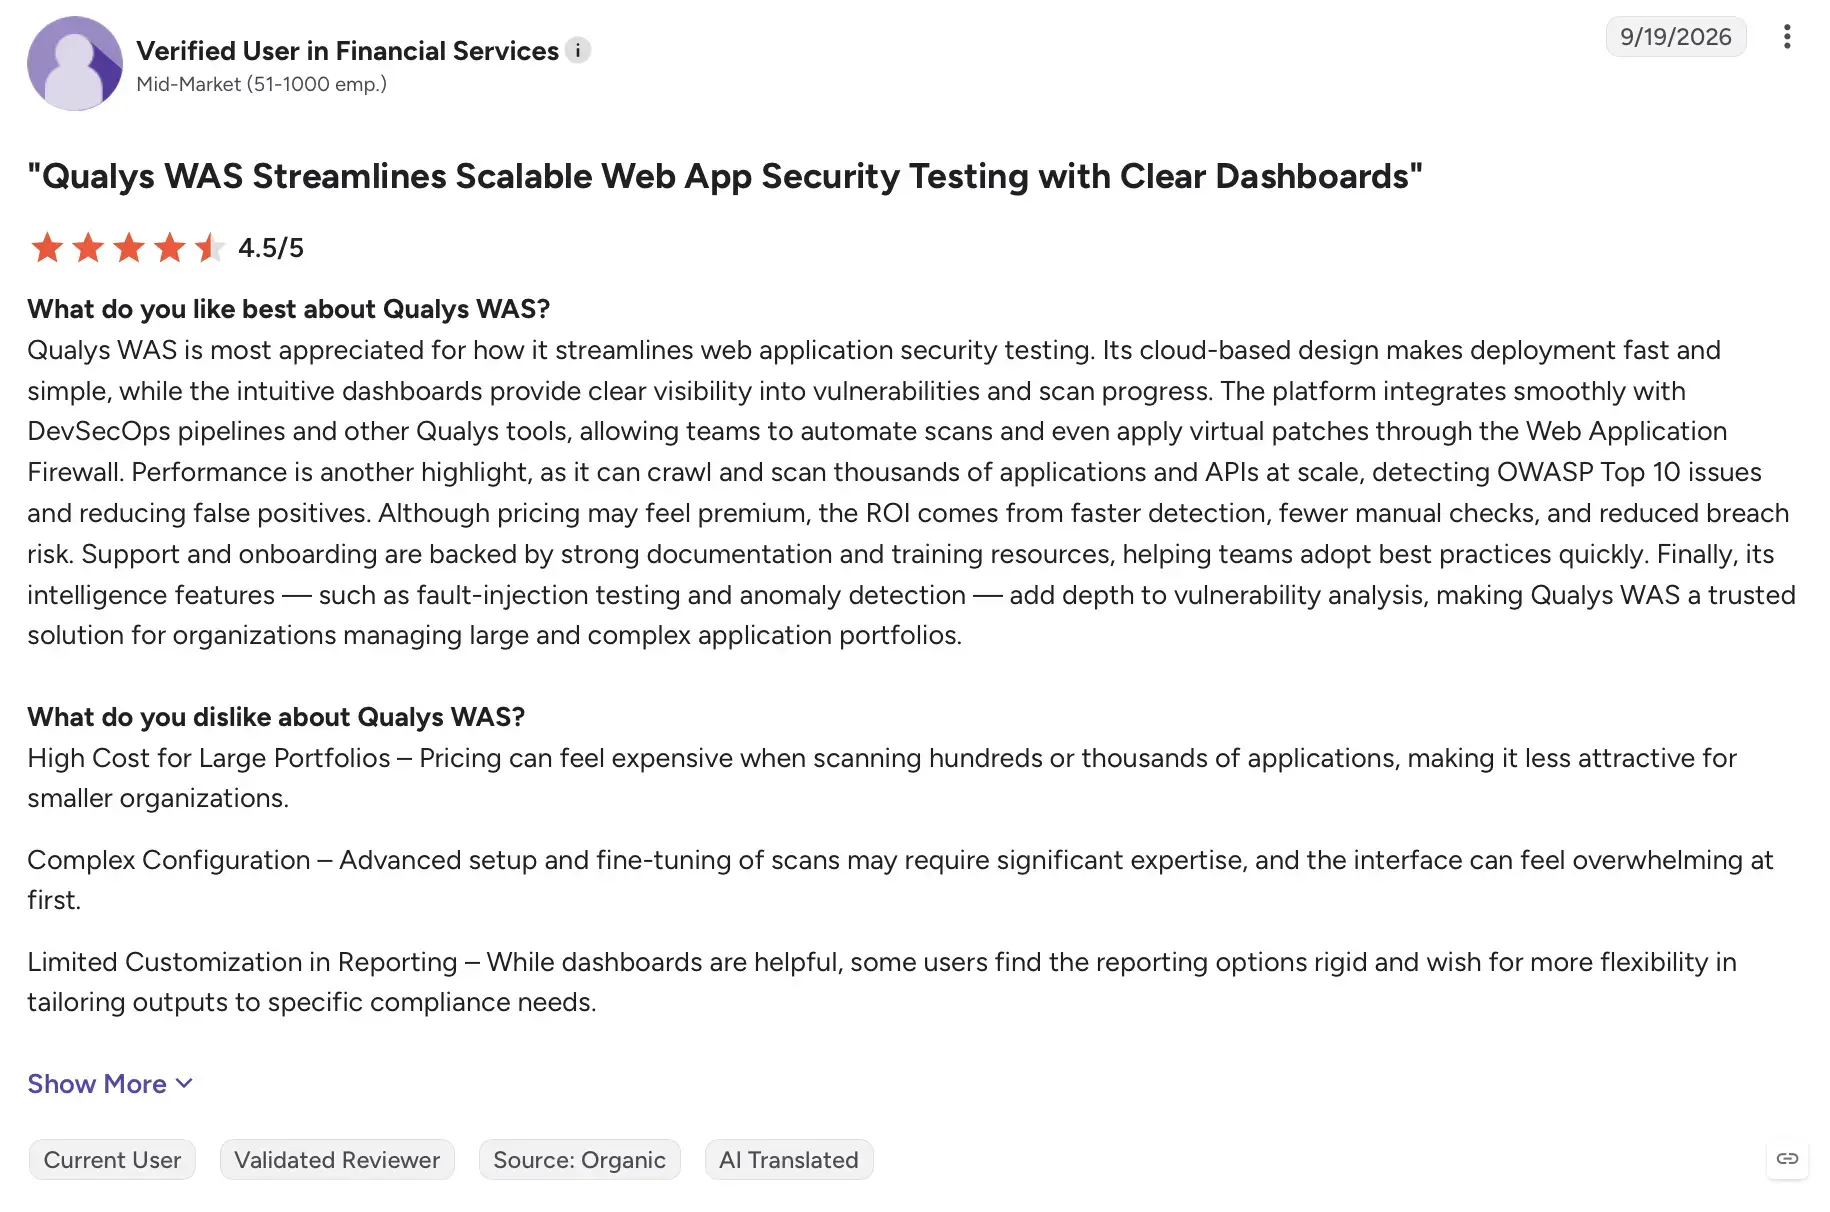
Qualys WAS scores 4.5/5 on G2 from 21 reviews. Users appreciate its reliability and compliance reporting but mention the user interface feels dated. Its greatest strength is integration with the larger Qualys platform, though standalone users may find it less appealing.
Tenable WAS
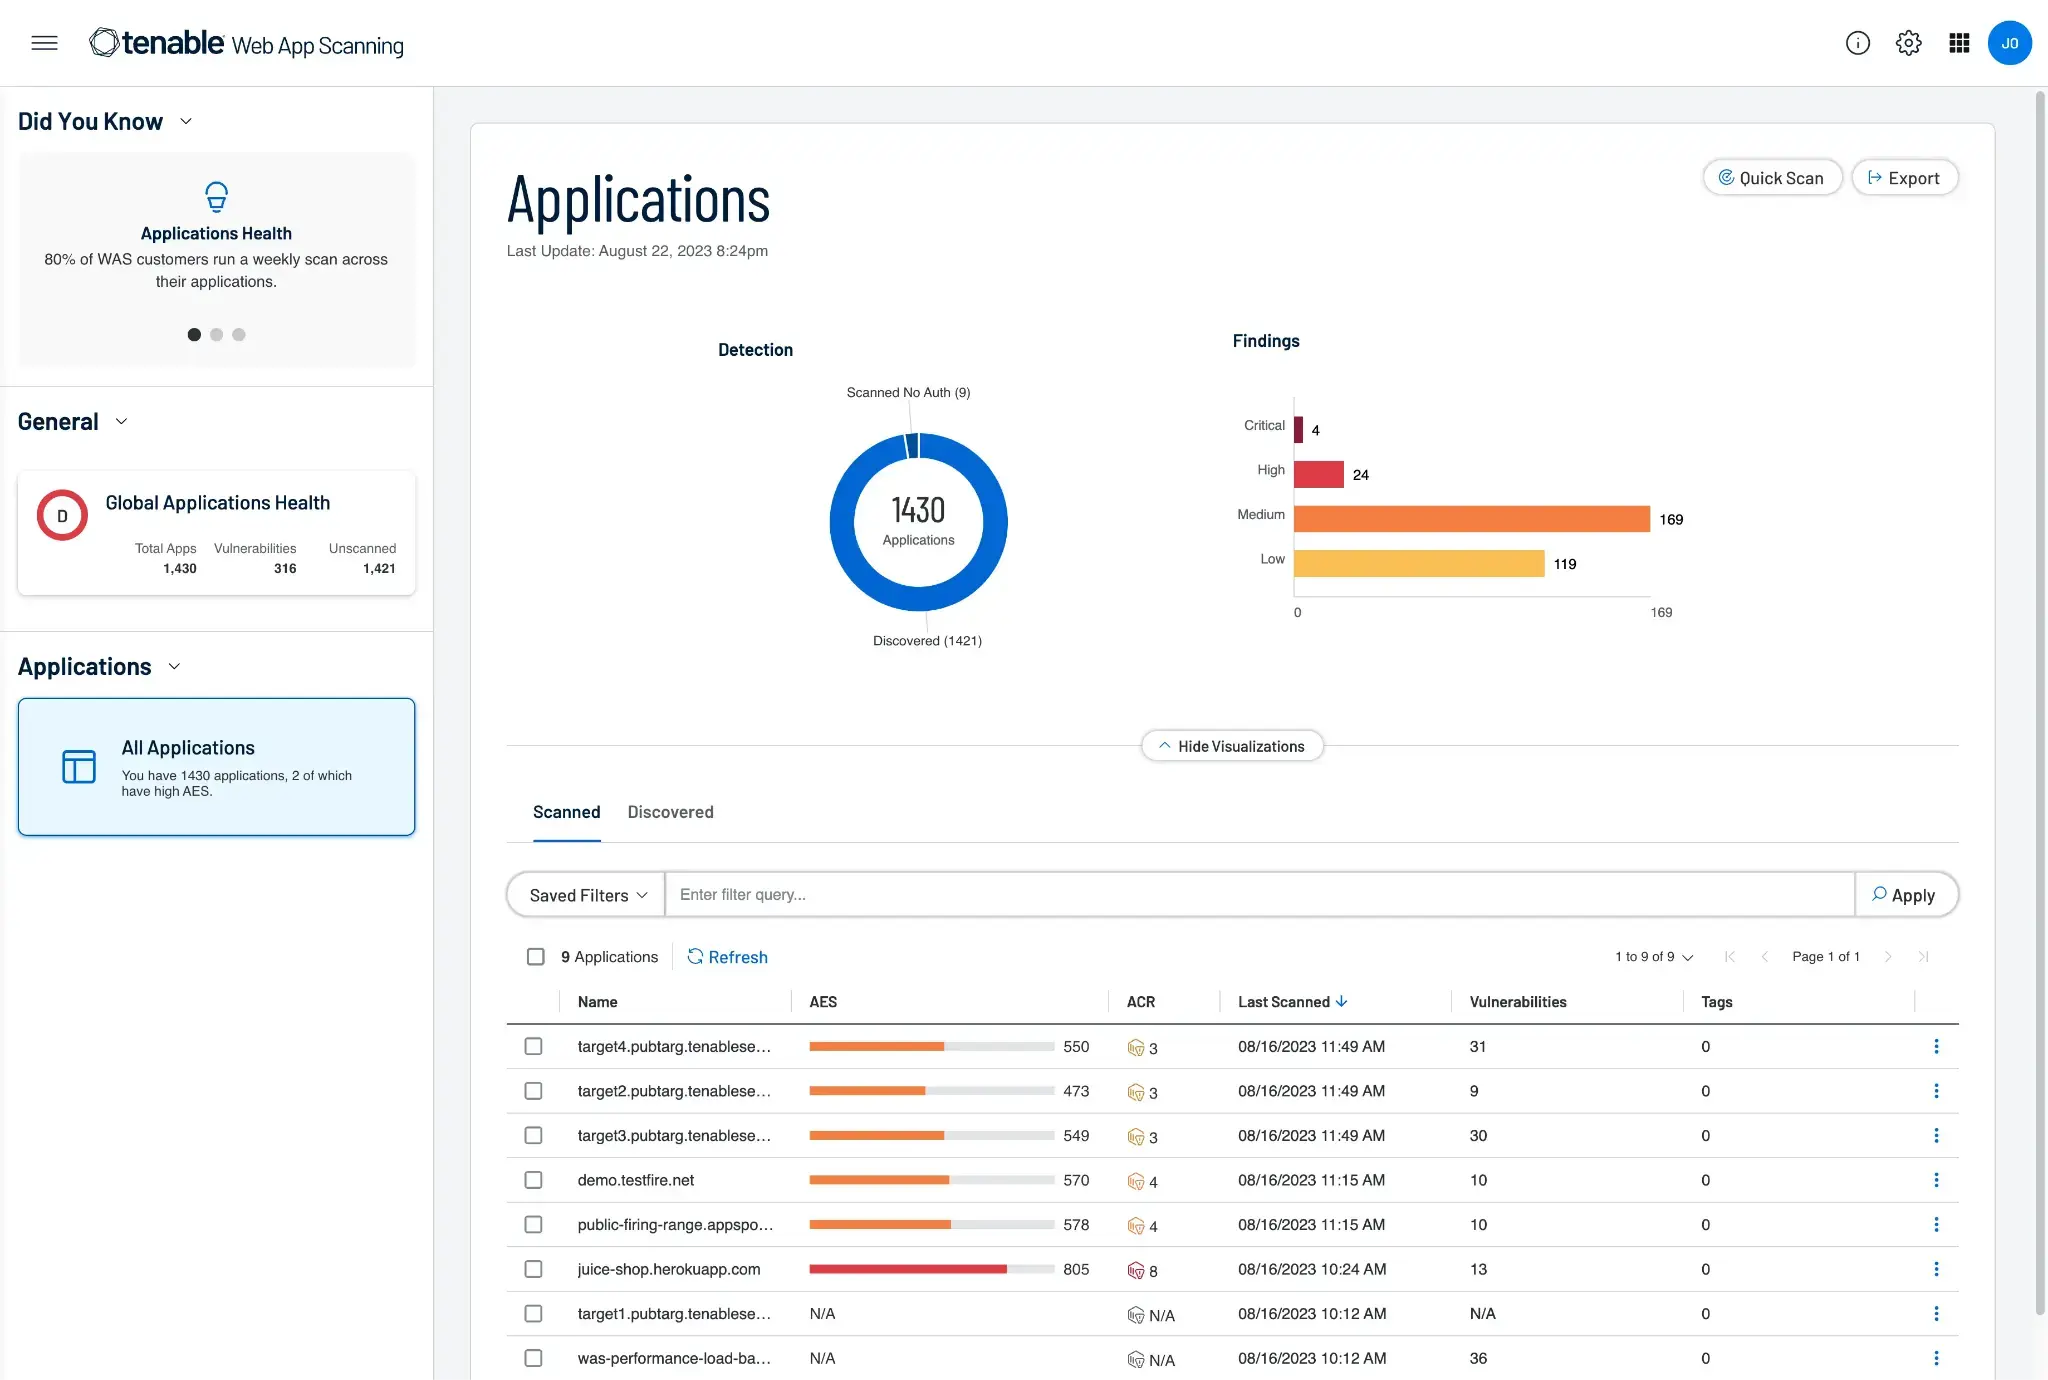
Tenable WAS extends the company’s well-known vulnerability management expertise into web application security. As part of the Tenable.io platform, it gives organizations unified visibility across infrastructure and applications.
Its straightforward onboarding and Chrome plugin for authentication simplify the setup process, which appeals to teams looking for quick deployment. While not as feature-rich as specialized DAST tools, it provides good value for organizations already invested in Tenable.
Key features
Provides automated application scanning integrated with Tenable.
Simplifies setup with a Chrome plugin for onboarding and authentication.
Supports cookies and form-based login for complex web apps.
Uses Vulnerability Priority Rating (VPR) to rank findings by risk.
Maps vulnerabilities to compliance frameworks for easier audits.
Offers a unified dashboard to view both infrastructure and app issues.
Pricing
Tenable WAS pricing begins at $7,434 annually for 5 FQDNs, with costs increasing based on the number of FQDNs.
Ratings & reviews
Gartner Peer Insights users generally rate Tenable Web App Scanning positively, with scores often reported in the range of 4.6/5 from 1,336 reviews. Customers frequently praise Tenable WAS for its intuitive setup, user-friendly interface, and seamless integration into broader vulnerability management workflows. However, some users note that advanced testing features and customizations are not as extensive as those found in highly specialized DAST platforms.
Rapid7 InsightAppSec
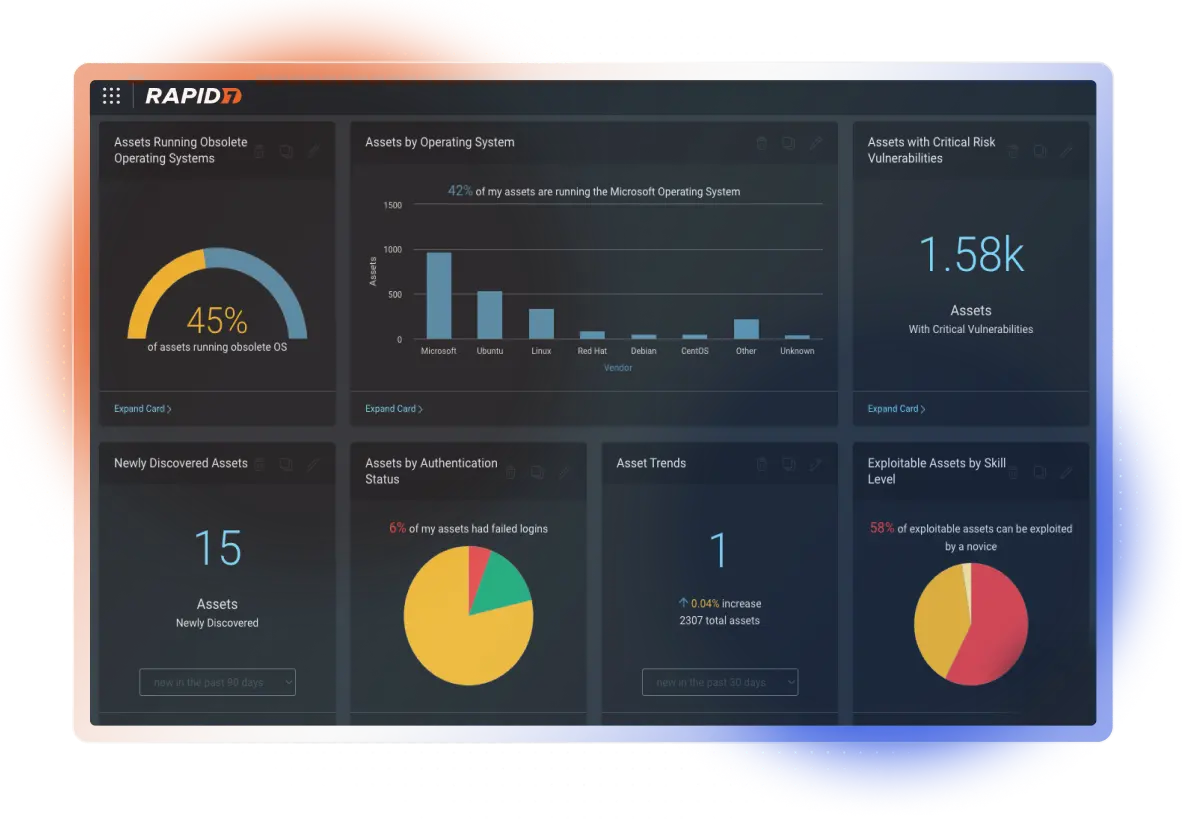
Rapid7 InsightAppSec is part of the Rapid7 InsightPlatform, giving it strong ties to vulnerability management, SIEM, and incident response modules. It is designed to handle modern applications while offering flexible integrations.
Key features
Provides web app and API security testing with modern app support.
Uses smart crawling to handle JavaScript-heavy and SPA environments.
Supports multifactor authentication and custom login flows.
Includes proof-of-concept attack simulations to validate findings.
Integrates natively with Rapid7’s broader Insight platform.
Offers REST API access for automation and DevSecOps workflows.
Pricing
InsightAppSec starts at $175 per application per month. While affordable for small deployments, costs can grow quickly for organizations with larger application portfolios.
Ratings & reviews
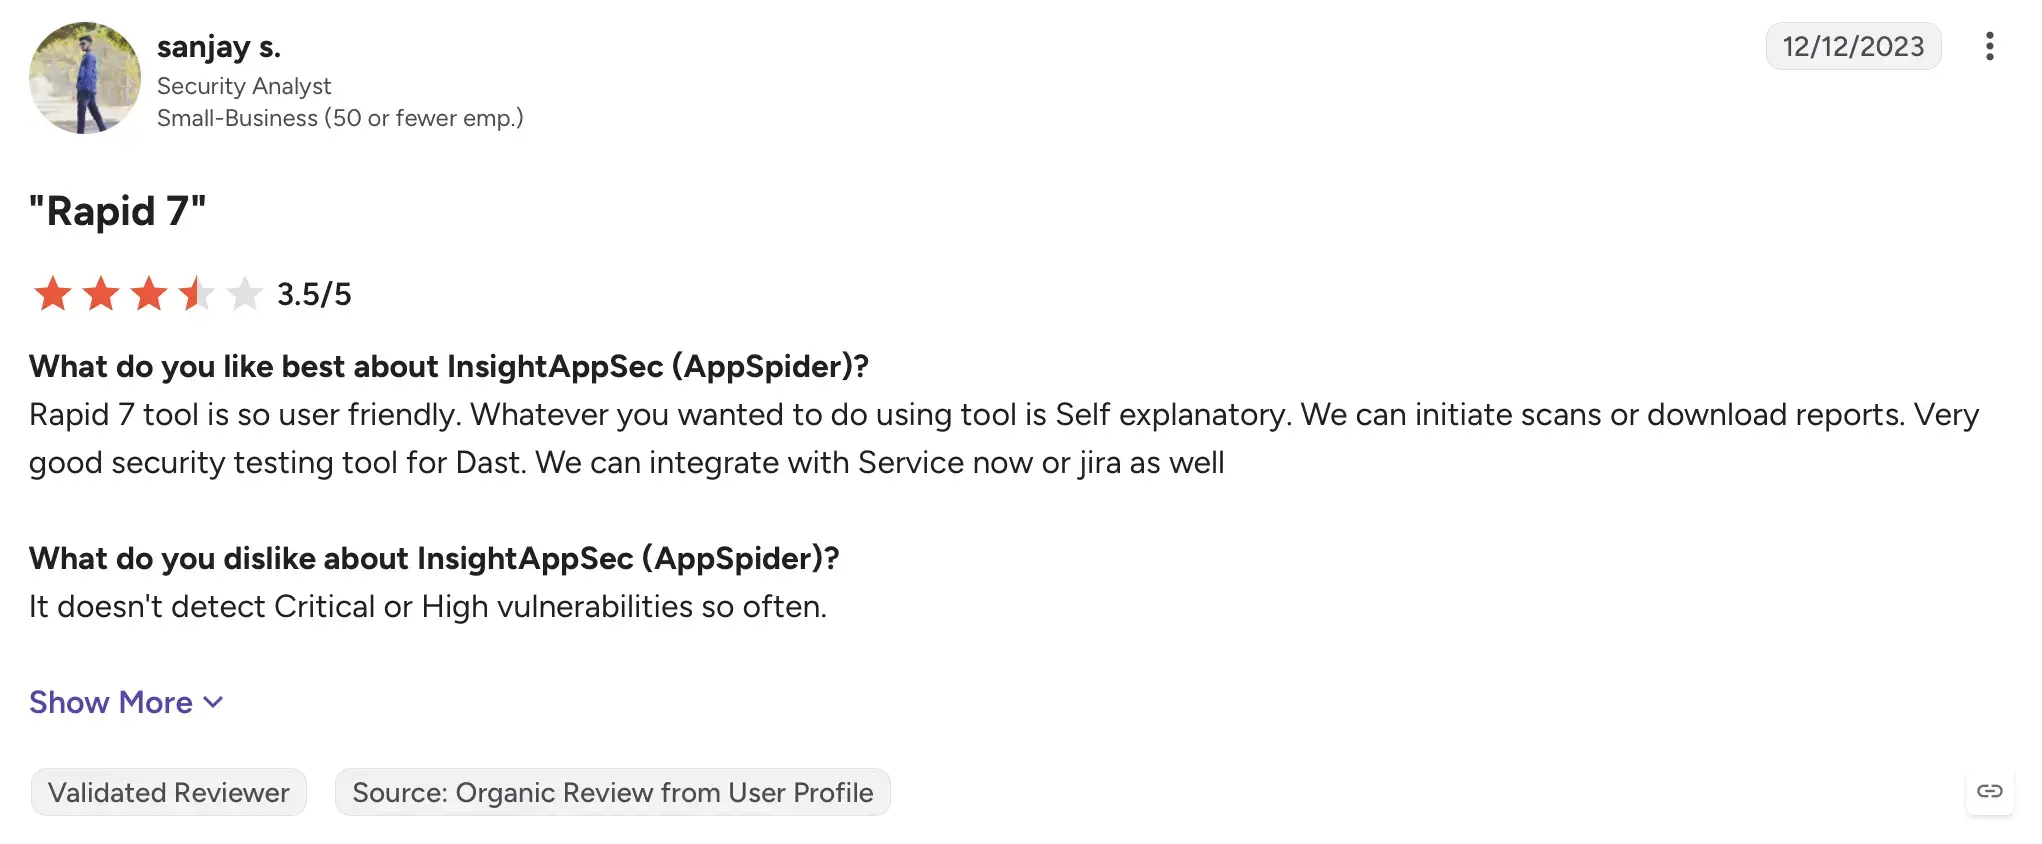
InsightAppSec is rated 3.9/5 on G2 from 10 reviews. Users value its ability to handle JavaScript-heavy applications and its integration into broader Rapid7 workflows. However, several reviews caution that pricing can escalate significantly as more apps are added.
Escape DAST
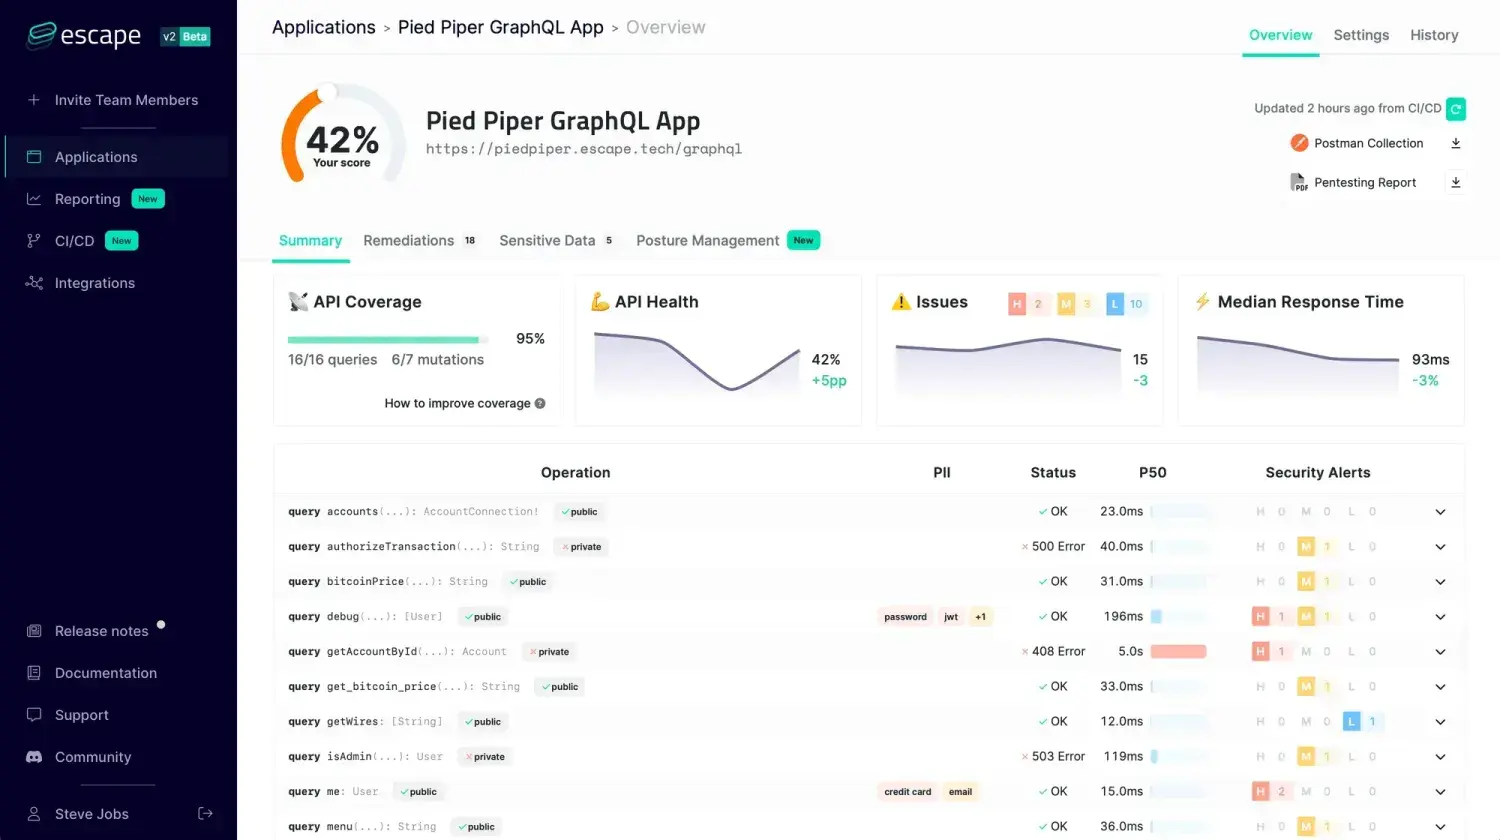
Escape DAST is a modern, API-first security platform built to address the needs of cloud-native applications. It emphasizes business logic testing and agentless discovery, which sets it apart from legacy scanners that often struggle with complex architectures. Its proprietary Business Logic Security Testing engine helps detect issues like IDORs and SSRFs, while AI-driven prioritization ensures teams focus on the most critical risks. Escape appeals to development teams who need a modern tool that integrates seamlessly with contemporary workflows.
Key features
Automatically discovers APIs and generates schemas without agents.
Provides GraphQL-native testing with context-aware security checks.
The proprietary BLST engine identifies business logic vulnerabilities like IDORs.
Uses AI-driven prioritization to highlight the most critical issues.
Offers framework-specific remediation guidance to speed up fixes.
CI/CD-friendly with YAML-based custom test definitions.
Pricing
Escape DAST uses custom pricing models based on application portfolio size. Enterprises typically request tailored quotes to match their API testing and feature requirements.
Ratings & reviews
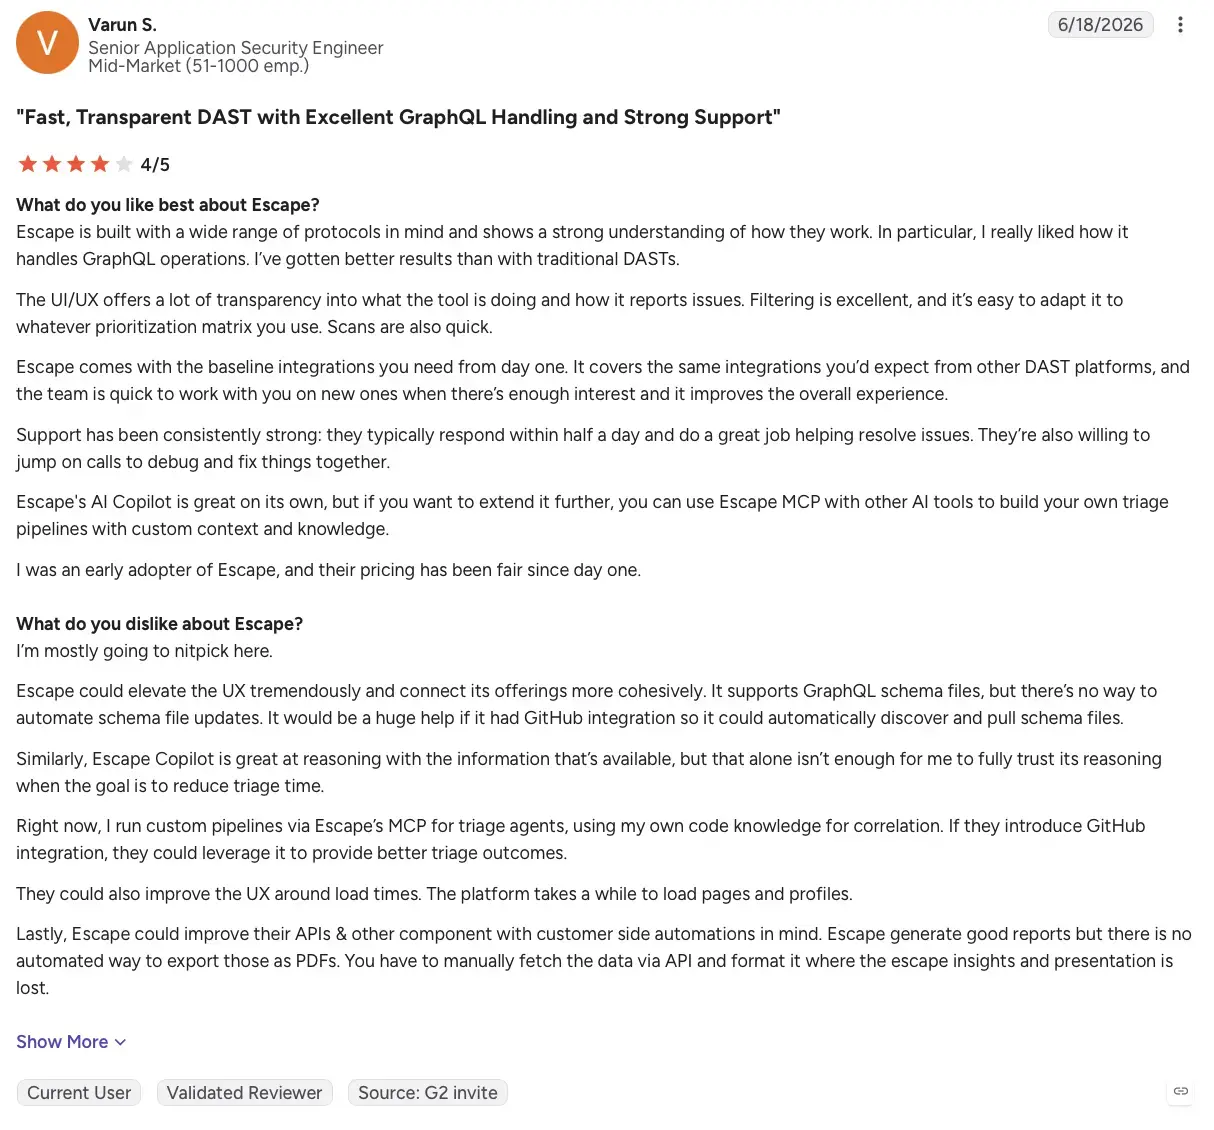
Escape DAST scores 4.9/5 on G2 from 10 reviews. Reviewers consistently mention its low false-positive rate and actionable remediation guidance. Teams appreciate how well it fits into modern development practices, though some note that its user community is still smaller than those of older tools.
Key factors for choosing an Invicti Web + API (formerly Acunetix) alternative
Primary use case and team focus
Automated DevSecOps & CI/CD: Beagle Security, Veracode, Checkmarx. Best for teams needing API coverage and CI/CD integration.
Manual penetration testing: Burp Suite Professional. Ideal for security professionals needing granular testing control.
Holistic vulnerability management: Tenable WAS, Rapid7 InsightAppSec, Qualys WAS. Suitable for enterprises requiring platform-level integration.
Budget-conscious scanning: ZAP. Free and powerful, but requires technical setup.
Ease of use and intended audience
Developer-friendly tools: Beagle Security, Invicti Web + API. Simple interfaces and clear remediation.
Security-professional focused tools : Burp Suite Professional, Checkmarx. Deep functionality requires expertise.
Scalability and environment size
Small to mid-sized businesses: Beagle Security, Invicti Web + API. Balanced cost and usability.
Large enterprises: Veracode, Checkmarx, Tenable WAS, Qualys WAS. Strong reporting and centralized dashboards.
Budget and pricing model
Free and open source: ZAP. No cost, but requires technical expertise.
Cost-effective: Burp Suite Professional (499/year), Beagle Security (1,188/year), Tenable WAS (Higher cost but broad coverage).
Deployment model
Cloud-native (SaaS): Beagle Security, Veracode, Tenable, Qualys Cloud. Easy setup, vendor-managed.
On-premise and hybrid: Burp Suite Enterprise, Checkmarx. Greater control for compliance-heavy teams.
Conclusion
Invicti Web + API (formerly Acunetix) remains a strong web application security scanner, but in 2025, organizations have many compelling alternatives. The tools explored here offer unique advantages, whether it is Beagle Security’s agentic AI penetration testing, Burp Suite’s professional testing depth, ZAP’s cost-free flexibility, or Escape DAST’s API-first approach.
Ultimately, the best choice depends on your team’s goals, scale, and budget. Small businesses may prefer developer-friendly tools with predictable pricing, while large enterprises often gravitate toward platforms like Veracode or Checkmarx for full lifecycle coverage. Open-source options like ZAP remain invaluable for those with the expertise to configure them.
The key is aligning the tool with your security priorities and workflows. With the right selection, organizations can achieve stronger security outcomes, lower costs, and greater efficiency than relying on Invicti Web + API alone.
FAQs
Why should businesses consider alternatives to Invicti Web + API (formerly Acunetix)?
Businesses may explore Invicti Web + API alternatives when they need different pricing models, more extensive API security testing, business logic testing, closer CI/CD integration, or broader application security capabilities. Comparing tools helps organizations find a solution that better fits their development workflows, security requirements, and budget.
Are there free alternatives to Invicti Web + API (formerly Acunetix)?
Yes. ZAP by Checkmarx is a free, open-source web application security testing tool. It supports automated scanning, passive analysis, application crawling, and API testing through OpenAPI definitions. However, using it effectively may require more technical expertise and configuration than a commercial platform.
What is the difference between Invicti Web + API (formerly Acunetix) and Beagle Security?
Invicti Web + API focuses on dynamic application security testing (DAST) for web applications and APIs, including vulnerability detection and proof-based scanning. Beagle Security focuses on agentic AI penetration testing, with capabilities such as business logic testing, authenticated testing, and contextual remediation guidance. The better fit depends on your testing requirements and the level of attack simulation your team needs.