Best cybersecurity agentic AI tools for 2026
Security teams are drowning in alerts. Analysts are overworked. Attackers are moving faster than ever. The result? A constant state of fatigue in Security Operations Centers (SOCs) worldwide. Traditional AI helped security teams process data faster, but it still relied heavily on human intervention. In 2026, that is no longer enough.
Enter agentic AI. This new class of AI does not just detect or recommend; it acts. It reasons, learns, and takes initiative to investigate and respond to threats autonomously. Imagine an AI security analyst that does not need a break, learns from every incident, and adapts to new attack patterns in real time. That is the promise of agentic AI cybersecurity.
Unlike traditional AI models, which classify data or make predictions based on static training, agentic AI operates with intent. It is goal-driven, context-aware, and capable of completing multi-step tasks such as investigating anomalies, gathering intelligence, and executing response actions. These systems are transforming how security teams operate, shifting the balance from reactive defense to proactive, autonomous protection.
In this blog, we will review the top cybersecurity agentic AI tools in 2026, comparing their features, use cases, and pricing so you can choose the one that fits your needs.
Top cybersecurity agentic AI tools at a glance
Here is a quick overview of the leading agentic AI security tools. Unlike traditional AI that merely flags risks, these platforms autonomously investigate, reason about threats, and take action, transforming security operations from reactive to proactive.
| Tool | Category | Primary use case | Pricing |
|---|---|---|---|
| Beagle Security | Application security testing | Autonomous vulnerability testing that adapts to app behavior | Starting at $1,188/year |
| Purple AI by SentinelOne | EDR/XDR | Natural language threat investigation and autonomous endpoint response | Custom pricing |
| Google SecOps | Security operations and analytics | LLM-powered threat correlation and automated response orchestration | Quote based |
| CrowdStrike Falcon Platform | EDR/XDR | Autonomous endpoint protection and real-time incident response | Starting at $7.99/endpoint/month |
| Vectra AI | Network detection and response | AI-driven network threat detection and automated attacker tracking | Custom pricing |
| Cyble | Threat intelligence and ASM | Proactive threat intelligence and autonomous dark web monitoring | Custom pricing |
| Radiant Security | Security orchestration and response | Autonomous incident response and multi-tool remediation workflows | Custom pricing |
Best cybersecurity agentic AI tools in 2026
Beagle Security
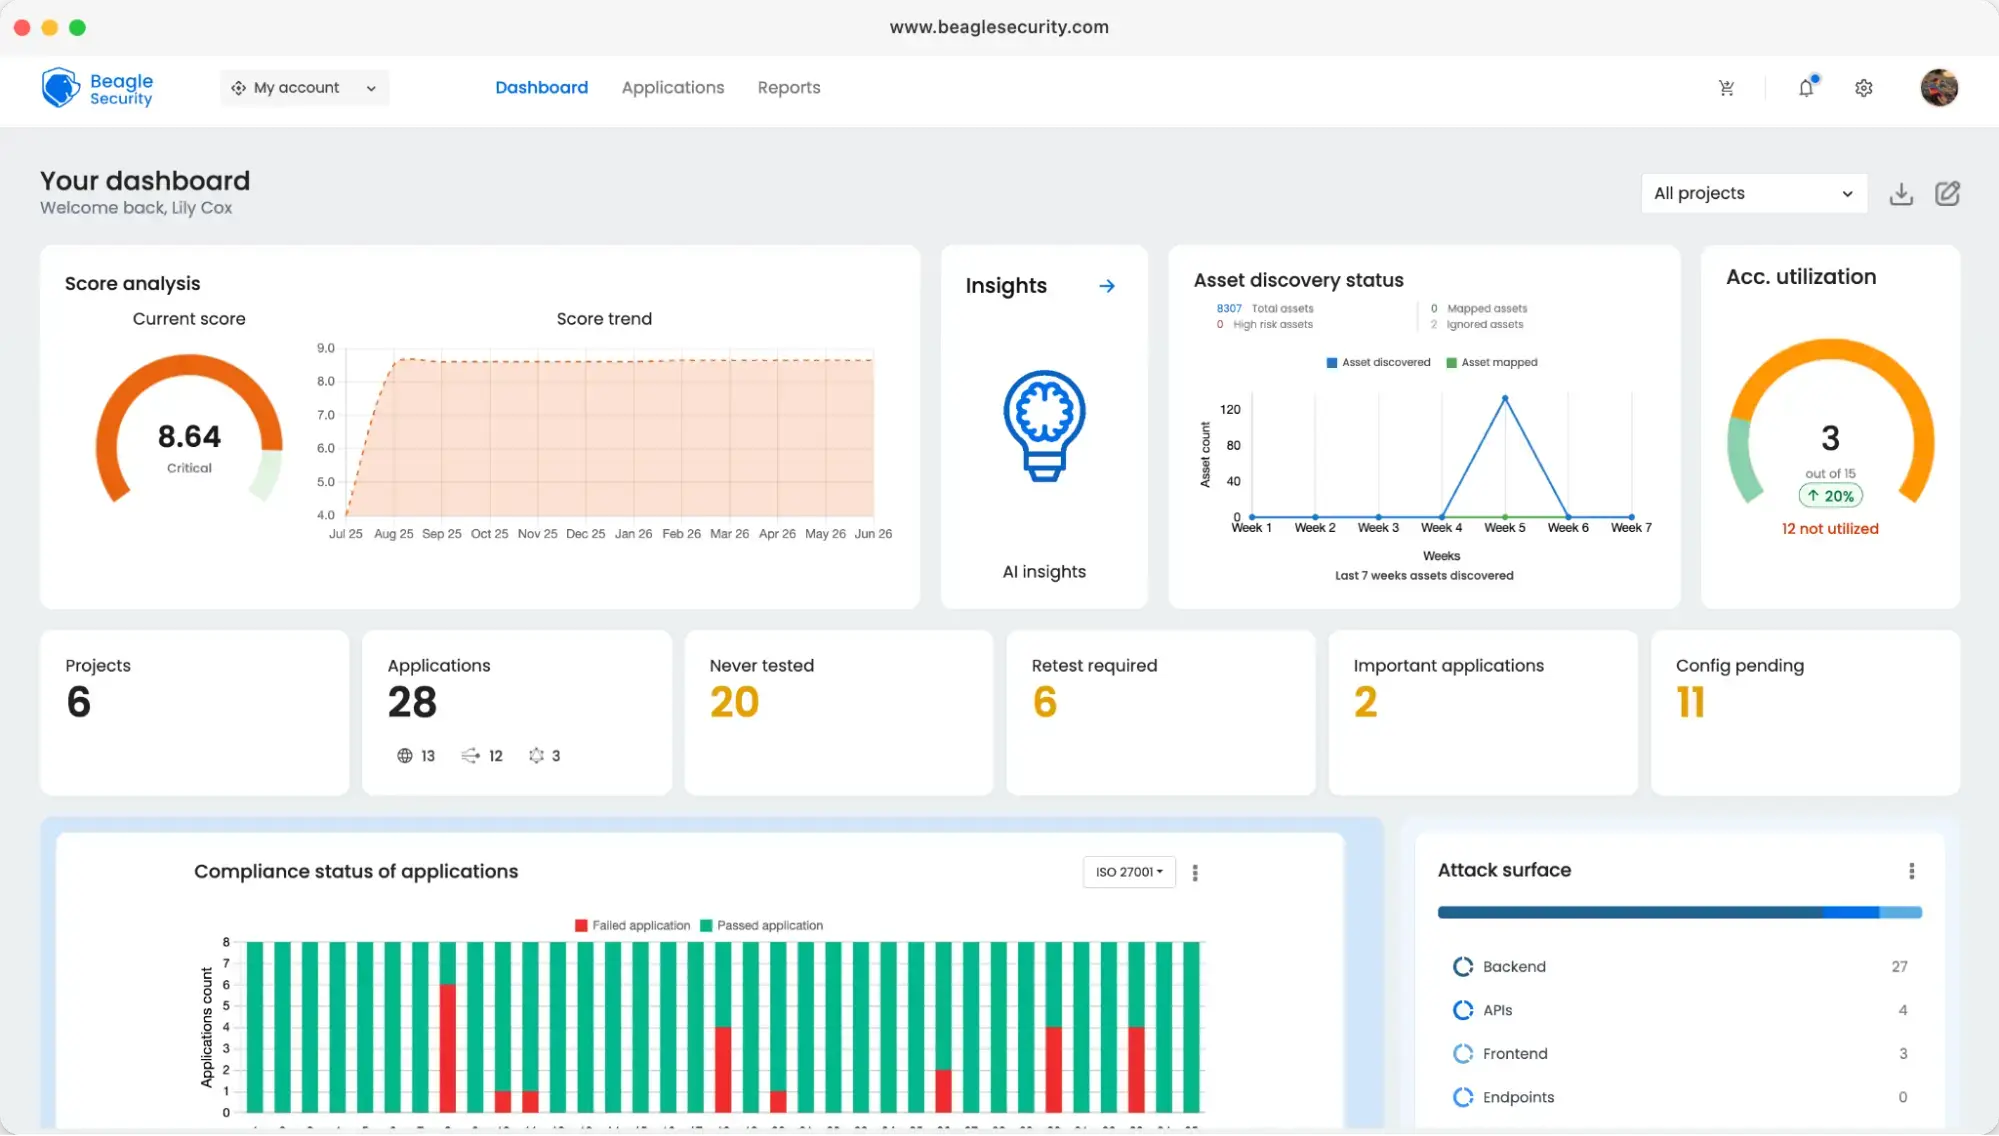
Beagle Security pioneers agentic AI in application security testing. Its platform continuously discovers, tests, and validates vulnerabilities using autonomous penetration testing. Instead of running static scans, Beagle Security’s agentic engine adapts test strategies based on application behavior, learns from previous results, and refines its attack simulations automatically. Designed for modern DevSecOps workflows, it functions like an AI security engineer embedded in your CI/CD pipeline.
Key features
Autonomous vulnerability discovery and validation
Adaptive testing that learns from previous runs
API-first design for CI/CD and cloud-native workflows
Continuous monitoring for API and web application changes
Context-aware prioritization and risk scoring
AI-driven remediation guidance with developer integration
Supports REST, GraphQL, and multi-cloud applications
G2 rating: 4.7/5 (88 reviews)
Pricing: Starting at $1,188/year
Purple AI by SentinelOne
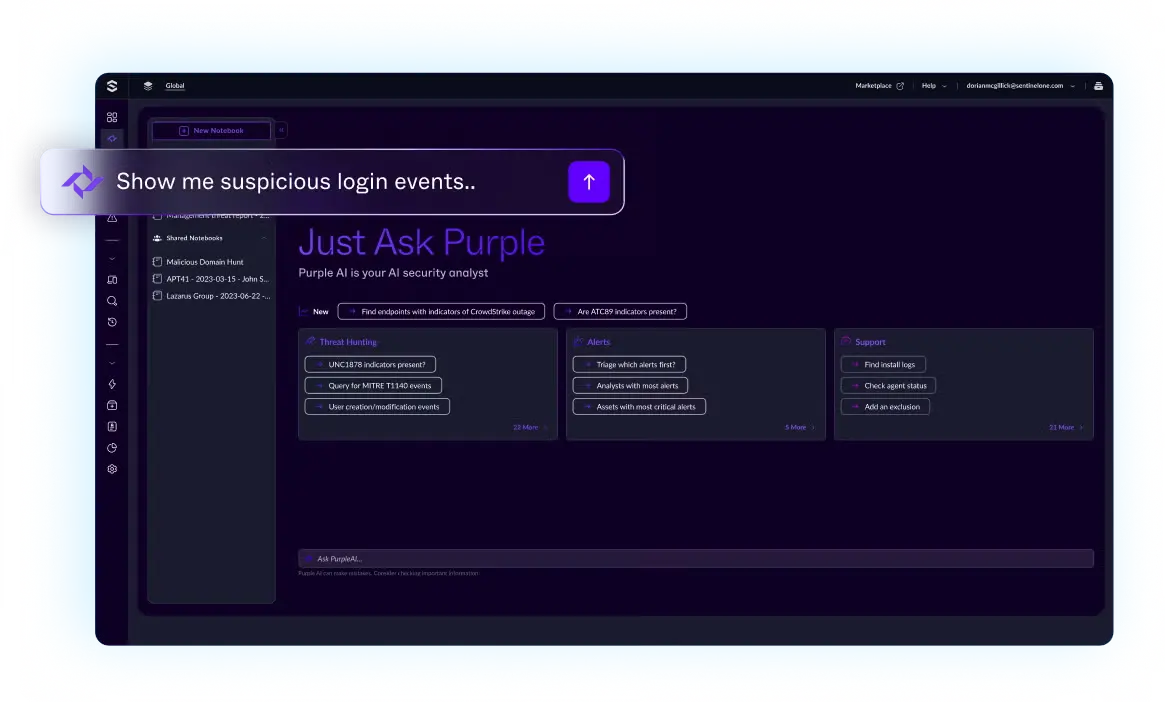
Purple AI acts as an autonomous SOC analyst within SentinelOne’s XDR ecosystem. Built on large language models, it enables natural language interaction, autonomous threat investigation, and response. Analysts can simply ask “What is the root cause of this alert?” and receive context-driven answers backed by AI reasoning. It correlates data across endpoints, identities, and cloud assets to make intelligent, autonomous decisions.
Key features
Natural language interaction for investigation and remediation
Autonomous threat correlation and analysis across data sources
Real-time decision-making with transparent reasoning
Integration with SentinelOne Singularity XDR
Automated incident response with minimal human oversight
Self-learning from prior incident data
Agentic reasoning engine for contextual prioritization
G2 rating: 4.8/5 (2 reviews)
Pricing: Custom pricing
Google SecOps
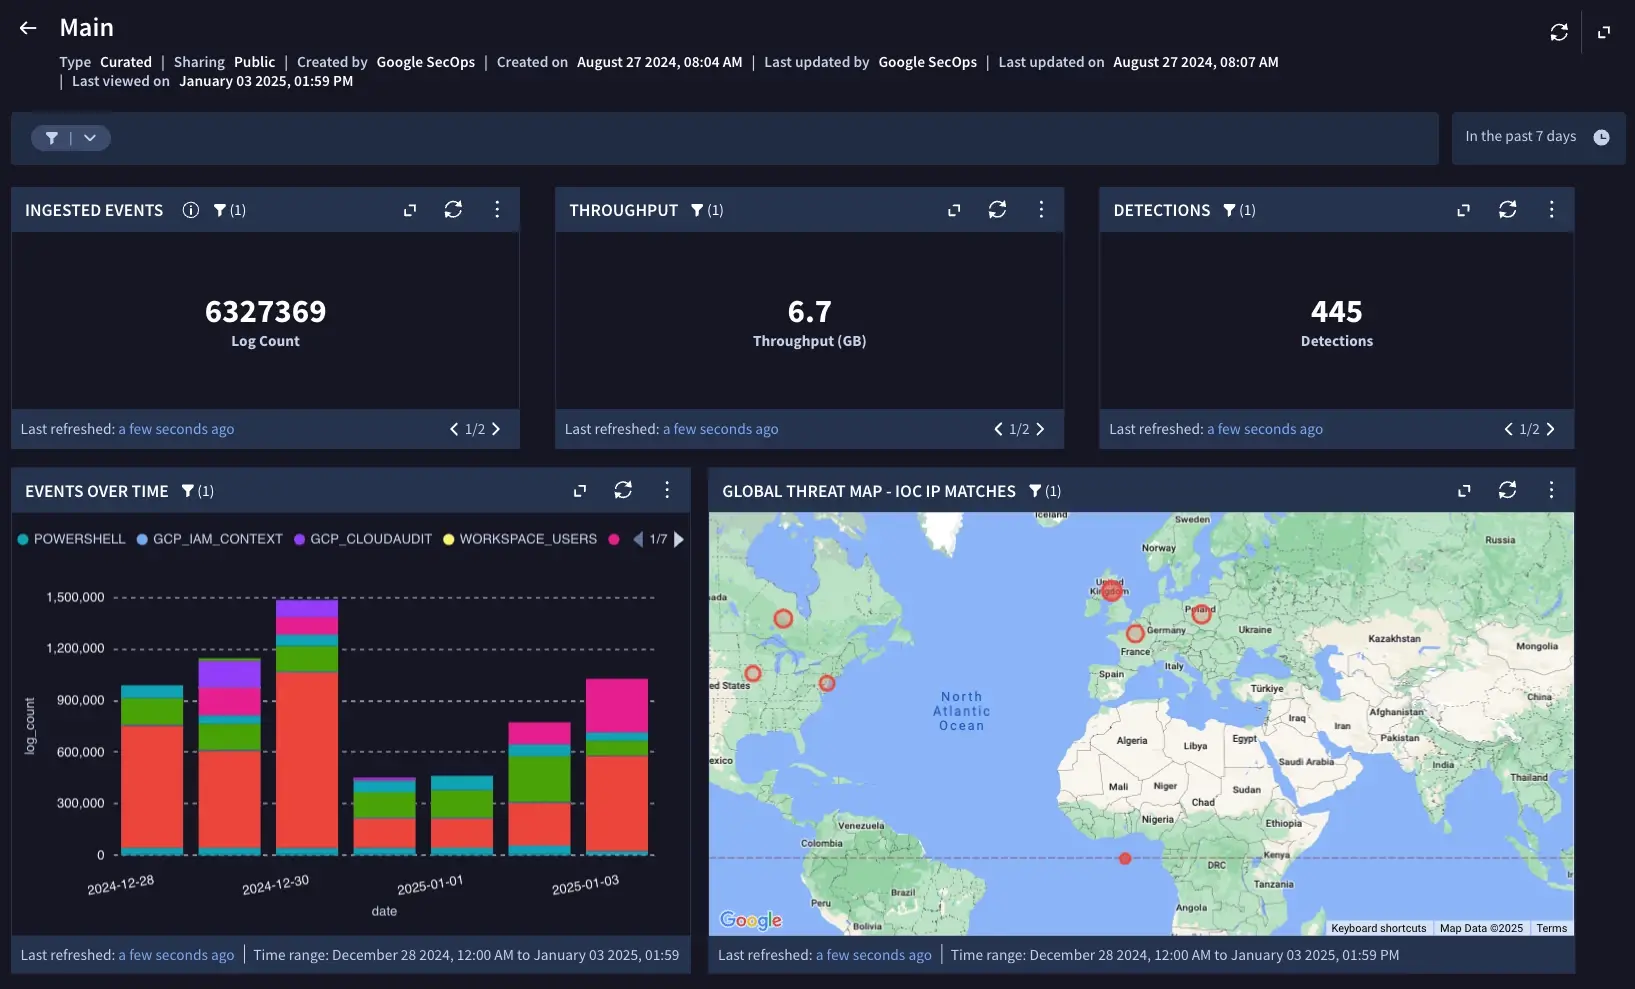
Google SecOps combines Chronicle SIEM, SOAR, and Gemini-based agentic AI to create an intelligent security operations platform. Its AI agents autonomously analyze billions of events, correlate cross-domain data, and surface actionable insights. Security teams can use natural language queries to trigger investigations or let the AI handle triage and response on its own.
Key features
Gemini LLM integration for autonomous reasoning
Automated alert triage and event correlation
Predictive analytics for early threat detection
Cloud-native scalability and multi-cloud integration
Automated playbook execution through SOAR workflows
Contextual prioritization using entity behavior analytics
Transparent audit trail of AI-driven decisions
G2 rating: 4.4/5 (143 reviews)
Pricing: Quote-based
CrowdStrike Falcon Platform
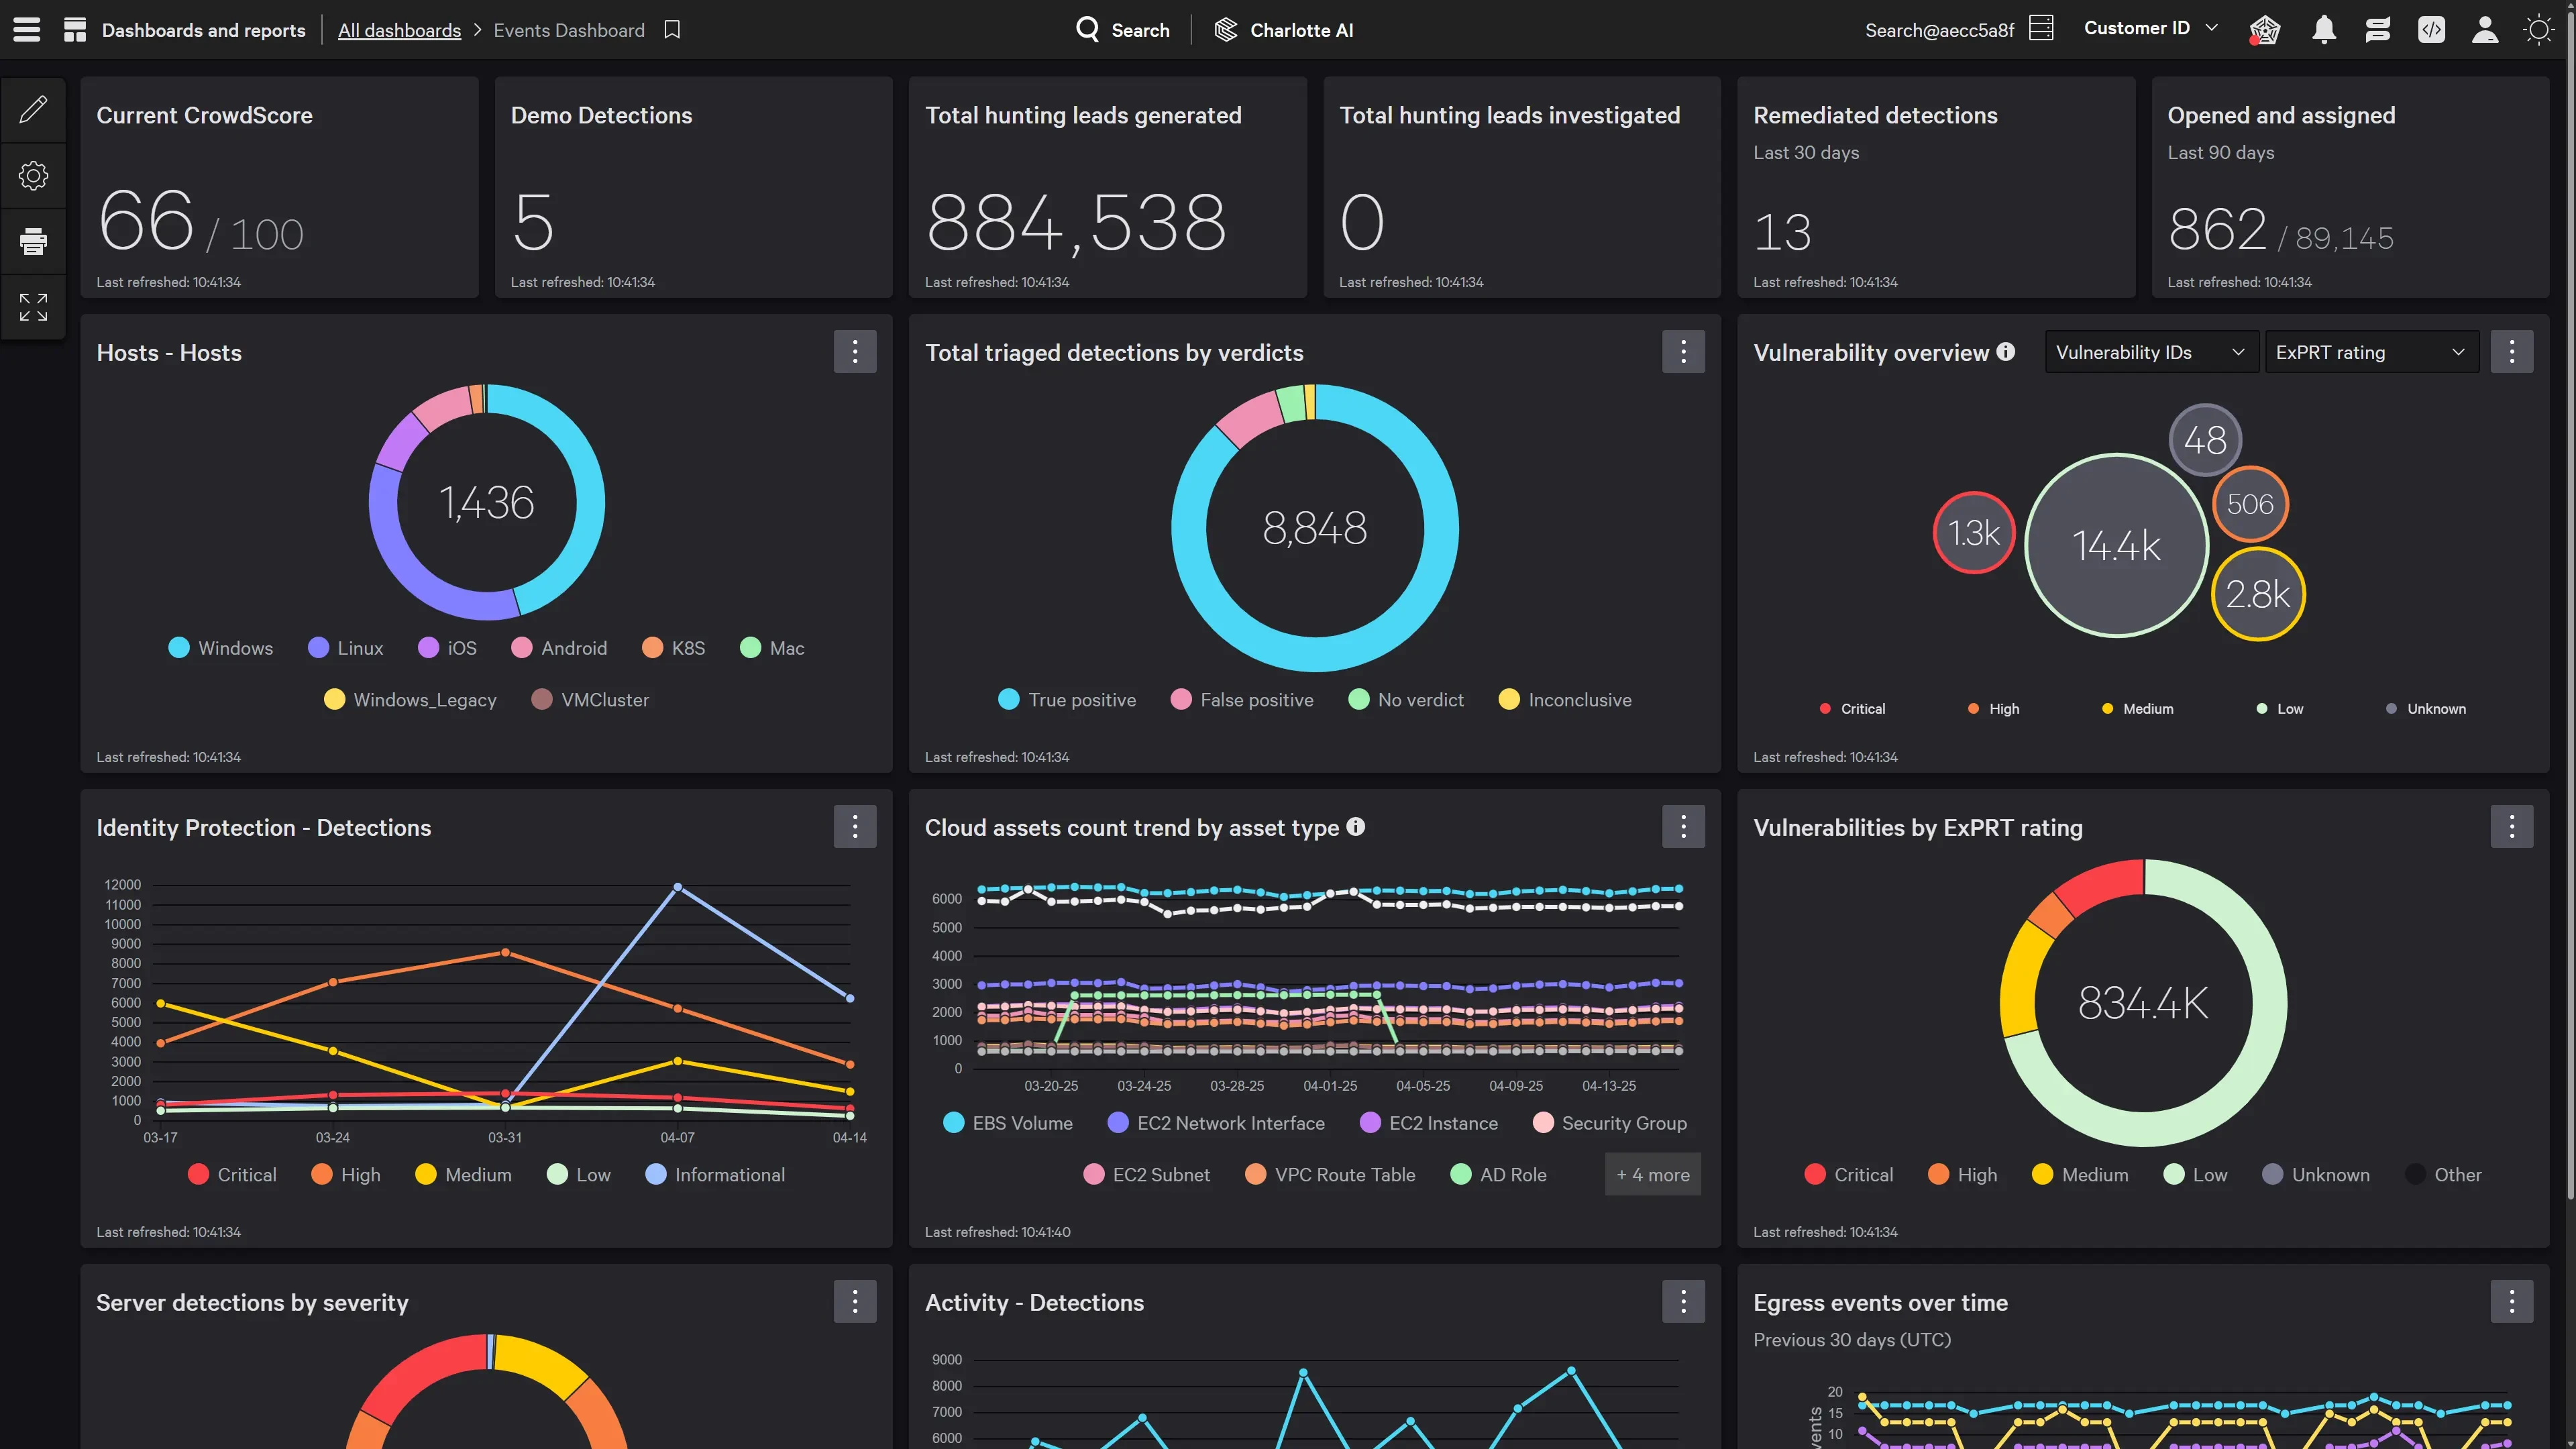
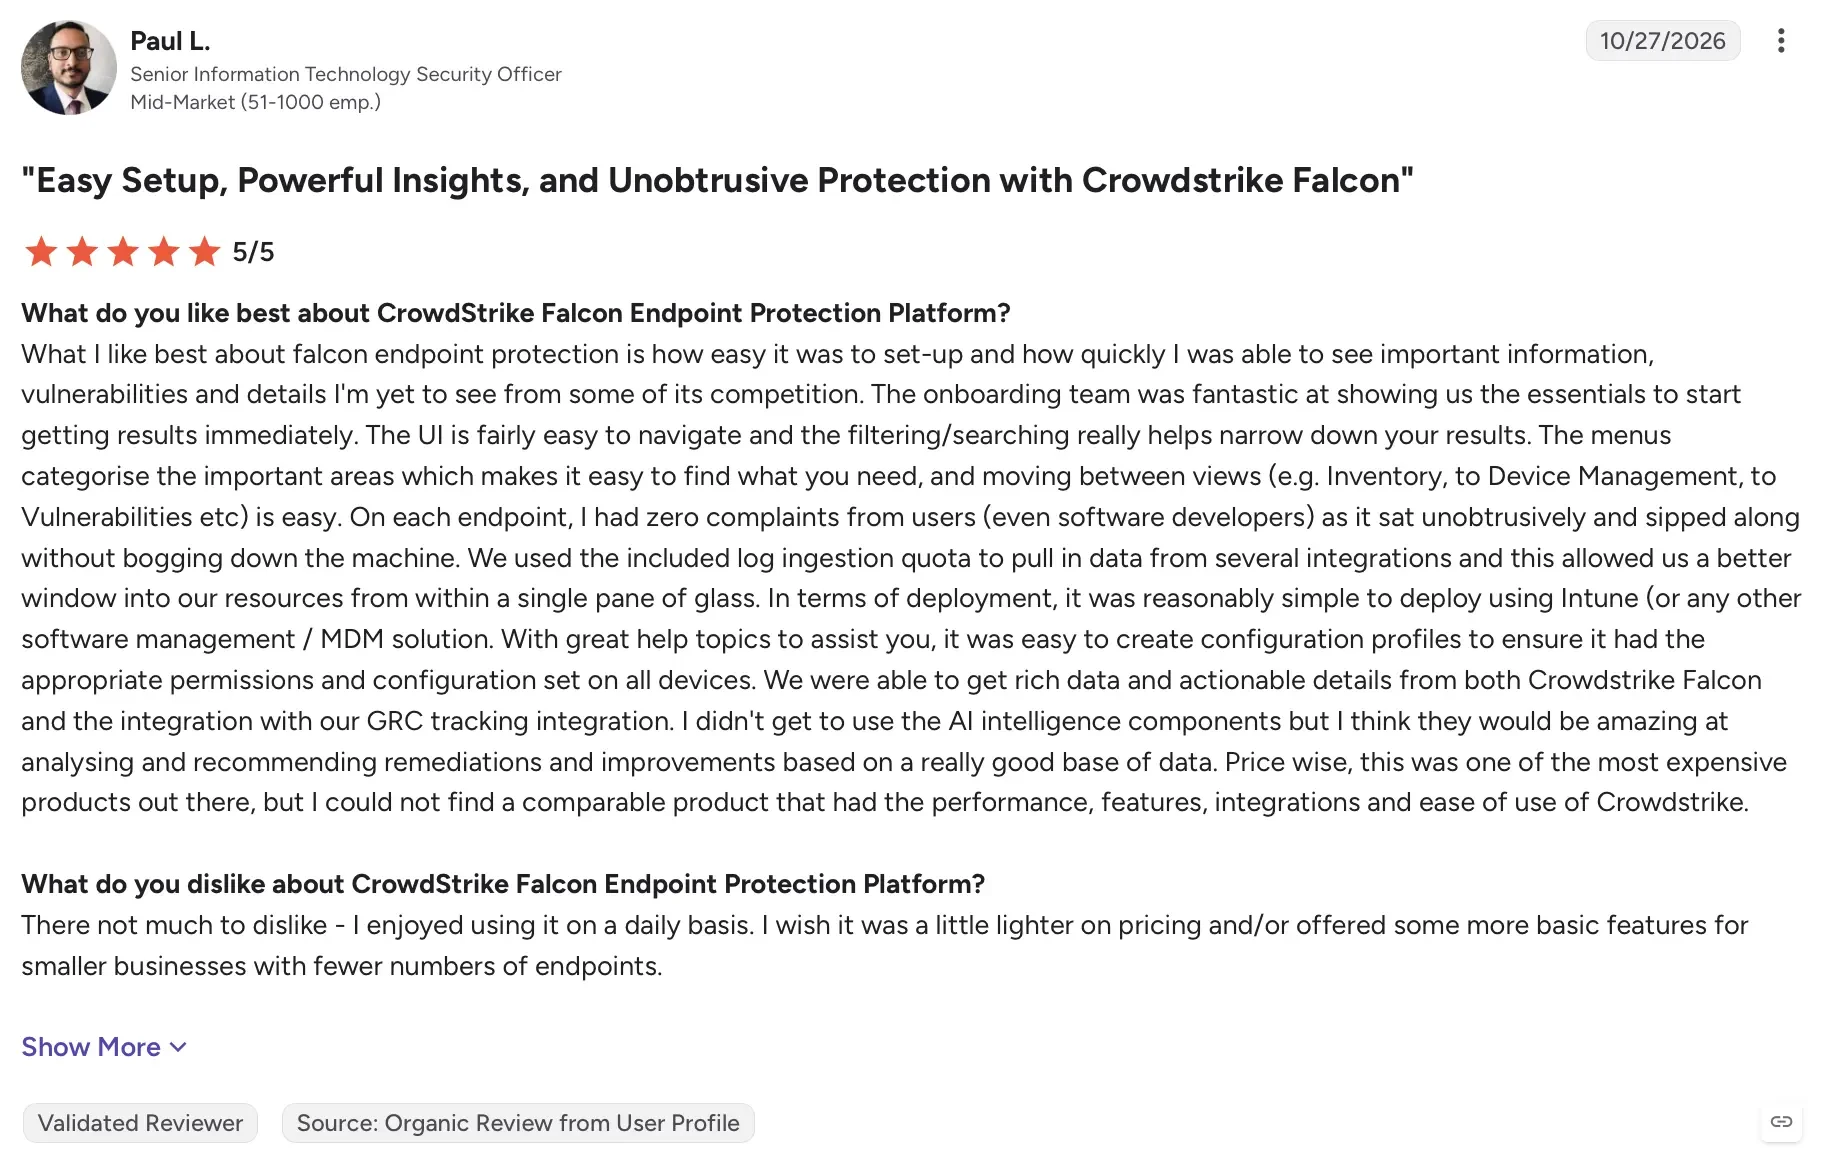
CrowdStrike Falcon integrates agentic AI capabilities through Charlotte AI, its natural language assistant and autonomous response layer. The platform learns from every endpoint event, identifies potential threats, investigates anomalies, and initiates remediation without manual triggers. It bridges human-AI collaboration by explaining its reasoning while executing autonomous actions at machine speed.
Key features
Charlotte AI for conversational threat investigation
Autonomous containment and remediation actions
Continuous behavioral learning from endpoint telemetry
Cross-environment correlation for hybrid cloud visibility
Self-updating threat models powered by the CrowdStrike AI engine
Human-in-the-loop transparency for decision approval
Integration with SIEM, SOAR, and ITSM platforms
G2 rating: 4.7/5 (589 reviews)
Pricing: Starting at $7.99/endpoint/month
Vectra AI
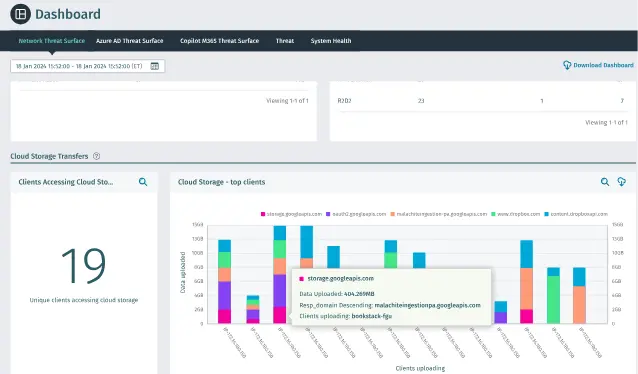
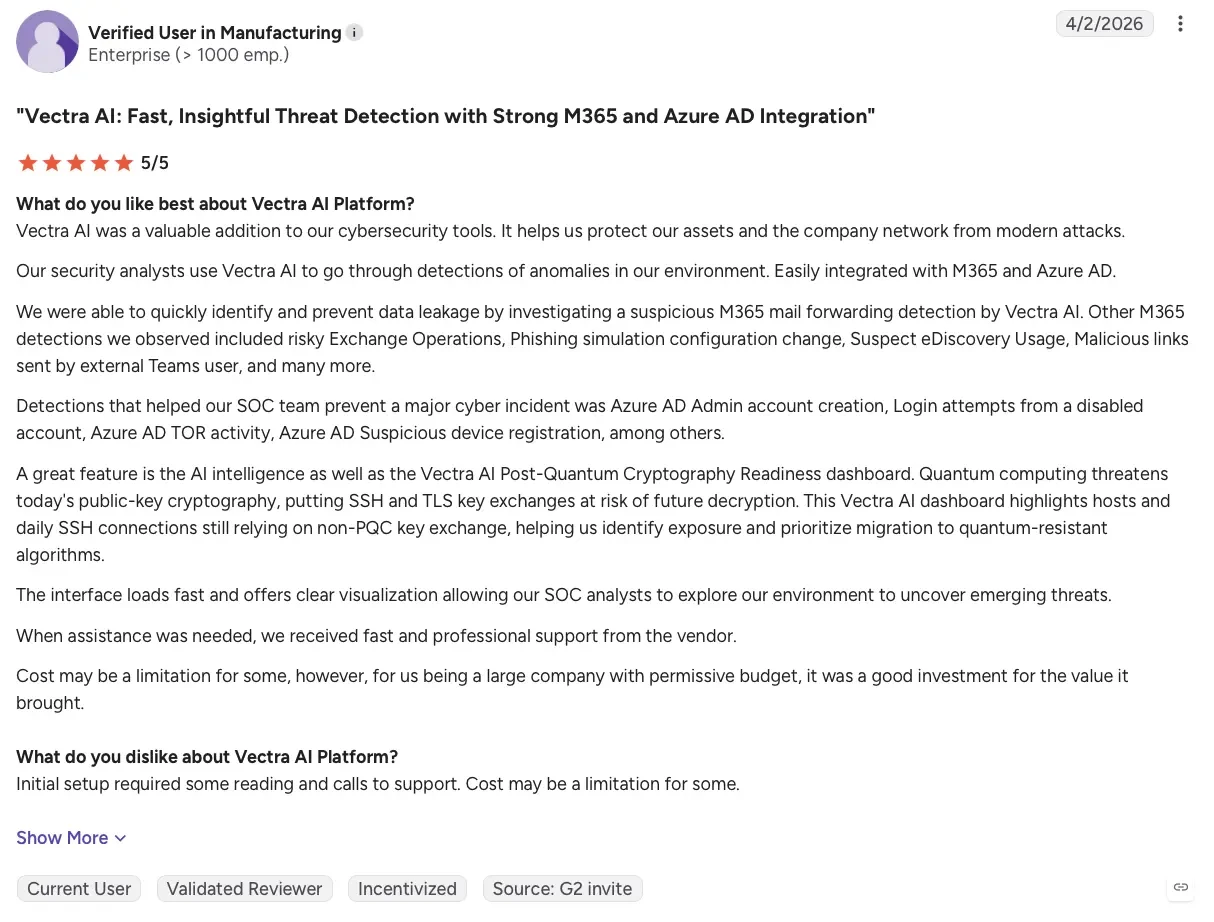
Vectra AI delivers autonomous network threat detection through continuous behavioral analysis and AI-driven threat progression mapping. Its agentic models detect subtle attacker movements like lateral spread, privilege escalation, and command-and-control communication. Vectra’s system learns from historical traffic and prioritizes critical threats in real time, enabling proactive defense at the network layer.
Key features
Continuous learning from network traffic behavior
Autonomous threat hunting and progression tracking
Correlation of attacker behaviors across environments
Real-time prioritization based on business impact
Integration with SIEM, SOAR, and XDR tools
AI-driven insights for network segmentation and hardening
Agentic decision-making for automated alerts and responses
G2 rating: 4.3/5 (20 reviews)
Pricing: Custom pricing
Cyble
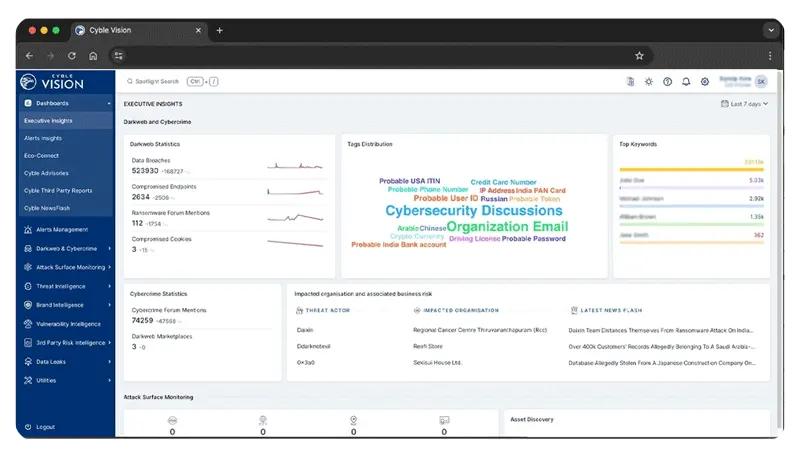
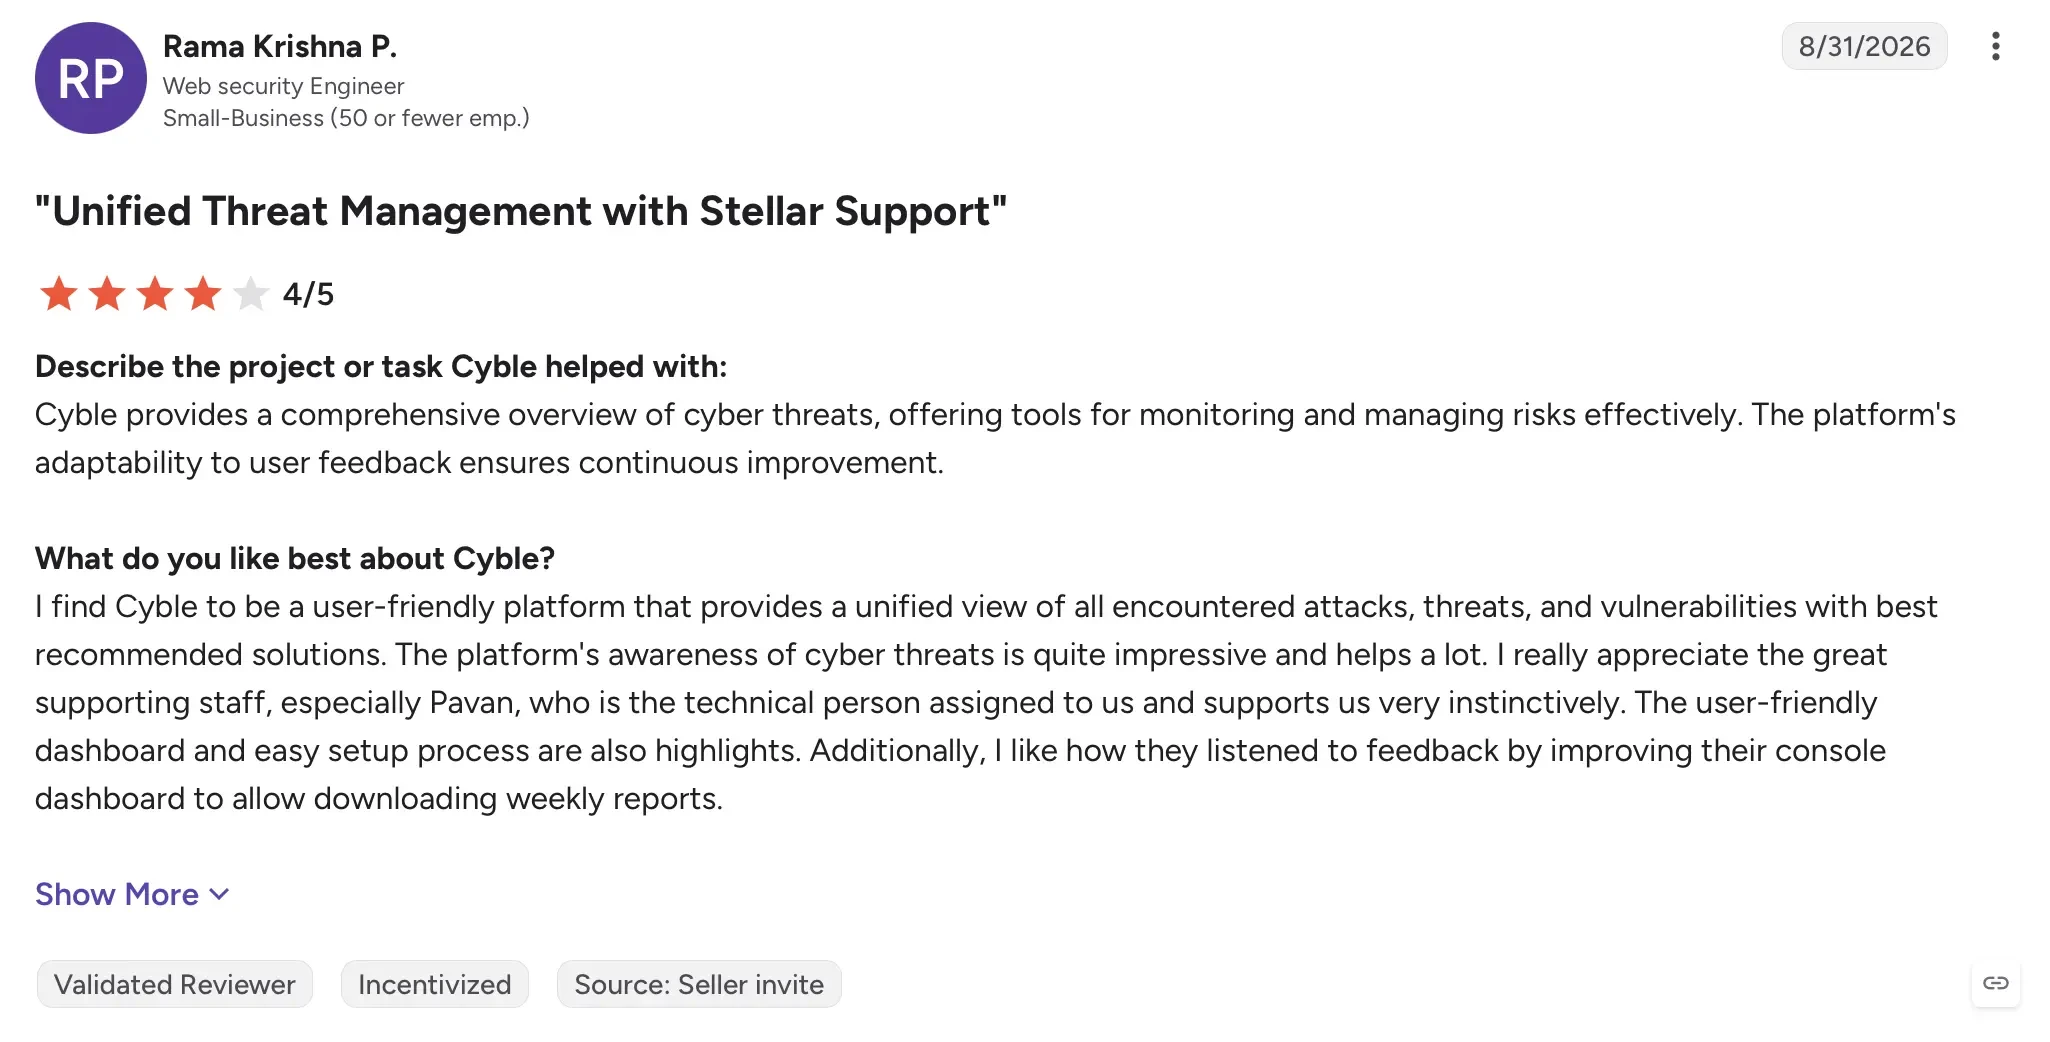
Cyble’s agentic AI platform automates external threat intelligence, dark web monitoring, and attack surface management. It continuously discovers new threats, predicts risks, and executes mitigation recommendations autonomously. The platform’s AI agents scour hacker forums, leaked databases, and dark web marketplaces to identify potential exposures before they turn into breaches.
Key features
Autonomous dark web and surface web intelligence gathering
Predictive risk scoring using adaptive AI models
Automated alerts for brand impersonation and data leaks
Continuous attack surface monitoring and risk mapping
Integration with threat intelligence feeds and SIEM tools
LLM-driven contextual analysis of threat actors
Actionable insights for proactive mitigation
G2 rating: 4.8/5 (150 reviews)
Pricing: Custom pricing
Radiant Security
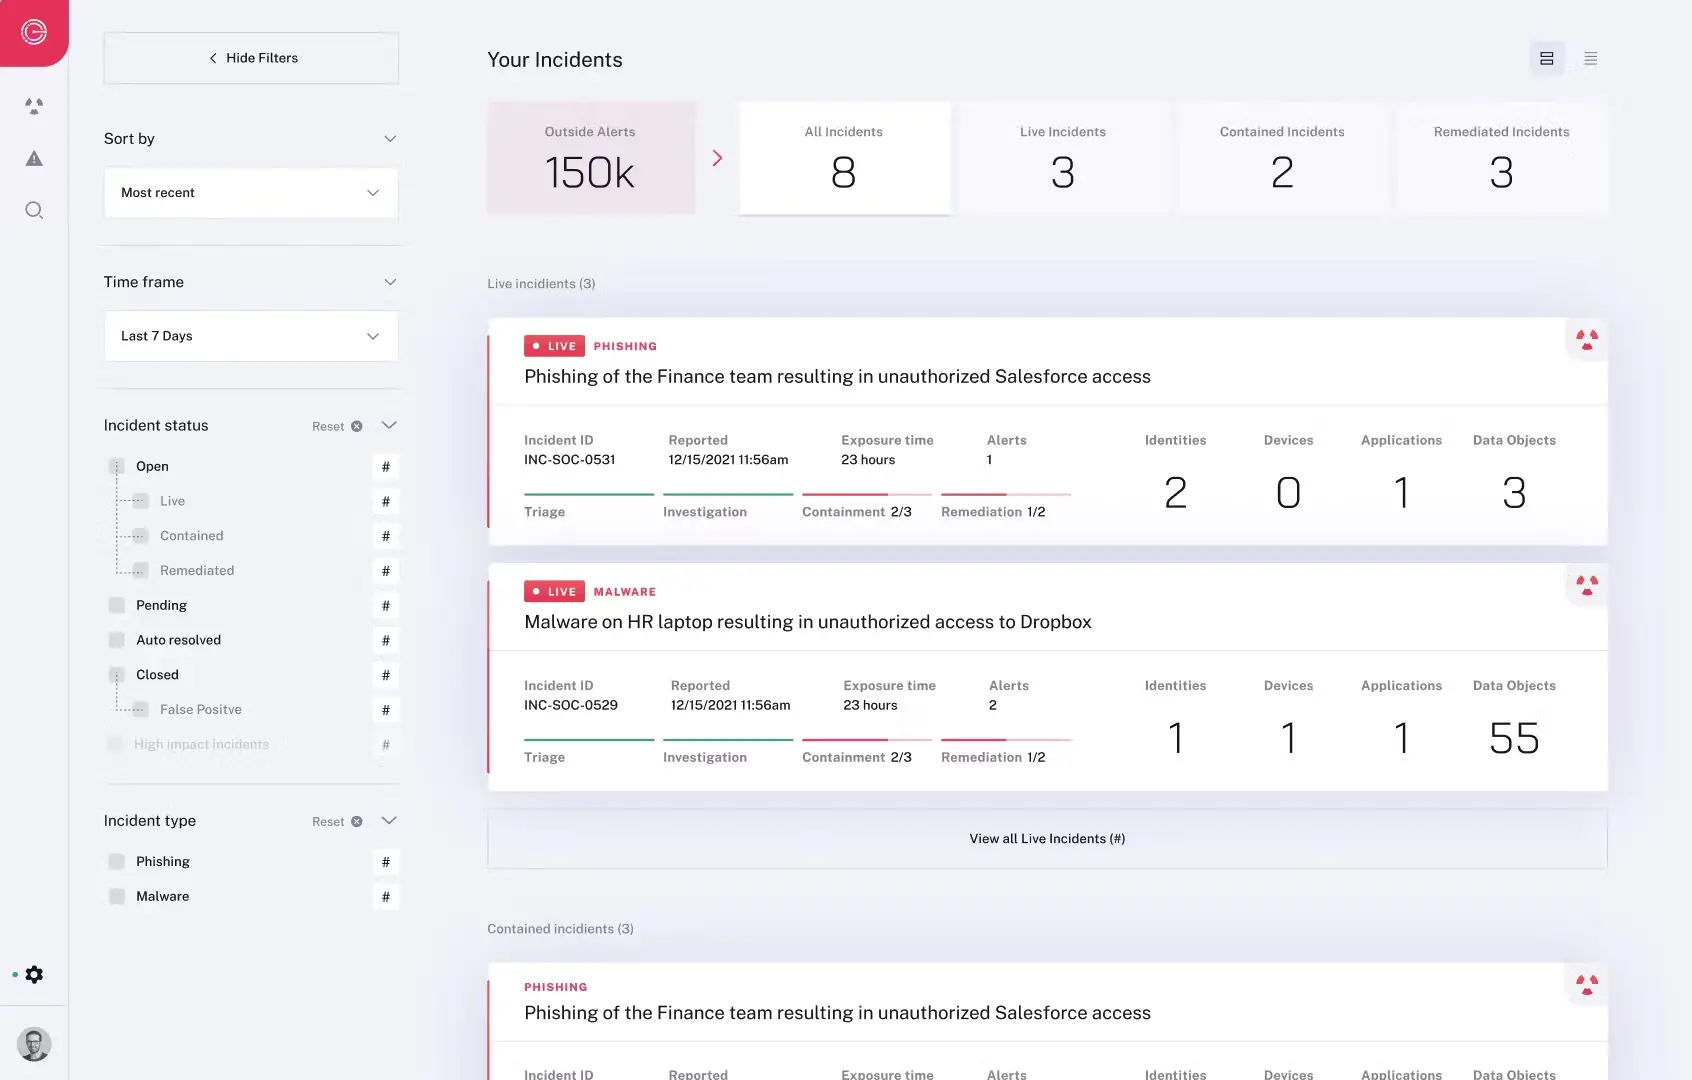
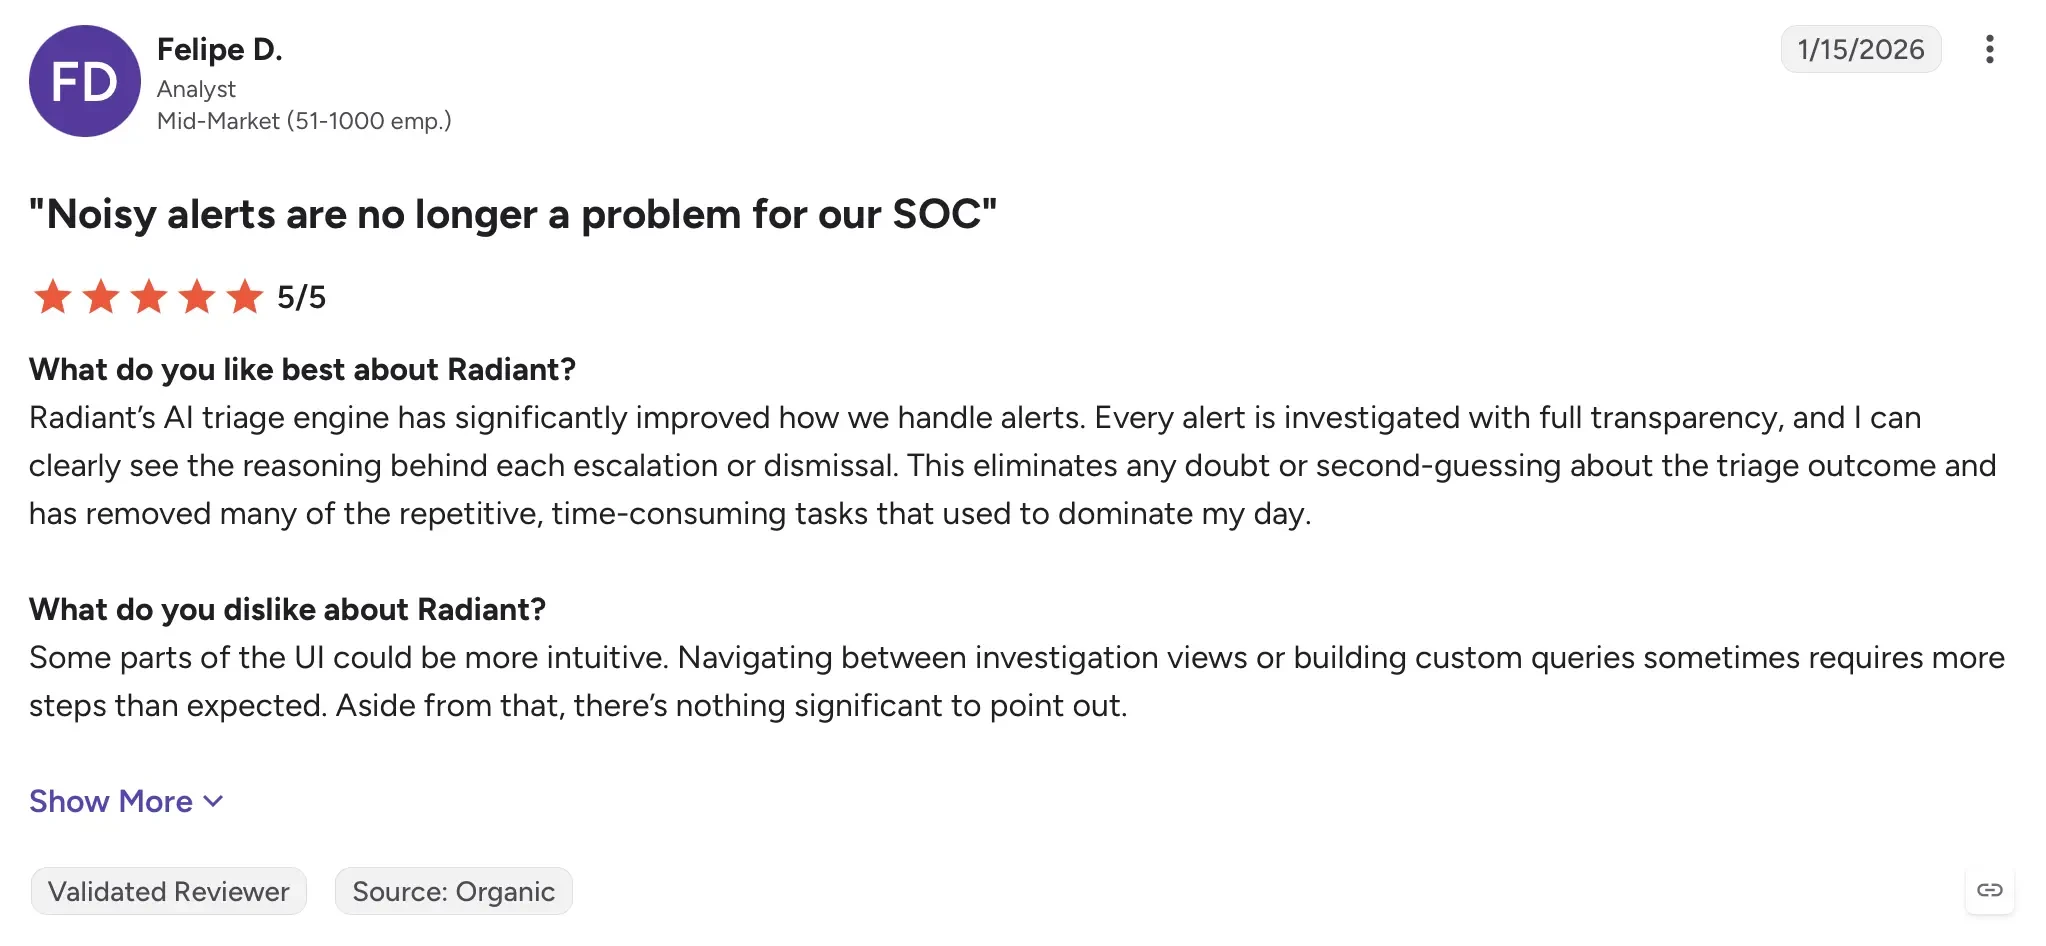
Radiant Security represents the next generation of agentic SOAR platforms. It automates incident response end-to-end, using AI reasoning to decide the right actions and execute them across integrated tools. Radiant learns from analyst feedback, improving its future decisions while maintaining transparency. It acts as an autonomous SOC teammate that closes the loop from detection to remediation.
Key features
Autonomous incident response and multi-tool orchestration
Context-aware playbook creation and execution
Reasoning engine for decision-making transparency
Continuous learning from past incidents
API integration with EDR, SIEM, and ticketing systems
Natural language query support for analyst interaction
Closed-loop response workflows for full automation
G2 rating: 5/5 (2 reviews)
Pricing: Custom pricing
Conclusion
Agentic AI is transforming cybersecurity by moving defense strategies from human-driven to human-supervised. These systems no longer just alert or suggest; they decide and act. By combining autonomous reasoning, adaptive learning, and contextual understanding, agentic AI allows security teams to scale faster than attackers can innovate.
For organizations seeking endpoint automation, Purple AI by SentinelOne and CrowdStrike Falcon Platform deliver autonomous EDR/XDR capabilities powered by natural language interaction. SOC teams battling alert fatigue will find Google SecOps and Radiant Security valuable for investigation and response automation. Network defense specialists benefit from Vectra AI’s continuous learning and autonomous threat hunting, while Cyble excels at proactive intelligence and dark web discovery. For developers and DevSecOps teams, Beagle Security stands out by applying agentic AI to continuously adaptive application security testing.
Beagle Security brings agentic intelligence to application security, a space long overdue for transformation. Its autonomous testing, adaptive learning, and API-first approach make it ideal for cloud-native teams that need continuous, self-evolving protection. It is not just automation; it is intelligence in action.
The agentic AI revolution has only begun. As models become more capable and context-aware, the line between human and machine collaboration will continue to blur. The question is no longer whether to adopt agentic AI; it is which platform will give you the autonomy and insight you need to stay ahead in 2026 and beyond.
FAQs
How does agentic AI differ from traditional AI in cybersecurity?
Traditional AI generally focuses on analyzing data, identifying patterns, classifying threats, and generating predictions or alerts. Agentic AI goes further by using contextual reasoning to plan and execute multi-step tasks. Depending on the platform, this can include investigating suspicious activity, correlating threats across systems, validating vulnerabilities, and initiating response actions.
How can agentic AI help security teams reduce alert fatigue?
Agentic AI can automate parts of the security investigation process by correlating alerts, gathering relevant information, identifying potential root causes, and prioritizing threats. This reduces the amount of repetitive analysis security analysts need to perform manually, allowing them to focus on complex investigations and higher-priority incidents.
Can agentic AI tools perform autonomous penetration testing?
Yes. Agentic AI-powered penetration testing tools can interact with applications, adapt testing strategies based on application behavior, investigate potential vulnerabilities, and validate security weaknesses. Beagle Security, for example, applies agentic AI to web application and API security testing, supporting adaptive vulnerability discovery and validation.
What should organizations consider when choosing an agentic AI cybersecurity tool?
Organizations should evaluate the tool’s primary security use case, autonomous capabilities, integration options, testing or detection coverage, reporting quality, and pricing. They should also consider how much human oversight is required, what actions the AI can perform independently, and whether the platform provides sufficient visibility into its decisions and actions.