Top ZAP alternatives and competitors [October 2026]
ZAP by Checkmarx continues to be one of the most popular open-source dynamic application security testing (DAST) tools in the world. It has long been a trusted choice for developers, security engineers, and ethical hackers thanks to its zero cost, strong community support, and wide accessibility.
That said, as modern applications evolve with APIs, microservices, and cloud-native infrastructures, the limitations in ZAP’s capabilities are becoming more evident. While ZAP is an excellent starting point, it requires significant manual configuration, struggles to detect advanced business logic vulnerabilities, and does not scale easily in enterprise CI/CD pipelines.
This is why security teams are increasingly searching for ZAP alternatives that provide more automation, scalability, and enterprise-grade features. In this guide, we will explore the best ZAP alternatives in 2026, categorized by their strengths, use cases, and pricing models. Whether you are a small development team or a global enterprise, you will find options that better suit your security maturity.
Best ZAP alternatives TL;DR
Here is a quick comparison of the top ZAP alternatives you should know about in 2026:
| Platform | Starting price | Strengths | Best for |
|---|---|---|---|
| Beagle Security | Starts at $1,188/year | Agentic AI powered DAST, developer-friendly reports | Agile teams and API-centric apps |
| Burp Suite | $499/user/year | Manual PT, deep control | Pen-test experts and detailed assessments |
| OpenVAS | Free / Open source | Broad VM scope, free | Budget-conscious users and VM scanning |
| Tenable WAS | $7,434/year (5 FQDNs) | Risk-based prioritization, vuln intelligence | Enterprises focused on exposure management |
| Rapid7 InsightAppSec | $175/month/app | DAST with lightweight IAST | Rapid7 Insight platform users |
| Qualys WAS | ~$1,995/year for 25 web apps | VMDR integration, asset visibility | Qualys cloud customers |
| HCL AppScan | $299/scan | Full AppSec suite, AI-driven accuracy | Enterprises needing on-prem and cloud support |
| Veracode | Custom quote | Full-spectrum AppSec (SAST, DAST, IAST) | Large enterprises with long-term AppSec plans |
| Checkmarx | Custom quote | Unified AppSec platform (SAST, DAST, SCA) | Organizations needing enterprise AppSec stack |
| Invicti Web + API (formerly Acunetix) | Custom quote | Automated web and API scanning | SMBs and teams needing ease of use |
Beagle Security
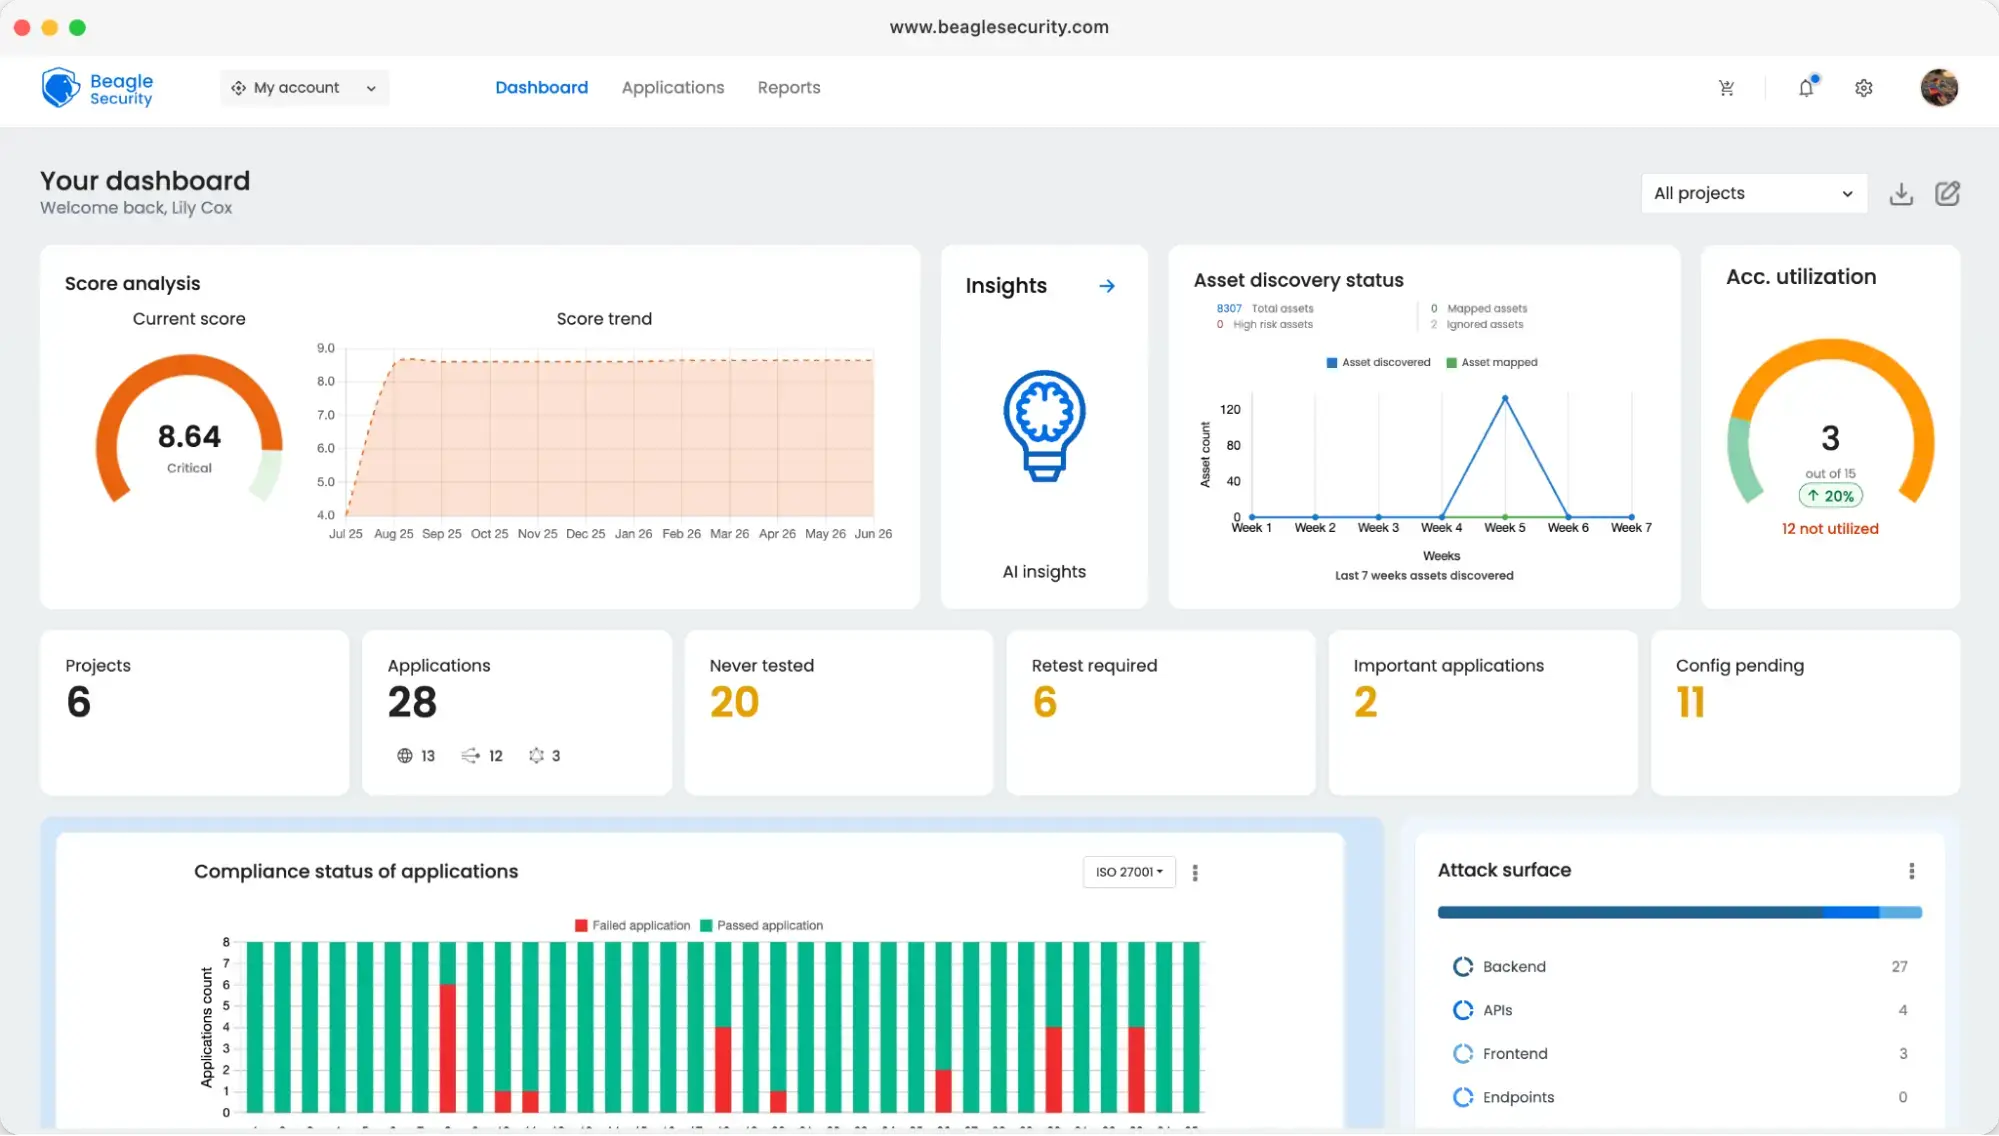
Beagle Security stands out as one of the best ZAP alternatives in 2026, particularly for modern development teams that rely on agile methodologies and rapid deployment cycles. Unlike ZAP, which leans heavily on manual setup and configuration, Beagle Security uses an agentic AI powered testing engine that simulates real-world attacker behavior with significantly less effort.
Beagle Security key features
Agentic AI penetration testing with advanced vulnerability coverage: This engine intelligently detects vulnerabilities that traditional scanners may miss, including complex web application logic flaws.
Business logic vulnerability detection with 2FA and authentication handling: Beagle Security can navigate login workflows, two-factor authentication, and multi-step processes that often challenge traditional scanners.
Full API security for REST and GraphQL endpoints: Many modern applications rely heavily on APIs, and Beagle Security covers these endpoints extensively.
Contextual, developer-friendly reports with clear remediation steps: Reports are designed to be actionable, helping developers fix issues quickly rather than simply listing vulnerabilities.
Seamless CI/CD pipeline integration: Security testing is automated within development workflows, reducing friction and supporting continuous security in agile practices.
Application discovery and prioritization of testing targets: Beagle Security can automatically identify the most critical areas to scan, improving efficiency and reducing unnecessary load.
Beagle Security pricing
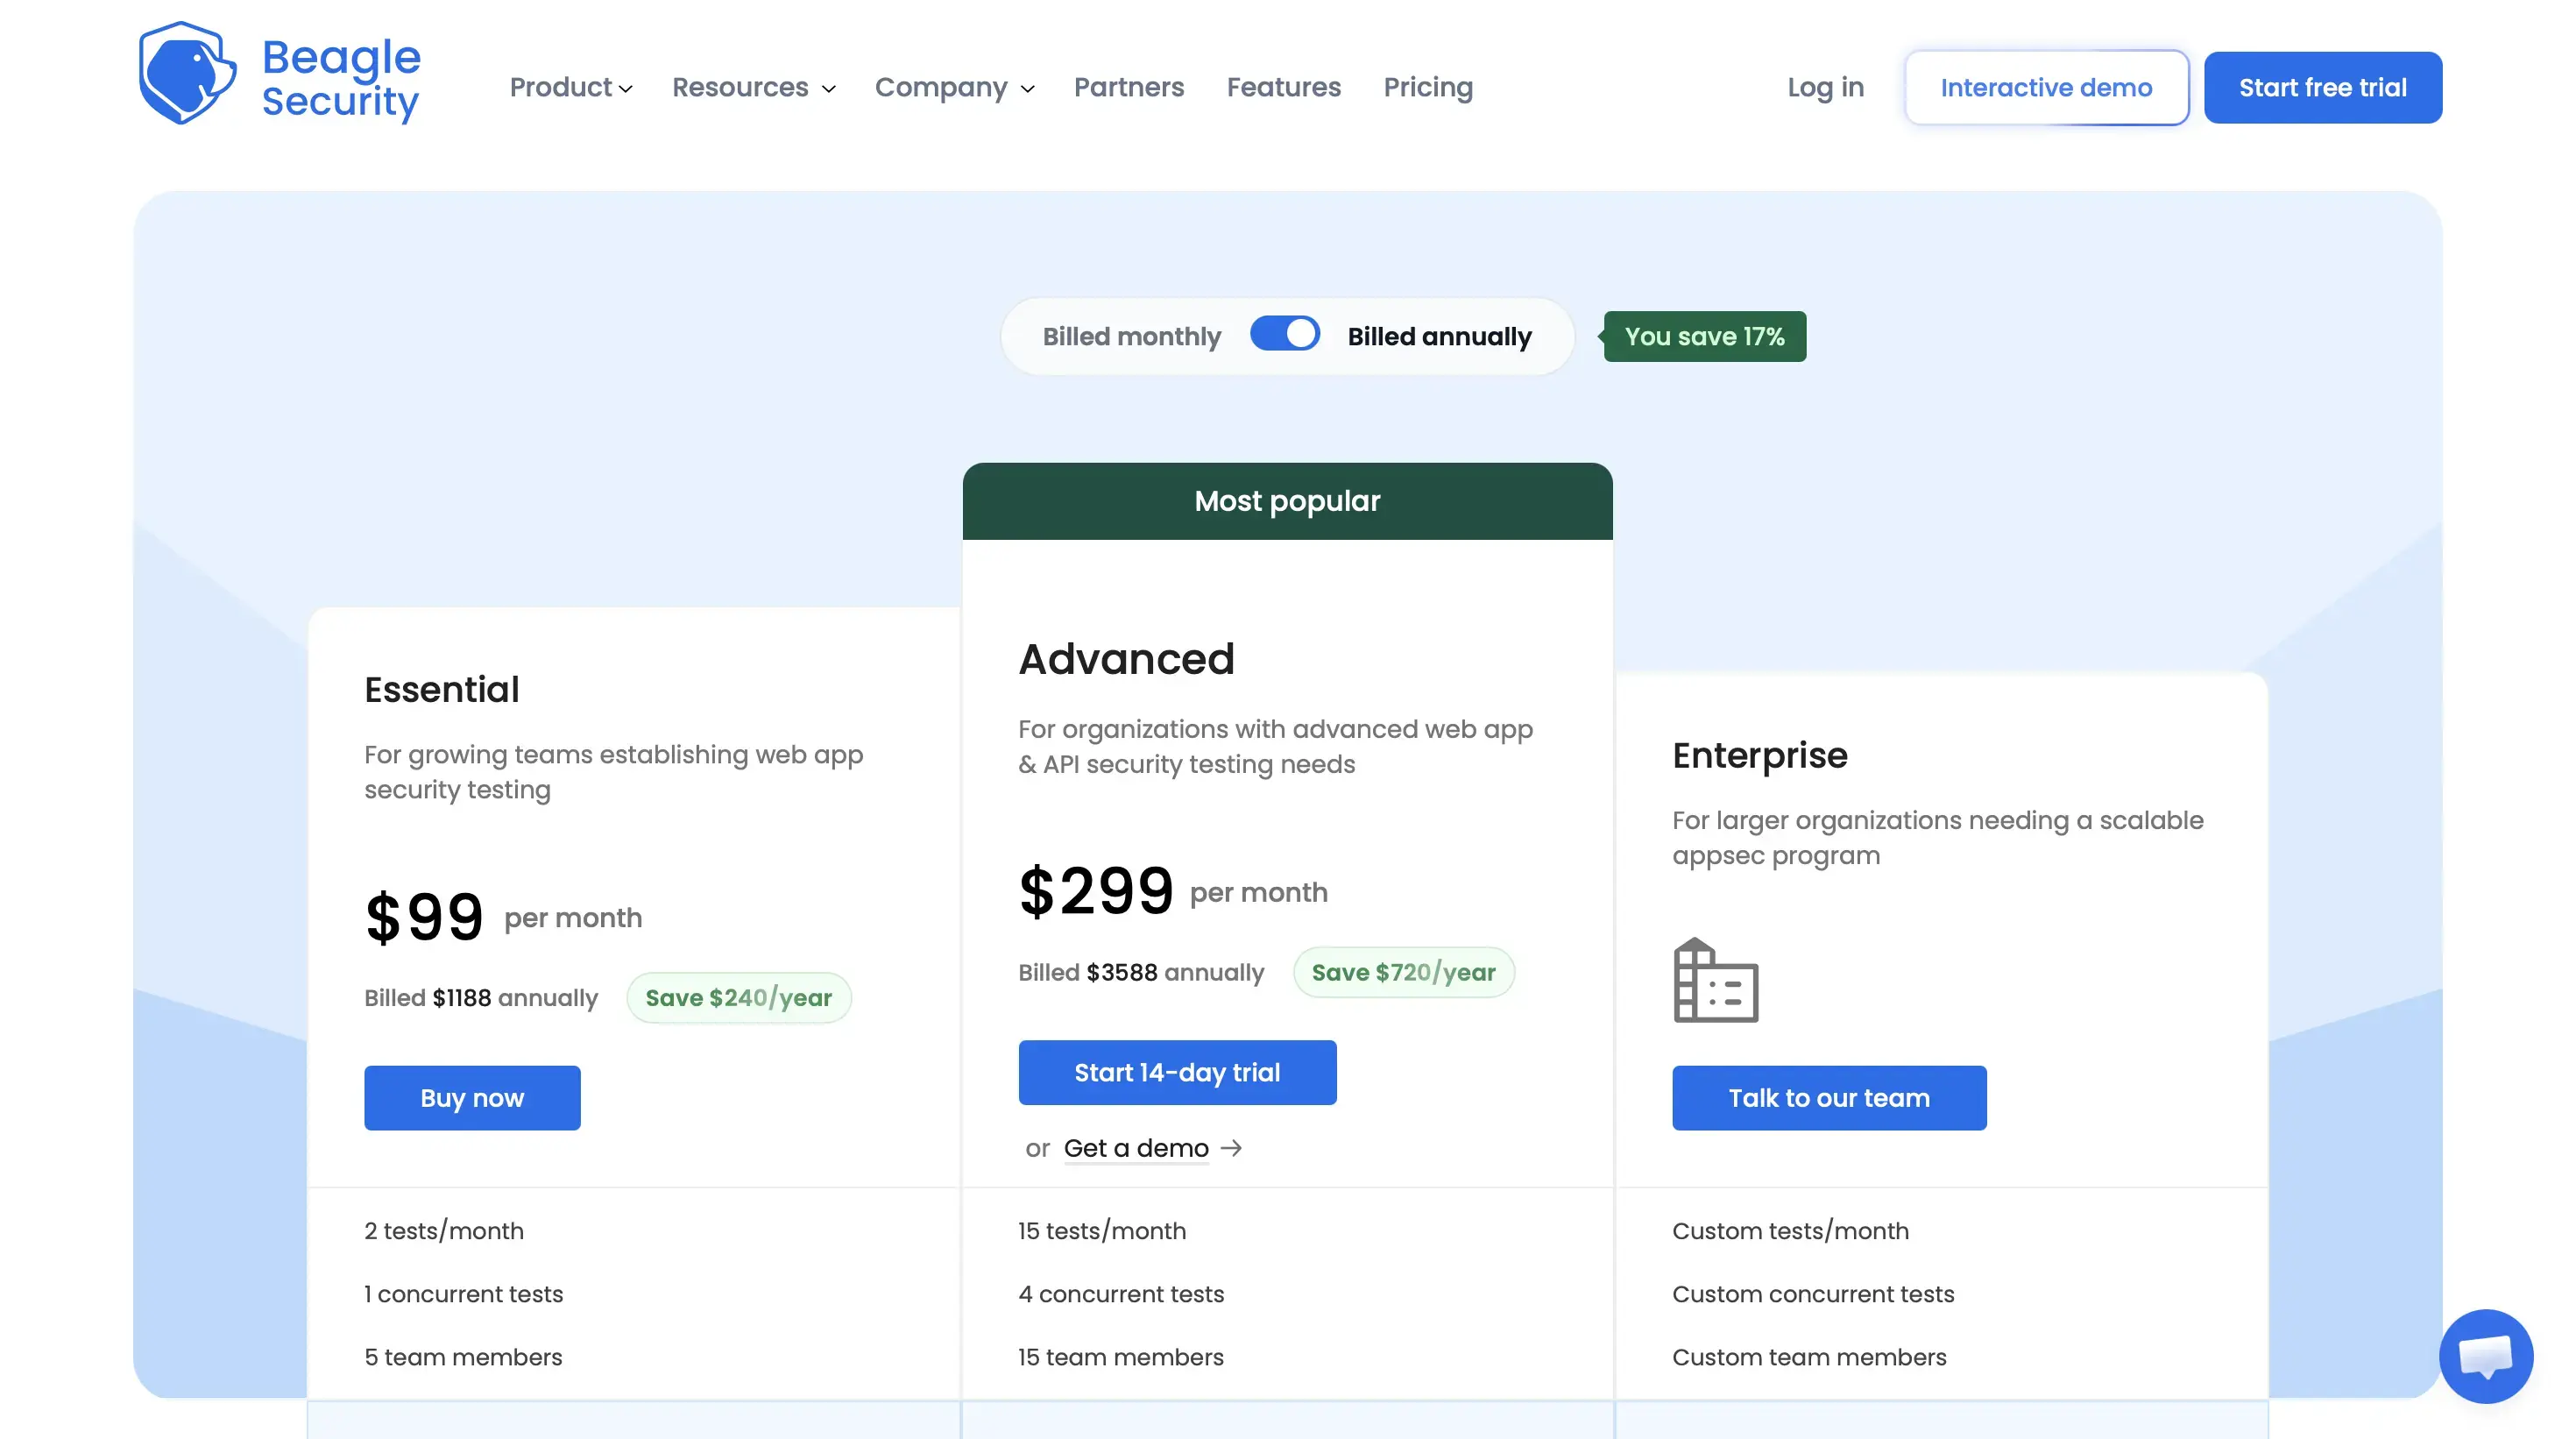
Essential: $1,188/year (2 tests per month)
Advanced: $4,308/year
Enterprise: Starting at $6,850/year
Beagle Security ratings & reviews
Source: G2
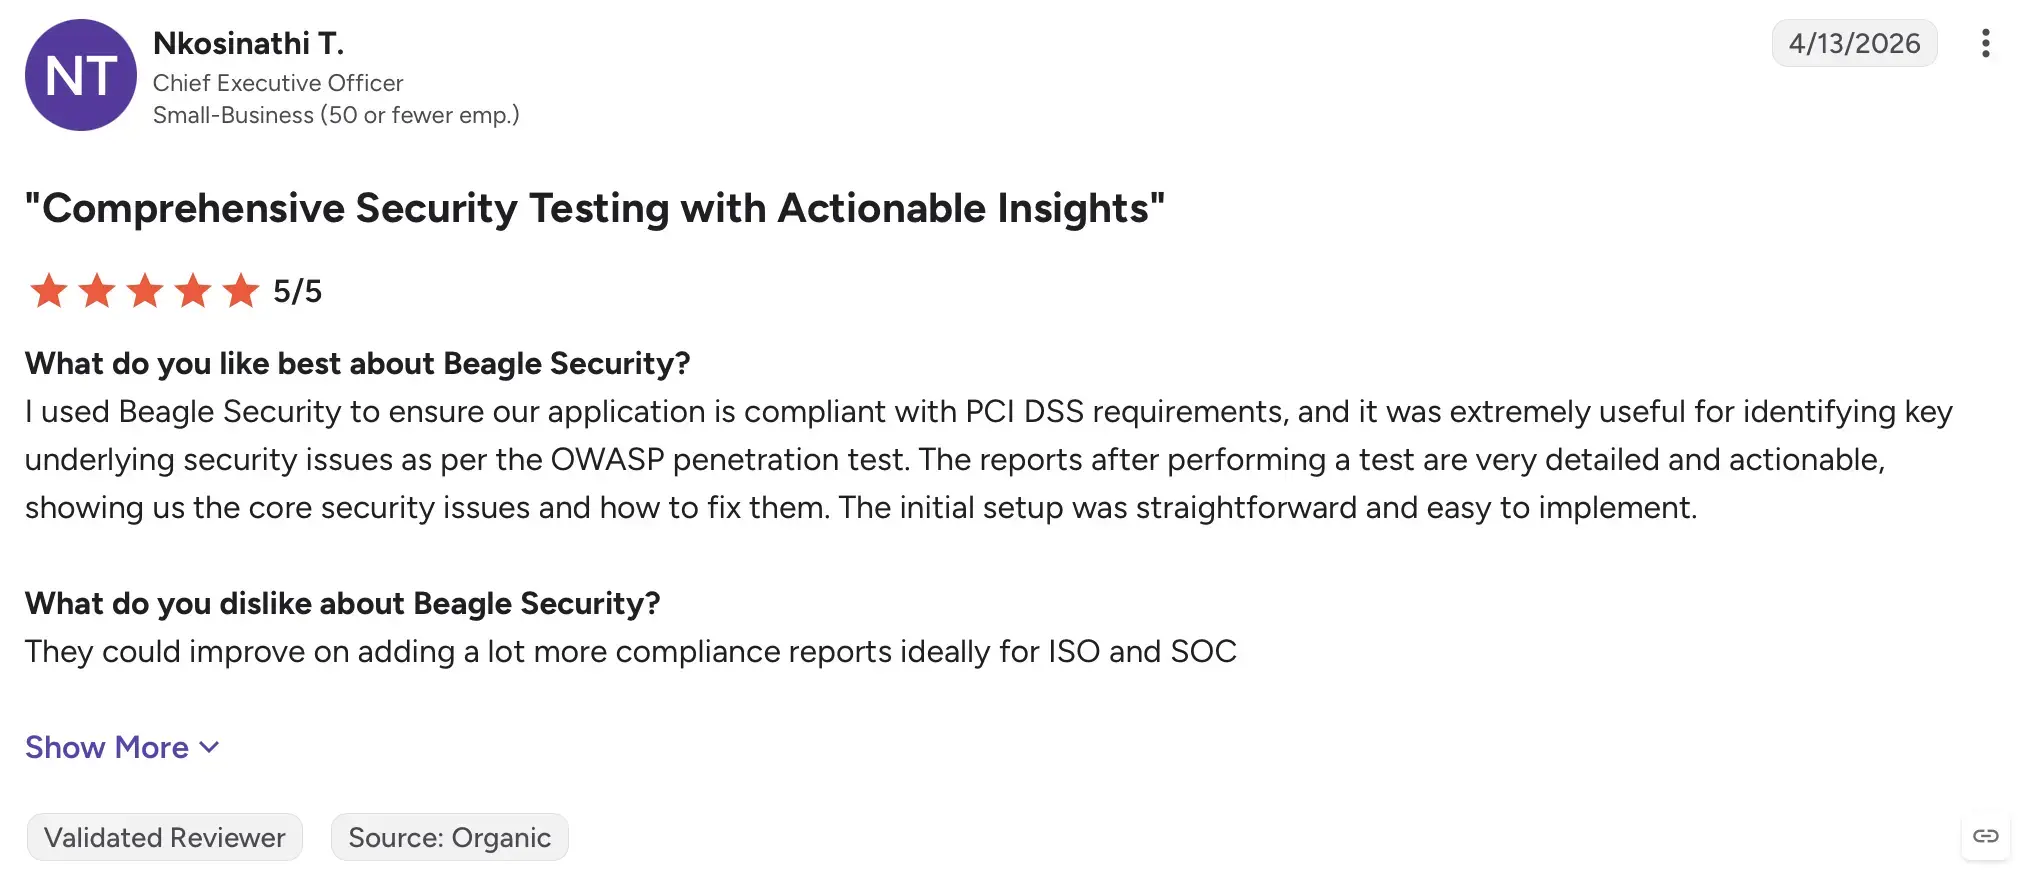
Beagle Security holds a 4.7/5 rating on G2. Users praise its intuitive interface, actionable developer reports, and AI-powered engine, highlighting its suitability for teams needing scalable, automated security in CI/CD pipelines. Its combination of automation, deep API coverage, and developer-friendly reporting makes it a strong alternative to ZAP for modern development teams.
Burp Suite Professional
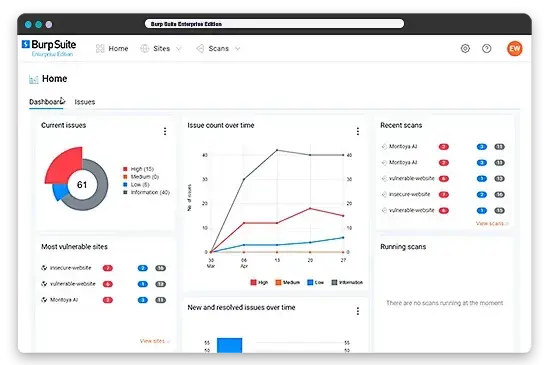
When it comes to manual penetration testing, Burp Suite remains the gold standard. While ZAP provides basic manual testing features, Burp’s professional suite gives penetration testers and ethical hackers a far richer toolbox.
Burp Suite Professional key features
Advanced manual testing modules such as Intruder, Repeater, Sequencer, and Decoder, which allow precise attack simulation and testing of web application vulnerabilities.
Low false-positive vulnerability scanner, providing accurate results that reduce time wasted on non-issues.
BApp Store with hundreds of extensions, allowing customization and extended functionality.
Smart crawling for JavaScript-heavy single-page applications (SPAs), which can be challenging to scan with basic tools.
Sophisticated authentication handling with macros, enabling testing of protected areas and complex workflows.
Professional-grade reporting and collaboration features for sharing findings with development and security teams.
Burp Suite Professional pricing
Professional: $499 per user/year
Enterprise edition: Custom pricing
Burp Suite Professional ratings & reviews
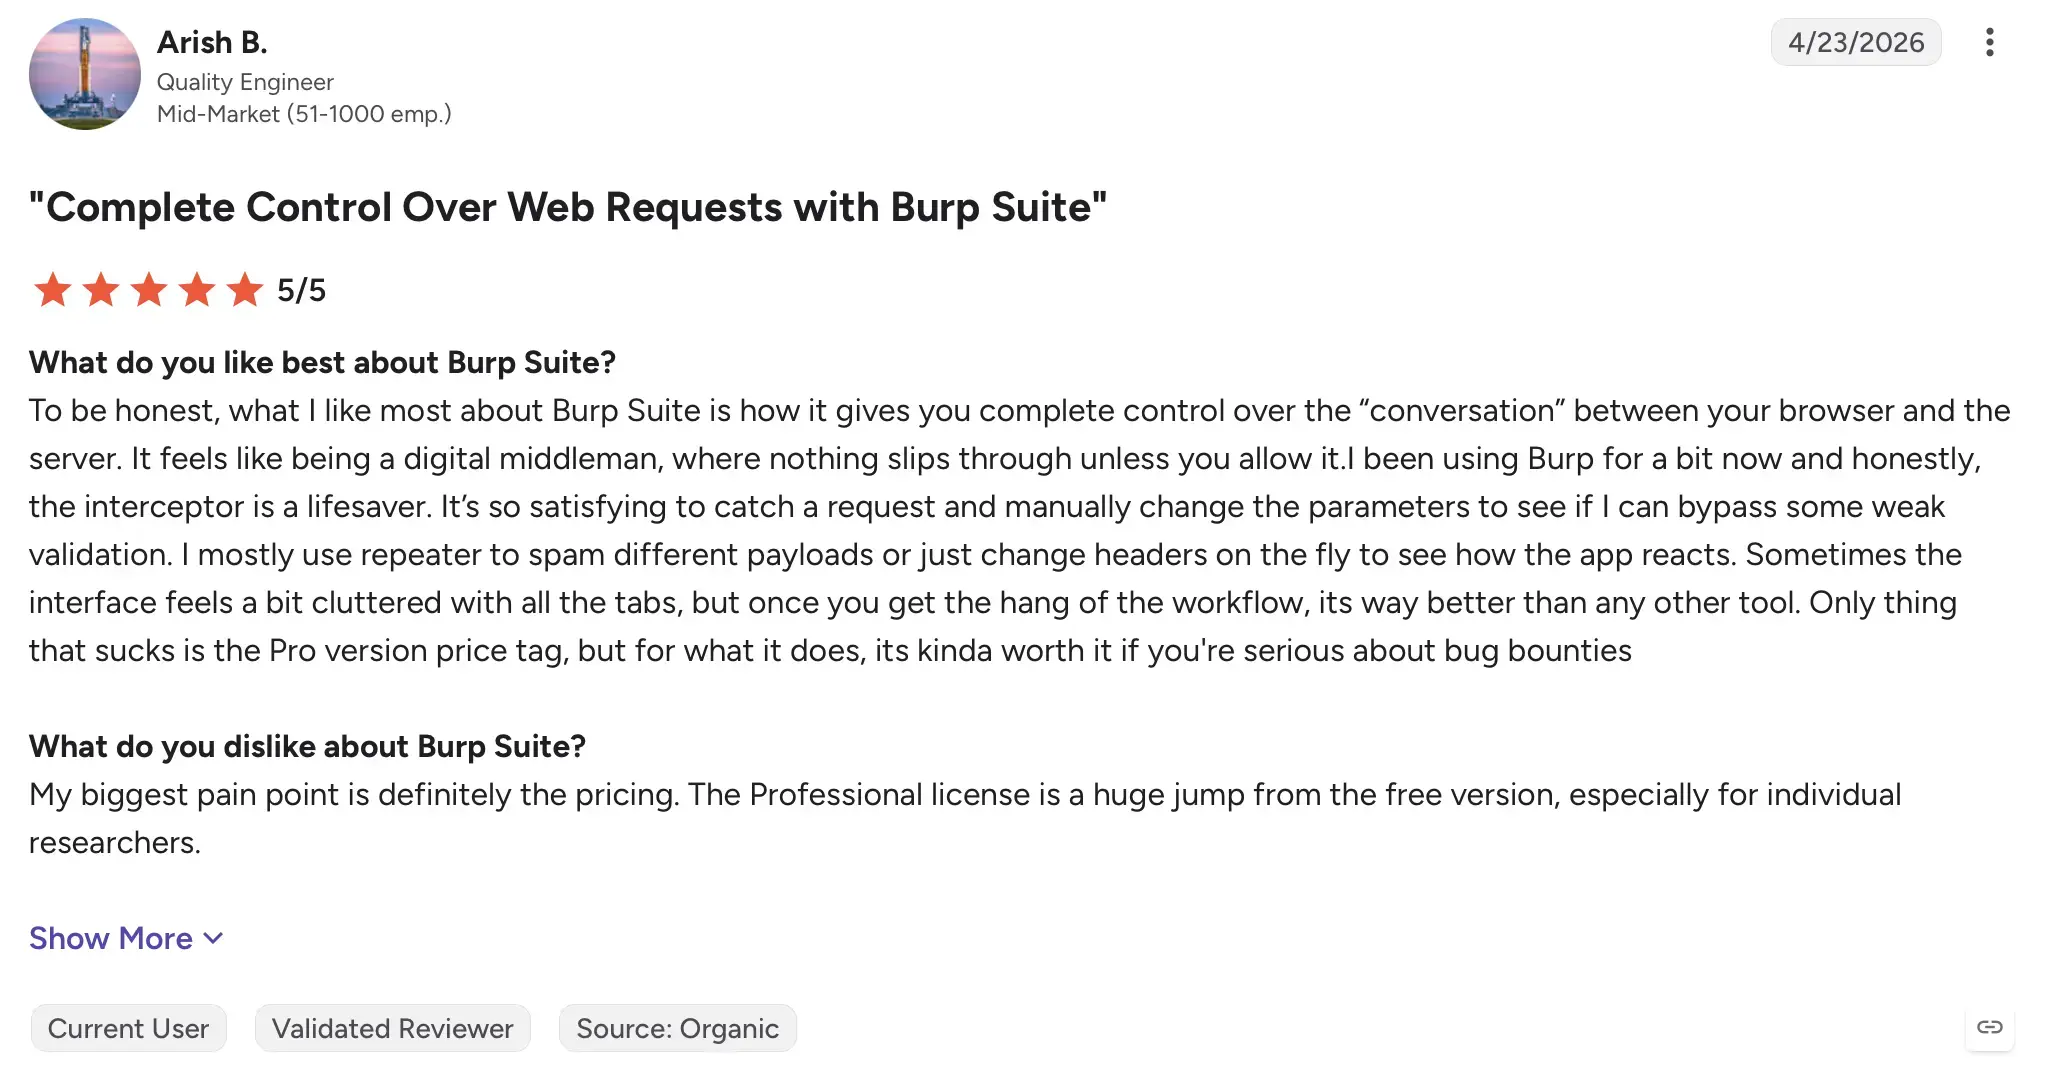
Source: G2
Burp is consistently rated highly with an overall rating of 4.8/5 , with testers noting its powerful feature set and accuracy. The main drawback is its learning curve, but for seasoned professionals, it is among the top ZAP alternatives for manual testing.
OpenVAS
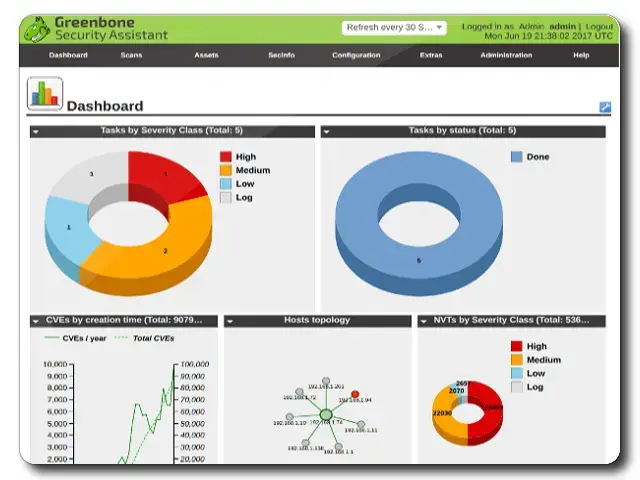
OpenVAS is a free, open-source vulnerability scanner that provides broad coverage for network and infrastructure security testing. It stands out as a cost-effective alternative to Tenable Nessus, offering strong community-driven updates and flexibility for organizations with budget constraints.
OpenVAS key features
Over 80,000 network vulnerability tests (NVTs) covering a wide range of known vulnerabilities.
Authenticated scanning for systems and applications, allowing more in-depth analysis.
Network and infrastructure vulnerability scanning, providing broader coverage beyond web applications.
Compliance checks and policy management to support regulatory requirements.
REST API for automation, allowing integration with existing workflows.
Docker deployment support for simplified installation and management.
OpenVAS pricing
Free and open-source, with commercial support available via Greenbone at lower costs than many commercial DAST solutions.
OpenVAS ratings & reviews
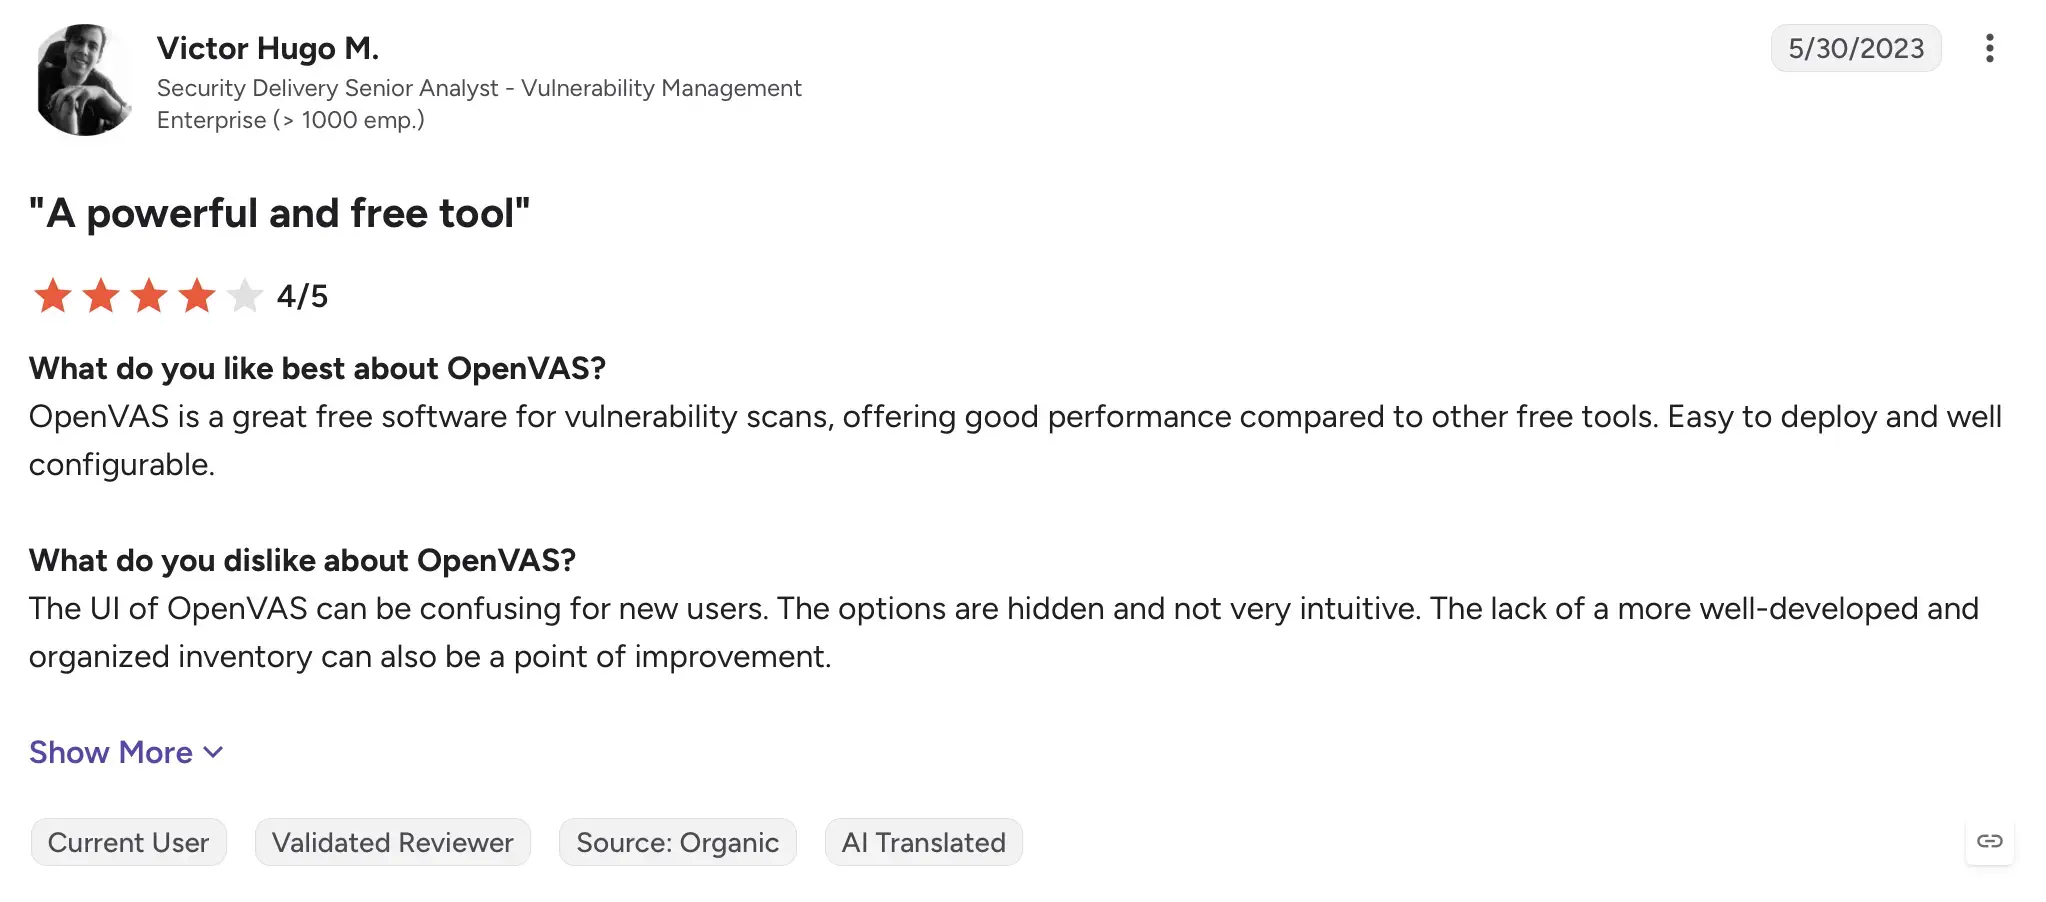
Source: G2
While powerful and free, OpenVAS requires significant technical expertise to set up and maintain. With a rating of 4.4/5 , it is a best ZAP alternative in 2026 for teams that need budget-conscious security coverage. It is praised for being open-source and reliable for vulnerability scanning. Users note that it is highly customizable and a solid free option, though sometimes challenging to configure.
Tenable WAS
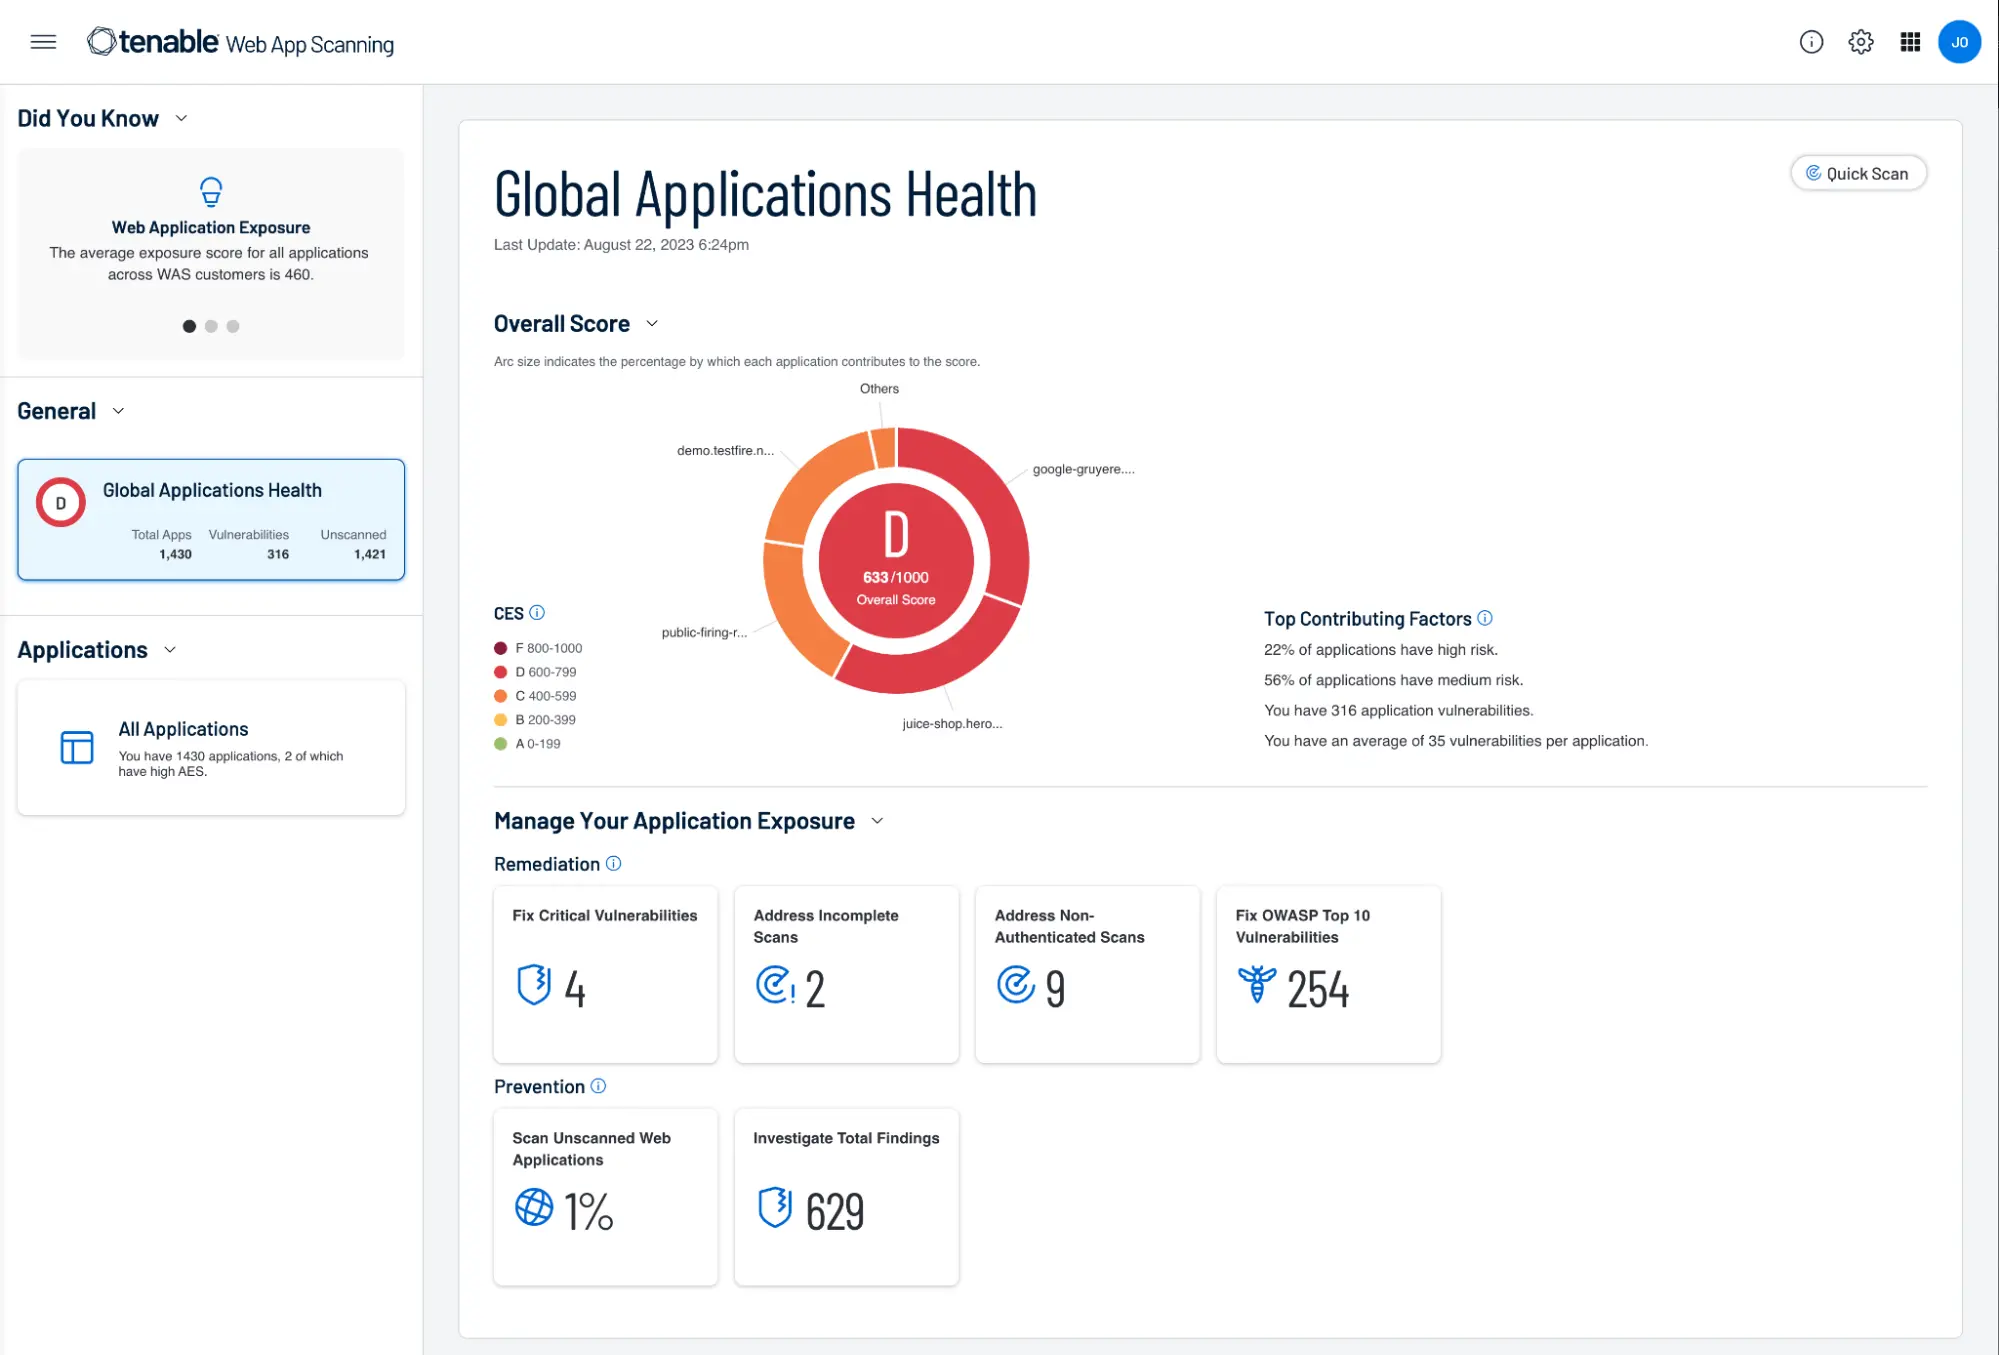
Tenable Web App Scanning (WAS) integrates deeply with the broader Tenable ecosystem, offering enterprises unified vulnerability management and risk assessment capabilities. Compared to ZAP, it provides risk-based prioritization and enhanced scalability, making it suitable for large organizations with multiple web applications.
Tenable WAS key features
Tenable VPR scoring for risk-based vulnerability prioritization.
Integration with Tenable.io for unified asset management across the organization.
Compliance-ready reporting covering PCI DSS, SOC 2, and other standards.
Integration with threat intelligence feeds to enhance detection accuracy.
Executive dashboards providing high-level risk visibility for decision-makers.
Tenable WAS pricing
Starts at $7,434/year(5 FQDNs)
Tenable WAS ratings & reviews
Source: Gartner
Tenable WAS scores a 4.6/5 rating on Gartner. Users like its strong vulnerability detection and accurate results. Many appreciate how it integrates smoothly with other Tenable products for broader security management.
Rapid7 InsightAppSec
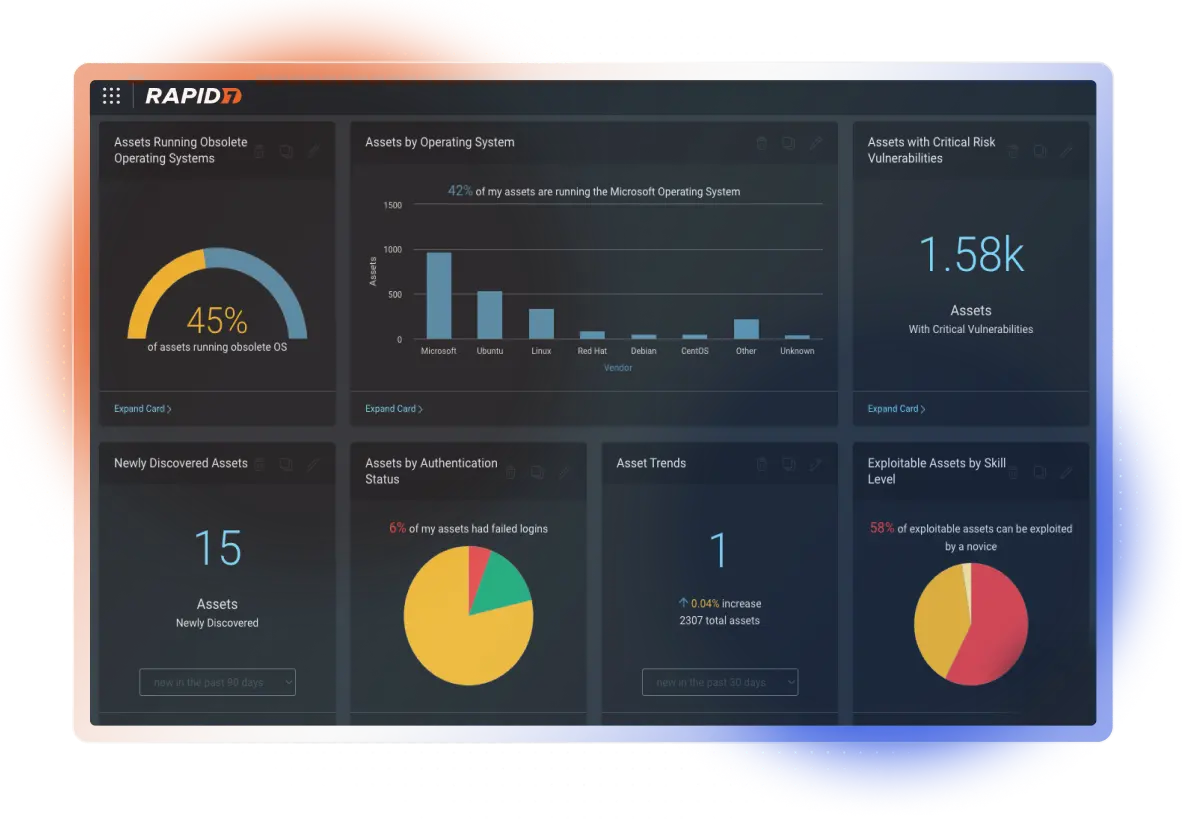
Rapid7 is a leading cybersecurity platform that combines vulnerability management, application security, and threat detection in a unified suite. It is often seen as a strong alternative to Tenable for organizations that want both depth of coverage and streamlined operations.
What makes Rapid7 stand out is its Insight platform, which delivers real-time analytics, automated remediation, and integrations with DevOps pipelines. This makes it particularly effective for teams that want to move beyond traditional scanning and adopt a more proactive approach to security.
Rapid7 InsightAppSec key features
DAST with lightweight IAST through agent-based scanning, enabling continuous security assessment.
Integration with tools like Jenkins and Azure DevOps for automated testing in CI/CD workflows.
Visual dashboards and compliance reporting for efficient risk prioritization.
Blackout scheduling to prevent testing during peak usage periods.
API security testing for modern application architectures.
Rapid7 InsightAppSec pricing
$175 per app/month (billed annually)
Rapid7 InsightAppSec ratings & reviews
Source: Gartner
With a 4.3/5 rating on Gartner, Rapid7 InsightAppSec is often praised for its ease of use and the detailed insights it provides. Security teams mention that the dashboard is intuitive and makes vulnerability prioritization much easier.
Qualys WAS
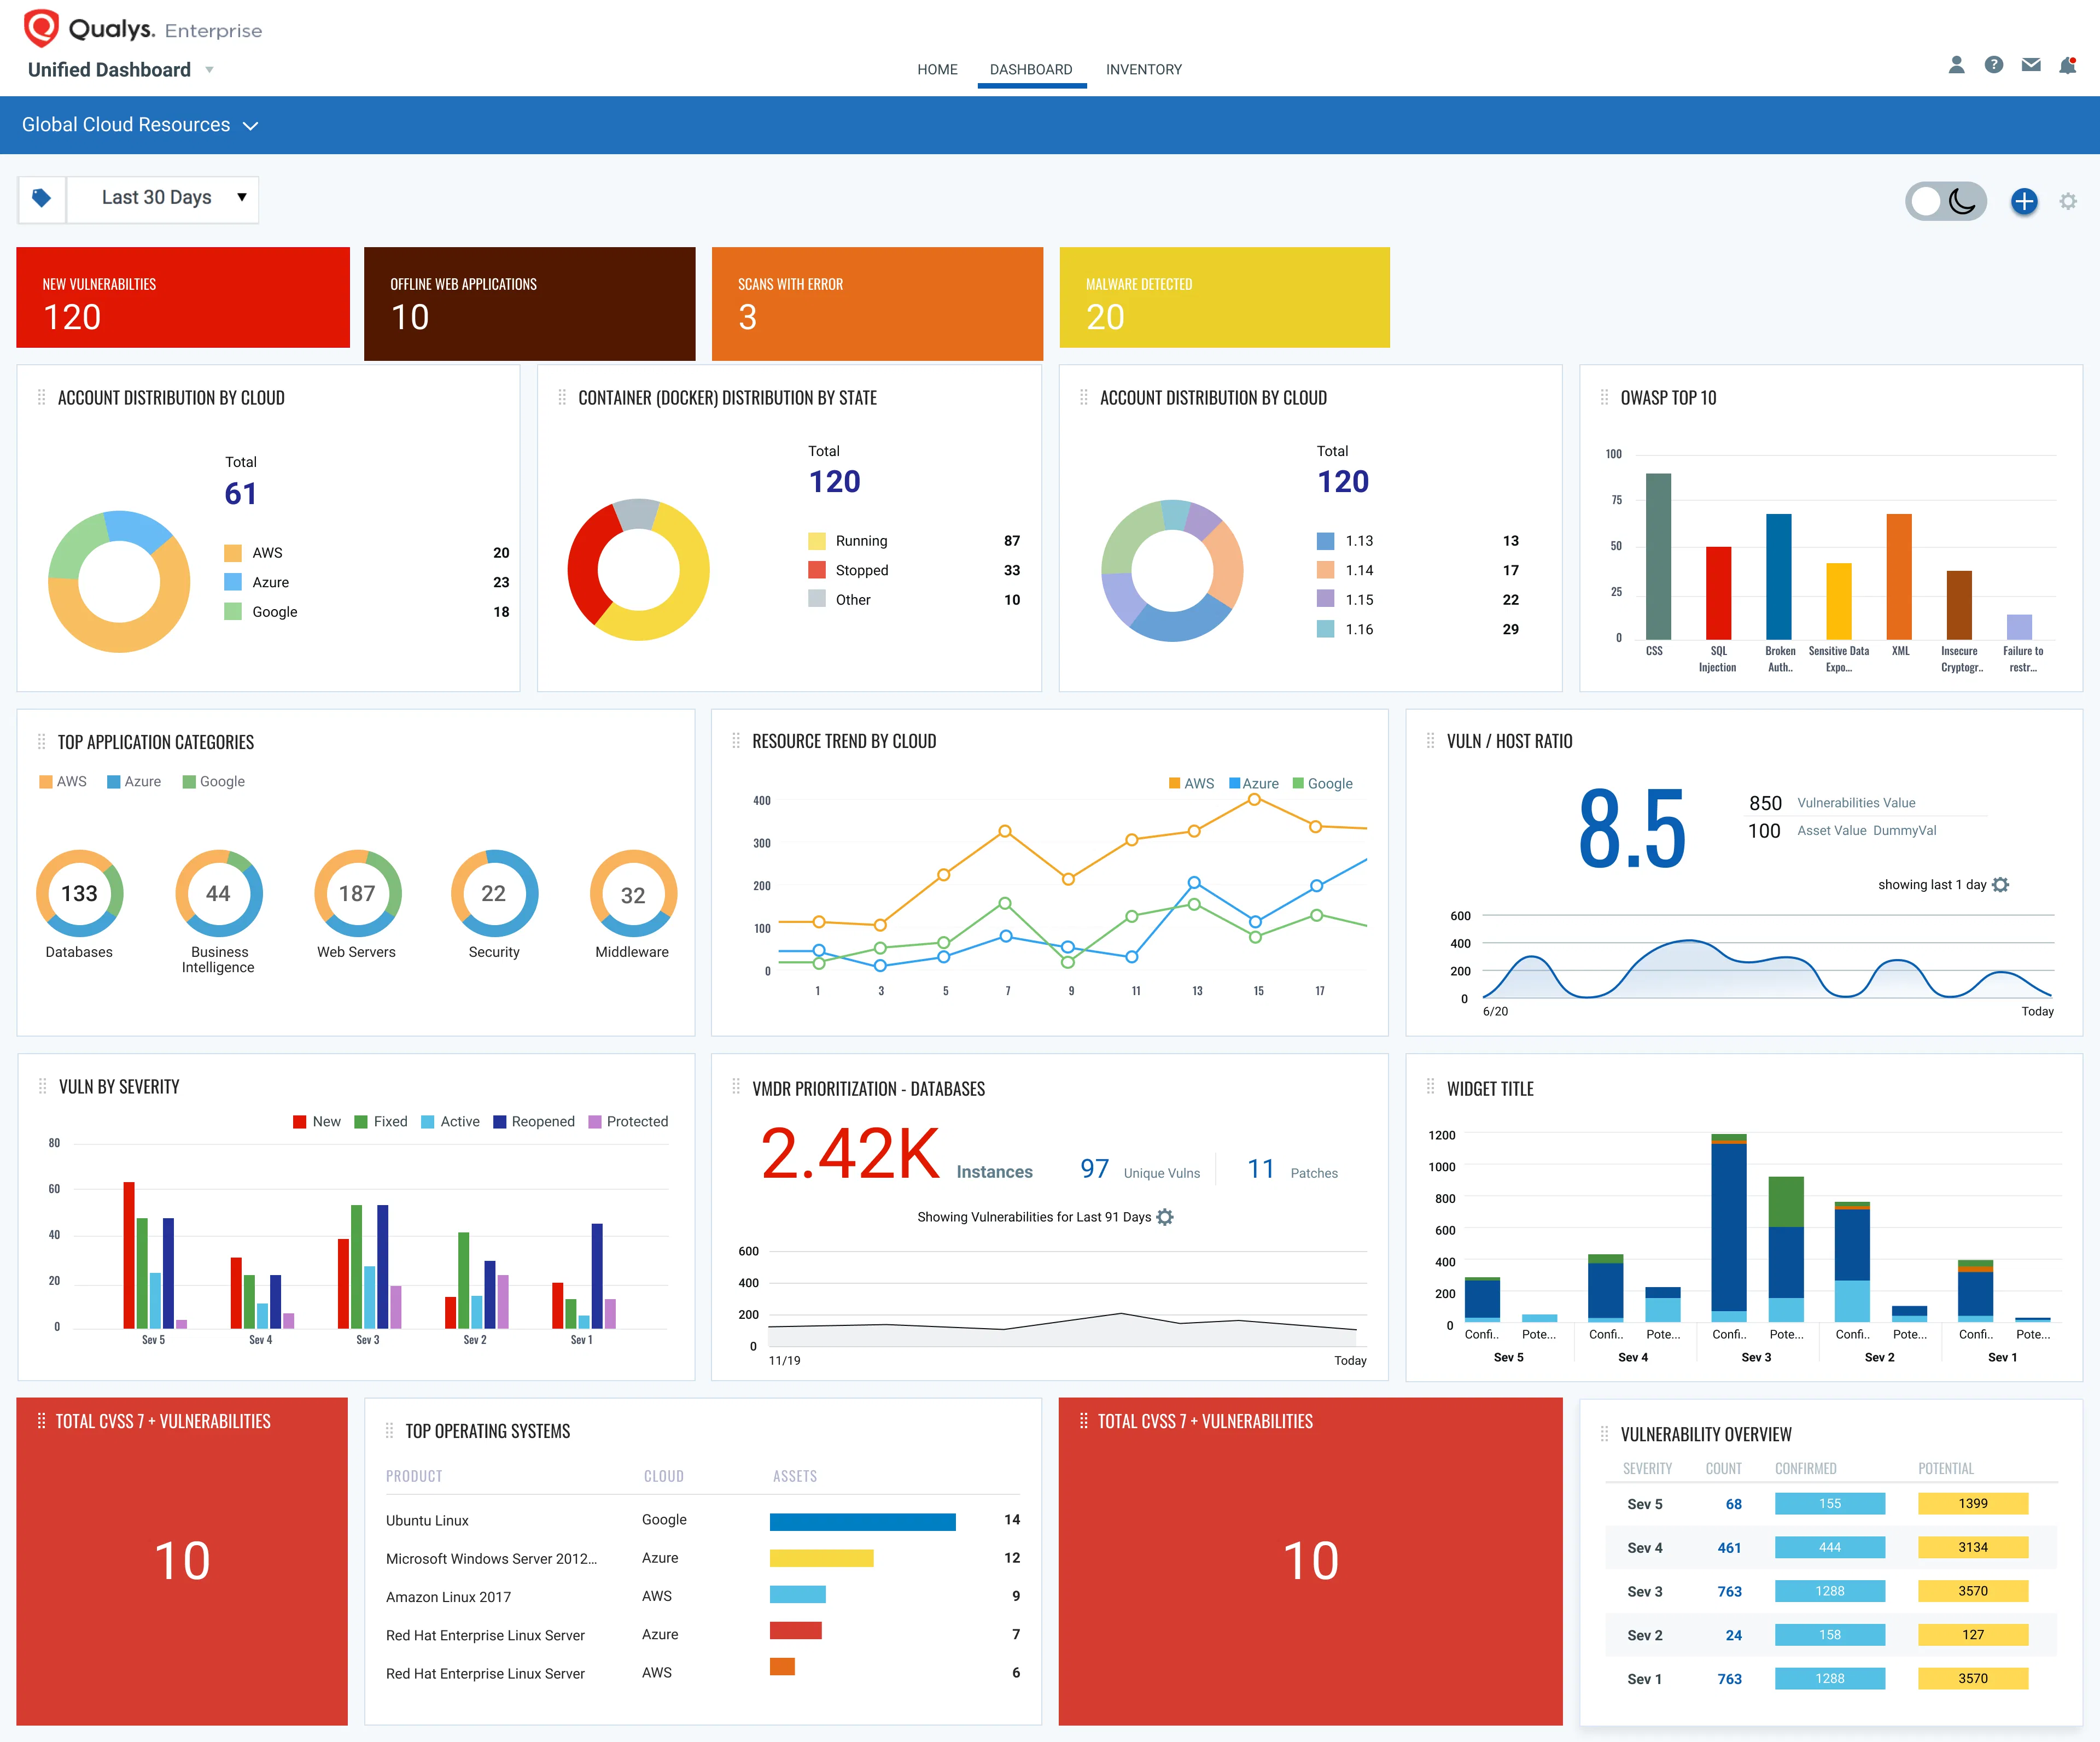
Qualys is one of the longest-standing players in vulnerability management, known for its cloud-native approach to scanning and compliance. Many enterprises use it as a scalable alternative to Tenable because of its broad coverage across assets, applications, and configurations.
Its strength lies in continuous monitoring, automated patch tracking, and extensive compliance reporting. This makes Qualys particularly valuable for organizations in regulated industries that need both visibility and audit-ready reporting.
Qualys WAS key features
OWASP Top 10 and CWE Top 25 coverage for web applications.
Automated scanning for APIs and SPAs, covering modern web app architectures.
Compliance reporting for industry standards and audit readiness.
Cloud-based global scanning infrastructure.
Integration with Qualys VMDR for vulnerability management and remediation.
Qualys WAS pricing
Starting at $1,995/year for 25 apps
Qualys WAS ratings & reviews
Source: G2
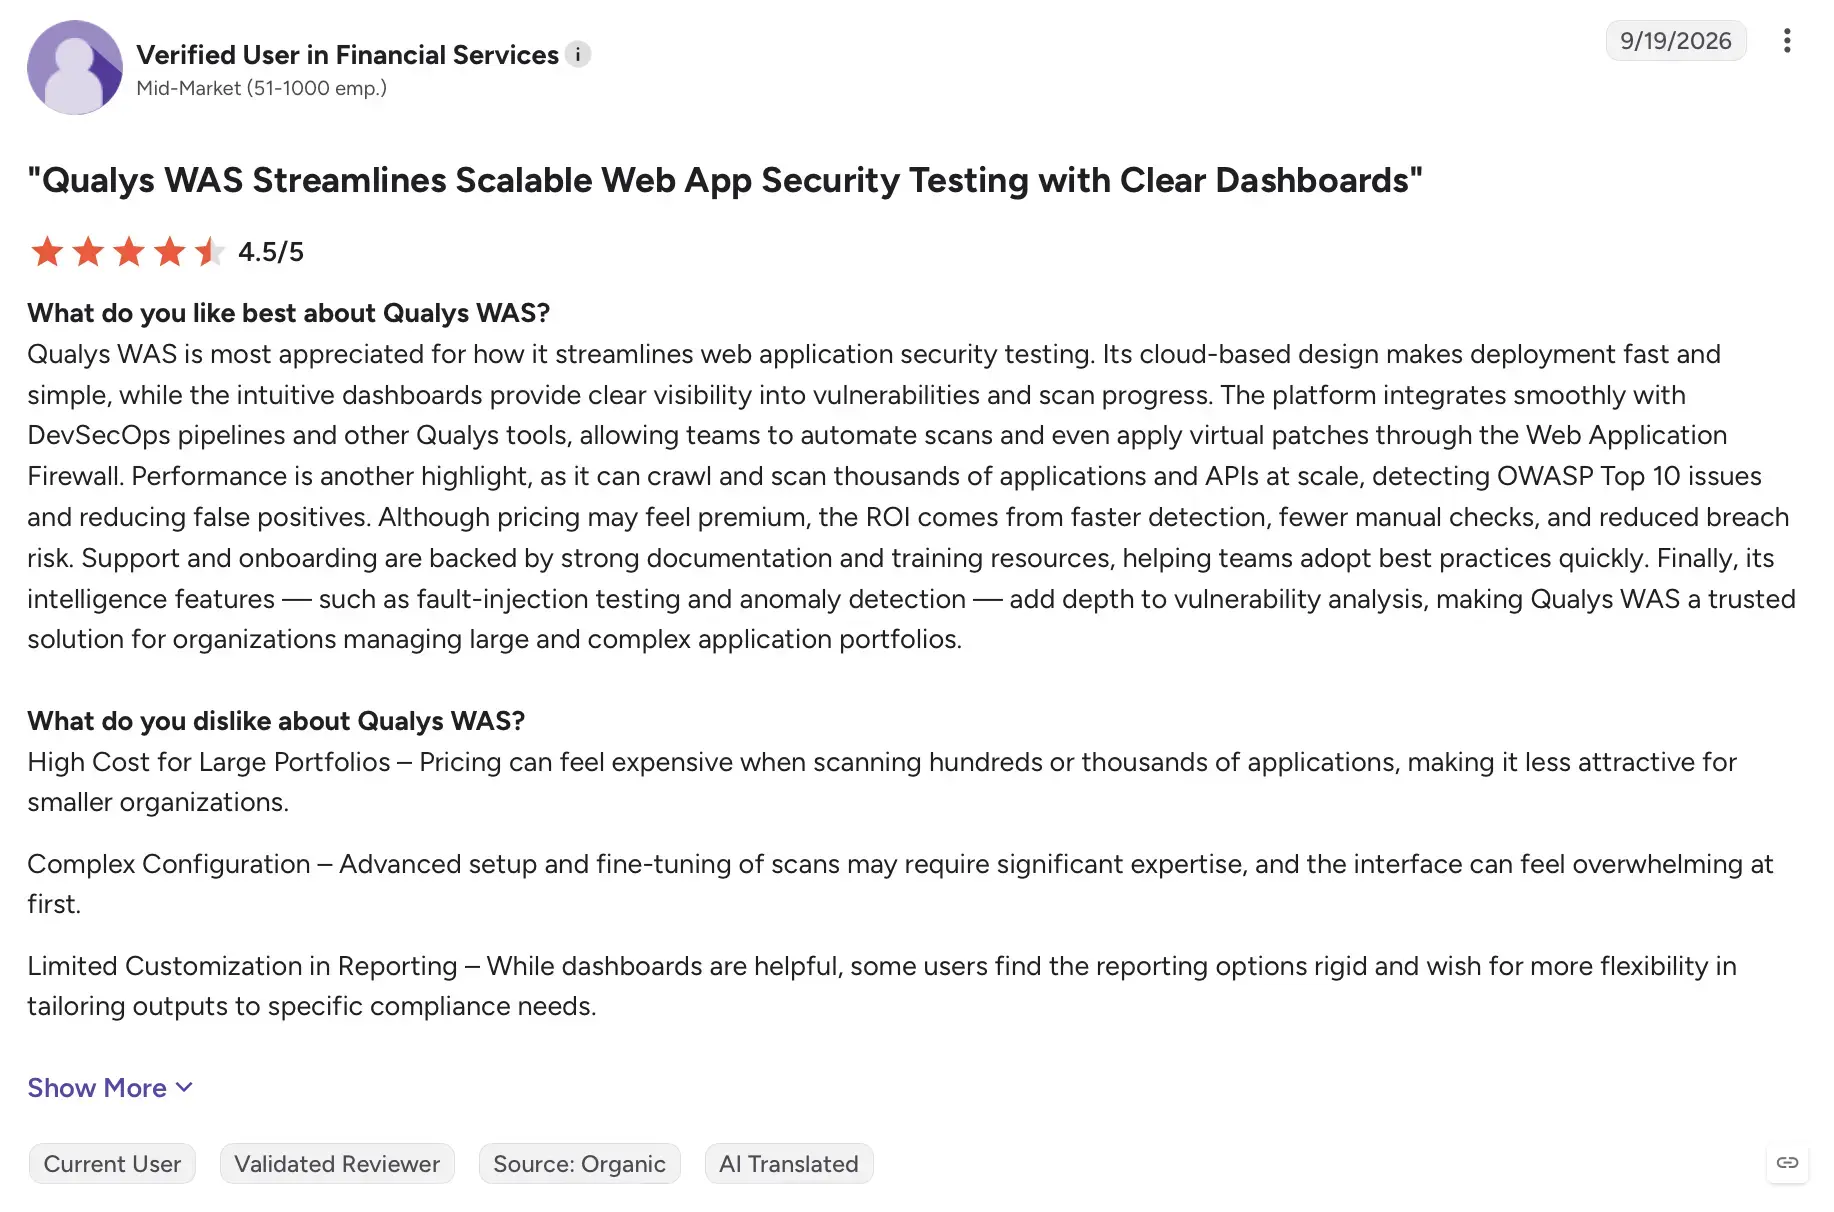
Qualys WAS carries a 4.5/5 rating on G2. Reviewers point out its scalability and ability to handle large enterprise-level needs. The compliance reporting features also receive frequent positive mentions.
HCL AppScan
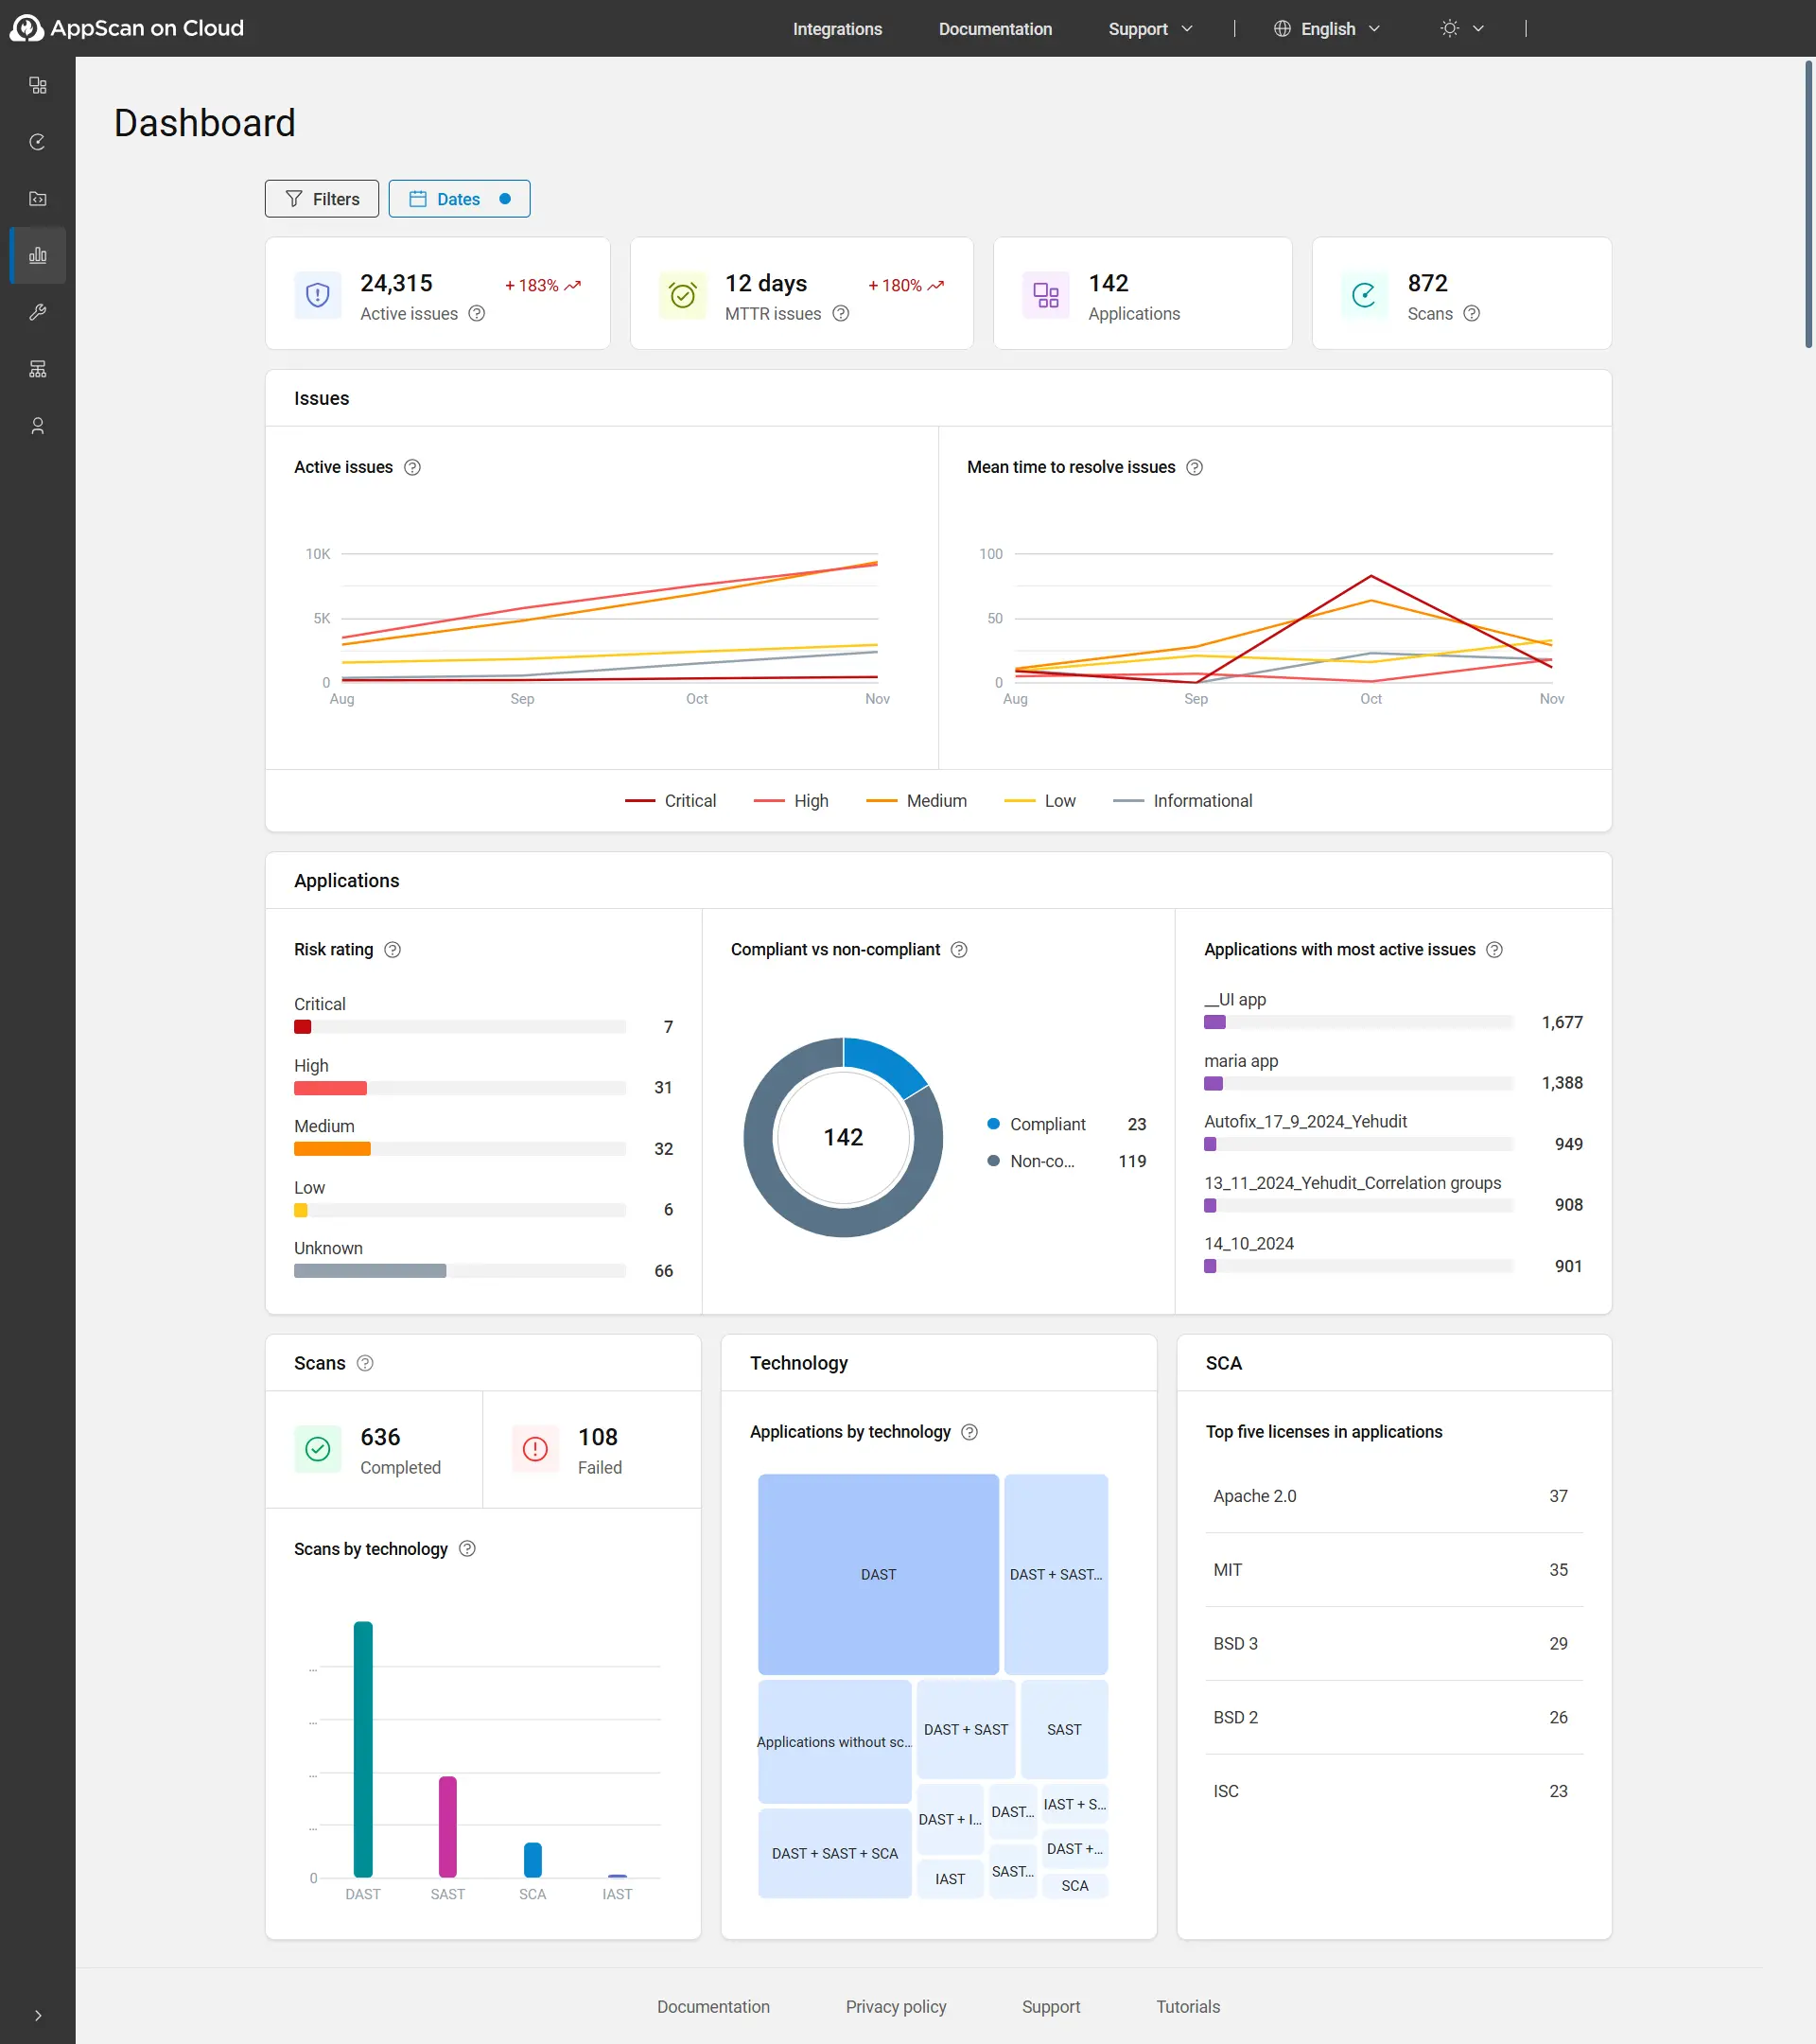
HCL AppScan offers a robust combination of static, dynamic, and interactive testing for enterprise applications. It is often chosen by organizations that need a comprehensive suite for regulatory compliance and secure development lifecycle integration. Unlike many modern tools that specialize in a single area, AppScan provides breadth across SAST, DAST, IAST, and mobile application testing, making it attractive to enterprises seeking a centralized solution.
HCL AppScan key features
Full AppSec suite coverage (SAST, DAST, IAST, mobile app testing).
AI-driven accuracy and optimization for efficient scanning.
Incremental scanning to reduce CI/CD overhead.
Web API scanning with OpenAPI and Postman support.
Cloud and on-premise deployment options.
Centralized dashboards for enterprise management.
HCL AppScan pricing
Pricing starts at $299/scan. Enterprise plans are custom quoted.
HCl AppScan ratings & reviews
Source: G2
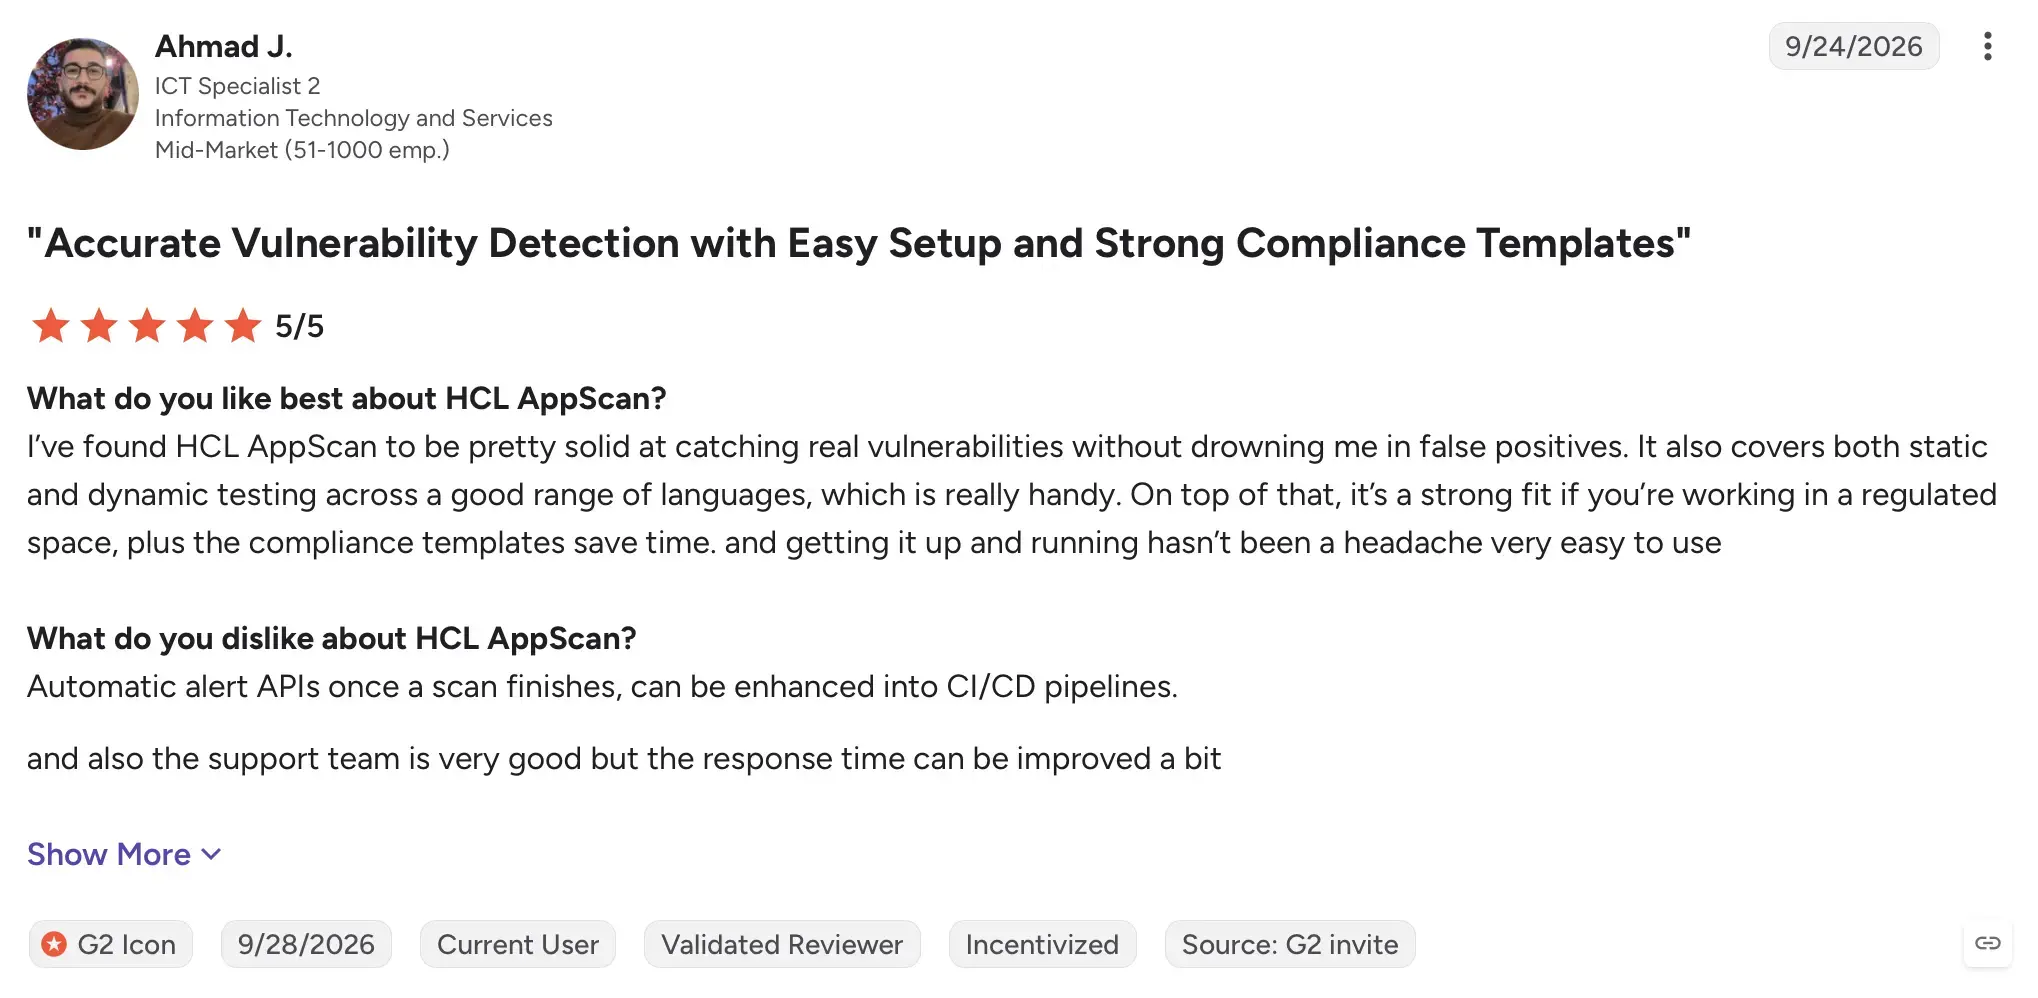
HCL AppScan holds a 4.1/5 rating on G2. Users commend its depth of coverage in vulnerability scanning and its suitability for large enterprises. Many also highlight the reporting quality and ease of integration.
Veracode
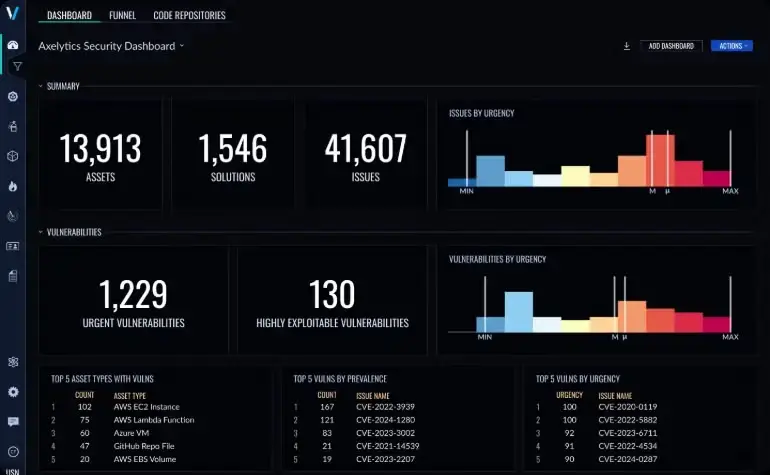
Veracode is a leading application security platform that combines static, dynamic, and software composition analysis in a single solution. It is often chosen as a more enterprise-focused alternative to ZAP or Tenable for organizations seeking full-spectrum AppSec coverage.
With strong IDE and CI/CD integrations, runtime vulnerability detection, and developer training modules, Veracode helps teams enforce security throughout the software development lifecycle. Its compliance reporting and governance features make it especially popular in regulated industries.
Veracode key features
DAST, SAST, IAST, and SCA in one platform.
Runtime vulnerability detection and monitoring.
IDE and CI/CD integration for secure development workflows.
Developer training modules via Veracode Labs.
Enterprise-level reporting and compliance documentation.
Veracode pricing
Pricing is not publicly published.
It’s tiered based on applications and scans.
To get pricing, you must schedule a demo.
Veracode ratings & reviews
Source: G2
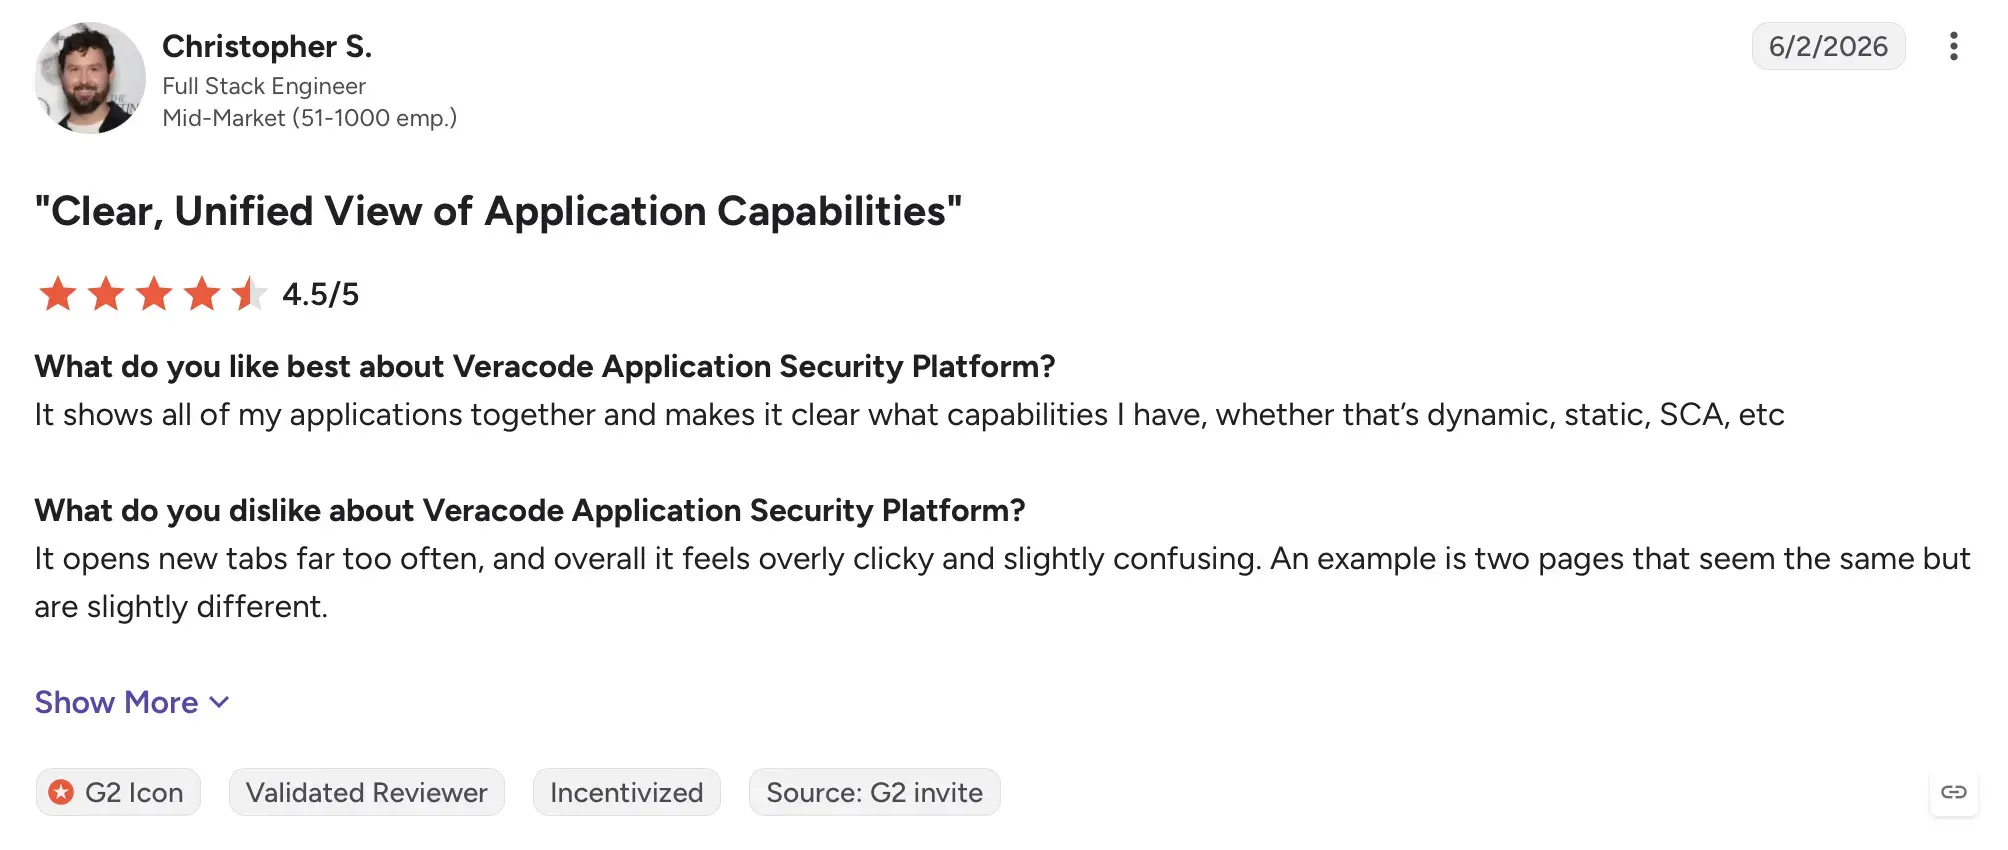
Veracode has a 4.0/5 rating on G2. Customers appreciate its strong application security testing suite and how well it supports secure development lifecycles. The focus on helping teams remediate vulnerabilities quickly stands out in reviews.
Checkmarx
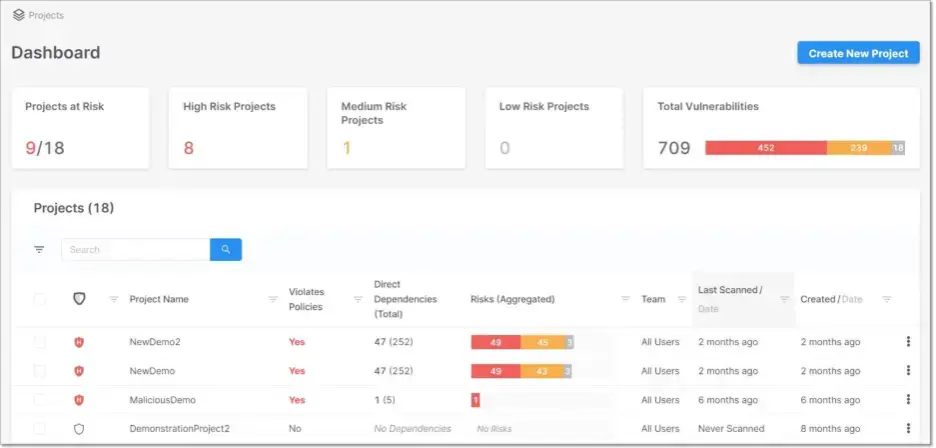
Checkmarx is a unified application security platform offering SAST, DAST, SCA, and API security capabilities. Unlike standalone tools, it provides comprehensive vulnerability coverage across code, dependencies, and runtime environments.
It is particularly strong for enterprises needing full-spectrum AppSec with CI/CD integration, policy enforcement, and detailed reporting. Users praise its broad language support and early detection of security issues, making it suitable for large development teams.
Checkmarx key features
Unified AppSec suite with end-to-end coverage.
Smart DAST runtime analysis.
ASPM integration for vulnerability prioritization.
API testing for REST, SOAP, and gRPC.
CI/CD integration with policy enforcement.
Checkmarx pricing
Custom enterprise quotes
Checkmarx ratings & reviews
Source: G2
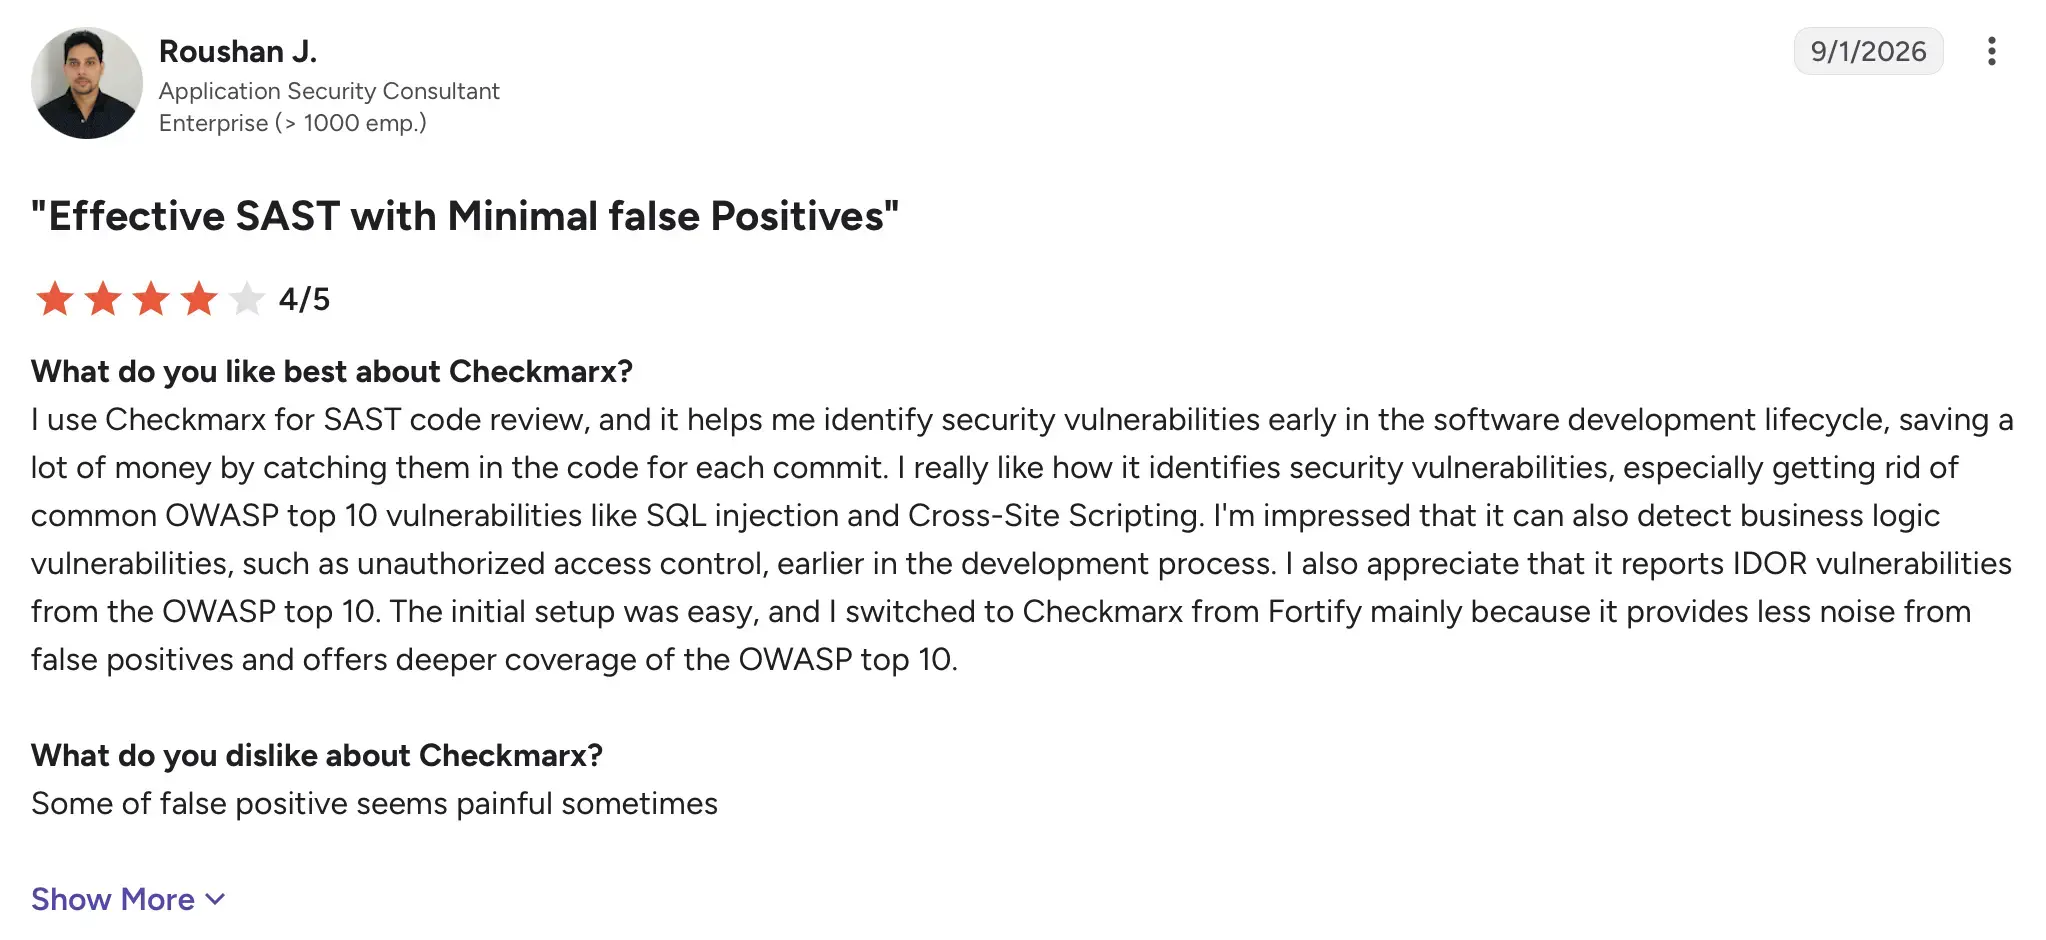
Checkmarx is rated 4.2/5 on G2. Reviewers frequently mention the tool’s effectiveness in static application security testing (SAST) and the high accuracy of results. Developers like how it fits naturally into the development pipeline.
Invicti Web + API (formerly Acunetix)
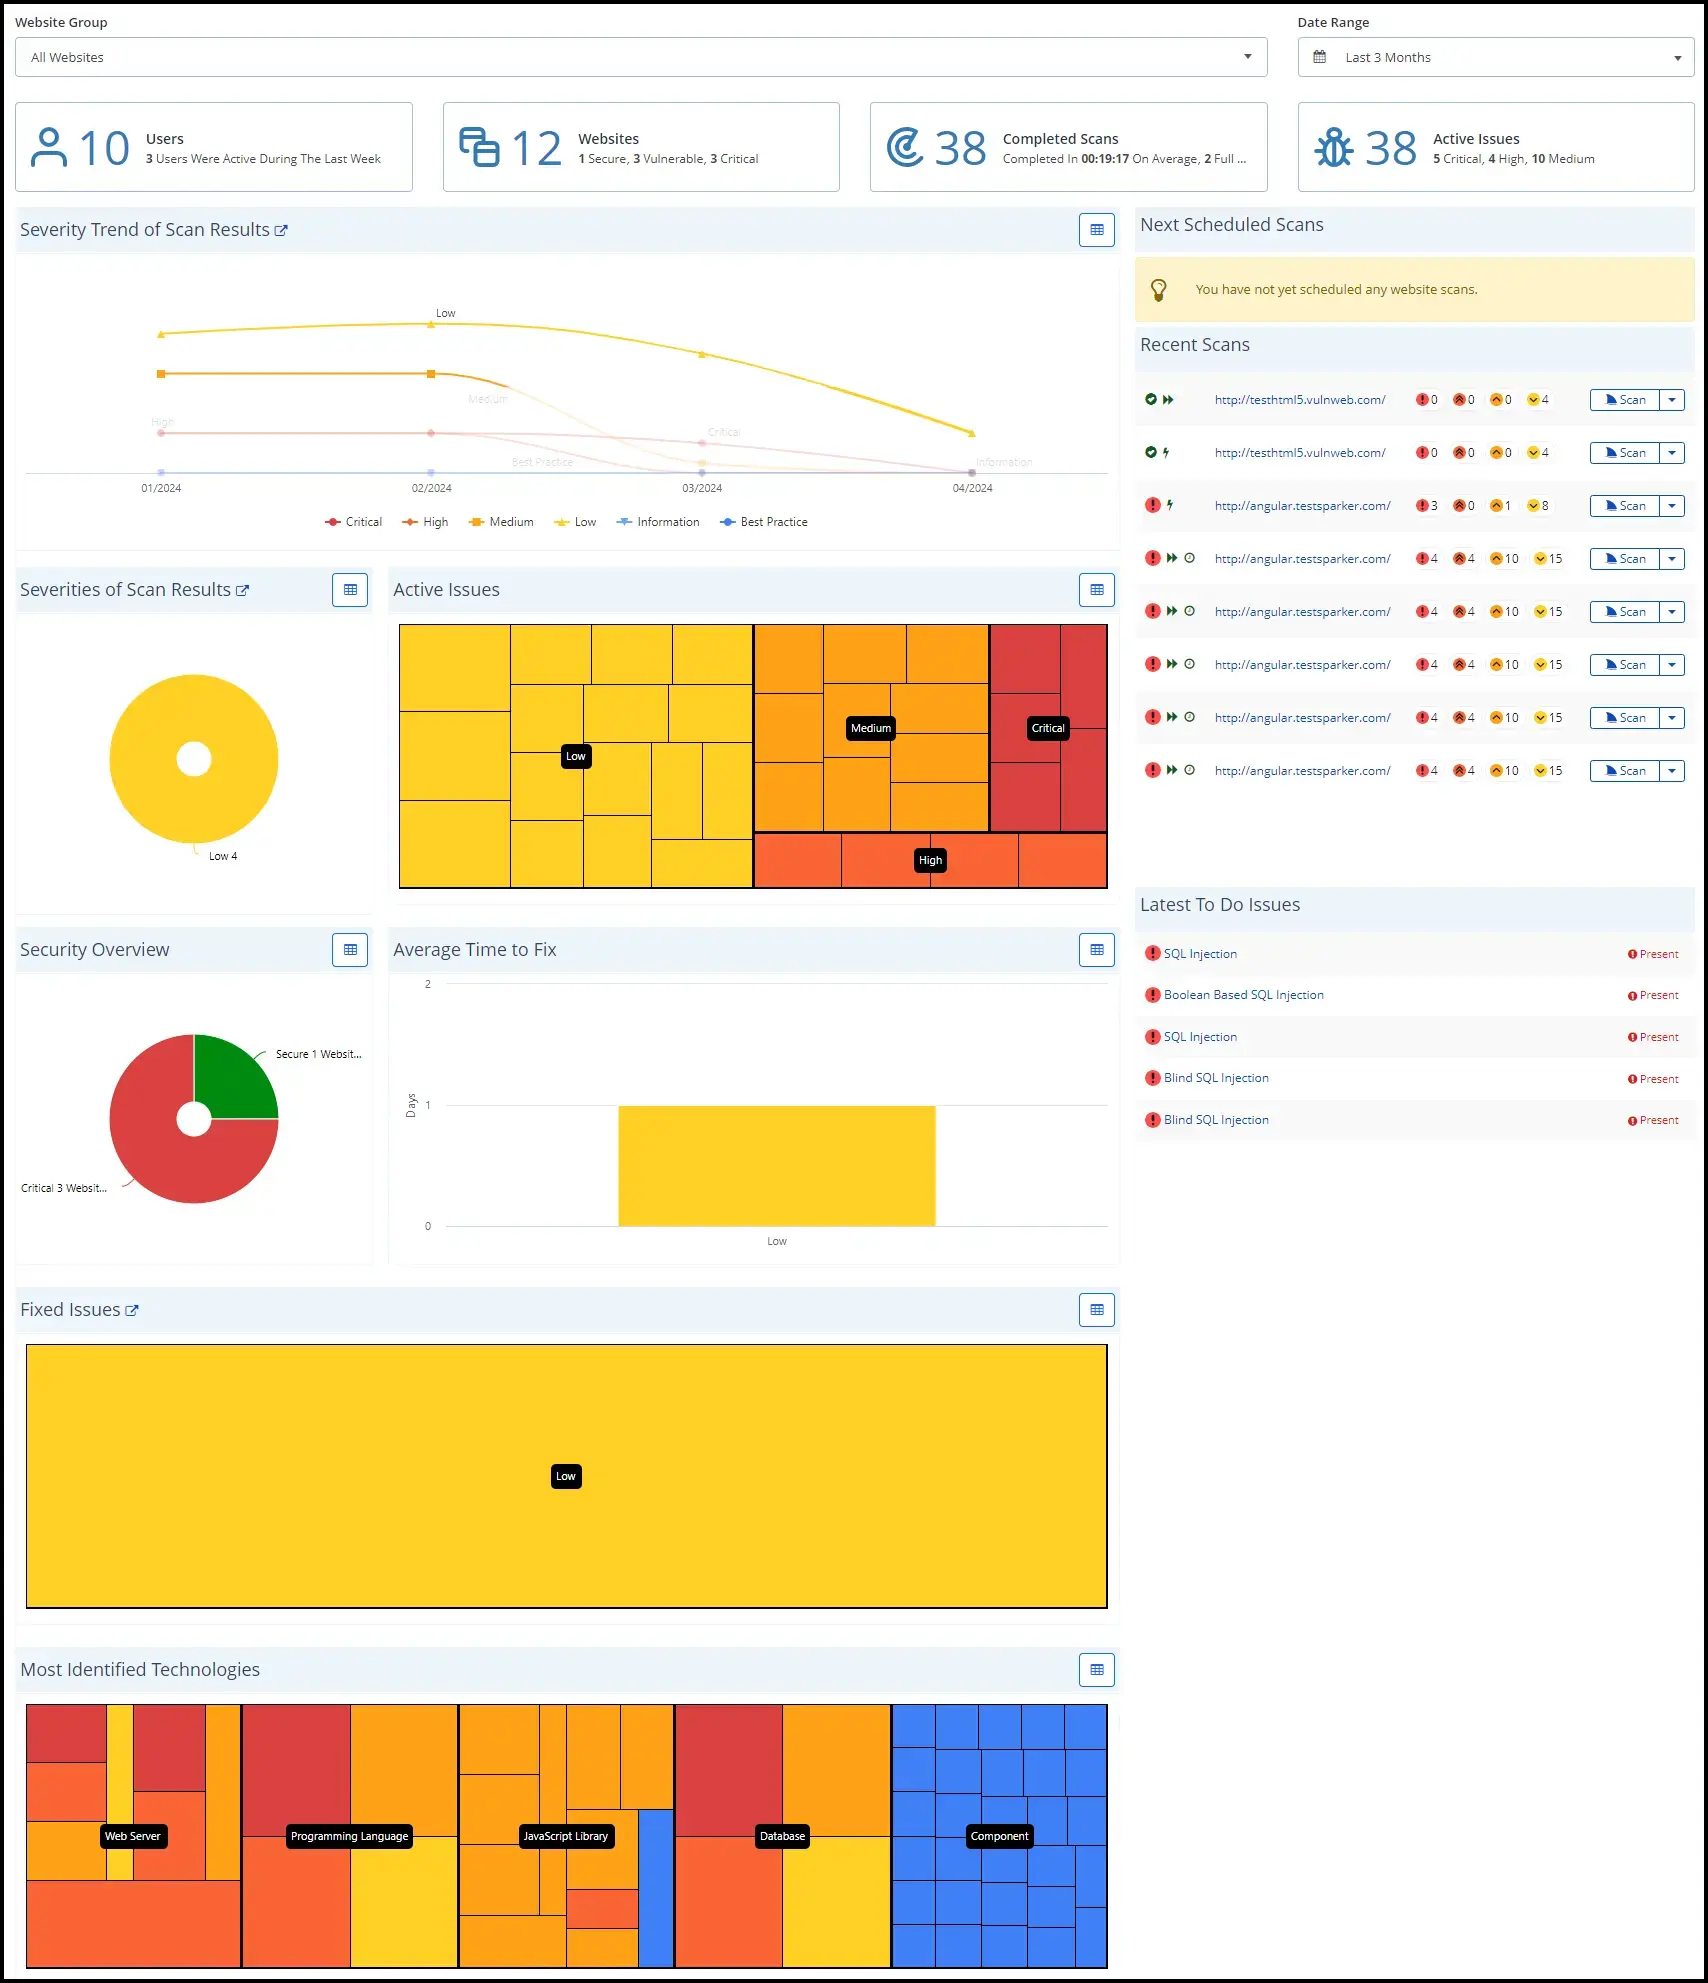
Invicti Web + API is known for its automated web application security scanning, providing comprehensive coverage of vulnerabilities across websites and web applications. Users commend its ease of use, quick scanning capabilities, and the depth of its vulnerability detection. The platform’s user-friendly interface and detailed reporting make it a valuable tool for organizations seeking to enhance their web application security.
Invicti Web + API key features
Automated crawling and vulnerability scanning.
API security testing.
Ticketing system integration.
Focused detection for SQL injection, XSS, and other common vulnerabilities.
Invicti Web + API pricing
Pricing is custom quoted.
Invicti Web + API ratings & reviews
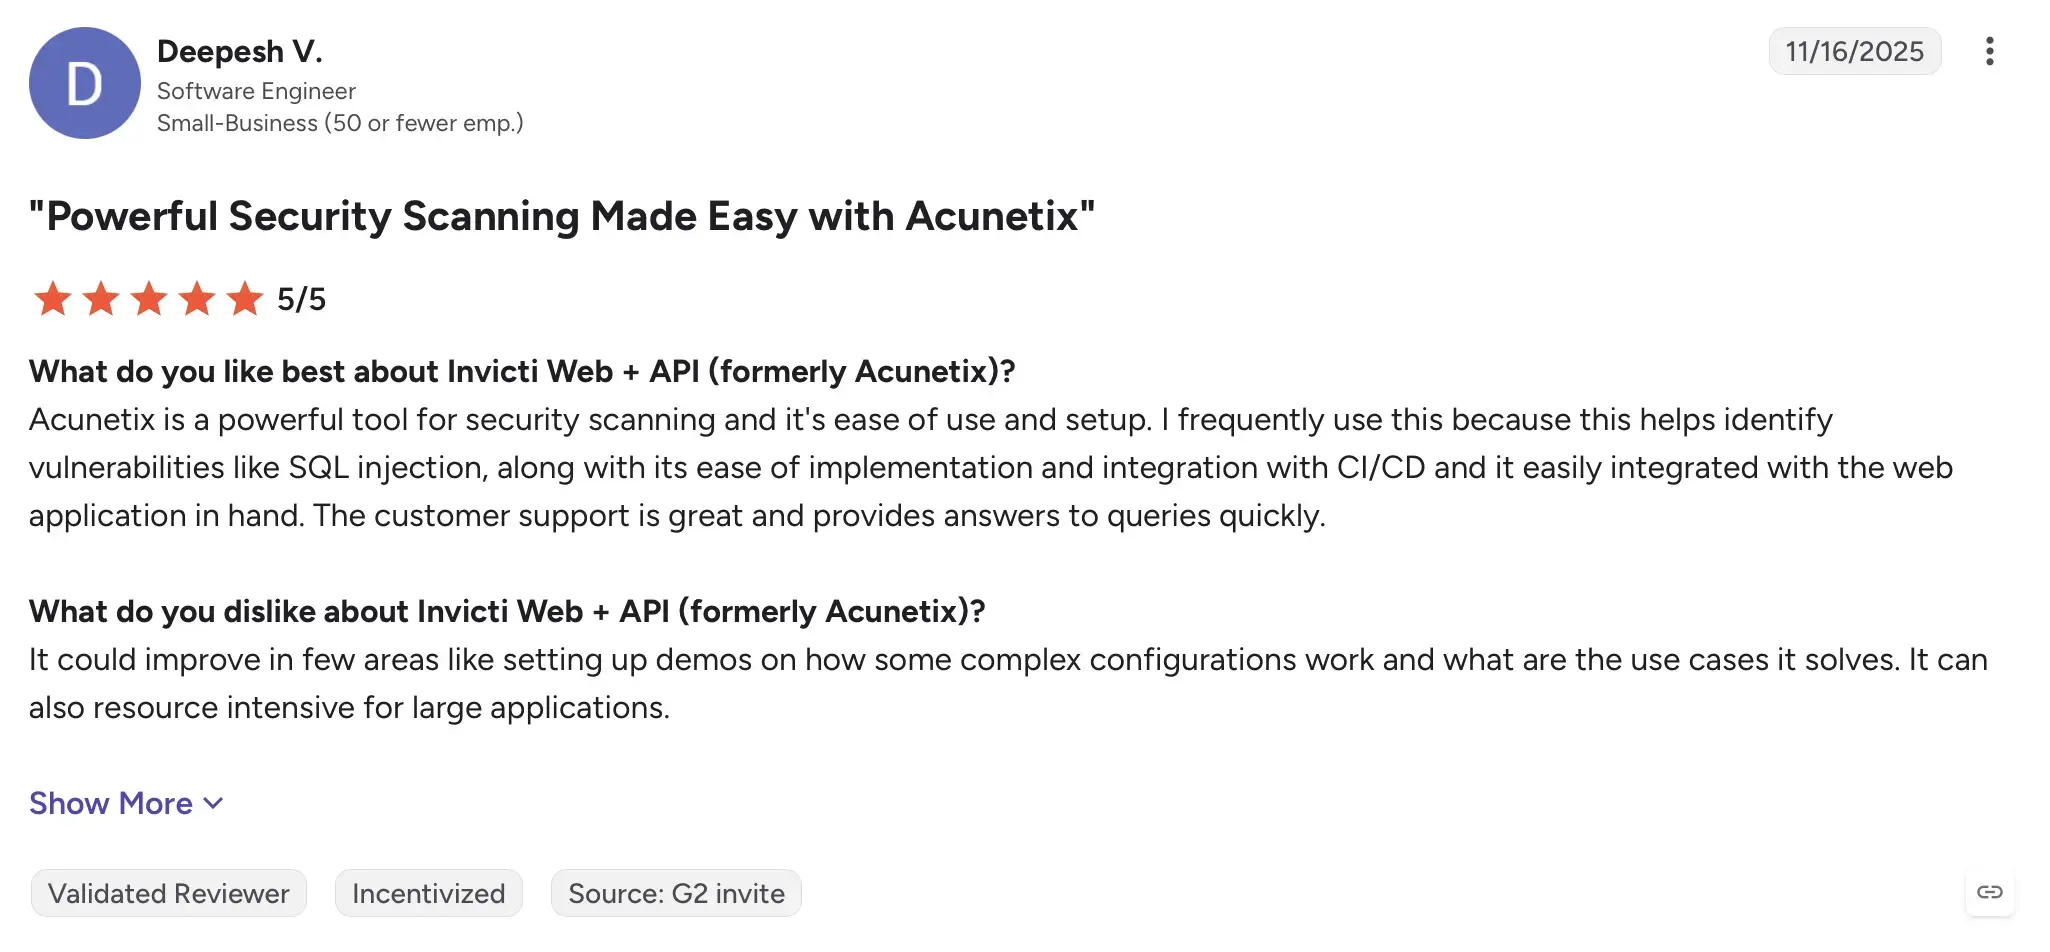
Source: G2
Invicti Web + API scores a 4.1/5 rating on G2. Users value its strong automated scanning capabilities and the speed at which it identifies vulnerabilities. Many also appreciate its user-friendly interface and clear reporting.
Key factors to consider when choosing a ZAP alternative
Selecting the right ZAP alternative involves more than just comparing features; it requires matching a tool’s strengths to your team’s specific workflow, technical environment, and business goals. The best solution for a small agile team will differ significantly from that of a large, compliance-driven enterprise. The decision should be guided by a careful evaluation of your primary use case, budget, and scalability needs. Below are the key factors to weigh before making a choice.
Primary use case & team focus
The first question to ask is: What is the main security challenge you need to solve, and who will be the primary user of this tool? Different tools are optimized for different tasks and user personas.
Automated DevSecOps & CI/CD: For teams focused on integrating security seamlessly into the development pipeline for fast feedback. Beagle Security, Veracode, and Checkmarx excel here with strong API support and native CI/CD plugins that enable automated testing within workflows.
Manual penetration testing: For dedicated security professionals who require deep, granular control to perform in-depth assessments. Burp Suite Professional is the undisputed leader, offering a powerful suite of manual tools for precise attack simulation.
Holistic vulnerability management: For organizations that need to view web application risks in the context of their entire IT infrastructure (servers, networks, cloud assets). Tenable WAS, Rapid7 InsightAppSec, and Qualys WAS are ideal as they integrate DAST findings into a broader enterprise risk dashboard.
Budget-conscious general scanning: For individuals or organizations with limited budgets needing a capable, broad-spectrum vulnerability scanner. OpenVAS provides extensive network and infrastructure scanning capabilities at no cost, though it requires significant technical expertise to manage.
Ease of use & intended audience
A tool’s value is directly linked to its adoption. If a platform is too complex for its intended users, it won’t be used effectively, regardless of its power.
Developer-friendly: Known for intuitive interfaces, straightforward setup, and reports that provide clear, actionable remediation guidance for developers. Beagle Security and Invicti Web + API are frequently praised for their usability and focus on making results easy for development teams to consume.
Security professional focused: Extremely powerful and feature-rich platforms that assume a high level of security expertise and have a steeper learning curve. Burp Suite Professional and HCL AppScan fit this category, offering the depth required by seasoned security analysts.
Scalability & environment size
A security solution must be able to grow alongside your organization. The tool you choose should effectively handle both your current and future asset count.
Small to mid-sized businesses (SMBs): Offer an optimal balance of powerful automated scanning and ease of management, perfect for smaller teams. Beagle Security and Invicti Web + API provide enterprise-grade scanning in a package that is easy to deploy and maintain without a large security team.
Large enterprises: Built to manage security across thousands of applications with features like centralized dashboards, role-based access control (RBAC), and advanced reporting. Veracode, Checkmarx, Tenable WAS, and Qualys WAS are designed for this scale, offering the governance and oversight features large organizations require.
Budget & pricing model
Cost is a critical factor, and ZAP alternatives cover the full spectrum from free, open-source projects to significant enterprise investments.
Free & open source: Tools with no licensing fees, ideal for those with the technical skill to handle setup and ongoing maintenance. OpenVAS is the leading choice in this category.
Cost-effective professional tools: Provide excellent value with predictable per-user or per-app pricing, making them accessible without requiring a massive budget. Burp Suite Professional (499/user/year) and Beagle Security (1,188/year) are prime examples.
Premium enterprise platforms: Comprehensive suites with custom pricing based on the number of apps, users, and features needed. These solutions are a significant investment but offer the broadest capabilities. Veracode, Checkmarx, and Tenable WAS fall into this tier.
Deployment model
Your organization’s infrastructure, data residency rules, and regulatory requirements will dictate whether a cloud-based or on-premise solution is a better fit.
Cloud-native (SaaS): Fully managed by the vendor, offering fast setup, low maintenance, and instant access to the latest updates. Beagle Security, Veracode, Tenable.io, and the Qualys Cloud Platform are all delivered as SaaS.
On-premise & hybrid: Allow you to install and run the software within your own data center, giving you full control over data and system configuration. HCL AppScan and Burp Suite Enterprise Edition offer robust on-premise deployment options for organizations with strict data governance needs
Final thoughts
ZAP remains a widely used, free tool for security testing, but many teams eventually outgrow its capabilities. Limitations in scalability, automation, and integration make it less suitable for modern enterprise security programs.
The alternatives reviewed here, including Beagle Security, Burp Suite, Invicti Web + API, and Veracode, offer diverse approaches to application security. Some prioritize automation and developer-friendly workflows, while others excel in manual penetration testing or full-spectrum enterprise vulnerability management.
The right tool depends on your team size, application architecture, security maturity, and operational needs. Smaller teams may benefit from simple, cost-effective options, while large organizations often require advanced automation, comprehensive coverage, and enterprise-level reporting. Selecting the right tool ensures more efficient vulnerability management, better developer adoption, and smoother integration of security into the SDLC.
FAQs
Why should businesses consider alternatives to ZAP?
Businesses may consider ZAP alternatives when they need easier configuration, more automated testing workflows, enterprise reporting, dedicated support, or integrations with existing development tools. Commercial platforms may also offer capabilities that reduce the manual effort required to configure, run, and manage security tests.
What is the best free alternative to ZAP?
ZAP itself is free and open source. OpenVAS is another free, open-source option, but it primarily focuses on network and infrastructure vulnerability scanning rather than serving as a direct replacement for web application DAST. The best option depends on whether you need application-specific security testing or broader infrastructure vulnerability assessment.
What is the difference between ZAP and Beagle Security?
ZAP is a free, open-source web application security testing tool that supports automated scanning and manual testing workflows. Beagle Security is a commercial platform focused on agentic AI penetration testing for web applications and APIs, with capabilities such as business logic testing, authenticated testing, and developer-oriented remediation guidance. ZAP may suit teams seeking an open-source tool with hands-on control, while Beagle Security is an option for teams looking for a more automated penetration testing workflow.