Moving to the cloud promised to accelerate everything, and it delivered. Development teams now ship features faster, scale instantly, and deploy globally with a few clicks.
The tradeoff is that vulnerabilities move just as fast. Traditional security testing tools, built for static environments and long release cycles, struggle to keep pace with containers, microservices, and CI/CD pipelines. This is where cloud based application security testing (AST) tools prove their value.
Cloud native AST tools integrate directly into DevSecOps workflows, enabling continuous and automated testing across dynamic environments. They combine DAST, SAST, SCA, and API testing into scalable, on demand platforms built to work at cloud speed. This guide compares the best cloud based AST tools in 2026, their features, methodologies, and G2 ratings, to help you choose the right fit for your team’s security needs.
Best cloud-based AST tools comparison chart
Here’s a quick overview of the leading cloud-based AST tools, highlighting their key capabilities, testing methodologies, and G2 ratings.
| Tool | Key features | AST methodologies covered | G2 rating |
|---|---|---|---|
| Beagle Security | Agentic AI pen-testing, GraphQL and REST API testing, CI/CD integration, zero false positives | DAST, API security, automated pentesting | 4.7/5 |
| Checkmarx One | Unified AppSec platform, AI-driven correlation, multi-cloud integration, compliance mapping | SAST, DAST, SCA, IAST | 4.2/5 |
| GitLab Ultimate Security | Built-in DevSecOps pipeline scanning, auto-remediation suggestions, merge request integration | SAST, DAST, dependency scanning, container security | 4.5/5 |
| Rapid7 InsightAppSec | Cloud-native DAST with IAST integration, REST and SOAP API support, advanced analytics | DAST, IAST | 3.9/5 |
| Tenable | Risk-based web app scanning, vulnerability prioritization, unified platform with Tenable.io | DAST, container security | 4.5/5 |
| Qualys | Enterprise-scale WAS, VMDR integration, compliance automation, global asset discovery | DAST, SCA | 4.4/5 |
| ZAP (Checkmarx ZAP) | Open-source, customizable, CI/CD integration, dynamic scanning, flexible automation | DAST | 4.7/5 |
| Burp Suite | Manual and automated testing, CI/CD automation, advanced proxy capabilities, BApp extensions | DAST | 4.8/5 |
| Mend.io | Advanced SCA and container scanning, policy automation, continuous monitoring | SCA, container security | 4.3/5 |
| Contrast Security | Runtime IAST and RASP, real-time vulnerability detection, code-level insight | IAST, RASP | 4.5/5 |
Best cloud-based AST tools in 2026
1. Beagle Security
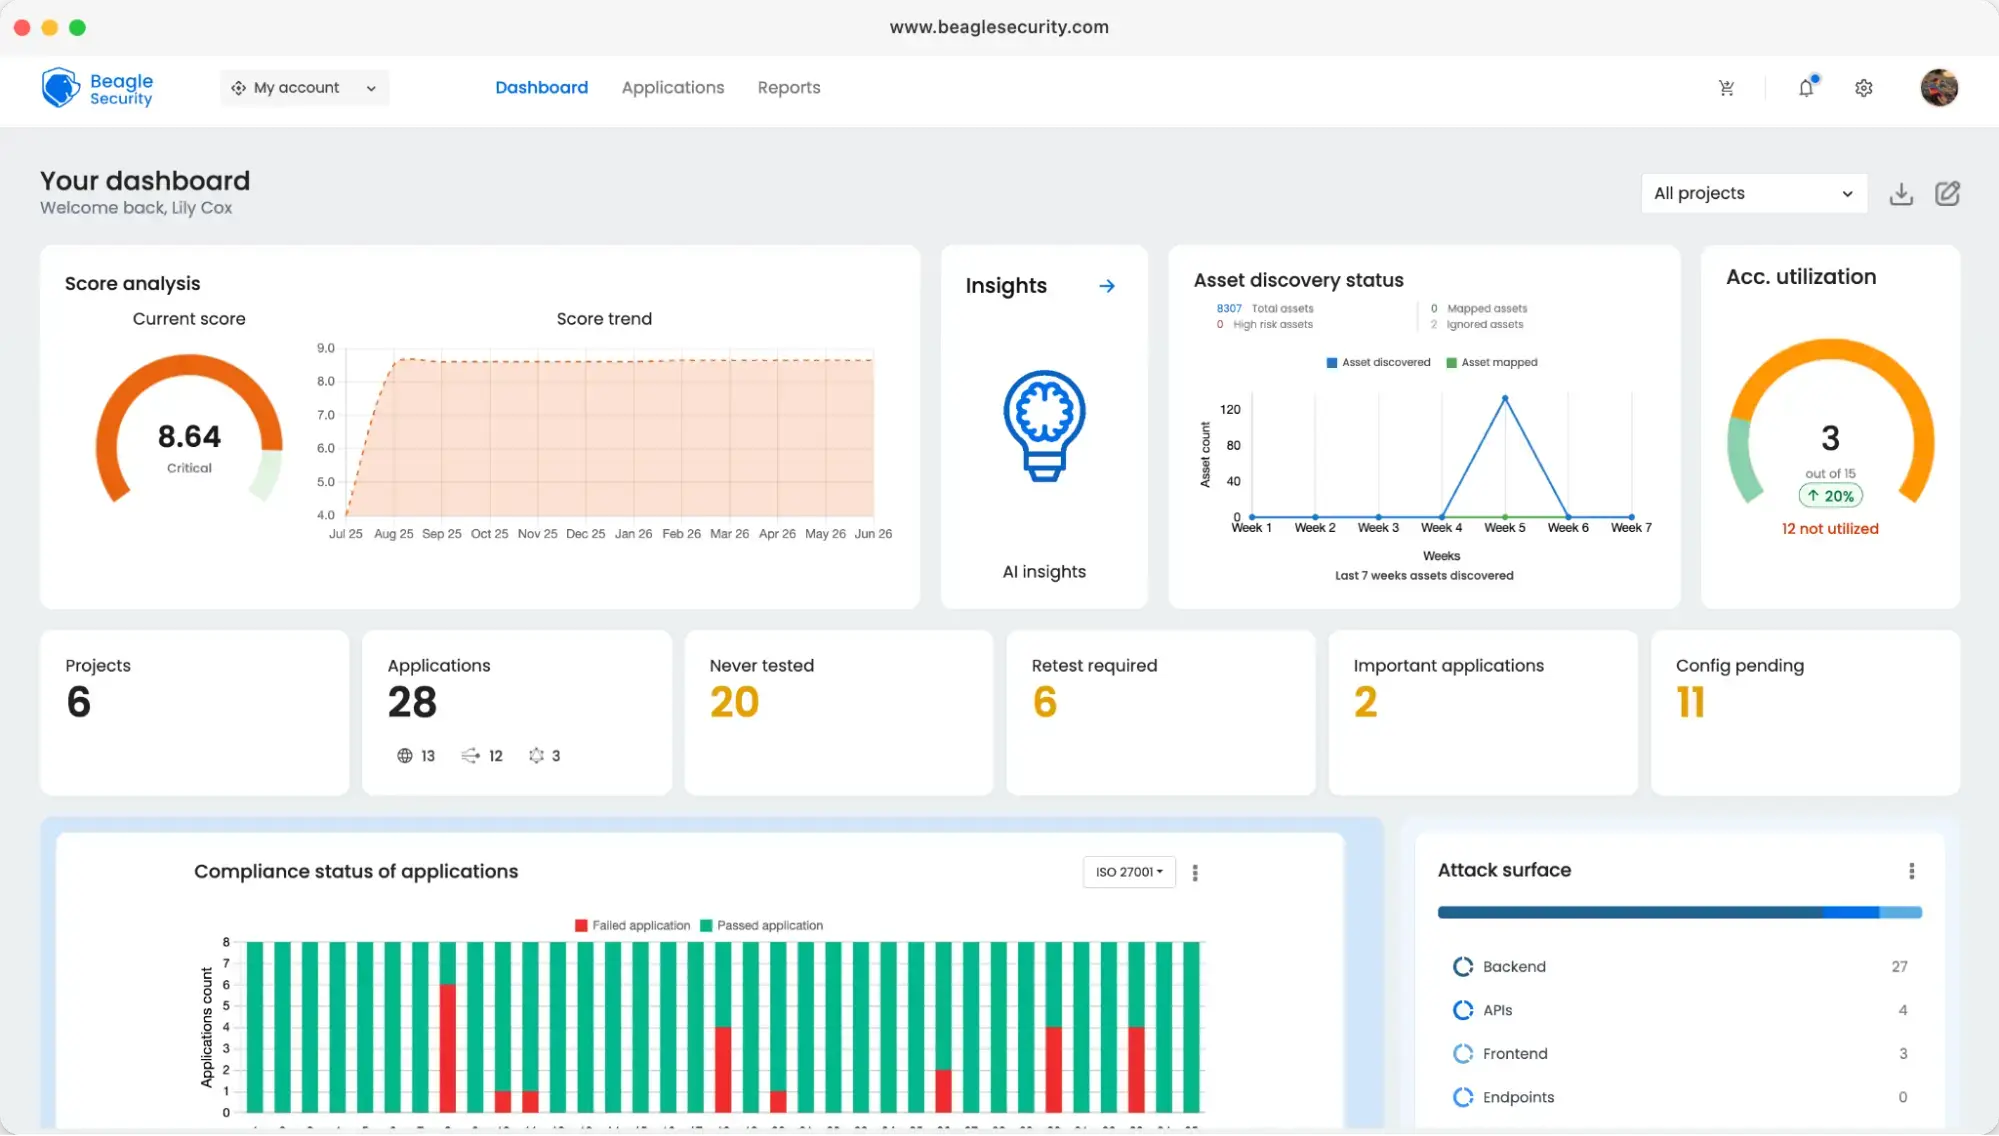
Beagle Security is a cloud-native application security testing platform with agentic AI- powered penetration testing that specializes in automated DAST and API security testing. It helps development teams identify, validate, and remediate vulnerabilities in web and API-based applications before attackers can exploit them. Built for CI/CD environments, Beagle Security integrates directly with pipelines to ensure every deployment is automatically tested.
Key features
Agentic AI-powered vulnerability validation with low false positive rate
REST, SOAP, and GraphQL API security testing
Pre-production and staging environment support
CI/CD integrations for GitLab, Jenkins, and GitHub Actions
Continuous scanning with automated reporting
G2 rating:
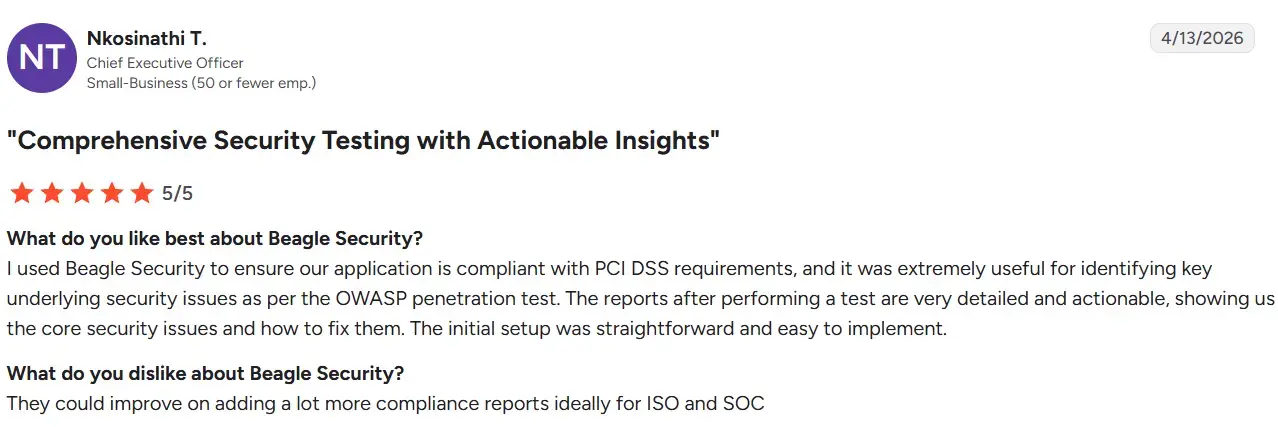
Users rate Beagle Security 4.7 out of 5, praising its ease of setup, accuracy, and automation capabilities.
Pricing:
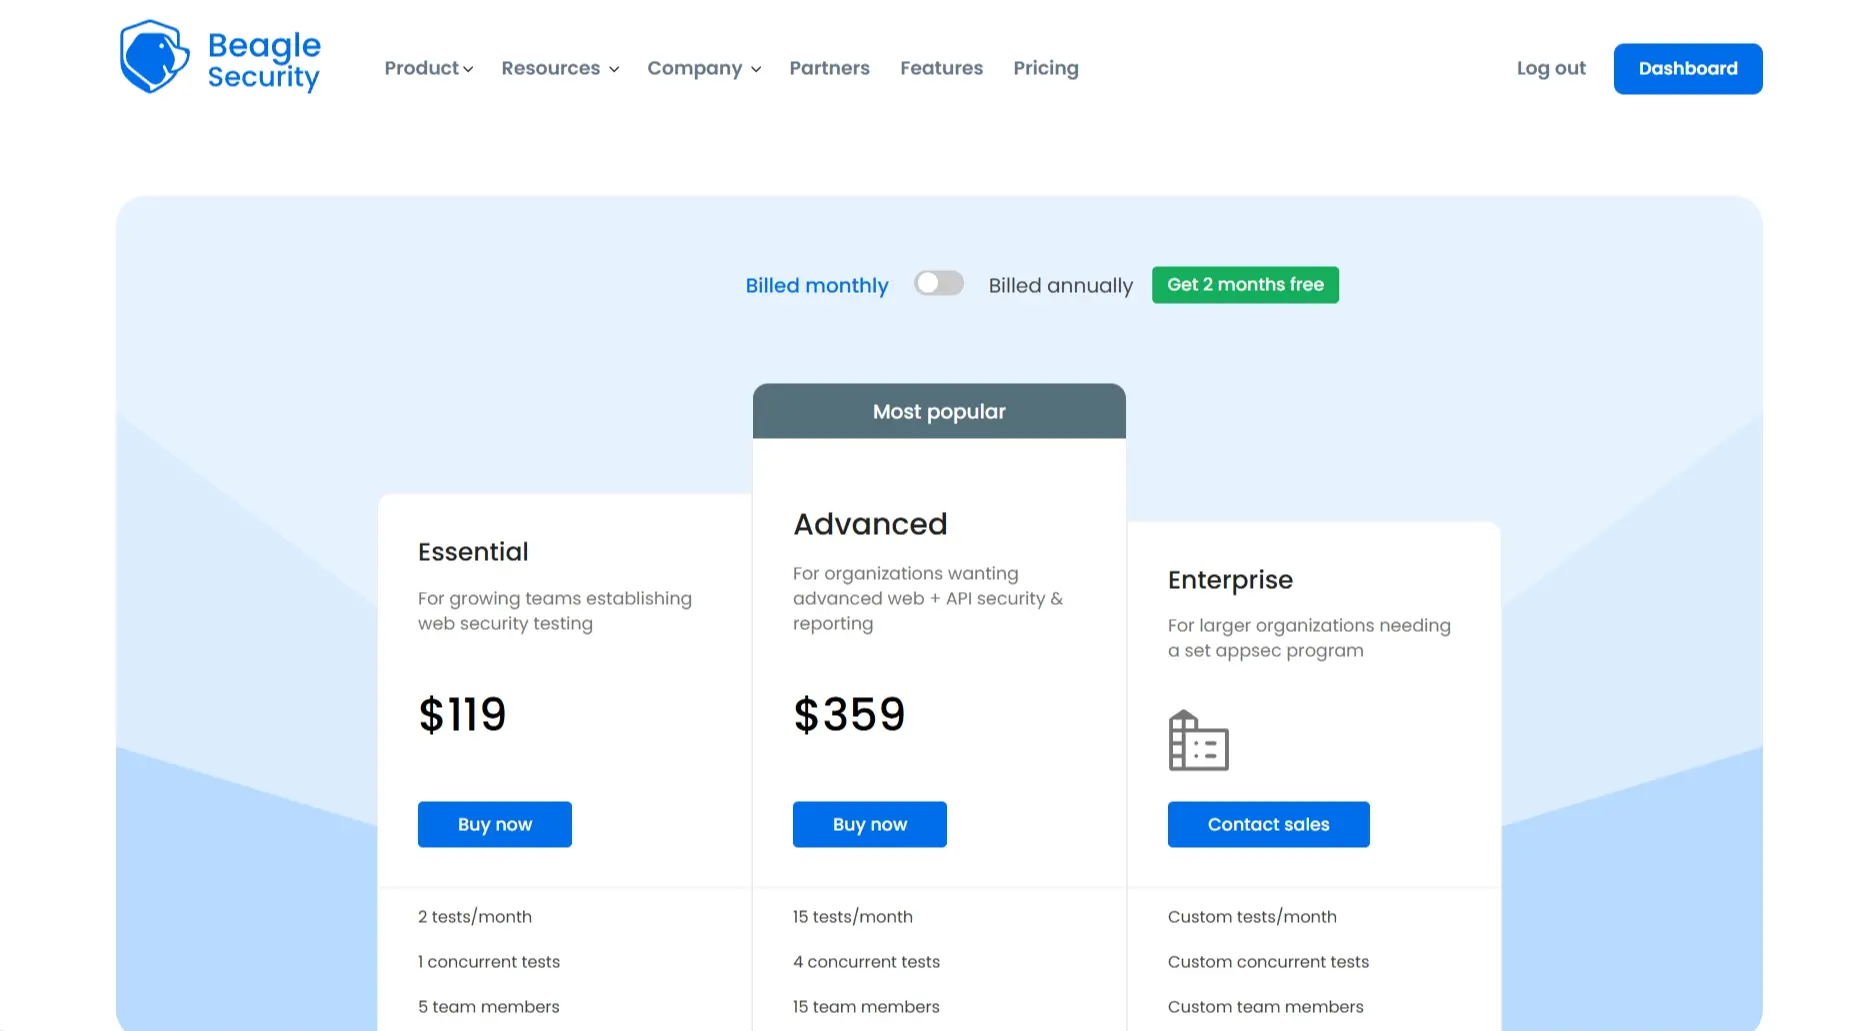
Essential plan : $119 per month
Advanced plan : $359 per month
Enterprise : Custom pricing available
2. Checkmarx One
Checkmarx One unifies SAST, DAST, SCA, and API security testing within a single cloud-based platform. It is designed for large organizations managing complex, multi-cloud environments that demand consistent visibility and governance across all application layers.
Key features
Unified cloud AppSec platform with cross-correlation across DAST, SAST, and SCA
AI-powered prioritization of vulnerabilities
Multi-cloud and hybrid deployment options
Pre-configured compliance templates for SOC 2, PCI DSS, and ISO
Secure coding feedback and developer education tools
Native integrations with popular CI/CD tools
G2 rating:
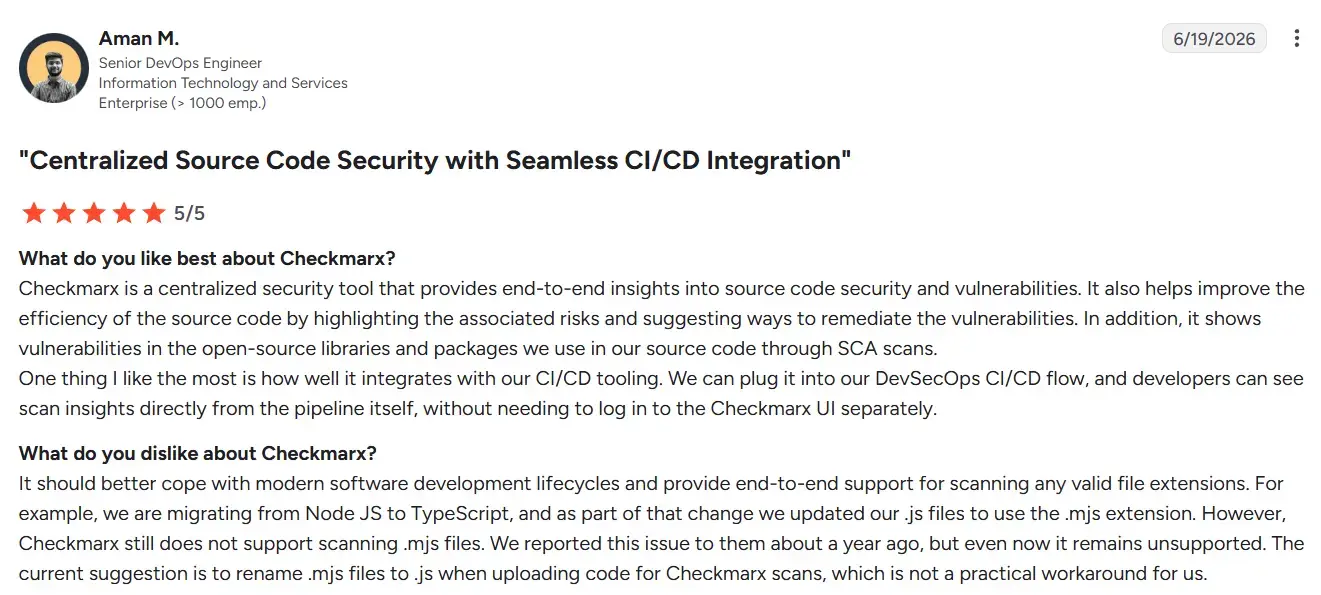
Checkmarx One holds a 4.2 out of 5 rating from users who appreciate its scalability and centralized visibility for large enterprise teams.
Pricing:
- Custom pricing based on organization size and deployment needs
3. GitLab Ultimate Security

GitLab Ultimate Security provides comprehensive cloud-based security scanning natively integrated into the DevOps pipeline. It is designed for organizations that prefer a single platform for both code collaboration and security automation.
Key features
Built-in SAST, DAST, and dependency scanning within GitLab pipelines
Merge request-based security approvals and auto-remediation
Container and Kubernetes image scanning
Compliance management and policy enforcement
Supports both cloud and self-managed deployments
Detailed vulnerability dashboards and metrics
G2 rating:
GitLab Ultimate Security has a 4.5 out of 5 rating from 897 reviews, with users highlighting the convenience of unified DevSecOps workflows.
Pricing:
- Custom pricing
4. Rapid7 InsightAppSec
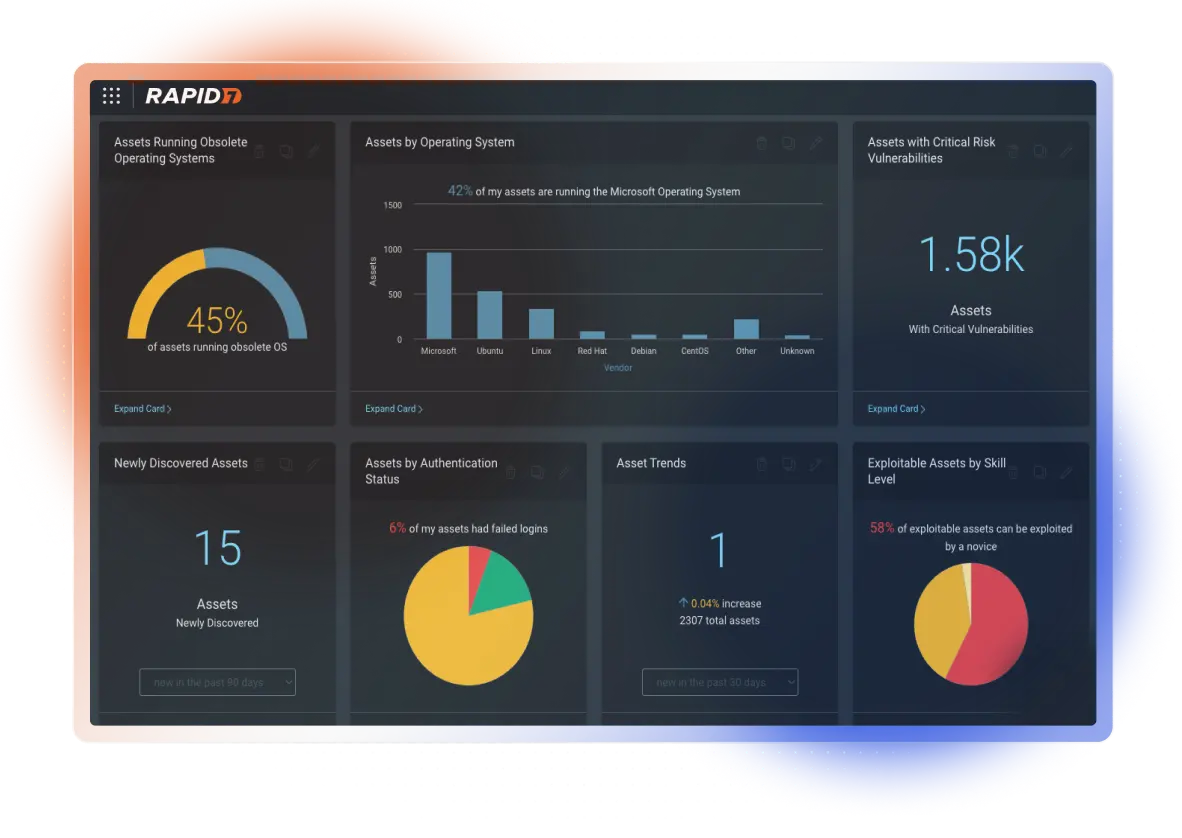
Rapid7 InsightAppSec brings powerful cloud-based DAST capabilities with IAST integration, enabling teams to dynamically test modern web applications. Its analytics and visualization features provide security and development teams a shared view of findings.
Key features
Cloud-native DAST with real-time analytics
IAST integration for deeper insight into vulnerabilities
Strong support for REST and SOAP APIs
Automation workflows for continuous testing
Comprehensive vulnerability reporting and dashboards
Insight platform integration for central visibility
G2 rating:
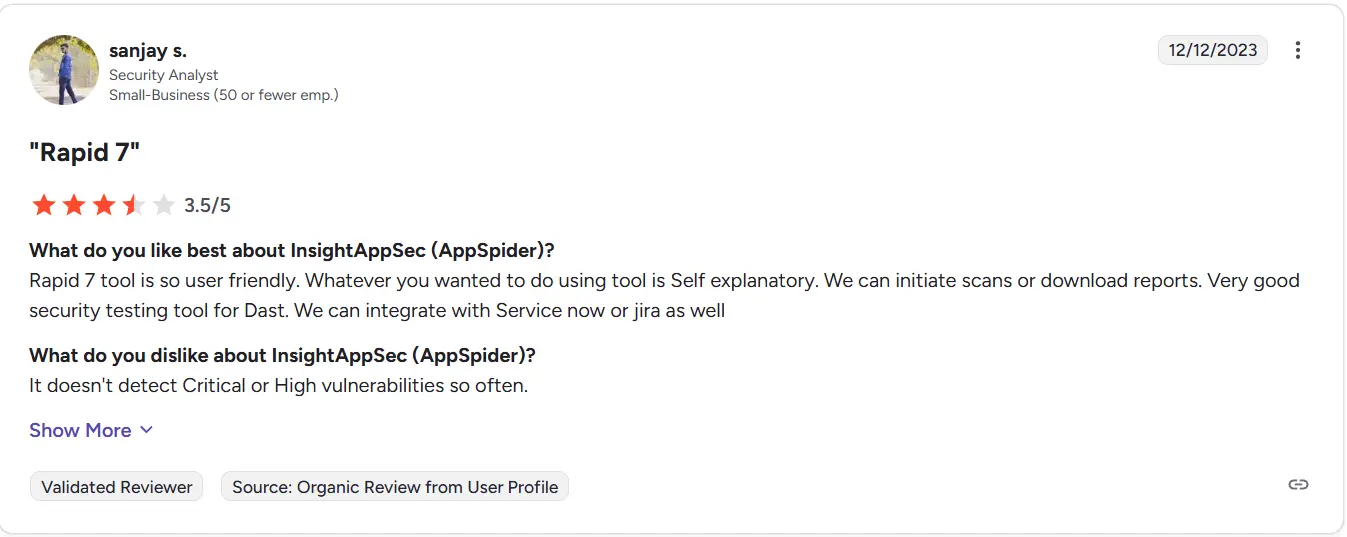
Rapid7 InsightAppSec is rated 3.9 out of 5 by users who value its accuracy and ease of cloud deployment.
Pricing:
- From $175 per application per month
5. Tenable
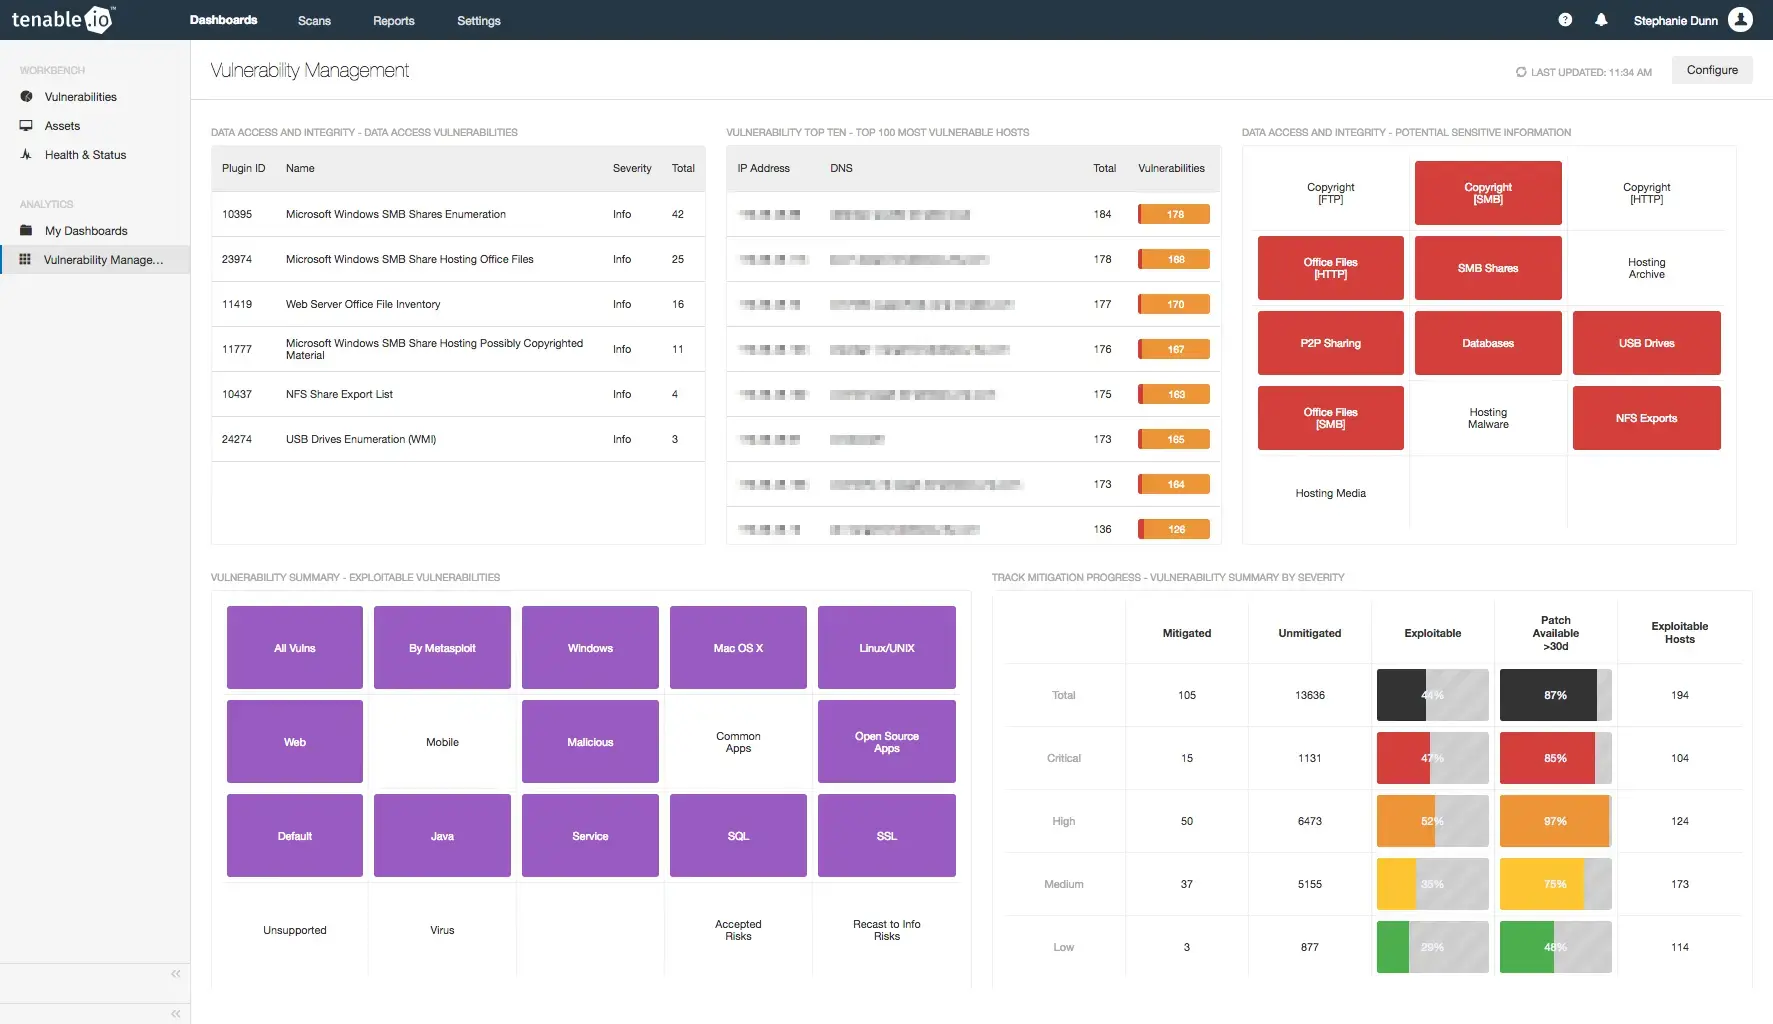
Tenable extends its well-known vulnerability management capabilities into cloud-based application testing. Integrated with Tenable.io, it offers risk-based prioritization that helps organizations focus on high-impact vulnerabilities across cloud assets.
Key features
Web application scanning integrated with Tenable.io
Risk-based prioritization using Tenable VPR
Support for containerized and cloud-native environments
Dashboards correlating vulnerabilities with risk exposure
Centralized reporting and compliance visibility
G2 rating:
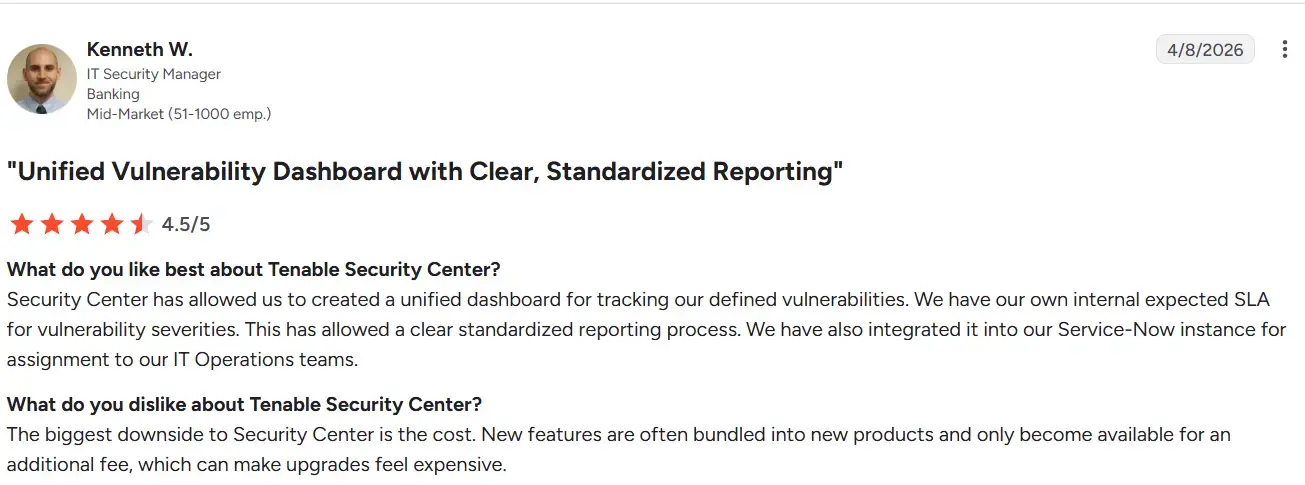
Tenable is rated 4.5 out of 5 by users who appreciate its unified visibility across infrastructure and applications.
Pricing:
- Annual plans start at $7,434 for five FQDNs
6. Qualys
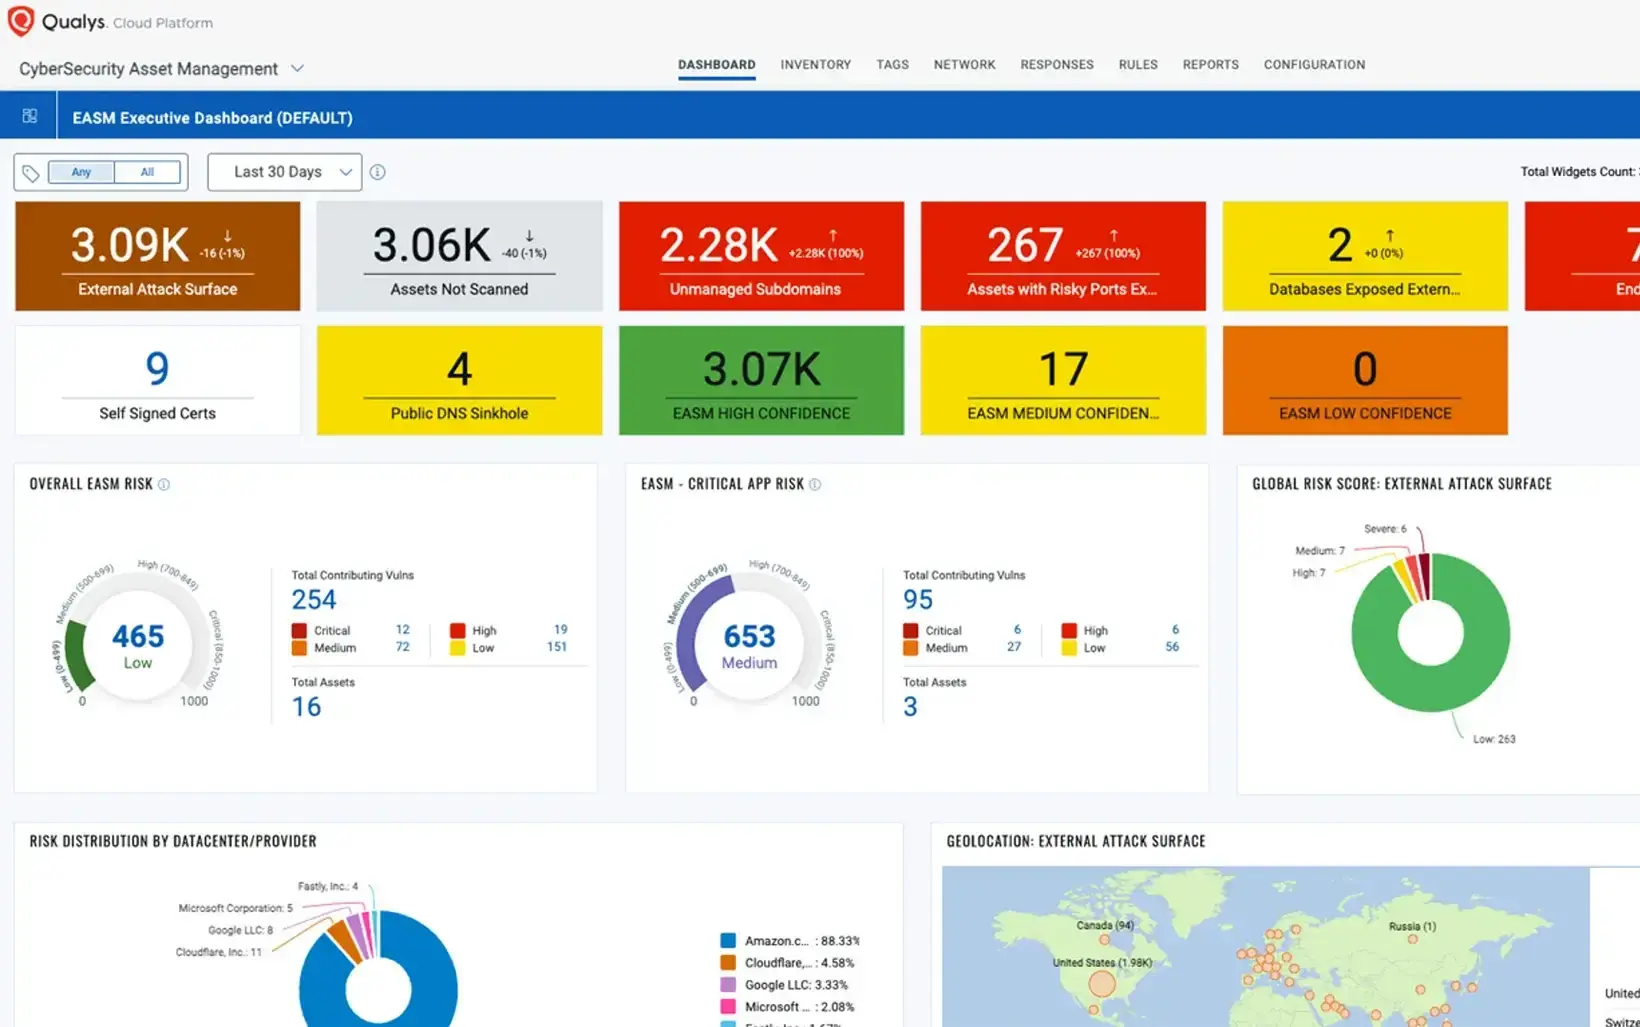
Qualys offers an enterprise-grade, cloud-native platform for DAST and SCA, combining web application scanning with vulnerability management and compliance automation. It is best suited for large organizations managing thousands of assets across multiple clouds.
Key features
Scalable web application scanning for global deployments
Built-in integration with VMDR and Policy Compliance modules
Continuous discovery of internet-facing assets
Support for hybrid and multi-cloud infrastructures
Automated compliance reporting and alerts
G2 rating:
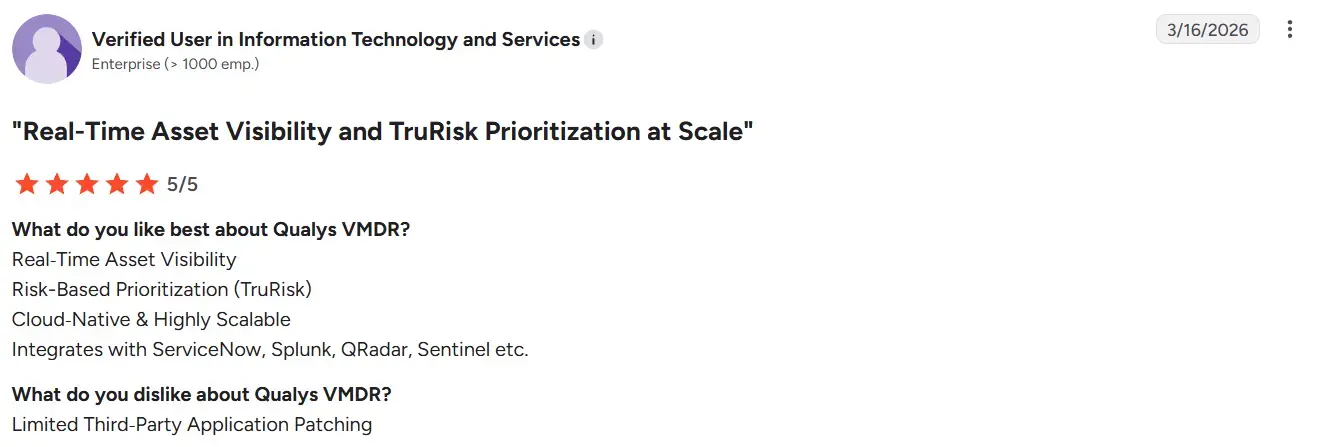
Qualys has a 4.4 out of 5 rating from users who appreciate its stability and integration depth with broader vulnerability management features.
Pricing:
- Custom quote-based pricing
7. ZAP (Checkmarx ZAP)
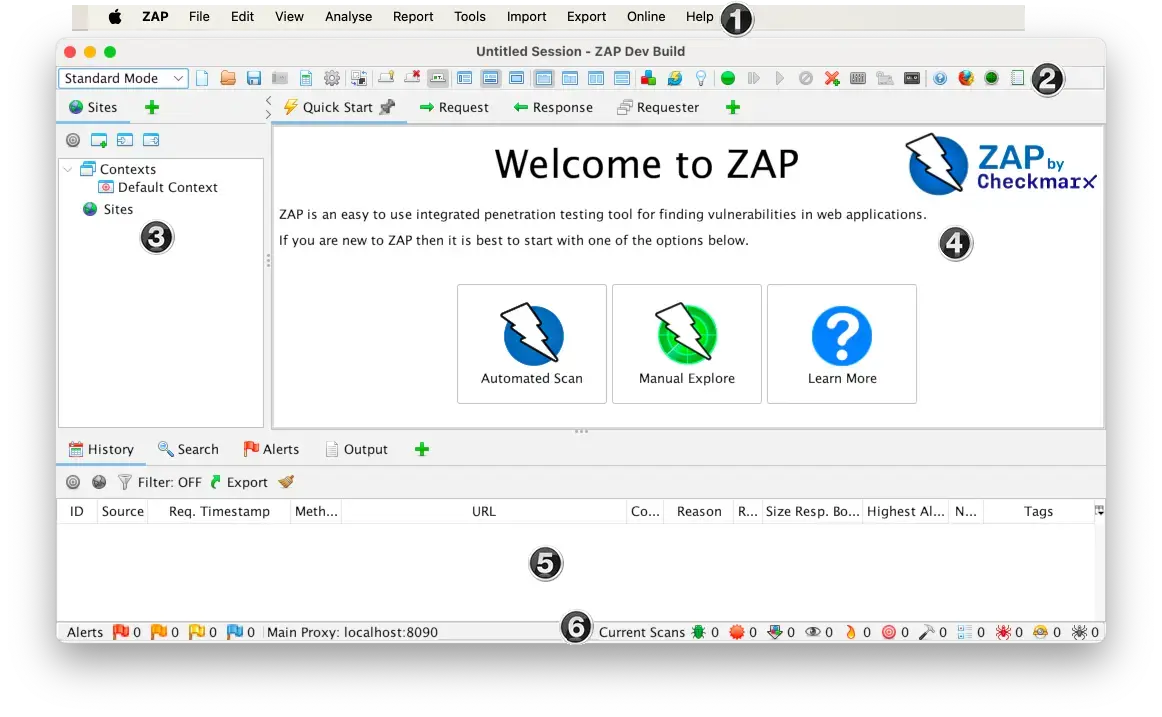
ZAP, now under Checkmarx, remains one of the most popular open-source DAST tools with extensive cloud deployment options. It allows flexible customization, integration into CI/CD pipelines, and automation for large-scale testing environments.
Key features
Dynamic web application scanning with customizable scripts
API scanning for REST and SOAP endpoints
Integration with cloud CI/CD platforms like GitHub Actions and GitLab CI
Headless scanning and automation modes for DevSecOps workflows
Strong community support and plugin ecosystem
G2 rating:
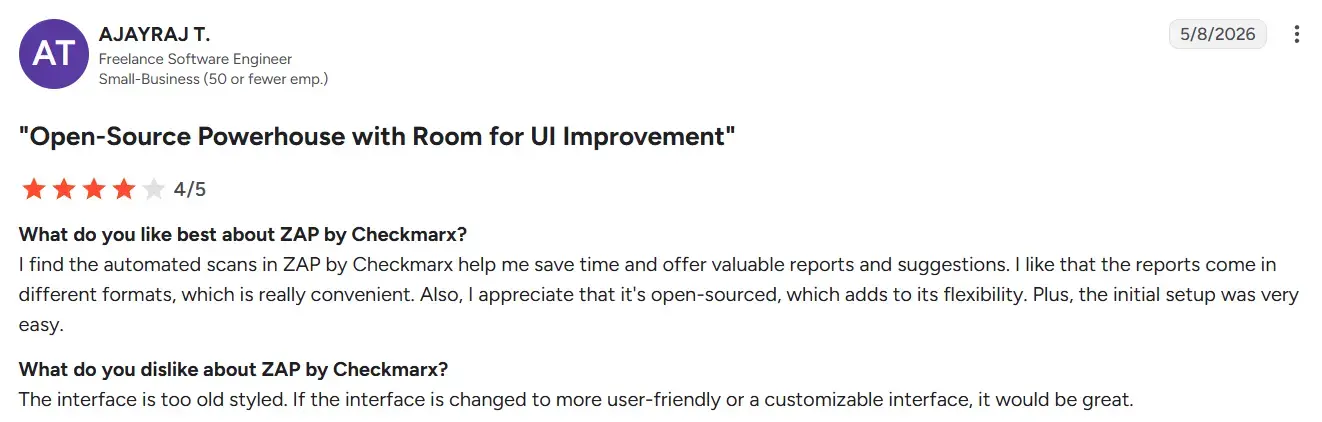
Checkmarx ZAP holds a 4.7 out of 5 rating from users, often praised for flexibility, value, and ease of cloud integration.
Pricing:
Free community version
Commercial support available through Checkmarx
8. Burp Suite
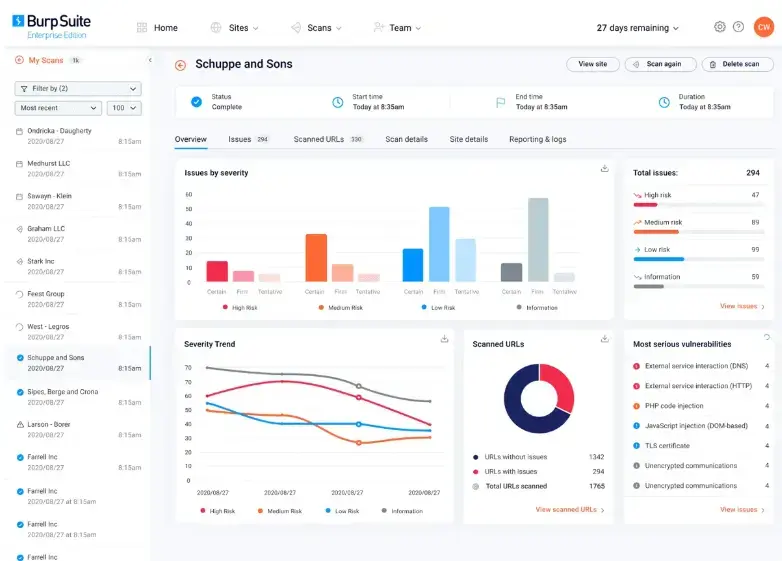
Burp Suite remains the preferred choice for manual and automated penetration testing. Its enterprise and cloud editions extend dynamic scanning capabilities for teams needing advanced control and customization.
Key features
Web and API testing with deep crawling capabilities
Enterprise edition for automated DAST at scale
BApp Store with hundreds of extensions
Integration with Jenkins and CI/CD pipelines
Detailed vulnerability reports with proof-of-exploit evidence
G2 rating:
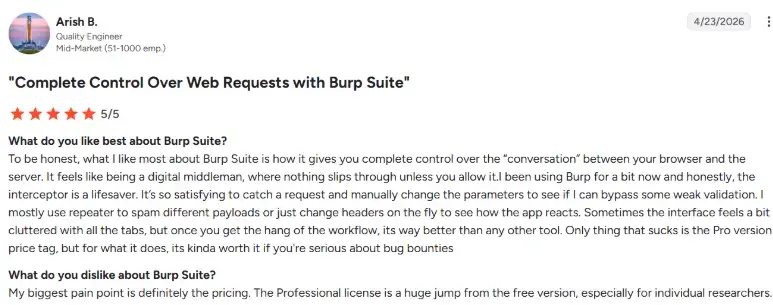
Burp Suite scores 4.8 out of 5 based on reviews, with users praising its powerful proxy and testing depth.
Pricing:
Professional: $499/user per year
Enterprise: Custom pricing for large-scale automation
9. Mend.io
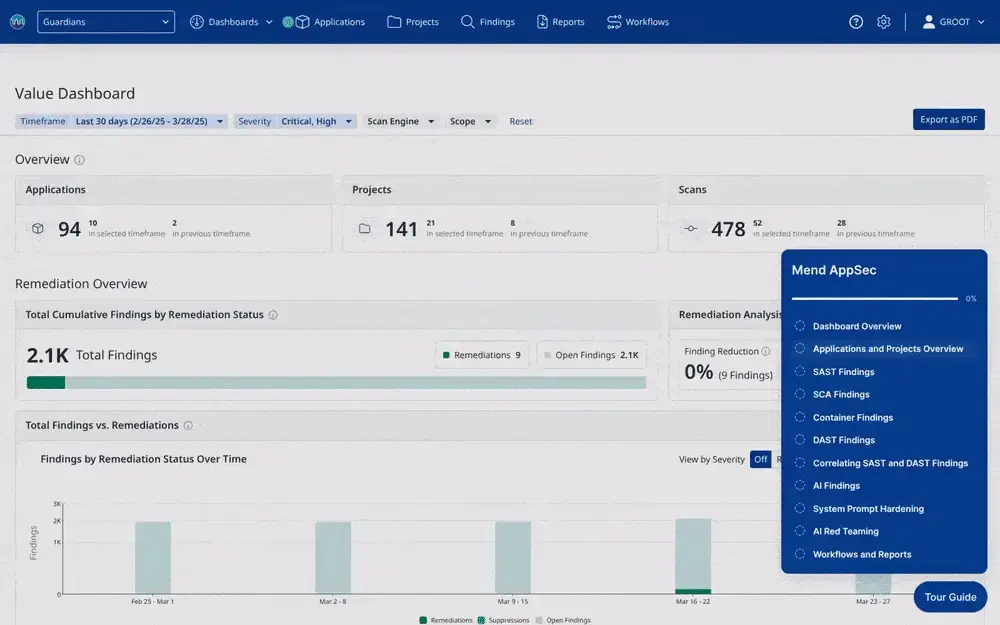
Mend.io, formerly known as WhiteSource, focuses on open-source component analysis and supply chain security. Its cloud-based SCA platform integrates directly into CI/CD workflows for automated dependency management.
Key features
Continuous monitoring of open-source vulnerabilities
Policy-driven license compliance management
Integration with popular cloud CI/CD systems
Container image scanning and remediation guidance
Vulnerability prioritization based on exploitability data
G2 rating:
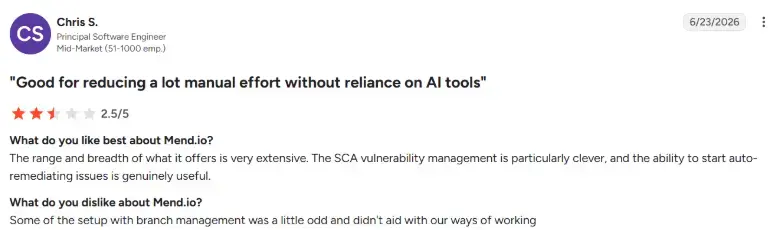
Mend.io has a 4.3 out of 5 rating from reviews, with users citing its depth in dependency analysis and compliance enforcement.
Pricing:
- Custom pricing based on organization size and integration scope
10. Contrast Security
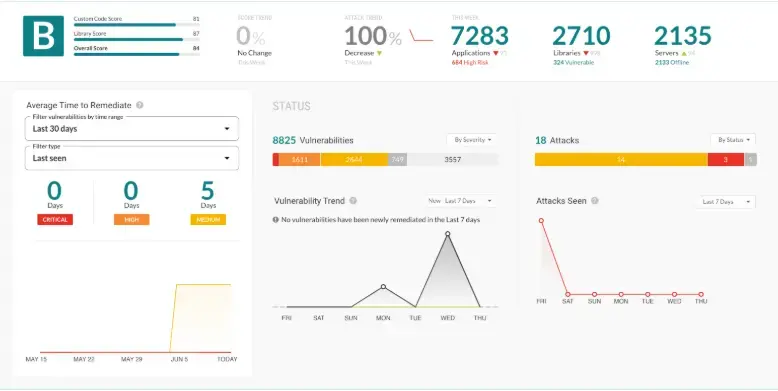
Contrast Security provides real-time application protection using interactive application security testing (IAST) and runtime application self-protection (RASP). It is built for cloud-native environments where applications need continuous runtime monitoring.
Key features
Runtime vulnerability detection and protection
IAST integrated directly into applications
Real-time feedback for developers during runtime
Supports containerized and serverless workloads
Centralized dashboard for visibility across clouds
G2 rating:
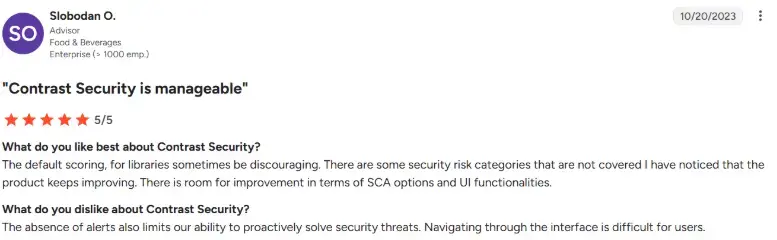
Contrast Security holds a 4.5 out of 5 rating from reviews, with users appreciating its runtime insights and minimal false positives.
Pricing:
- Custom pricing based on application volume and deployment scale
Final thoughts
Cloud-based application security testing tools have become essential in 2026 for organizations looking to secure modern, fast-evolving environments. Each tool brings unique strengths depending on team structure, deployment models, and testing maturity.
Organizations seeking unified AST platforms with broad coverage tend to look at Checkmarx One, GitLab Ultimate Security, Rapid7, Tenable, and Qualys, which offer enterprise scale governance. Teams prioritizing flexibility and specialization often choose Beagle Security for API security, agentic AI-powered pentest and automated DAST, ZAP for open source automation, or Mend.io for supply chain risk management. For runtime protection and IAST, Contrast Security offers deep visibility into live application behavior.
| If you need | Consider |
|---|---|
| Unified enterprise AST with broad governance | Checkmarx One, GitLab Ultimate Security |
| API security and agentic AI-powered pentest for modern stacks | Beagle Security |
| Open source testing | Checkmarx ZAP |
| Manual testing with deep proxy based control | Burp Suite |
| Runtime protection and IAST | Contrast Security |
| Risk based vulnerability management at scale | Tenable, Qualys |
| Supply chain and dependency security | Mend.io |
If your team is testing modern applications with authenticated flows, business logic, and API surfaces including GraphQL, Beagle Security is built specifically for that kind of coverage inside an existing CI/CD pipeline. Start a 14 day advanced free trialor book a demo to see how it fits your workflow.
FAQ
What is the best cloud based AST tool?
It depends on your architecture and team structure. Teams needing unified governance across large portfolios often choose Checkmarx One or GitLab Ultimate Security, while teams focused on API and business logic testing tend to look at Beagle Security.
How much does cloud based application security testing cost?
Pricing varies by category. Beagle Security starts at $119 per month, Burp Suite Professional is billed per user annually, and platforms like Checkmarx One, Qualys, and Tenable use custom enterprise pricing based on scale.
Is there a free cloud based AST tool?
Checkmarx ZAP is fully open source and free. Burp Suite offers a free Community Edition, though its Professional and Enterprise tiers are paid and the underlying product is not open source