Top penetration testing companies in Australia
Australian organisations are under more pressure than ever to prove their security posture, not just claim it. Regulators, boards, insurers, and enterprise customers now expect evidence. A completed penetration test has become the standard form of that evidence across frameworks like the Essential Eight, ISO 27001, SOC 2, and APRA CPS 234.
The market built around this demand is wide and uneven. It spans large, CREST accredited national firms, boutique senior led teams, and newer AI driven platforms built for continuous release cycles. Pricing and delivery models vary just as much, with engagements ranging from a few thousand dollars to well over $40,000 AUD for enterprise scope.
This guide breaks down the top 7 penetration testing companies in Australia in 2026, their key features, pricing context, and who each one is best suited for. Whether you are running a compliance driven audit or setting up continuous testing for your dev pipeline, this list will help you make the right choice for your team.
TL;DR: penetration testing companies in Australia at a glance
| Company | Best for | Delivery model | Pricing |
|---|---|---|---|
| Beagle Security | Dev teams needing continuous, CI/CD integrated testing | Agentic AI platform, SaaS | From $119/month (Essential), $359/month (Advanced), custom Enterprise |
| CyberCX | Large enterprise and government, full spectrum assurance | Human led, CREST accredited, national scale | Custom quote based on scope |
| Core Sentinel | SMEs wanting senior tester only delivery | Human led, boutique, Sydney based | Fixed price, quoted from scope |
| Tesserent (Thales Cyber Services ANZ) | Organisations wanting a pentest partner backed by a global security group | Human led, full service | Custom quote based on scope |
| Cyber7 | Businesses wanting a small, personally involved consulting team | Human led, boutique, Australia based | Fixed price packages, quoted from scope |
| Cyber Sapiens | Startups, SaaS, and compliance focused teams on a budget | Human led, global delivery team | Custom quote based on scope |
| KiwiQA | Teams that want pentesting bundled with wider QA services | Human led, part of a broader QA offering | Custom quote based on scope |
1. Beagle Security
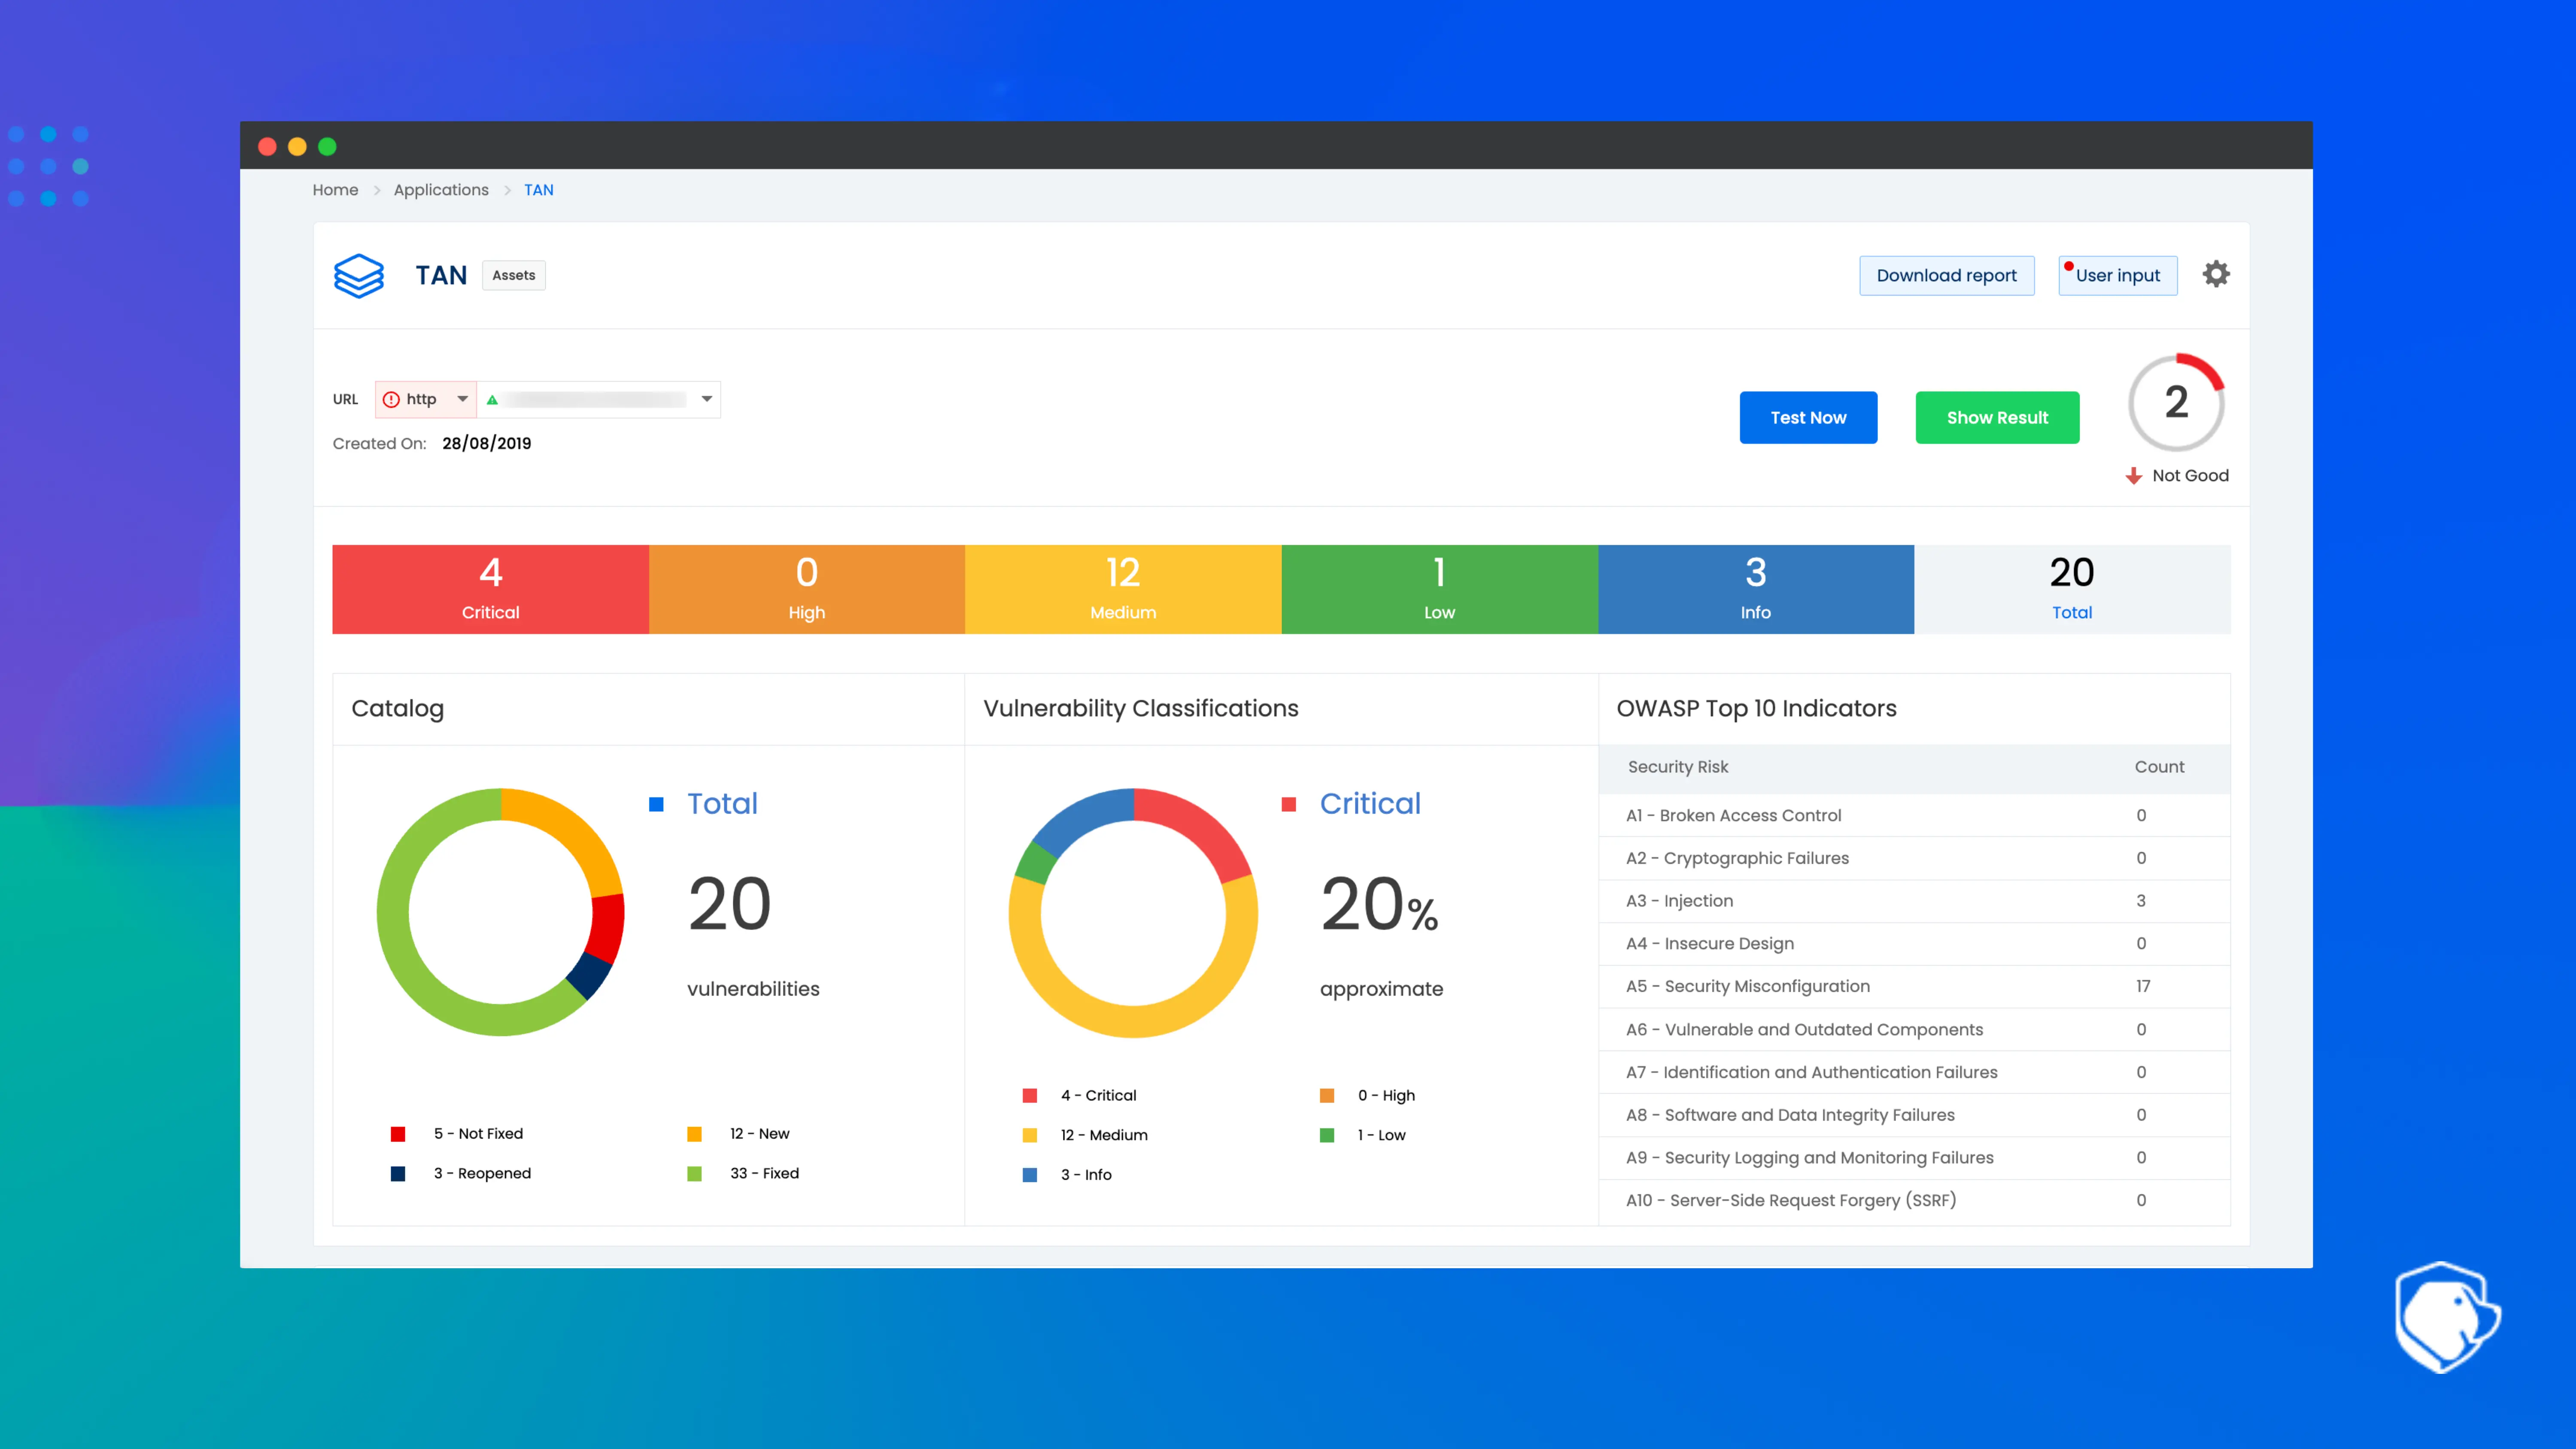
Beagle Security is an agentic AI penetration testing platform built for web applications, public APIs, and GraphQL endpoints. Rather than a point in time engagement delivered by a consulting firm, it runs as a continuous SaaS tool that development and security teams can plug directly into their release cycle.
The platform is built around business logic aware testing rather than surface level scanning, and it maps findings to compliance frameworks including SOC 2, ISO 27001, HIPAA, and PCI DSS. This makes it a common fit for product and engineering teams who need repeatable security testing between formal audits, not just once a year.
Key features
Agentic AI testing engine covering web apps, APIs, and GraphQL
CI/CD integration so tests run as part of the release pipeline
Business logic aware test cases, not just automated vulnerability scanning
Reporting mapped to SOC 2, ISO 27001, HIPAA, and PCI DSS
Interactive demo and self serve trial, no sales call required to start
Reviews
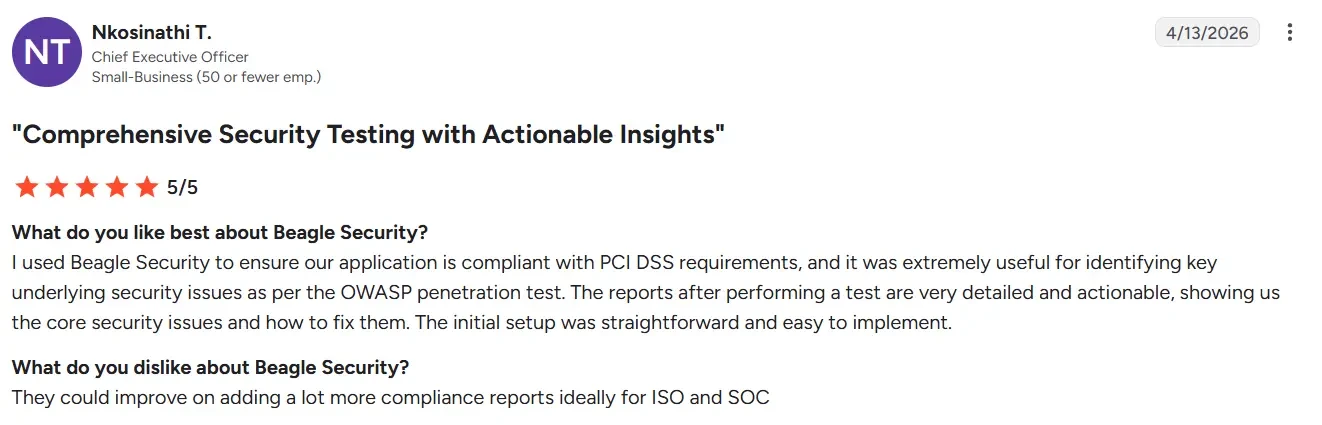
Beagle Security holds a 4.7 out of 5 rating on G2 across reviews concentrated heavily among small business users. Reviewers consistently point to the depth of its agentic AI scans and the clarity of its dashboards and reports as standout areas, with support quality also rated highly.
Pricing
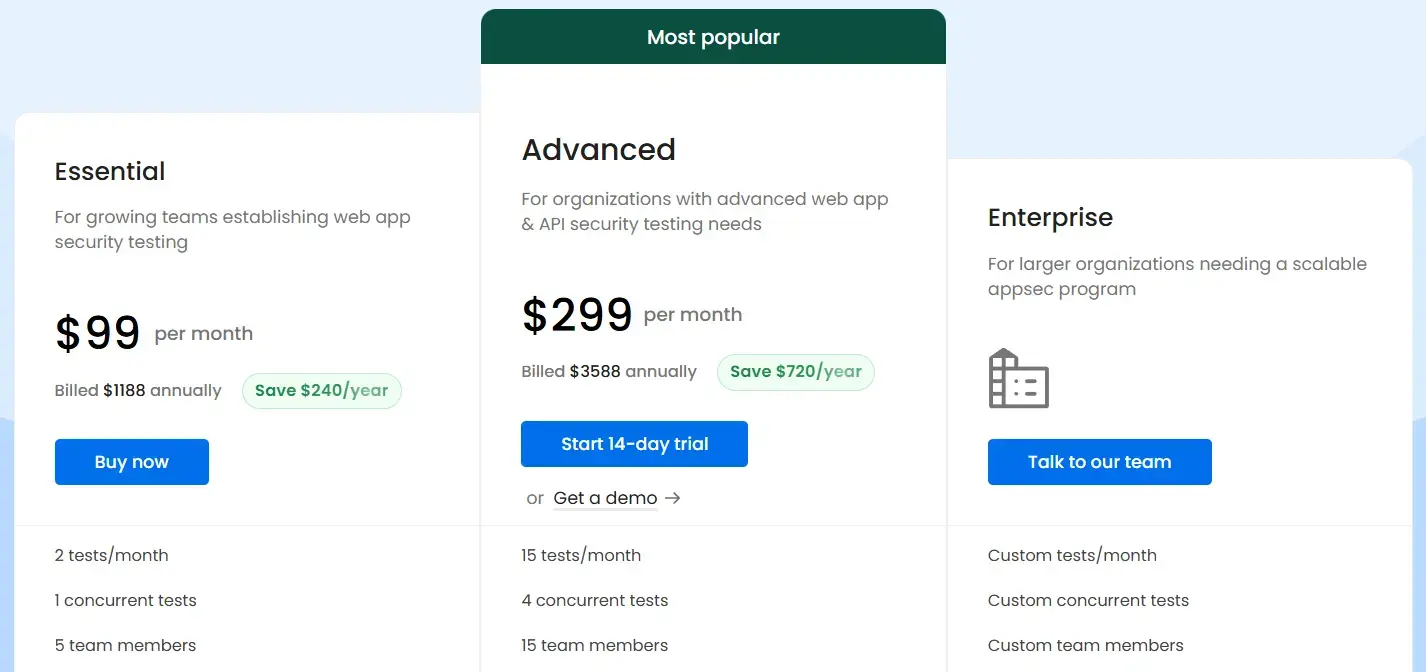
Beagle Security runs on a subscription model. The Essential plan starts at $99 a month (around $140 AUD), billed at $1,188 annually (around $1,685 AUD). The Advanced plan is $299 a month (around $424 AUD), billed at $3,588 annually (around $5,095 AUD). Enterprise pricing is custom based on the number of applications and scan frequency. A 14 day free trial is available to test the platform before committing.
2. CyberCX
CyberCX positions itself as Australia’s largest cyber security organisation, and the numbers back that up: more than 1,400 security and cloud professionals, over 3,000 penetration tests delivered annually, and nine security operations centres globally. It is a full service provider, with penetration testing sitting alongside incident response, managed detection, and governance and risk consulting.
Its client base skews toward government, financial services, healthcare, and critical infrastructure, sectors where scale, CREST accreditation, and the ability to run large, multi workstream engagements matter more than speed or price. CyberCX covers the full range of testing types, from web and API to wireless, physical, and social engineering.
Key features
CREST accredited penetration testing across web, API, network, wireless, and physical
Social engineering and red team capability alongside standard testing
National scale delivery with local presence across Australian states
Broader cyber security portfolio, including incident response and managed services
Experience across government, finance, healthcare, and critical infrastructure
Reviews
CyberCX has a Clutch profile, though it does not currently list published client reviews there. Its reputation instead rests on third party industry recognition, including being named a leader across multiple categories in ISG’s Provider Lens report, and on case studies published directly on its own site.
Pricing
CyberCX does not publish fixed pricing. Engagements are scoped and quoted individually, and given the breadth of services on offer, cost varies significantly based on the number of assets, testing types, and compliance requirements involved.
3. Core Sentinel
Core Sentinel is a Sydney based, senior only penetration testing firm founded in 2015 by Steve McLaughlin, an OSCE and OSCP certified tester with more than 20 years in the industry. The firm’s central pitch is direct: every engagement is delivered by a senior, certified tester, with no junior bench and no automated scan and send.
It covers web, mobile, external and internal infrastructure, and wireless testing, and works Australia wide from its Sydney base, including SME focused packages for businesses that need OWASP aligned testing without enterprise overhead.
Key features
Every engagement led by an OSCE or OSCP certified senior tester
Manual, OWASP and NIST aligned methodology rather than automated scanning
Coverage across web, mobile, external and internal infrastructure, and wireless
Fixed price, scope based quoting with no surprise costs
Compliance mapping across the Essential Eight, ISO 27001, SOC 2, APRA CPS 234, PCI DSS, and ST4S
Reviews
Core Sentinel has a Clutch profile, though no published reviews appear there yet. The feedback available comes from client testimonials on its own website, which point to detailed, fast turnaround testing and practical hardening guidance.
Pricing
Core Sentinel uses fixed price, upfront quotes based on the number of applications, IP ranges, users, and testing depth involved, rather than time and materials billing.
4. Tesserent
Tesserent was founded in 2015 and grew into an ASX listed, full service cyber security and secure cloud provider across Australia and New Zealand before being acquired by the Thales Group in October 2023. Its penetration testing services now operate under the Thales Cyber Services ANZ banner, combining the local team and methodology with the backing of a global defence and security company.
The service covers internal and external network testing, web and mobile application testing, API testing, and secure code review, delivered to clients across government and commercial sectors throughout ANZ.
Key features
Internal and external network penetration testing
Web, mobile, and API application testing with OWASP aligned methodology
Secure code review combining static and dynamic analysis
Backed by Thales Group’s global security and defence expertise
Long standing relationships across ANZ government and enterprise clients
Reviews
Tesserent has a Clutch profile with no published client reviews at present. Its market reputation is built on scale and longevity instead, including its former status as an ASX listed provider with more than 1,200 mid-sized to enterprise, government, and critical infrastructure clients, cited on its own Clutch and company profile.
Pricing
As with other full service providers, pricing is scoped per engagement and not published. Cost depends on the systems in scope, testing type, and reporting requirements.
5. Cyber7
Cyber7 is a smaller, Australia based cyber security firm built around close, personal involvement in every engagement. Its penetration testing work is performed by principal security consultants directly, rather than being delegated down to junior staff, with its CEO personally overseeing testing quality across projects.
The team draws on more than 30 years of combined IT industry experience spanning penetration testing, security architecture, cryptography, and computer forensics, and offers fixed price packages for organisations that want a straightforward, predictable engagement.
Key features
Testing performed directly by principal security consultants
Coverage across web applications, networks, and wireless devices
Broader security assessment services beyond testing alone
Fixed price penetration testing packages
Small team model that keeps client relationships close and consistent
Reviews
Cyber7 does not have a visible Clutch, G2, or Google review base at scale. What is available comes from the company’s own site and LinkedIn page, which highlight personalised service and its award recognised leadership, though this has not been independently verified through a third party review platform.
Pricing
Cyber7 offers fixed price penetration testing packages, with cost depending on the scope and systems being tested. Specific figures are provided on request rather than published.
6. Cyber Sapiens
Cyber Sapiens, styled CyberSapiens, is an ISO 27001:2022 certified security firm with delivery teams spread across India, Australia, Canada, and the United States. This global delivery model is central to its pitch: broad VAPT coverage across web, mobile, API, cloud, network, IoT, and client side systems, aimed at cost conscious teams.
Its client base leans toward startups, SaaS platforms, fintech, ecommerce businesses, and SMEs, organisations that need practical, remediation focused findings without enterprise level engagement costs.
Key features
Web, mobile, API, cloud, network, IoT, and client side VAPT coverage
ISO 27001:2022 certified internal security practices
Global delivery team spanning India, Australia, Canada, and the US
Strong focus on startups, SaaS, fintech, and ecommerce clients
Remediation support included alongside findings, not just a report
Reviews
Cyber Sapiens does not have a visible G2 or Clutch review base. Its available feedback comes from case studies published on its own site, describing resolved authorisation, session management, and API security issues for Australian clients, alongside praise for clear communication during testing.
Pricing
Cyber Sapiens does not publish fixed pricing and quotes engagements individually, with its global delivery model generally positioned as a more budget friendly option than Australia only enterprise providers.
7. KiwiQA
KiwiQA is primarily a software testing and QA company, with penetration testing offered as one part of a much wider security and quality assurance practice. This makes it a different kind of choice from the dedicated security firms on this list: it suits organisations that already use, or want to use, a single vendor for both functional QA and security testing.
Its penetration testing covers web applications, networks, mobile apps, cloud infrastructure, and IoT devices, delivered by an in-house team alongside its broader automation and manual testing services.
Key features
Penetration testing bundled with wider QA and automation testing services
Coverage across web, network, mobile, cloud, and IoT
Five phase testing methodology from scoping through to exploitation
Structured penetration test reports aimed at both technical and business readers
Established presence in Australia, the UK, and beyond
Reviews
KiwiQA has a Clutch profile with a small number of published reviews, describing thorough vulnerability assessment and penetration testing work with clear, professional communication. Feedback tends to come from smaller development teams and agencies rather than large enterprises, consistent with its broader QA services focus.
Pricing
KiwiQA prices penetration testing on a custom quote basis, with cost depending on scope. Its marketing consistently positions pricing as accessible relative to specialist security only firms.
What to look for in a penetration testing company
Choosing between these providers comes down to more than price. A few factors matter more than most when you are comparing quotes.
Certification and methodology
Look for testers holding OSCP, OSCE, or CREST credentials, and ask whether testing is manual, automated, or a genuine mix. A report generated purely from an automated scan is not the same product as one built on manual exploitation.
Compliance mapping
If you need a test for a specific framework, such as SOC 2, ISO 27001, PCI DSS, or APRA CPS 234, confirm the provider can map findings directly to that framework’s control requirements, not just produce a generic vulnerability list.
Reporting quality
Ask to see a sample report. The best reports separate technical detail for engineers from an executive summary for leadership, and prioritise findings by real world risk rather than raw vulnerability count.
Retesting and remediation support
Confirm whether retesting after fixes are applied is included or billed separately, and whether the provider offers any guidance beyond the initial findings.
Delivery model and cadence
A once a year manual engagement suits organisations with slow release cycles. Teams shipping continuously are usually better served by a platform that can test on every release, or a provider that supports more frequent, lighter touch testing between full engagements.
Final thoughts
There is no single best penetration testing company in Australia, only a best fit for a given organisation’s size, release cadence, and compliance obligations. Large enterprises and government agencies with complex environments tend to gravitate toward full service, CREST accredited firms like CyberCX or Tesserent. SMEs that want senior led, manual testing without enterprise overhead often find a better match with boutique firms like Core Sentinel or Cyber7. Teams running lean and needing broad but affordable VAPT coverage may lean toward Cyber Sapiens or KiwiQA.
For development and product teams that release software continuously and need security testing to keep pace with that cadence, a platform like Beagle Security offers a different model entirely: business logic aware, agentic AI testing that runs inside the CI/CD pipeline rather than waiting for an annual audit window. The right choice depends on how your team actually ships software, not just which name is most familiar.
FAQ
How much does penetration testing cost in Australia?
Pricing typically ranges from around $6,000 to $40,000 AUD, depending on the scope, the number of applications or systems tested, and whether the engagement needs to satisfy a specific compliance framework. Simpler single application tests sit at the lower end, while enterprise infrastructure or multi framework compliance engagements cost more.
How often should penetration testing be done?
Most frameworks and industry guidance recommend at least once a year, or after any significant change to an application or infrastructure. Organisations with high risk profiles, or those shipping code frequently, generally test more often, which is where continuous testing platforms fit in alongside annual manual engagements.
What is the difference between automated scanning and manual penetration testing?
Automated scanning identifies known vulnerability patterns quickly but can miss business logic flaws and chained attack paths. Manual testing, performed by a certified tester, can uncover issues that require understanding how an application actually works. Many providers, including several on this list, combine both approaches.