SaaS penetration testing: a complete guide [2026]
SaaS (Software-as-a-service) adoption has not slowed down, and neither has attacker interest in it. Every business workflow that moves to a cloud-hosted platform brings a new set of APIs, integrations, and permission structures that someone has to secure. Attackers know this, and they have shifted their focus accordingly, targeting misconfigured access controls, insecure APIs, broken tenant isolation, and business logic flaws rather than chasing zero-days.
This is the case for SaaS penetration testing as a standing practice rather than a one-time checkbox. Whether you run a B2B platform, a consumer app, or a multi-tenant cloud service, a structured pentest finds the vulnerabilities an attacker would find first, before they do.
This guide covers what SaaS penetration testing is, why it matters for modern SaaS architecture specifically, what a complete test includes, and how to build it into your security program.
What is SaaS penetration testing?
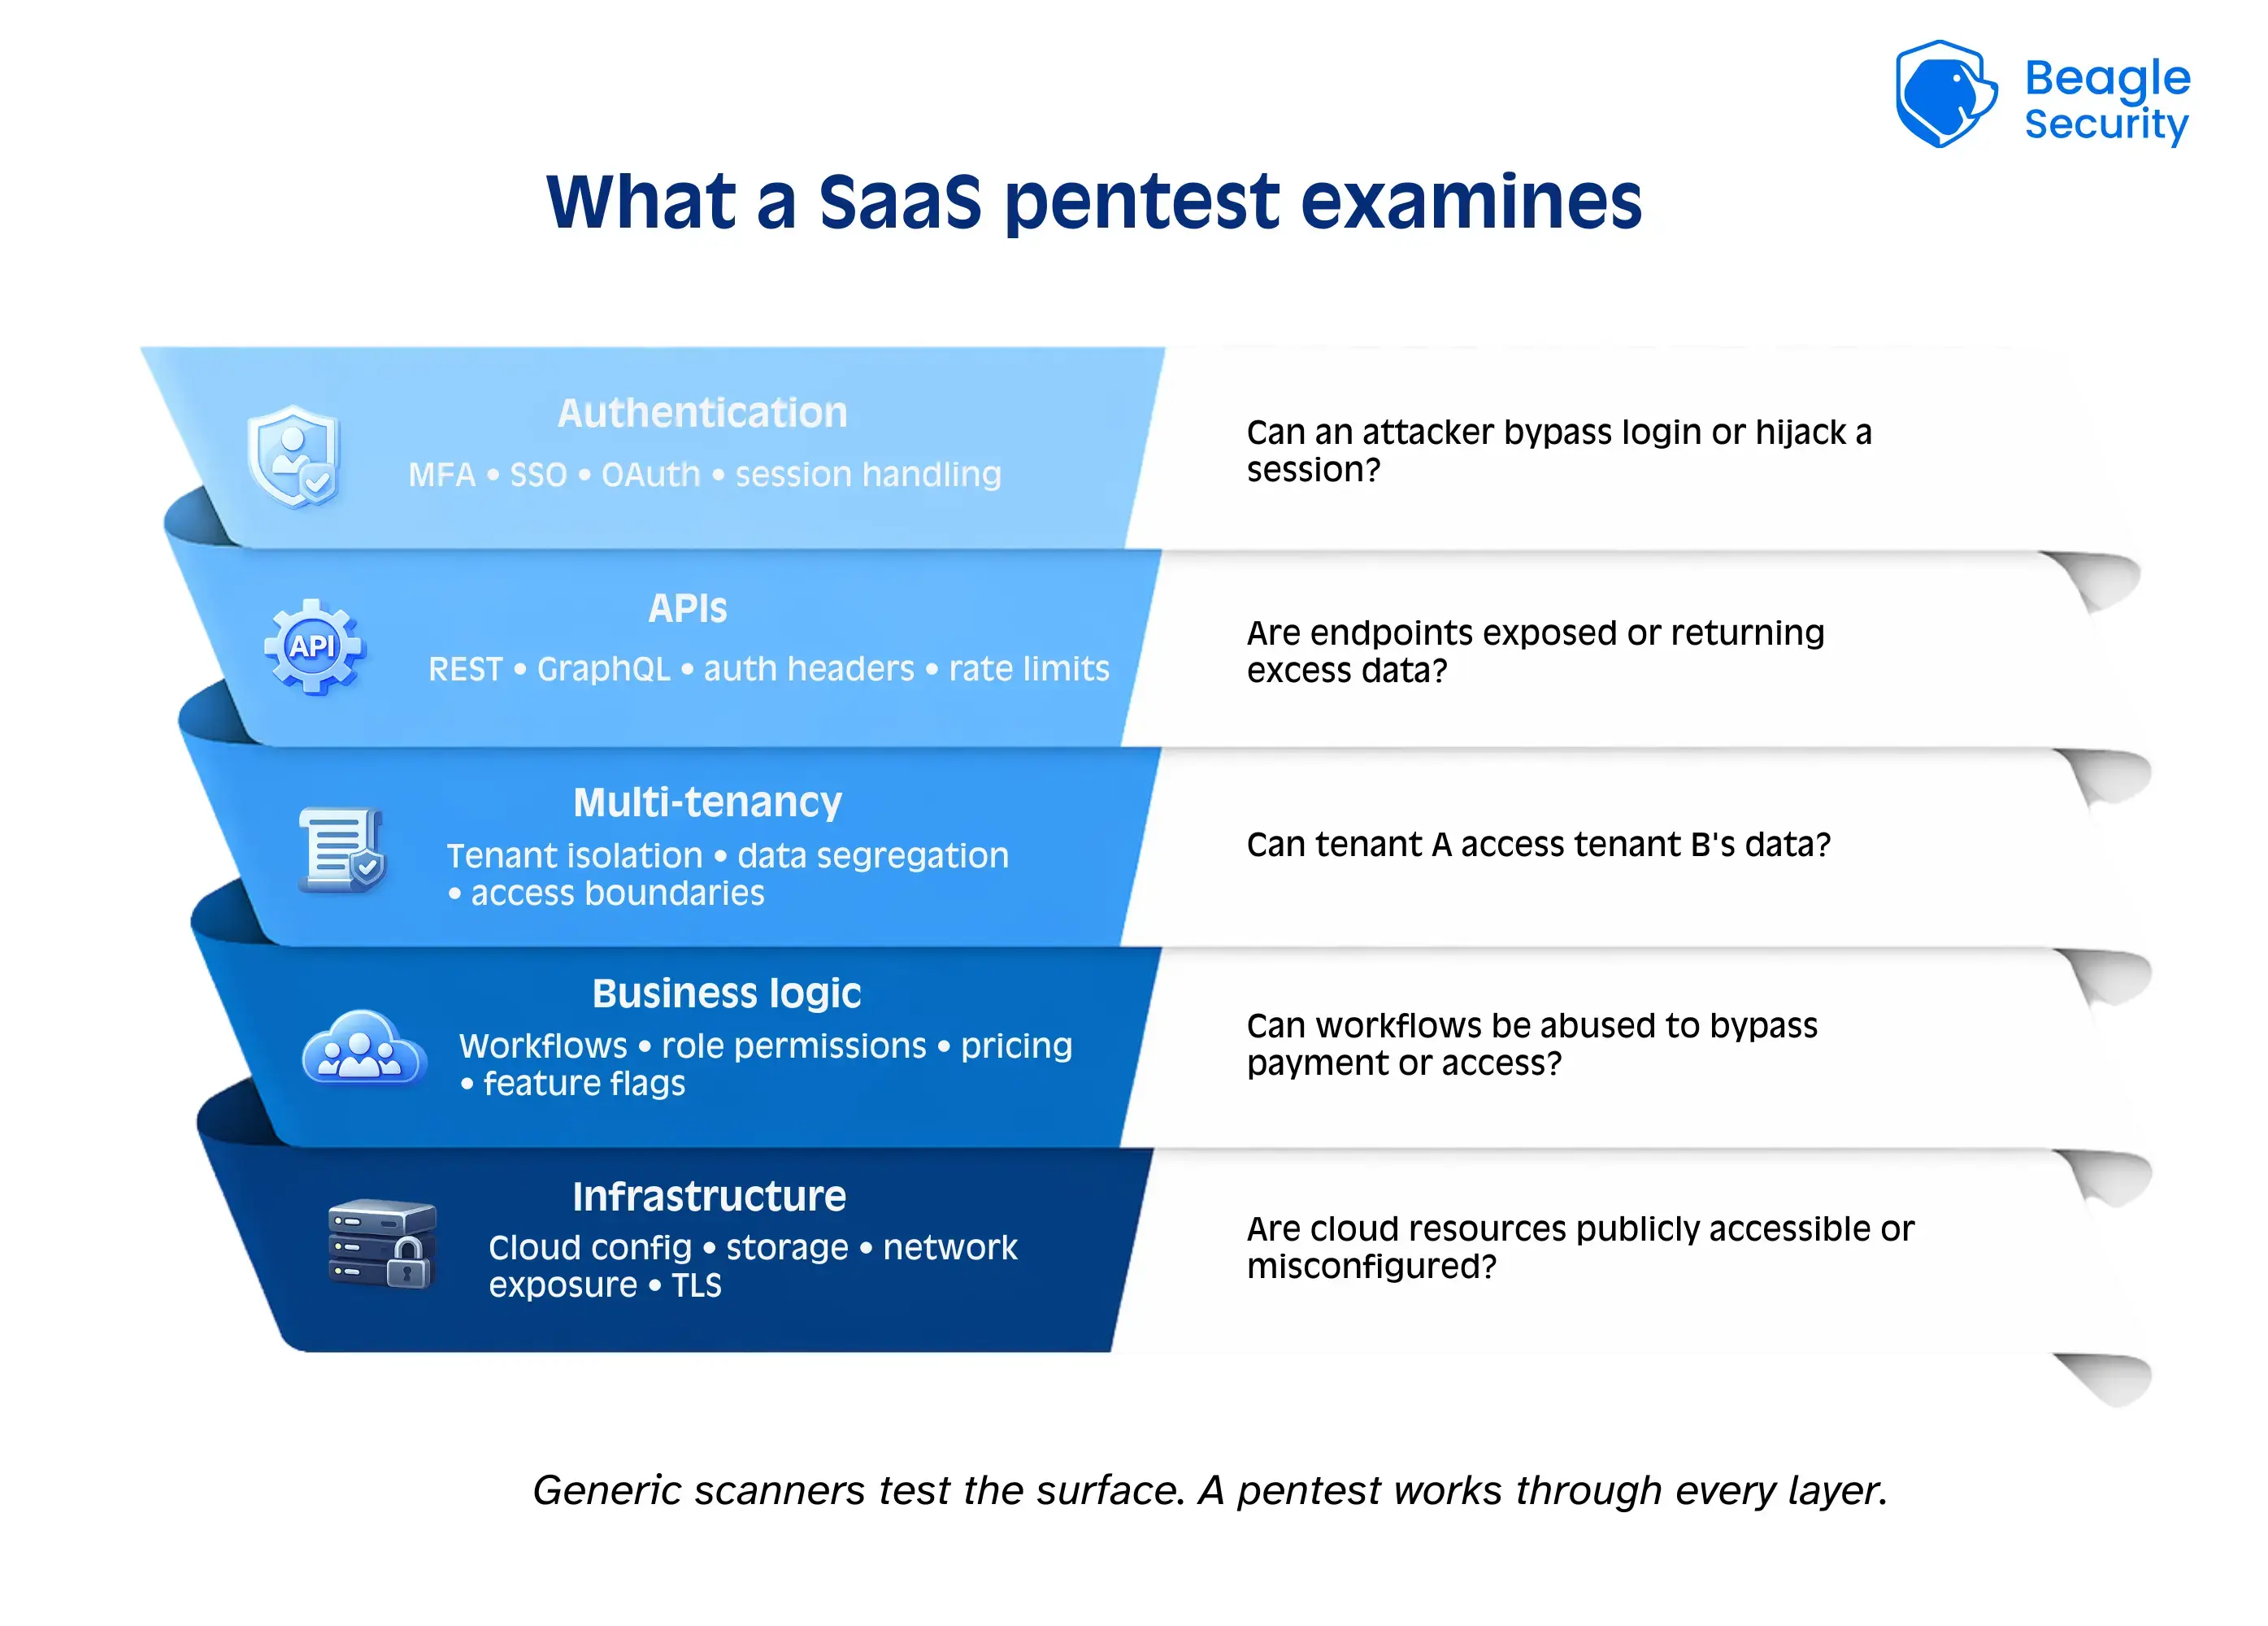
SaaS penetration testing is a security assessment that identifies, exploits, and validates vulnerabilities in cloud-hosted applications. It differs from a traditional web app pentest in what it prioritizes: multi-tenant architecture, API and microservices security, role-based access controls, business logic workflows, authentication and SSO integrations, and data segregation between tenants.
A SaaS pentest combines automated and manual testing to answer a specific question: can an attacker compromise the application, access data outside their scope, disrupt a workflow, or escalate privileges beyond their intended role? Because SaaS platforms typically hold sensitive business data, financial information, or user identities on behalf of every customer on the platform, the answer to that question carries weight well beyond a single account.
Why SaaS penetration testing matters
SaaS applications run in dynamic, interconnected, cloud-native environments. Unlike on-premise software, they need to secure multi-tenant data, integrations, APIs, and continuous product updates all at once, which creates a security profile attackers are actively learning to exploit.
Here’s a closer look at where that risk concentrates.
Attackers actively target SaaS misconfigurations
Most modern SaaS breaches don’t start with a zero-day exploit. They start with a misconfiguration, often introduced through rapid feature releases, layered permission systems, or simple human error.
Common misconfiguration risks include misconfigured access control that grants users unintended privileges, unsecured admin or super-admin consoles, overly permissive APIs that expose sensitive data, publicly accessible development or staging environments, inconsistent tenant isolation rules, and API keys or secrets stored incorrectly.
Because SaaS platforms ship changes constantly, a small configuration mistake can become a critical entry point within days. A pentest simulates how an attacker would find and exploit that gap before it becomes an incident report rather than a fixed bug.
SaaS is multi-tenant: one flaw can expose every customer
SaaS platforms often serve hundreds or thousands of tenants on shared infrastructure. A single vulnerability in the multi-tenant architecture can compromise every customer on the platform, not just one.
Pentesting validates isolation at the layers that matter: database isolation at the row, schema, or instance level, role-based access control and the privilege escalation paths around it, API endpoints checked for cross-tenant data leakage, shared storage systems like S3 buckets and caches, and session management that could allow takeover or fixation.
Something as small as an incremental ID or a leaked tenant identifier in an API response can be enough to expose data across the entire platform. Multi-tenancy doesn’t just add risk, it multiplies the blast radius of any single flaw, which is why isolation boundaries need to be tested directly rather than assumed.
SaaS integrates with third-party systems, broadening the attack surface
Modern SaaS products sit inside a wider ecosystem of integrations, and each one introduces a new trust relationship, a new set of permissions, and a new potential failure point.
Typical integrations span SSO and authentication providers like Okta, Azure AD, and Google Workspace, payment gateways like Stripe, Razorpay, and PayPal, CRM and ERP platforms like Salesforce, SAP, and HubSpot, communication tools like Slack, Teams, and Gmail APIs, workflow automation services like Zapier and Make, and cloud providers like AWS, GCP, and Azure.
Attackers target integrations because compromising one external system can hand them indirect access to the SaaS environment itself. Pentesting checks token handling, OAuth and OIDC flow correctness, webhook signature verification, API permission scopes, and data validation between connected systems, since a weakness in any one of these can cascade quickly across the rest of the ecosystem.
Organizations handling customer data are expected to follow established security frameworks, and most of those frameworks build regular penetration testing directly into their certification requirements.
SOC 2, ISO 27001, GDPR, and PCI DSS each expect evidence of ongoing testing, not a one-time assessment. Without it, certification renewal becomes harder to defend, audits take longer, and customer trust is the first thing to erode when a gap surfaces.
What does a SaaS pentest include?
A complete SaaS penetration test examines the full security posture of your platform, from authentication flows to multi-tenant isolation and underlying infrastructure. Because SaaS applications evolve quickly, each layer must be tested thoroughly to ensure attackers can’t exploit business logic, API weaknesses, or misconfigurations.
Here’s what a modern SaaS pentest typically covers:
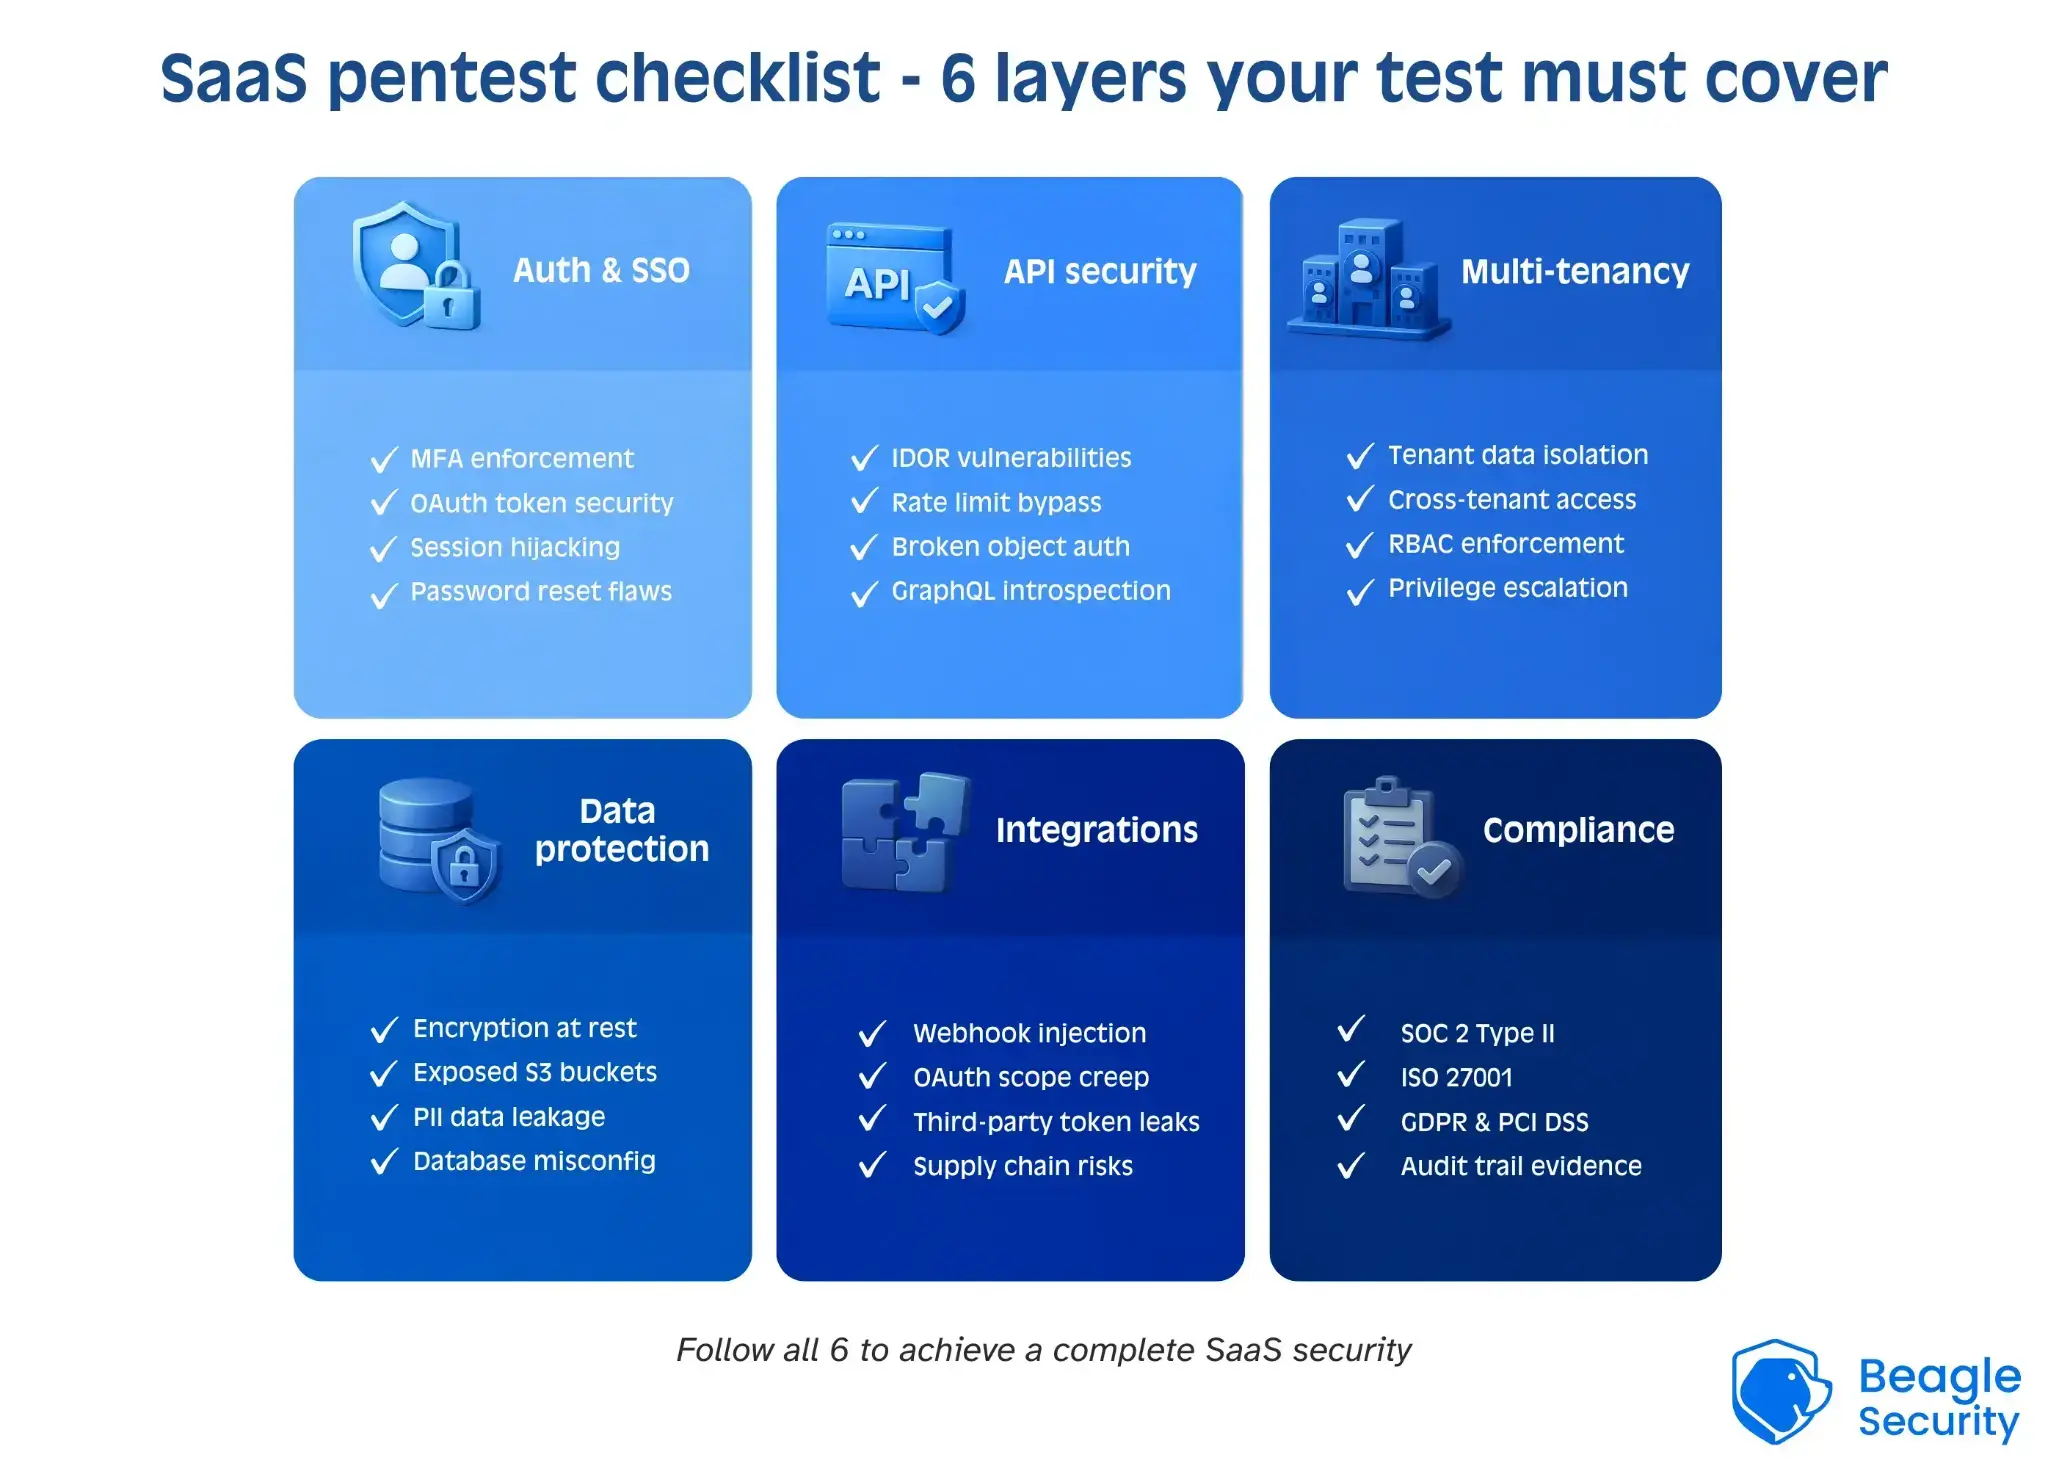
1. Authentication & access control testing
Evaluates MFA, SSO, OAuth, password policies, session handling, and role permissions to ensure attackers cannot bypass authentication or gain unauthorized access.
2. API & microservices security testing
Checks APIs for BOLA, insecure endpoints, rate-limit bypasses, token leaks, and microservice trust issues to prevent data exposure or unauthorized actions.
3. Business logic testing
Identifies workflow flaws like skipped steps, payment bypasses, approval manipulation, or privilege misuse that automated scanners typically miss.
4. Multi-tenant isolation testing
Ensures strict tenant separation by testing for cross-tenant data access, predictable IDs, and weak access controls that could expose other customers’ data.
5. Configuration & infrastructure review
Assesses cloud settings, storage permissions, CI/CD security, dependencies, and secrets management to detect misconfigurations attackers often exploit.
6. Frontend & client-side testing
Tests for XSS, CSRF, DOM issues, insecure CSP, and client-side data exposure to protect users from browser-based attacks.
7. Reporting & remediation verification
Delivers clear findings, impact analysis, and fixes, followed by re-testing to verify vulnerabilities are resolved and security is maintained.
How SaaS penetration testing works: step-by-step process
Step 1: Scoping and pre-engagement
The scoping phase sets the direction for the entire engagement and gets both teams aligned before any testing starts. This includes defining test boundaries and in-scope functionality, the user roles and tenant types to be tested, the cloud components, APIs, and integrations involved, compliance requirements such as SOC 2, ISO 27001, GDPR, or PCI DSS, the testing environment, whether staging, a production mirror, or a sandbox, and the access, accounts, and timeline needed to run the test.
This phase exists to remove ambiguity before it costs anyone time. It ends with a signed scope document and engagement plan that guides everything that follows.
Step 2: Information gathering
Pentesters use this step to understand how the platform actually functions before attempting to break it. That means reviewing system architecture and data flows, the technology stack across frontend, backend, and cloud services, authentication flows including SSO, MFA, OAuth, and API keys, API documentation and endpoint structure, business logic workflows, and any public-facing assets such as subdomains or open API documentation.
Pentesters often talk directly with developers or product teams during this phase. The goal is a complete enough picture that testing can target real risk rather than guess at it.
Step 3: Vulnerability assessment
This step runs a broad pass across the platform, combining automation with manual checks. Focus areas typically include outdated libraries, packages, or frameworks, known CVEs and dependency risk, exposed or unauthenticated endpoints, weak configurations in CORS policies, headers, and rate limits, missing security controls, and insecure or forgotten staging environments still reachable from the internet.
The result is an initial map of where risk concentrates across the SaaS ecosystem, before deeper exploitation begins.
Step 4: Manual exploitation
This is the phase where a tester behaves like an actual attacker rather than a scanner. That means attempting to escalate privileges, break tenant isolation through cross-tenant access, manipulate or abuse APIs, bypass authentication or session controls, exploit gaps in workflow and business logic, and chain smaller vulnerabilities together into something more severe.
The point of this step is to show what an attacker could realistically achieve, not what a scanner flagged as theoretically possible.
Step 5: Reporting
A useful pentest report gives a team both clarity and a clear next step. That includes an executive summary for leadership, risk scoring with severity levels, proof-of-concept detail for each finding, step-by-step reproduction instructions, screenshots or payload samples where relevant, tenant-specific or environment-specific impact, and remediation guidance ordered by priority.
The report’s job is to make sure engineering and security teams understand what went wrong, how serious it is, and exactly what to do about it.
Step 6: Re-test and continuous testing
A pentest isn’t finished the moment the report ships. This phase covers re-testing every vulnerability that was previously identified, confirming the patches actually hold, checking that remediation didn’t introduce new issues, updating compliance-ready documentation, and recommending ongoing or continuous testing where it makes sense.
Because SaaS products change constantly, many teams move past a single annual test toward continuous testing that catches issues as new features ship. The goal isn’t passing a test once. It’s keeping the product secure as it keeps changing.
How often should you perform SaaS penetration testing?
| Scenario | Recommended frequency |
|---|---|
| Minimum for compliance | Annually |
| Fast-moving SaaS companies | Quarterly |
| Enterprise-facing SaaS | Quarterly or bi-annual |
| API-first, multi-tenant, or AI-driven SaaS | Continuous |
| After major releases | Immediately |
| After incidents | Immediately |
The most secure SaaS companies follow a continuous and annual approach:
Continuous pentesting for real-time coverage
One annual full-scope pentest for compliance and audits
This gives you the best of both worlds. Strong security posture year-round and complete documentation for compliance.
SaaS pentesting vs. traditional web app pentesting
| Feature | SaaS pentest | Traditional web pentest |
|---|---|---|
| Multi-tenant testing | Yes | Usually no |
| API-first focus | High | Medium |
| SSO / OAuth | Critical | Optional |
| Role & access control depth | Deep | Standard |
| Compliance requirements | High (SOC 2, ISO) | Medium |
This comparison reinforces the importance of SaaS-specific testing, not generic web testing.
How Beagle Security helps SaaS companies stay secure
Beagle Security offers a modern, automated penetration testing platform designed for high-growth SaaS teams.
Key benefits include:
Business-logic testing with no-code workflows
Advanced API, GraphQL, and authentication testing
Continuous CI/CD native penetration testing
Multi-tenant isolation validation
Role-based scenario testing (RBAC-aware)
Enterprise-ready reports
Integrations with Slack, Jira, GitHub, GitLab, Bitbucket & more
Zero false-positive approach
This ensures SaaS teams get deep security coverage with faster turnaround compared to traditional pentesters.
Final thoughts
SaaS penetration testing has moved from optional to expected. It’s what keeps your application, your customers, and their data secure as the platform itself keeps changing. Modern SaaS environments are API-driven and multi-tenant by default, which means they need testing that goes deeper than what a traditional web app requires.
Regular pentesting, paired with the right security partner, strengthens how much your product can be trusted, narrows the realistic attack surface, and keeps you ahead of compliance expectations rather than scrambling to meet them.
If you’re looking for a modern, accurate, and developer-friendly way to test your SaaS platform, Beagle Security offers a complete solution built around SaaS workflows specifically.
FAQs
What is the penetration test for SaaS?
A SaaS penetration test simulates a real attack against your cloud-hosted application to find vulnerabilities in authentication, APIs, multi-tenant isolation, and business logic. It combines automated scanning with manual exploitation, since the most damaging SaaS risks, like a workflow bypass or a tenant isolation gap, are the kind a scanner alone won’t catch.
What is SaaS vs PaaS?
Software as a Service (SaaS) delivers fully functional, ready-to-use software applications over the internet, usually via a subscription. Platform as a Service (PaaS) provides developers with a cloud-based framework and tools to build, test, and deploy their own custom applications without worrying about managing the underlying servers or infrastructure.
Why do SaaS companies need penetration testing?
To prevent breaches, meet compliance, secure multi-tenant data, and protect API-driven workflows.